How can SOC Teams use MCPs for threat detection or enrichment?
How can SOC Teams use MCPs for threat detection or enrichment?
Scenario: A Tier 1 analyst needs instant context around a suspicious IP. Example Task: “Investigate IP 198.51.100.10 and show reputation, malware associations, breach records, and any linked phishing domains.” Outcome: The MCP Server merges SOCRadar Threat Intelligence, attack surface signals, dark web findings, and repository exposures into one enriched profile with recommended next steps.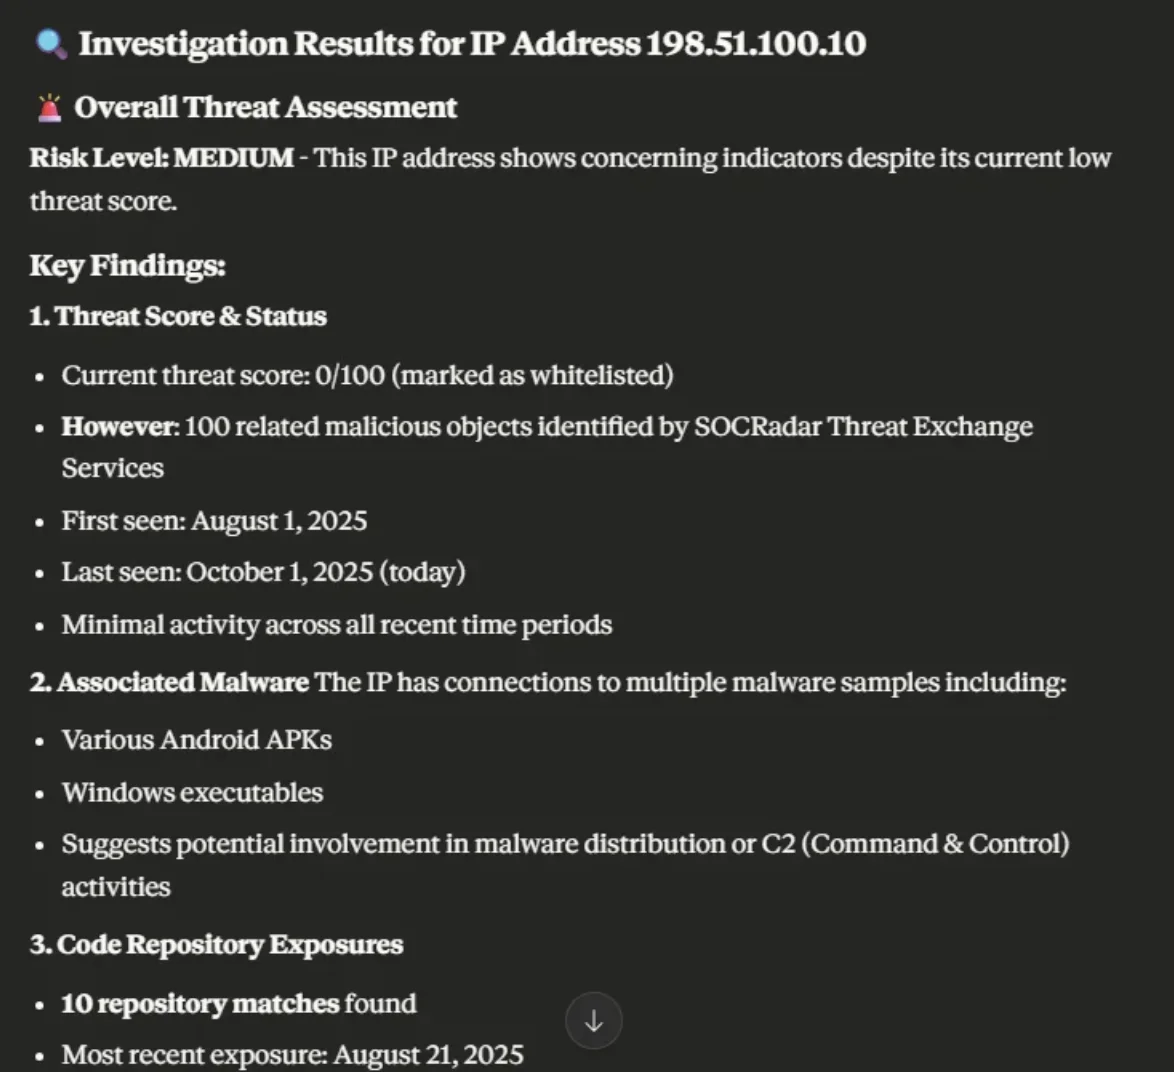 See the SOC MCP Use Cases blog for detailed examples (critical incident surfacing, phishing detection, code repo exposure monitoring, ransomware infrastructure tracking, credential analysis, and more)
Uncategorized @us-en
Oct 16, 2026
CVE-2026-102764: BeyondTrust Zero-Day Exploited
BeyondTrust has disclosed CVE-2026-102764, a critical Remote Support vulnerability exploited as a zero-day weeks before customers received a patch. The attack began…
Cyber News
Oct 15, 2026
Cisco Secure Email & PAN-OS Zero-Days Exploited
Cisco Secure Email & PAN-OS Zero-Days Exploited Cisco and Palo Alto Networks have patched two actively exploited zero-day vulnerabilities that can lead…
CTI Fundamentals
Oct 15, 2026
SOCRadar Splunk Integration: New MSSP and Vulnerability Apps
SOCRadar Splunk Integration: New MSSP and Vulnerability Apps Your analysts live in Splunk. Your external risk does not: SOCRadar alarms for dozens…
Intelligence in your inbox every Thursday.
Join 30,000+ security professionals reading SOCRadar research.
Subscribe