Extended Threat Intelligence (XTI) Platform
Proactively stop threats at the source.
SOCRadar's Extended Threat Intelligence (XTI) platform empowers organizations to proactively identify, analyze, and mitigate cyber threats. Functioning as an extension of your security team, our platform is built on a powerful fusion of automation and human expertise.
Core Use Cases
Explore five core XTI modules.
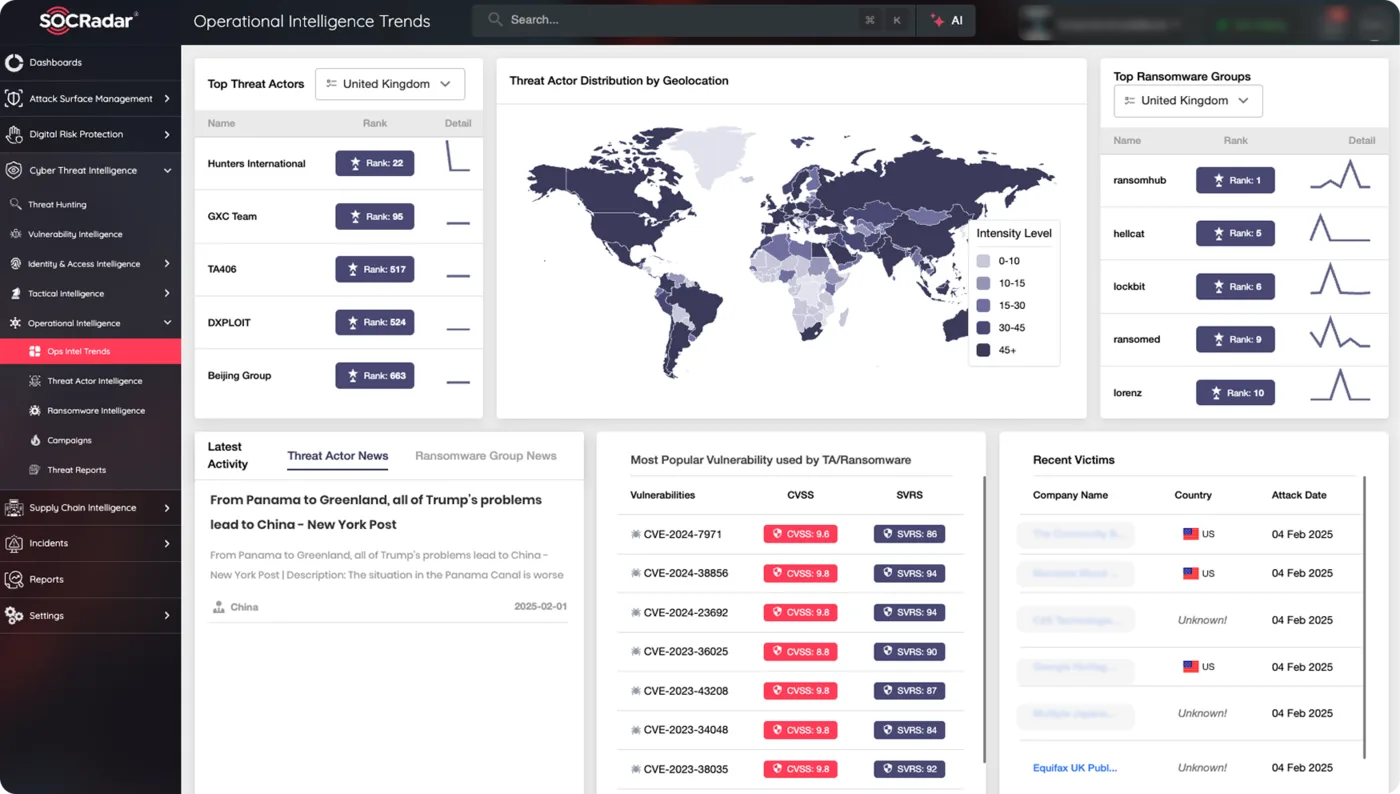
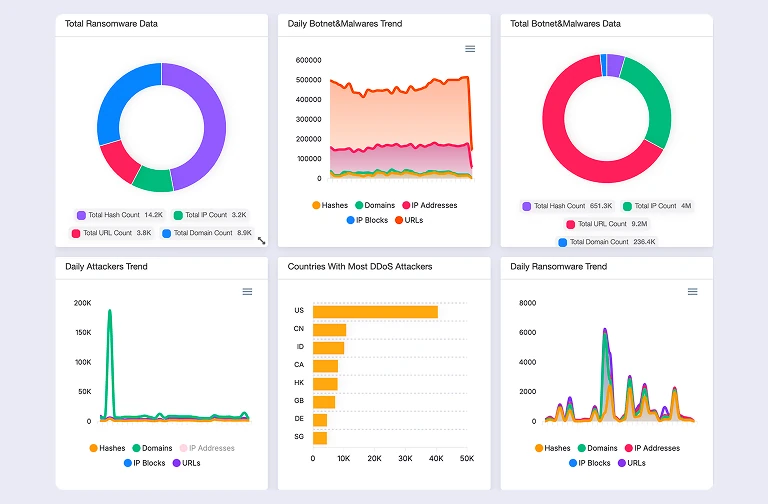
Cyber Threat Intelligence Module
Rapid, contextual insights from a single, searchable threat intelligence database, built for swift response.
Explore Cyber Threat Intelligence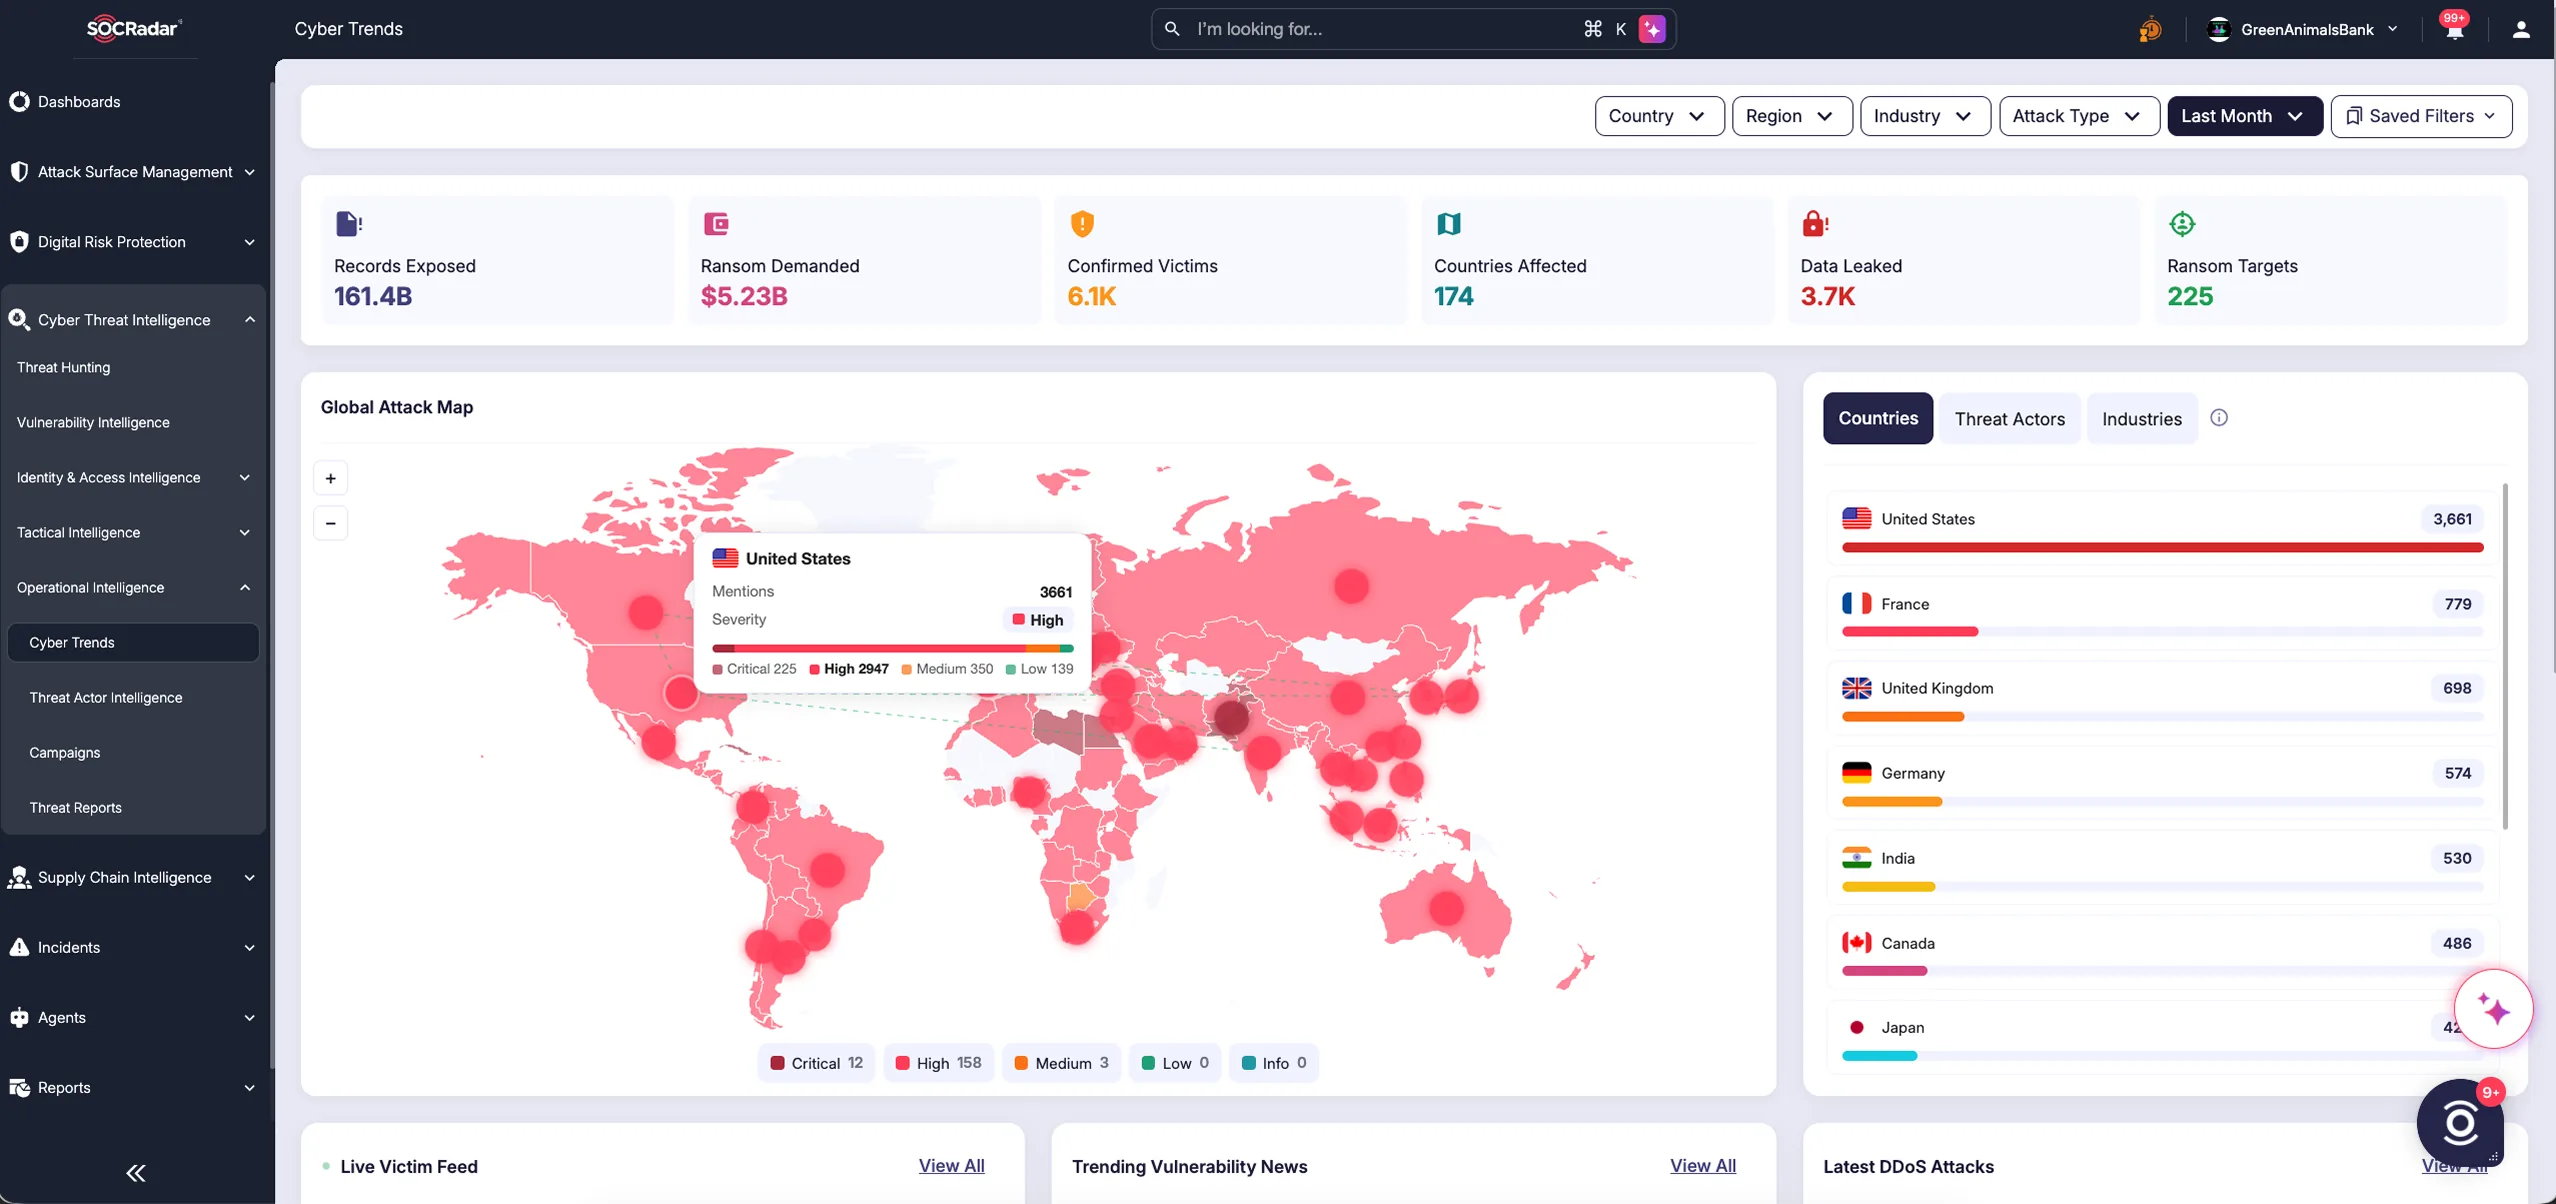
Advanced Dark Web Monitoring Module
Monitor criminal marketplaces, forums, and encrypted chat channels to surface stolen credentials, leaked data, and attacker chatter before it reaches your perimeter.
Explore Advanced Dark Web Monitoring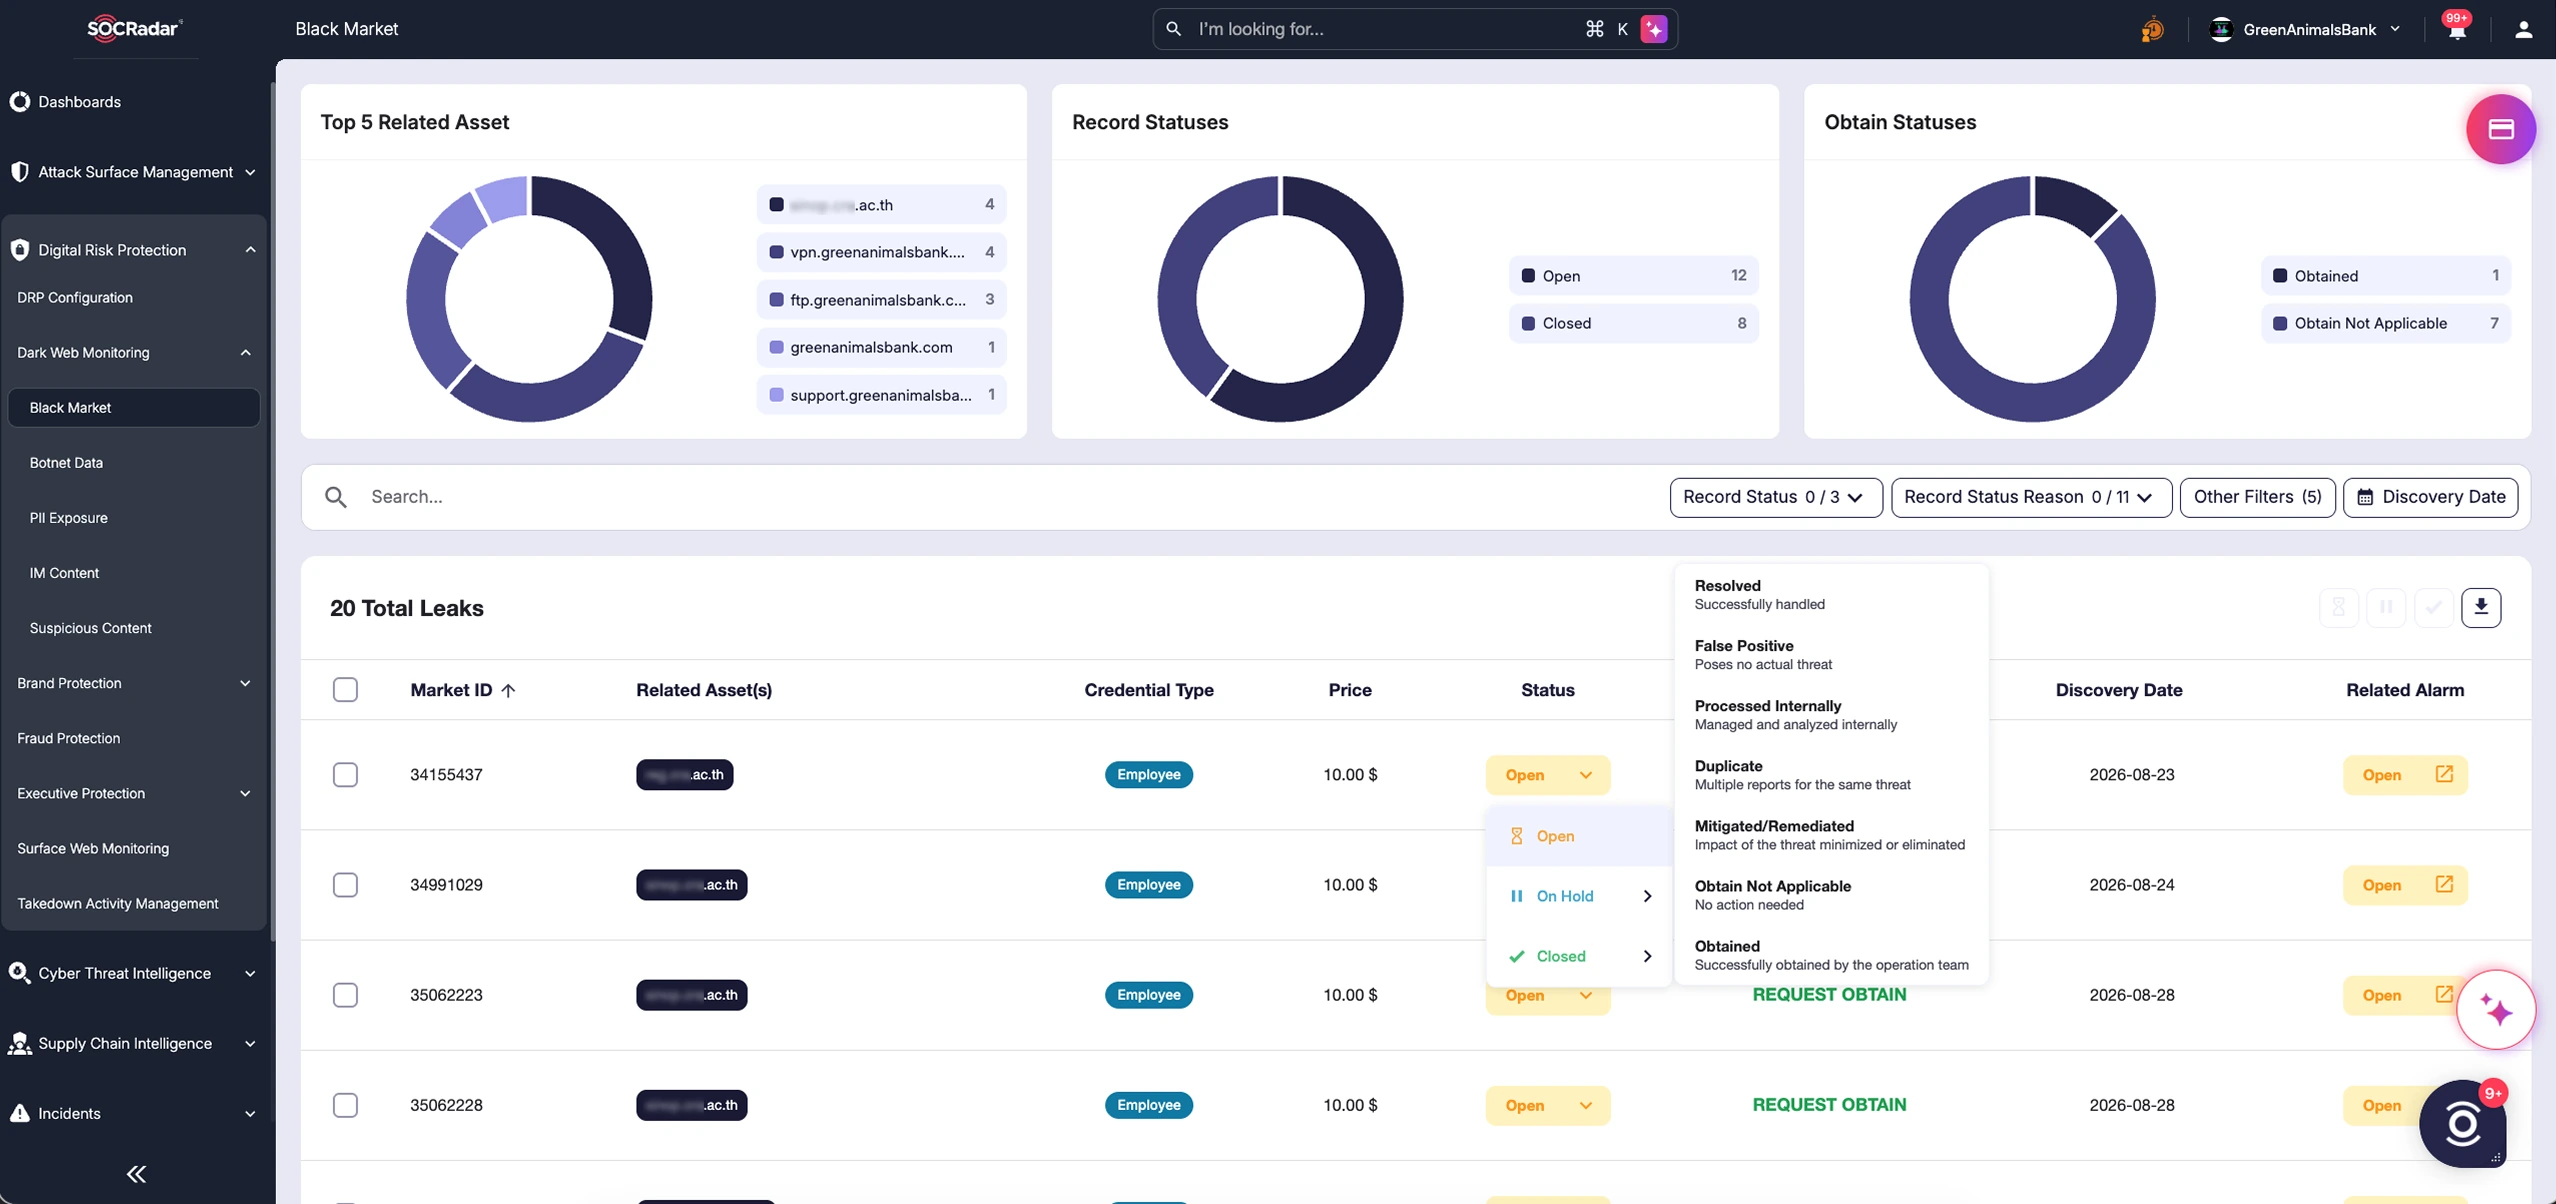
Attack Surface Management Module
Continuously discover, monitor, and reduce every exposed asset before attackers find it first.
Explore Attack Surface Management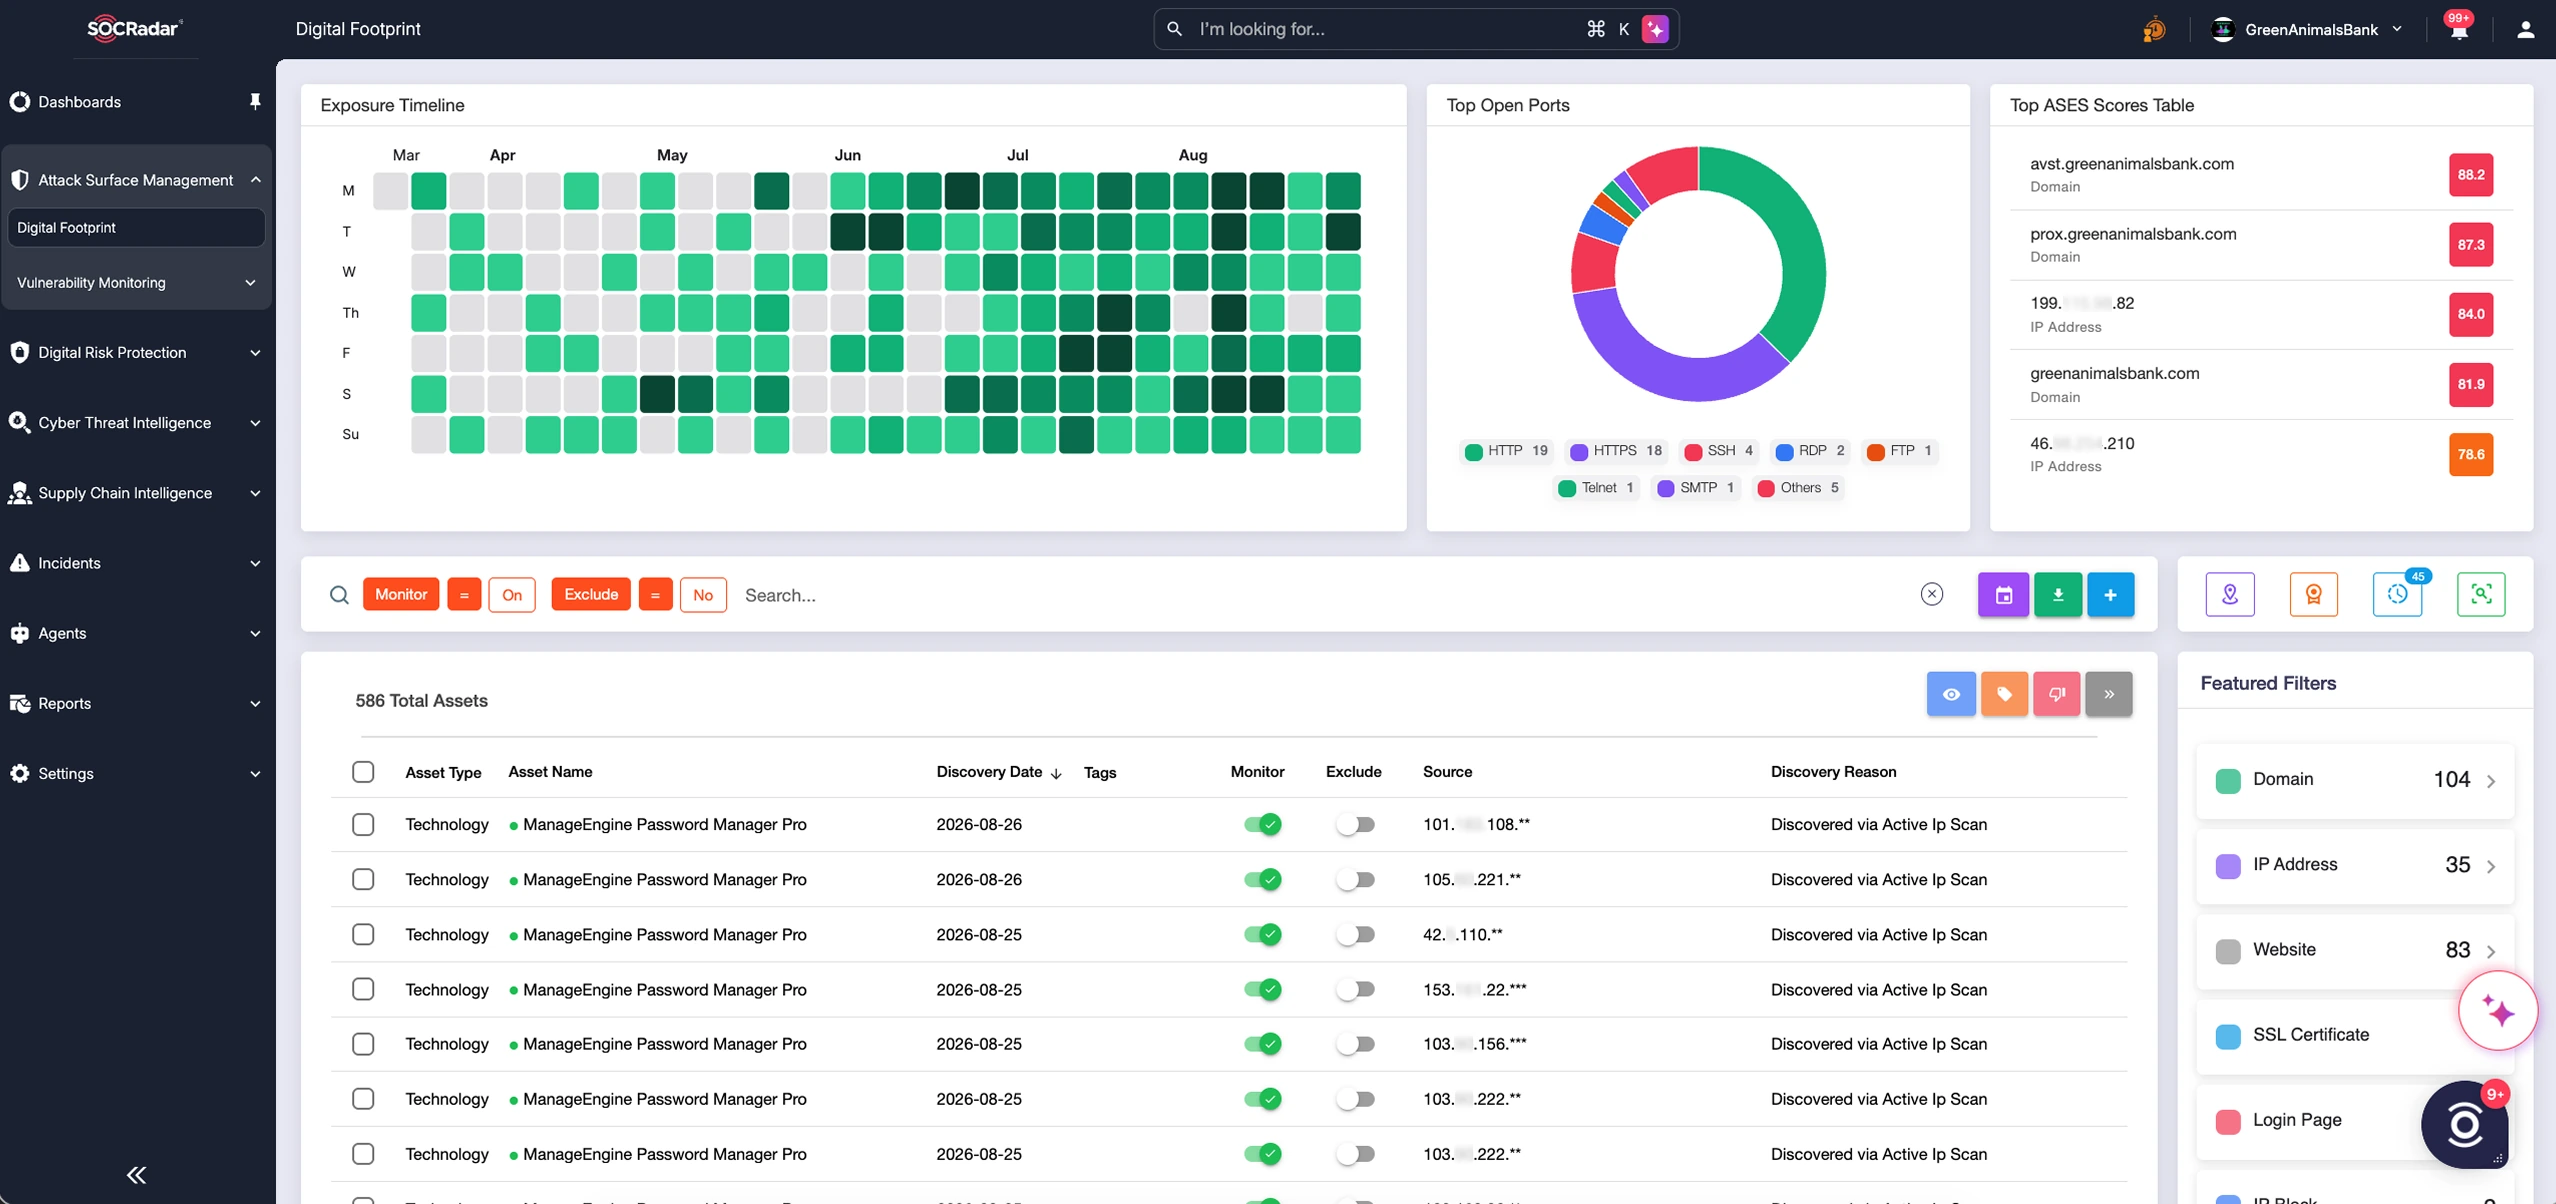
Brand Protection Module
Continuously monitor for impersonation, phishing, and brand abuse across the web, social media, and app stores, then take it down before it costs you customer trust.
Explore Brand Protection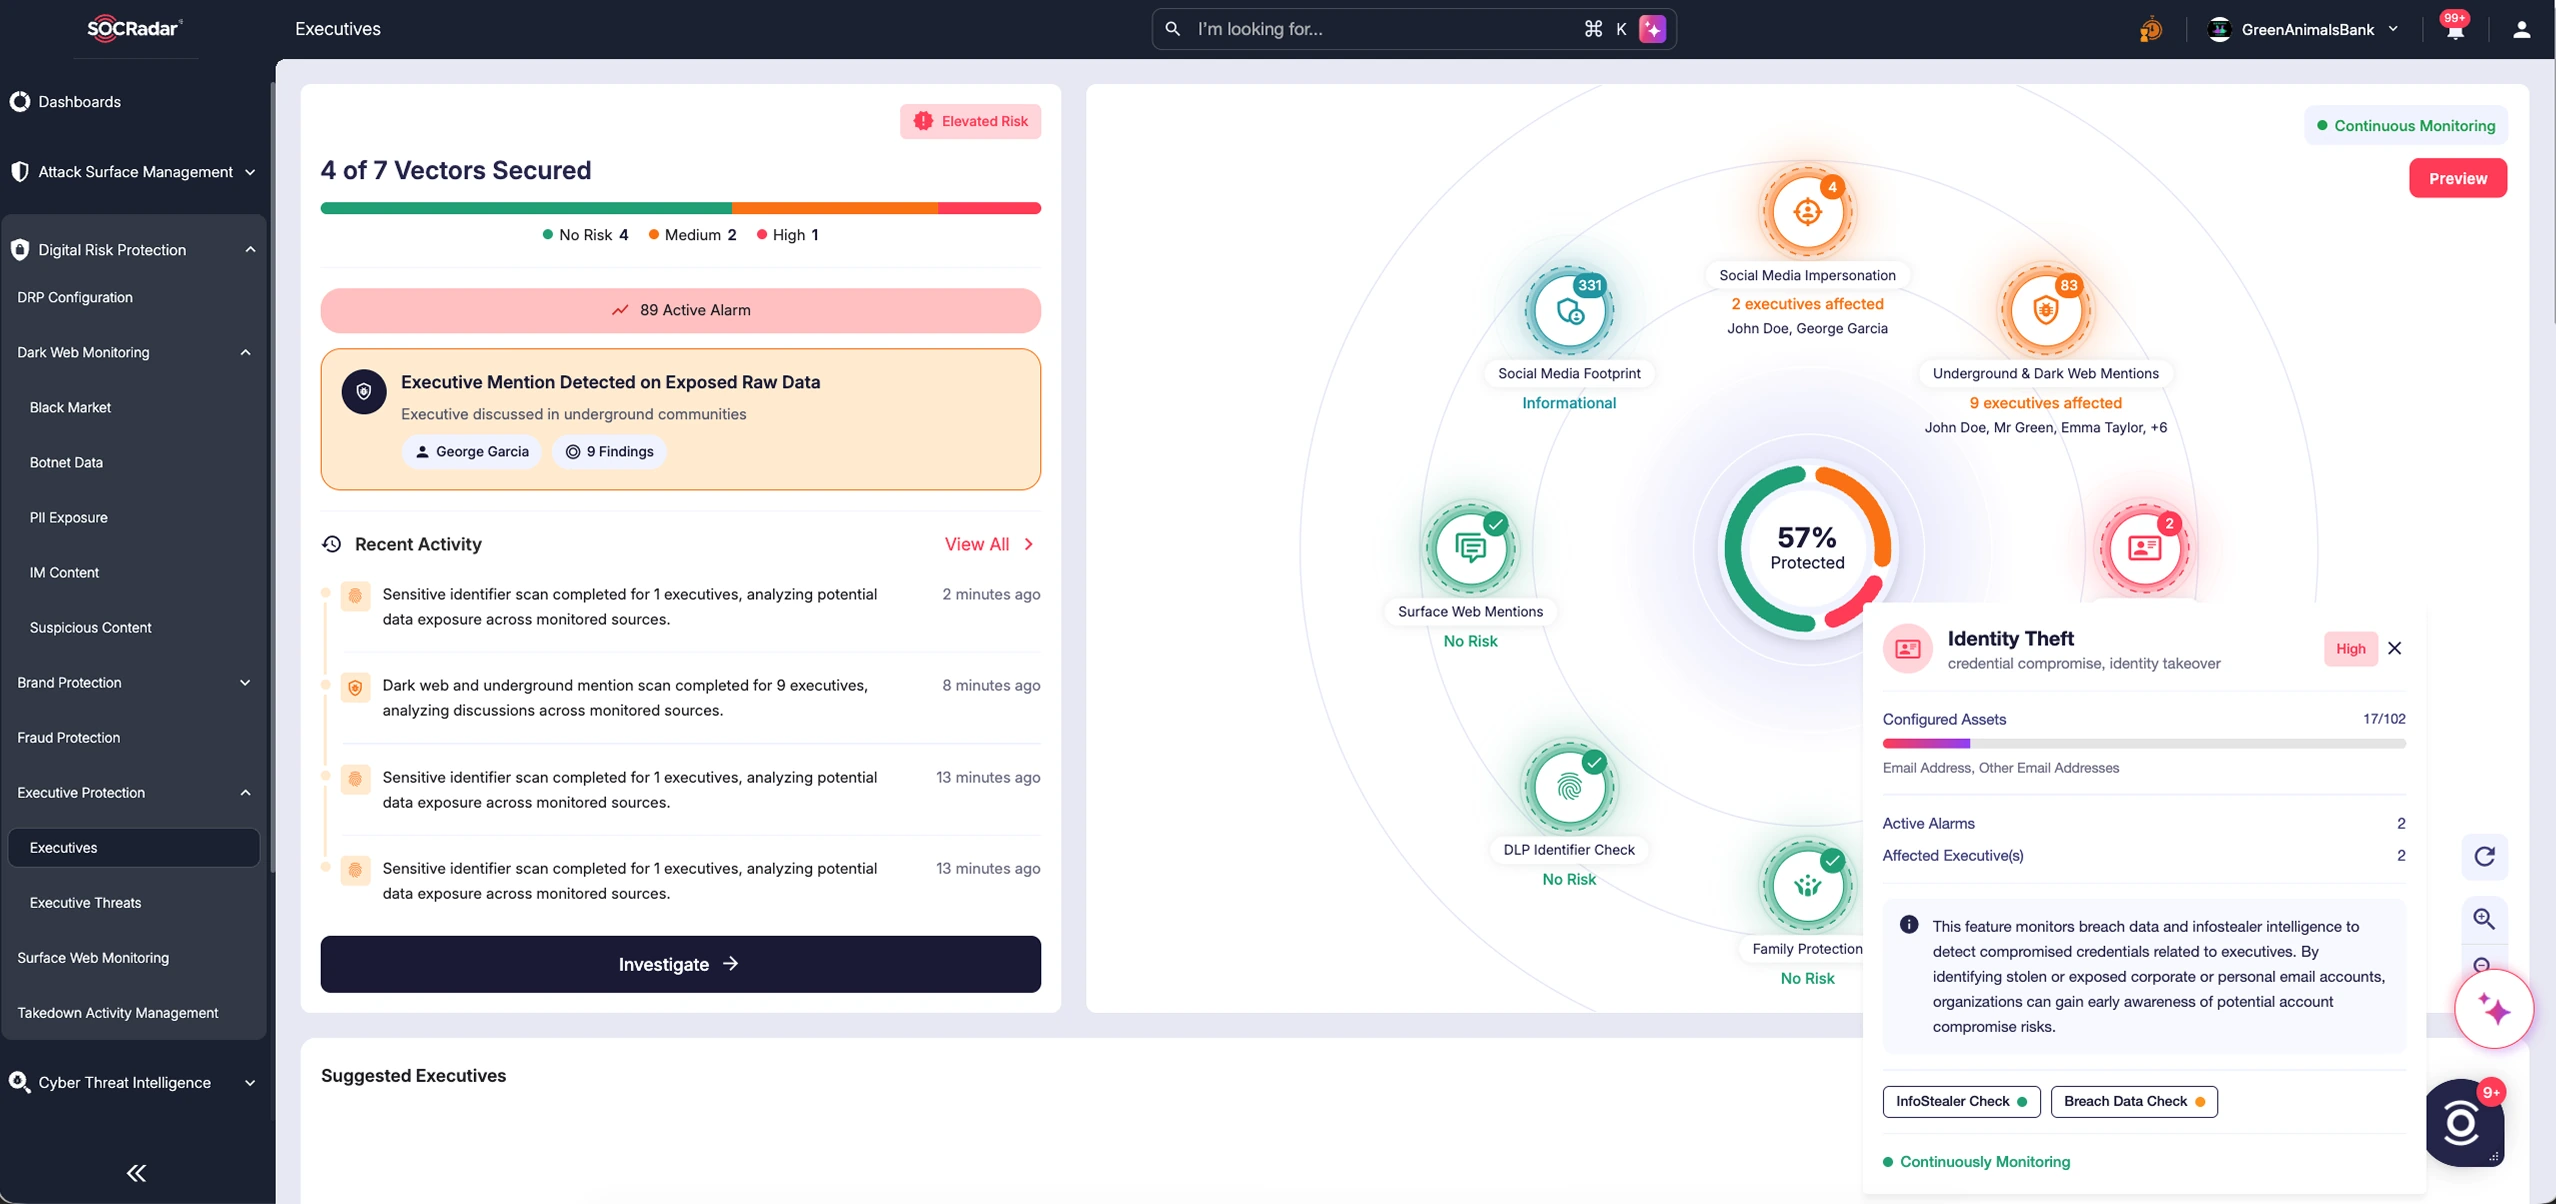
Supply Chain Intelligence Module
Actively assess the security posture of your continuously expanding supply network, so high-risk vendors surface before a breach reaches you.
Explore Supply Chain Intelligence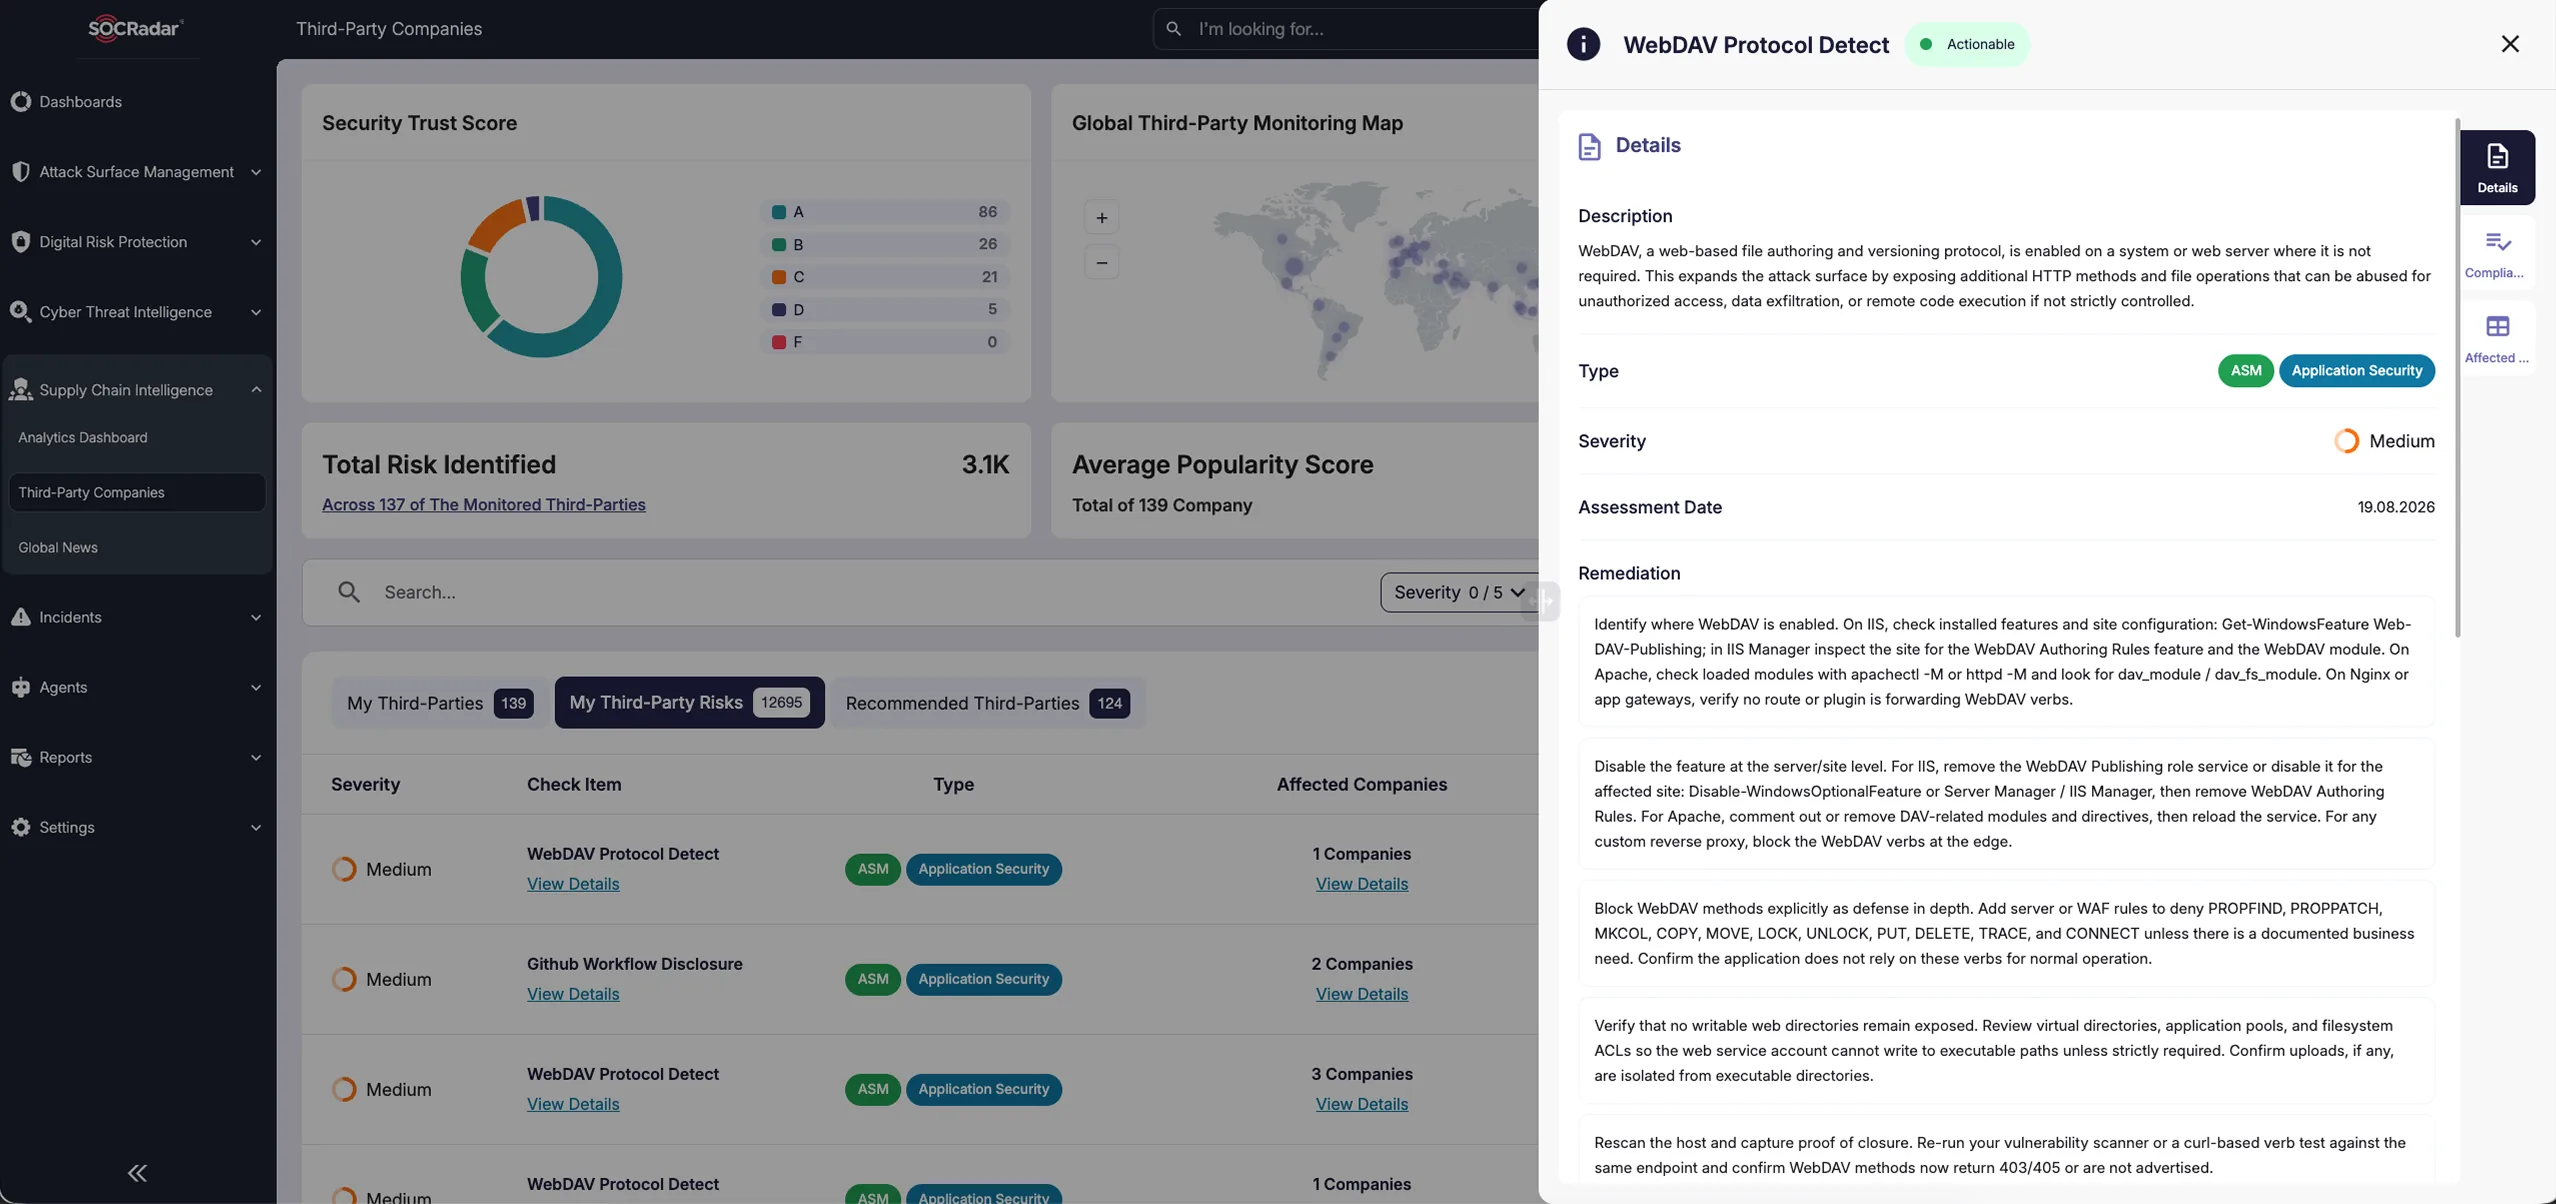
XTI Platform Overview
Intelligence built for action. From end-to-end.
The platform’s deep insights into the evolving threat landscape, with intelligence such as new vulnerabilities, attack methods, sectoral or regional cyber attack campaigns, supply chain attacks and threat actor groups, enables organizations to make informed decisions about security infrastructure, prioritize investments in security technologies.
- Collect & MonitorIngest intel from sources across the Surface, Deep, & Dark Web.
- Detect & AlertIdentify vulnerabilities, compromised credentials, phishing, etc.
- Analysis & ContextEliminate false positives and rank by criticality.
- Investigate & validateSearch and connect the dots with TTPs and automated enrichment.
- Action to RemediateTake down threats, recover data, and fix exposures.
Unified defense, from one codebase.
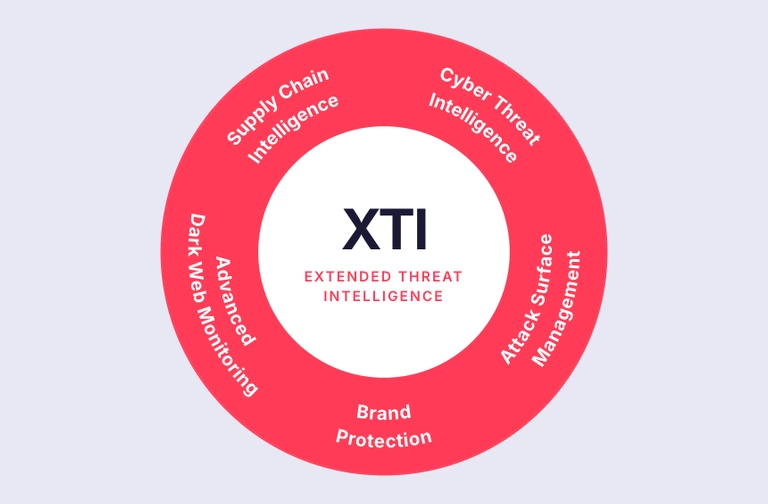
Every SOCRadar module runs on the same platform, so intelligence moves seamlessly between CTI, ASM, Dark Web Monitoring, Brand Protection, and Supply Chain Intelligence without disparate connectors or exports. Unified dashboards correlate findings across modules, and any alarm drills down to the case behind it in one click. Your team works from one login, one alarm queue, and one shared picture of external risk.
Modular & built for scale.
Start with the modules you need today and add more as your program matures, without re-platforming or retraining your team. The cloud-native SaaS platform requires no infrastructure and begins discovering your assets with no initial input. Enterprise controls like RBAC, SAML-based SSO, and audit trails come standard, and credit-based Advanced APIs scale with your data usage, not your seat count.
Less noise, faster response.
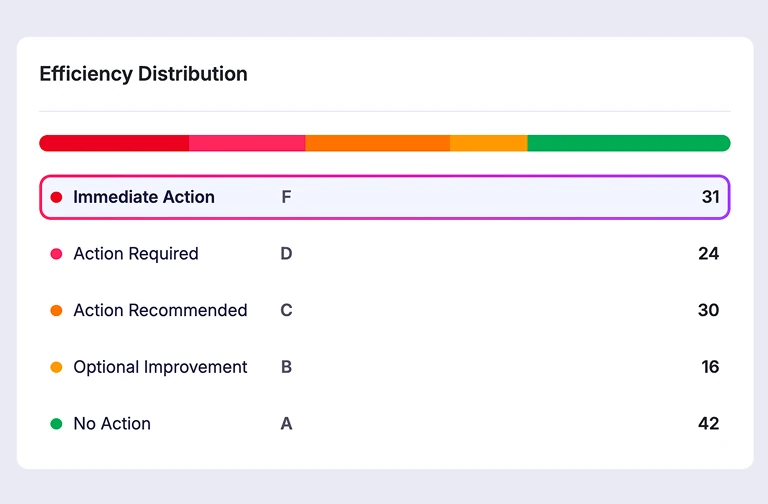
Every alert arrives enriched with the context your team needs to separate real threats from noise with greater accuracy. Analyst validation and proprietary risk scoring, built from dark web, social media, and EPSS data, push the exposures most likely to be exploited to the top of the queue. One click pivots any alarm into a full investigation, so your analysts move from signal to response faster and reduce mean time-to-respond (MTTR).
AI that drives swift & decisive action.
SOCRadar’s Agentic Threat Intelligence (ATI) gives your team a digital workforce of purpose-built AI agents, each specialized for a security job like alarm triage, IOC enrichment, or threat actor profiling. Hire agents from a growing marketplace and direct them through SOCRadar’s integrated CoPilot interface in plain language. They correlate data across every module using cross-functional tools, turning hours of manual investigation into a single query, while your analysts keep the final say.
Explore Agentic Threat Intelligence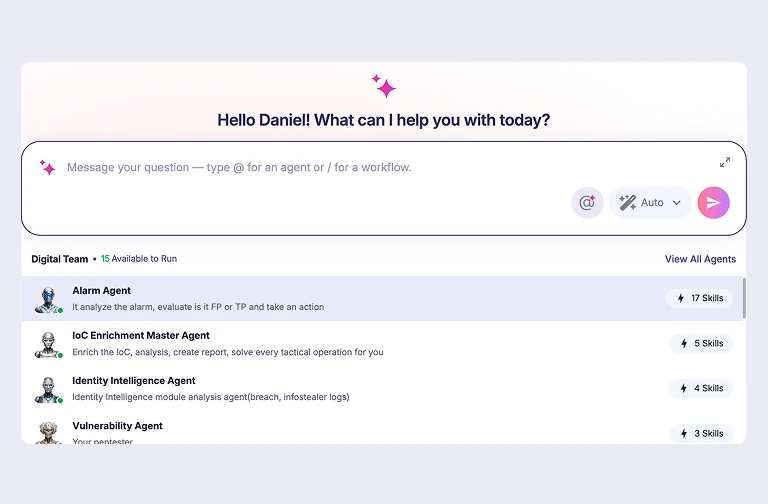
Integrated, one-click remediation.
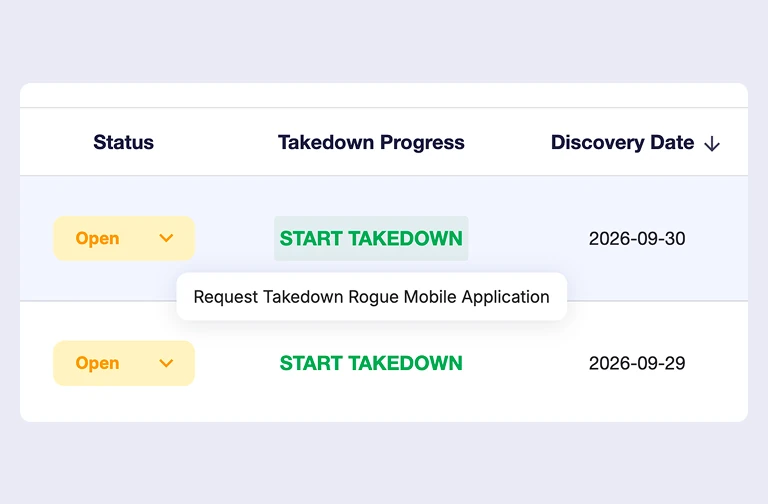
Move from alert to action without leaving the platform or rebuilding context in another tool. Submit managed takedowns for phishing domains, impersonating accounts, and rogue apps in one click, or revoke compromised sessions via a connected database tool like Entra ID. When exposed credentials show up in stealer logs for sale on dark web marketplaces, launch an integrated re-acquisition workflow in the platform to take the listing off the market and secure the data for investigation.
Platform Capabilities
Only the intelligence.
The platform’s deep insights into the evolving threat landscape, with intelligence such as new vulnerabilities, attack methods, sectoral or regional cyber attack campaigns, supply chain attacks and threat actor groups, enables organizations to make informed decisions about security infrastructure, prioritize investments in security technologies.
Integrations
SOCRadar XTI offers integrations with various product groups.
Scalable SaaS
As a SaaS and cloud base product, SOCRadar XTI allows users to seamlessly scale their software usage up or down based on their ever-changing needs.
Customizable Dashboard
With the customizable dashboard the users can easily manage alarms. Early warning system against cyber threats.
Early Warning System
SOCRadar XTI offers monitoring services for dark web and other sources for potential threats targeting organizations, detecting impersonating domains, tracking social media platforms for brand abuse alerting companies to potential threats before they could cause damage.
FAQ
Frequently Asked Questions
What is Extended Threat Intelligence (XTI)?
XTI unifies Cyber Threat Intelligence (CTI), Digital Risk Protection Services (DRPS), and External Attack Surface Management (EASM) in a single platform, giving security teams one unified view of external risk instead of managing separate tools for each capability.
What does "Extended" mean in Extended Threat Intelligence?
“Extended” refers to threat intelligence that goes beyond traditional indicator feeds, extending visibility into an organization’s attack surface, digital footprint, and dark web exposure, and correlating all of it together rather than treating each as a separate discipline.
Is XTI a SOCRadar-specific term, or an industry-wide category?
SOCRadar pioneered the Extended Threat Intelligence concept, combining External Attack Surface Management (EASM), Digital Risk Protection Services (DRPS), and Cyber Threat Intelligence (CTI) under one platform, capabilities that were traditionally sold and managed separately. While the term has since been adopted more broadly across the industry, SOCRadar originated the framing and continues to lead its development.
Why was the XTI concept created?
Security teams were managing EASM, DRPS, and CTI as disconnected point solutions, each with its own alerts, dashboards, and workflows. XTI was created to unify these into a single platform so external risk could be assessed and acted on as one coherent picture, rather than three separate ones.
What modules are included in XTI?
Core modules include Advanced Dark Web Monitoring, Brand Protection, Attack Surface Management, Supply Chain Intelligence, and Cyber Threat Intelligence.
Who is XTI designed for?
Security teams look to see what attackers see by combining external attack surface, digital footprint, dark web exposure, and supply chain visibility into one workflow, particularly useful for security teams juggling multiple point tools today.
How does XTI evolve as threats change?
SOCRadar is extending the concept further through Agentic Threat Intelligence (ATI), shifting organizations from passively investigating threat feeds toward AI-powered agents that track threats, assess context, and trigger the right response. This reflects XTI’s design as a continuously evolving framework, not a fixed feature set.
SOCRadar® Cyber Intelligence Inc. | Extended Threat Intelligence