Cyber Threat Intelligence
Your dynamic shield against cyber adversaries.
Rapid, contextual insights from a single, searchable threat intelligence database, built for swift response.
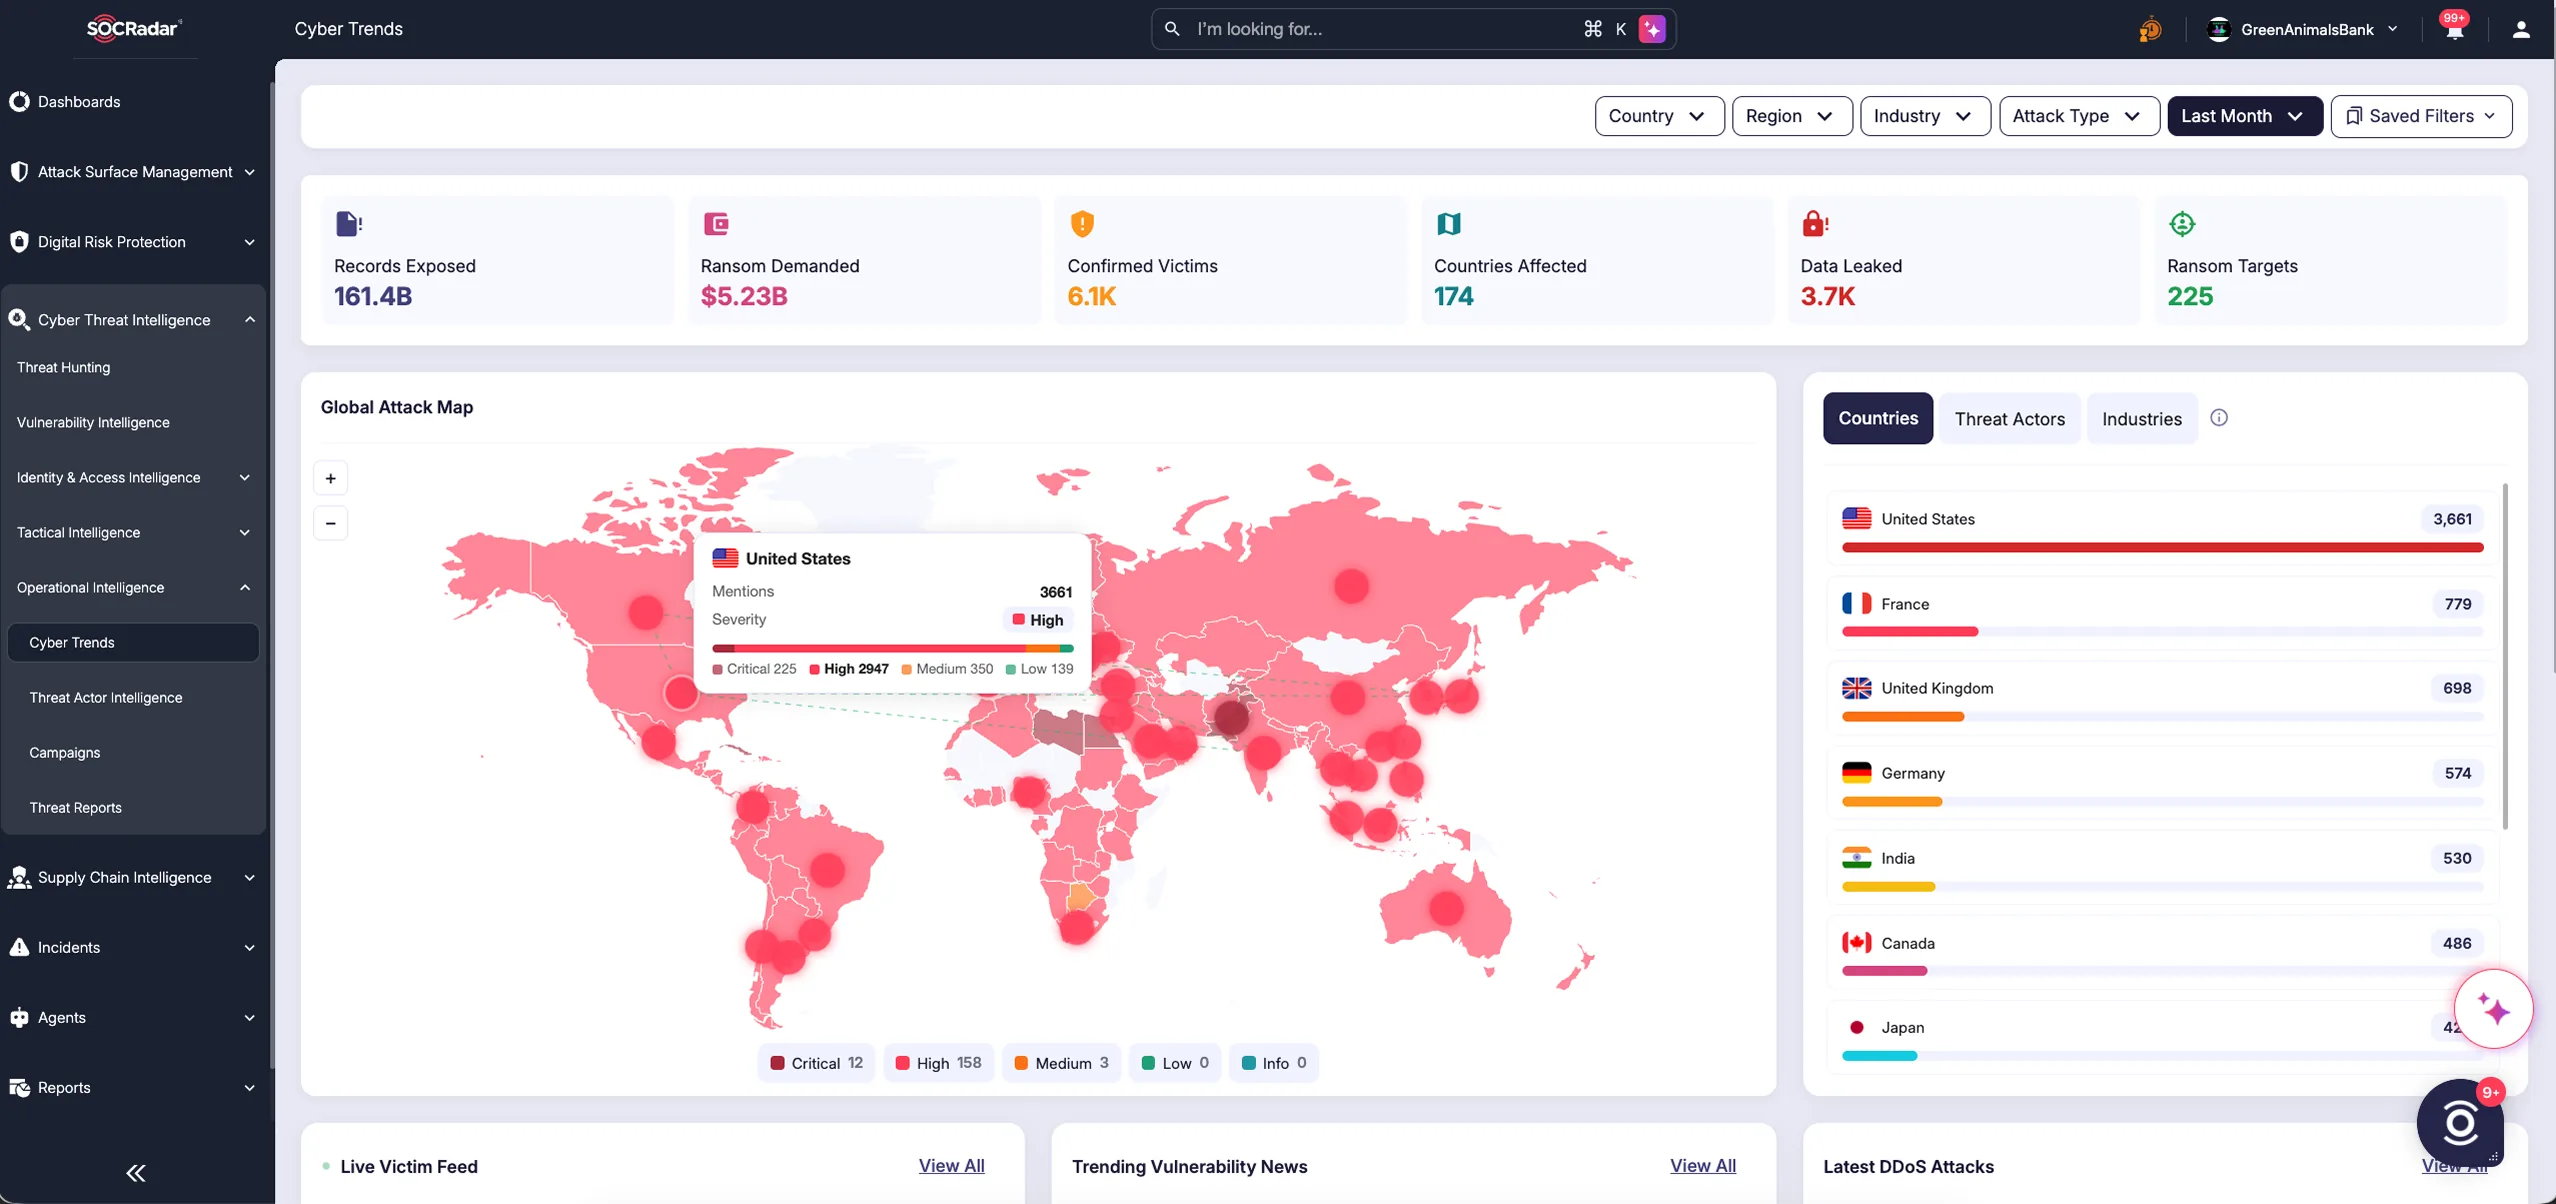
Move from reactive to proactive, before the alert fires.
Roughly 50% of daily alerts and tasks go unaddressed by CTI analysts. SOCRadar's CTI module cuts through that backlog with correlated intelligence across vulnerabilities, identities, tactics, and adversary operations, so your team acts on signal, not noise.
Investigate across thousands of data feeds & sources.
Search IPs, domains, and keywords across dark web markets, code repositories, and messaging platforms from a single environment.
Act on what’s at risk.
Every alert includes risk context from correlated intelligence and clear investigation pivot points, so your team knows exactly what to do next.
Track adversaries by name.
Profile threat actors and ransomware groups targeting your exact sector, mapped to MITRE ATT&CK.
Use Cases
Turn global threat and adversary data into direct, actionable defense.
Threat Hunting
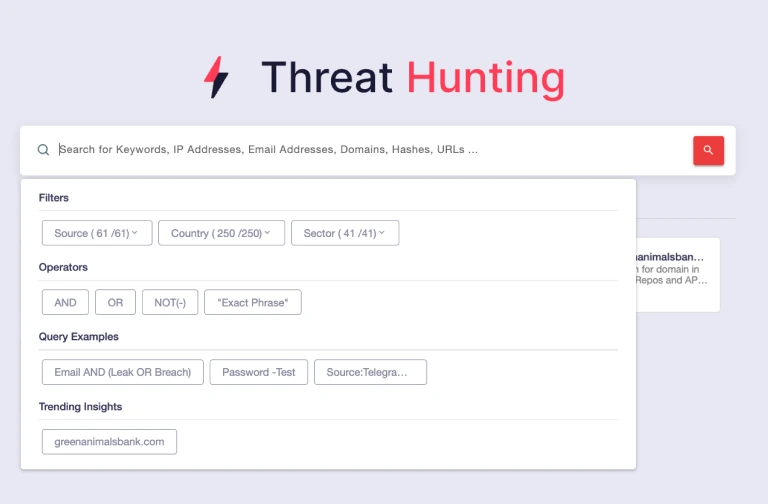
Search for any indicator, IP, domain, email, hash, or keyword, across 50+ sources including dark web markets and code repositories.
APT & Threat Actor Tracking
Track the specific threat actors and ransomware groups targeting your exact sector. Interconnected profiles combine historical behavior, TTPs, and detection rules, so your team can prepare defenses in advance.
Vulnerability Intelligence
Move past generic CVE lists. Vulnerability Intelligence flags what’s actively being exploited, pairs CVSS with a proprietary risk score, and surfaces PoCs and IOCs tied to each finding.
Identity & Access Intelligence
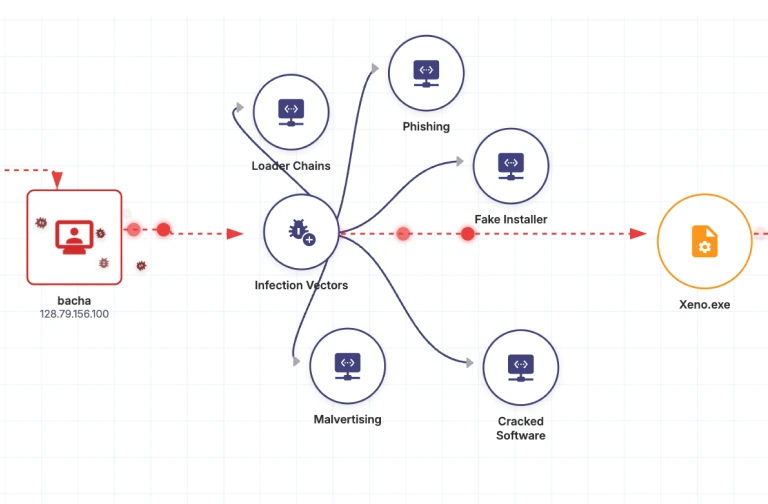
Detect exposed accounts and credential leaks across breaches, infostealer logs, and dark web listings. Visual attack flows reconstruct the infection path from entry point to endpoint.
Geographic Threats
Stay informed on localized cyber campaigns and regional geopolitical tensions that could disrupt your offices or supply chain, filtered by country and industry.
Breach Monitoring
Continuously monitor for exposure of your corporate or third-party data across the surface, deep, and dark web, so your team can contain a leak before it spreads.
Malware Analysis
Static and dynamic malware analysis surfaces evasive threats and maps observed behaviors directly to MITRE ATT&CK.
Key Features
See it all from a single search.
Conduct proactive, language-agnostic investigations across a unified platform spanning 50+ threat intelligence sources.
- Investigate global and region-specific data across messaging apps, social media, dark web markets, and code repositories
- Search any indicator, including IPs, domains, and keywords, to retrieve contextual metadata like JARM hashes, WHOIS, and DNS records
- Prioritize high-risk results with severity-based filtering, group-based source management, and logical search operators
- Save personalized search parameters for automated, recurring hunts
- Access 35,000+ YARA, Sigma, SNORT, and SURICATA threat hunting rules
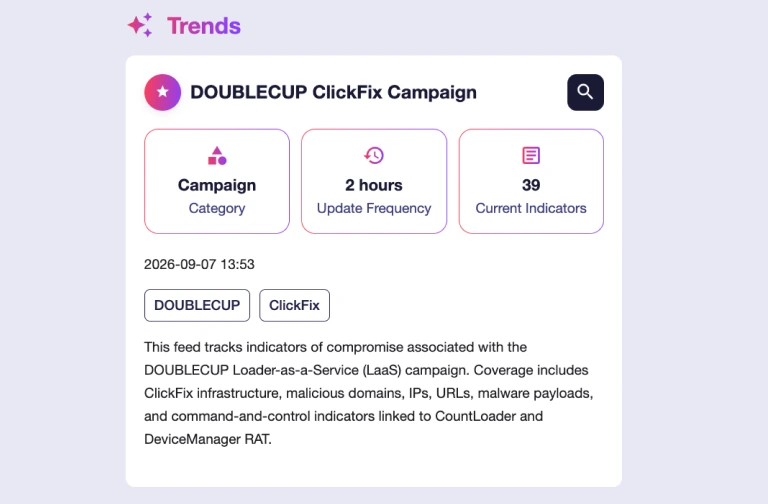
Turn thousands of daily IOCs into one clean feed.
Aggregate and correlate indicators from 130+ OSINT, proprietary, and commercial sources, then push them straight into your defense stack.
- Access 130+ threat feeds delivering tens of thousands of new IOCs daily
- Export curated feeds to SIEM, SOAR, or firewalls via API, MISP, or TAXII server
- Build customized feed collections filtered by country, IOC type, and risk score
- Correlate suspicious IPs, domains, and hashes with known threat actors and malware infrastructure
- Visualize IOC relationships and run historical analysis to accelerate triage
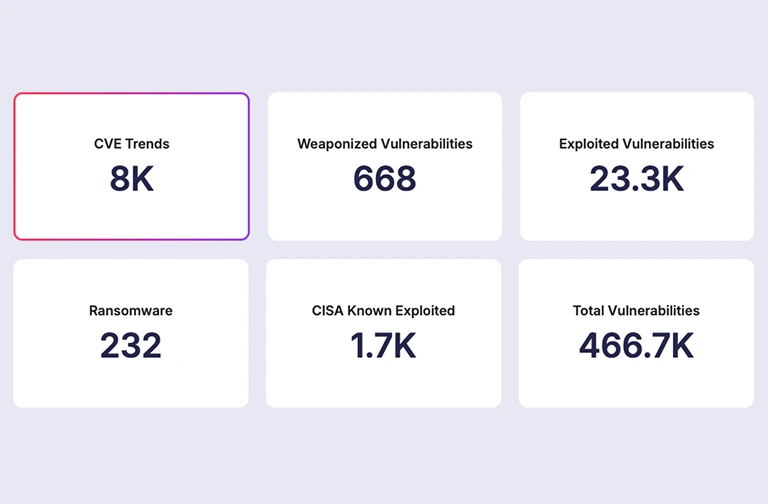
Find and mitigate vulnerability risk.
Get proactive alerts on critical vulnerabilities and exploits affecting your public-facing technologies.
- Subscribe to specific vendors, products, and versions for immediate zero-day notifications
- Review CVSS breakdowns, threat actor mapping, public PoCs, and associated IOCs
- Estimate real-world exploitation likelihood with a proprietary risk score built on dark web, social media, and EPSS data
- Automatically tag vulnerabilities actively exploited or used in ransomware campaigns
Detect and investigate identity vectors before they’re breached.
Detect, visualize, and neutralize compromised credential risk across breaches, infostealer logs, and underground markets.
- Run smart searches by domain, URL, or username across leaks, cookie caches, and dark web listings
- Map affected business functions, third-party SaaS risk, and lateral movement paths
- Reconstruct end-to-end infection paths with interactive attack flow visualization
- Generate AI-powered natural language summaries with step-by-step remediation guidance
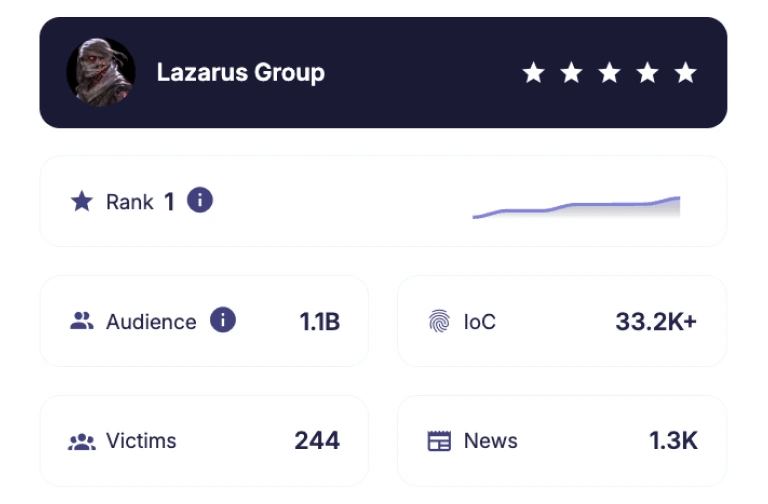
Know your adversary by name.
Get real-time, tailored insight into the ransomware groups and threat actor tactics most likely to target your organization.
- Track threat actors and ransomware groups by industry, country, and organization
- Access adversary profiles enriched with TTPs, aliases, and detection rules
- Prioritize using Customer Impact Score, Threat Meter, and Sophistication Level metrics
- Map campaign financial footprints, including blockchain transaction history
- Receive automated daily digests and AI-generated remediation summaries
- Get structured, traceable hacktivist threat intelligence
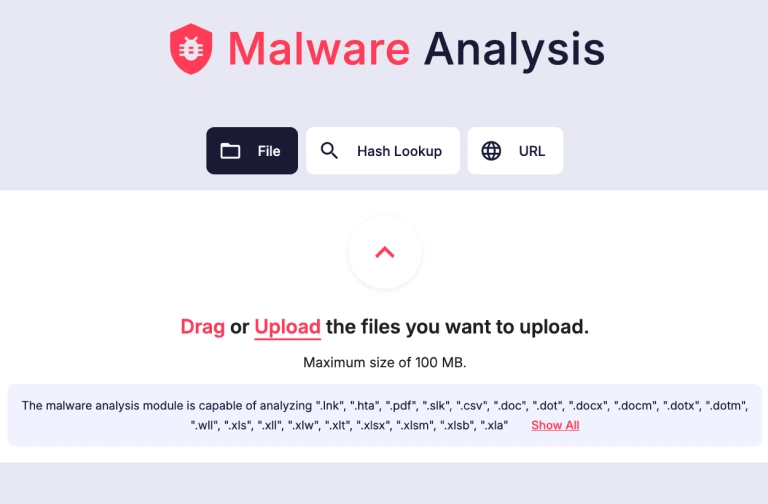
Analyze suspicious malware files without slowing down.
Combine static and sandboxed dynamic analysis to classify malicious files and understand attacker intent.
- Inspect documents, scripts, QR codes, and archives with AMSI, YARA, and 40+ detection rules
- Execute files in a controlled sandbox to monitor behavioral execution chains and C2 traffic
- Surface evasive threats missed by static triage alone
- Map observed behaviors directly to MITRE ATT&CK techniques and known malware families
Additional Capabilities
-
In-Application Threat Hunting Search & Browser
Query 50+ sources for indicators without leaving the platform.
-
GitHub and Bucket Leak Detection
Catch exposed secrets in code repositories and cloud storage before attackers do.
-
Bi-Directional API Connectivity
Push curated intel into your SIEM, SOAR, or TIP, and pull enriched context back.
What our customers say.
Key Benefits
Benefits of Cyber Threat Intelligence
Access contextual, correlated intelligence that turns analyst alert backlog into prioritized action.
Correlate raw feeds against your specific exposure so analysts investigate what matters, not everything.
Profile the threat actors and ransomware groups actively targeting your sector.
Combine dark web, social, and EPSS signals into one proprietary risk score.
Unified threat actor, IOC, and campaign context replaces arduous, manual research.
Modules
Cyber Threat Intelligence Modules
Explore the five modules that make up SOCRadar Cyber Threat Intelligence.
Detect advanced threats or malicious activities with proactive threat hunting.
Explore the moduleEnriched IOC feeds, TTPs and detection-ready context, delivered straight into your security stack.
Explore the moduleTrack campaigns and threat actor activity as it unfolds, mapped to your sector and region.
Explore the moduleUnderstand how credentials were stolen, what data was exposed, and what it puts at risk.
Explore the moduleImprove your security vigilance with Vulnerability Intelligence, offering advanced alerts for critical vulnerabilities.
Explore the moduleFAQ
Frequently Asked Questions
What is Cyber Threat Intelligence?
According to Gartner, “threat intelligence is evidence-based knowledge, including context, mechanism, indicators, implications, and actionable advice, about an existing or emerging menace or hazard to assets that can be used to inform decisions regarding the subject’s response to that menace or hazard”.
EC Council’s definition is very similar, “threat intelligence is the analysis of data using tools and techniques to generate meaningful information about existing or emerging threats targeting the organization that helps mitigate risks”.
What is the purpose of Cyber Threat Intelligence (CTI)?
Cyber threat intelligence aims to help institutions and organizations understand the risks of cyber attacks or cyber threats. These attacks can range from zero-day attacks, crypto viruses, APTs (Advanced Persistent Threats), botnets, or exploits. These threats are reported with the intelligence activities after being reviewed by CTI analysts to provide special protection methods to assist in an active defense in your organization.
Why do you need Cyber Threat Intelligence?
The skilled, well-funded, well-organized, and highly-sophisticated cyber attackers use techniques that reveal security strategies to the technology alone. To develop a defense strategy against attackers, organizations need to know how hackers operate, how they function, and what techniques they use.
Cyber-threat intelligence allows companies to identify the dynamics and consequences of risks, improve security plans and structures, and reduce their attack potential to minimize damage and defend their network.
Why is Cyber Threat Intelligence so important?
CTI can identify and analyze cyber threats against your business. Therefore, CTI can help you to:
- Focus on actionable alarms; the legacy threat intelligence solution provided only feeds and (Indicator of Compromise) IOCs, which were not actionable. But organizations started to need more and more of the latest intelligence about them. With real-time intelligence on threat actors, botnets, malware, and data from the dark web and the deep internet, organizations need to detect phishing domains targeting their customers.
- Collect, Verify, and Prioritize External Threats; CTI can deliver the hard work for your business with enriched intelligence that allows you to apply smarter defense and improvement processes.
- Detect Forgotten Assets and Monitor Attack Surface in Real-time; CTI can determine the blind spots by following the changing attack surface all the time.
- Prevent Data Loss; by using CTI, cyber threats can be detected, and security breaches can be prevented from disclosing confidential information.
What are the types of Cyber Threat Intelligence (CTI)?
Various threatening knowledge and theoretical approaches are useful at various businesses’ levels. The four categories of cyber threat intelligence have to do with different objectives:
- Strategic Cyber Threat Intelligence; It utilizes comprehensive pattern and emerging risk analysis to provide an outline of future cyber-attack implications.
- Operational Cyber Threat Intelligence; It is mainly used to make resource management decisions regarding actual and potential risks, historical resources, affiliations, and motives of threat actors.
- Tactical Cyber Threat Intelligence; Primarily, its main target is a technically trained audience and allows them to learn more specific details on threat actors’ tactics, techniques, and procedures (TTPs).
- Technical Cyber Threat Intelligence; It focuses on the technological details suggesting a cyber-security threat, such as phishing email lines or malicious URLs.
What are the differences between "information" and "intelligence"?
| Information | Intelligence |
|---|---|
| Unfiltered and raw data | Processed and sorted data |
| Not evaluated | Evaluated by Threat Intelligence Analysts |
| Too much-aggregated data | Only useful data |
| Not actionable | Actionable |
| Disconnected, incomplete, irrelevant | Connected, completed, and relevant |
What are the differences between Cyber Threat Intelligence (CTI) and Cyber Intelligence (CI)?
Usually, cyber threat intelligence and cyber intelligence terms are used for the same meaning. But in theory, the two terms have different contexts.
CTI is the collection and revealing of threats that may harm business elements and security at any level to institutions and organizations. It is a type of intelligence that enables early measures to be taken by detecting the goals, methods, or types of attacks of the attackers as a result of analyzing the data collected and enriched from electronic media through a process.
CTI provides information on malicious actors, their tools, their infrastructure, and their methods for;
- Identifying types of attacks,
- Defining, guiding, and prioritizing operational requirements,
- Understanding threat actor capability, tactics, techniques, and procedures,
- Deploying detection systems,
- Developing defense strategies.
Cyber intelligence (CI) translates the data obtained from the attackers’ networks into an operative report through “standard intelligence approaches.”
As can be understood from the definitions, while CTI focuses information on cyber threats, CI focuses on useful Intel from the Internet.
Experience the power of comprehensive cybersecurity firsthand.
See SOCRadar in action. Join 30,000+ security professionals who trust SOCRadar to protect their organizations.