| Affected Versions | Fixed Version |
|---|---|
| 18.1.6 through before 19.2.4 | 19.2.4 or later |
| 19.3 through before 19.3.2 | 19.3.2 or later |
| 19.4 through before 19.4.1 | 19.4.1 or later |

Oct 05, 2026
4 Mins Read

Summarize with:
CVE-2026-90970: GitLab AI Gateway RCE
GitLab has patched CVE-2026-90970, a critical vulnerability in the Self-Hosted AI Gateway that can allow an authenticated user with Duo Agent Platform access to execute arbitrary commands on the gateway.
The flaw carries a CVSS 3.1 score of 9.9. GitLab strongly recommends that affected Self-Hosted AI Gateway customers upgrade to 19.2.4, 19.3.2, or 19.4.1 as soon as possible. Active exploitation has not been confirmed.
What Is CVE-2026-90970?
CVE-2026-90970 is a template engine vulnerability classified as CWE-1336: Improper Neutralization of Special Elements Used in a Template Engine.
Under certain conditions, an authenticated user with access to the Duo Agent Platform can submit a specially crafted flow configuration that escapes the prompt-template sandbox and results in arbitrary command execution on the AI Gateway.
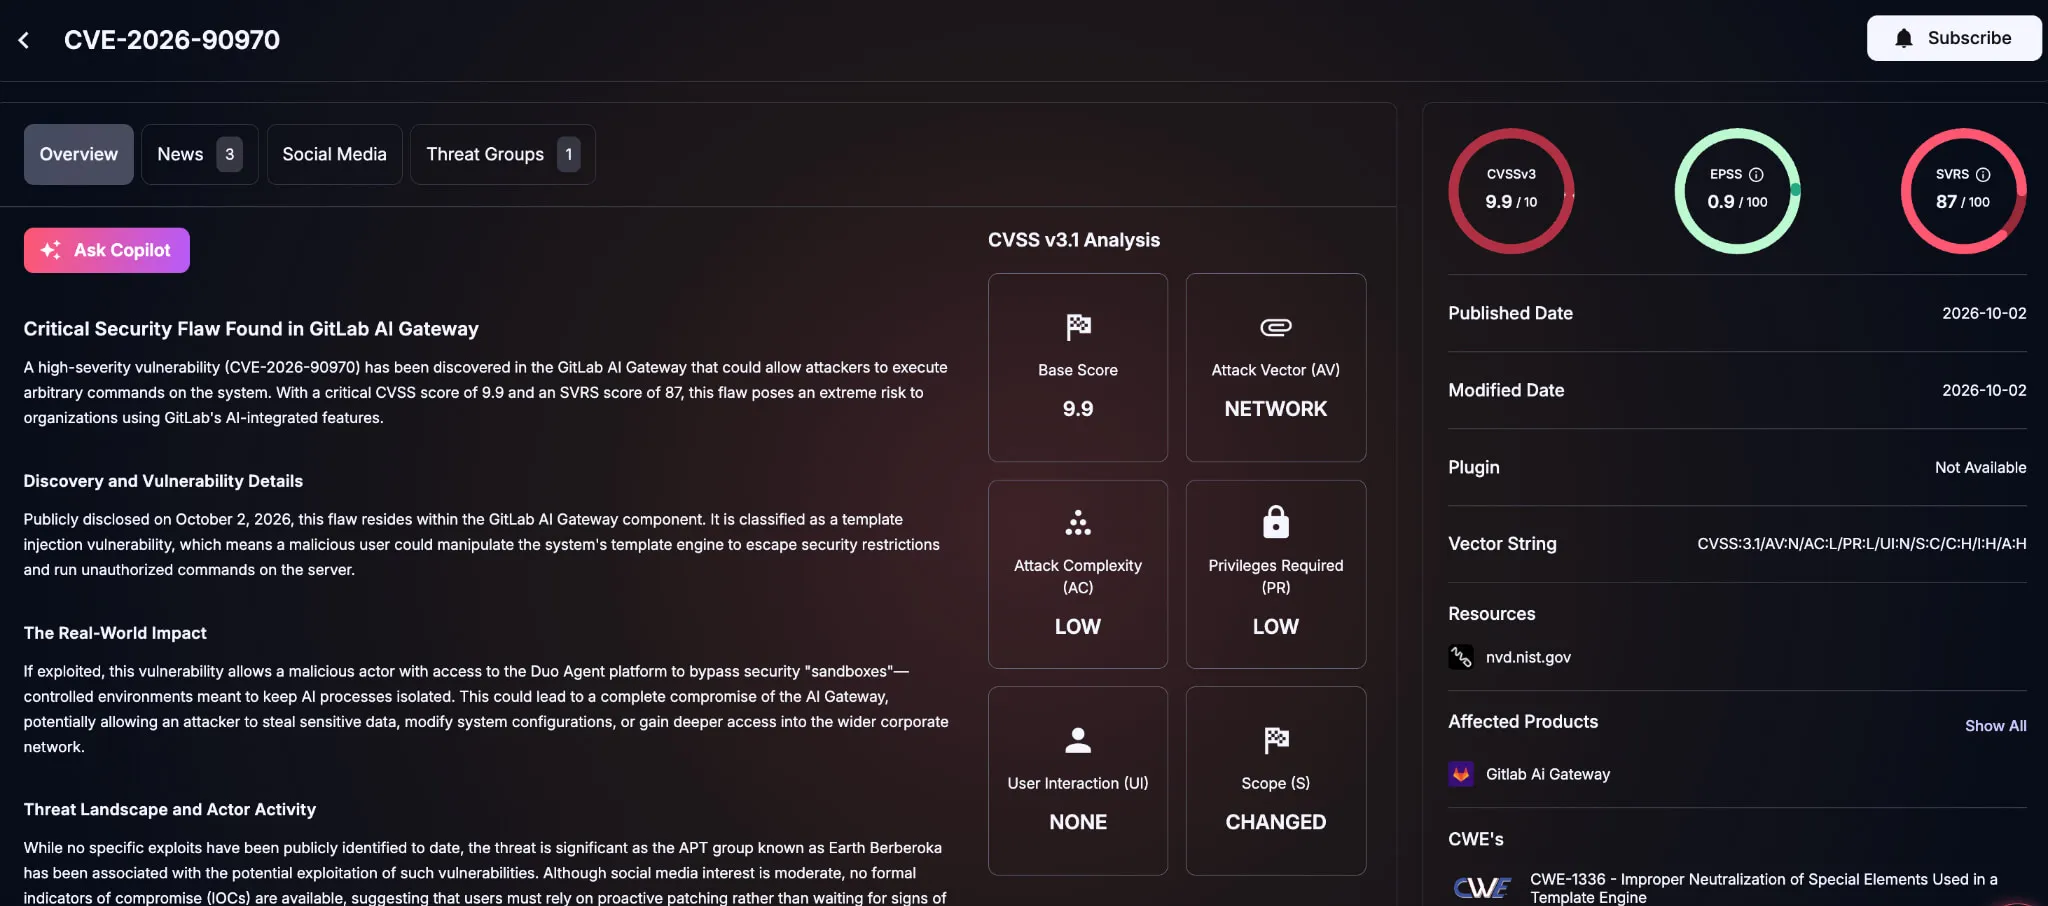
GitLab assigned the following CVSS vector:
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H
This reflects network reachability, low attack complexity, low required privileges, no user interaction, and potentially high confidentiality, integrity, and availability impacts.
GitLab has not publicly disclosed the exploit syntax, payload, or detailed code path involved.
Which GitLab AI Gateway Versions Are Affected?
The vulnerability affects these Self-Hosted AI Gateway releases:
Organizations operating versions below the 19.2 branch should move to an applicable fixed release because GitLab does not list a patched 18.x, 19.0, or 19.1 build.
The AI Gateway can be deployed separately from the main GitLab application, so administrators should verify the gateway’s container image or Helm deployment rather than relying only on the GitLab application version.
GitLab states that a fix has already been deployed to GitLab-hosted AI Gateways. GitLab.com, GitLab Dedicated, and Self-Managed customers using a GitLab-hosted gateway therefore do not need to take action for this vulnerability.
Why Is CVE-2026-90970 Critical?
The AI Gateway connects GitLab’s AI functionality with models and agentic workflows. In Self-Hosted environments, its runtime may also have access to internal services, credentials, mounted files, or model provider resources.
Successful exploitation provides arbitrary command execution on the gateway. What an attacker could do afterward depends on the gateway’s runtime permissions, network access, mounted resources, and available secrets.
The vulnerability does not mean that every GitLab user can compromise the gateway. The attacker must be authenticated and have access to the relevant Duo Agent Platform functionality.
Is CVE-2026-90970 Being Exploited?
No confirmed exploitation has been identified as of October 5, 2026.
GitLab’s advisory does not report exploitation in the wild, and CVE-2026-90970 is not currently listed in CISA’s Known Exploited Vulnerabilities catalog. Current public vulnerability records likewise show no evidence of active exploitation.
Track CVE-2026-90970 with SOCRadar
CVE-2026-90970 has no confirmed exploitation yet, but the combination of a public CVSS 9.9 rating and a Self-Hosted AI Gateway attack surface makes tracking PoC developments and exploitation signals the practical next step.
Powered by SOCRadar’s Cyber Threat Intelligence module, Vulnerability Intelligence helps teams follow severity, affected versions, exploit developments, and changes in exploitation status. It can help manage internal asset and deployment inventories by enabling your team to monitor whether new PoCs, threat activity, or remediation information emerges while patching progresses.
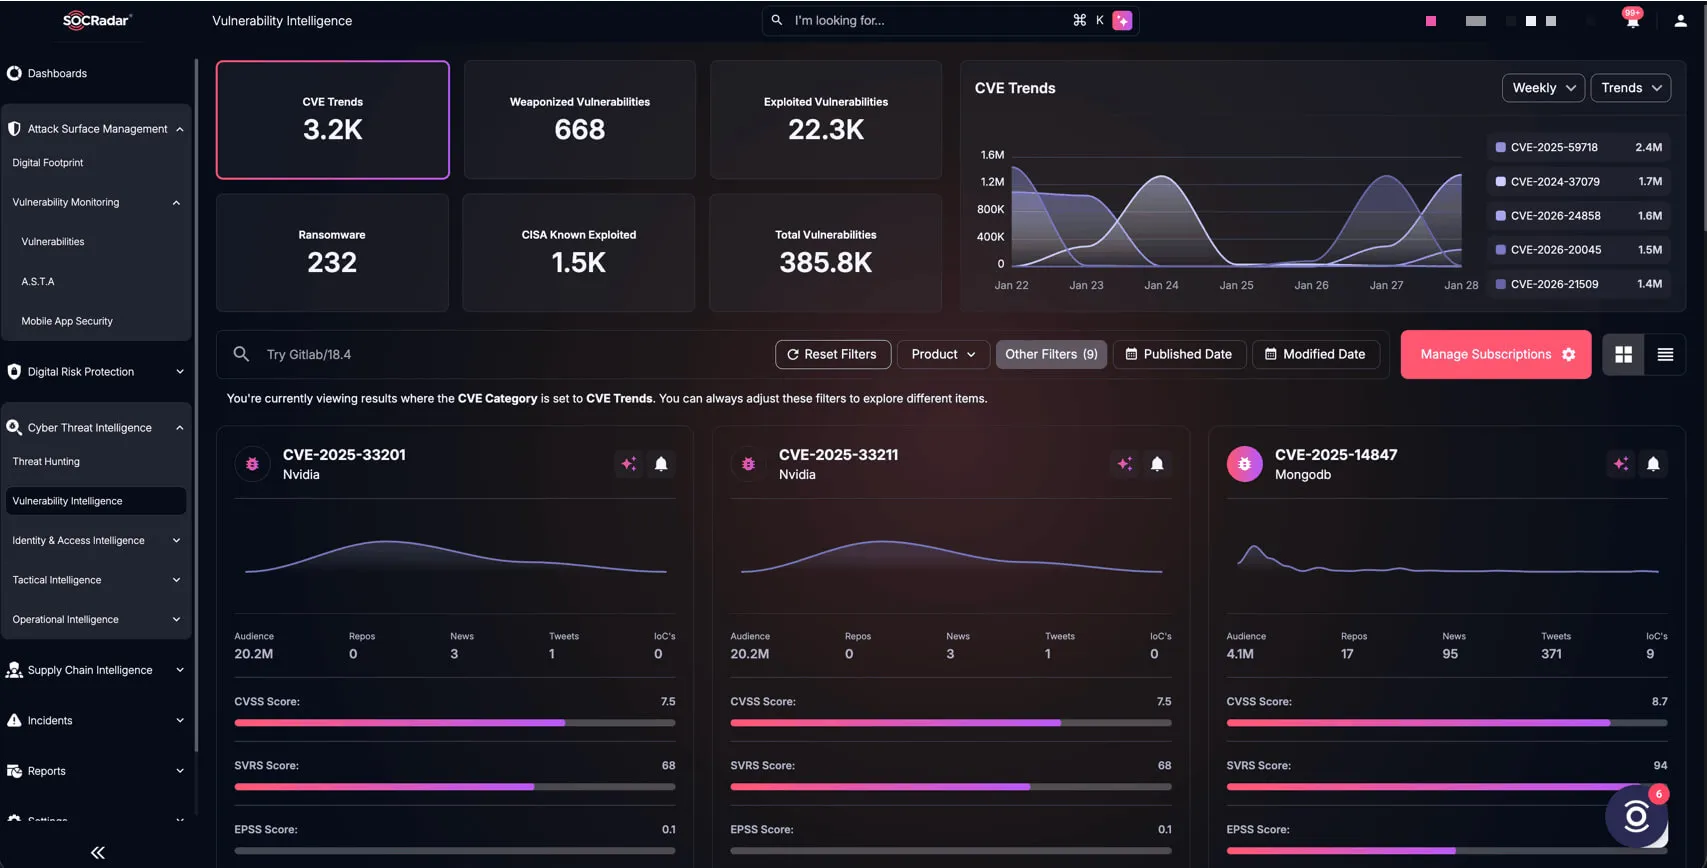
SOCRadar’s Vulnerability Intelligence
What Should Defenders Do?
Upgrade Self-Hosted AI Gateways
Upgrade affected deployments to 19.2.4, 19.3.2, 19.4.1, or a later fixed version. GitLab’s AI Gateway patch release notes strongly recommend updating affected installations immediately.
Verify the deployed Docker image or Helm image tag after upgrading.
Restrict Access and Exposure
Limit Duo Agent Platform and custom flow access to users who require it. Review newly provisioned accounts and recent changes to flow configurations.
Restrict gateway network access to required GitLab services, model providers, and trusted administrative networks. These measures reduce risk but do not replace the update.
Hunt for Suspicious Gateway Activity
No CVE-specific indicators have been published. Defenders can nevertheless investigate:
- Unexpected changes to custom flows or template configurations.
- Unusual Duo Agent Platform activity.
- Unexpected child processes launched by the AI Gateway container.
- Shells, interpreters, or system utilities not normally used by the service.
- Suspicious access to mounted files or configuration data.
- Unusual outbound connections to internal services or unfamiliar infrastructure.
If suspicious command execution is identified, determine which GitLab tokens, model-provider credentials, signing material, or other secrets were accessible to the gateway and rotate potentially exposed credentials after investigation.
Table Of Content
Related Articles

FortiMail Zero-Day Under Active Exploitation
Oct 02, 2026

TeamViewer Fixes Five Remote Access Flaws
Oct 01, 2026

CVE-2026-76504: Cisco SD-WAN Flaw Exploited
Oct 01, 2026

CVE-2026-86950: Apple CoreGraphics Zero-Day
Sep 30, 2026