Sep 21, 2026
Table Of Content
Related Articles
Clop Hack: ShinyHunters Hijacks Data Leak Site
CVE-2026-91843: Check Point Root RCE
Sep 18, 2026
CVE-2026-76460: Cisco ISE Flaw Actively Exploited
Sep 17, 2026
CVE-2026-76461: Cisco Email Gateway Flaw Exploited
Sep 16, 2026
CVE-2026-27540 WooCommerce Flaw Exploited
Sep 16, 2026

Sep 21, 2026
5 Mins Read

Summarize with:
Click2Shell: WordPress Flaw Enables RCE Chain
Click2Shell is a vulnerability in WordPress Core that allows a logged-in administrator’s browser to be manipulated into installing and previewing a theme without explicit consent. Although this security flaw cannot directly execute arbitrary code on its own, security researchers proved it can be combined with a susceptible theme to achieve remote execution of attacker-specified PHP code.
What Is WordPress Click2Shell?
Click2Shell impacts the theme preview and installation workflow within the WordPress administration panel. According to WordPress, the flaw enables a specially crafted URL to automatically install and preview a theme from WordPress.org. The issue was reported by Paulos Yibelo and pwn.ai.
The core vulnerability arises from a disparity in how WordPress processes a URL-derived theme parameter between its administrator-side JavaScript and the Themes API. While the Themes API sanitizes the parameter into an authorized theme slug, the client browser passes the original unescaped value into a jQuery selector. This mismatch effectively diverts standard theme operations toward the authorized Install function.
Exploitation does not require an attacker to hold an account on the target WordPress site. It does, however, necessitate that an authenticated administrator click a malicious link, though no manual authorization is required to trigger the theme installation.
As of September 21, a CVE identifier has not yet been assigned to Click2Shell.
Which WordPress Versions Are Affected?
Researchers expect the Core vulnerability to affect WordPress versions before 7.1.1. WordPress released 7.1.1 on September 17 with the fix and simultaneously published security updates for older branches.
Relevant September 17 releases include:
| WordPress branch | Security release |
|---|---|
| 7.1 | 7.1.1 |
| 7.0 | 7.0.5 |
| 6.9 | 6.9.8 |
| 6.8 | 6.8.9 |
| 6.7 | 6.7.8 |
| 6.6 | 6.6.8 |
| 6.5 | 6.5.11 |
| 6.4 | 6.4.11 |
| 6.3 | 6.3.11 |
| 6.2 | 6.2.12 |
| 6.1 | 6.1.13 |
| 6.0 | 6.0.15 |
Administrators should preferably move to the latest maintained WordPress release rather than relying on an outdated branch. WordPress currently identifies 7.1.1 as the latest release.
How Can Click2Shell Lead to PHP Execution?
While the Core flaw enables forcing WordPress to retrieve and preview a theme from the official WordPress.org catalog, it does not grant the ability to upload custom theme archives directly. Instead, the primary risk emerges when Click2Shell is paired with an additional security flaw.
According to the Click2Shell technical disclosure, security researchers illustrated an exploit chain targeting Mobile Repair Zone 2.5.4. During a Customizer preview, WordPress executed PHP code from the inactive theme, revealing an unauthenticated AJAX handler that lacked capability checks and nonce validation.
Leveraging this secondary weakness, researchers successfully executed arbitrary PHP code and indicated that over 40 other third-party themes suffer from comparable flaws.
This highlights a crucial distinction: Click2Shell serves as the mechanism for forced theme installation, whereas achieving full PHP execution depends on a secondary vulnerable component.
Regarding severity, researchers rated the standalone vulnerability at CVSS 7.1 (High), while the full exploit chain received a CVSS 9.3 (Critical) rating. As of the disclosure date, WordPress has yet to issue an official CVSS score.
Is There a Public Click2Shell PoC?
Yes. pwn.ai publicly disclosed technical details and a Proof-of-Concept (PoC) on September 18, one day after WordPress released the security updates. The researchers originally reported the Core vulnerability to WordPress on August 22 and provided the complete pre-activation chain on September 1.
The public research demonstrates both forced theme installation and the chained PHP-execution scenario. It does not establish that every vulnerable WordPress installation is directly exploitable for remote code execution.
Is Click2Shell Being Actively Exploited?
There is currently no confirmed evidence of Click2Shell exploitation in the wild from WordPress or the researchers who disclosed the vulnerability.
The availability of technical details and a public PoC increases the potential for independent weaponization, but exploitability still depends on an administrator visiting a crafted link. Achieving PHP execution additionally requires a suitable secondary weakness.
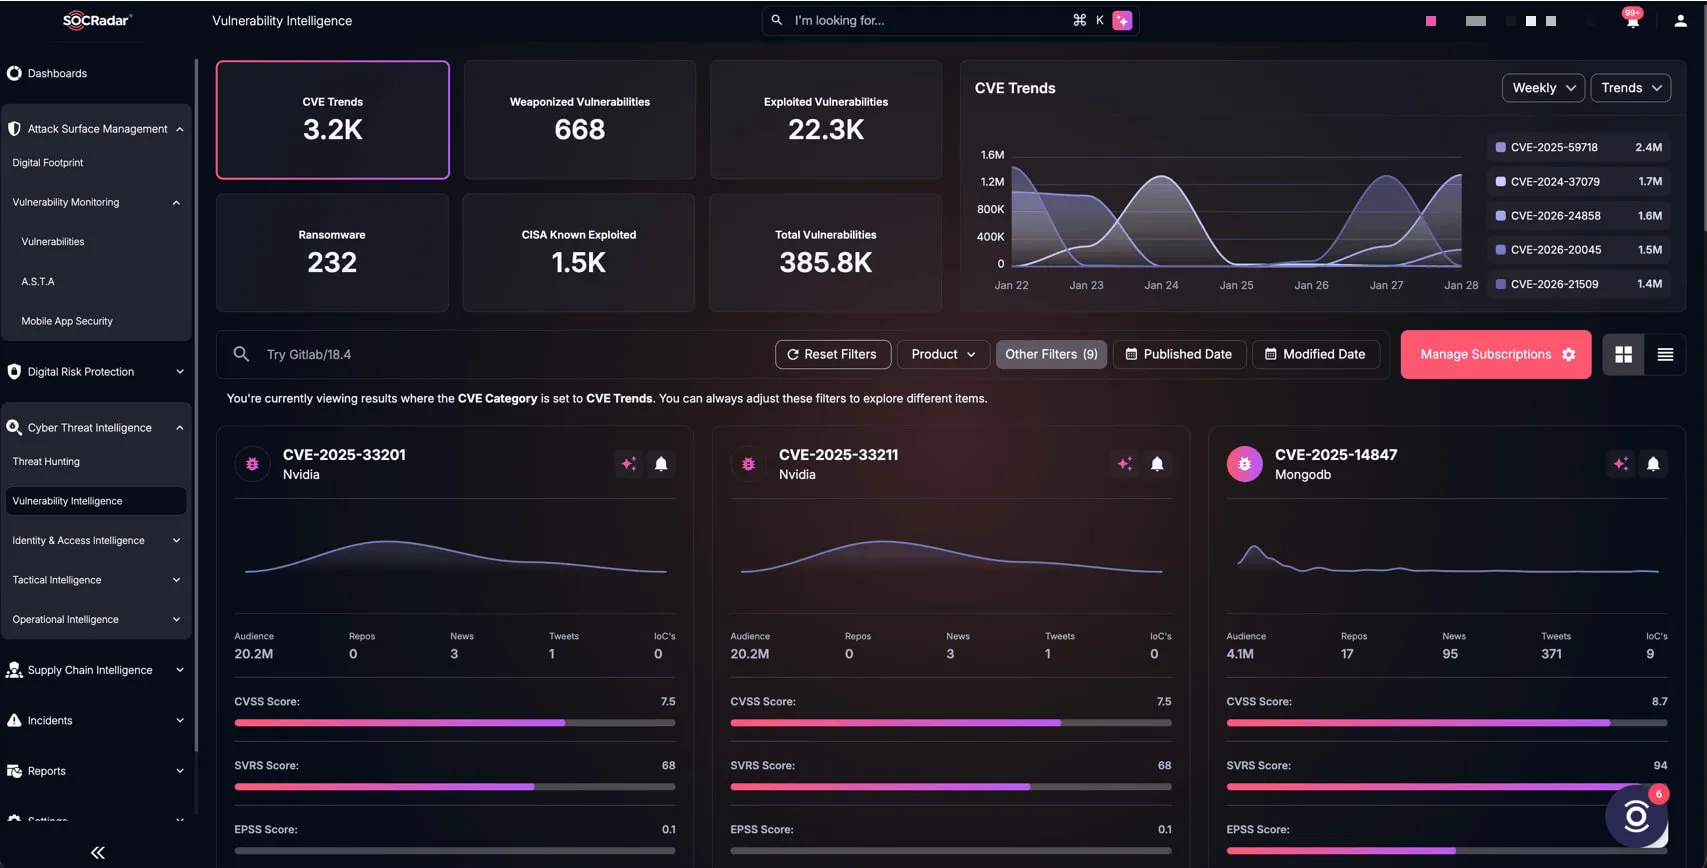
SOCRadar’s Vulnerability Intelligence, CTI module
SOCRadar’s Cyber Threat Intelligence (CTI) module can help teams monitor Click2Shell for CVE assignment, exploit developments, severity changes, and remediation guidance. Attack Surface Management (ASM) can complement this by identifying exposed WordPress assets that may require prioritized updates. Key capabilities supporting these modules include:
- IOC enrichment: Adds context to IPs, domains, URLs, hashes, and other indicators.
- Vulnerability intelligence: Helps teams prioritize flaws based on exploitation and threat activity.
- Digital risk protection: Monitors dark web mentions, phishing, brand abuse, impersonation, and leaked data.
- Attack surface visibility: Connects external threats to exposed assets and infrastructure.
What Should Defenders Do About Click2Shell?
Update WordPress Core
Administrators should install the latest WordPress security release. WordPress recommends updating sites immediately following the September 17 security release.
The official WordPress 7.1.1 security announcement provides details about the release and its security fixes.
Organizations should also inventory themes and plugins, including inactive components, and remove those that are unnecessary. Themes containing AJAX handlers, package-installation functionality, or code that runs during Customizer previews deserve particular attention.
Hunt for Unexpected Theme and Plugin Activity
No vendor-provided Click2Shell detection signature is available. Defenders can instead investigate behavioral signs that may be consistent with attempted exploitation, including:
- Unexpected theme installations or previews
- Unusual requests to wp-admin/theme-install.php
- Unexpected Customizer or admin-ajax.php activity involving inactive themes
- New or modified PHP files under wp-content/themes/ or wp-content/plugins/
- Plugin downloads or file writes shortly after theme-preview activity
- Unexpected administrator-account or configuration changes
- Unusual outbound connections from the WordPress server
These are general hunting signals rather than confirmed Click2Shell indicators. Teams should correlate WordPress activity with web server, WAF, EDR, and hosting provider telemetry before drawing conclusions.
For Click2Shell, the immediate priority is updating WordPress Core and reviewing installed themes. Sites that remained unpatched after technical details became public should also review administrator sessions, theme installation, and filesystem activity for unexpected changes.