Sep 14, 2026
Table Of Content
Dominican Republic Leak, Celestial Malware, Money Network Sale, CVV Auction, and US VPN Access
Alleged Dominican Republic Citizen Data Leak is Detected
Alleged Celestial Malware Suite is Advertised
Alleged Money Network Database is Offered for Sale
Alleged U.S. CVV Database is Auctioned
Alleged U.S. SSL VPN and Fortigate SSH Access is Advertised
Related Articles
Dark Web Market: Anubis Market
Sep 08, 2026

Sep 21, 2026
5 Mins Read

Summarize with:
Dominican Republic Leak, Celestial Malware, Money Network Sale, CVV Auction, and US VPN Access
SOCRadar Dark Web Team identified several new underground posts, including an alleged Dominican Republic citizen data leak, an alleged Celestial malware suite sale, and an alleged Money Network database sale. Other posts advertised an alleged U.S. CVV database auction involving 1.9 million records and alleged SSL VPN/Fortigate SSH access to a U.S. industrial machinery and manufacturing organization.
Receive a Free Dark Web Report for Your Organization:
Alleged Dominican Republic Citizen Data Leak is Detected
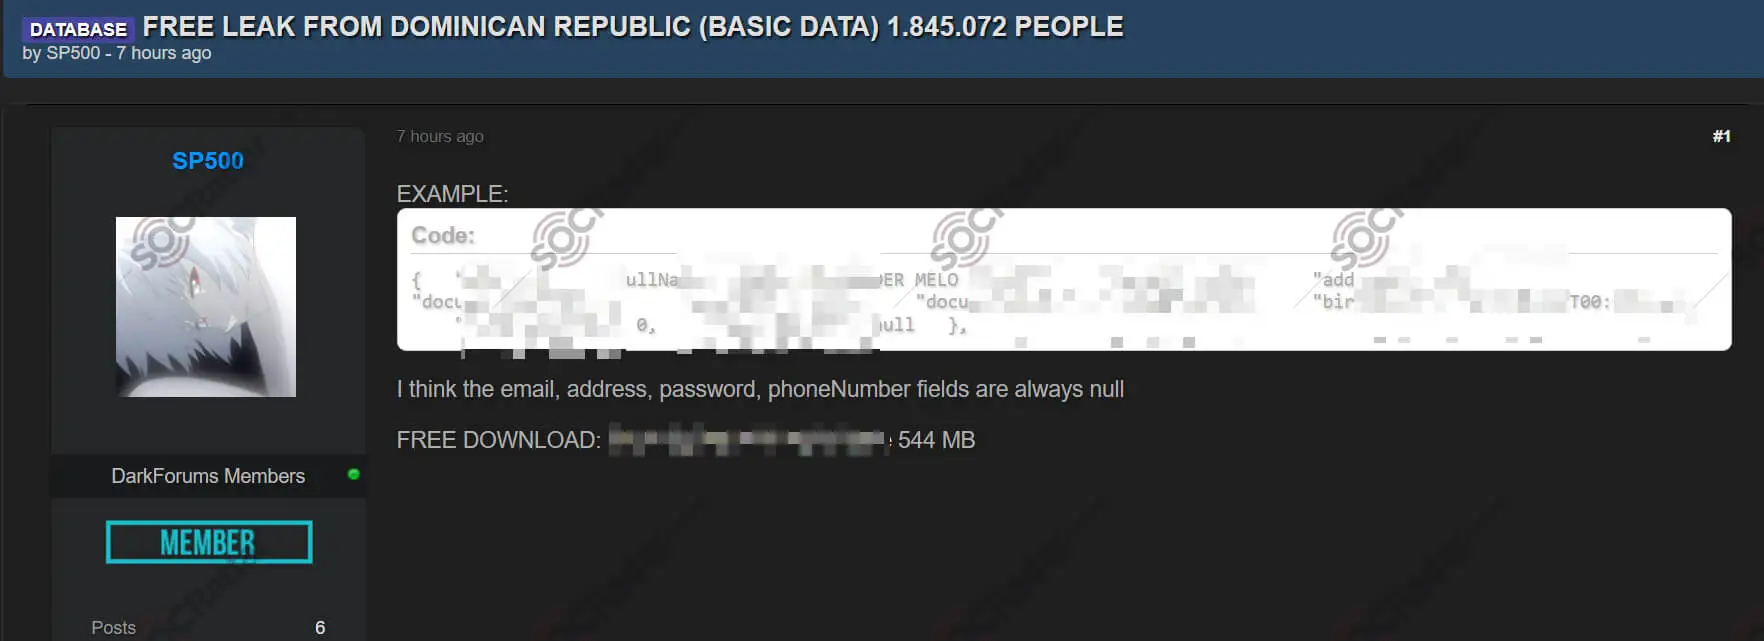
SOCRadar Dark Web Team detected a dark web post claiming to leak basic citizen data allegedly associated with the Dominican Republic. The actor claimed the dataset contains approximately 1,845,072 records and made the archive available as a free download.
The sample shown in the post appears to include fields such as document-related identifiers, names, and birth information. The actor also stated that some fields, including email, address, password, and phone number, may be null. Even with limited fields, the exposure of identity-related data could increase the risk of fraud, profiling, phishing, and identity misuse.
Alleged Celestial Malware Suite is Advertised
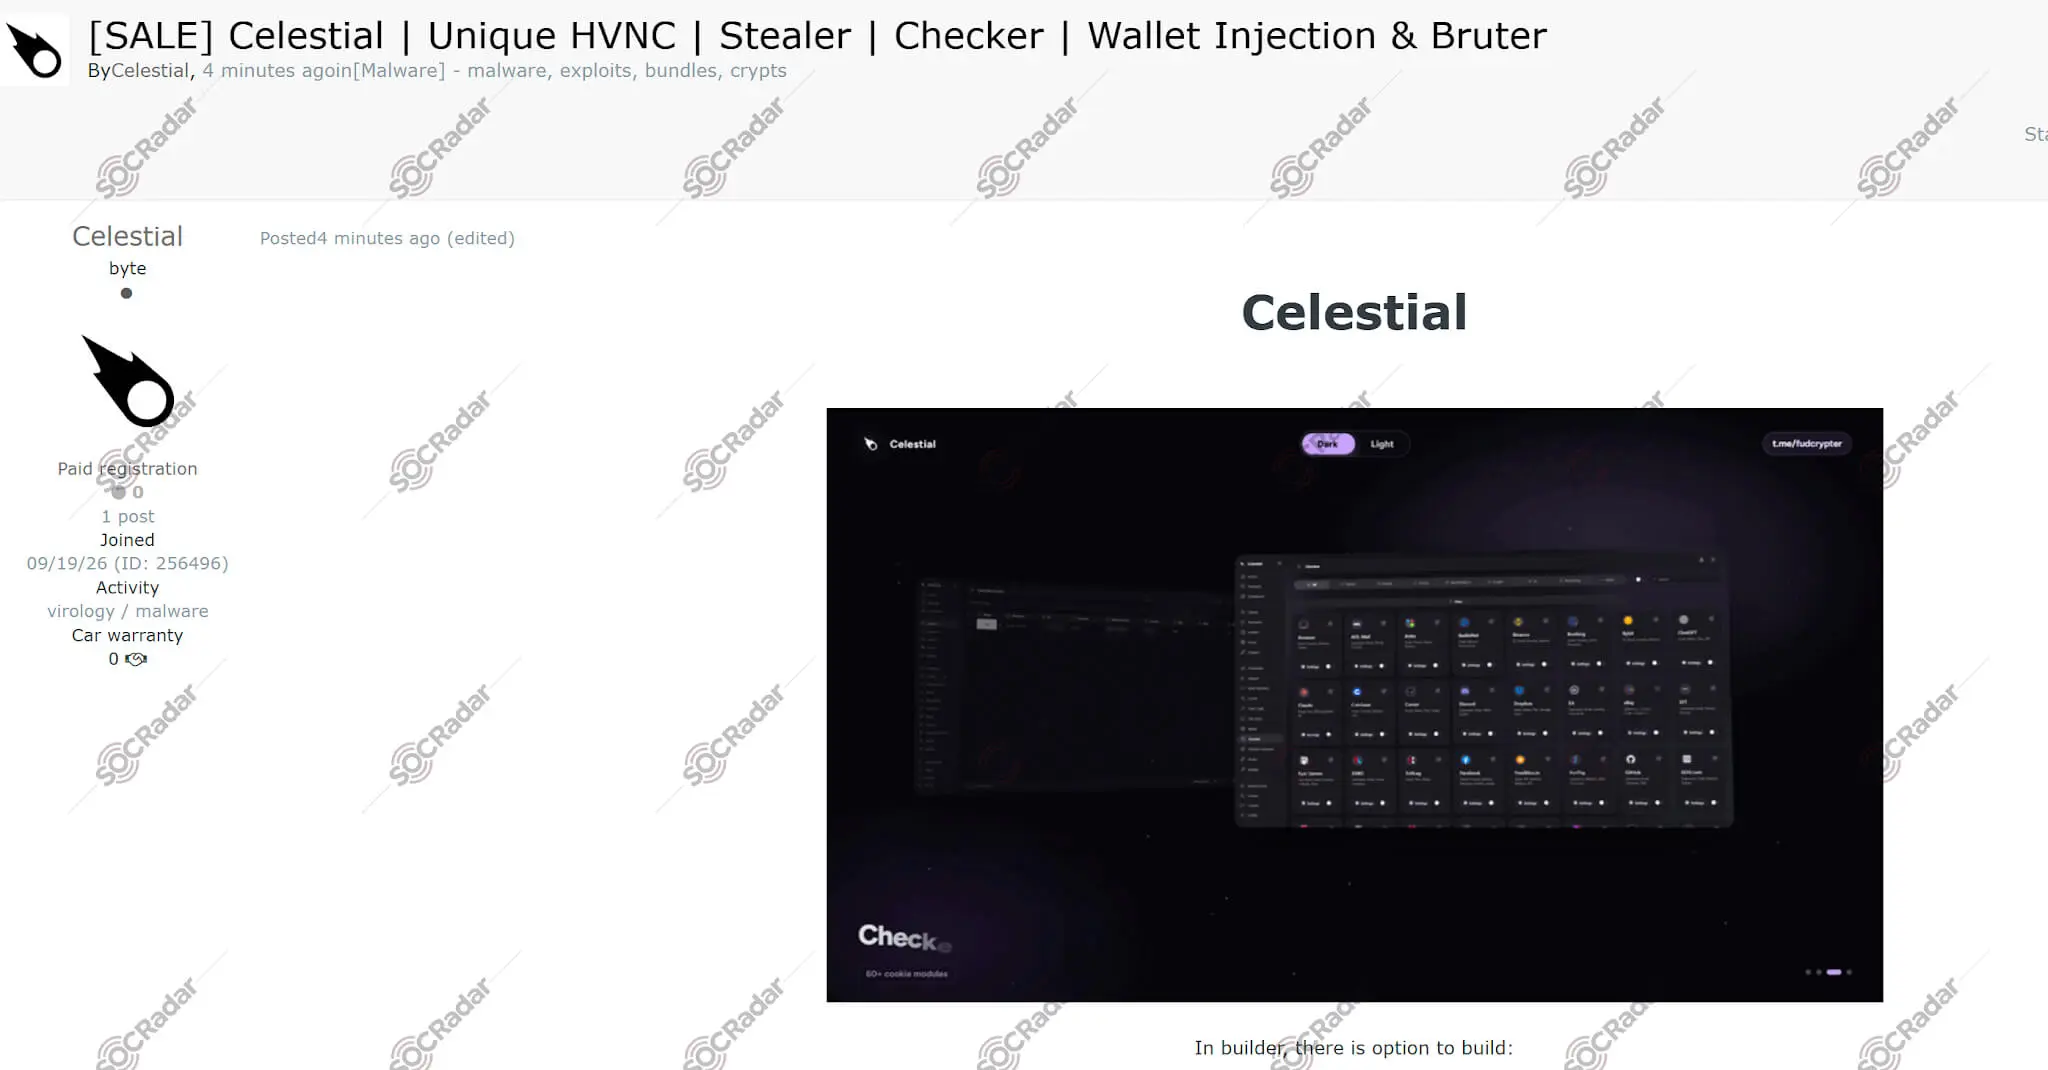
SOCRadar Dark Web Team detected a Dark Web forum post advertising Celestial, a malware suite described as offering multiple cybercrime functions in one package. The listing promoted capabilities such as HVNC, stealer functionality, checker features, wallet injection, and brute-force modules.
The post presented Celestial as a builder-style malware platform, suggesting that operators could generate payloads and use the tool for credential theft, remote access, and cryptocurrency-focused abuse. If operational, this type of toolkit may support broader malware campaigns by combining access, theft, and monetization features in a single offering.
Alleged Money Network Database is Offered for Sale
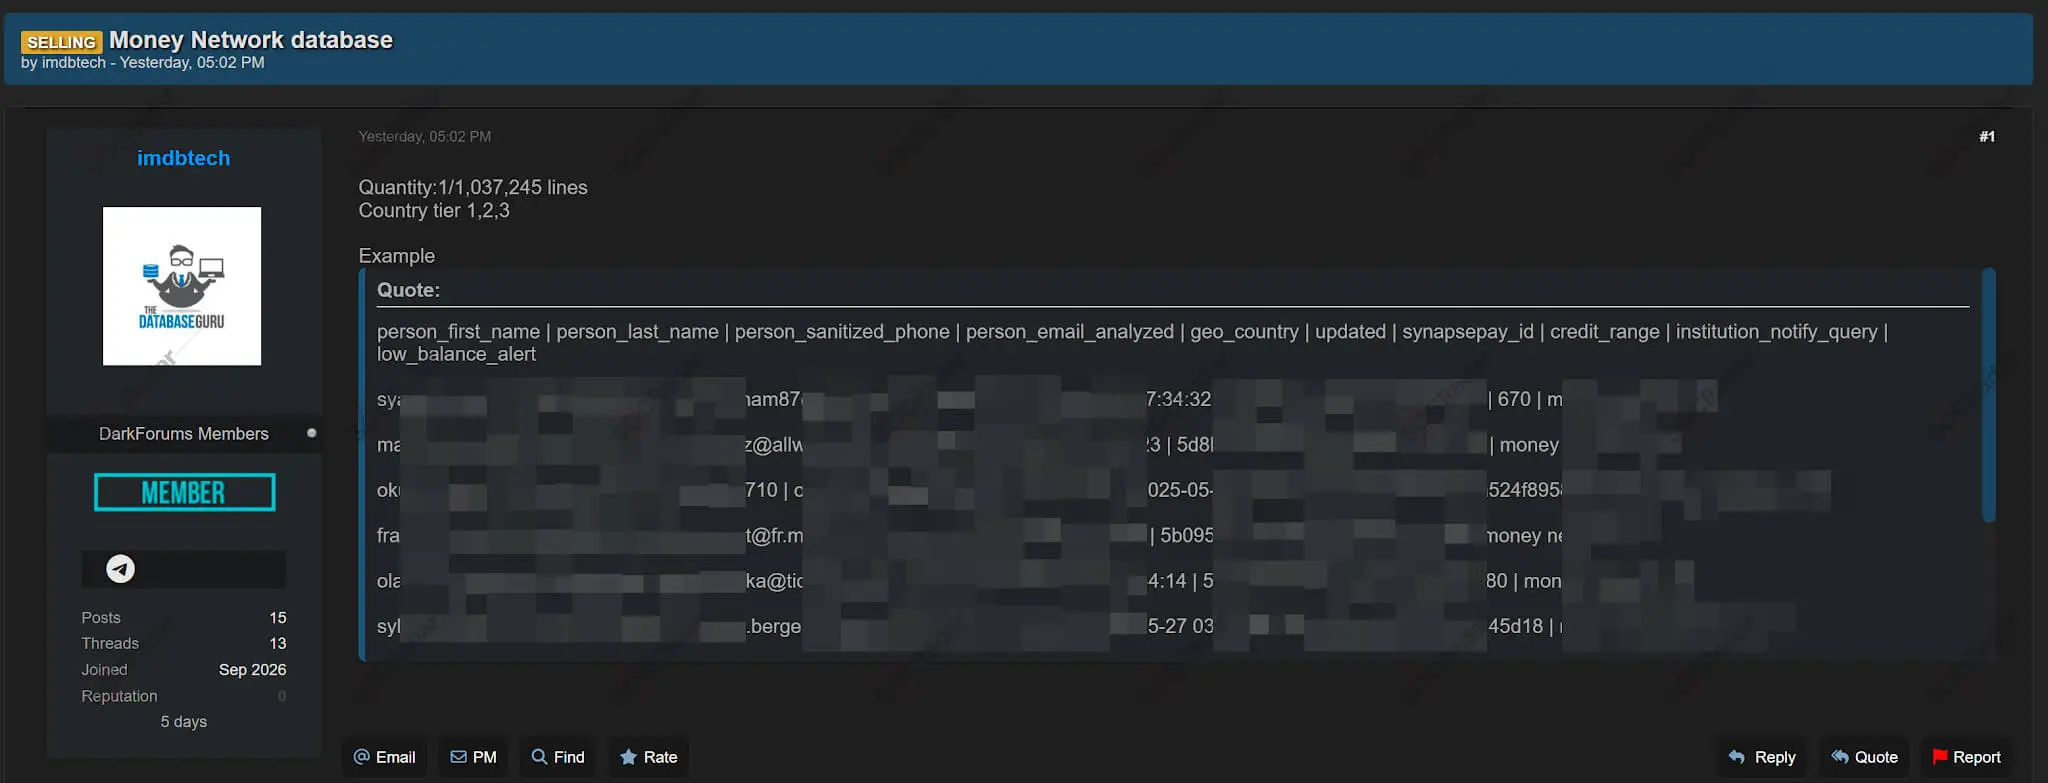
SOCRadar Dark Web Team detected a dark web post advertising an alleged Money Network database. The seller claimed the dataset contains approximately 1,037,245 lines and includes records from multiple country tiers.
The sample structure shown in the listing includes fields such as first name, last name, sanitized phone number, analyzed email address, country information, SynapsePay ID, credit range, institution notification query, and low-balance alert fields. If authentic, the exposure could support targeted phishing, financial fraud, and social engineering attempts using payment or account-related context.
Alleged U.S. CVV Database is Auctioned
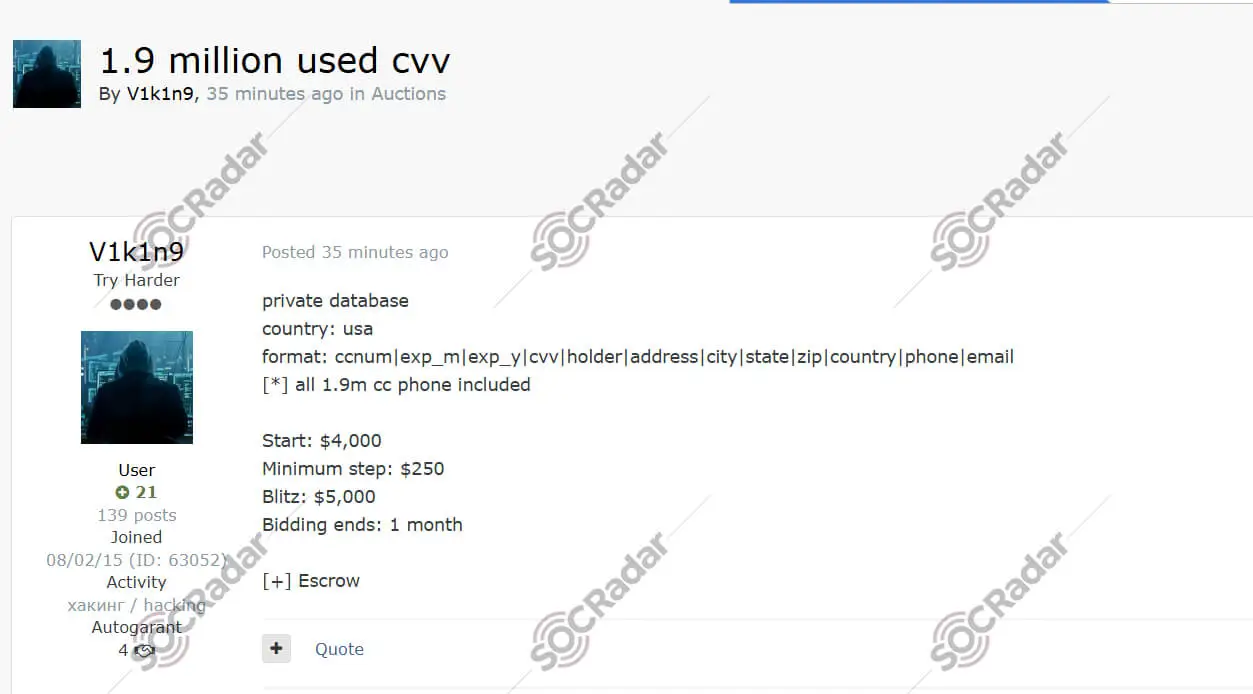
SOCRadar Dark Web Team detected a post auctioning an alleged 1.9 million U.S. CVV records. The seller described the dataset as a private database and claimed that all records include phone numbers.
The listing referenced fields such as card number, expiration month and year, CVV, cardholder name, address, city, state, ZIP code, country, phone number, and email address. The auction terms included a $4,000 starting price, $250 minimum step, and $5,000 blitz price. If valid, the dataset could enable payment fraud, identity theft, phishing, and card-not-present abuse.
Alleged U.S. SSL VPN and Fortigate SSH Access is Advertised
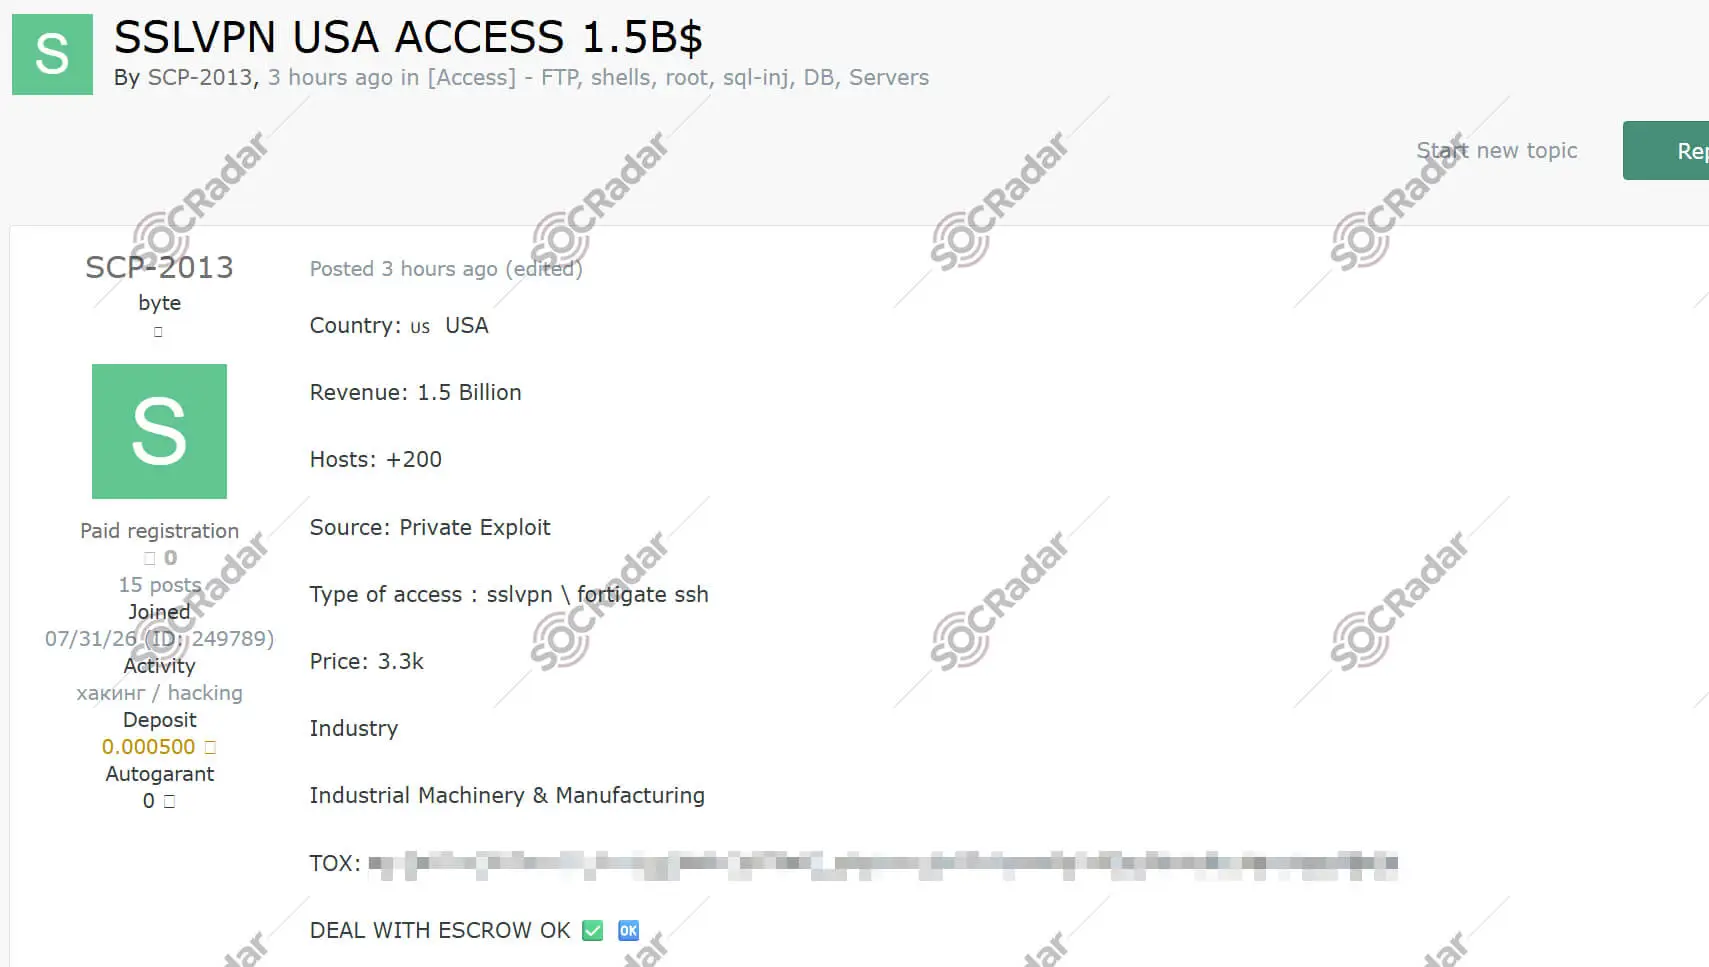
SOCRadar Dark Web Team detected an initial access broker post advertising alleged access to a U.S.-based industrial machinery and manufacturing organization. The seller claimed the victim organization generates approximately $1.5 billion in revenue and has more than 200 hosts.
The post listed the access type as SSL VPN / Fortigate SSH and claimed the source was a private exploit. The asking price was listed as $3,300, with escrow accepted. If verified, this type of access could provide threat actors with an entry point for lateral movement, data theft, ransomware deployment, or further compromise of the victim environment.
Powered by DarkMirror™
Gaining visibility into deep and dark web threats can be extremely useful from an actionable threat intelligence and digital risk protection perspective. However, monitoring all sources is simply not feasible, which can be time-consuming and challenging. One click-by-mistake can result in malware bot infection. To tackle these challenges, SOCRadar’s DarkMirror™ screen empowers your SOC team to follow up with the latest posts of threat actors and groups filtered by the targeted country or industry.