Sep 25, 2026
Table Of Content
Metree and WuBook Leaks, SonicWall Access, Campus.gov.il Data, and Kenya Vehicle Database
Alleged Metree E-Commerce Database Leak is Detected
Alleged WuBook Customer Data Leak is Detected
Alleged SonicWall-Based U.S. Automotive Access is Auctioned
Alleged Campus.gov.il Student Data Leak is Detected
Alleged Kenyan Vehicle Valuation Database Leak is Detected
Related Articles
Dark Web Profile: Blue Locker Ransomware
ShinyHunters Claims Access to FBI Systems
Sep 24, 2026
Clop Hack: ShinyHunters Hijacks Data Leak Site
Sep 21, 2026
Sep 28, 2026
4 Mins Read

Summarize with:
Metree and WuBook Leaks, SonicWall Access, Campus.gov.il Data, and Kenya Vehicle Database
SOCRadar Dark Web Team identified several new underground posts, including an alleged Metree e-commerce database leak, an alleged WuBook customer data leak, and an alleged SonicWall-based access auction for a U.S. automotive engineering firm. Other posts advertised alleged student records from campus.gov.il and an alleged Kenyan vehicle valuation database containing more than 1.2 million records.
Receive a Free Dark Web Report for Your Organization:
Alleged Metree E-Commerce Database Leak is Detected
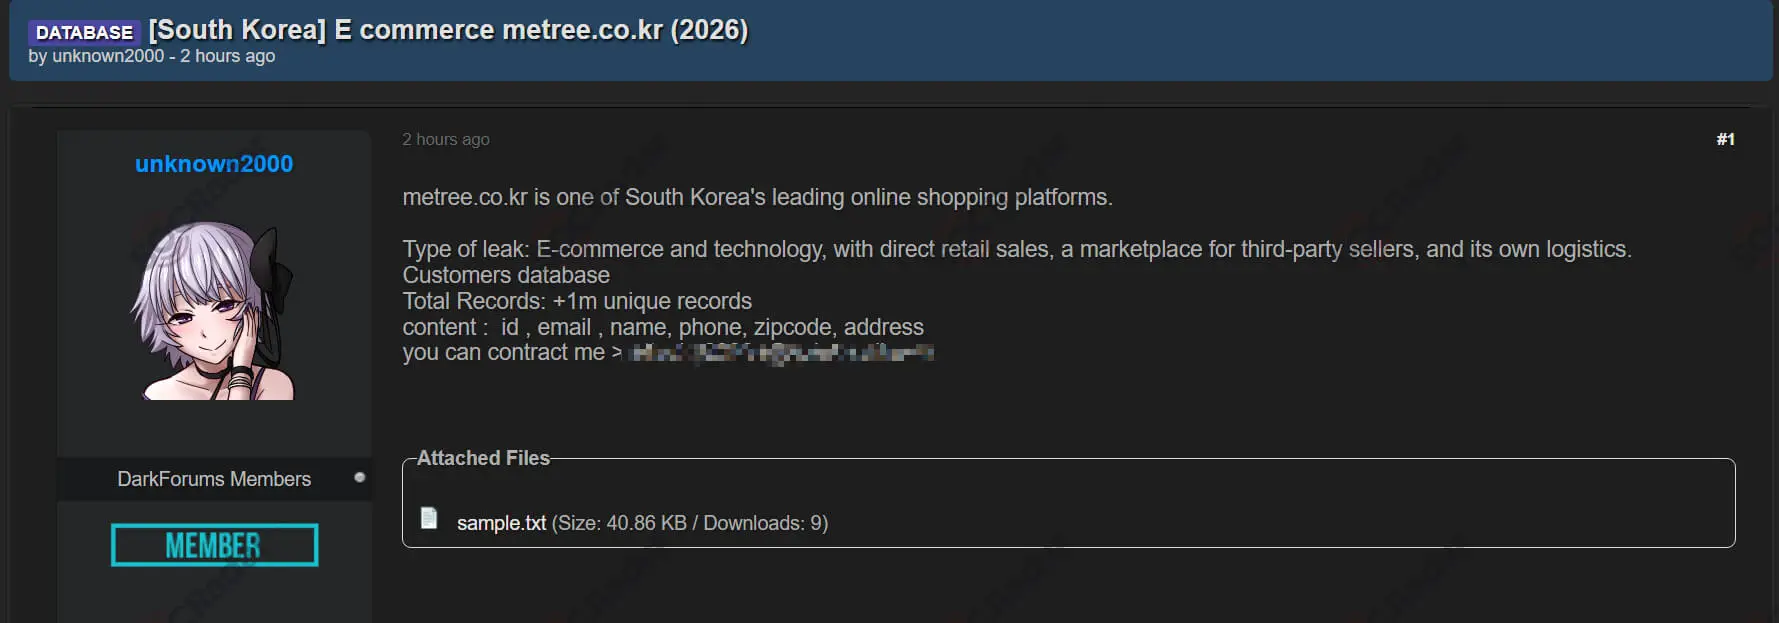
SOCRadar Dark Web Team detected a dark web post claiming to offer a customer database allegedly belonging to Metree, a South Korean e-commerce platform. The actor claimed the dataset contains over 1 million unique records tied to the platform’s e-commerce, retail, marketplace, and logistics operations.
The exposed data reportedly includes user IDs, email addresses, full names, phone numbers, zip codes, and physical addresses. If confirmed, the exposure could increase the risk of targeted phishing, identity theft, social engineering, and fraud against affected customers.
Alleged WuBook Customer Data Leak is Detected
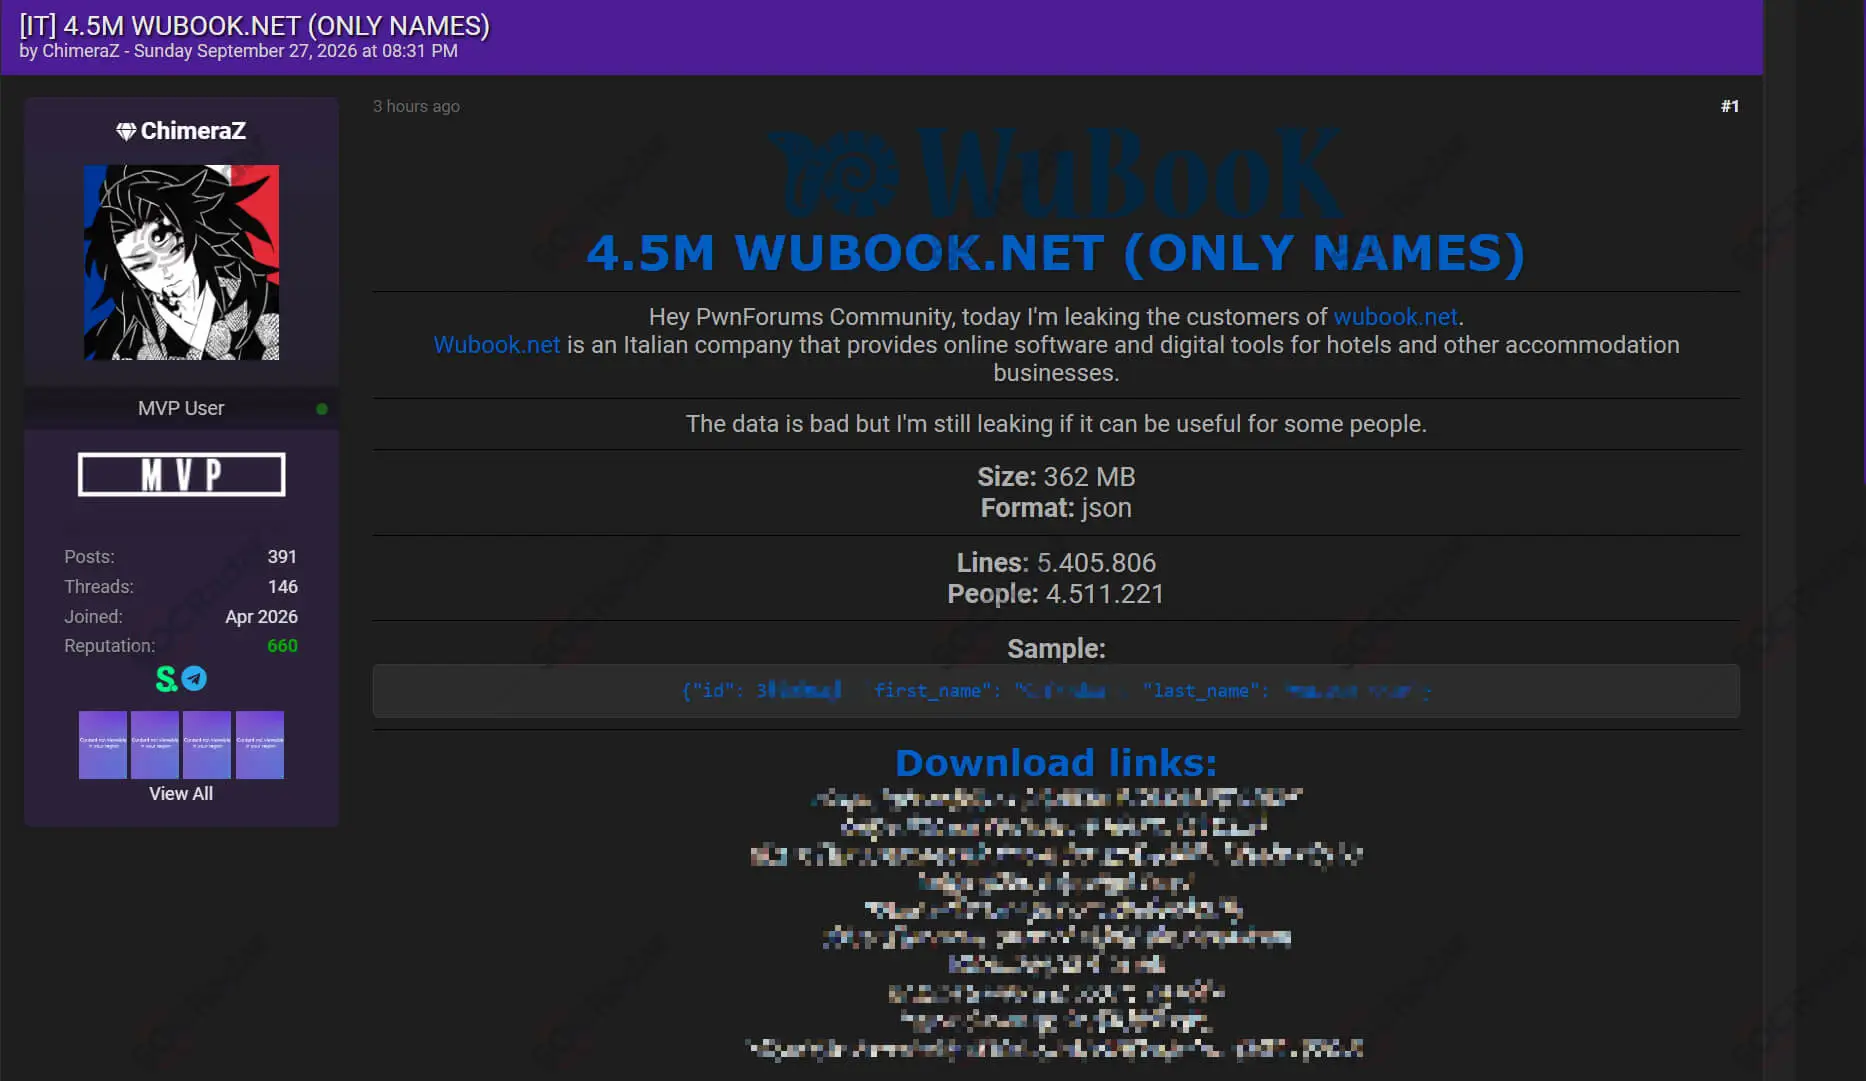
SOCRadar Dark Web Team detected a post claiming to leak a database allegedly belonging to WuBook, an Italian hospitality software provider. The actor claimed the dataset contains more than 4.5 million user records, with approximately 5.4 million lines in JSON format.
The sample data reportedly includes user IDs, first names, and last names, while the actor described the dataset as limited in scope. Even if the exposed fields are mainly names, the association with a hospitality software platform could still support targeted phishing and social engineering campaigns against hotel staff, business owners, and platform users.
Alleged SonicWall-Based U.S. Automotive Access is Auctioned
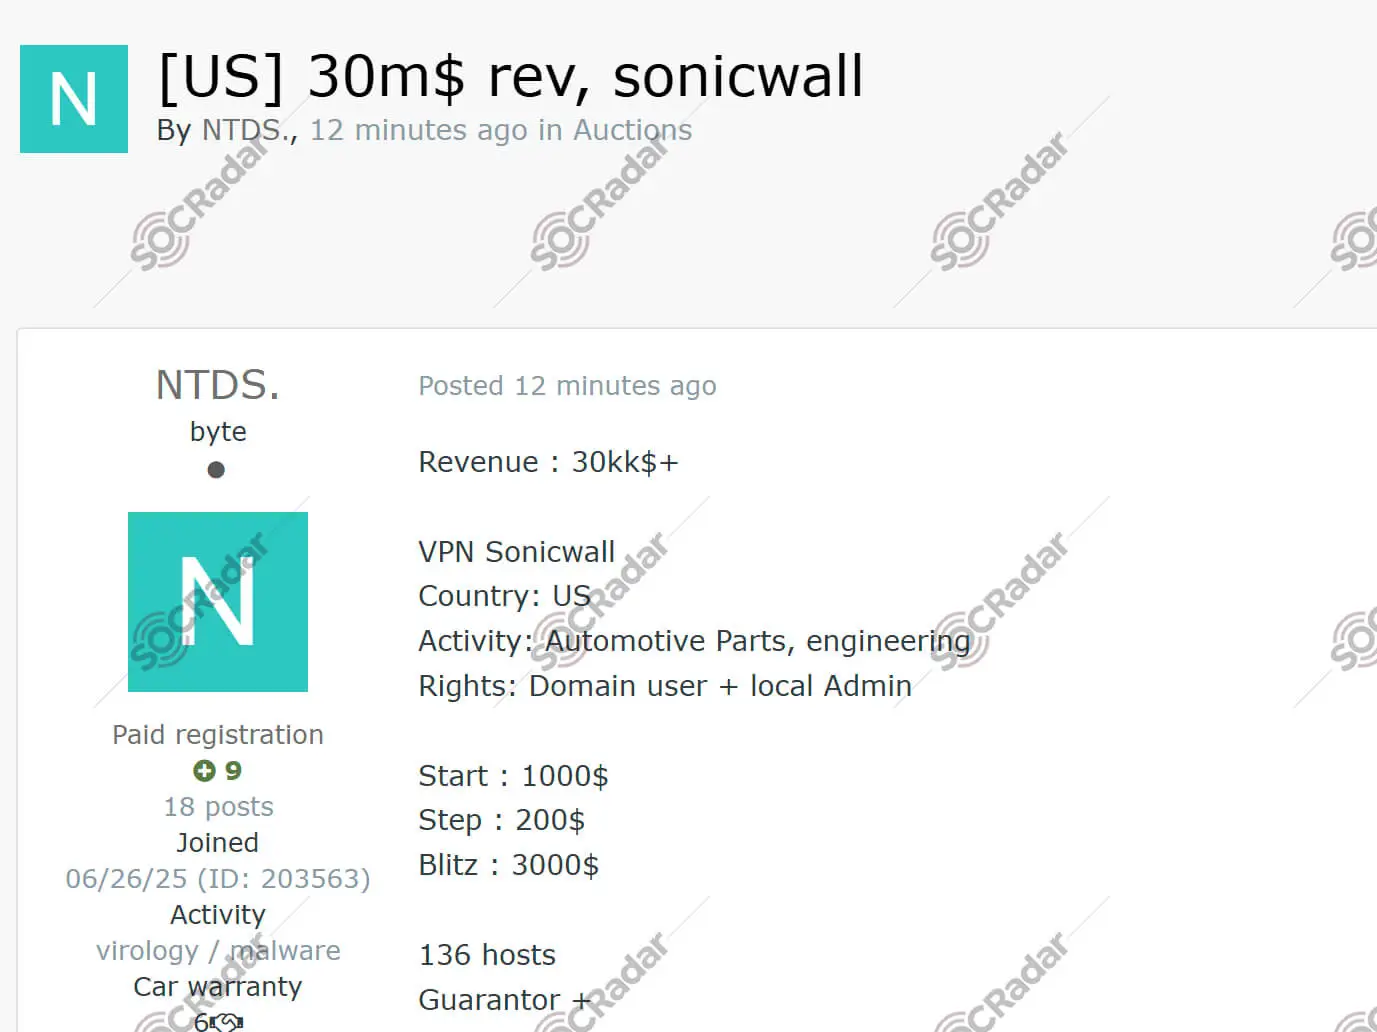
SOCRadar Dark Web Team detected an initial access broker post auctioning alleged access to a U.S.-based automotive parts and engineering company. The seller claimed the victim organization generates more than $30 million in annual revenue.
The listing claims access through a SonicWall VPN, with domain user and local administrator privileges across approximately 136 hosts. If valid, this access could enable lateral movement, data theft, ransomware deployment, or further compromise of engineering and supply chain systems.
Alleged Campus.gov.il Student Data Leak is Detected
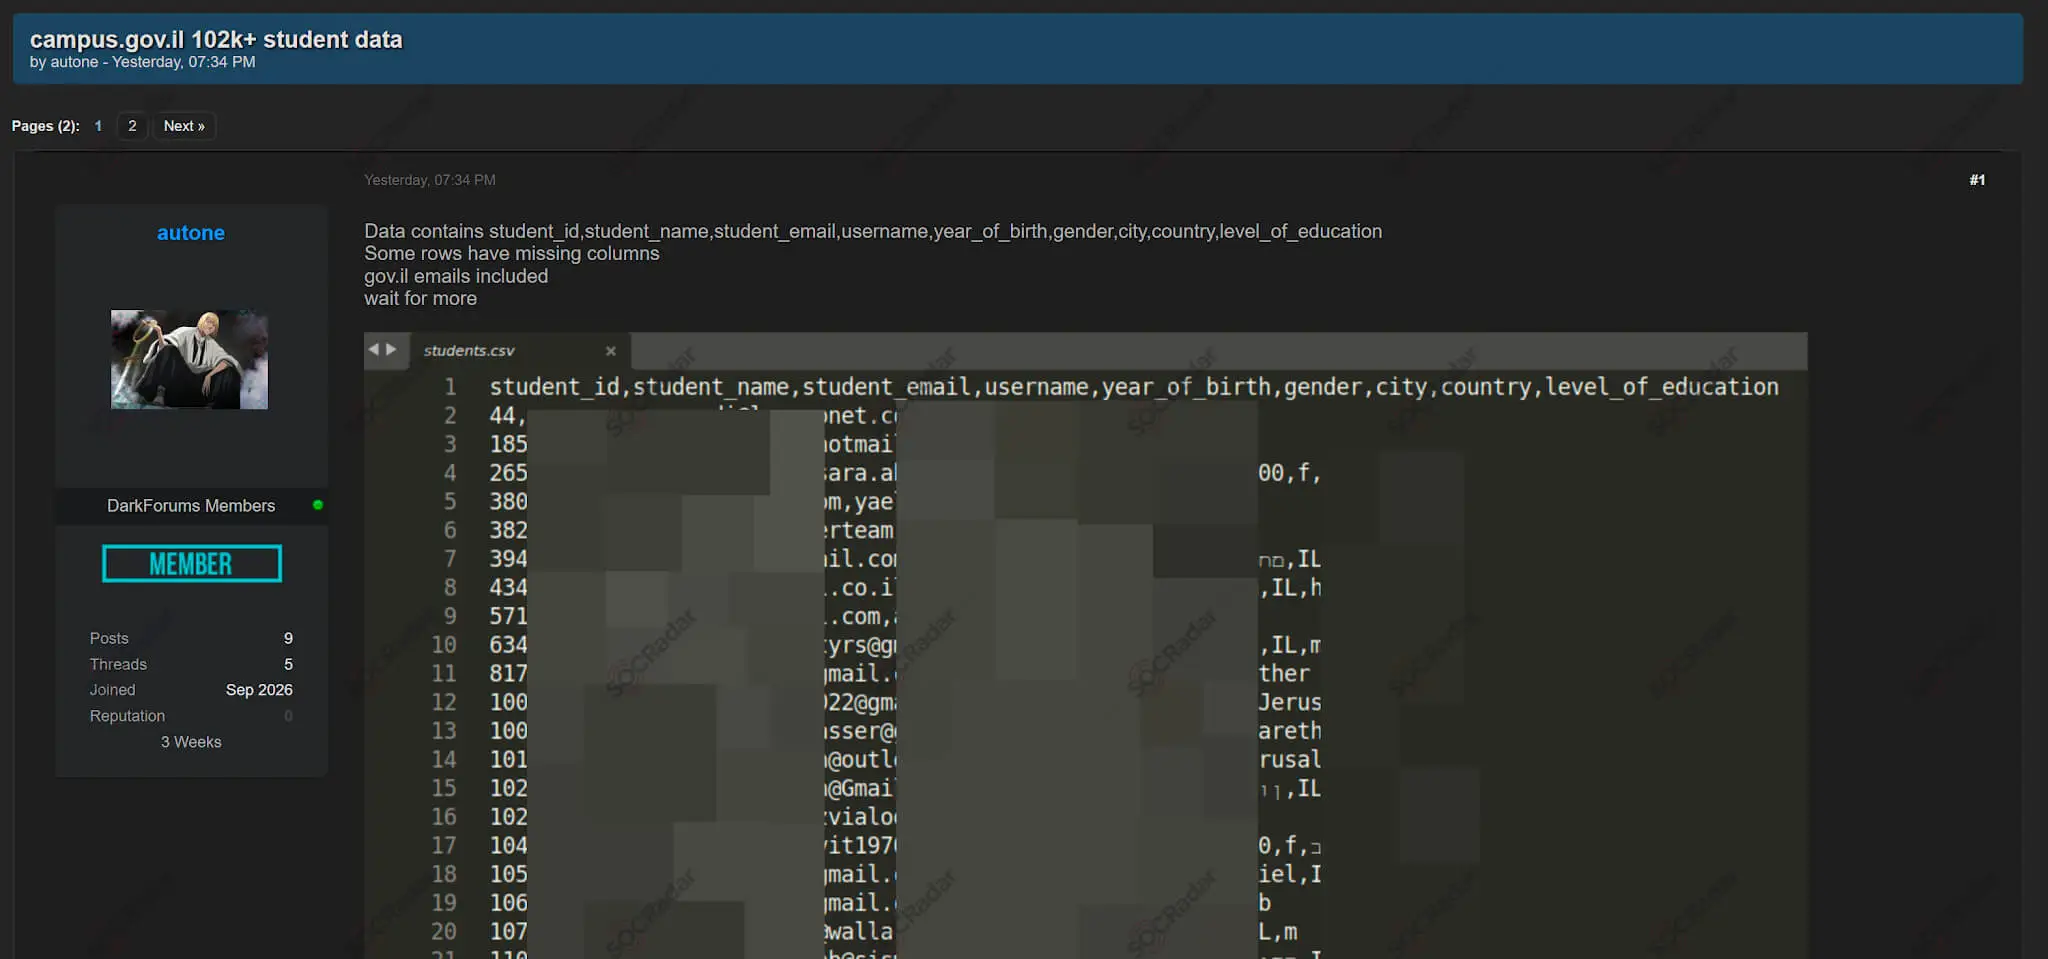
SOCRadar Dark Web Team detected a dark web post claiming to possess student records allegedly linked to campus.gov.il, Israel’s government-affiliated digital education portal. The actor claimed the dataset contains more than 102,000 student records.
The post reportedly references fields such as student ID, student name, student email, username, year of birth, gender, city, country, and education level. If verified, this exposure could create risks around phishing, identity theft, and misuse of education-related personal information.
Alleged Kenyan Vehicle Valuation Database Leak is Detected
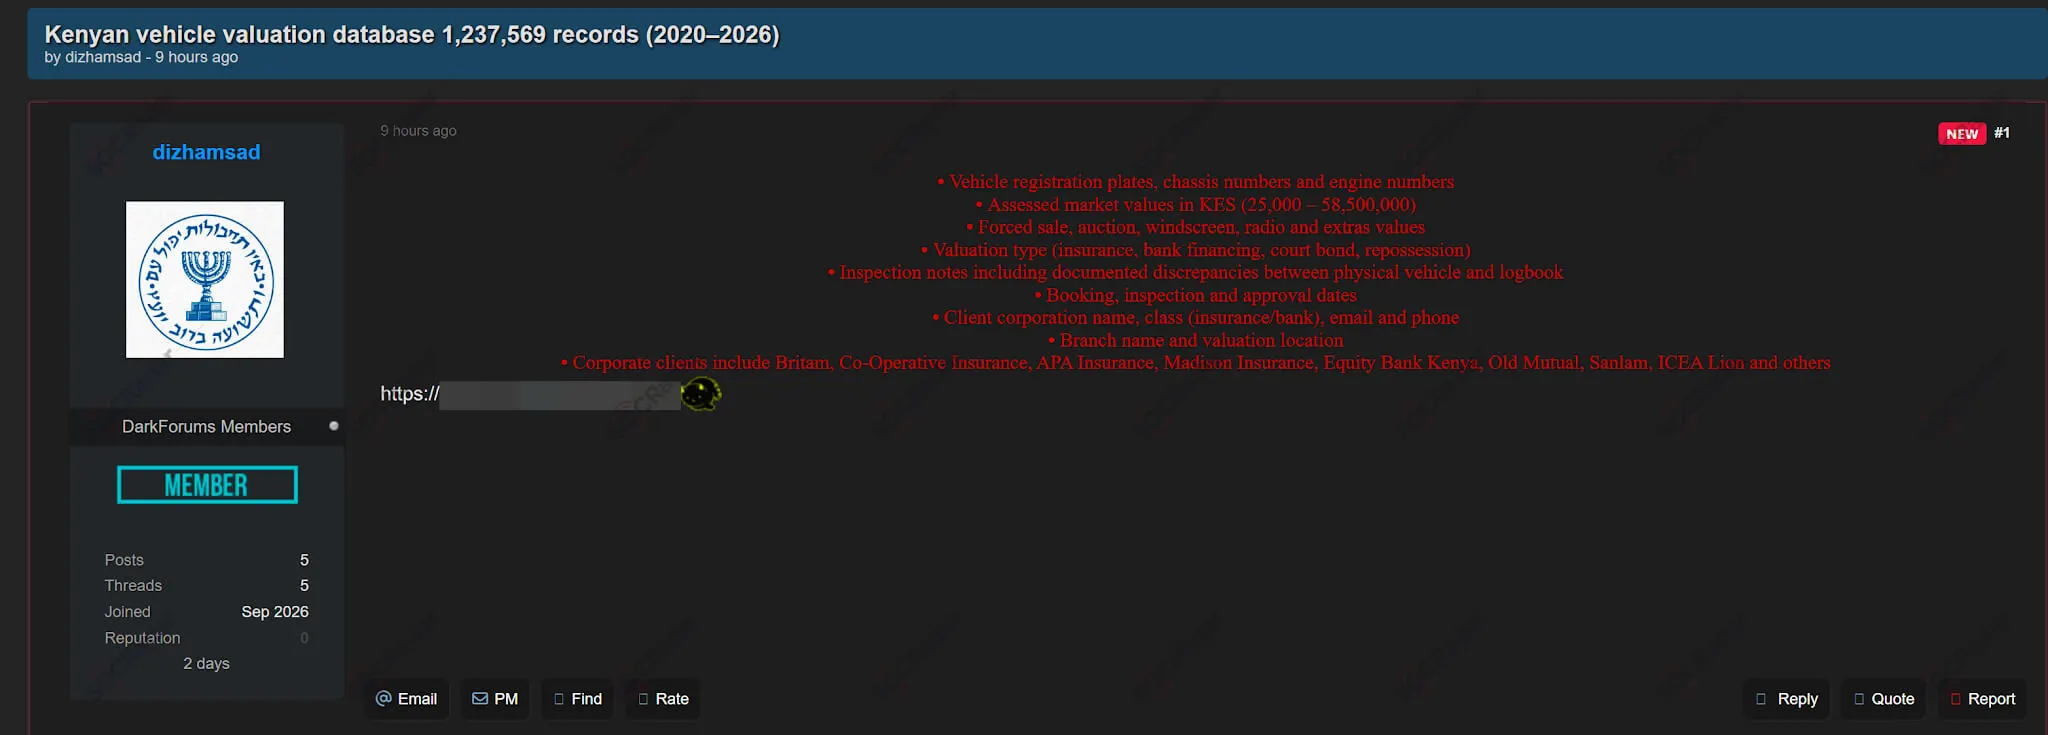
SOCRadar Dark Web Team detected a post claiming to leak a Kenyan vehicle valuation database containing 1,237,569 records from 2020 to 2026. The exposed information reportedly includes vehicle registration plates, chassis numbers, engine numbers, valuation data, inspection notes, and corporate client information.
The listing names several major Kenyan insurance and financial organizations as corporate clients, including Britam, Co-Operative Insurance, APA Insurance, Madison Insurance, Equity Bank Kenya, Old Mutual, Sanlam, and ICEA Lion. If authentic, the dataset could support vehicle-related fraud, targeted phishing, corporate intelligence gathering, and attacks against organizations relying on third-party valuation services.
Powered by DarkMirror™
Gaining visibility into deep and dark web threats can be extremely useful from an actionable threat intelligence and digital risk protection perspective. However, monitoring all sources is simply not feasible, which can be time-consuming and challenging. One click-by-mistake can result in malware bot infection. To tackle these challenges, SOCRadar’s DarkMirror™ screen empowers your SOC team to follow up with the latest posts of threat actors and groups filtered by the targeted country or industry.