Oct 05, 2026
Oct 12, 2026
4 Mins Read

Summarize with:
Angi Data Sale, The Tour Guy Breach, Healthcare Leads, KPN Leak, and CafeMom Data Resurface
SOCRadar Dark Web Team identified several new underground posts, including an alleged Angi customer database sale, an alleged The Tour Guy breach exposing 3.8 million records, and an alleged healthcare leads database covering Australia, South Korea, Japan, and China. Other posts advertised an alleged KPN Netherlands customer database and a resurfaced historical CafeMom breach dataset.
Receive a Free Dark Web Report for Your Organization:
Alleged Angi Database Sale is Detected
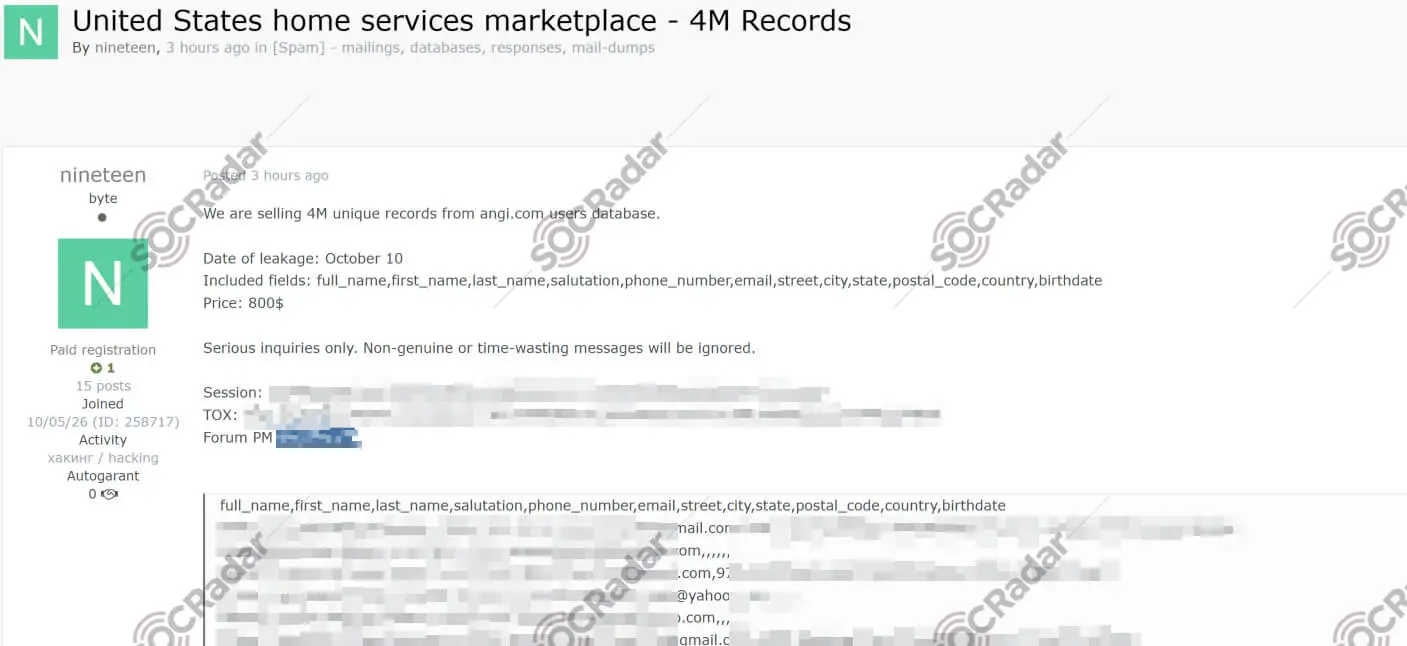
SOCRadar Dark Web Team detected a dark web post advertising a database allegedly stolen from Angi, the U.S.-based home services marketplace. The seller claimed the dataset contains 4 million unique records and listed it for $800.
The exposed fields reportedly include full names, first names, last names, salutations, phone numbers, email addresses, street addresses, cities, states, postal codes, countries, and birthdates. If authentic, the data could support targeted phishing, smishing, identity fraud, and social engineering campaigns against Angi users.
Alleged The Tour Guy Breach is Detected
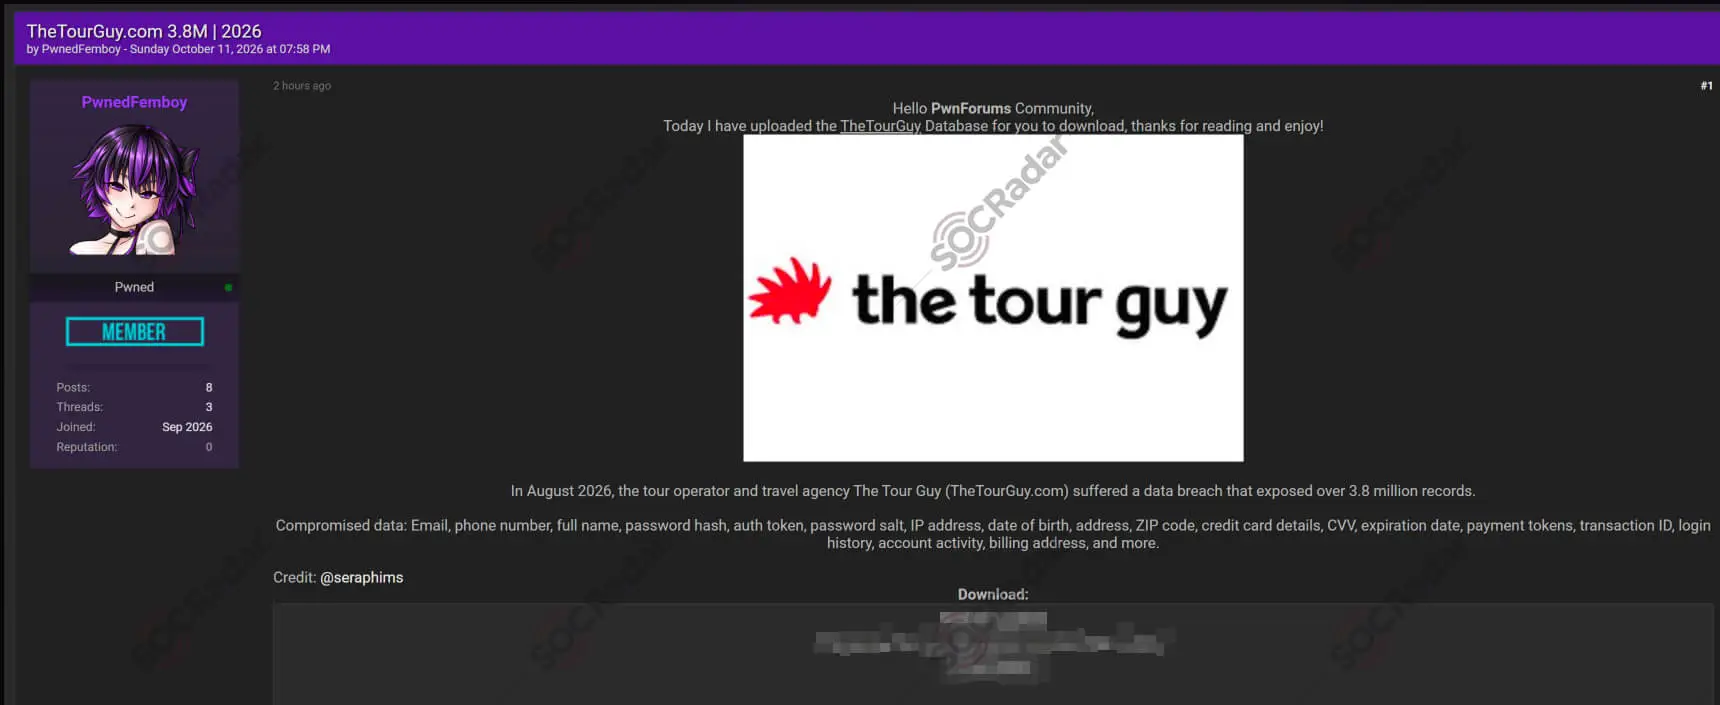
SOCRadar Dark Web Team detected a post claiming a breach of The Tour Guy, a travel operator and agency. The actor claimed the breach occurred in August 2026 and exposed more than 3.8 million records.
The compromised data reportedly includes full names, email addresses, phone numbers, physical addresses, ZIP codes, dates of birth, IP addresses, password hashes, salts, authentication tokens, login history, account activity, billing details, payment tokens, transaction IDs, and payment card data. If verified, the exposure could create a high risk of financial fraud, identity theft, account takeover, and targeted phishing.
Alleged Healthcare Leads Database is Offered for Sale
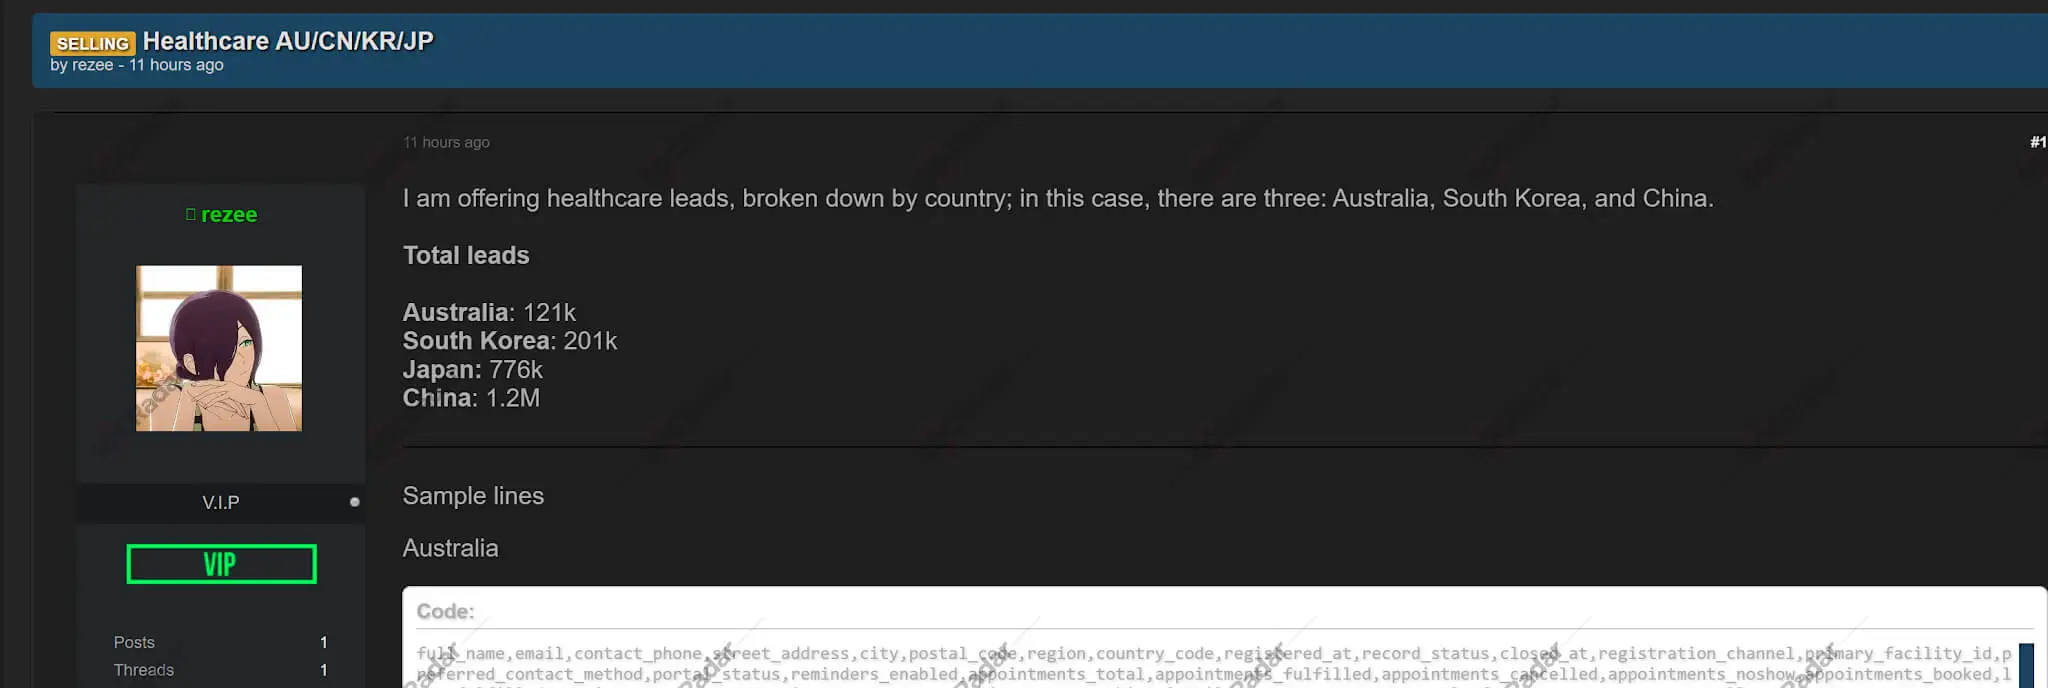
SOCRadar Dark Web Team detected a post advertising healthcare-related leads across multiple countries. The seller claimed to offer records from Australia, South Korea, Japan, and China, totaling more than 2.3 million records.
The claimed breakdown includes 121,000 records from Australia, 201,000 from South Korea, 776,000 from Japan, and 1.2 million from China. The exposed data reportedly includes names, email addresses, phone numbers, street addresses, appointment history, facility identifiers, and registration details. If valid, this could enable healthcare-themed phishing, patient impersonation, and medical fraud attempts.
Alleged KPN Netherlands Database Leak is Detected
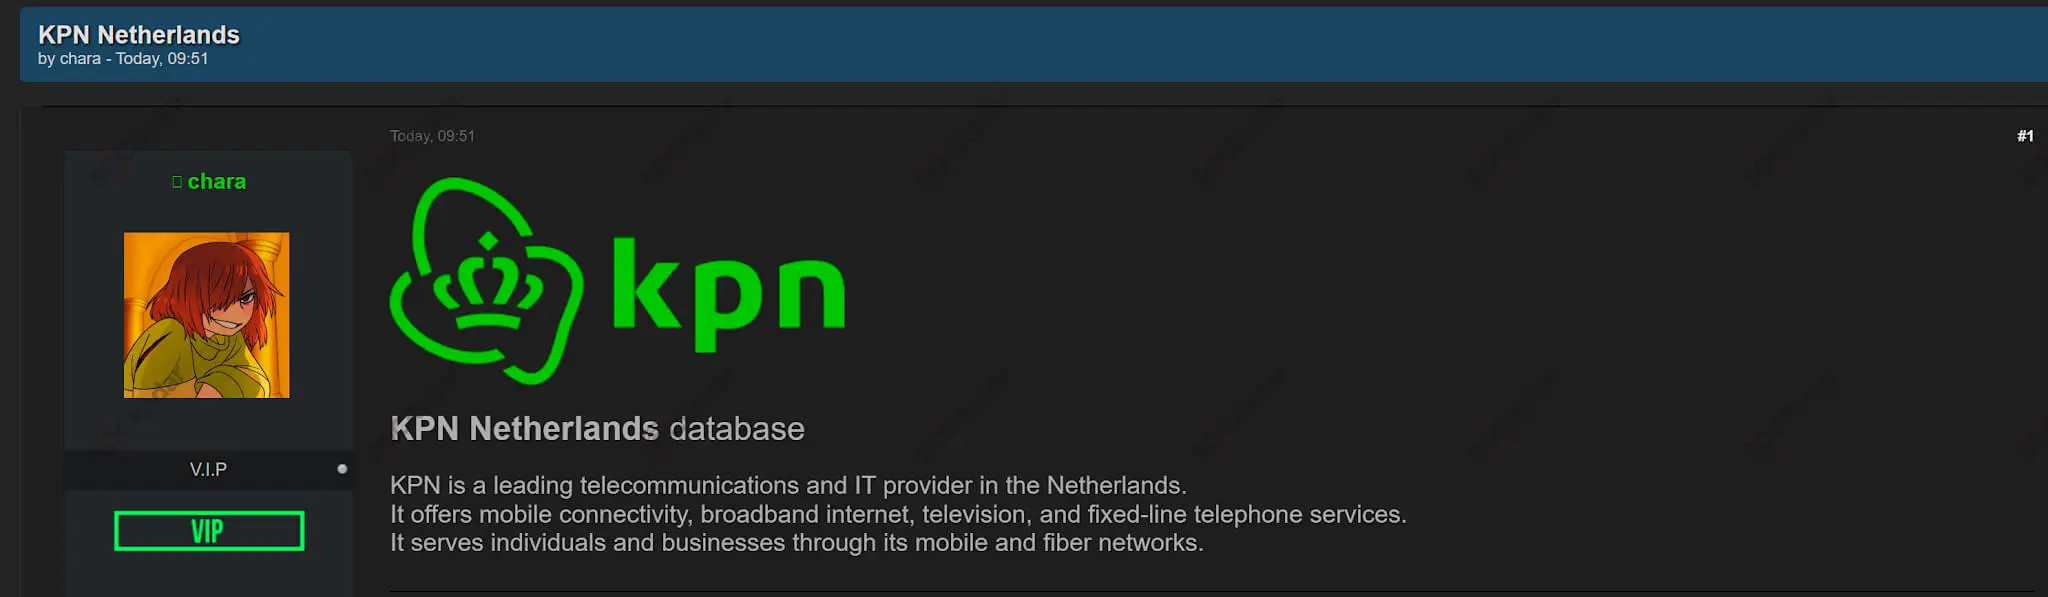
SOCRadar Dark Web Team detected a post advertising a database allegedly belonging to KPN Netherlands, a telecommunications and IT provider. The actor claimed the dataset contains 4.7 million customer records and offered it for sale for $320.
The exposed information reportedly includes full names, email addresses, phone numbers, street addresses, billing account identifiers, mobile plan details, SIM card types, data usage statistics, and contract status. If authentic, this type of telecom customer data could support highly convincing phishing, SIM-swap attempts, identity theft, and account fraud.
Alleged CafeMom Historical Breach Data Resurfaces
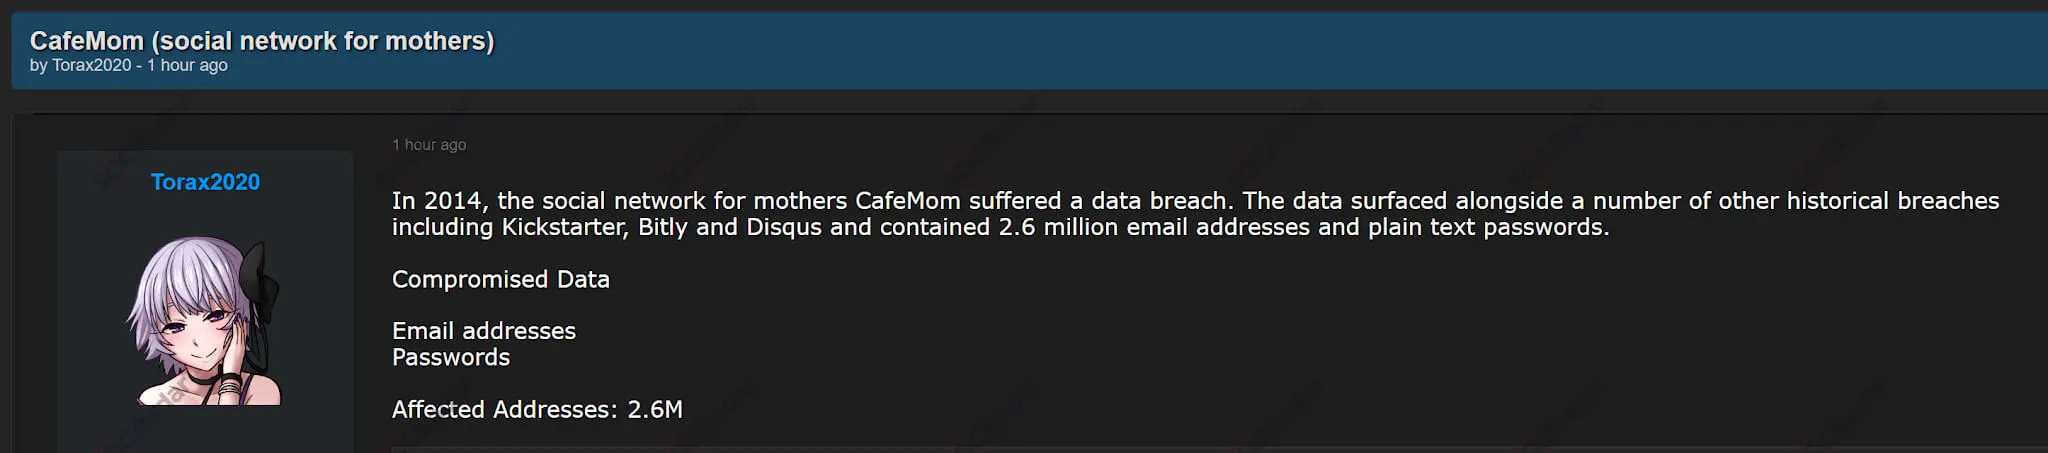
SOCRadar Dark Web Team detected a post publishing data tied to the historical 2014 CafeMom breach. The dataset reportedly contains 2.6 million email addresses and plain text passwords from the social network for mothers.
Although this is not described as a new breach, the resurfacing of plaintext credentials still presents risk for users who reused passwords on other platforms. The data reportedly appeared alongside other historical breach collections, increasing the likelihood of credential stuffing, phishing, and automated account takeover attempts.
Powered by DarkMirror™
Gaining visibility into deep and dark web threats can be extremely useful from an actionable threat intelligence and digital risk protection perspective. However, monitoring all sources is simply not feasible, which can be time-consuming and challenging. One click-by-mistake can result in malware bot infection. To tackle these challenges, SOCRadar’s DarkMirror™ screen empowers your SOC team to follow up with the latest posts of threat actors and groups filtered by the targeted country or industry.
Table Of Content
Angi Data Sale, The Tour Guy Breach, Healthcare Leads, KPN Leak, and CafeMom Data Resurface
Alleged Angi Database Sale is Detected
Alleged The Tour Guy Breach is Detected
Alleged Healthcare Leads Database is Offered for Sale
Alleged KPN Netherlands Database Leak is Detected
Alleged CafeMom Historical Breach Data Resurfaces
Related Articles
Dark Web Profile: Blue Locker Ransomware
Sep 25, 2026
ShinyHunters Claims Access to FBI Systems
Sep 24, 2026
Clop Hack: ShinyHunters Hijacks Data Leak Site
Sep 21, 2026