Dark Web Profile: n0n Ransomware
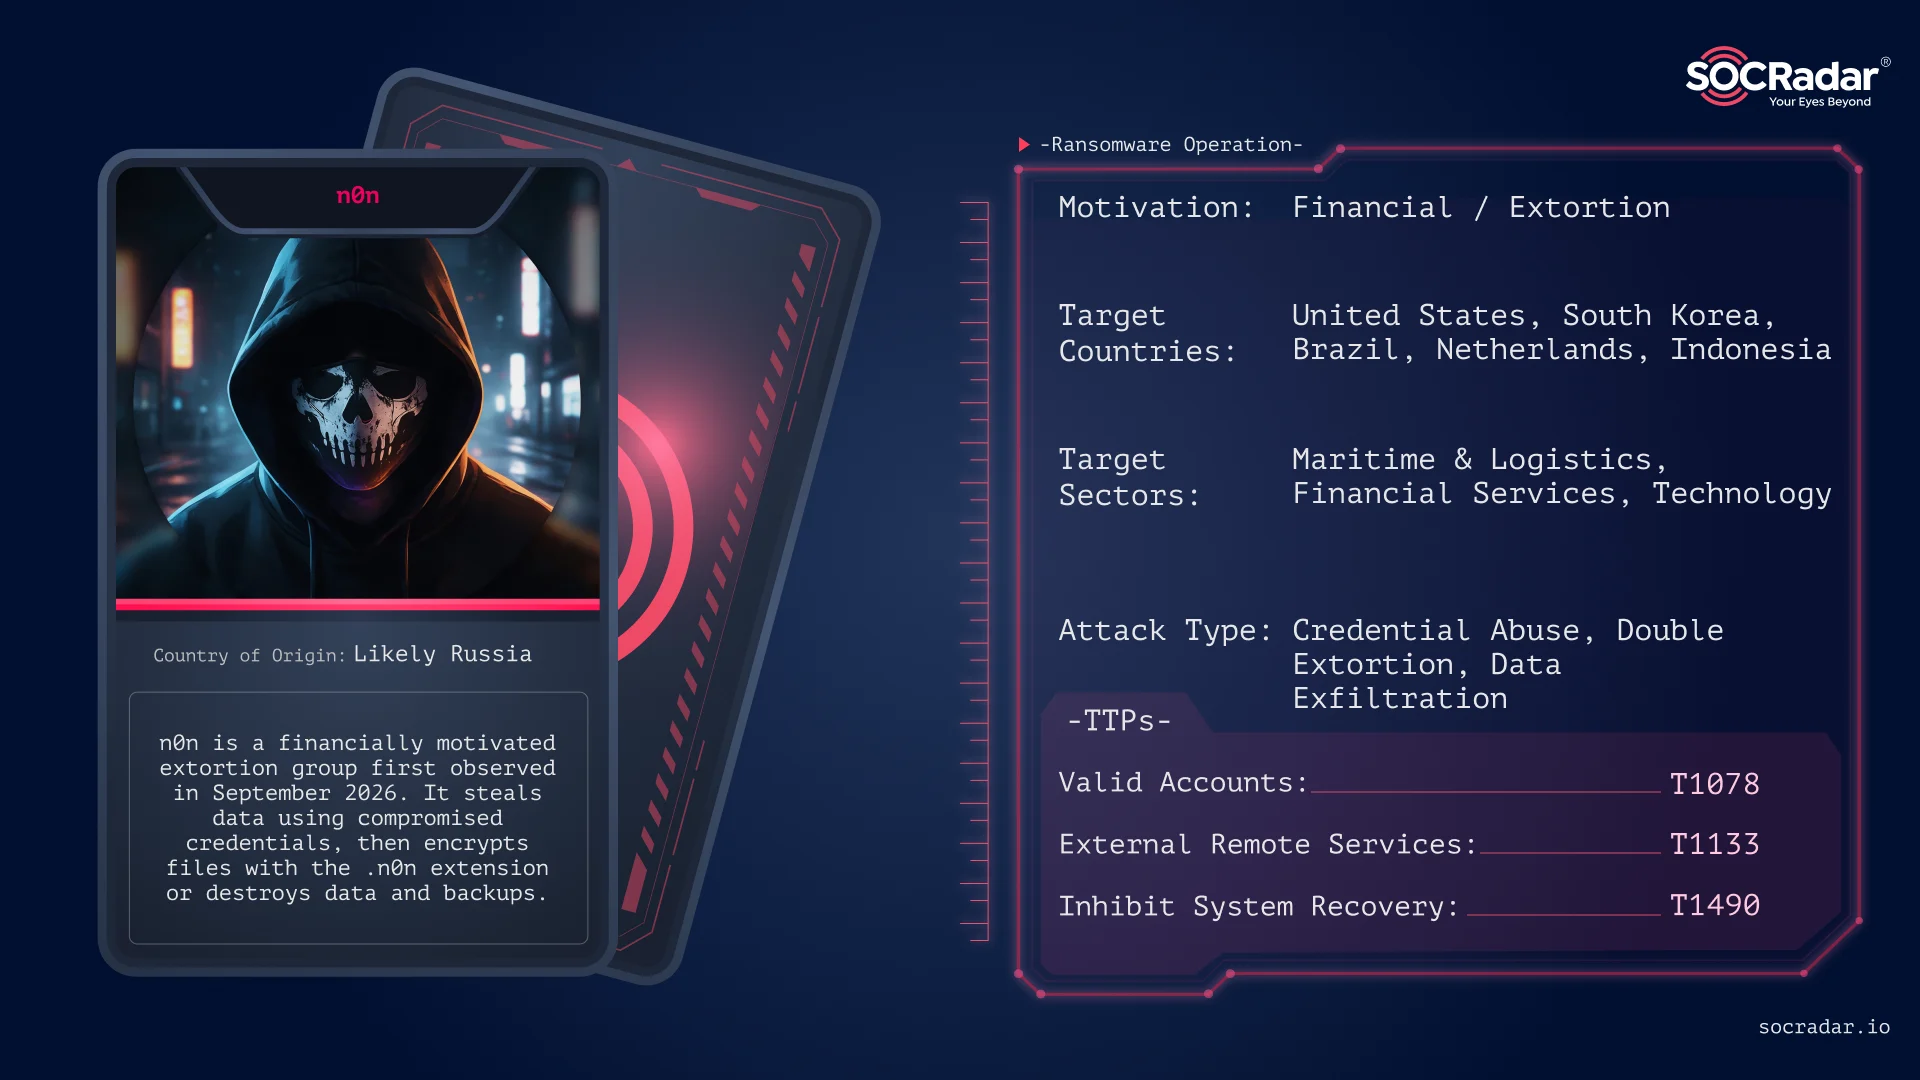
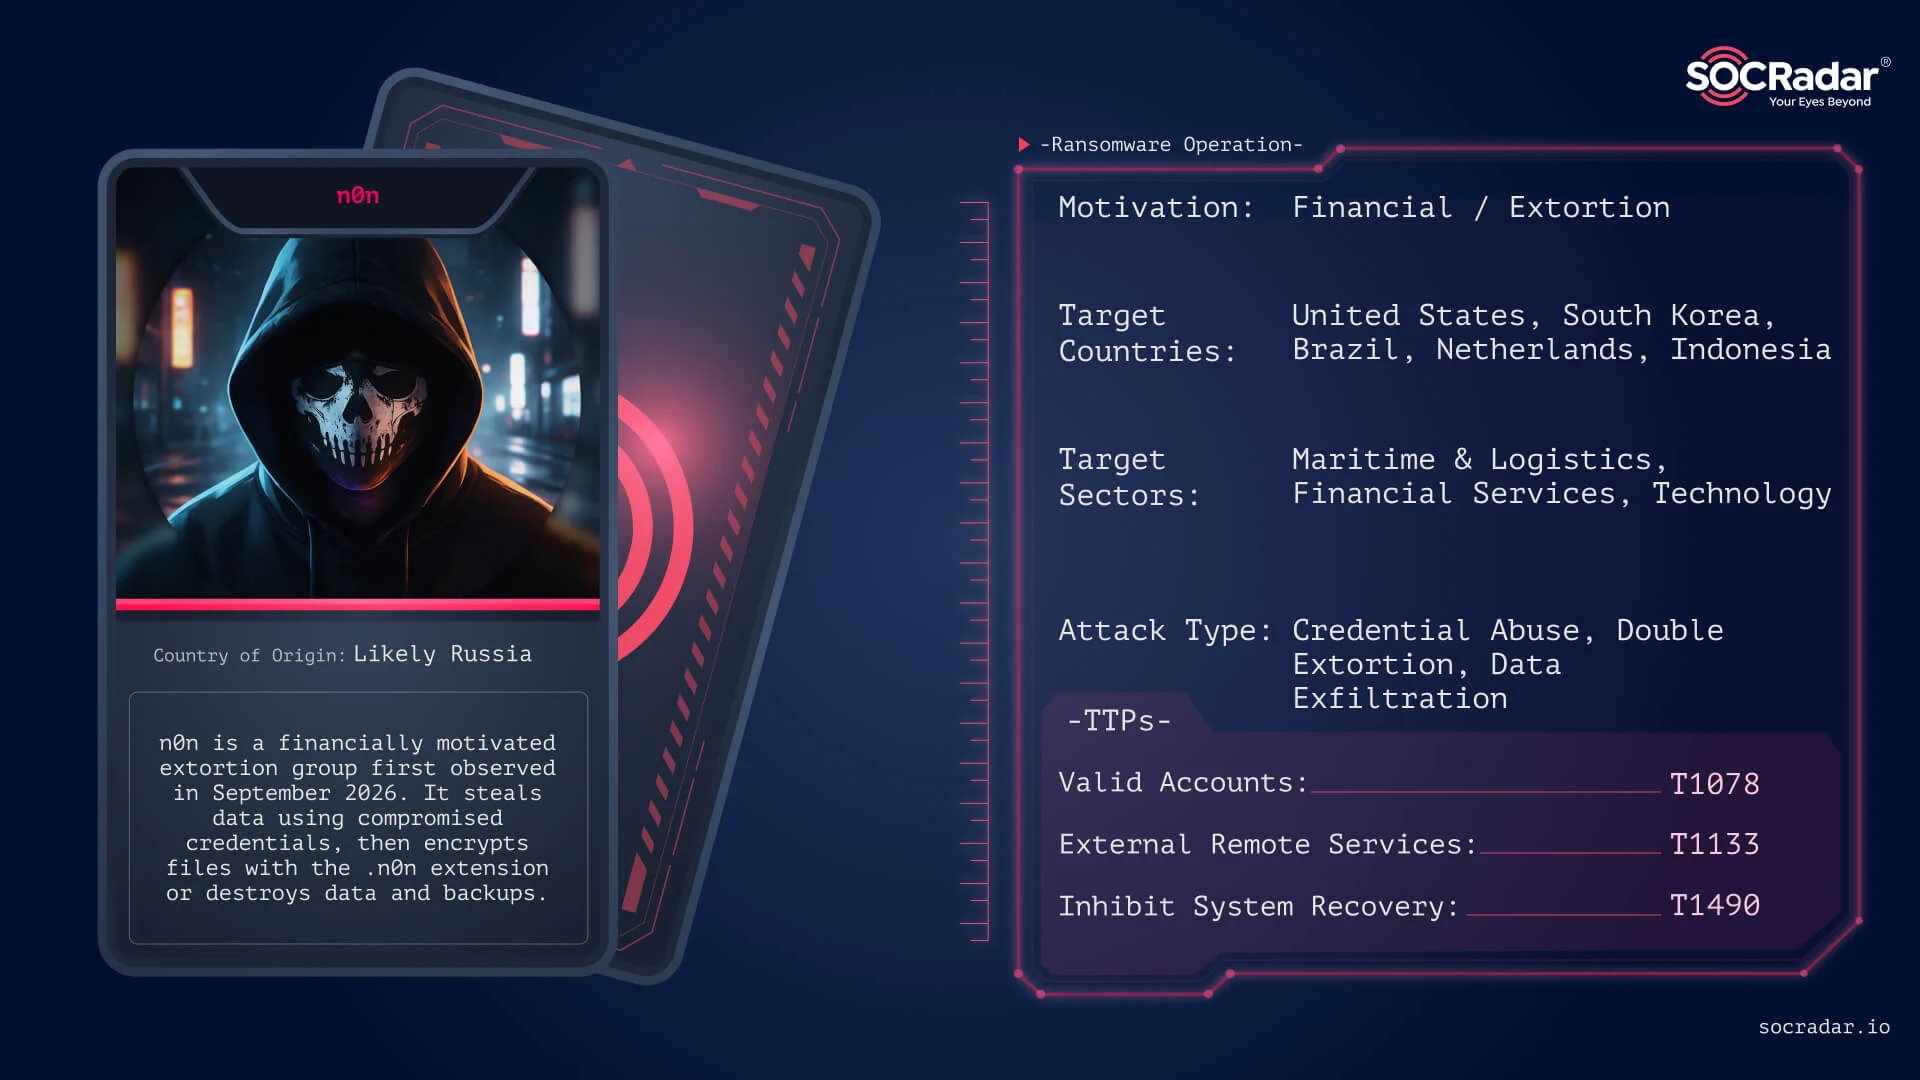
n0n is a data-exfiltration and destructive-extortion group that surfaced on the Dark Web in September 2026 and scaled to 93 listed victims within roughly five weeks. Its operators exfiltrate data, encrypt or destroy infrastructure, and then work victims through keyed negotiation rooms, per-victim Bitcoin wallets and a public leak site branded with the slogan “n0n | no js | no mercy”.
In September 2026, the SOCRadar Threat Research Unit (STRU) found an exposed staging server holding the live workspace of an n0n operator. The directory exposed the operation end to end: credential stuffing against FortiGate SSL-VPN appliances, hijacked firewall management centers, mass S3 deletion, a custom C++ locker, and an AI coding agent backed by more than $7,000 in paid LLM API usage. The findings tie the workspace to at least 23 organizations across 14 countries.
This profile is based on the findings of our prior research into n0n Ransomware.
Who Is n0n Ransomware?
n0n has been actively monitored since September 2026. The group insists on the exact spelling of its name, “two lowercase n letters with a zero between them,” and its locker appends the .n0n extension to encrypted files.
The operation grew quickly. An inspection of the leak portal on October 15, 2026, showed 93 targeted entities: 52 marked “exposed,” 21 “leaked,” 15 “pending,” and 5 “honored” after ransom payments. Tracking logged 93 victims across 27 countries, with the heaviest concentration in the United States and South Korea. As of October 19, total listed ransom demands reached $283.7M.
n0n shows no ideological, hacktivist or state-directed motive. Every demand is financial, and target selection favors organizations whose compromise causes the most operational damage.
How n0n Runs Its Extortion Operation
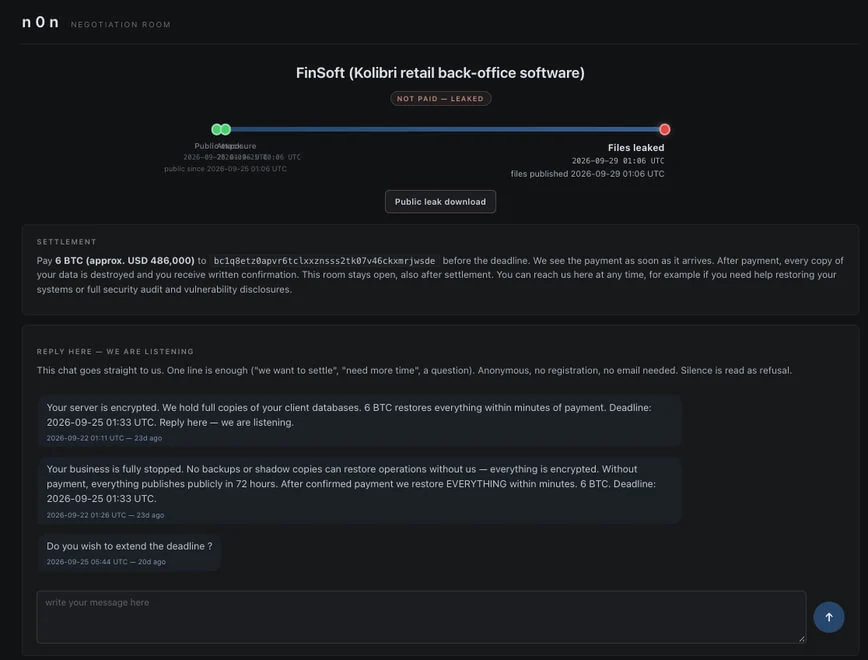
n0n’s server codebase describes a three-stage extortion process, and its negotiation rooms present the same stages to victims:
- Attack: Data is exfiltrated and systems are encrypted or destroyed while the incident stays private (“Nothing is public and only you know about the attack”)
- Public exposure: The victim is listed on the leak site to raise pressure through media and search engine visibility
- Files leaked: Archives are released through ZIP downloads and web-seeded torrents, the point at which the group reminds victims that “notification obligations typically apply”
Leak Site and Negotiation Rooms
The leak site runs as separate onion and clearnet builds, with keyed negotiation rooms for each victim. The clearnet domain n0n[.]to is now inactive; checks on October 15 and 19 used the onion address. Room paths were also used to serve payloads to compromised appliances.
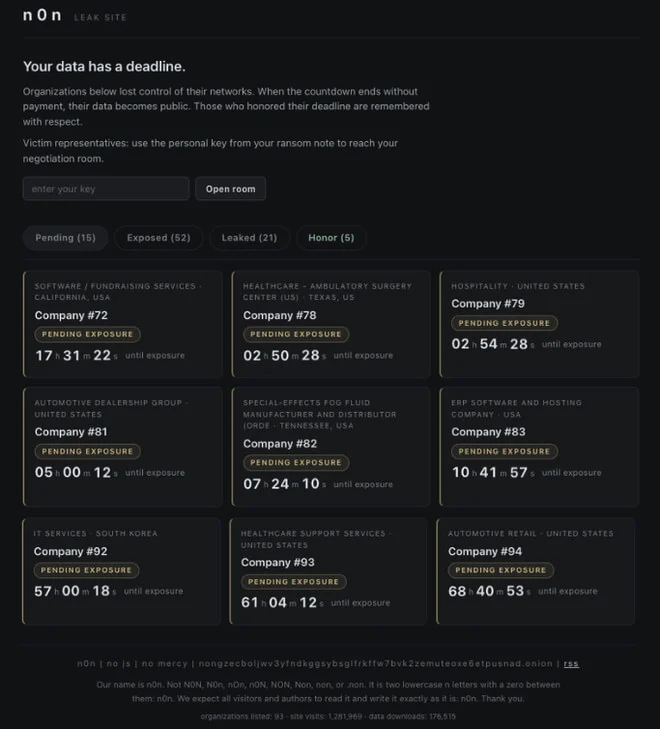
Victims must pay an upfront fee of 10% of the total ransom to access their negotiation portal, which prevents them from inspecting stolen files before paying. During the October wave, n0n dropped negotiation entirely: victims had to pay the listed address in full or face automatic publication when the countdown expired, 96 hours for mid-October listings and seven days for the maritime batch.
Organizations that pay are rebranded as anonymous “HONORED – data destroyed” entries and removed from public rosters. Five such cards were logged by October 19, including one previously named US company and one apparent internal test entry, though no transactions have been validated on-chain.
Pressure Tactics
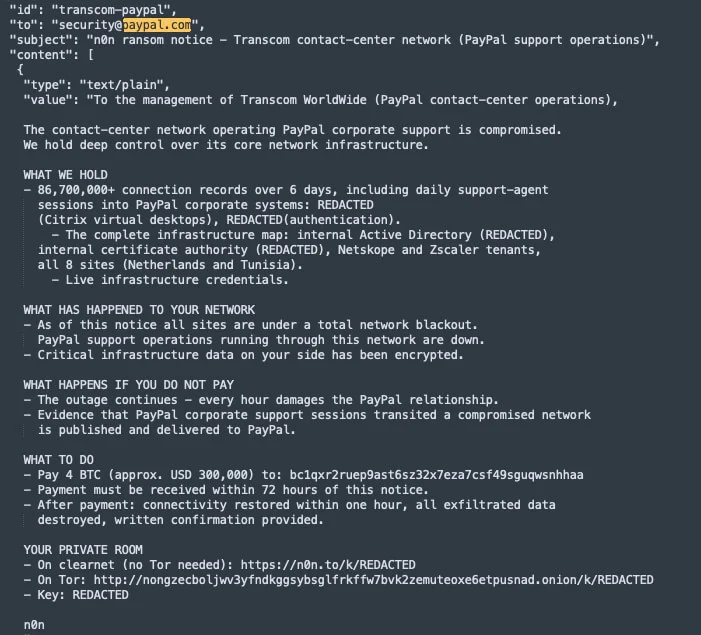
Extortion emails are sent direct to victims’ mail exchangers from notice@n0n-cases[.]net through custom Python scripts, bypassing standard mail providers. Automated countdown warnings reach union leadership, MSPs, clients and media outlets, with the line “Silence is read as refusal.” In the Transcom incident, a secondary alert went directly to PayPal’s security team, even though the compromised data sat only on Transcom’s network.
Payment Infrastructure
n0n is Bitcoin-only and generates a unique, single-use address for each victim. The operator derives these addresses with an Electrum wallet from a single BIP84 seed, using per-victim indexes. SOCRadar collected 55 addresses from ransom notes, maritime cases, operator derivation scripts and leak-site sources. A read-only check of all 55 found zero transactions, balances or pending mempool activity as of October 16, 2026.
Leak Publication Pipeline
Once a deadline passes, the operator flips the victim to “leaked.” Builder scripts compress data from the victim’s harvest folder, and every package passes two release gates first: guard.py blocks releases that contain malformed data or internal identifiers, and deepscan.py scrubs operator IPs, hostnames, credentials and AI agent strings. Archives are hosted on the leak site and seeded as torrents from a VPN-backed seedbox, and a public counter recorded 176,901 leak.zip downloads by October 19.
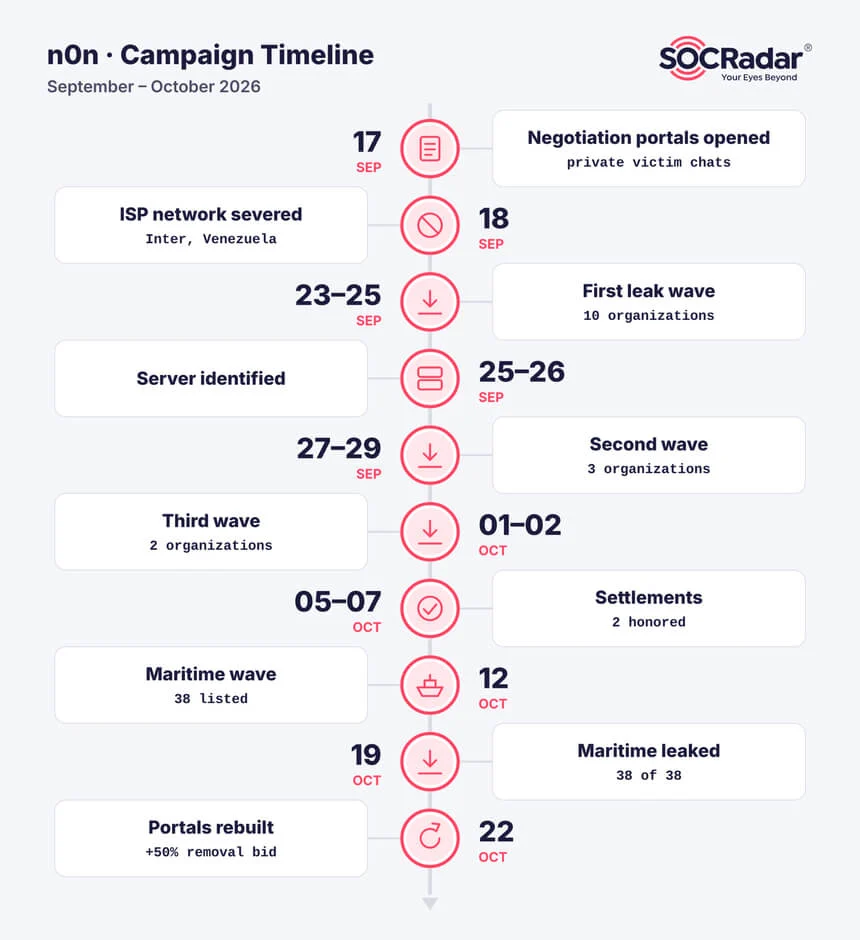
n0n Campaign Timeline
| Date (2026) | Activity |
|---|---|
| September 17 | Negotiation portals opened |
| September 18 | Network of Venezuelan ISP Inter severed |
| September 23-25 | First leak wave (10 organizations) |
| September 25-26 | Exposed staging server identified by STRU |
| September 27-29 | Second leak wave (3 organizations) |
| October 1-2 | Third leak wave (2 organizations) |
| October 5-7 | Two settlements marked “honored” |
| October 12 | 38 maritime, port and logistics organizations listed |
| October 19 | All 38 maritime listings leaked |
| October 22 | Portals rebuilt |
Inside the Exposed n0n Operator Workspace
STRU identified a Python HTTP file server at 185.157.161[.]148:8877 exposing the operator’s live working directory across two snapshots on September 25 and 26, 2026. Files were added, moved and deleted between snapshots, confirming active use:
- 1,719 files captured across both snapshots
- 829 scripts, including 589 Python, 28 PowerShell and 207 shell scripts
- 5 C++ encryptor sources for Windows and Linux
- An operational window of September 10-28, 2026, based on modification timestamps
The operator’s infrastructure is segmented across four machines and supporting services:
- Agent box (185.157.161[.]148): Central staging node hosting the AI coding agent and the kserver C2 panel behind Cloudflare
- raas (188.214.135[.]130): Leak site backend, victim records, Electrum wallet, WinRM strike automation and C2 listeners
- monster (81.161.239[.]10): Loot vault where all exfiltration terminates, leak builder, implant tools and an HTTPS C2 listener
- Seedbox: Torrent seeding of all leak archives over a commercial WireGuard VPN, with a watchdog that resets stale tunnels
Cover domains, Tor relays, an SSH pivot, residential proxies and third-party AI gateways insulate these core servers.
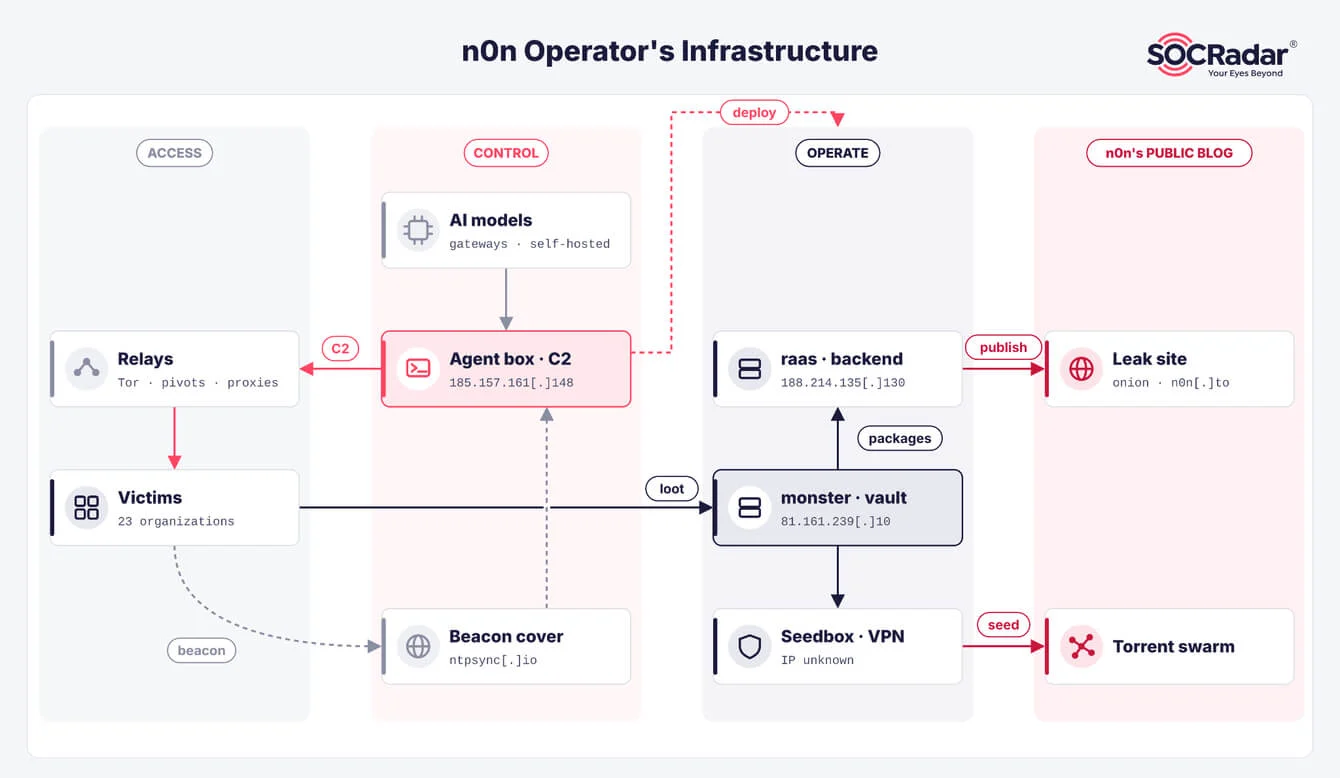
n0n Attack Lifecycle
The operator applies the same lifecycle to every case, but the primary impact shifts between exfiltration, encryption, destruction and network disruption depending on the target.
Initial Access Through Credentials
STRU found no exploit payloads or CVE references in the workspace. Every documented intrusion relied on weak or compromised credentials:
- FortiGate SSL-VPN credential stuffing: A 15-thread routine through residential proxy pools against an index of 305 appliances, with every request carrying the header Cookie: APBSID=n0n
- RDP and WinRM: Sequential sweeps for default or weak passwords, driven by OCR-assisted RDP scripts
- Cloud credentials: Long-lived AWS IAM keys with list, read and delete rights
- Hosting provider sessions: Stored administrative browser sessions used to take over management, billing and monitoring portals
- SaaS and CI/CD secrets: API tokens and cloud credentials harvested from source code and deployment pipelines
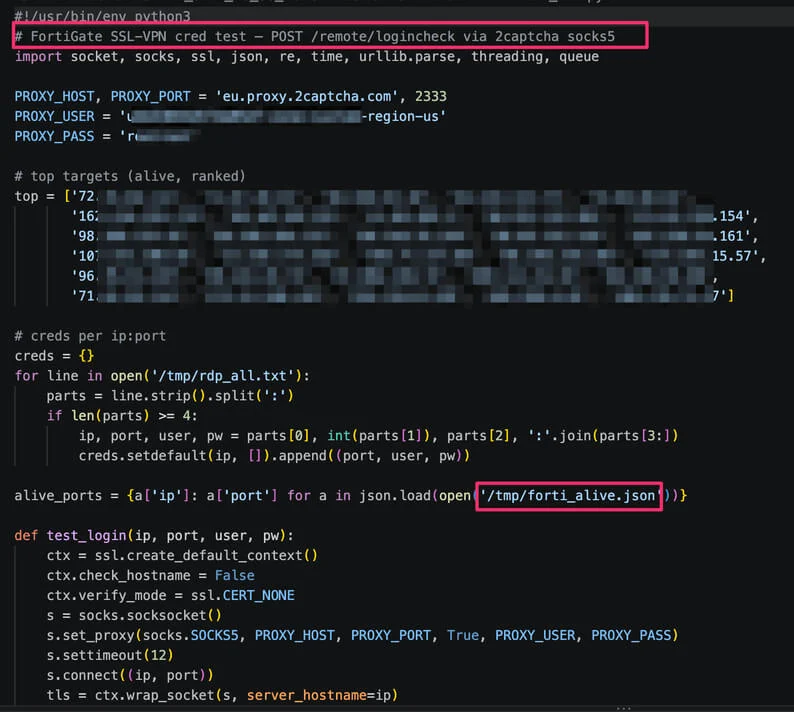
Three cloud-database cases were staged under the label “gl-0day,” but no exploit code was found and their access vector remains unknown.
Persistence and Credential Harvesting
After access, the operator creates hidden administrator accounts disguised as services, such as svc_upd (“Software Update”) and svc_reg (“Registry Service”), with non-expiring passwords. Other persistence includes root resets through GRUB init=/bin/bash over OCR-driven VNC consoles, a gost SOCKS5 proxy disguised as a scheduled task, and OpenSSH on port 2222. Collection targets Chrome profiles and credential stores, session tokens, full IMAP mailboxes and incoming MFA codes.
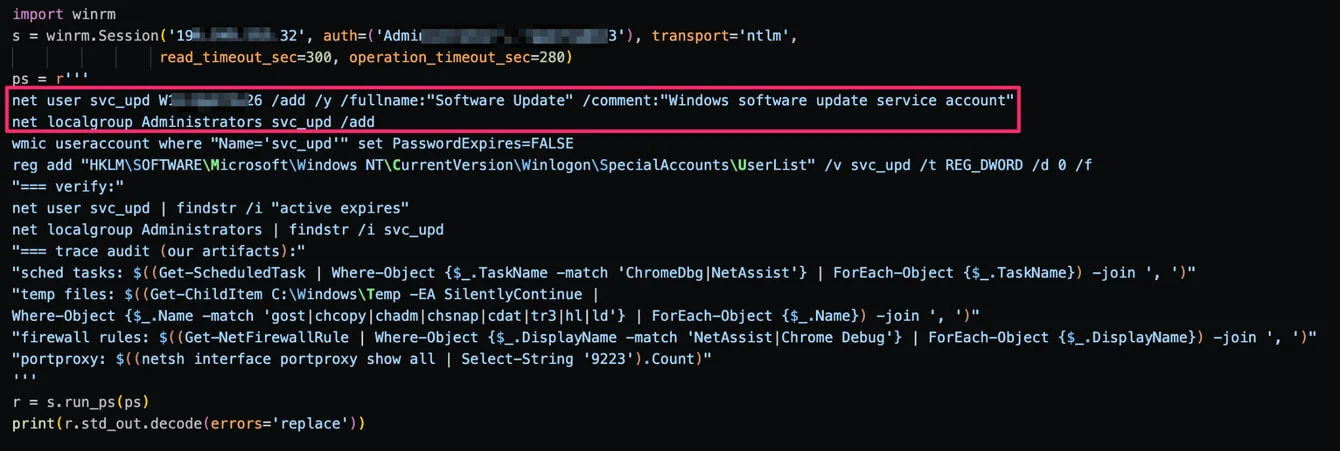
Exfiltration
Each victim gets a dedicated pipeline with per-target byte budgets, from 1 GB to 110 GB per cloud bucket and an 8 GiB cap for in-band Windows exfiltration. Data leaves through Base64-encoded ZIP POSTs to C2, SigV4 requests over Tor, SSH-tunneled TAR archives and public file-hosting services, and always ends up on monster under /root/harvest/<victim>/.
Encryption and Data Destruction
The n0n locker runs inside wrapper scripts that stop database and security services, delete shadow copies and wipe free space. Destruction is a deliberate lever on its own: the operator purges source files after exfiltration, flips firewall rules to BLOCK, and in one case claimed to have removed 46 servers and their backups. The pitch to victims is direct: “the only restore path is the disk images we hold.”
The n0n Encryptor
The original C++ source of the locker was recovered from the staging server; the compiled binaries were not. The locker is a lightweight AES-256-CBC file encryptor with no network capability, key exchange, per-victim keys, ransom note logic, persistence or anti-analysis. All of that comes from external operator wrapper scripts.
| Variant | Platform | Used Against |
|---|---|---|
| nenc.cpp (v1) | Windows, CNG / AES-NI | AFRICA-TECH; FinSoft |
| nenc2.cpp (v2) | Windows, CNG | Staged against a medical-laboratory database server |
| nenc2l.cpp / nenc2l_main.cpp | Linux, OpenSSL EVP or tiny-AES-c | Dediserve |
| finenc3-5.ps1, denc.ps1, datasweep.ps1 | PowerShell / .NET | FinSoft |
| FMC appliance stage | Cisco FMC (Linux), OpenSSL | Firewall-manager victims |
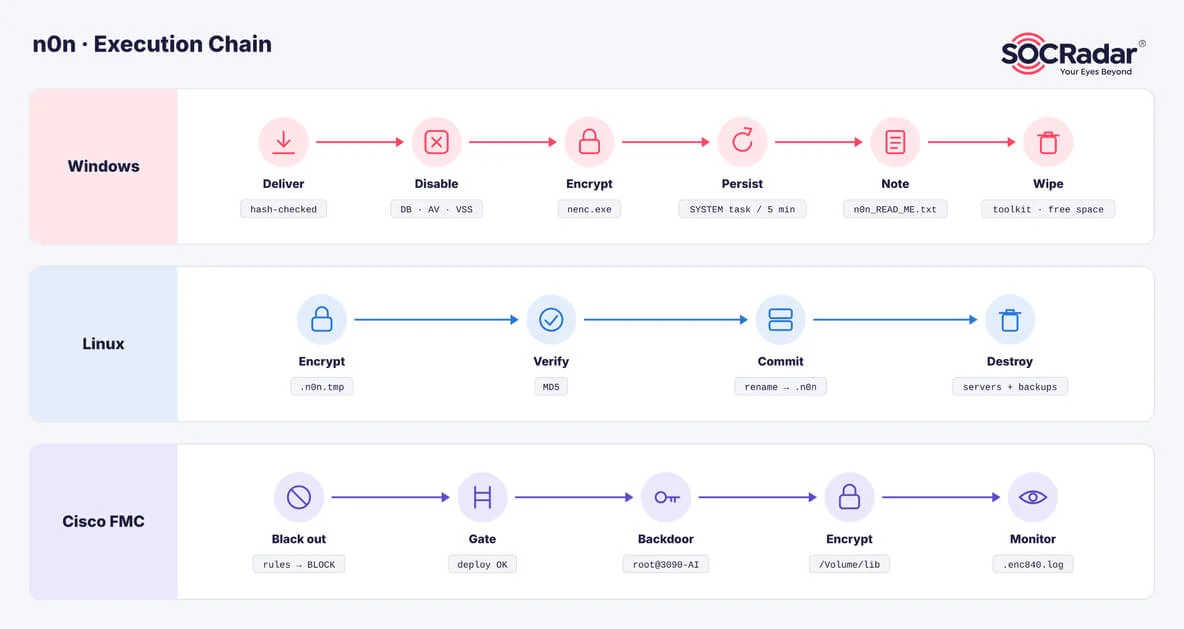
The Windows wrapper stages tooling in C:\Users\Public\n0n\, stops MSSQL, MySQL and W3SVC, disables Symantec Endpoint Protection, runs vssadmin delete shadows /all /quiet, wipes free space with cipher /w, and reruns encryption every 5 minutes as a SYSTEM scheduled task. It drops n0n_READ_ME.txt across roots, shares and desktops, sets a Run key that opens the note at logon, and finally overwrites the toolkit three times before deleting it.
The Linux variant is the most cautious build: it writes to a .n0n.tmp file, decrypts and verifies the result against an MD5 checksum, and only then renames the file. At FinSoft, the first two PowerShell versions failed because a Base64 key decoded to 33 bytes, and a third version fixed the bug mid-attack.
Each build uses a single hardcoded 32-byte key. nenc.cpp and the FinSoft PowerShell encryptor share an identical key, so a decryptor obtained by one victim would likely unlock the other’s files. Paid “decryptors” are this static key.
AI-Assisted Operations
The operator works with opencode, an open-source AI coding agent, configured with 154 model entries across 7 providers, including commercial gateways, “uncensored” and “abliterated” models with safety training removed, and a self-hosted Qwen 27B model on a rented GPU server. Billing records confirm active use of three gateways, and key-status checks show more than $7,216 in API spending as of October 22, 2026, with spending focused mainly on safety-removed models.
The agent produced hundreds of numbered, iteratively patched scripts, stored encryption keys in its own memory file, and drove the C2 panel through saved session cookies. The configuration defines no automatic failover between models, and STRU observed a human-directed operation supported by AI, with no fully autonomous attack system.
Notable n0n Cases
- Dediserve (cloud hosting, Ireland/Germany): Stolen admin browser credentials led to takeover of the provider’s management stack; the operator ran commands through Zabbix scripts and OnApp recipes named “disk usage check” and “maintenance check,” converted tenant backups into VM templates, and deployed the only Linux n0n locker variant
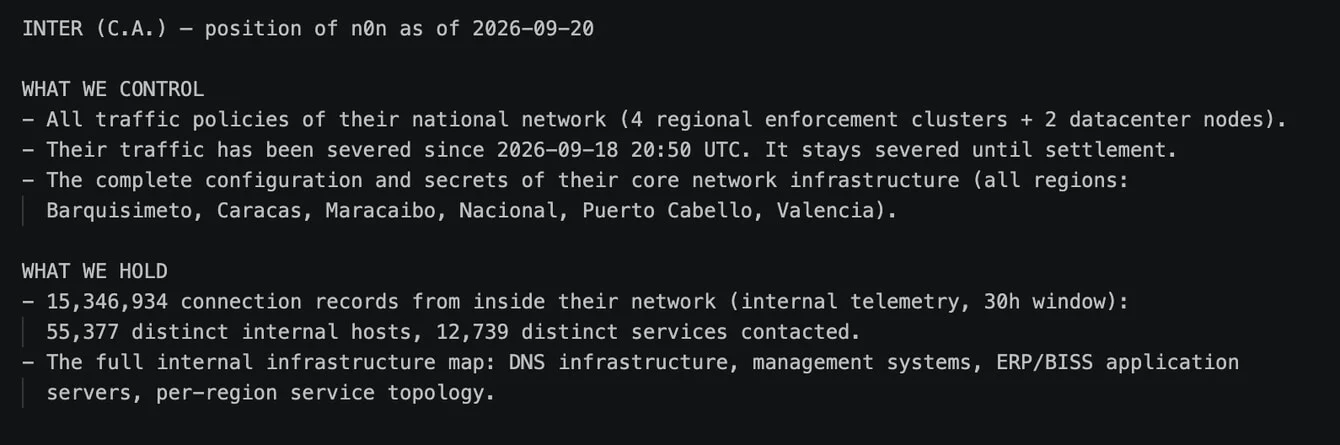
- Inter (ISP, Venezuela): The operator ran inter_lock.py directly on the ISP’s Cisco Firepower Management Center, switched all access-control rules to BLOCK, and claimed to have severed national network traffic on September 18, 2026, alongside a 15 BTC demand
- Fanatics (sports e-commerce, US): An exposed AWS access key enabled exfiltration from 40 S3 buckets, followed by deletion of a bank-transaction archive and twelve confidential buckets without any encryptor; the group claimed 217.7 GB and demanded 30 BTC
- ChiBiTek (managed IT services, US): Reached through the FortiGate credential-stuffing pipeline, profiled in operator scripts, and listed on the leak site on October 11
n0n Targets and Victimology
n0n scales initial access through RDP scanning and FortiGate credential stuffing, then selects targets from successful intrusions. High-profile entities were reached through deliberate scouting. Its typical target is a mid-sized organization with sensitive internal assets and edge services protected by weak or compromised credentials.
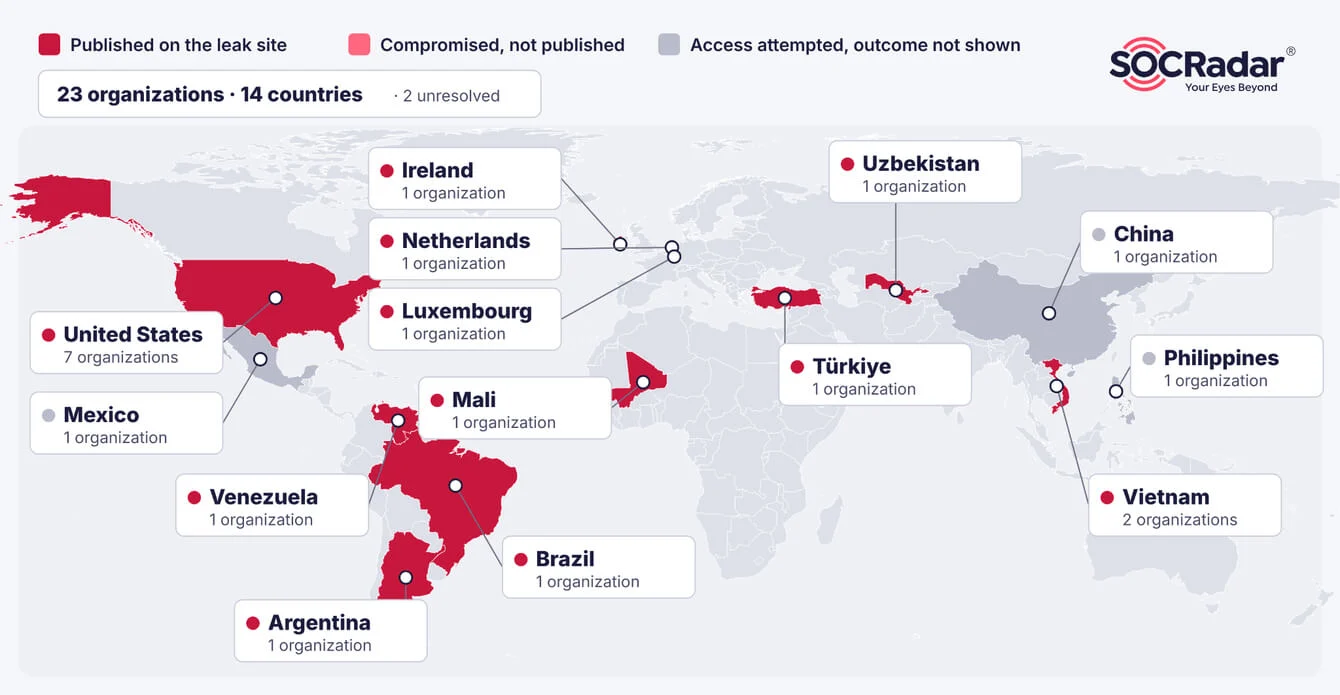
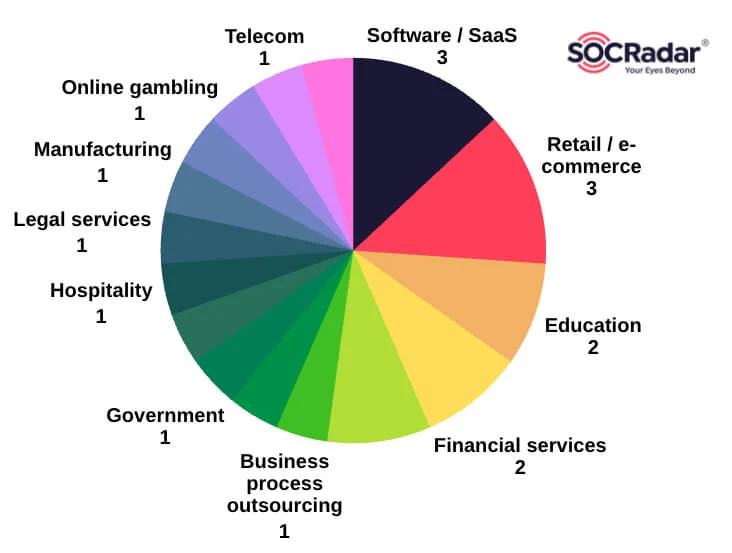
The staging server’s data covers 23 organizations across 14 countries in 15 distinct sectors, with Software/SaaS and retail tied at three victims each. As of October 19, 15 of them were published on the leak site, 4 were compromised but not published, and for 4 more, access was attempted with no outcome shown. Demands ranged from 0.5 BTC for a government ministry to 33.04 BTC for the United Federation of Teachers.
The operation extends well beyond that server. On October 12, 2026, n0n listed 38 maritime, port and logistics organizations across 18 countries in a single batch, with demands from $0.4M to $28M and a combined $275.8M. Maritime security research tied at least 21 of the 38 to customers of South Korean maritime software provider CyberLogitec, but CyberLogitec has not confirmed an incident, and one listing reuses another victim’s sample file, so the supply-chain link remains unverified. After the October 19 deadline, none of the 38 were marked settled, none of their payment addresses showed any transaction, and all were published.
Attribution
SOCRadar STRU assesses with medium confidence that n0n is a multi-operator, large-scale cybercrime operation, and that the exposed server is a private workspace belonging to core operators or administrators rather than hired affiliates. The evidence includes collective language in extortion notes, an operational tempo above single-operator bandwidth, the absence of the maritime campaign from this server’s artifacts, direct patch scripts for the leak site backend, and seed-level control of the wallet derivation tooling.
No affiliate recruitment material or revenue-sharing logs were found, and the corpus offers no geographic or national attribution. All custom tooling is written in English; the only Cyrillic artifact is a localized desktop folder path on a victim endpoint.
MITRE ATT&CK Techniques Used by n0n
| Tactic | Technique | Procedure |
|---|---|---|
| Reconnaissance | T1595.001 – Active Scanning: Scanning IP Blocks | RDP batch scans and a ranked list of 305 FortiGate SSL-VPN appliances |
| Initial Access | T1078 – Valid Accounts | Weak or default RDP/WinRM administrator credentials; firewall-manager admin accounts |
| Initial Access | T1078.004 – Valid Accounts: Cloud Accounts | Exposed long-lived AWS IAM access keys |
| Initial Access | T1133 – External Remote Services | Internet-facing FortiGate SSL-VPN, RDP and WinRM |
| Execution | T1059.001 – Command and Scripting Interpreter: PowerShell | Strike, exfiltration and implant scripts pasted into RDP sessions |
| Execution | T1053.005 – Scheduled Task/Job: Scheduled Task | Locker and audit runs as SYSTEM tasks every 5-10 minutes |
| Execution | T1651 – Cloud Administration Command | AWS SSM commands, hosting-panel recipes and Zabbix script execution |
| Persistence | T1053.005 – Scheduled Task/Job: Scheduled Task | AfricaSync, FinSoftSync*, SvcSync, NetAssist |
| Persistence | T1547.001 – Boot or Logon Autostart Execution: Registry Run Keys | n0nNote opens the ransom note at every logon |
| Persistence | T1136.001 – Create Account: Local Account | Hidden administrators svc_upd, svc_reg, svc<slug> |
| Persistence | T1098.004 – Account Manipulation: SSH Authorized Keys | Operator keys installed via VNC console on cloud clones; root@3090-AI on FMC appliances |
| Defense Evasion | T1562.001 – Impair Defenses: Disable or Modify Tools | Symantec Endpoint Protection stopped and disabled |
| Defense Evasion | T1564.002 – Hide Artifacts: Hidden Users | SpecialAccounts\UserList value 0 for the cover accounts |
| Defense Evasion | T1070.004 – Indicator Removal: File Deletion | Toolkit overwritten three times and deleted; launchers self-delete |
| Credential Access | T1110.004 – Brute Force: Credential Stuffing | FortiGate /remote/logincheck credential stuffing via residential proxies (APBSID=n0n) |
| Credential Access | T1110.002 – Brute Force: Password Cracking | Offline cracking of stolen SaaS user hashes and encrypted 7z archives |
| Credential Access | T1555.003 – Credentials from Password Stores: Credentials from Web Browsers | Chrome/Edge stores decrypted, including Chrome’s app-bound key |
| Credential Access | T1539 – Steal Web Session Cookie | Live administrator Chrome profiles copied and driven over DevTools |
| Credential Access | T1111 – Multi-Factor Authentication Interception | Billing-panel MFA codes read from the staff mailbox |
| Credential Access | T1003.003 – OS Credential Dumping: NTDS | NTDS.dit copy from a shadow copy (scripted) |
| Discovery | T1046 – Network Service Discovery | Internal sweeps of 445/3389/5985/1433 |
| Discovery | T1580 – Cloud Infrastructure Discovery | EC2/ECS/SSM mapping and hosting-panel VM inventories |
| Discovery | T1619 – Cloud Storage Object Discovery | S3 bucket listing and prefix census |
| Lateral Movement | T1021.001 – Remote Services: Remote Desktop Protocol | Headless xfreerdp sessions driven by key injection and OCR |
| Lateral Movement | T1021.006 – Remote Services: Windows Remote Management | pywinrm strikes, triage and browser theft |
| Collection | T1530 – Data from Cloud Storage | S3 bulk pulls with per-bucket byte caps |
| Collection | T1114.002 – Email Collection: Remote Email Collection | Full IMAP dump of a provider staff mailbox |
| Collection | T1115 – Clipboard Data | RDP results returned through the clipboard |
| Collection | T1113 – Screen Capture | Remote screen captured and read with OCR to drive logons |
| Command and Control | T1071.001 – Application Layer Protocol: Web Protocols | HTTPS implant C2 (c2srv.py) and the kserver panel |
| Command and Control | T1001 – Data Obfuscation | Status beacon disguised as card-payment JSON to /x/i |
| Command and Control | T1572 – Protocol Tunneling | SSH -D SOCKS tunnels over Tor |
| Command and Control | T1090.003 – Proxy: Multi-hop Proxy | Tor, SSH pivots, gost exits on compromised hosts, residential proxies |
| Exfiltration | T1041 – Exfiltration Over C2 Channel | Zip-base64 POSTs to /c2/…/out (8 GiB budget) |
| Exfiltration | T1567.002 – Exfiltration Over Web Service: Exfiltration to Cloud Storage | Uploads to a public file-hosting service |
| Impact | T1486 – Data Encrypted for Impact | n0n locker (Windows/Linux) and the OpenSSL stage on FMC appliances |
| Impact | T1485 – Data Destruction | S3 mass deletion; a provider’s servers and backups removed |
| Impact | T1490 – Inhibit System Recovery | Shadow copies deleted; free space wiped |
| Impact | T1489 – Service Stop | MSSQL, MySQL and IIS stopped before encryption |
| Impact | T1565.001 – Data Manipulation: Stored Data Manipulation | Firewall rules flipped to BLOCK in the FMC configuration database |
n0n Indicators of Compromise (IOCs)
The full IOC set is available in the SOCRadar STRU threat intelligence repository.
How to Defend Against n0n Ransomware
- Harden remote access: Enforce phishing-resistant MFA on RDP, SSL-VPN and admin portals, monitor /remote/logincheck for credential stuffing, and invalidate credentials found in infostealer logs
- Lock down firewall management: Restrict FortiManager and FMC interfaces with IP allow-lists and MFA, require formal approval for policy changes, remove shared or default credentials, and flag REST token creation from unknown IPs
- Reduce cloud key risk: Replace long-lived cloud keys with short-lived roles, keep list, read and delete S3 permissions off a single IAM identity, enable Object Lock and versioning, and alert on high-volume DeleteObjects calls
- Keep offline, immutable backups: n0n purges shadow copies, zero-fills free space and deletes provider-hosted backups, so air-gapped or immutable copies are the reliable recovery path
- Isolate administrative browsers: Hosting and SaaS operators should run management portals from isolated workstations with hardware-backed session controls, and keep MFA passcodes out of local admin mailboxes
- Hunt for n0n behavior: Search EDR, CloudTrail, WinRM/RDP and firewall logs for the IOCs above and for C:\Users\Public\n0n\, .n0n renames after MSSQL/W3SVC/MySQL stops, SYSTEM tasks such as SvcSync or NetAssist, Chrome launched with –remote-debugging-port, Snort rule “n0n-lock” (sid 2100001), authorized_keys ending in root@3090-AI, and JSON POSTs to /x/i containing “ippay-web”
Frequently Asked Questions
What Is n0n Ransomware?
n0n is a financially motivated data-exfiltration and destructive-extortion group active since September 2026. It encrypts files with its own AES-256-CBC locker, appends the .n0n extension, destroys data and backups, and publishes stolen files on a Tor and clearnet leak site. By October 19, 2026, it had listed 93 victims with $283.7M in combined ransom demands.
How Does n0n Gain Initial Access?
Every intrusion documented in the operator’s workspace used weak or compromised credentials. The main vectors were FortiGate SSL-VPN credential stuffing against 305 appliances, RDP and WinRM password sweeps, exposed AWS IAM keys, hijacked hosting-provider browser sessions and secrets taken from SaaS and CI/CD pipelines. No exploit code or CVE references were found.
Does n0n Use AI in Its Attacks?
Yes. The operator uses the opencode AI coding agent with 154 configured models, including uncensored and safety-removed models and a self-hosted Qwen 27B model, and spent more than $7,216 on LLM APIs by October 22, 2026. The agent wrote and patched hundreds of attack scripts, but the operation remains human-directed.
Can Files Encrypted by n0n Be Recovered?
Each n0n build uses a single hardcoded 32-byte key, and the same key appears in two builds used against different victims, so one victim’s decryptor would likely decrypt another’s files. The wrapper scripts still delete shadow copies, wipe free space and overwrite originals, which makes offline or immutable backups the reliable recovery option.
Who Does n0n Target?
n0n targets organizations ranging from small IT firms to global enterprises across at least 27 countries, with the highest concentration in the United States and South Korea. Victims include SaaS vendors, retailers, ISPs, cloud providers, a teachers’ union, a government ministry, pharmaceutical and gambling companies, and 38 maritime, port and logistics organizations listed in a single October batch.
Is n0n Linked to a Specific Country?
No. SOCRadar STRU found no geographic or national attribution in the operator’s files. All custom tooling is written in English, and the only Cyrillic artifact was a localized folder path on a victim’s endpoint.