n0n Ransomware: Inside an AI-Assisted Extortion Operation
In September 2026, the SOCRadar Threat Research Unit (STRU) discovered an exposed staging server holding the live workspace of an operator tied to the n0n ransomware group. The open directory exposed the operation’s full September workflow: breach and exfiltration tooling, original locker source code, extortion infrastructure, and an AI coding agent environment backed by more than $7,000 in paid LLM API usage.
The findings implicate at least 23 organizations across 14 countries, including a US sports retailer, a cloud provider, a teachers’ union, a Venezuelan ISP, an Argentine ministry and a pharmaceutical subsidiary. No vulnerability exploitation was identified: every documented compromise relied on weak or stolen credentials. Where n0n does not encrypt, it destroys data and backups after exfiltration.
This post summarizes the research. The full technical analysis, including locker internals, per-victim case studies and the complete operator toolkit, is available in the whitepaper, Automating Extortion: Inside an AI-Assisted n0n Ransomware Operation.
Key Takeaways
- Exposed workspace: An open directory at 185.157.161[.]148 exposed 1,719 files from a n0n operator’s workspace across two September 2026 snapshots, including 829 scripts and 5 C++ encryptor sources
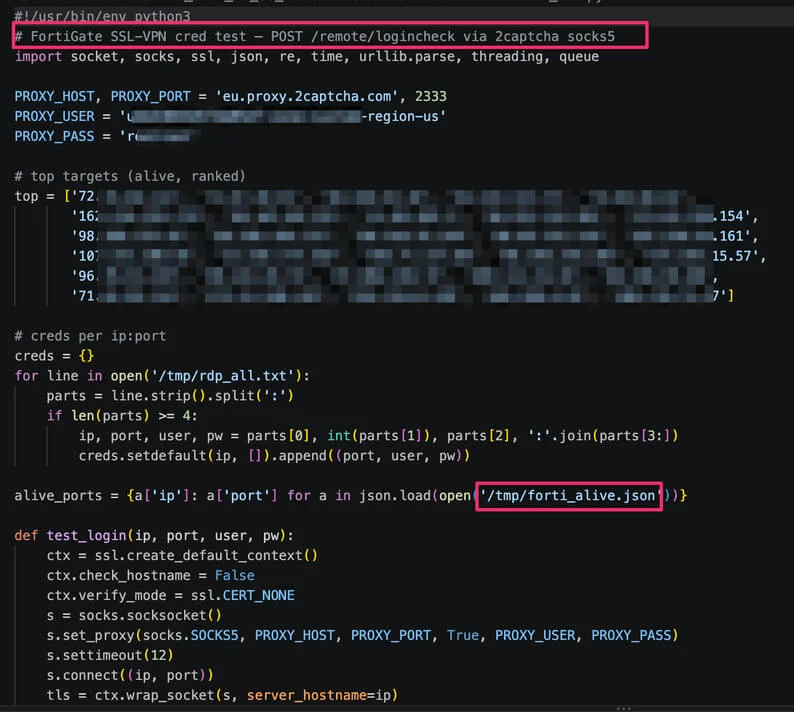
- Credential-only access: Entry points included a credential stuffing campaign against 305 FortiGate SSL-VPN devices, exposed AWS keys, weak RDP/WinRM credentials and compromised hosting management portals
- Security tools turned against victims: The operator hijacked Cisco Firepower Management Center instances to switch all access policies to BLOCK, which the actor claimed caused widespread service disruption
- AI-built tooling: An AI coding agent configured with about 150 models produced hundreds of attack scripts, with more than $7,216 in usage costs
- Scale: As of October 19, n0n listed 93 victims with total ransom demands of $283.7M
Who Is n0n?
n0n is a data-exfiltration and destructive-extortion actor tracked by SOCRadar since September 2026. The group insists on the exact spelling of its name, “two lowercase n letters with a zero between them,” uses the slogan “n0n | no js | no mercy” across its Tor and clearnet portals, and appends the .n0n extension to encrypted files.
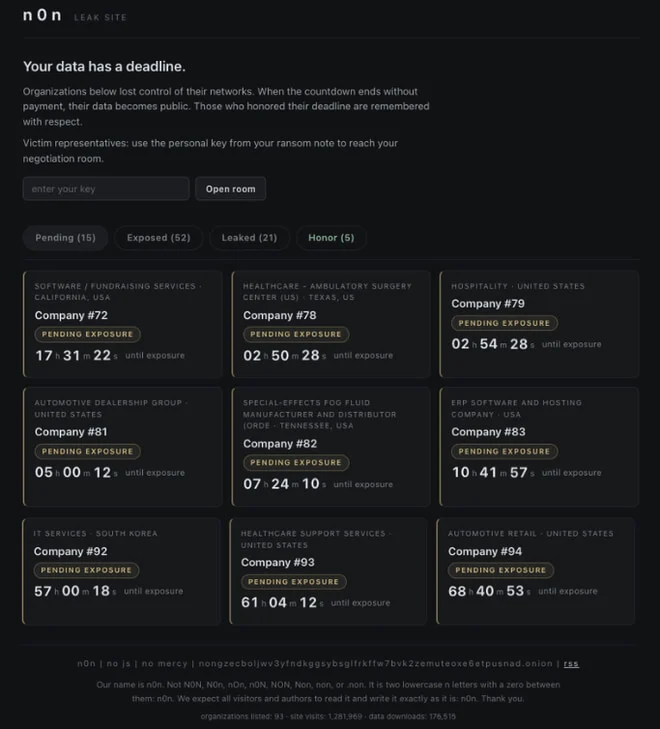
The operation has scaled quickly. On October 12, 2026, the group added 38 maritime, port and logistics organizations across 18 countries to its Dark Web leak site in a single batch. Maritime security research linked at least 21 of them to customers of South Korean maritime software provider CyberLogitec, though CyberLogitec has not confirmed an incident and the supply-chain connection remains unverified. None of the 38 listings was marked as settled after the October 19 deadline, and all were published.
Discovery and Infrastructure
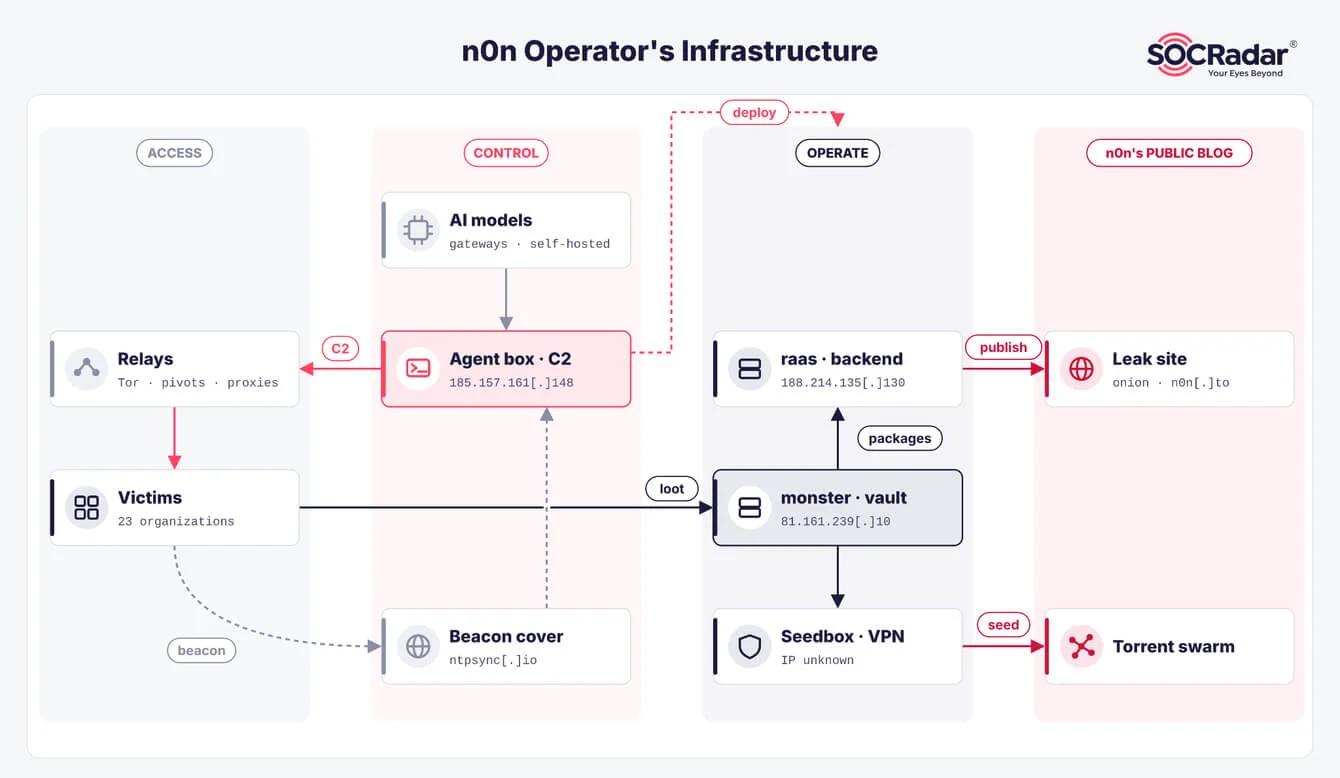
STRU found a Python HTTP file server on 185.157.161[.]148:8877 (AS42675, Sweden) exposing the operator’s working directory in two snapshots on September 25 and 26, 2026. The files map a segmented setup: an agent box hosting the AI coding agent and C2 panel, a “raas” node running the leak site backend and per-victim Bitcoin wallet generation, a “monster” server where all stolen data lands, and a VPN-bound seedbox that distributes leak torrents.
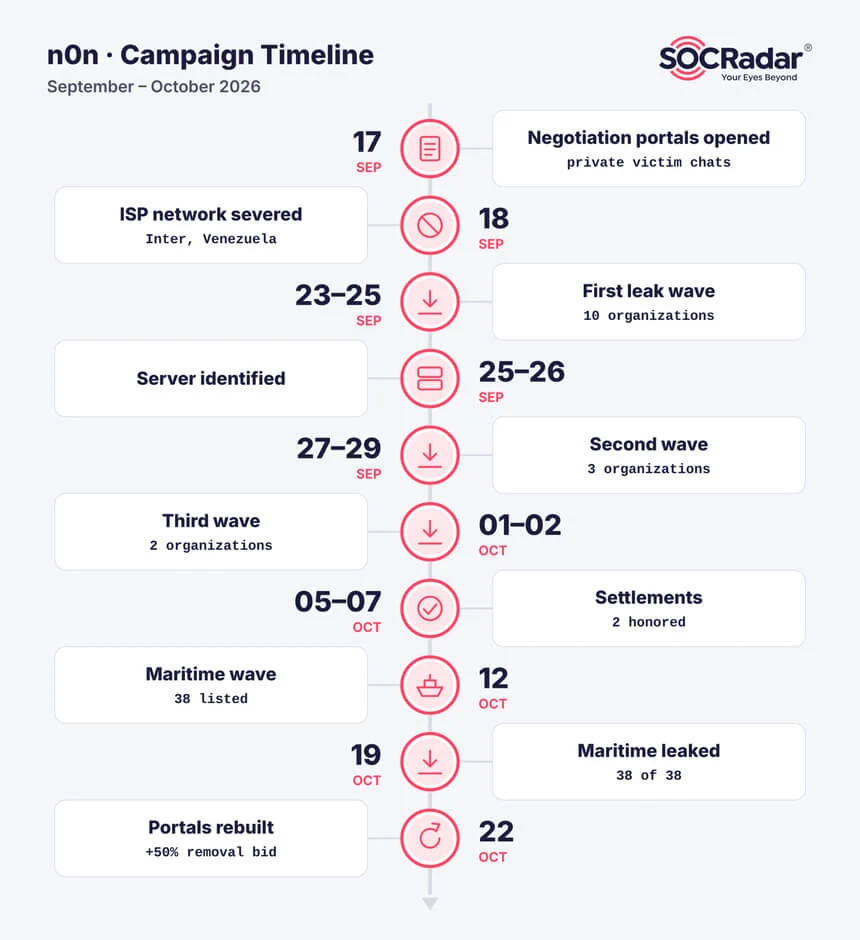
Campaign Timeline
n0n’s tracked operations ran from September 17 to October 22, 2026. Across three publication rounds and the ChiBiTek listing on October 11, the group exposed 15 of the 23 organizations identified in the workspace, typically leaking data four days after public disclosure.
Modus Operandi
Every case follows the same lifecycle, with the main impact shifting between exfiltration, encryption, destruction and network disruption depending on the target.
- Initial access: Credential stuffing against 305 FortiGate SSL-VPN appliances through residential proxies, plus weak RDP/WinRM credentials, exposed AWS keys and reused hosting portal sessions
- Persistence and collection: Hidden admin accounts disguised as services, covert proxies, and theft of browser credentials, session tokens, mailboxes and emailed MFA codes
- Exfiltration: Per-target pipelines with data budgets, sending everything to the operator’s central storage
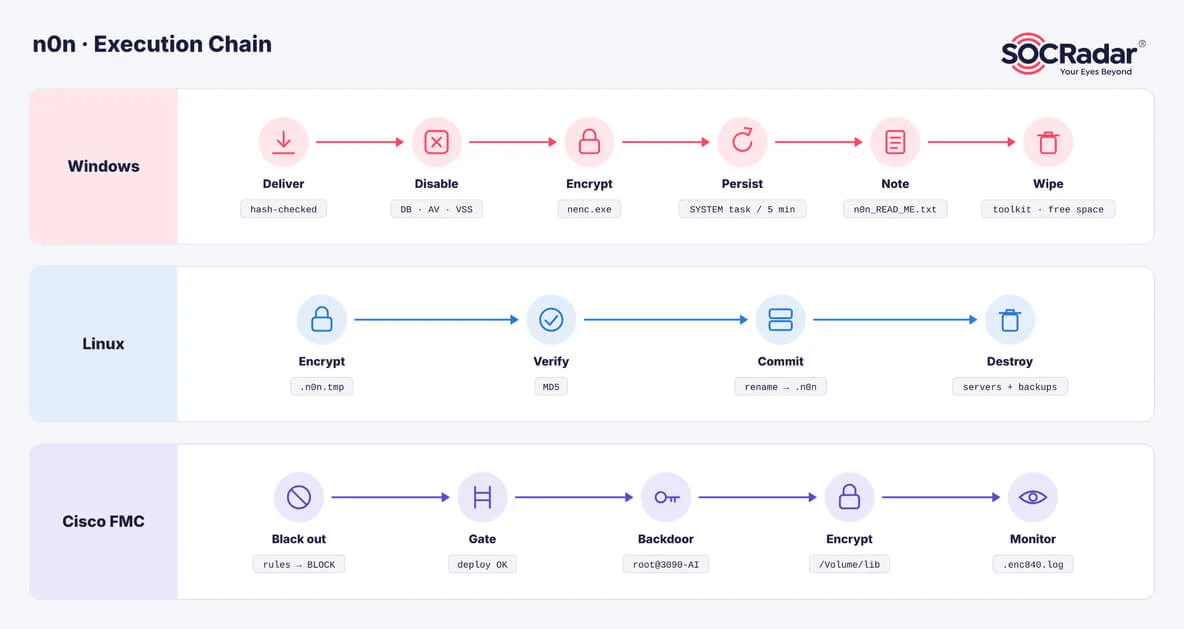
- Encryption and destruction: Wrapper scripts stop services, delete shadow copies and wipe free space before the locker runs; in some cases, the operator deleted data and backups instead of encrypting
- Extortion and publication: Ransom notes, countdowns, negotiation rooms and direct extortion emails, followed by scrubbed ZIP and torrent leaks
The n0n Encryptor
The locker is a lightweight AES-256-CBC encryptor with Windows, Linux and PowerShell variants, plus an OpenSSL stage for firewall appliances. Most destructive steps live in external wrapper scripts. Each build uses a single hardcoded key, and one key is likely shared across two victims, so a decryptor for one could unlock the other.
Extortion Playbook
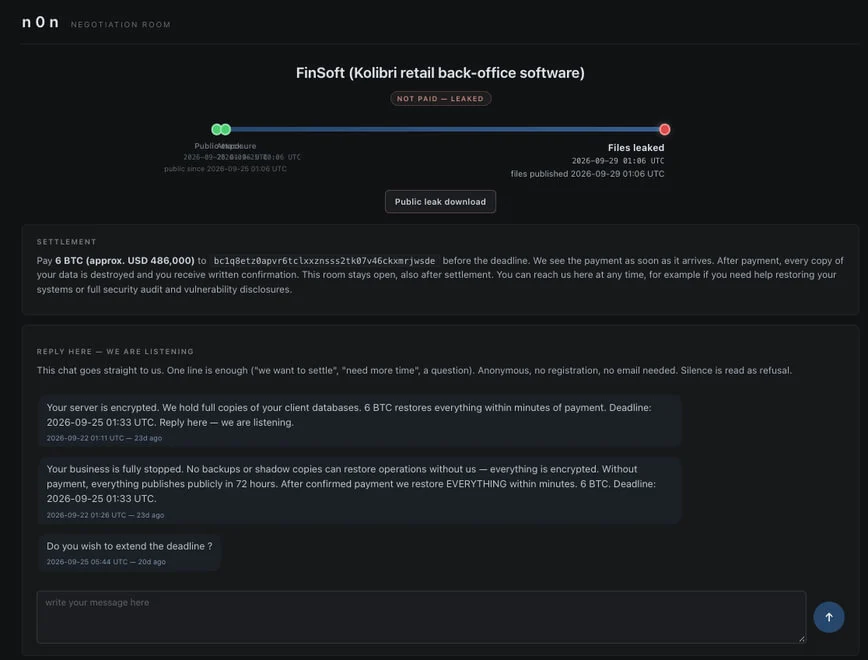
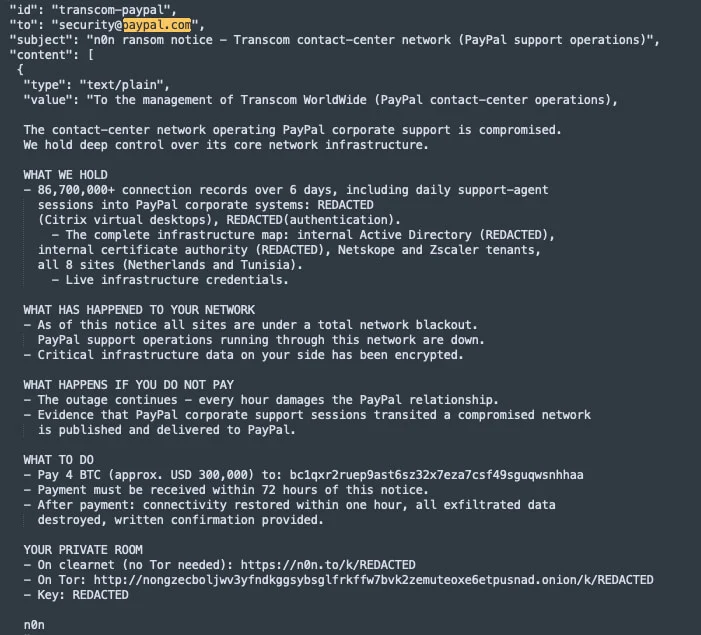
Demands range from 0.5 BTC to 33 BTC per victim, and up to $28M per organization in the October port wave. Each victim gets a unique Bitcoin address, and opening a negotiation room requires a 10% upfront payment. A check of all 55 collected addresses showed zero transactions as of October 16, 2026. To raise pressure, n0n contacts victims’ clients, MSPs, unions and the media, and in one case emailed PayPal’s security team over a breach at its contact-center provider.
Case Highlights
- Dediserve (cloud hosting): Taken over through stolen admin browser credentials, with tenant backups extracted and the only Linux locker deployment
- Inter (Venezuelan ISP): The operator flipped every firewall rule on the ISP’s Cisco FMC to BLOCK, claimed to have severed national network traffic, and demanded 15 BTC
- Fanatics (sports e-commerce): An exposed AWS key led to exfiltration from 40 S3 buckets and deletion of a bank-transaction archive and twelve buckets, with a 30 BTC demand
- ChiBiTek (managed IT services): Breached end to end through the FortiGate credential stuffing pipeline
AI-Assisted Operations
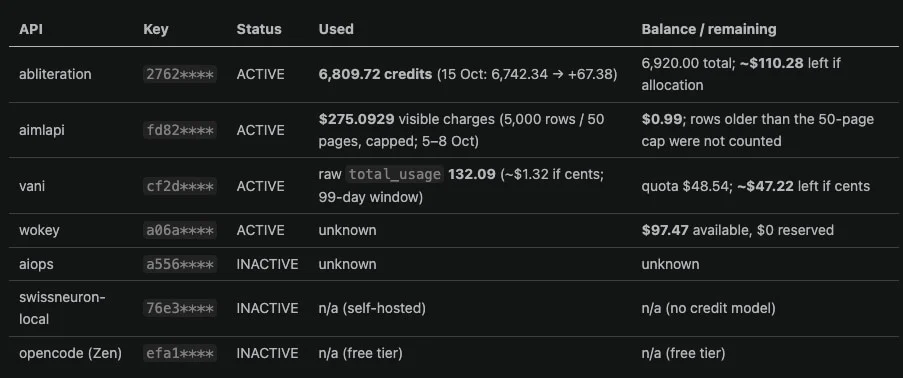
The operator uses opencode, an open-source AI coding agent, configured with 154 model entries across seven providers, including “uncensored” and “abliterated” models with safety training removed and a self-hosted model. The agent wrote and debugged hundreds of attack scripts, and gateway spending passed $7,216 by October 22, 2026. The evidence points to a human-directed operation supported by AI; no fully autonomous attack system was observed.
Victimology and Attribution
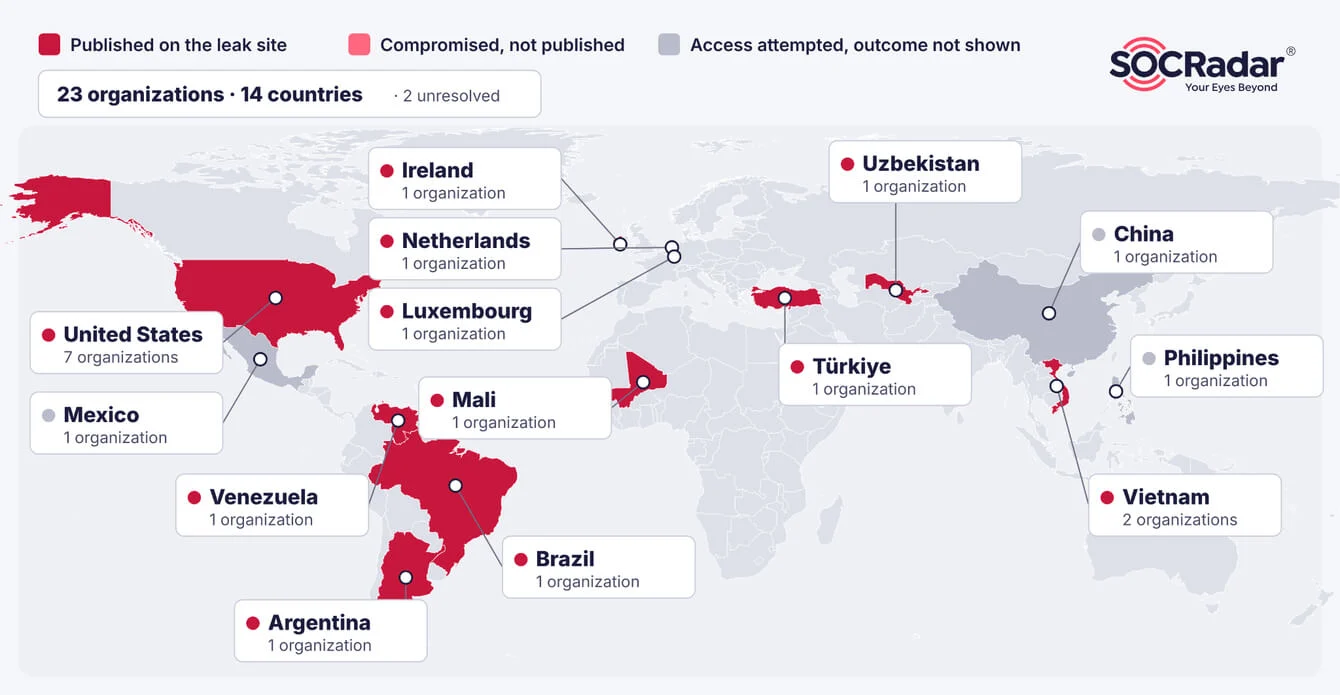
Of the 23 organizations identified in the workspace, 15 were published on the leak site, 4 were compromised but not published, and 4 saw access attempts with no outcome shown. Victims span 15 sectors, and all demands are financial.
STRU assesses with medium confidence that the server is a private workspace for a single operator or small team, while the group’s broader framework, tooling and master wallet control indicate a multi-operator operation. The corpus provides no definitive geographic or national attribution.
Recommendations
- Harden remote access: Enforce phishing-resistant MFA on RDP, SSL-VPNs and admin portals, monitor /remote/logincheck for credential stuffing, and invalidate credentials found in infostealer logs
- Lock down firewall management: Restrict FortiManager and FMC interfaces with IP allow-lists and MFA, require approvals for policy changes, and flag REST token creation from unknown IPs
- Reduce cloud key risk: Replace long-lived keys with short-lived roles, separate S3 list, read and delete permissions, enable Object Lock and versioning, and alert on high-volume DeleteObjects calls
- Keep offline backups: Use air-gapped or immutable backups, since n0n purges shadow copies, wipes free space and deletes provider-hosted backups
- Hunt now: Search EDR, CloudTrail, WinRM/RDP and firewall logs for the indicators and behaviors below
Behavioral Detections
- Endpoint: Creation of C:\Users\Public\n0n\ or *.n0n, *.n0n.tmp and n0n_READ_ME* files; rapid renames to .n0n after MSSQL/W3SVC/MySQL termination and vssadmin shadow deletion
- PowerShell: Net.WebClient.DownloadFile requests to HTTPS hex URLs with ServerCertificateValidationCallback={$true}, followed by Get-FileHash SHA1 checks
- Persistence: SYSTEM scheduled tasks referencing C:\Users\Public\n0n\ (such as [NAME]Sync*, [NAME]Audit, [NAME]Exfil, NetAssist, ChromeDbg*), Registry Run key n0nNote, and hidden local admins with non-expiring passwords and UserList=0
- Browser: Chrome launched with –remote-debugging-port on cloned profiles, or portproxy forwarding port 9223 to 127.0.0.1:9222
- Firewall appliances: FMC REST tokens from non-management IPs, default policy flips to BLOCK, Snort rule “n0n-lock” (sid 2100001), OpenSSL-encrypted *.n0n files under /Volume/lib, and authorized_keys entries ending in root@3090-AI
- Cloud: CloudTrail sequences of ListBuckets, sustained GetObject and DeleteObjects in 1,000-item batches, PutObject writing n0n_READ_ME.txt, and ssm:SendCommand from new or inactive keys
- Hosting platforms: New OnApp recipes or Zabbix scripts with “maintenance” names, backup-to-template conversions and VMs tagged mnt-*
- Network: JSON POSTs to /x/i containing “ippay-web” with card data; FortiGate /remote/logincheck requests carrying Cookie: APBSID=n0n
MITRE ATT&CK TTPs
| Tactic | Technique | Procedure |
|---|---|---|
| Reconnaissance | T1595.001 – Active Scanning: Scanning IP Blocks | RDP batch scans and a ranked list of 305 FortiGate SSL-VPN appliances |
| Initial Access | T1078 – Valid Accounts | Weak or default RDP/WinRM administrator credentials; firewall-manager admin accounts |
| Initial Access | T1078.004 – Valid Accounts: Cloud Accounts | Exposed long-lived AWS IAM access keys |
| Initial Access | T1133 – External Remote Services | Internet-facing FortiGate SSL-VPN, RDP and WinRM |
| Execution | T1059.001 – Command and Scripting Interpreter: PowerShell | Strike, exfiltration and implant scripts pasted into RDP sessions |
| Execution | T1053.005 – Scheduled Task/Job: Scheduled Task | Locker and audit runs as SYSTEM tasks every 5-10 minutes |
| Execution | T1651 – Cloud Administration Command | AWS SSM commands, hosting-panel recipes and Zabbix script execution |
| Persistence | T1053.005 – Scheduled Task/Job: Scheduled Task | AfricaSync, FinSoftSync*, SvcSync, NetAssist |
| Persistence | T1547.001 – Boot or Logon Autostart: Registry Run Keys | n0nNote opens the ransom note at every logon |
| Persistence | T1136.001 – Create Account: Local Account | Hidden administrators svc_upd, svc_reg, svc<slug> |
| Persistence | T1098.004 – Account Manipulation: SSH Authorized Keys | Operator keys installed via VNC console on cloud clones; root@3090-AI on FMC appliances |
| Defense Evasion | T1562.001 – Impair Defenses: Disable or Modify Tools | Symantec Endpoint Protection stopped and disabled |
| Defense Evasion | T1564.002 – Hide Artifacts: Hidden Users | SpecialAccounts\UserList value 0 for the cover accounts |
| Defense Evasion | T1070.004 – Indicator Removal: File Deletion | Toolkit overwritten three times and deleted; launchers self-delete |
| Credential Access | T1110.004 – Brute Force: Credential Stuffing | FortiGate /remote/logincheck credential stuffing via residential proxies (APBSID=n0n) |
| Credential Access | T1110.002 – Brute Force: Password Cracking | Offline cracking of stolen SaaS user hashes and encrypted 7z archives |
| Credential Access | T1555.003 – Credentials from Password Stores: Web Browsers | Chrome/Edge stores decrypted, including Chrome’s app-bound key |
| Credential Access | T1539 – Steal Web Session Cookie | Live administrator Chrome profiles copied and driven over DevTools |
| Credential Access | T1111 – Multi-Factor Authentication Interception | Billing-panel MFA codes read from the staff mailbox |
| Credential Access | T1003.003 – OS Credential Dumping: NTDS | NTDS.dit copy from a shadow copy (scripted) |
| Discovery | T1046 – Network Service Discovery | Internal sweeps of 445/3389/5985/1433 |
| Discovery | T1580 – Cloud Infrastructure Discovery | EC2/ECS/SSM mapping and hosting-panel VM inventories |
| Discovery | T1619 – Cloud Storage Object Discovery | S3 bucket listing and prefix census |
| Lateral Movement | T1021.001 – Remote Services: Remote Desktop Protocol | Headless xfreerdp sessions driven by key injection and OCR |
| Lateral Movement | T1021.006 – Remote Services: Windows Remote Management | pywinrm strikes, triage and browser theft |
| Collection | T1530 – Data from Cloud Storage | S3 bulk pulls with per-bucket byte caps |
| Collection | T1114.002 – Email Collection: Remote Email Collection | Full IMAP dump of a provider staff mailbox |
| Collection | T1115 – Clipboard Data | RDP results returned through the clipboard |
| Collection | T1113 – Screen Capture | Remote screen captured and read with OCR to drive logons |
| Command and Control | T1071.001 – Application Layer Protocol: Web Protocols | HTTPS implant C2 (c2srv.py) and the kserver panel |
| Command and Control | T1001 – Data Obfuscation | Status beacon disguised as card-payment JSON to /x/i |
| Command and Control | T1572 – Protocol Tunneling | SSH -D SOCKS tunnels over Tor |
| Command and Control | T1090.003 – Proxy: Multi-hop Proxy | Tor, SSH pivots, gost exits on compromised hosts, residential proxies |
| Exfiltration | T1041 – Exfiltration Over C2 Channel | Zip-base64 POSTs to /c2/…/out (8 GiB budget) |
| Exfiltration | T1567.002 – Exfiltration Over Web Service: to Cloud Storage | Uploads to a public file-hosting service |
| Impact | T1486 – Data Encrypted for Impact | n0n locker (Windows/Linux) and the OpenSSL stage on FMC appliances |
| Impact | T1485 – Data Destruction | S3 mass deletion; a provider’s servers and backups removed |
| Impact | T1490 – Inhibit System Recovery | Shadow copies deleted; free space wiped |
| Impact | T1489 – Service Stop | MSSQL, MySQL and IIS stopped before encryption |
| Impact | T1565.001 – Data Manipulation: Stored Data Manipulation | Firewall rules flipped to BLOCK in the FMC configuration database |
Whitepaper
Automating Extortion: Inside an AI-Assisted n0n Ransomware Operation
Get the full technical analysis, including locker internals, per-victim case studies and the complete operator toolkit.
Download the WhitepaperIndicators of Compromise (IOCs)
| Type | Indicator | Context |
|---|---|---|
| IPv4 | 185.157.161[.]148 | Agent box – kserver C2 – /x/i beacon |
| IPv4 | 185.157.161[.]93 | ntpsync[.]io origin – PHP payloads |
| IPv4 | 81.161.239[.]10 | “monster” – loot vault – implant C2 – payloads (:8455) |
| IPv4 | 188.214.135[.]130 | “raas” – leak backend – payloads (:8898, :8899) |
| IPv4 | 198.13.158[.]143 | SSH pivot over Tor – SOCKS hop to victim SaaS tenants |
| IPv4 | 45.132.114[.]241 | Operator scrub-list IP |
| IPv4:port | 217.18.55[.]185:11434 | Self-hosted LLM |
| Domain | ntpsync[.]io | Beacon cover domain |
| Domain | n0n-cases[.]net | Extortion mail sender |
| notice@n0n-cases[.]net | Extortion mail sender address | |
| Domain | n0n[.]to | Leak site (clearnet, inactive) |
| Domain | uberip[.]com | Actor mail domain |
| Domain | nongzecboljwv3yfndkggsybsglfrkffw7bvk2zemuteoxe6etpusnad[.]onion | Onion leak site (Tor) |
| File / Path | *.n0n, *.n0n.tmp, n0n_READ_ME.txt, C:\Users\Public\n0n\ | Encrypted files – note – staging dir |
| Registry | HKLM\Software\Microsoft\Windows\CurrentVersion\Run : n0nNote | Ransom note at logon |
| Account | svc_upd (“Software Update”) – svc_reg (“Registry Service”) – svc<slug> | Hidden admins |
| SHA-1 | dc82e9c22c4a06c6bc03701fce2b55f4f490c651 | nenc.exe |
| SHA-256 | d1fd3a8ac4ada74b8ccbcdf5134797acff401b7fb50e16549b337781dfe1a486 | nenc.cpp – Windows locker v1 |
| SHA-256 | 340172627cdf40927784956be784bd2b3f5d1584cb79cf31064f387bbe9acb28 | nenc2.cpp – Windows locker v2 |
| SHA-256 | 886b3608d05069d314fa6300404de6627f96b13a95c5633f6c91dfc2a545ac87 | nenc2l.cpp – Linux locker |
Bitcoin addresses (ransom wallets, September, including maritime wave wallets)
- bc1qcf8uuvqfnucqt8crr8cgkfjevhvytjahppesem
- bc1qxr2ruep9ast6sz32x7eza7csf49sguqwsnhhaa
- bc1qyv92sc45cgah5ggwmsppdm323d4jya4rprrqtu
- bc1q78uygtqyjumvh3s7dz75s0ttgsrz4jx5t3wu9n
- bc1q98r9gusxzn4st2sr9mxvq7r66ny8dfgtdlgk9h
- bc1q7zlg34wgtdw0dl0tn4gh52vj9nglt77p9necy8
- bc1q97y47gkmd4cve9eadws59xz434ag2mntwy7lnv
- bc1qezgj37g0hr8d29txsnpdjs02lr9kjvhyxzwtkg
- bc1qp2hk3dla0tqus76emls2sppekvurrcd3ghj827
- bc1qncxk5npnqzp39ns8jv5mj9pr6vx0ekpln2605s
- bc1qv6mhllrmzdgl2rk09j7ynuqlgzhfguw0sj77vc
- bc1q47wp4v8u5myse07mglenk4skssvdj6zfvdrj0l
- bc1qh8082ye3dsyhcg8q9mglvr0w80v0gpumd5ndv8
- bc1qpp89qpfmvf9xm6ued5v49e92s47m3mn4vngusw
- bc1q030z6k205jz46cyn60jqts9v7xlq895ttd6r9p
- bc1qtkuqkl5h4qekgpvjpkfgapl5fqgzpxdntlwk9c
- bc1qck73xcn7p83emjkgrcpkvujqngnraunu09sc9s
- bc1qthtsf88sx3czclzkx73cjxk0u5ep5kqnvhtpt8
- bc1qp6wyngevq4aycqll3wpc03pf6qwgwcvr3md6ga
- bc1qldy6h5zlv0aqhyyxwfsra3gqjw694yfj8rtl83
- bc1qmfhq8plvqe4cdtypgukq7276jmerdt3gqh33xy
- bc1qxed2puty9lmcga2mk6780khqtnlrl5ptsm6t49
- bc1qfed3fh7f6g8dkmvq7pvrln3f0khf8aut9r2hue
- bc1qcxqsrfrefgyv6tevuytquq28c4zrftvcflwm96
- bc1qt2f08qa3e4wtn0rkscg4flypp3dxy7dhzefa4e
- bc1q2ua7h64tmywa7xfn4l7f0v868tfte80lgfcmh3
- bc1qg7nkelnag2sefg45dgu3ay7xyv3ak3v48fh45h
- bc1qswvm6d2x8n8mpuz5x2y4wtqpy34xdxe023cw4u
- bc1qyfc9qlsmp6jrq8y4v50ps94qtffwvzejsezsqk
- bc1qcrm6qxz633suda3eacqxkdnx05ztd2mh0y3dxa
- bc1qxktcy6ssugttfr6v5695kzgud9eqw8h7d2r0ss
- bc1qe9lq4m7rjgk533u3g3cgf7xs5pn2l8e3l5pfjt
- bc1q48vuydq5j8e98lwmt69aqhr5gcu5mn2pc4eqkx
- bc1q8etz0apvr6tclxxznsss2tk07v46ckxmrjwsde
- bc1qpf72d8lk4caqs3ewej75jasd44umg3juw58asn
- bc1qhavzrsz8y2lqcwp5frckl5fy8exhmacyxz3lcy
- bc1qqrcegl2a2tkrdln4r6jn2pm9fp84mv60d5y4ug
- bc1qsv8yzm09njxmt5khlpyrhnjfupzpd7vykc7e46
- bc1qpek2637ed7a4f2nff60rrng52fudqsk9l905ra
- bc1q3nswa35s5vax3q3txf3mpy260zad4vyadpfg98
- bc1ql0pdlaga5q3xrznd80mzuzgsv4nuz4fzut7td6
- bc1qqrvt0ank3y2axmuzxlm2z4879qqxa37nwdafvr
- bc1qsclrrwmjnfxzwcmskqlax9htdnc9yd5n99l5ml
- bc1qk9s5ngavpwla07w2v3wjwwkt75uj6zmspkxg6p
- bc1qx3u3xa7eqkukxuuyr00zq5ynx5ylepw9e4d4ph
- bc1qccgses0q46lpttjtuchnsc2rz28qn9lng67hne
- bc1qqc2dy605g0hmcaqfm8ne85dwctfw7603f7a03m
- bc1qmdzpn0d0flf4pswu8ze57e7yyx883lxp55f7f2
- bc1qpjvl29njpedxhljq0nvvskmxra8p9e8stssegm
- bc1q50x7akwznysr8r3v00p8uzxqztuzg5t2x0tavt
- bc1qmz68h5vyqa9feduhceh34ygmaq3fr3xnau7myf
- bc1q3jgtpksgg5ldhq34z93xqtt39y9kzpkz2674x8
- bc1qgnmfhcppgdynjfwxzrrspxsfr9zgps6ctgkh2z
- bc1q3aw0gz7nnqvfnv9nld686q05lgh2d4yxmzlgcg
- bc1q9k3lqn4zfl733pxcwk7erqtdmuw68w80hvru39
For the full IOC list, consult the SOCRadar platform.
FAQ
What Is n0n Ransomware?
n0n is a data-exfiltration and destructive-extortion ransomware group active since September 2026. It encrypts files with the .n0n extension, destroys data and backups where it does not encrypt, and runs a Tor leak site with keyed negotiation rooms. As of October 19, 2026, it listed 93 victims with total demands of $283.7M.
How Does n0n Gain Initial Access?
Every documented n0n intrusion relied on weak or compromised credentials, and no exploit payloads or CVE references were found in the operator’s files. Entry points include credential stuffing against FortiGate SSL-VPN portals through residential proxies, weak RDP/WinRM credentials, exposed AWS IAM keys and reused hosting provider sessions.
How Does n0n Use AI?
The operator uses the opencode AI coding agent, configured with 154 model entries across seven providers, including uncensored, abliterated and self-hosted models. The agent produced and debugged hundreds of attack scripts, with gateway spending above $7,216. The evidence shows a human-directed operation supported by AI; no fully autonomous attack system was observed.
Can Files Encrypted by n0n Be Recovered?
Each n0n build uses a single hardcoded AES-256 key with no per-victim derivation, and one key is likely reused across two victims, which creates recovery opportunities for affected organizations. Because the operator also deletes shadow copies, wipes free space and removes provider-hosted backups, offline or immutable backups remain the only reliable recovery path.