Sep 28, 2026

Oct 05, 2026
5 Mins Read

Summarize with:
IQUALIF France Leak, IUT Paris Seine Breach, US IAB Auction, SMTP Credential Dump, and Apache Struts Exploit Sale
SOCRadar Dark Web Team identified several new underground posts, including an alleged IQUALIF-based French residential data leak, an alleged breach affecting IUT Paris Seine, and an alleged initial access auction for a U.S. manufacturing company. Other posts advertised an alleged 19 million SMTP credential dump and access to servers reportedly compromised through CVE-2017-5638.
Receive a Free Dark Web Report for Your Organization:
Alleged IQUALIF France Residential Data Leak is Detected
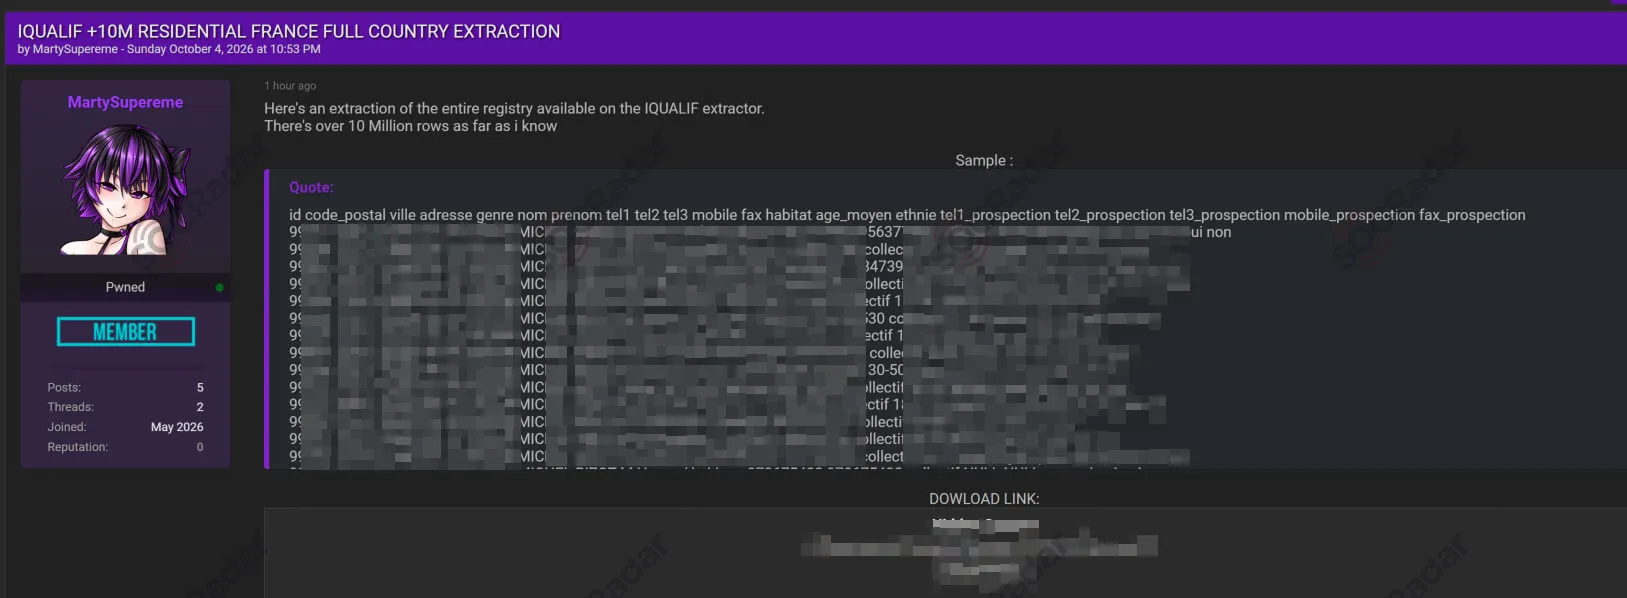
SOCRadar Dark Web Team detected a dark web post claiming to leak a database allegedly containing more than 10 million French residential records. The threat actor claimed the dataset was extracted using the IQUALIF tool and made available for download.
The exposed sample reportedly includes names, postal codes, cities, residential addresses, gender, phone numbers, mobile numbers, fax details, housing type, average age, ethnicity, and marketing/prospection fields. If valid, the dataset could support targeted phishing, smishing, fraud, and large-scale social engineering campaigns against individuals in France.
Alleged IUT Paris Seine Breach is Detected
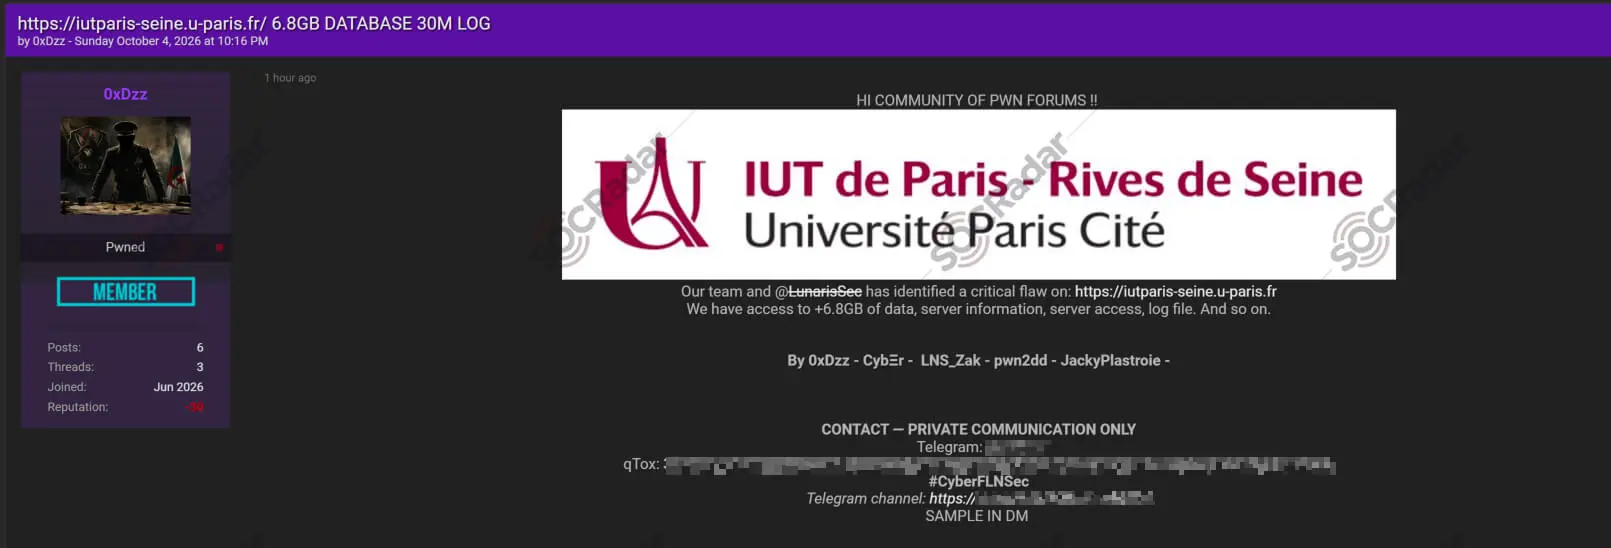
SOCRadar Dark Web Team detected a post claiming a breach of IUT Paris Seine, part of Université Paris Cité. The threat actor group claimed to have identified a critical flaw on the institution’s web infrastructure and obtained access to approximately 6.8GB of data.
The post also referenced 30 million logs, server information, server access, and other related data. While the claim remains unverified, the alleged exposure of logs and access-related information could create risks around credential abuse, follow-on intrusion attempts, and potential exposure of student or institutional data.
Alleged U.S. Manufacturing Access is Auctioned
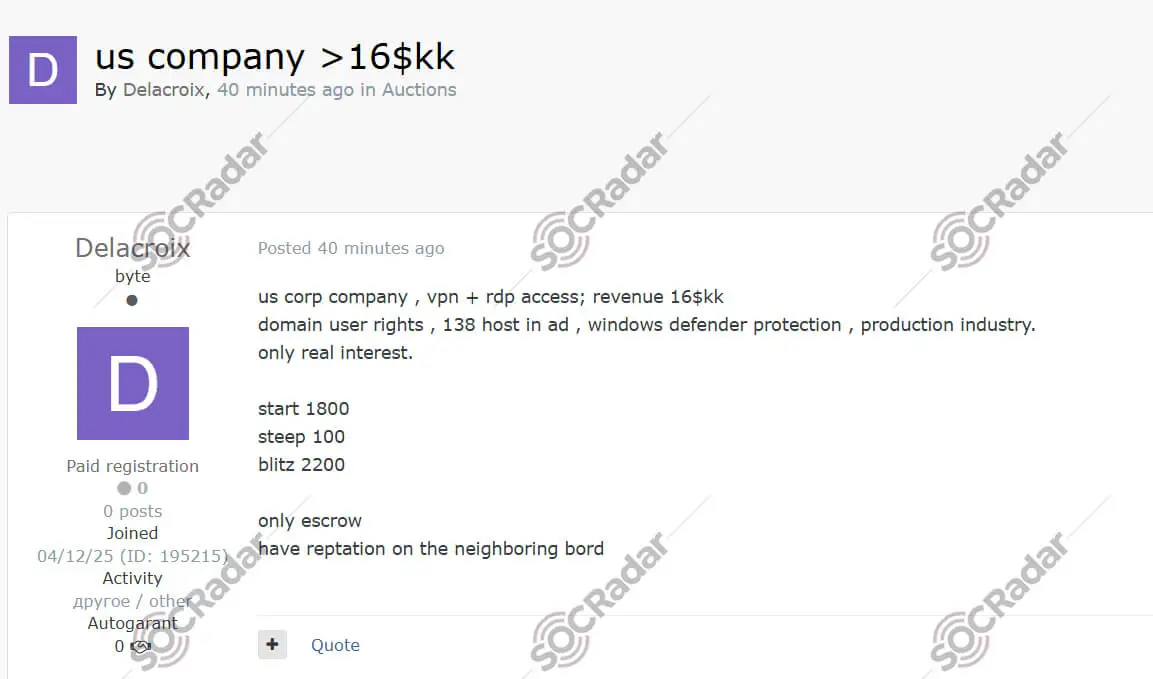
SOCRadar Dark Web Team detected an initial access broker post auctioning access to a U.S.-based manufacturing company. The seller claimed the company has approximately $16 million in revenue and offered both VPN and RDP access.
The actor stated that the environment includes 138 Active Directory hosts, domain user rights, and Windows Defender protection. The auction terms included a starting price of $1,800, a $100 step, and a $2,200 buy-it-now price. If valid, this access could be used for ransomware deployment, data theft, privilege escalation, or lateral movement.
Alleged SMTP Credential Dump is Leaked
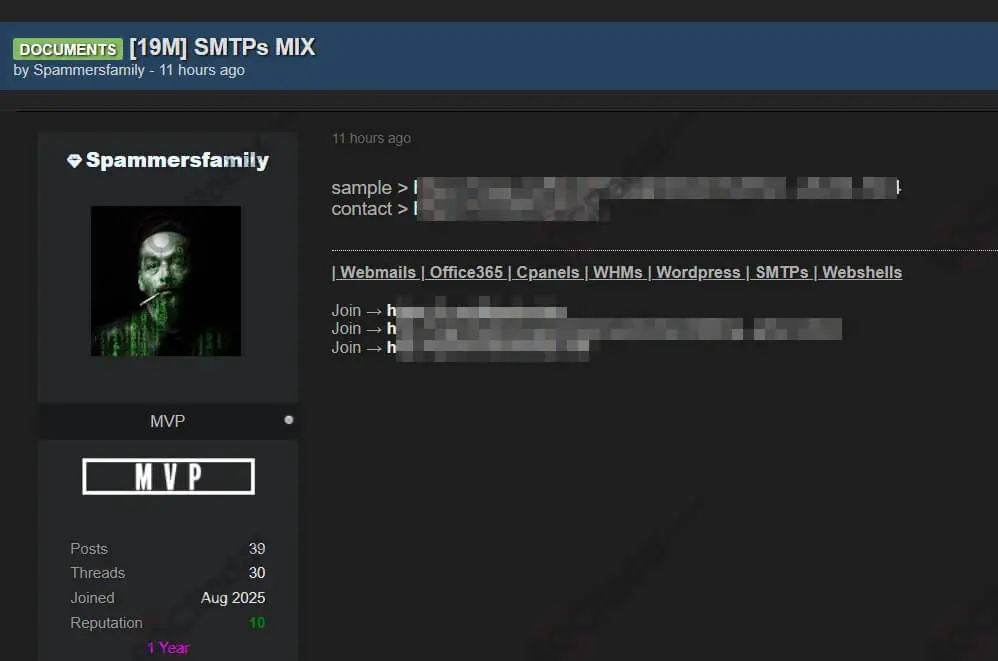
SOCRadar Dark Web Team detected a post advertising a large credential dump titled “19M SMTPs MIX.” The actor claimed the dataset contains approximately 19 million SMTP credentials and shared a sample through an external file-hosting link.
SMTP credentials are valuable for cybercriminals because they can be used to send emails through legitimate mail infrastructure. If the dump is authentic, it could support phishing, spam campaigns, malware delivery, business email compromise attempts, and domain reputation abuse at scale.
Alleged Apache Struts Exploit and Server Access Sale is Detected
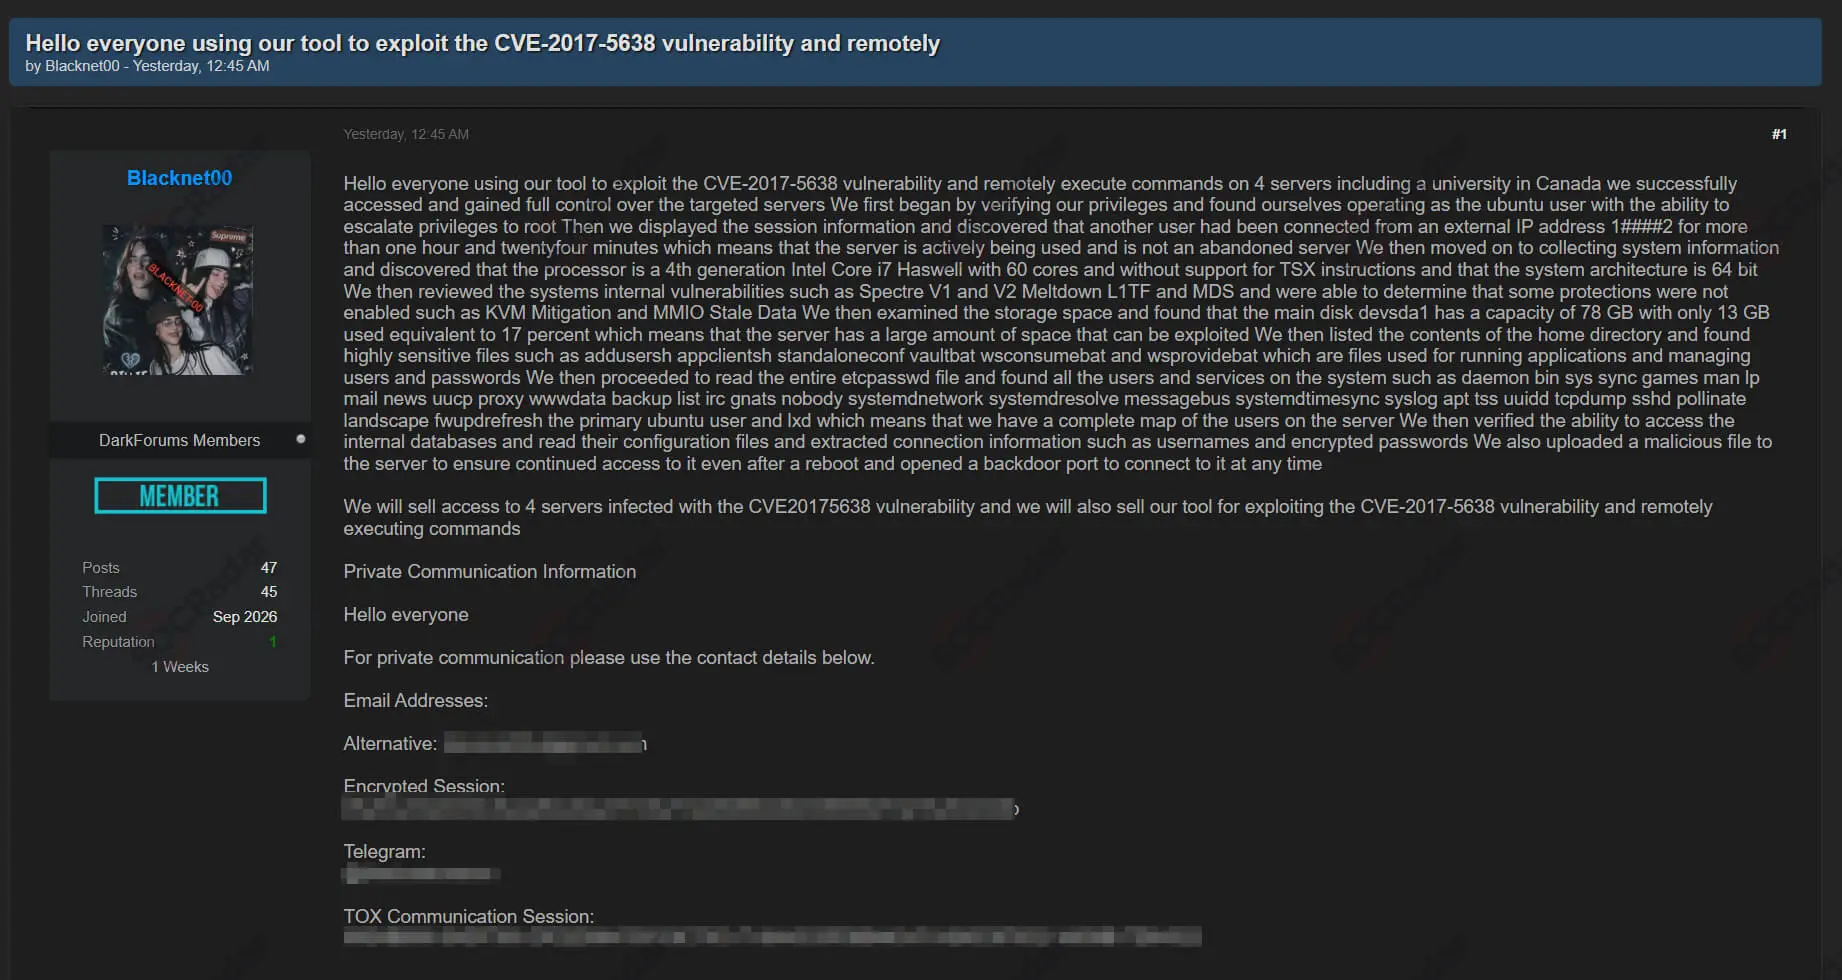
SOCRadar Dark Web Team detected a post advertising a tool allegedly used to exploit CVE-2017-5638, a critical Apache Struts remote code execution vulnerability. The actor also claimed to be selling access to four compromised servers, including one allegedly linked to a university in Canada.
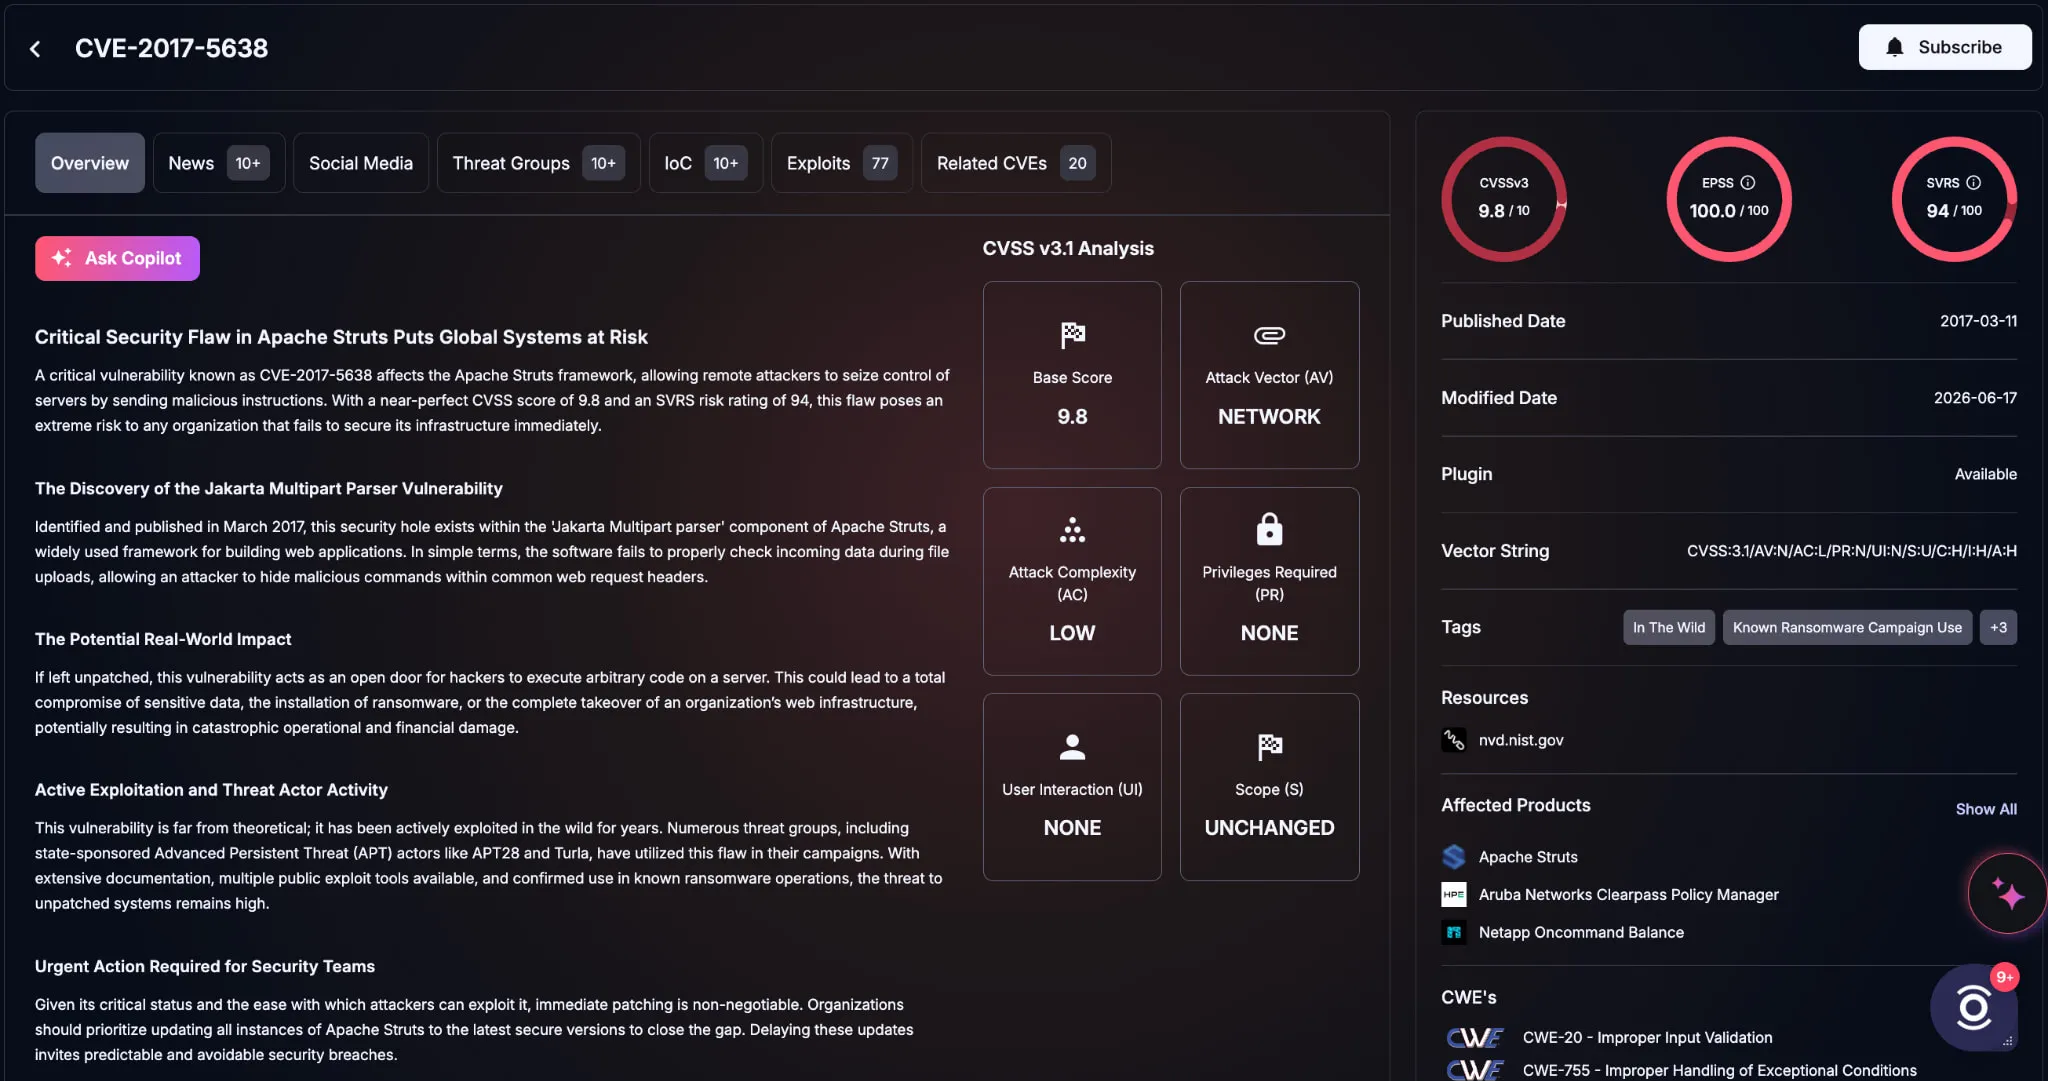
Details of CVE-2017-5638 (SOCRadar Vulnerability Intelligence)
According to the post, the actor claimed to have executed commands remotely, gained administrative control, reviewed system users and server details, extracted configuration information, and established persistence. If verified, the access could enable data exfiltration, additional malware deployment, or further compromise of connected systems.
Powered by DarkMirror™
Gaining visibility into deep and dark web threats can be extremely useful from an actionable threat intelligence and digital risk protection perspective. However, monitoring all sources is simply not feasible, which can be time-consuming and challenging. One click-by-mistake can result in malware bot infection. To tackle these challenges, SOCRadar’s DarkMirror™ screen empowers your SOC team to follow up with the latest posts of threat actors and groups filtered by the targeted country or industry.
Table Of Content
IQUALIF France Leak, IUT Paris Seine Breach, US IAB Auction, SMTP Credential Dump, and Apache Struts Exploit Sale
Alleged IQUALIF France Residential Data Leak is Detected
Alleged IUT Paris Seine Breach is Detected
Alleged U.S. Manufacturing Access is Auctioned
Alleged SMTP Credential Dump is Leaked
Alleged Apache Struts Exploit and Server Access Sale is Detected
Related Articles