




Sep 22, 2026

Table Of Content
Closing the Dark Web Blind Spot in EclecticIQ Intelligence Center with SOCRadar
Exposure Starts Underground, and Most Teams Find Out Last
A Platform Can Only Correlate What It Is Given
Where the Intelligence Comes From: SOCRadar
Integration with EclecticIQ Intelligence Center
An Intelligence Center Example
Take the Next Step
Frequently Asked Questions
Learn More
Related Articles


Sep 24, 2026
8 Mins Read

Summarize with:
Closing the Dark Web Blind Spot in EclecticIQ Intelligence Center with SOCRadar
Your analysts start the morning in their threat intelligence platform, working the feeds, cases, and detections in front of them. What they cannot see is the forum post from three days ago offering access to a server on their perimeter, or the stealer log with a finance team member’s credentials sitting in a Telegram channel. By the time that exposure reaches an internal alert, the adversary has had a head start measured in weeks.
SOCRadar now delivers its Dark Web and underground intelligence directly into EclecticIQ Intelligence Center, through three continuously updated feeds covering Dark Web news, black market activity, and PII exposure.
Exposure Starts Underground, and Most Teams Find Out Last
Stolen credentials, exposed customer data, and company information routinely surface on Dark Web forums, black markets, and underground channels before they ever appear in internal logs or alerts. That is the nature of the kill chain: an initial-access broker lists the access, someone buys it, and only then does anything show up on your network.
For security teams, manually tracking these sources is slow, inconsistent, and easy for threat actors to outpace. Forums require standing access and language coverage. Marketplaces change addresses. Closed channels need an operator who is already trusted inside them. Very few teams can staff that work, and the ones that can rarely do it continuously.
A Platform Can Only Correlate What It Is Given
A threat intelligence platform is built to structure, correlate, and operationalize intelligence. Collecting that intelligence from closed underground communities is a separate discipline: persistent access to forums and marketplaces, coverage across languages and regions, harvesting of stealer and botnet logs at scale, and enough context to tell a real exposure from recycled noise.
Without that source layer, analysts miss early warning signs of data leaks, credential exposure, and initial-access listings until an incident has already progressed. This delays response, increases fraud and account-takeover risk, and forces analysts to switch between disconnected tools to piece together what has been exposed. The gap is felt across SOC triage, threat hunting, fraud and brand protection, and exposure management alike.
Where the Intelligence Comes From: SOCRadar
SOCRadar Dark Web Monitoring continuously collects and analyzes data across the surface, deep, and Dark Web, including forums, marketplaces, paste sites, Telegram and Discord channels, ransomware leak sites, and leaked databases. It then enriches and prioritizes what it finds with cross-source confidence scoring, so only findings relevant to their organization reach an analyst.
That collection layer is what the integration carries into Intelligence Center:
- Leaked employee and customer credentials found in Dark Web markets, forums, and stealer and botnet logs
- Black market listings tied to stolen data sales, initial-access offers, and tooling
- Exposed personally identifiable information, including financial and account details
- Threat actor and ransomware group discussion relevant to your organization, sector, or region
- Mentions of vendors and partners that could indicate upstream, supply-chain exposure
These three feeds are one slice of the wider SOCRadar Extended Threat Intelligence Platform, which also covers brand protection and takedown services, external attack surface management, supply chain intelligence, and VIP and fraud protection.
Integration with EclecticIQ Intelligence Center
SOCRadar delivers findings into Intelligence Center as three separate incoming feeds, each drawing continuously from the SOCRadar API and arriving as native Intelligence Center entities. Analysts do not open a second portal; SOCRadar’s underground findings sit alongside everything else they already correlate.
The integration does not include a data entitlement. The feeds are a connection layer that carries intelligence you are already licensed to receive from SOCRadar into Intelligence Center. Installing or enabling them does not grant access to SOCRadar data on its own. The feeds return results only for organizations with an active SOCRadar subscription that includes the relevant module and API access.
SOCRadar Dark Web News Feed: Curated intelligence from Dark Web forums, marketplaces, and closed channels, delivered as structured reports. Your CTI team can assess relevance, tag, and file underground developments the same way they handle any other reporting, with no need to trawl the sources themselves.
SOCRadar Black Market Monitoring Feed: Listings tied to stolen data sales, initial-access offers, and other black market activity, delivered as indicator and observable entities. Because they arrive as structured data, they correlate automatically against active investigations, existing entities, and your detection content.
SOCRadar PII Exposure Monitoring Feed: Alerts raised when employee or customer personally identifiable information, such as credentials, financial data, or account details, appears exposed on Dark Web sources, structured for immediate triage by SOC and fraud teams.
What each feed requires on the SOCRadar side:
- The Dark Web News Feed requires access to the SOCRadar Dark Web News API.
- Credential leak data, which powers the PII exposure and black market findings, requires access to the SOCRadar Dark Web module and the standard SOCRadar API.
Without the corresponding SOCRadar API access, the feed can be configured in Intelligence Center but will not return data.
An Intelligence Center Example
An analyst on your team is working a suspected compromise of a partner-facing application. There is a suspicious authentication pattern, but nothing conclusive, and the working theory is a misconfiguration rather than an intrusion.
In Intelligence Center, the entity for the application’s external hostname now carries observables that came from SOCRadar’s black market collection: a listing offering access to that host, posted eleven days earlier. Pivoting on the seller’s handle surfaces a SOCRadar Dark Web news report describing the same actor’s recent activity against organizations in your sector. A SOCRadar PII exposure alert ties two service-account credentials to a stealer log from the same window.
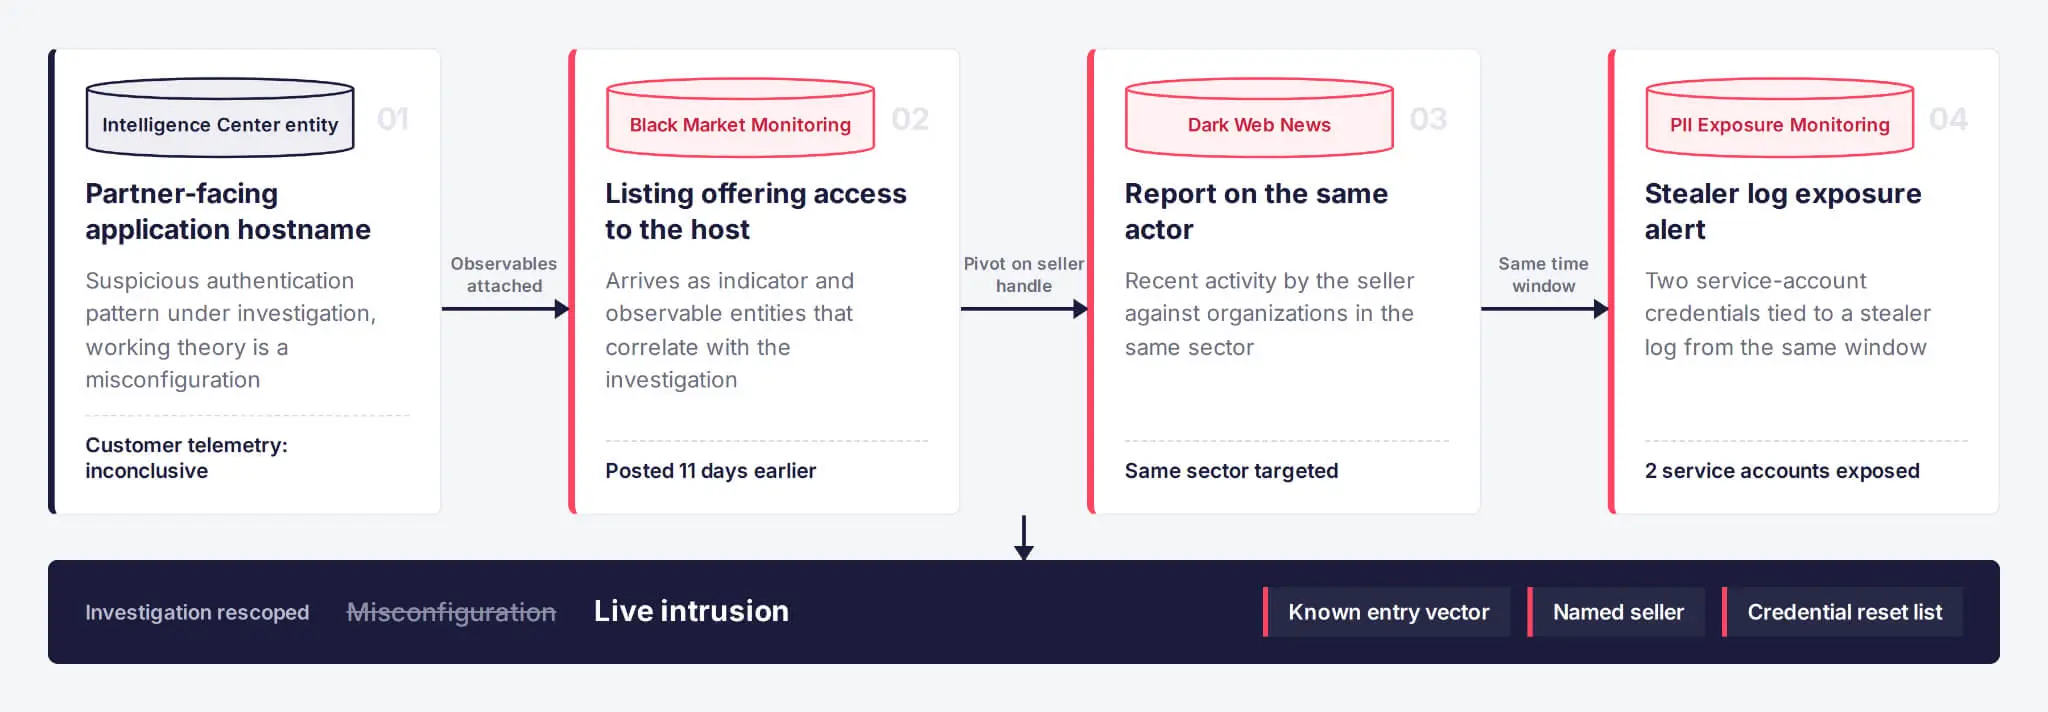
A single investigation in EclecticIQ Intelligence Center, rescoped from misconfiguration to live intrusion by three SOCRadar findings.
The investigation changes shape in minutes. What looked like a misconfiguration is scoped as a live intrusion with a known entry vector, a named seller, and a concrete credential reset list. None of those three findings existed anywhere in the customer’s own telemetry. They surfaced because SOCRadar was already inside the sources where the activity happened.
Take the Next Step
If your team runs its intelligence operations in EclecticIQ Intelligence Center, this integration puts SOCRadar’s underground collection to work in the place your analysts already spend their day. Intelligence Center is one of many destinations SOCRadar feeds: the same intelligence reaches SIEM, SOAR, TIP, and case management tools across the SOCRadar integrations ecosystem, so standardizing on SOCRadar as the source does not lock you into a single workflow surface.
To get started, contact your SOCRadar Account Manager or Customer Success Manager to confirm which feeds fit your use cases and to enable the required module and API access on your subscription. Once that is in place, the feeds can be configured in Intelligence Center. If you are an EclecticIQ customer but not yet a SOCRadar customer, request a demo and mention that you use EclecticIQ. The integration becomes available once your SOCRadar subscription is in place.
Frequently Asked Questions
What Does the SOCRadar Integration Add to EclecticIQ Intelligence Center?
Three continuously updated feeds: Dark Web News, Black Market Monitoring, and PII Exposure Monitoring. Findings are drawn from the SOCRadar API and arrive as native Intelligence Center entities.
Does Enabling the Feeds Give Access to SOCRadar Data?
No. The feeds carry intelligence you are already licensed to receive from SOCRadar. They return data only for organizations with an active SOCRadar subscription that includes the relevant module and API access.
Which SOCRadar Access Does Each Feed Require?
The Dark Web News Feed requires the SOCRadar Dark Web News API. Credential leak data, which powers the PII exposure and black market findings, requires the SOCRadar Dark Web module and the standard SOCRadar API.
What Underground Findings Reach Intelligence Center?
Leaked employee and customer credentials, black market listings for stolen data and initial access, exposed PII, threat actor and ransomware group discussion, and vendor or partner mentions that could indicate supply chain exposure.
How Do I Get Started?
Contact your SOCRadar Account Manager or Customer Success Manager to enable the required module and API access, then configure the feeds in Intelligence Center. EclecticIQ customers without a SOCRadar subscription can request a demo.


