Latest articles
 SOCRadar
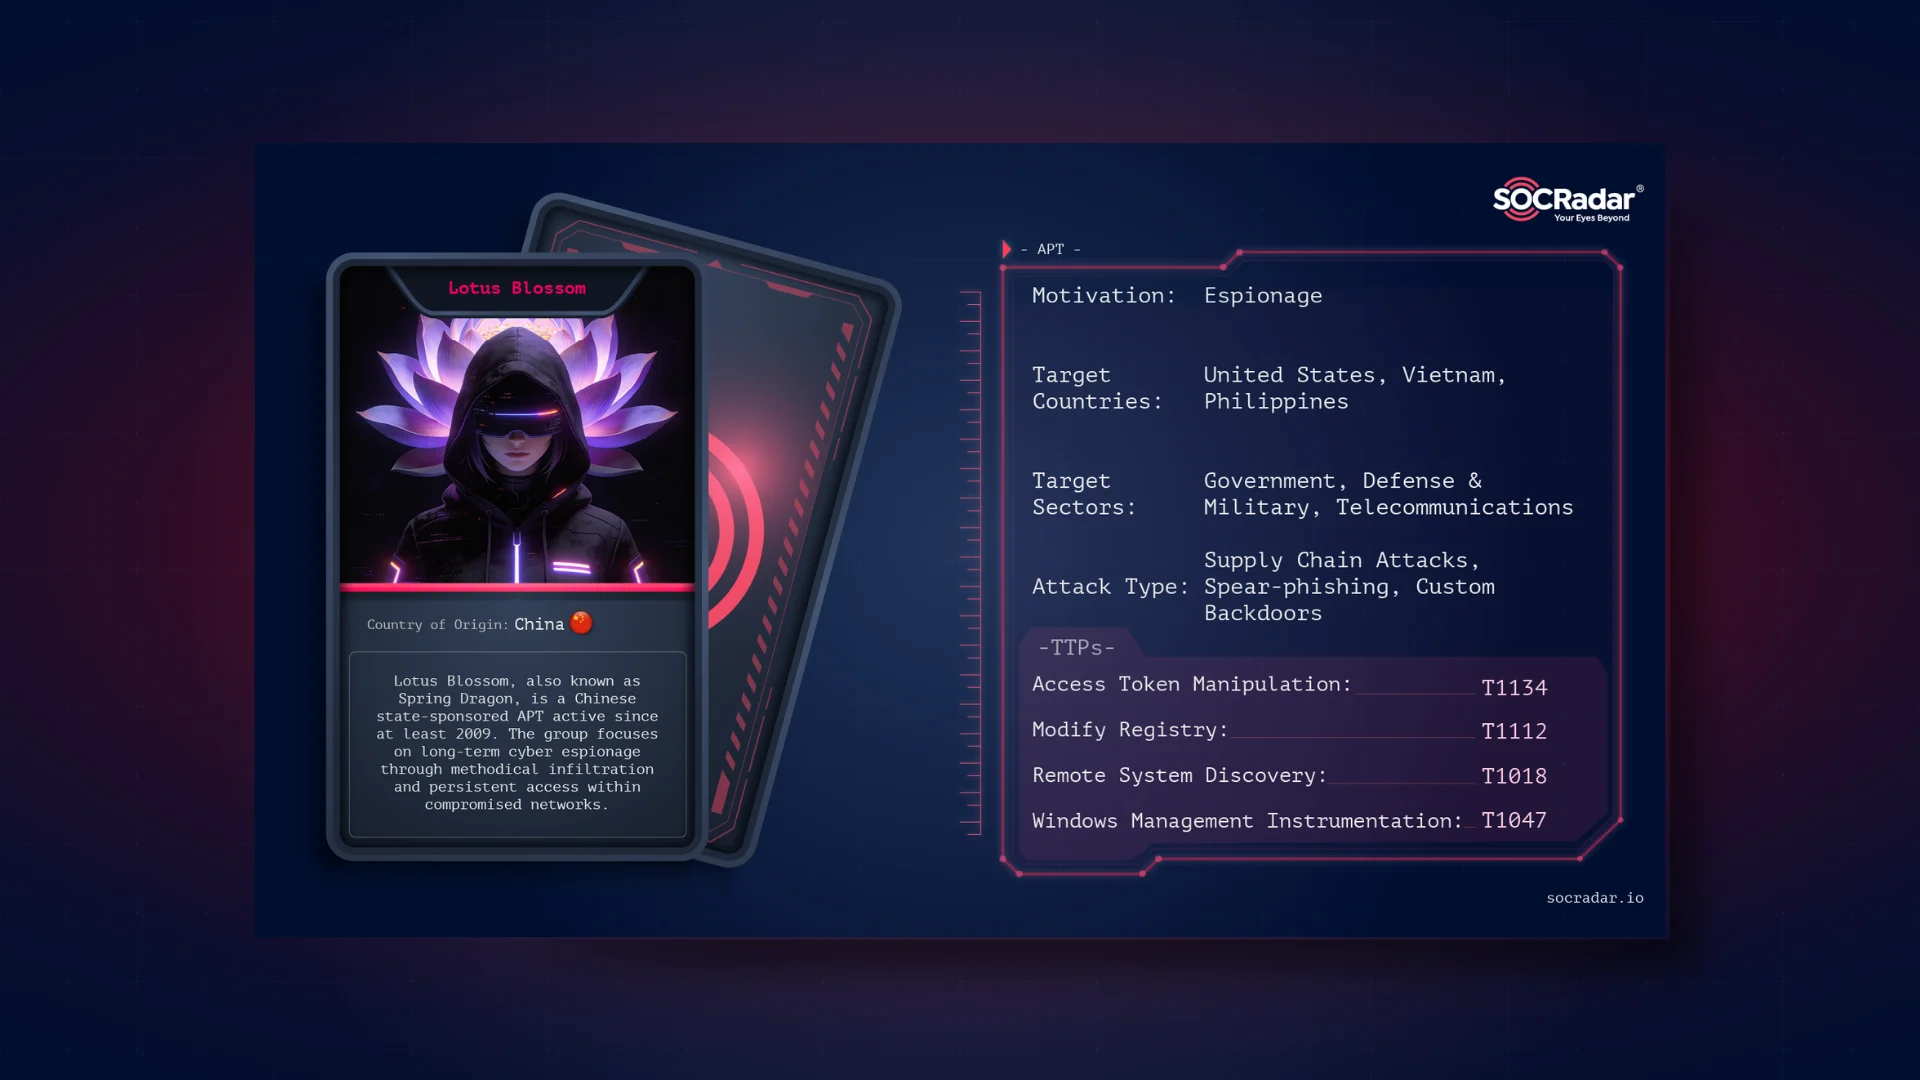
Dark Web Profile: Lotus Blossom
Lotus Blossom is a long-running cyber espionage Advanced Persistent Threat (APT) group active since at least 2009 and widely attributed to the People’s Republic of China (PRC). The threat group…
 SOCRadar
Severe VS Code Extension CVEs Expose Developers to RCE and File Exfiltration
A recent report highlighted a coordinated disclosure affecting four popular Visual Studio Code (VS Code) extensions: Live Server, Code Runner, Markdown Preview Enhanced, and Microsoft Live Preview. Three of the…
 SOCRadar
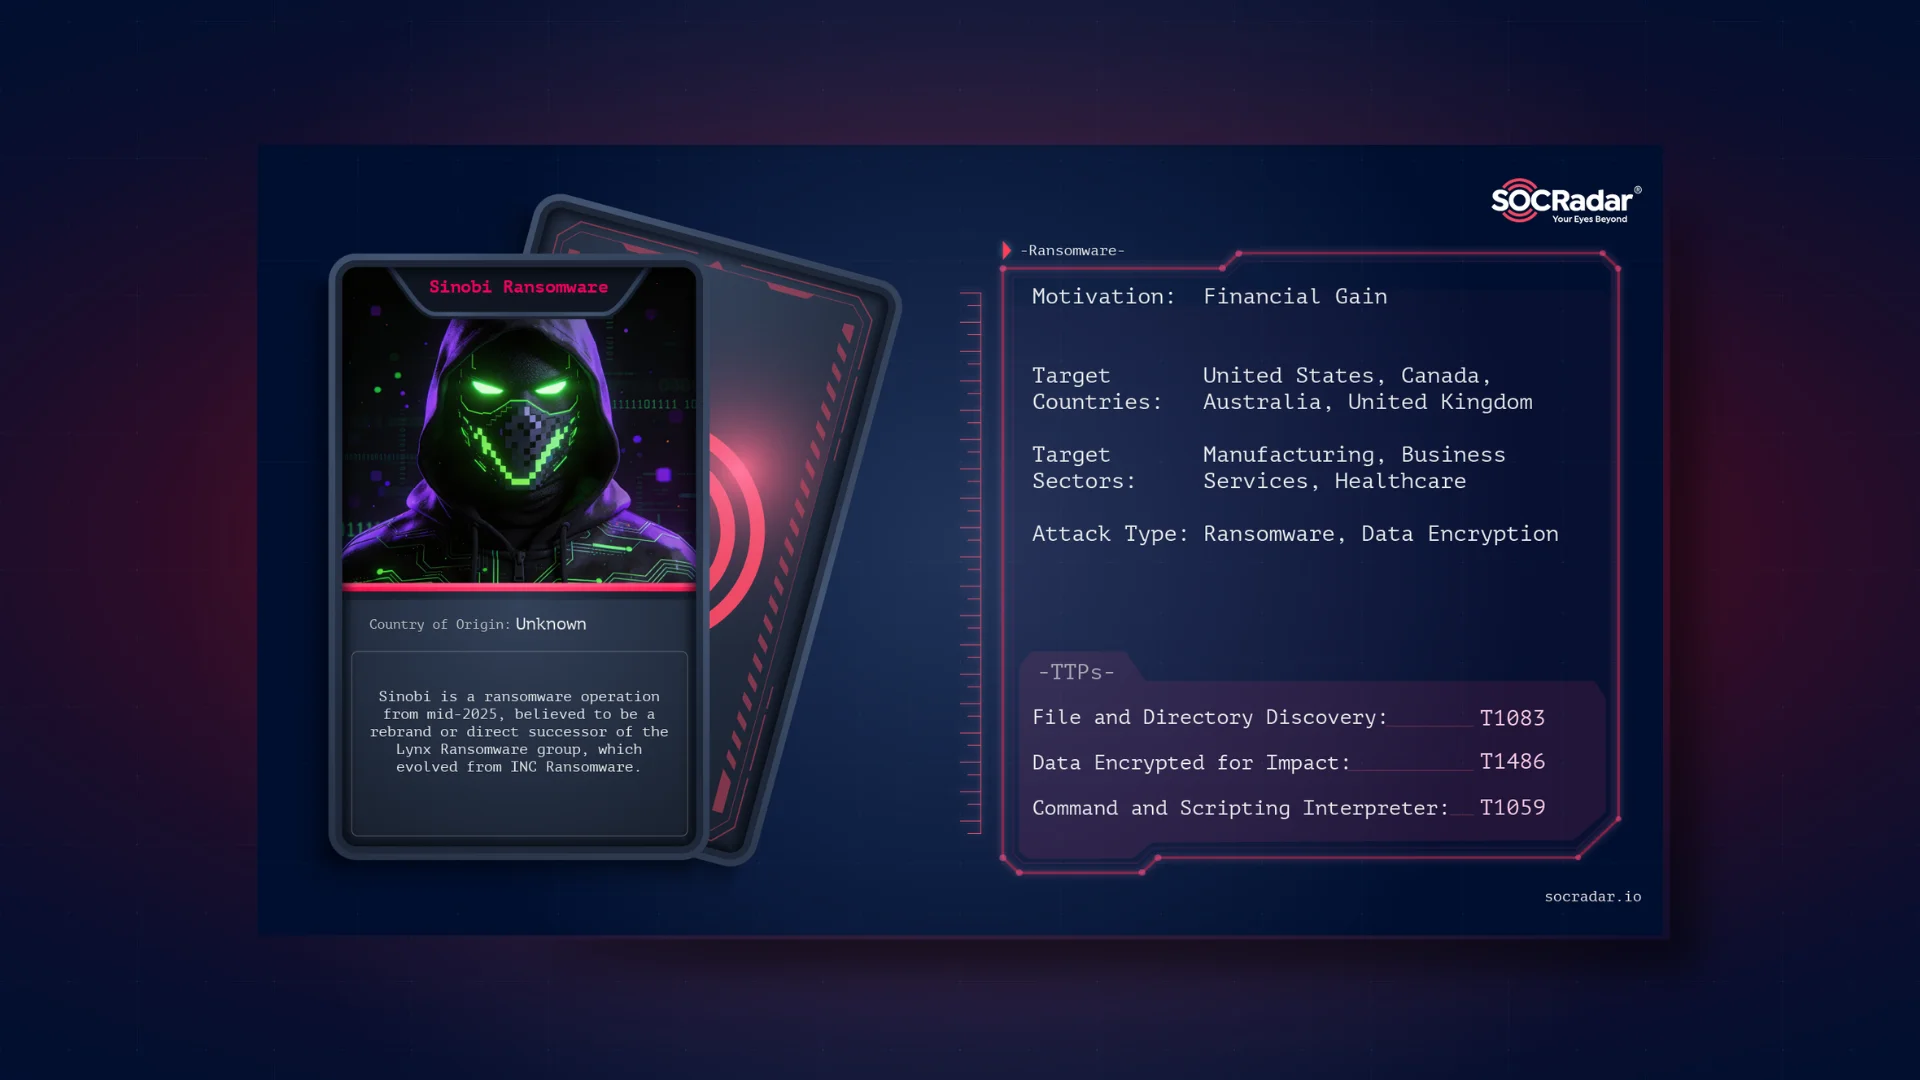
Dark Web Profile: Sinobi Ransomware
Sinobi Ransomware is a cybercrime operation that emerged in mid-2025, operating as a Ransomware-as-a-Service model. It is believed that the group is a rebrand or direct successor of the Lynx…
 SOCRadar
Public Elasticsearch Instances Expose 43M+ Records Including Credentials, Credit Cards, and Customer Data
SOCRadar’s AI-powered Sensitive Data Exposure Monitoring service has identified three publicly accessible and misconfigured Elasticsearch instances leaking highly sensitive data, including infostealer logs, credit card information, and millions of personal…
 SOCRadar
What U.S. CISOs Should Track in Early 2026?
Midway through the first quarter of 2026, it’s observed that U.S.-based Chief Information Security Officers (CISOs) face a cyber landscape defined by unprecedented technological acceleration and complex geopolitical shifts this…
 SOCRadar
Political DDoS Pivots to Japan: Weekly DDoS Threat Intelligence Analysis
Analysis Period: February 9 – 15, 2026 Between February 9 and 15, 2026, SOCRadar identified an extensive coordinated DDoS campaign conducted by the pro-Russian threat actor NoName057(16) using their DDoSia…
 SOCRadar
CVE-2026-2441: Chrome Zero-Day Enables In-Sandbox Code Execution
Google has patched CVE-2026-2441, noting that it is “aware that an exploit for CVE-2026-2441 exists in the wild” as of the Stable Channel update published on February 13, 2026. This…
 SOCRadar
Operation TwinBrand: Massive Fortune 500 Brand Impersonation Campaign Uncovered
SOCRadar’s Threat Hunting Team has uncovered a sophisticated phishing operation that has been targeting Fortune 500 companies and their customers for years. The campaign, attributed to a financially-motivated threat actor…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action