Latest articles
 SOCRadar
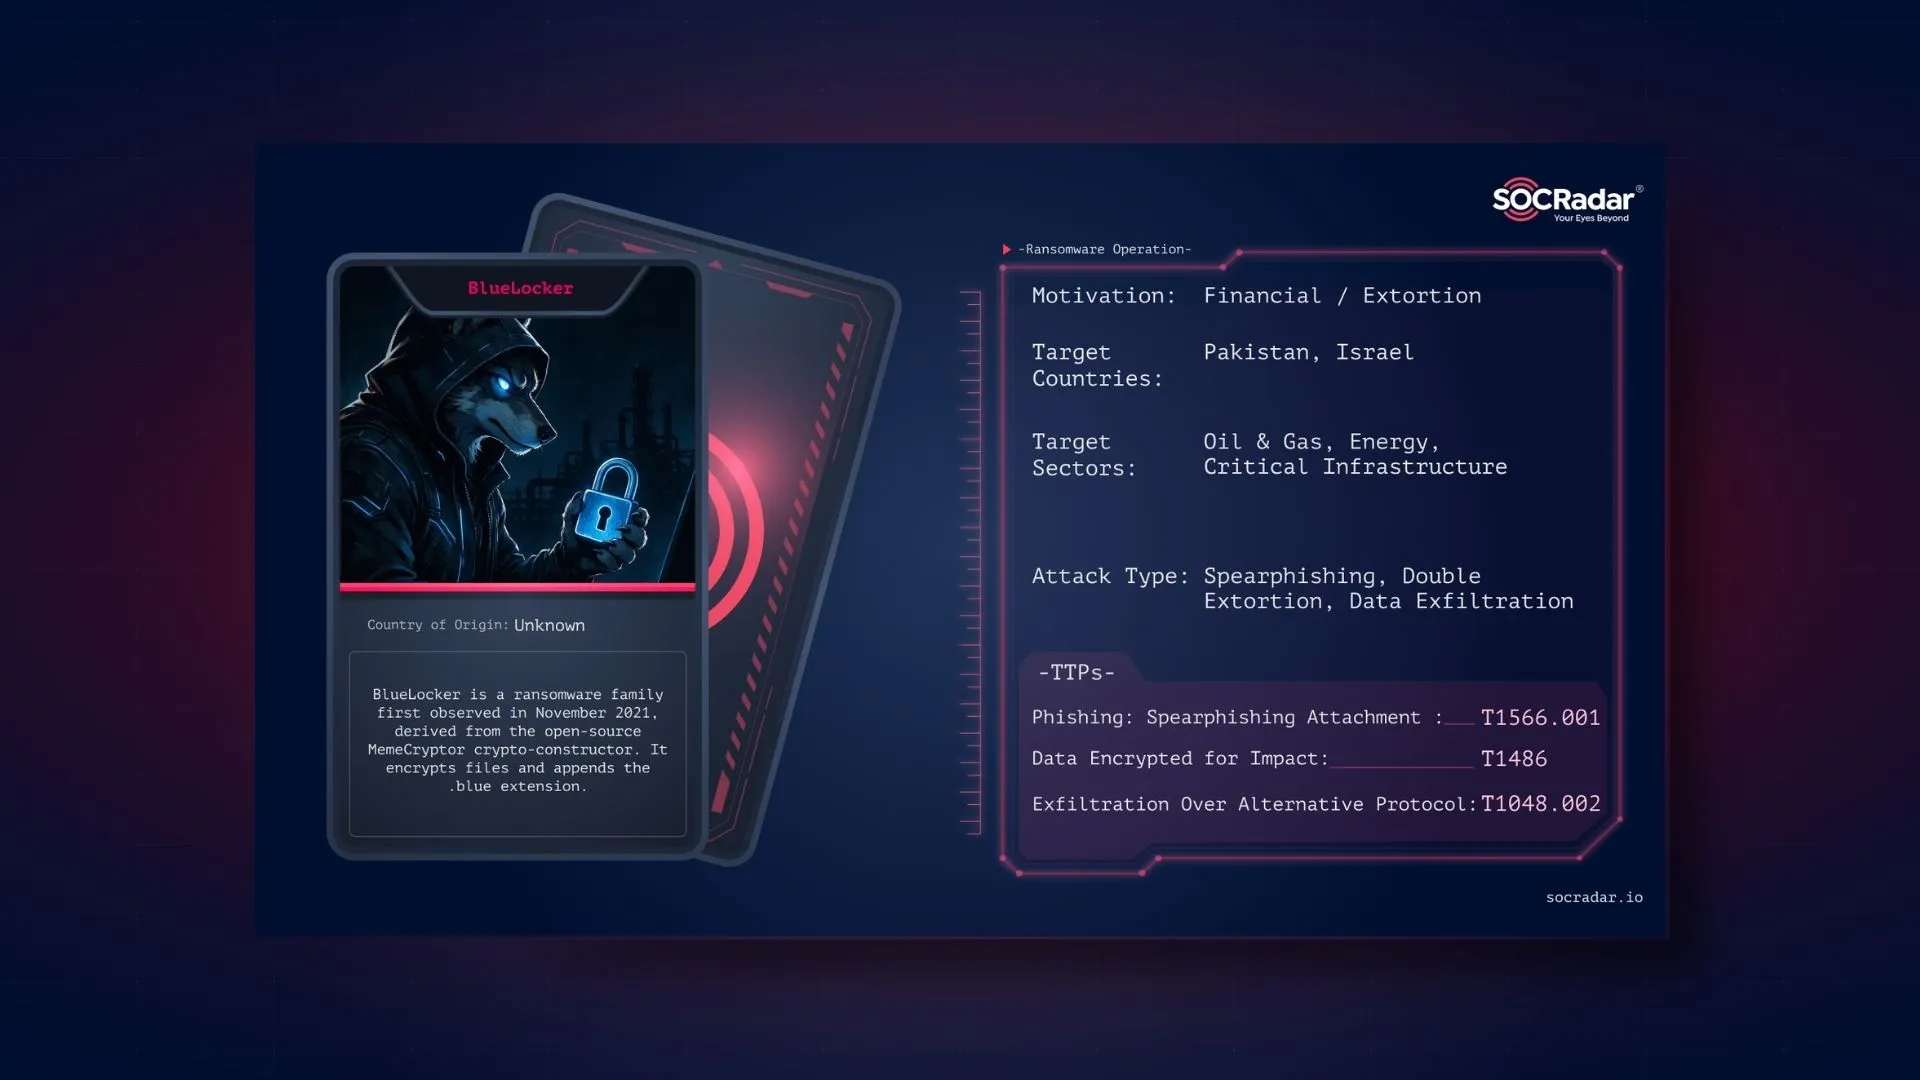
Dark Web Profile: Blue Locker Ransomware
Threat Actor Profile: Blue Locker Ransomware Blue Locker Ransomware, first detected in late 2021, the group stayed low-profile for years before making global headlines in August 2025 with a targeted…
 SOCRadar
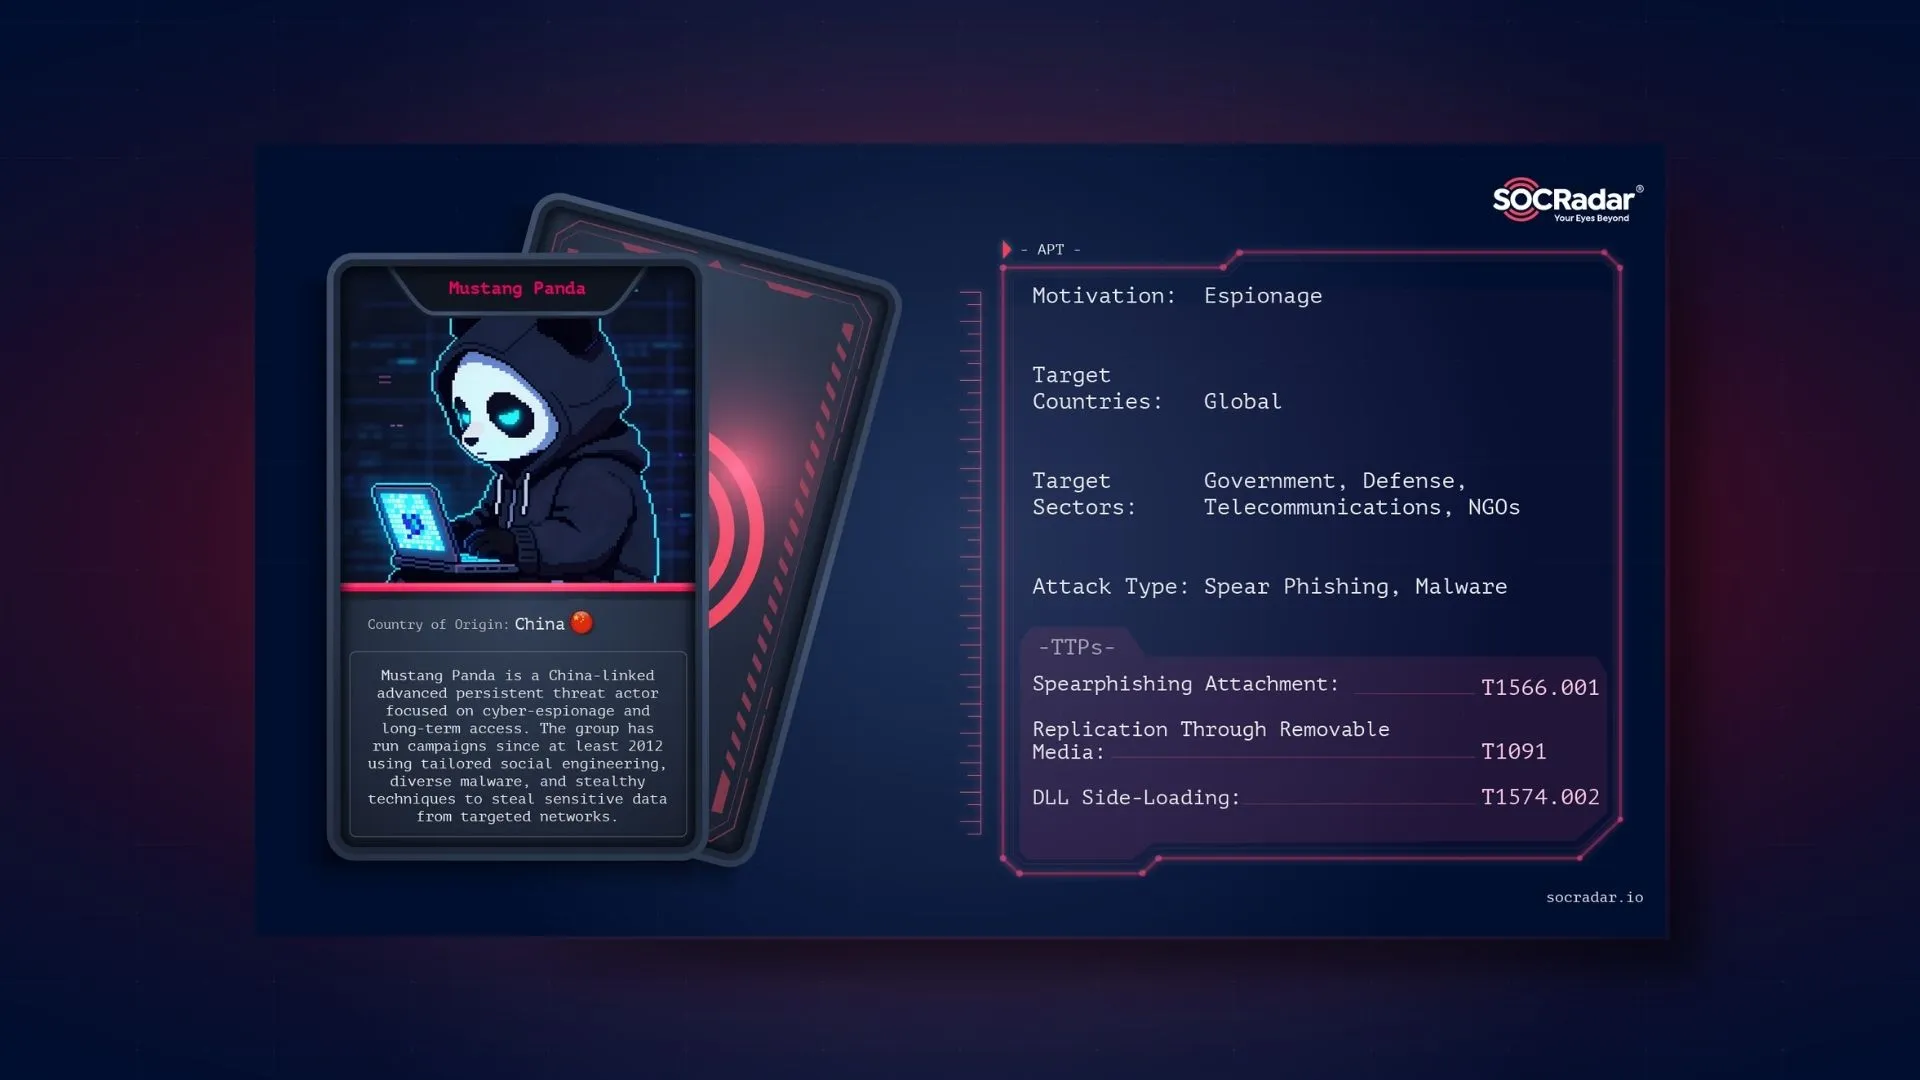
Dark Web Profile: Mustang Panda
Dark Web Profile: Mustang Panda Mustang Panda is one of the most persistent China-nexus cyber espionage groups operating today. Active since at least 2012 , the group has targeted government…
 SOCRadar
Dark Web Profile: Section9 Ransomware
Dark Web Profile: Section9 Ransomware Section9 or SECTION9, is a ransomware operation that skipped the slow, quiet build-up most new brands go through before any victim ever appears on a…
 SOCRadar
Dark Web Profile: ExfilSquad
Dark Web Profile: ExfilSquad ExfilSquad is an emerging data-extortion group that surfaced with a rapid wave of public claims and a Tor-hosted Data Leak Site (DLS). The group is associated…
 SOCRadar
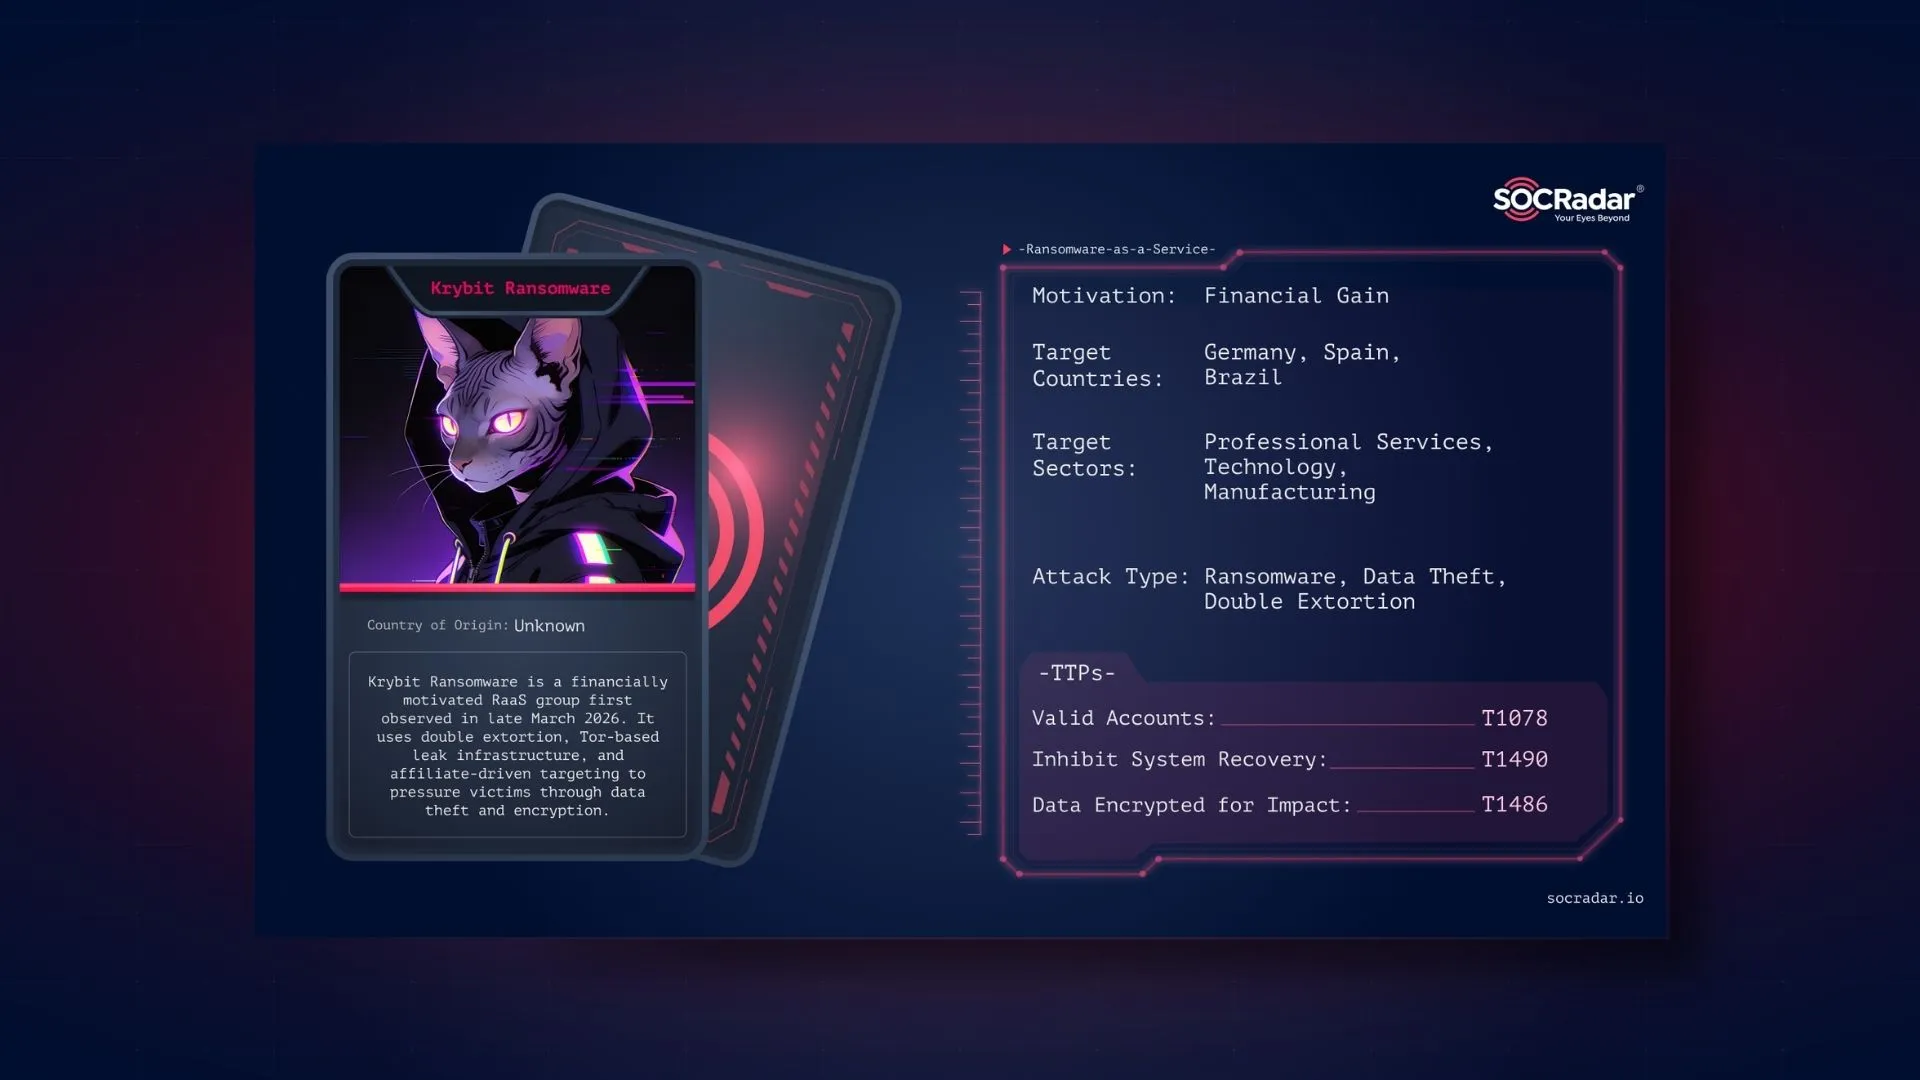
Dark Web Profile: Krybit Ransomware
Dark Web Profile: Krybit Ransomware Emerging from an increasingly crowded and combative ransomware ecosystem, Krybit Ransomware operates as a financially motivated, opportunistic Ransomware-as-a-Service (RaaS) threat. Wi
 SOCRadar
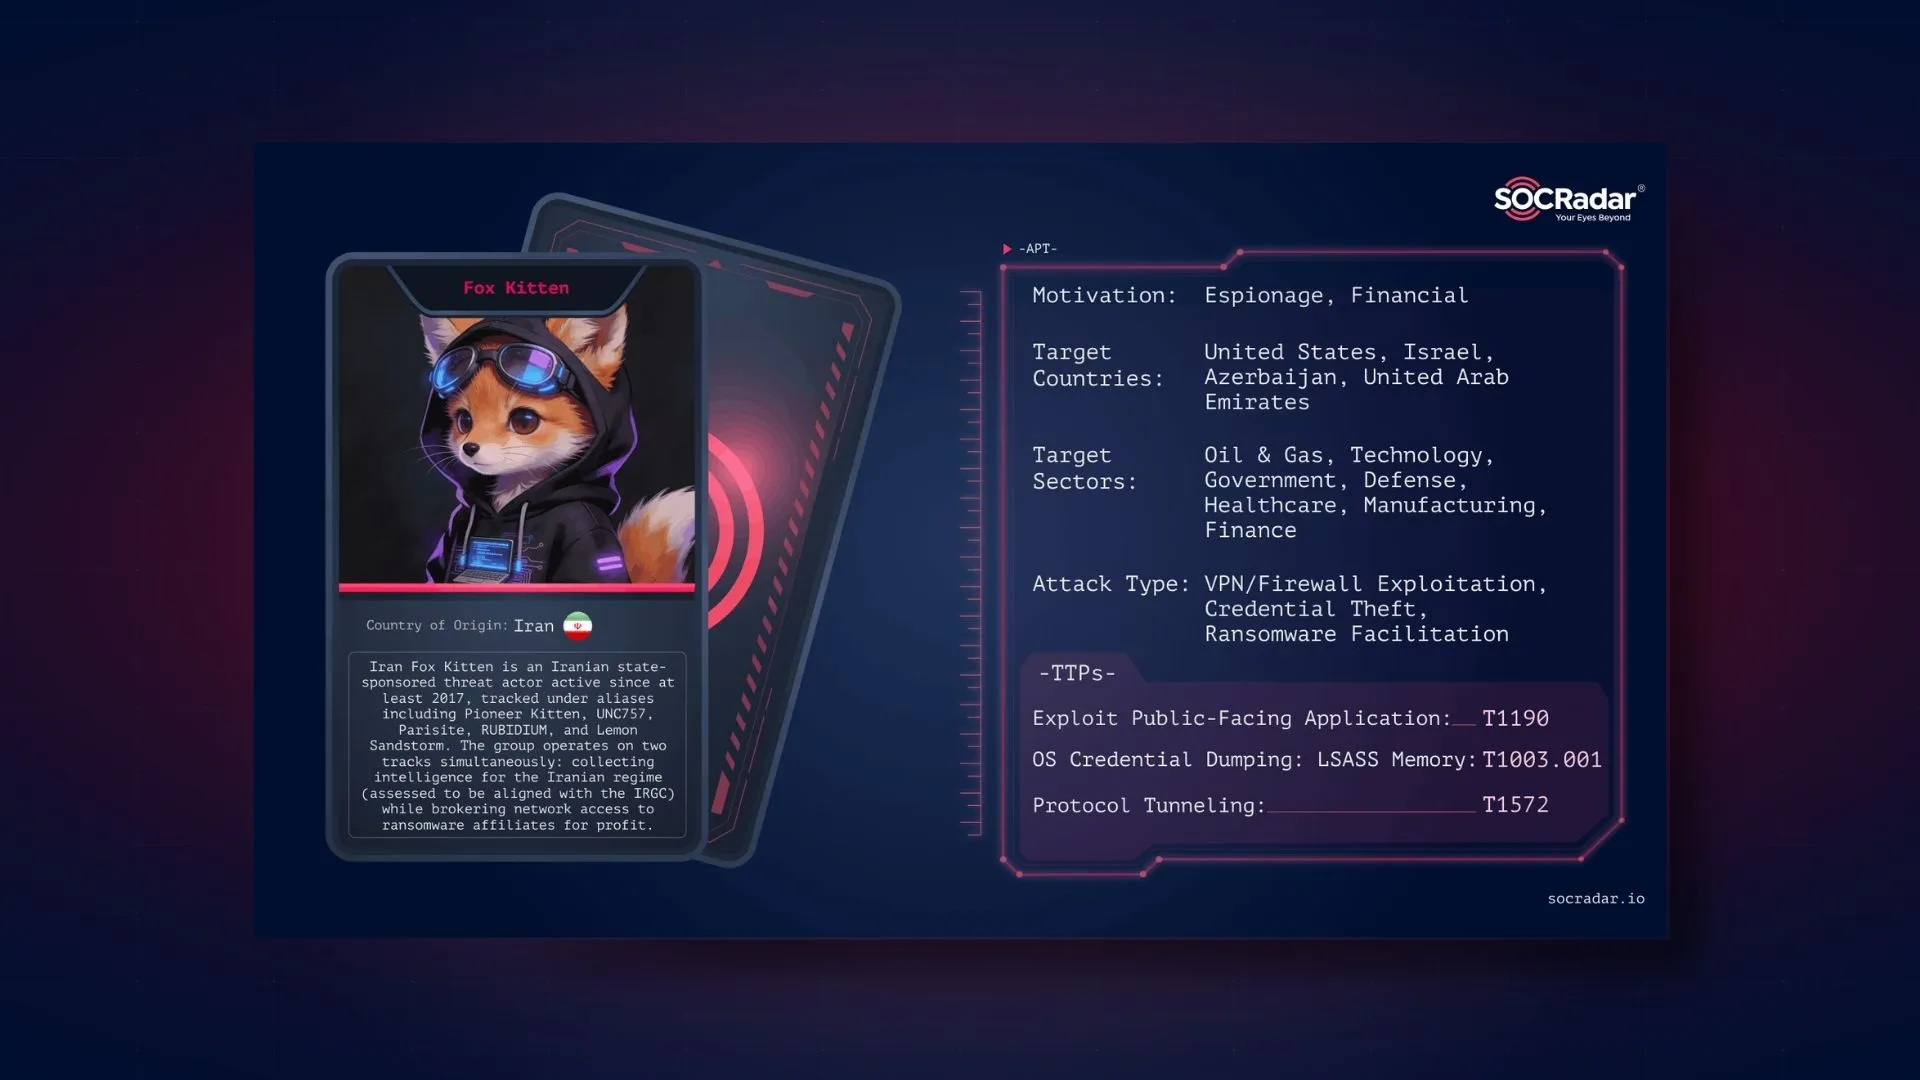
Dark Web Profile: Fox Kitten
Fox Kitten stands out among Iranian Advanced Persistent Threat (APT) groups for operating on two tracks simultaneously: collecting intelligence for the Iranian regime while brokering network access to ransomware affiliates…
 SOCRadar
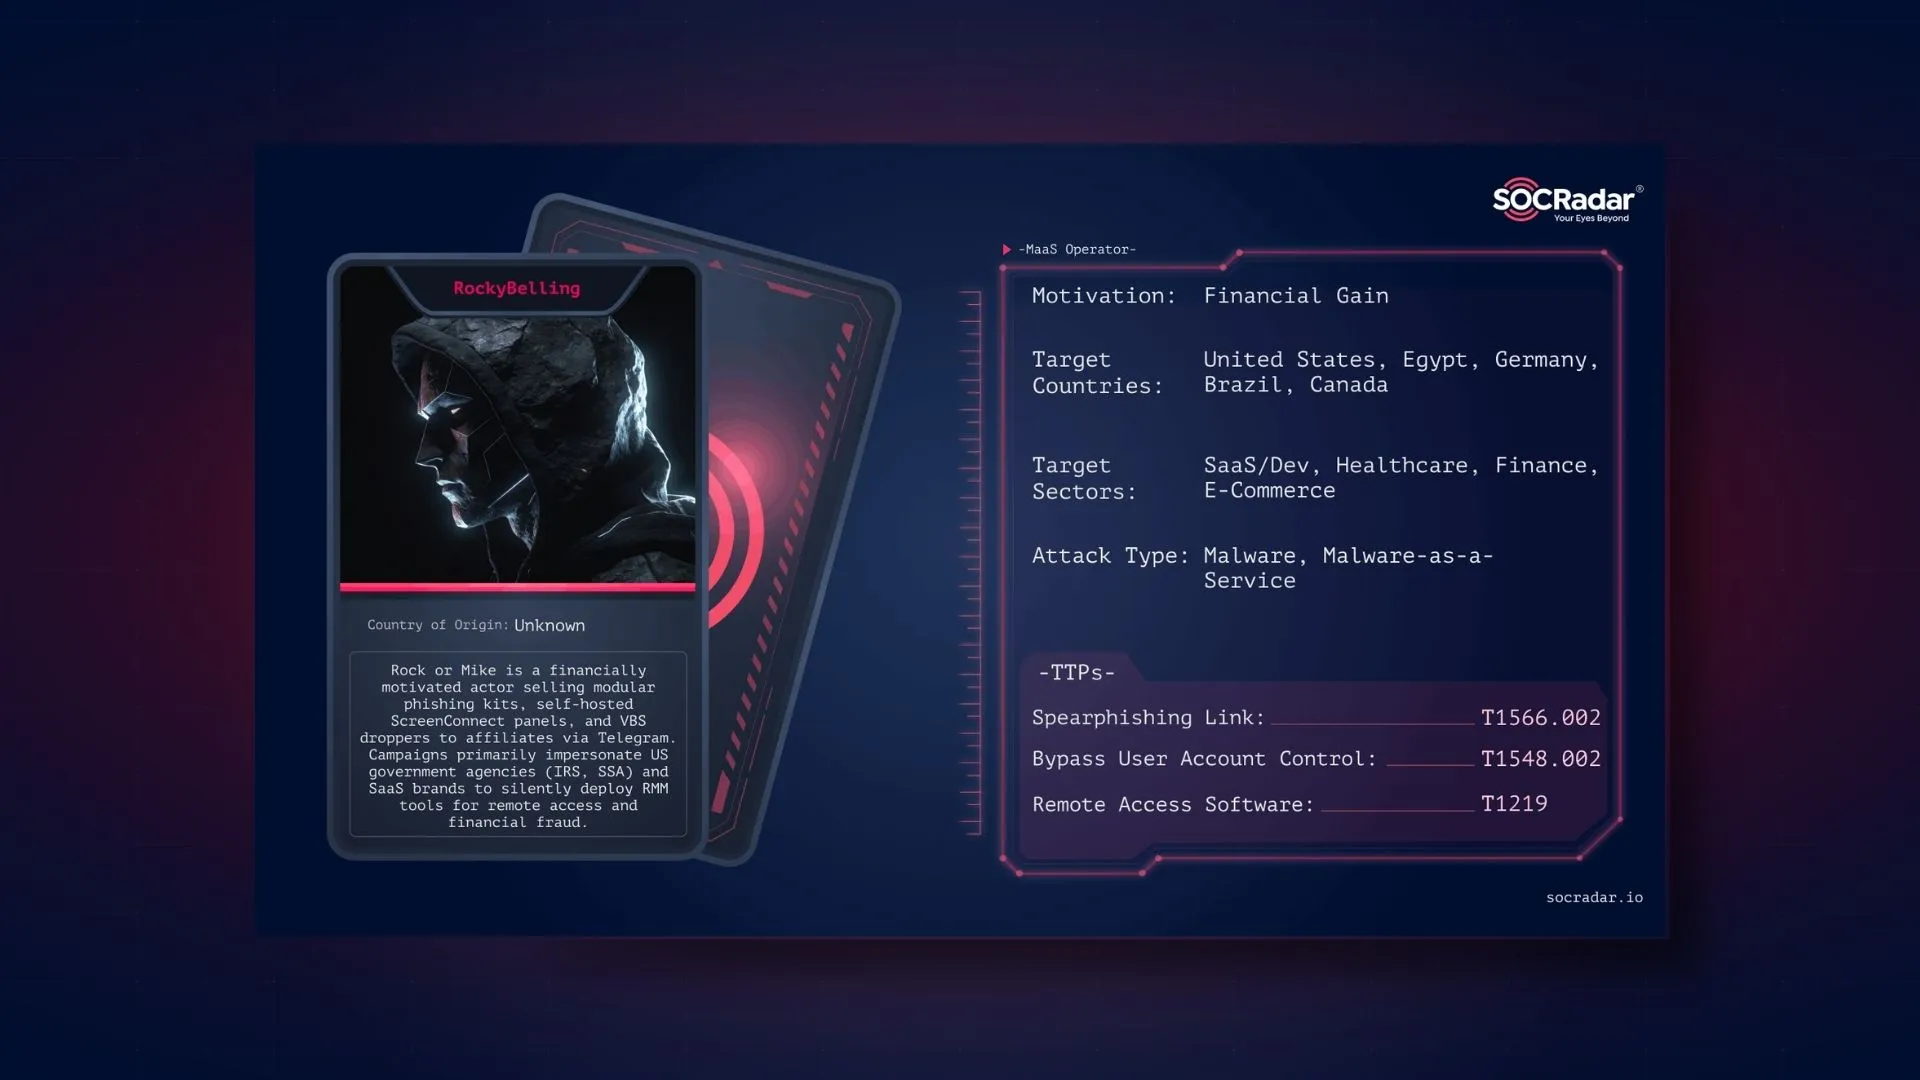
Dark Web Profile: Rock
Most Phishing-as-a-Service operations are run by a faceless brand. Rock is the opposite: a single developer who builds, maintains, and sells an entire phishing and remote access toolkit, then sits…
 SOCRadar
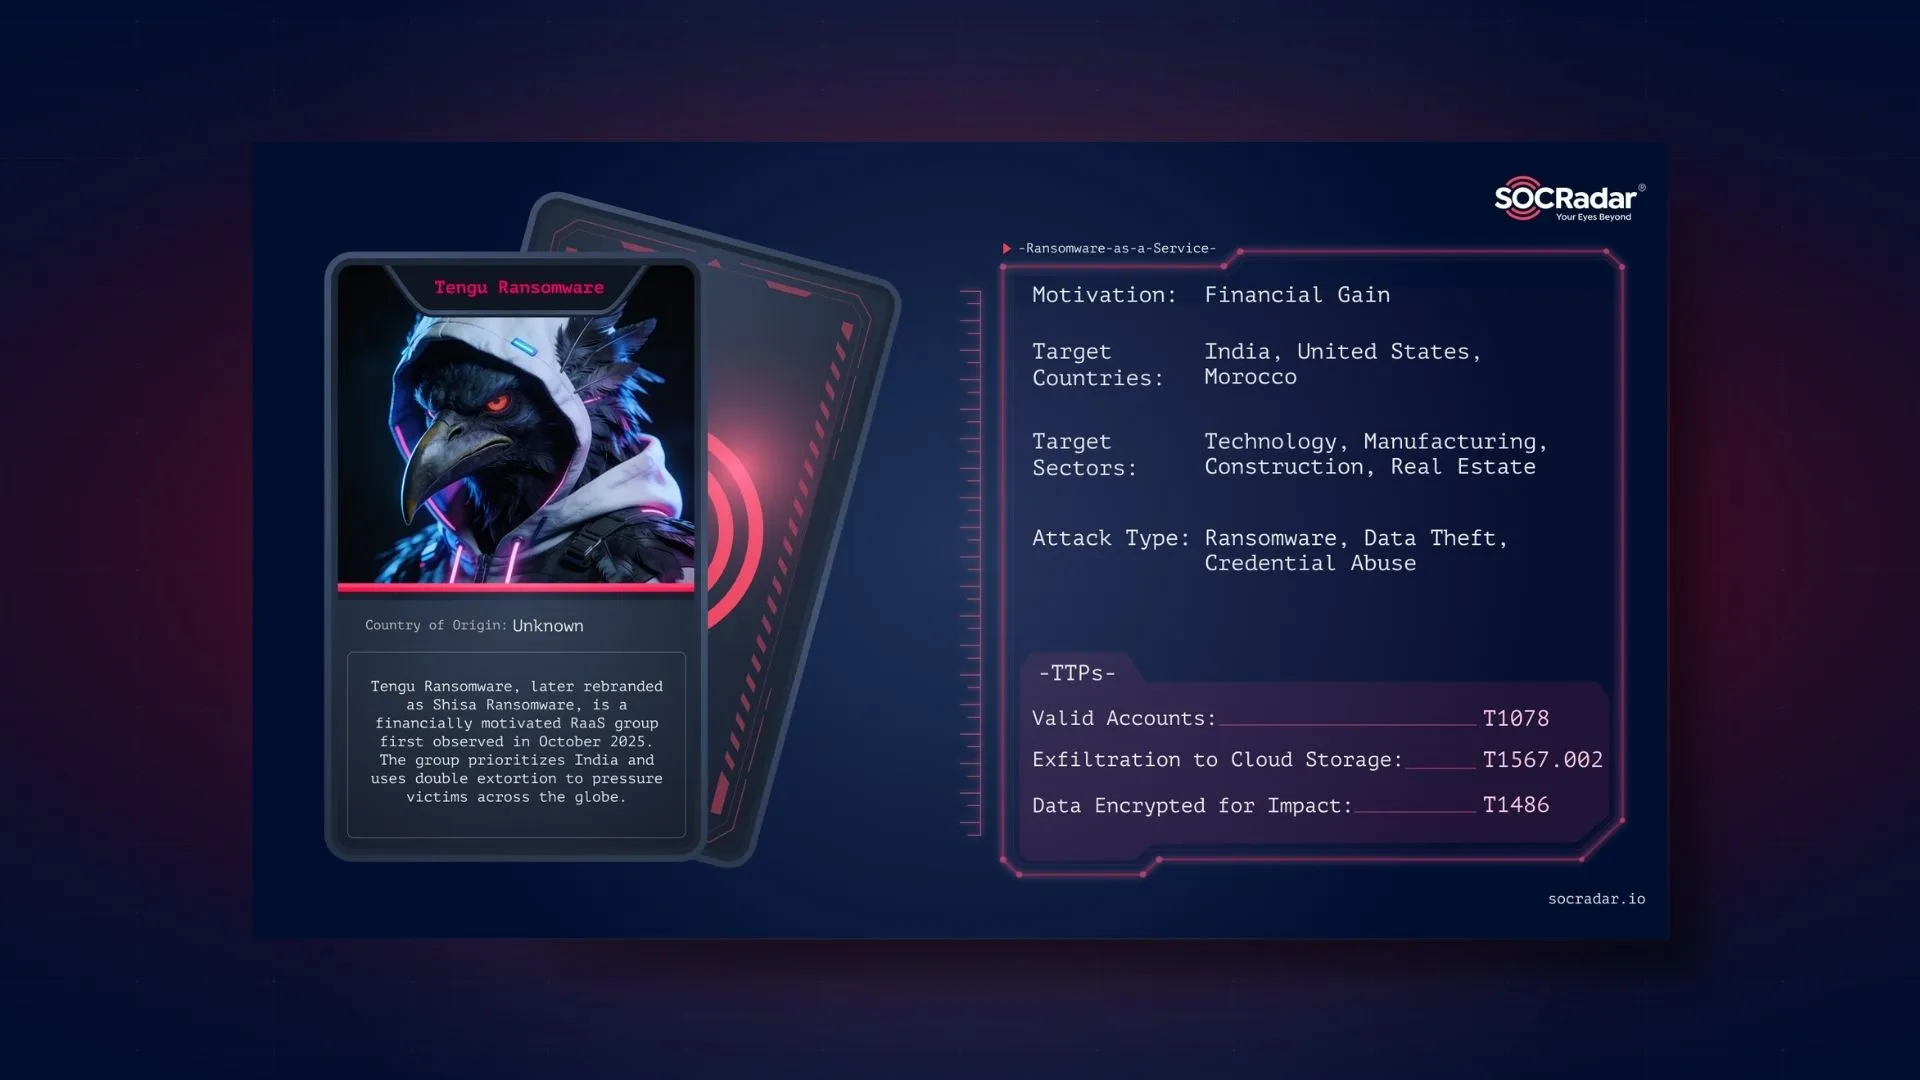
Dark Web Profile: Tengu Ransomware (Shisa)
Despite a measured public persona, Tengu Ransomware operates as a financially motivated, well-organized threat. First observed in late 2025, the group emerged as a Ransomware-as-a-Service (RaaS) operation combining a double-extortion…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action