Sep 08, 2026

Sep 14, 2026
5 Mins Read

Summarize with:
UCQ Leak, Israeli GlobalProtect Access, Digital Nirvana Dump, 32baar, and Ghorer Bazar
SOCRadar Dark Web Team identified several new underground posts, including an alleged Universidad Cuauhtémoc database leak, an alleged GlobalProtect-based access auction for an Israeli manufacturing firm, and an alleged 900GB Digital Nirvana data dump. Other posts advertised an alleged 32baar.com customer database and an alleged Ghorer Bazar e-commerce breach involving more than 4.2 million records.
Receive a Free Dark Web Report for Your Organization:
Alleged UCQ Database Leak is Detected
SOCRadar Dark Web Team detected a dark web post claiming to leak a database allegedly belonging to Universidad Cuauhtémoc (UCQ) in Mexico. The post claims that approximately 381,000 records were exposed, including student personal information and institutional email addresses.
The leaked data was reportedly shared in two files, “ReferenciasUCQ.json” and “UCQ-Alumnos.json.” The sample fields include full names, institutional email addresses, student registration numbers, academic program details, and CURP identifiers, which may increase the risk of targeted phishing, identity theft, and impersonation against students and staff.
Alleged Israeli Manufacturing Access is Auctioned
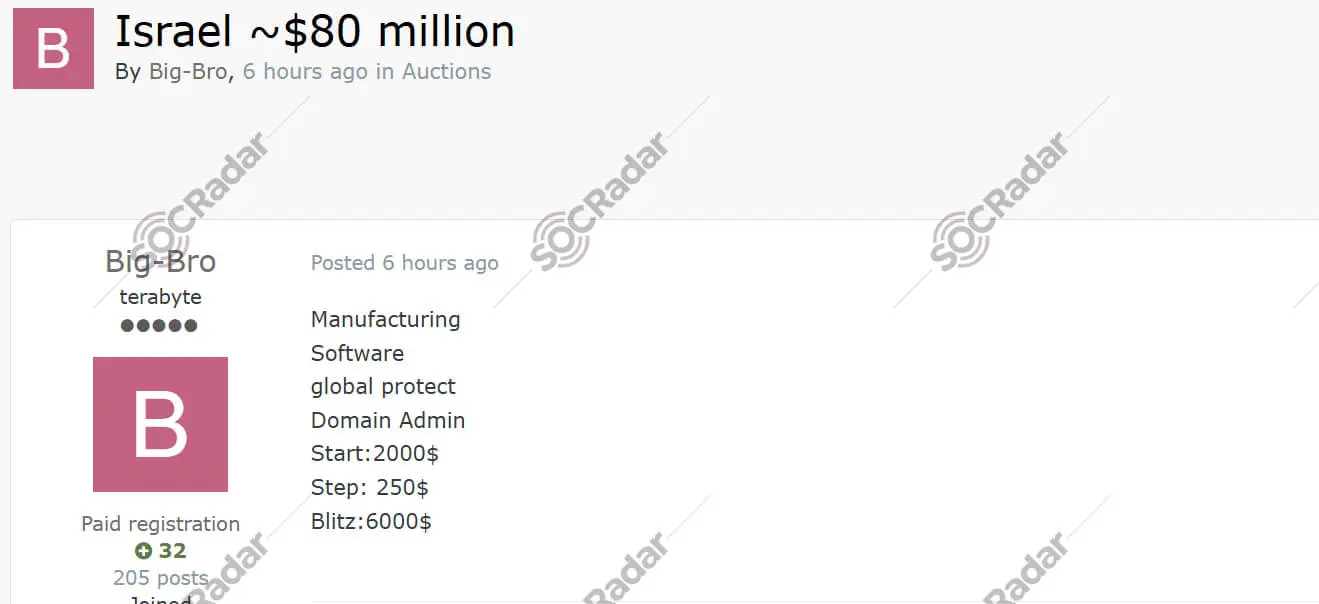
SOCRadar Dark Web Team detected an initial access broker post auctioning administrative access to an Israeli manufacturing company. The actor claimed the target generates approximately $80 million in annual revenue and offered Domain Admin level access.
The listing referenced GlobalProtect as the access vector and set the auction terms at a $2,000 starting bid, $250 step, and $6,000 buy-it-now price. If valid, this type of access could enable ransomware deployment, data theft, or longer-term intrusion activity inside the victim environment.
Alleged Digital Nirvana Data Dump is Offered for Sale
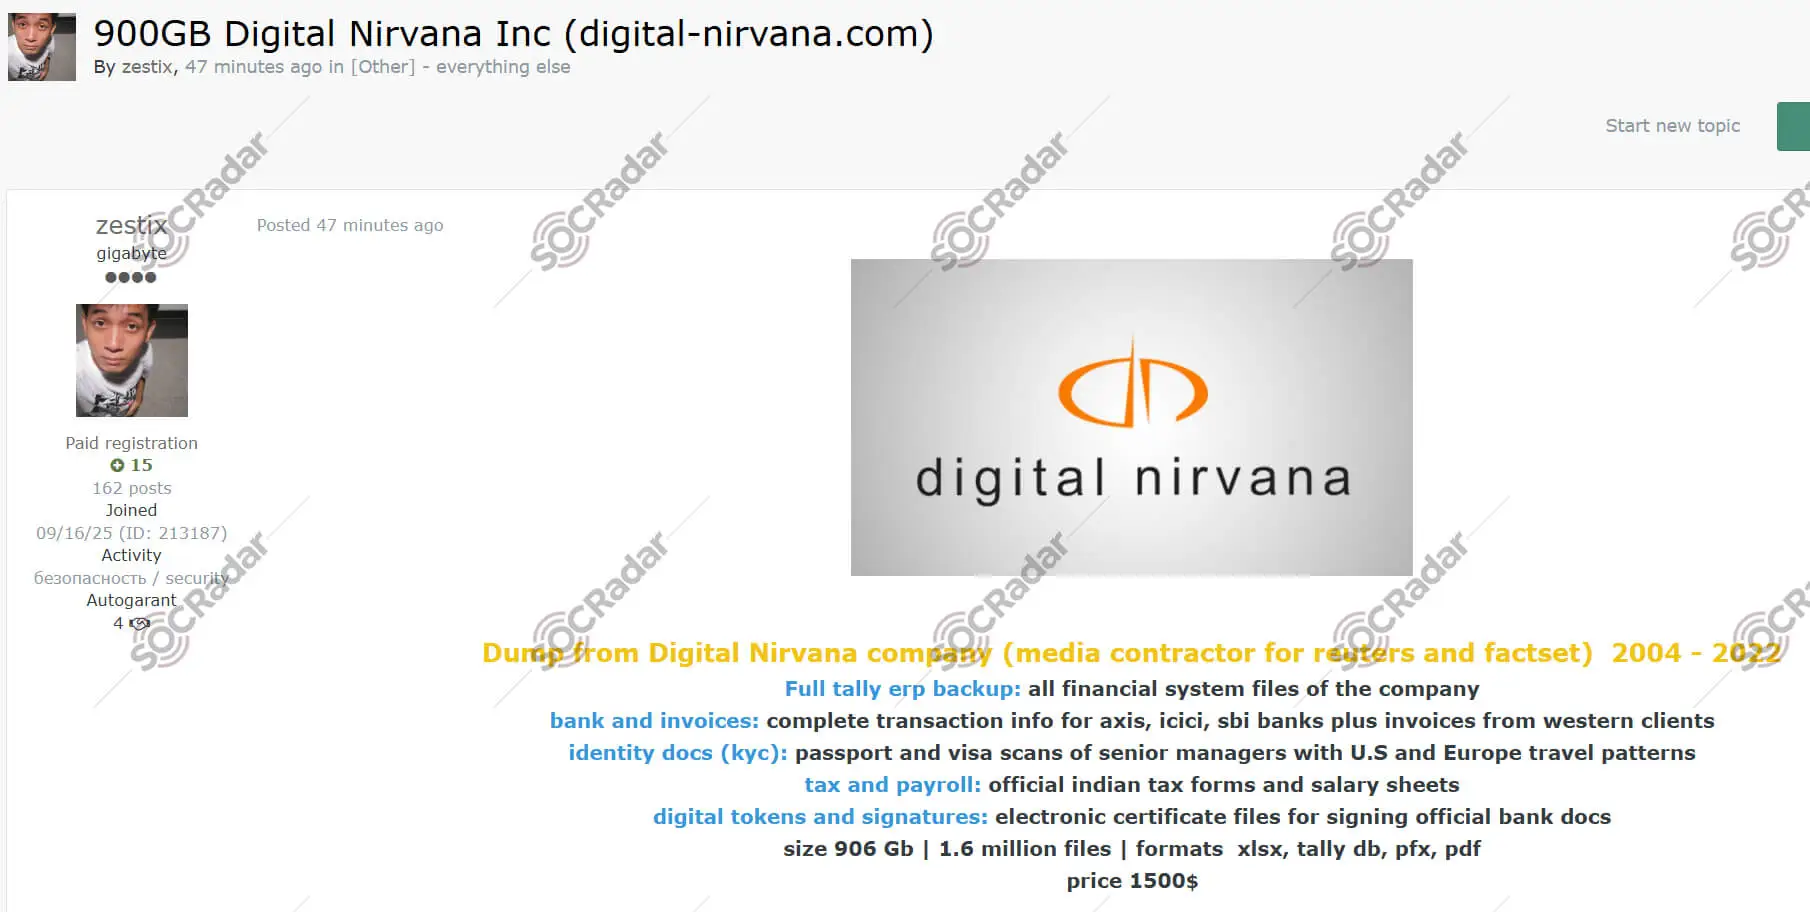
SOCRadar Dark Web Team detected a post advertising an alleged 900GB data dump from Digital Nirvana Inc. The seller claimed the archive contains around 1.6 million files spanning 2004 to 2022, including financial records, KYC documents, and digital signing materials.
The claimed contents include Tally ERP backups, bank transaction records, invoices, passport and visa scans, tax forms, payroll data, and .pfx electronic certificate files. If authentic, the exposure could create risks around financial fraud, document forgery, identity theft, and targeted attacks against company leadership.
Alleged 32baar.com Customer Database is Detected
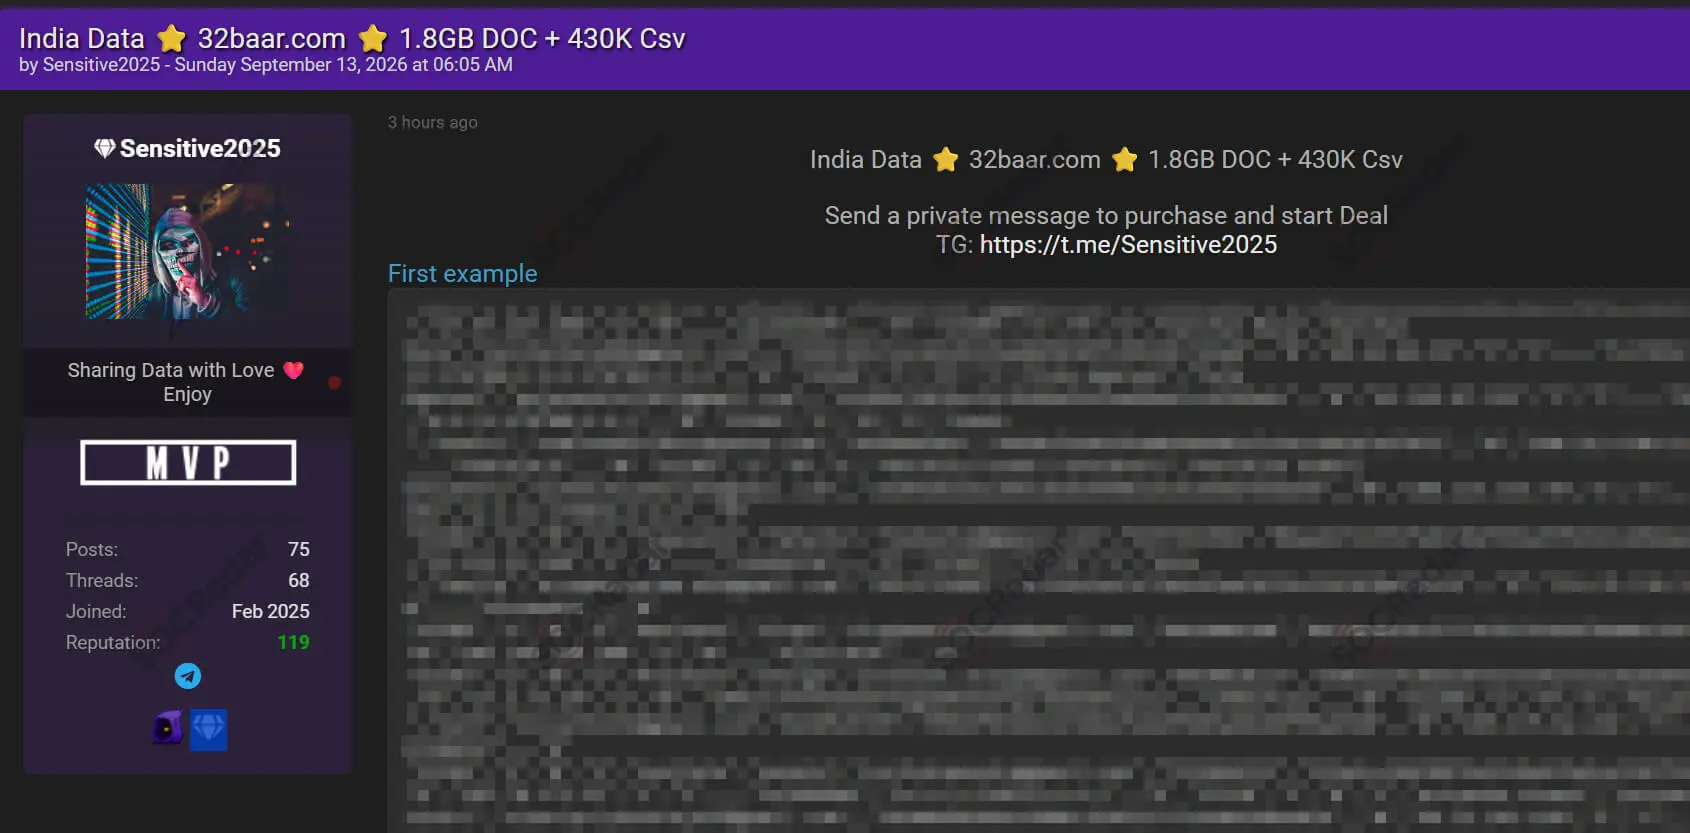
SOCRadar Dark Web Team detected a post advertising an alleged data breach involving 32baar.com, with approximately 430,000 customer records and a 1.8GB dataset offered for sale. The exposed data reportedly includes customer names, email addresses, telephone numbers, physical shipping addresses, hashed passwords, order history, and IP addresses.
The sample structure suggests a compromise of a WordPress-based platform using WooCommerce, with the presence of hashed passwords and order data increasing the risk of credential stuffing, phishing, and social engineering attacks against affected users.
Alleged Ghorer Bazar E-Commerce Breach is Detected
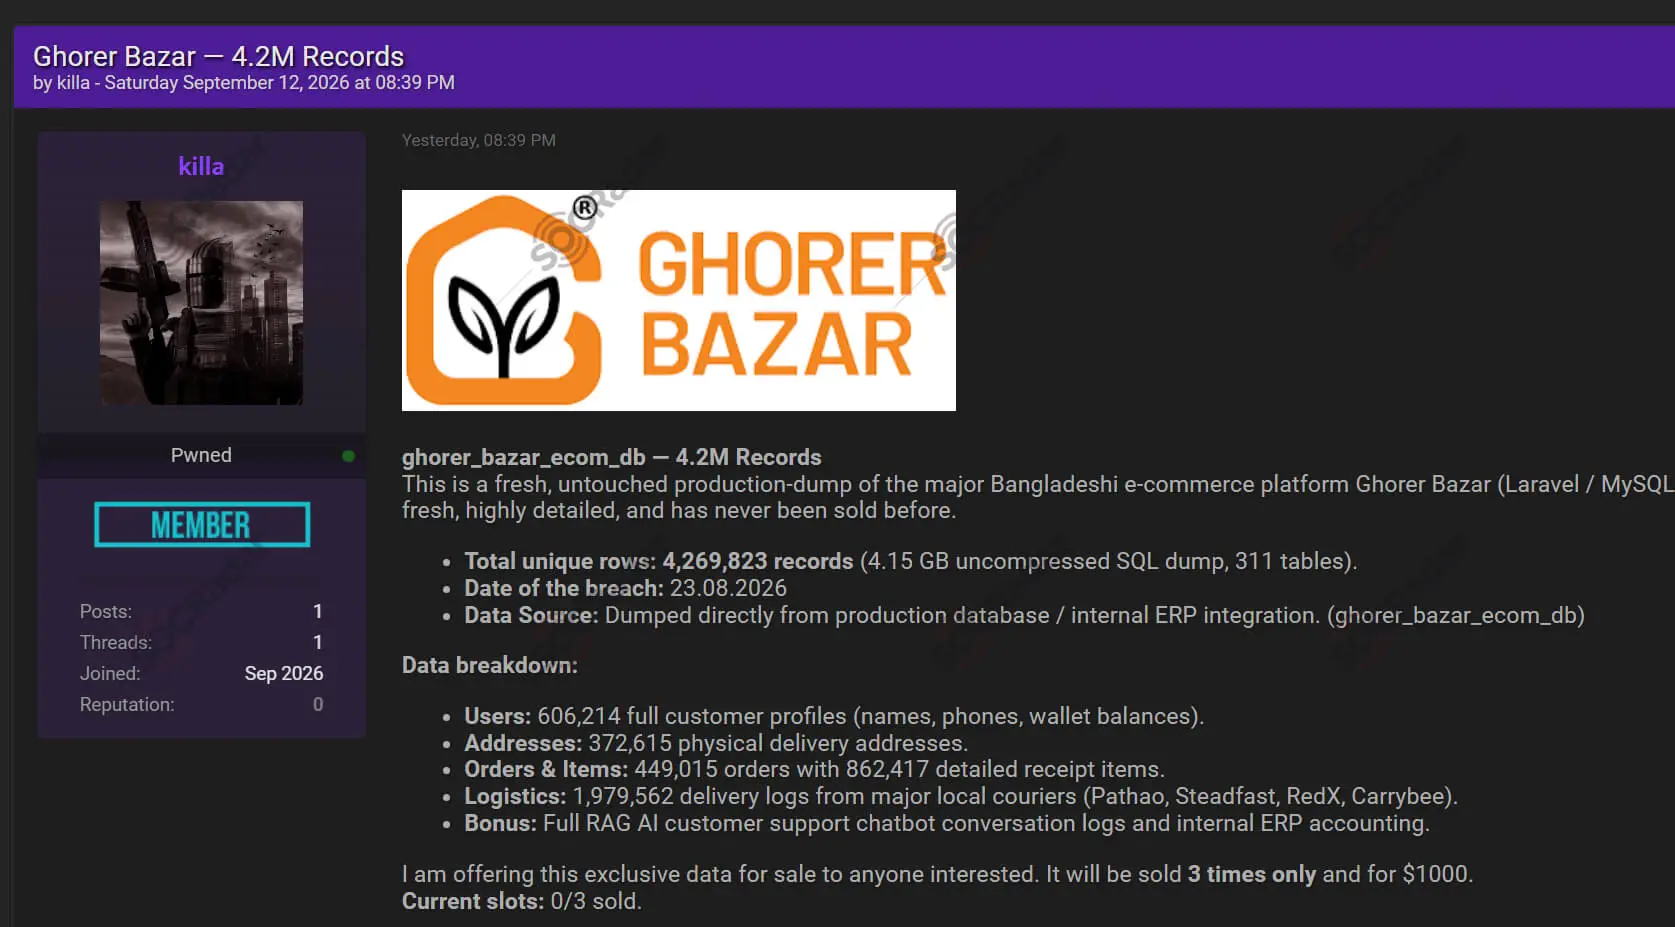
SOCRadar Dark Web Team detected a dark web post claiming a breach of the Bangladeshi e-commerce platform Ghorer Bazar. The actor claimed to offer more than 4.2 million records, including customer profiles, order history, delivery addresses, logistics data, internal ERP information, and RAG AI customer support conversation logs.
The seller claimed the data was taken directly from production systems and listed 606,214 customer profiles, 372,615 delivery addresses, more than 449,000 order records, and nearly 2 million delivery logs from local courier integrations. If verified, the exposure could support phishing, fraud, identity theft, and operational targeting of the platform and its partners.
Powered by DarkMirror™
Gaining visibility into deep and dark web threats can be extremely useful from an actionable threat intelligence and digital risk protection perspective. However, monitoring all sources is simply not feasible, which can be time-consuming and challenging. One click-by-mistake can result in malware bot infection. To tackle these challenges, SOCRadar’s DarkMirror™ screen empowers your SOC team to follow up with the latest posts of threat actors and groups filtered by the targeted country or industry.
Table Of Content
UCQ Leak, Israeli GlobalProtect Access, Digital Nirvana Dump, 32baar, and Ghorer Bazar
Alleged UCQ Database Leak is Detected
Alleged Israeli Manufacturing Access is Auctioned
Alleged Digital Nirvana Data Dump is Offered for Sale
Alleged 32baar.com Customer Database is Detected
Alleged Ghorer Bazar E-Commerce Breach is Detected
Related Articles

Dark Web Market: Anubis Market