Latest articles
 SOCRadar
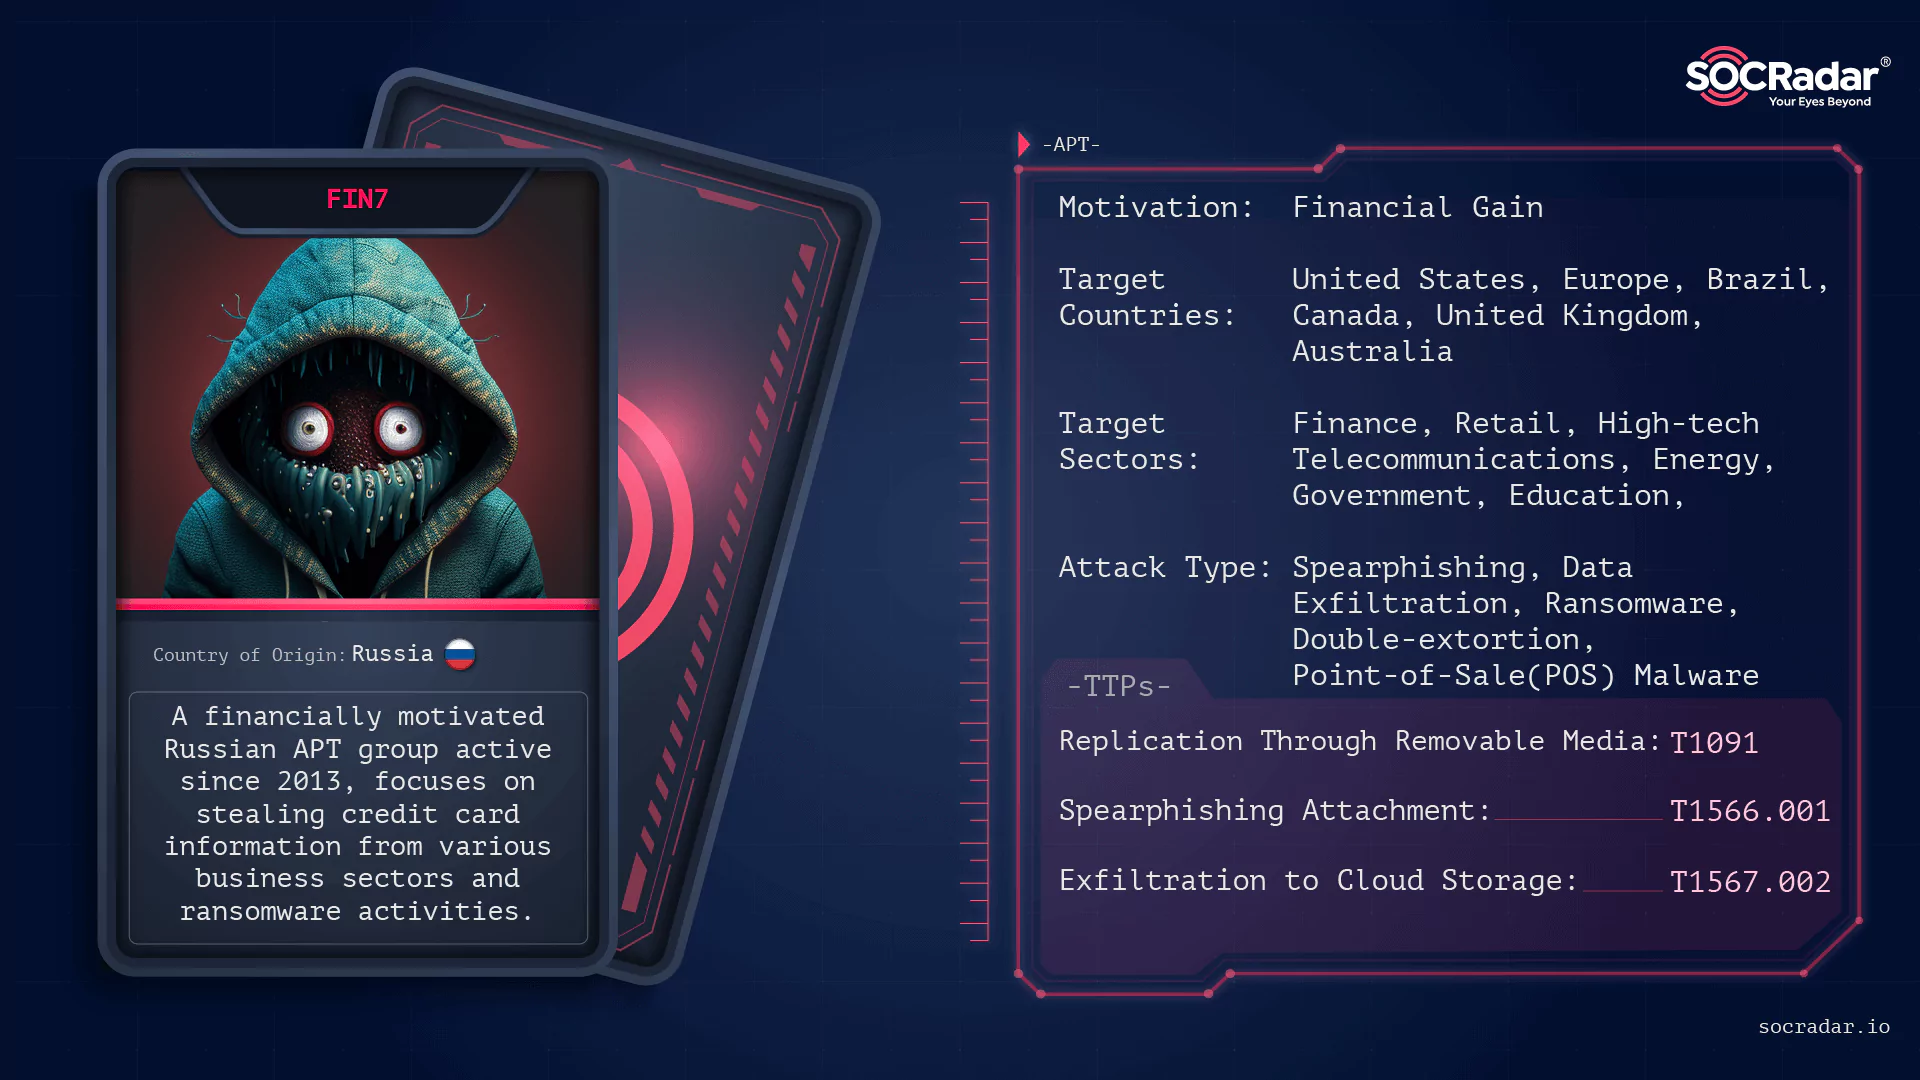
Dark Web Profile: FIN7
In the world of cybercrime, a name resounds with an unsettling echo – FIN7 . This notorious cyber gang has left its mark on the globe, causing digital chaos wherever…
 SOCRadar
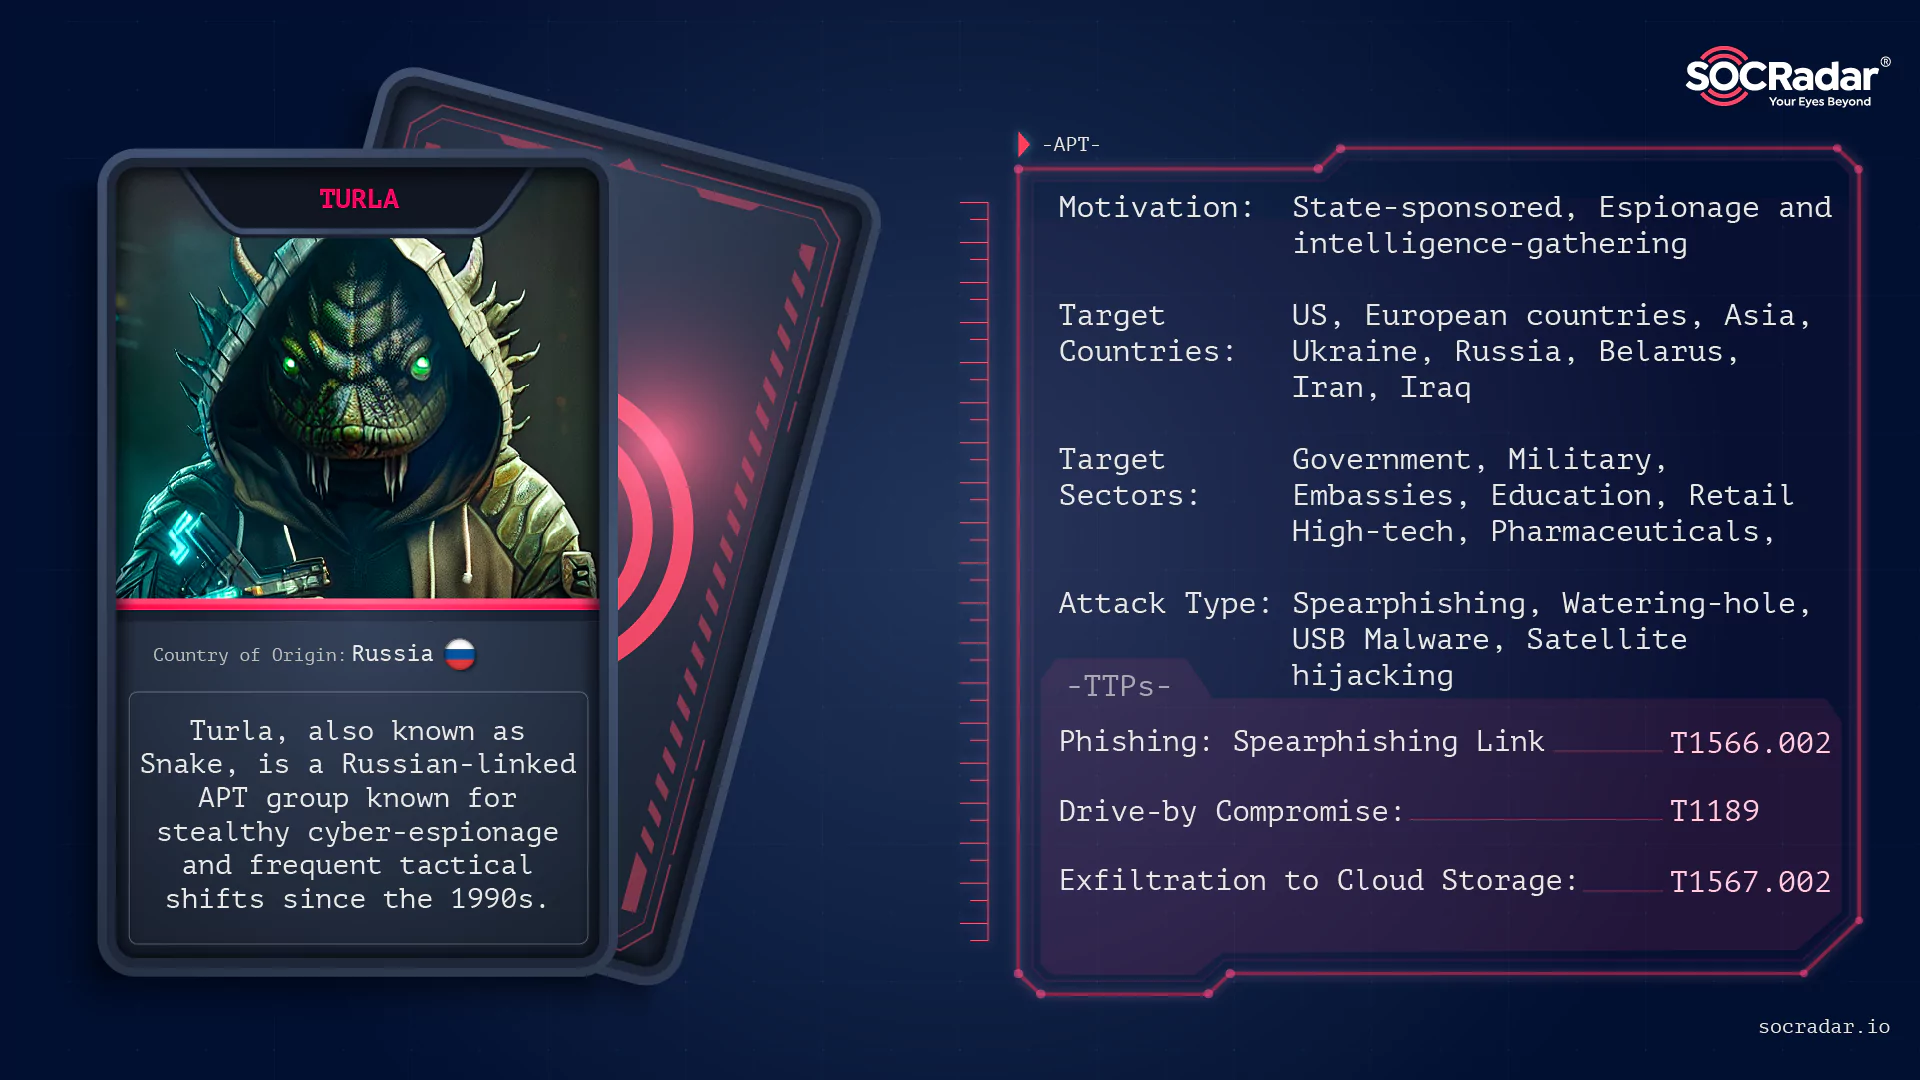
Dark Web Profile: Turla
In the digital age, war has transitioned into the virtual world, where many types of cybercriminals, such as hacktivists and nation-state actors, are called Advanced Persistent Threats (APT) play a…
 SOCRadar
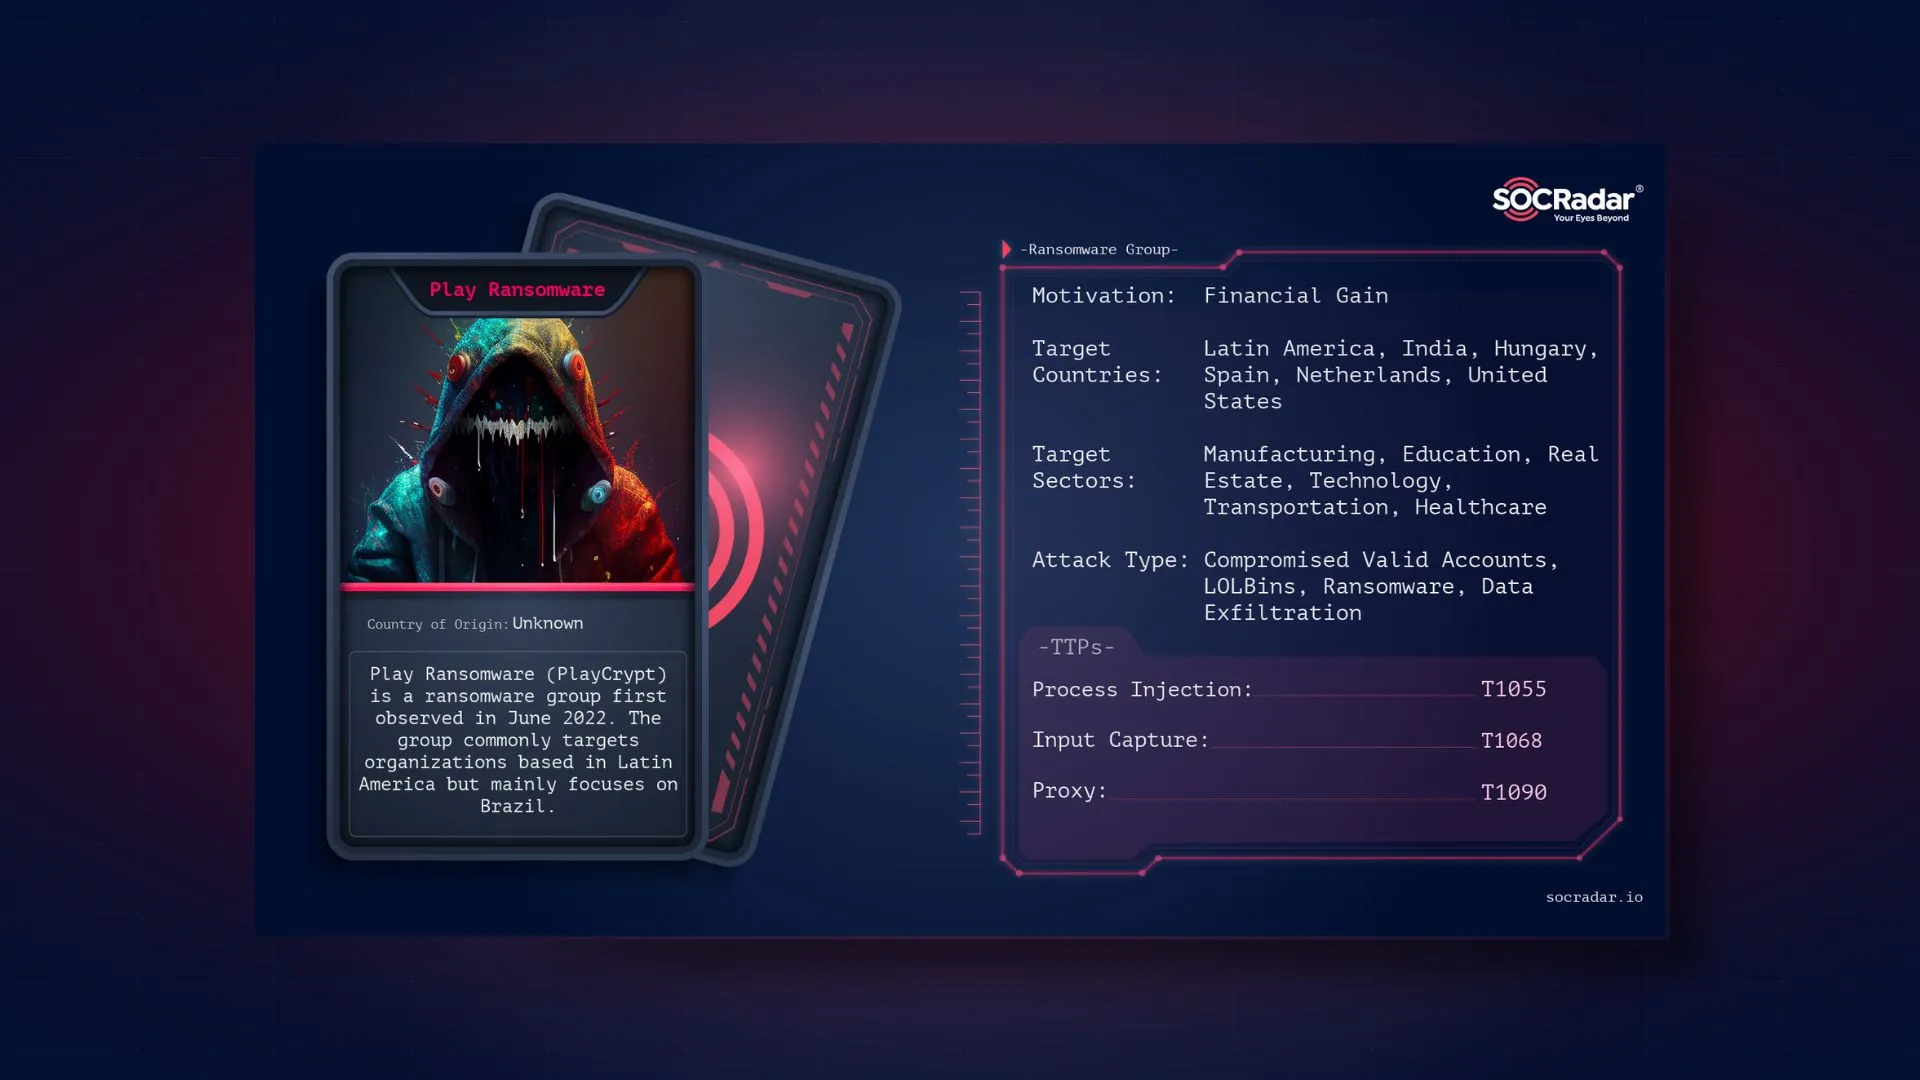
Dark Web Profile: Play Ransomware
[Update] July 22, 2024: “Play Ransomware Broadens Its Scope with New Linux Variant Targeting ESXi” [Update] December 19, 2023: “Collaborative Advisory on Play Ransomware: 300 Entities Affected by October 2023.”…
 SOCRadar
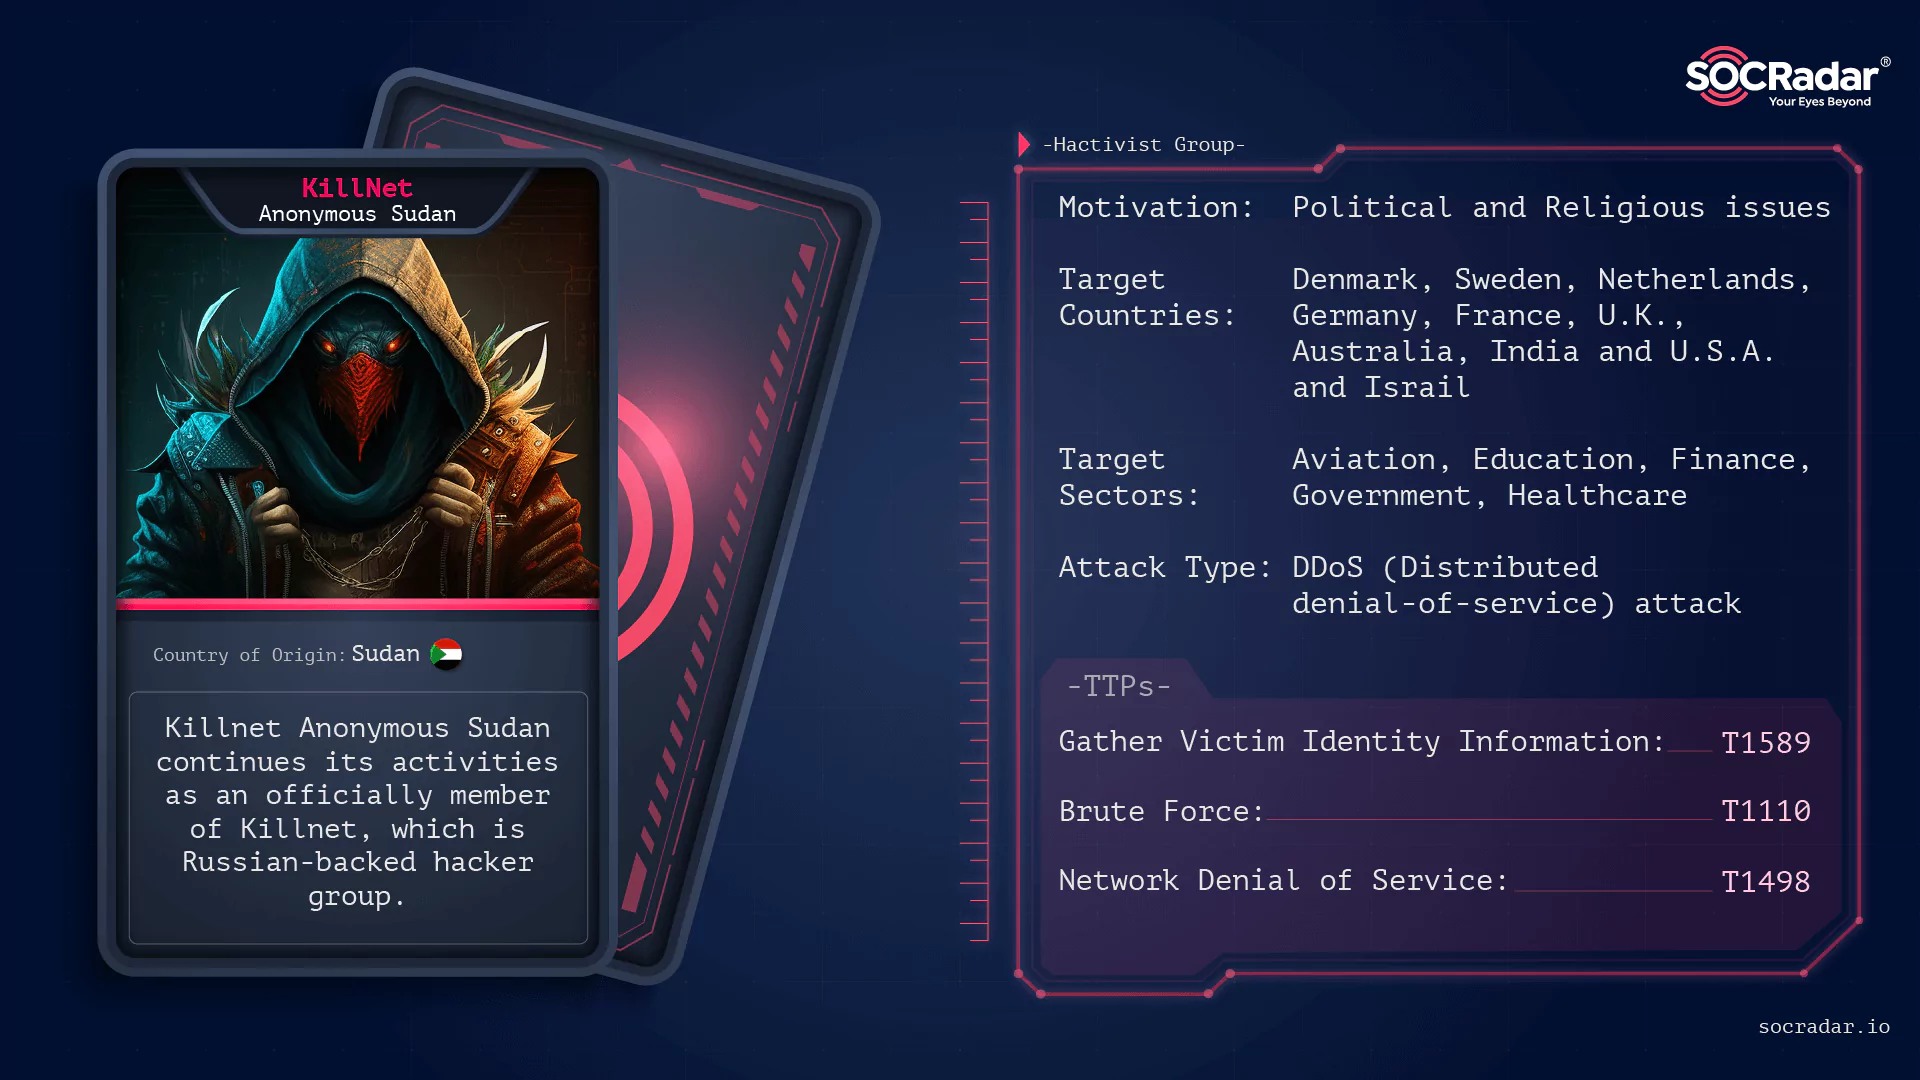
Dark Web Profile: KillNet Anonymous Sudan
[Update] October 17, 2024: “Indictment of Two Sudanese Nationals Behind Anonymous Sudan” [Update] July 5, 2023: In a recent cyber attack, Anonymous Sudan claimed to have targeted the login portal of…
 SOCRadar
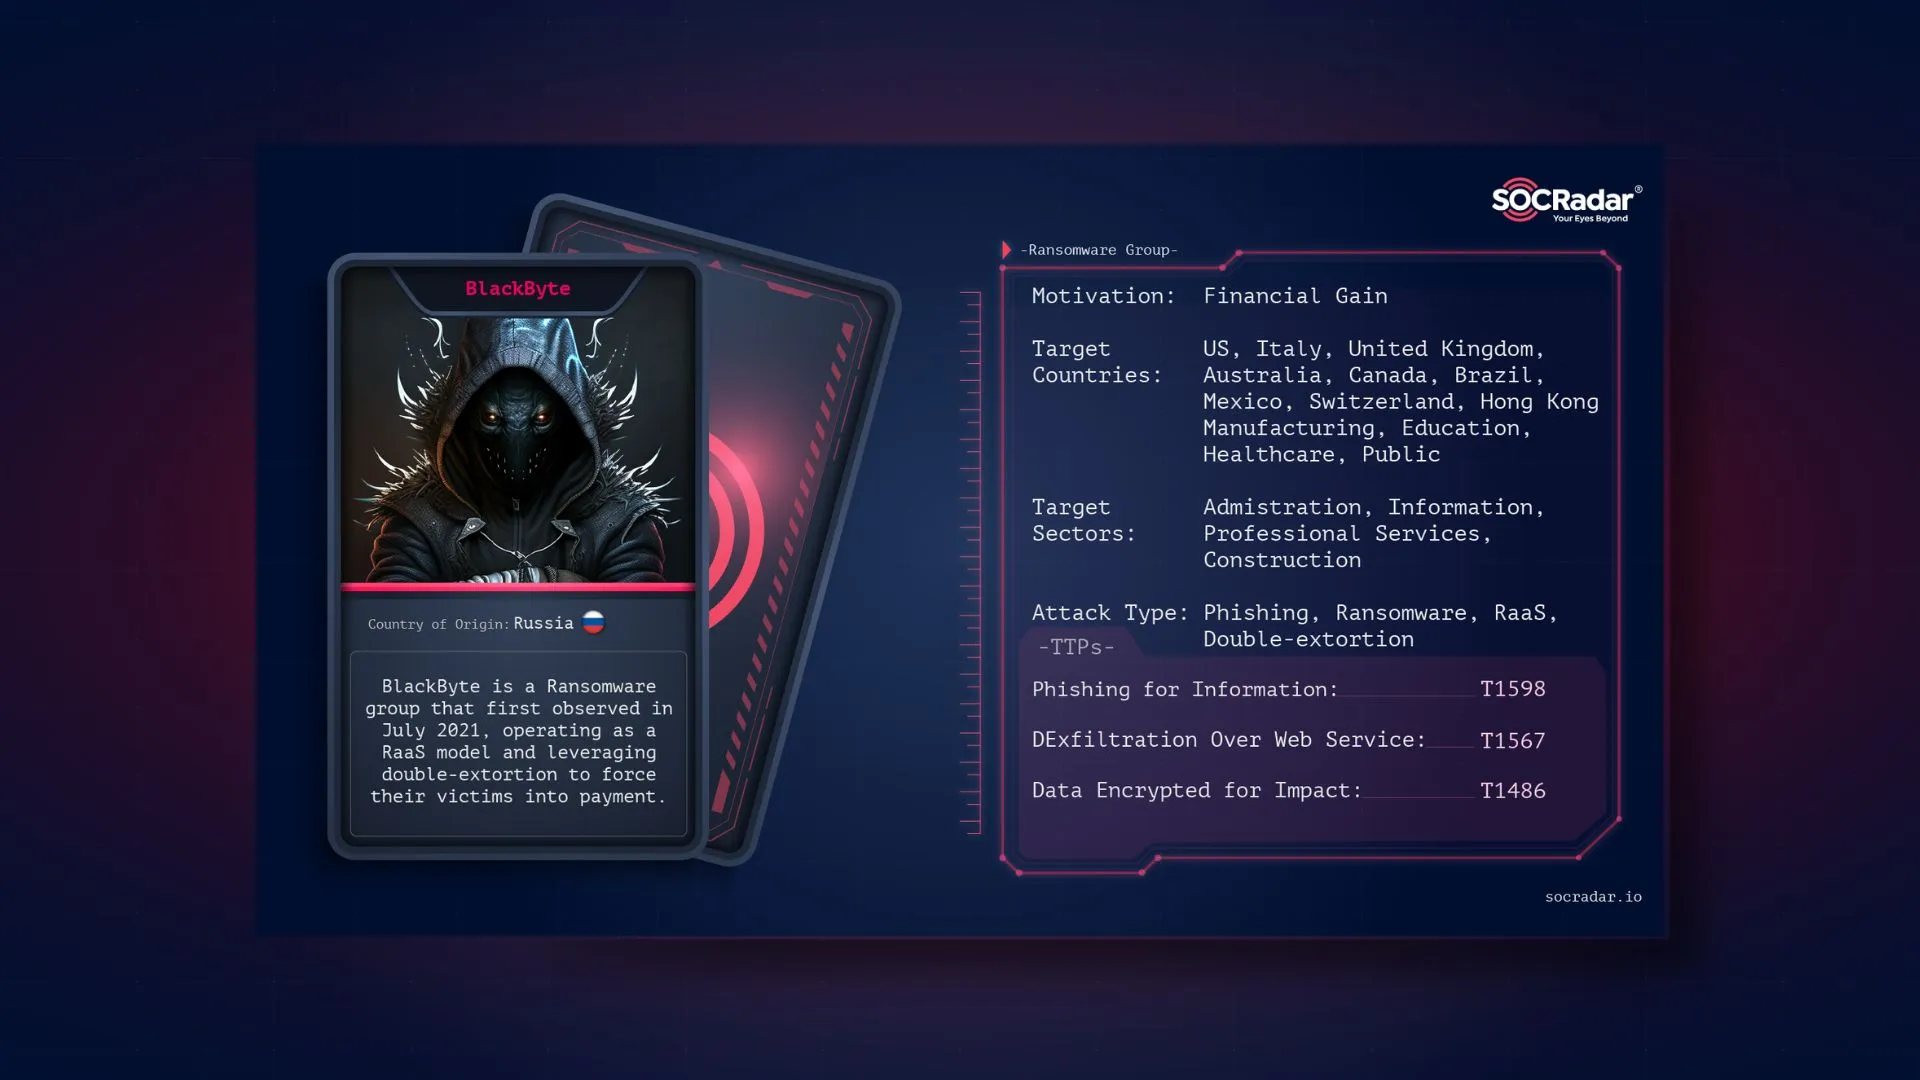
Dark Web Profile: BlackByte Ransomware
Ransomware has been one of the most glaring threats against organizations in recent years. Since 2021 SOCRadar has detected around 5,600 ransomware attacks . There was a rise from 2021…
 SOCRadar
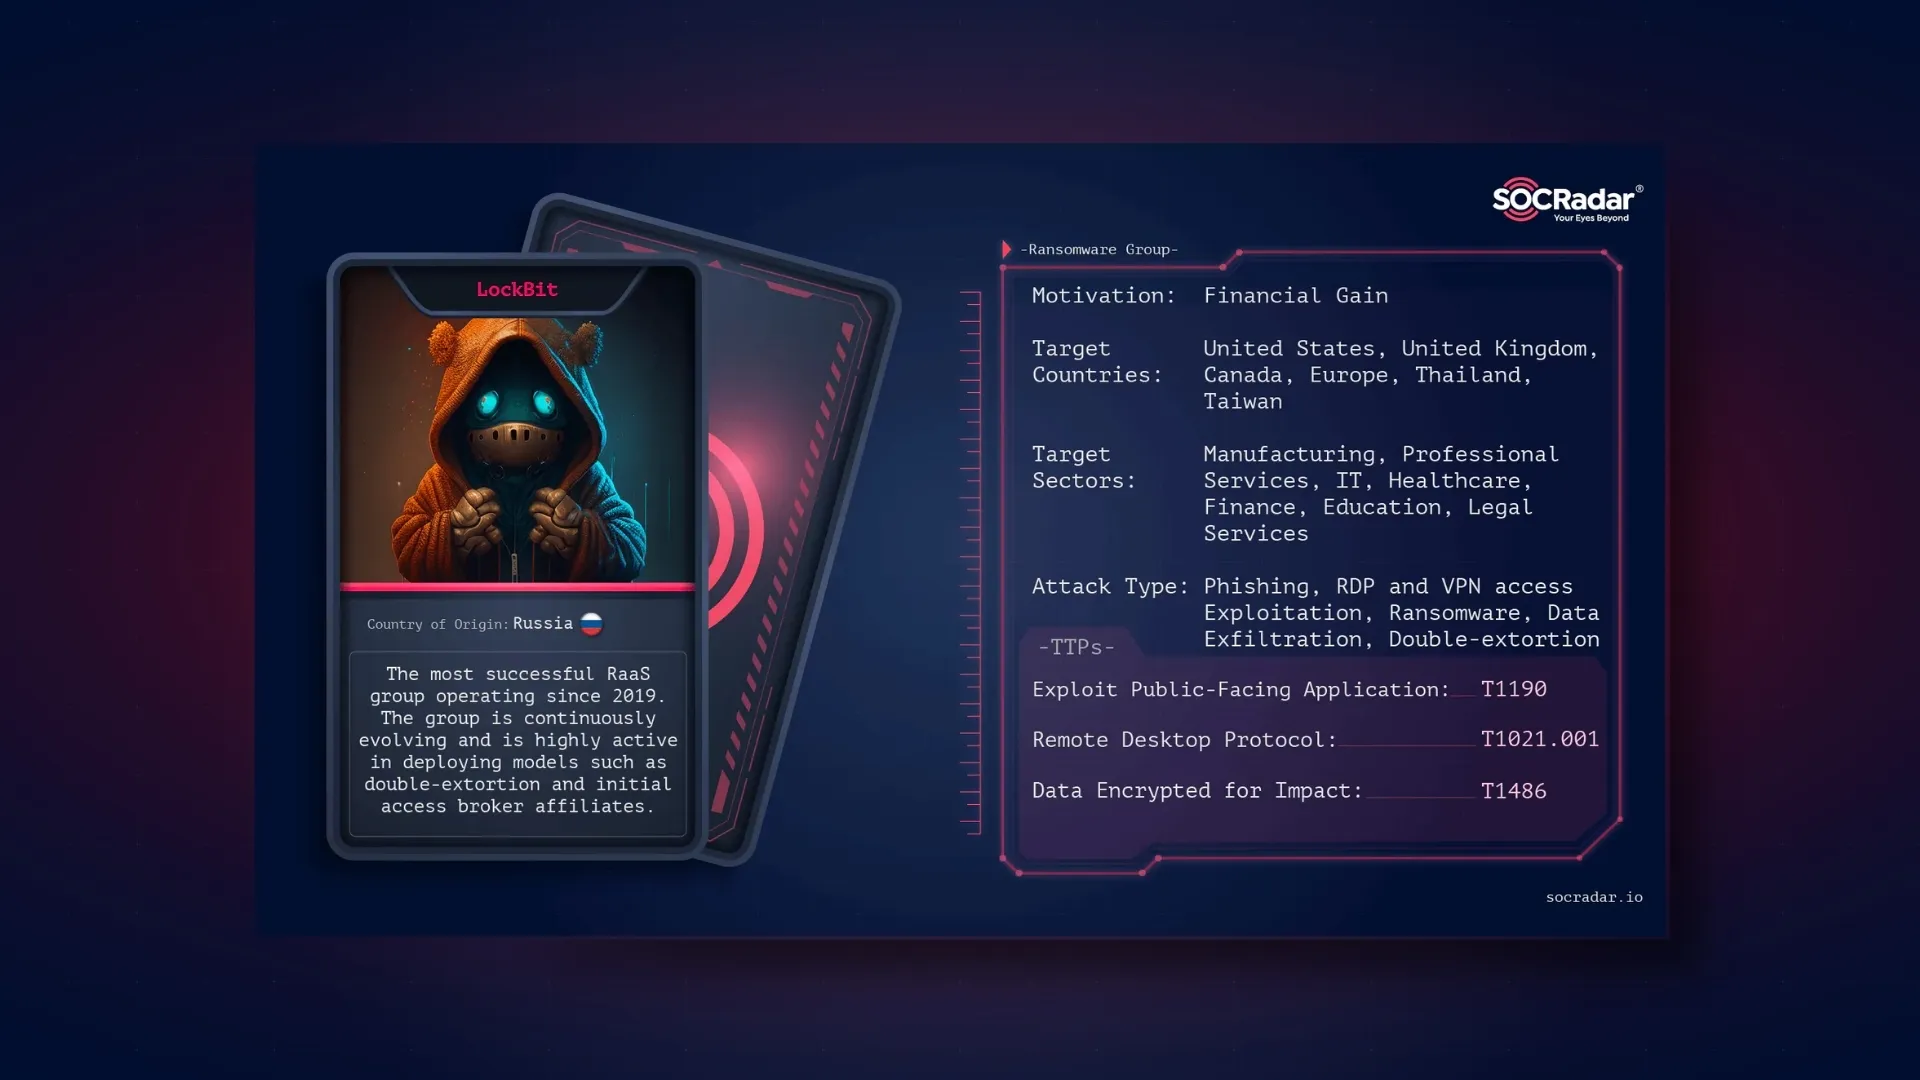
Dark Web Profile: LockBit Ransomware
LockBit is a long-running Ransomware-as-a-Service (RaaS) operation that has survived repeated malware upgrades, affiliate turnover, infrastructure exposure, and major law-enforcement disruption. First observed in 2019, the ransomware has evolved through…
 SOCRadar
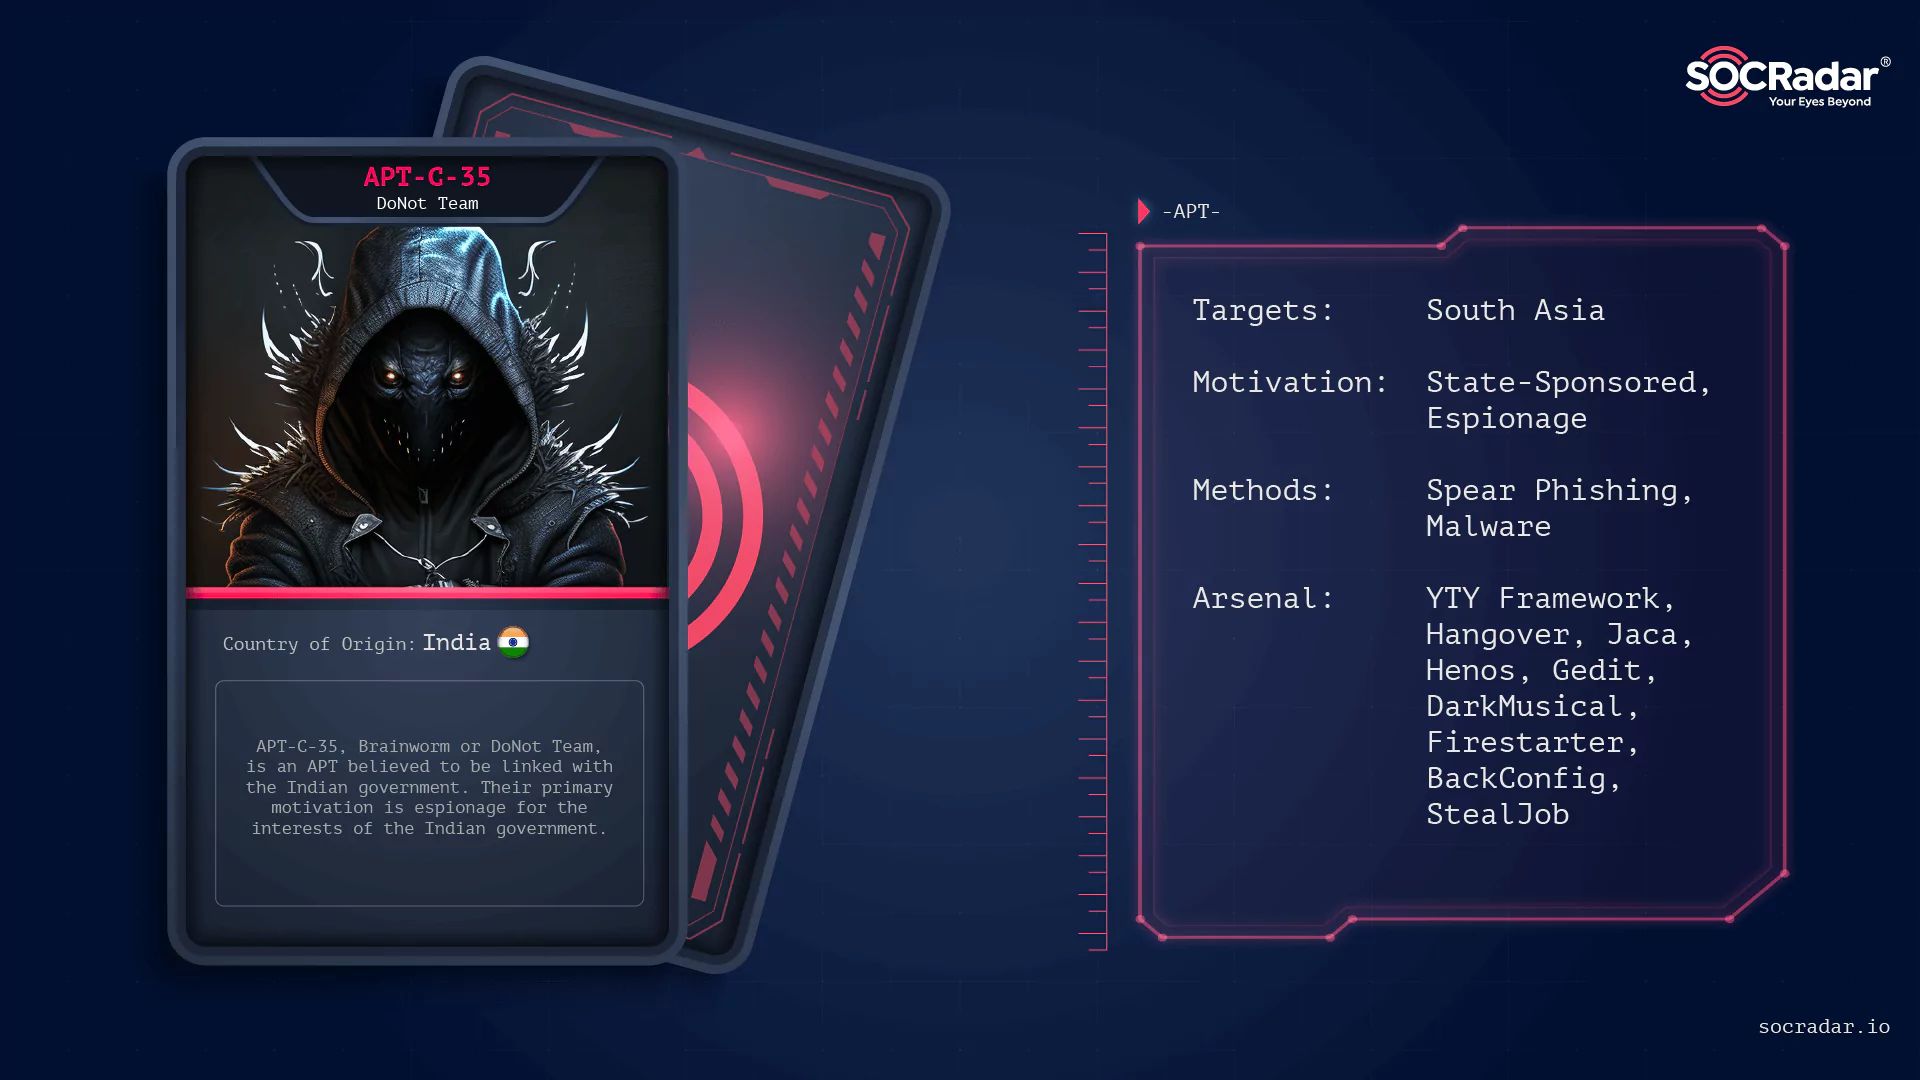
Dark Web Profile: APT-C-35 / DoNot Team
[Update] June 20, 2023: A new espionage campaign attributed to APT-C-35 (DoNot Team) targets users in Pakistan with trojanized apps on Google Play, added the subheading: “New APT-C-35 Campaign Targets…
 SOCRadar
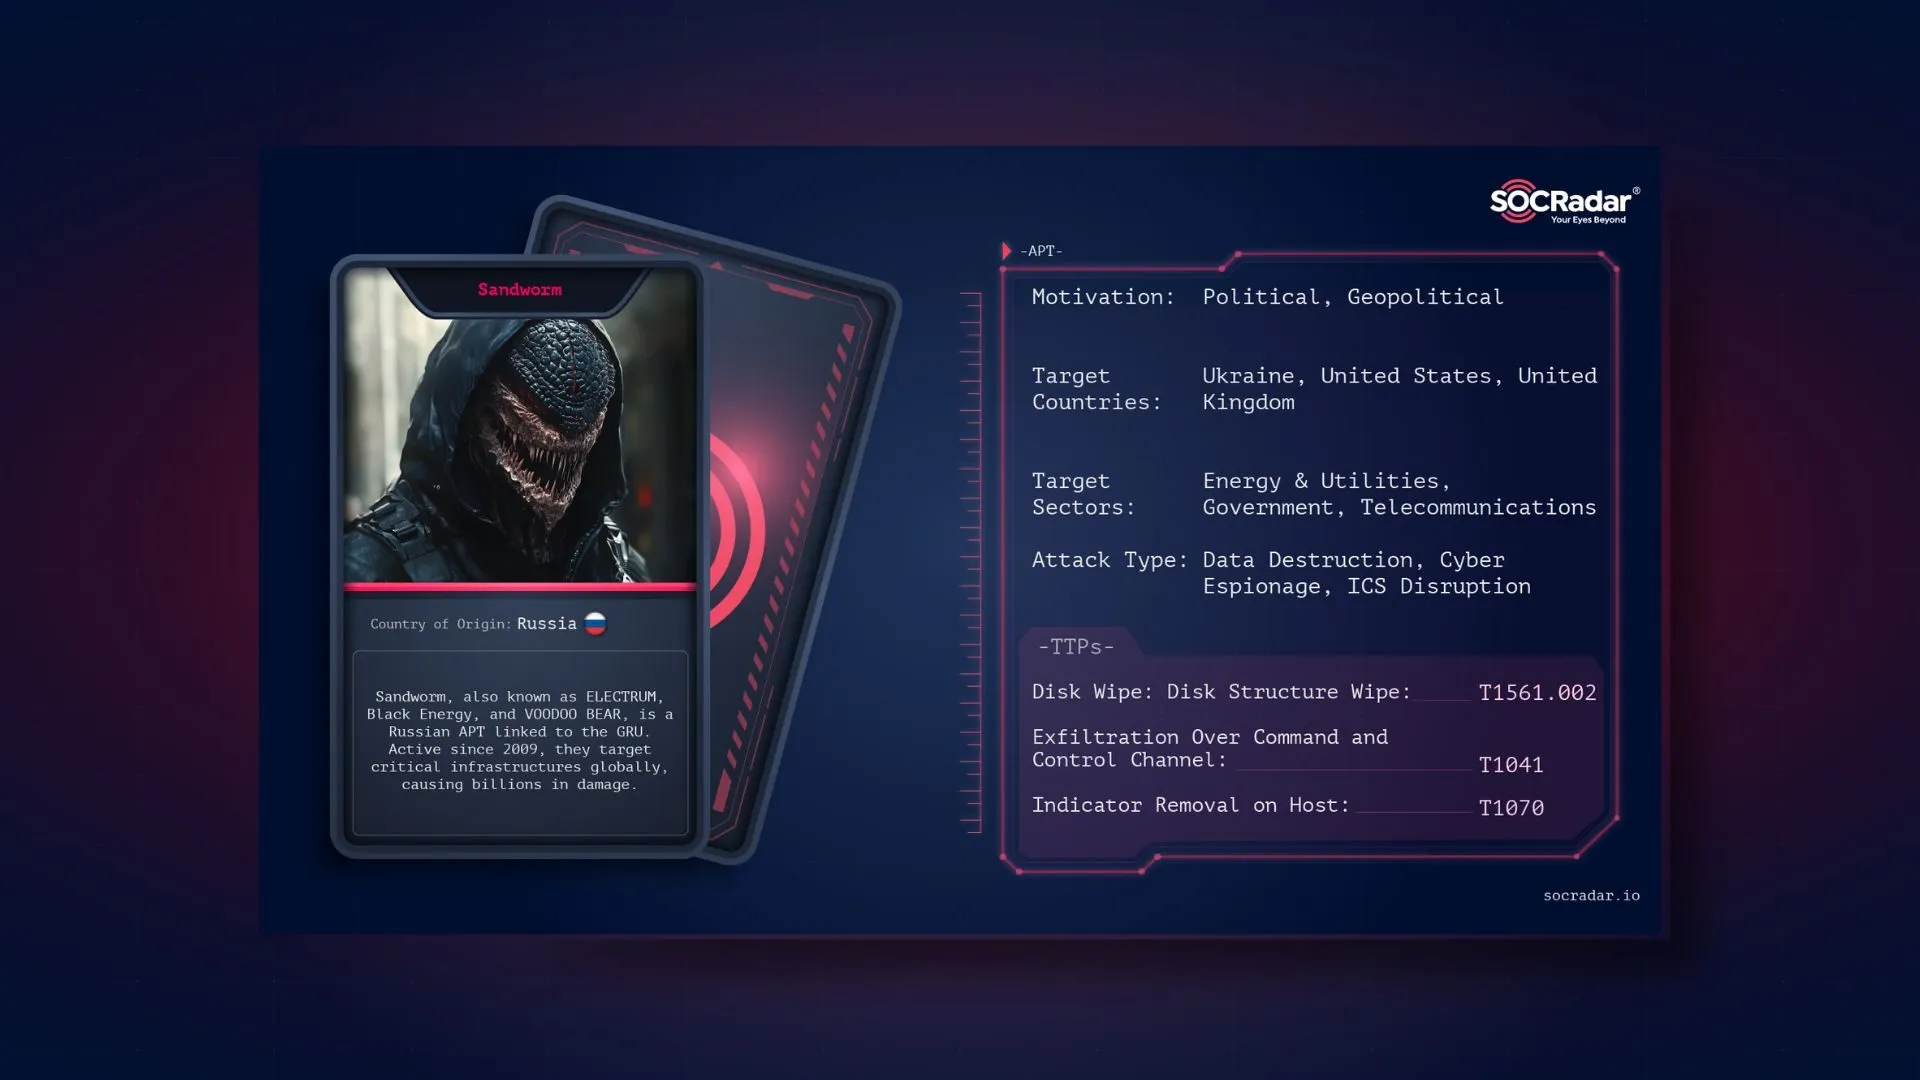
Dark Web Profile: Sandworm
Threat actors range from teenagers eager to earn quick cash to state-sponsored actors with agendas behind their operations. The agendas of these state-sponsored groups may include espionage activities on neighboring…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action