Latest articles
 SOCRadar
What Happened to XSS.is? Everything You Need to Know About the Forum Takedown
This week, authorities made a major move against the cybercrime underground. After years of investigation, the suspected admin of XSS.is, one of the most active Russian-speaking hacker forums, was arrested…
 SOCRadar
What Is the Deep Web?
The deep web refers to parts of the internet that search engines can’t index. It includes private databases, login-protected pages, and subscription-only content. While often misunderstood, the deep web is…
 SOCRadar
Cybercriminal Listings Target Fujitsu, Baxter Kelly, AGX Financeira, and a Belgian IT Platform
SOCRadar’s Dark Web Team has observed several new listings involving unauthorized access sales and data breaches affecting companies across Japan, the U.K., Brazil, and Belgium. One post allegedly offers Citrix access tied…
 SOCRadar
ToolShell Campaign: New SharePoint Zero-Day (CVE-2025-53770) Triggers Widespread Exploitation
[Update] October 5, 2026: Warlock Continues Using SharePoint Flaws to Deploy Ransomware [Update] October 23, 2025: Broader Exploitation of ToolShell Vulnerability by Chinese Threat Actors [Update] August 5, 2025: 4L4MD4R…
 SOCRadar
CVE‑2025‑37103: Remote Access Risk in Aruba Instant On Access Points Due to Hardcoded Passwords
HPE has disclosed a critical vulnerability in Aruba Instant On access points. The flaw involves a hardcoded admin password that allows remote access to the device’s web interface without authentication.…
 SOCRadar
CVE-2025-54309: New CrushFTP Zero-Day Exploited in the Wild
[Update] “Exploit Details and PoC for CVE-2025-54309 Released” A zero-day vulnerability in CrushFTP, tracked as CVE-2025-54309, is under active exploitation. The flaw allows attackers to gain administrator-level access through the…
 SOCRadar
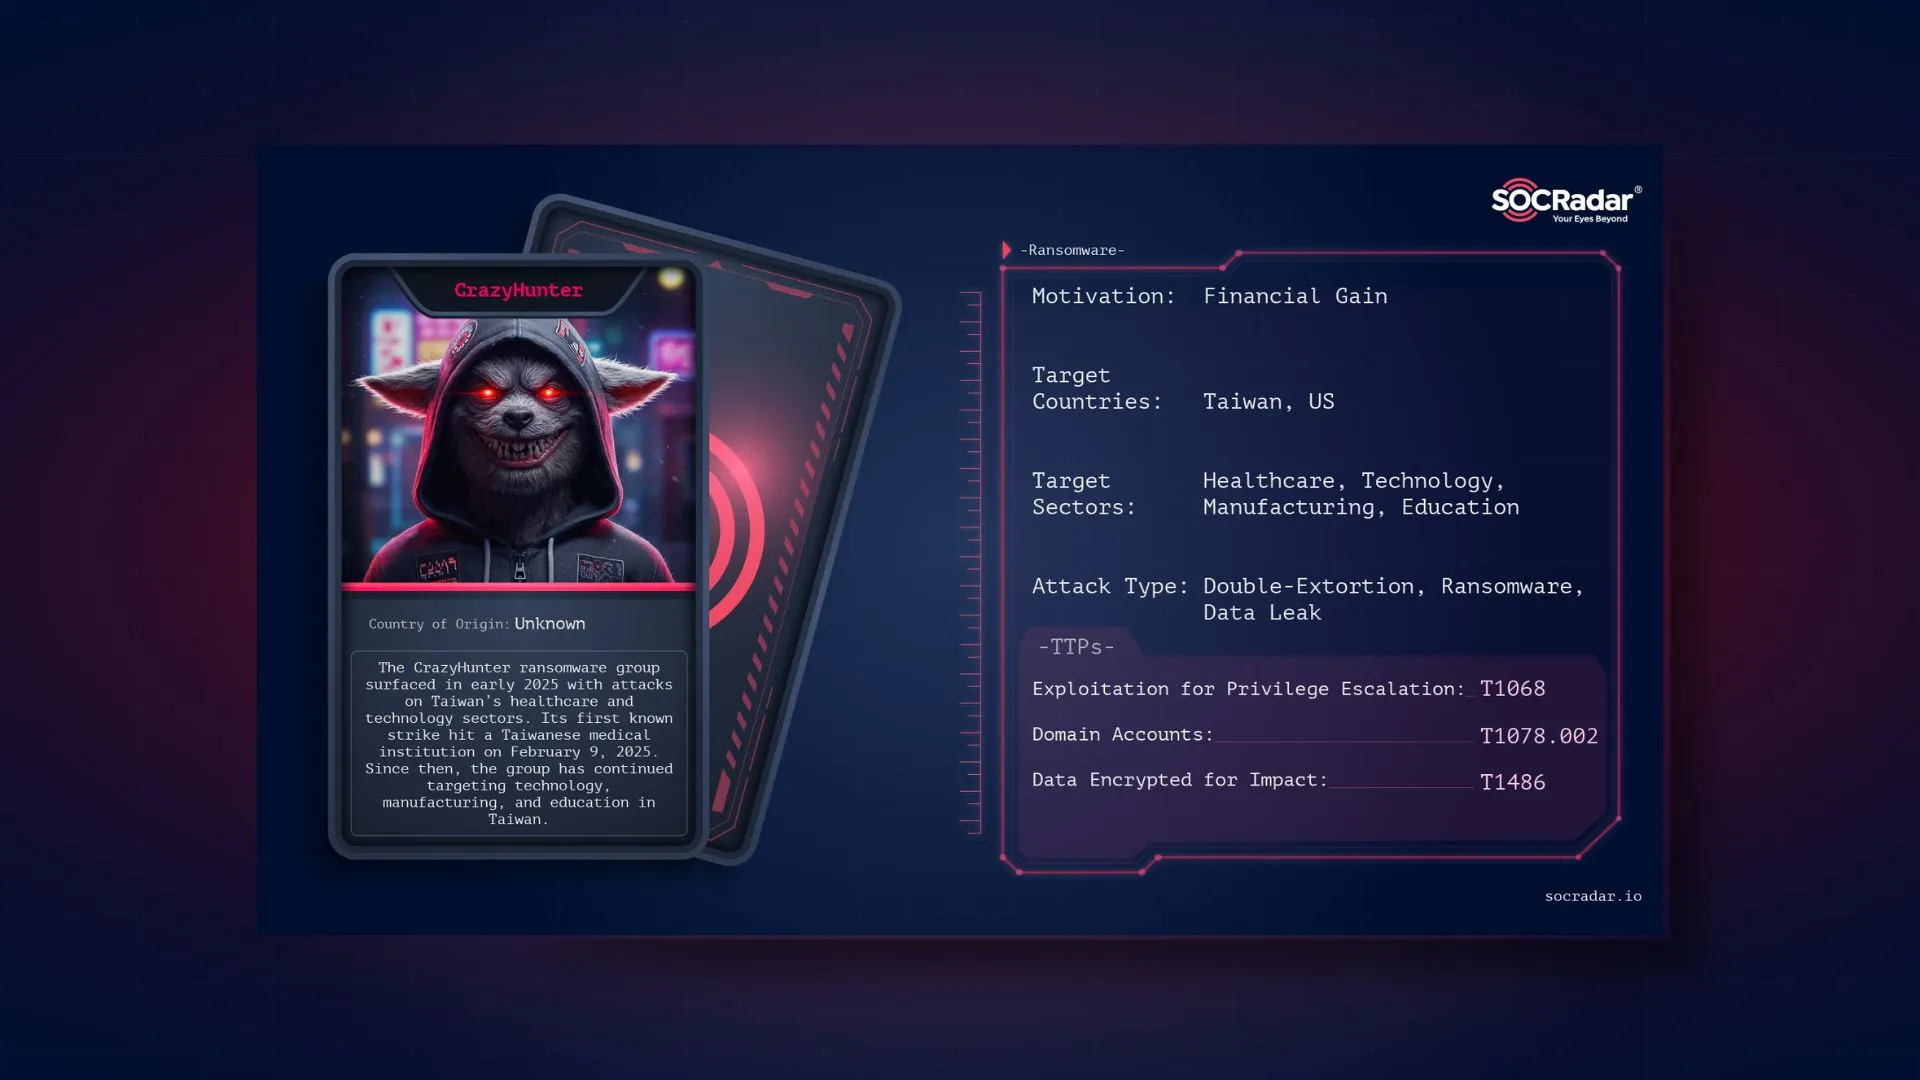
Dark Web Profile: CrazyHunter Ransomware
On February 9, 2025, Taiwan MacKay Memorial Hospital suffered a major ransomware attack. It hit the emergency and outpatient systems at both the Taipei and Tamsui campuses. More than 500…
 SOCRadar
CVE-2025-25257: Attackers Exploit FortiWeb SQL Injection Bug for Remote Code Execution
Cybersecurity researchers have sounded the alarm on an actively exploited vulnerability, tracked as CVE-2025-25257, affecting Fortinet’s FortiWeb appliances. FortiWeb acts as a Web Application Firewall (WAF), a critical line of…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action