Latest articles
 SOCRadar
Critical Vulnerabilities in Cisco URWB and HPE Aruba Access Points (CVE-2024-20418, CVE-2024-42509)
In recent security updates, Cisco has addressed a maximum severity vulnerability affecting Unified Industrial Wireless Software for Cisco URWB (Ultra-Reliable Wireless Backhaul) access points—network devices widely used in industrial environments…
 SOCRadar
 Joins the Cyber Threat Alliance: Advancing Cybersecurity Through Collaboration
Collaboration is crucial to preventing cyber threats in today’s rapidly evolving cybersecurity landscape. We’re thrilled that SOCRadar has joined the Cyber Threat Alliance (CTA) as an Affiliate Member. This partnership…
 SOCRadar
RISK:STATION (CVE-2024-10443) – Unpatched Synology Devices at Risk of RCE
Researchers have identified a zero-click vulnerability impacting Synology’s DiskStation and BeeStation devices, posing a significant risk to millions of users. Dubbed RISK:STATION and tracked as CVE-2024-10443, this flaw enables attackers…
 SOCRadar
November 2024 Android Security Update Fixes Actively Exploited Vulnerabilities CVE-2024-43093, CVE-2024-43047
[Updated] November 8, 2024: “CISA Adds Android Vulnerability CVE-2024-43093 to KEV Catalog” Google recently rolled out the November 2024 Android security update, resolving 40 security vulnerabilities. Among these, two zero-day…
 SOCRadar
Android RAT Tool, Asus Taiwan Access, and Palo Alto Exploit Detected on Dark Web
A wave of cyber threats has been uncovered in recent investigations by SOCRadar’s Dark Web Team, including a service offering bank accounts in German banks tailored for dropshipping across the…
 SOCRadar
LottieFiles Supply Chain Attack: Compromised npm Package Targets Cryptocurrency Wallets
LottieFiles recently disclosed a major supply chain attack affecting its open-source JavaScript library, lottie-player. This npm package, widely used by developers to embed animations on websites, was compromised, creating serious security…
 SOCRadar
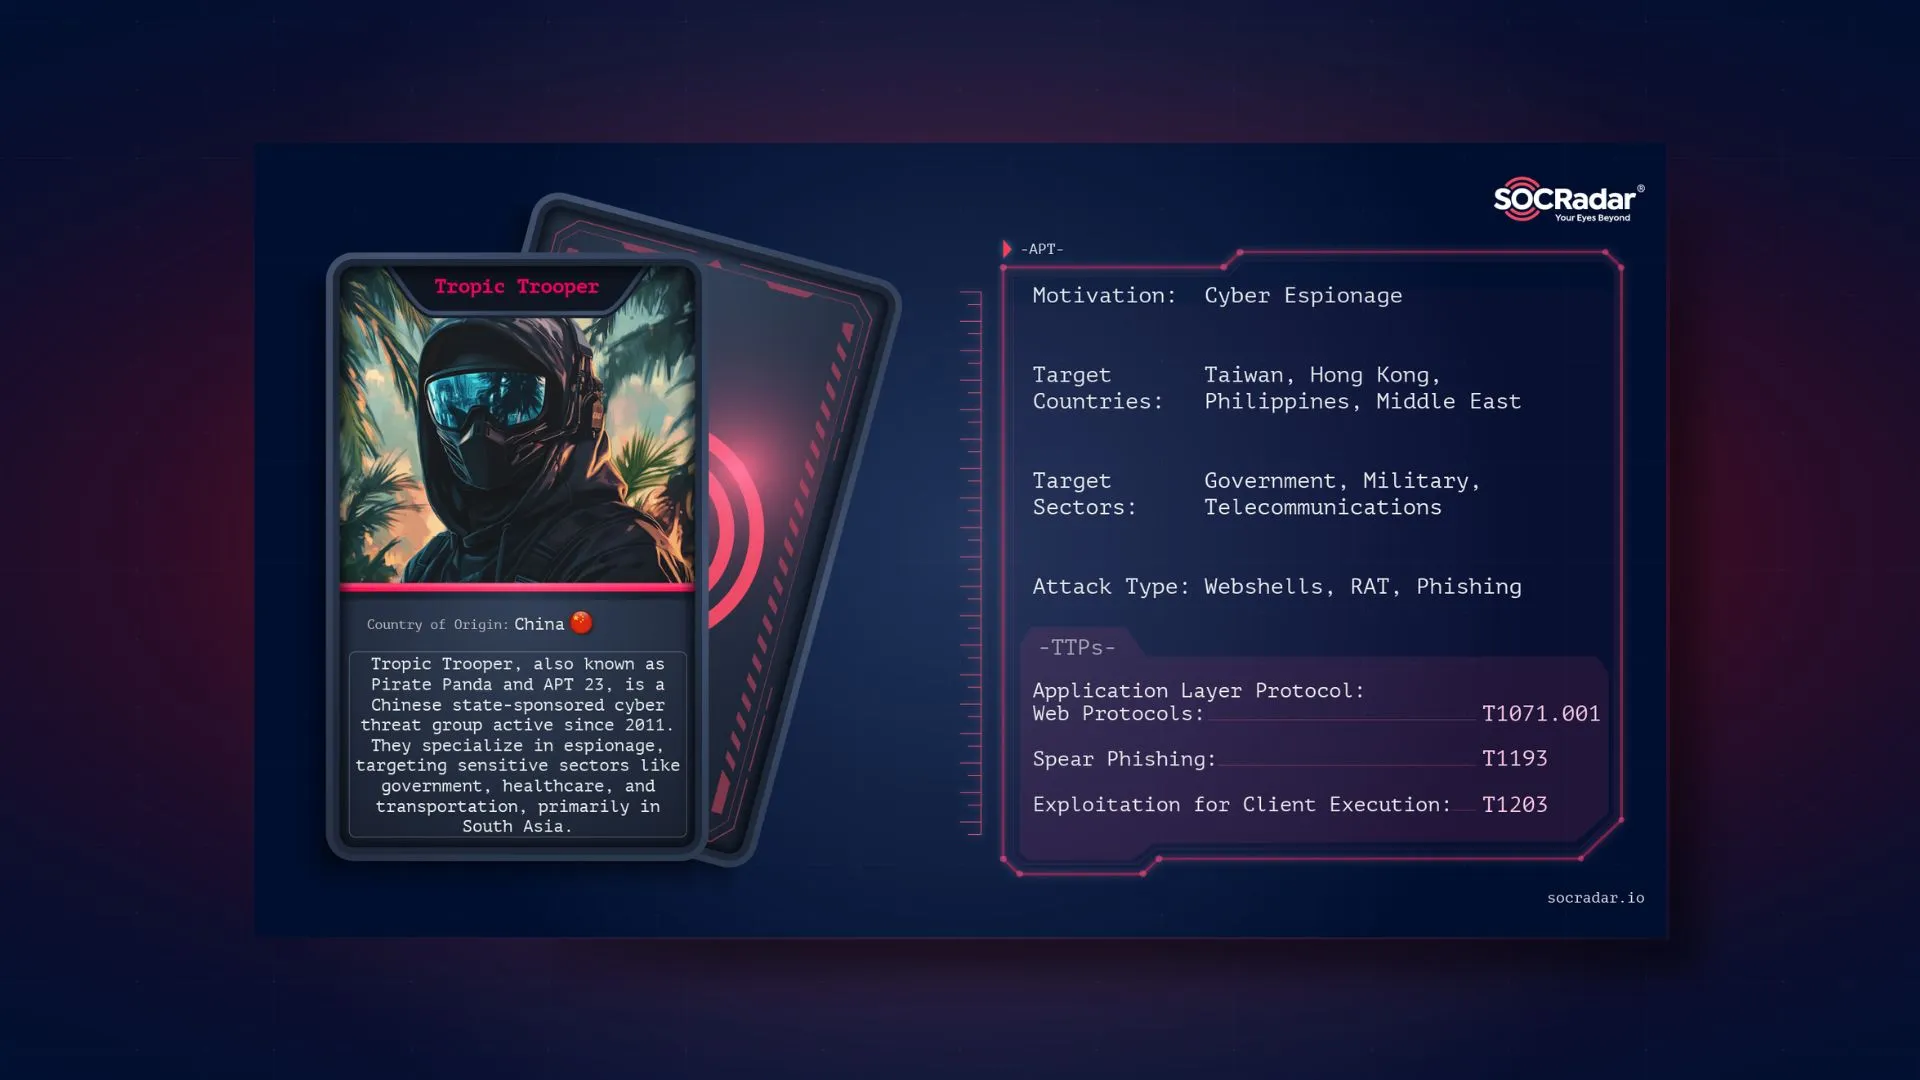
Dark Web Profile: Tropic Trooper (APT23)
Tropic Trooper, also known as Pirate Panda and APT 23, is a Chinese state-sponsored cyber threat group that has been active since 2011. Specializing in espionage, the group primarily targets…
 SOCRadar
ServiceNow Now Platform Vulnerabilities Enable RCE and SQL Injection Risks (CVE-2024-8923, CVE-2024-8924) – Patch Now
ServiceNow’s Now Platform, known for its AI-driven tools that help business processes and increase productivity, recently encountered two critical vulnerabilities. These newly disclosed flaws (CVE-2024-8923 and CVE-2024-8924) pose serious risks to…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action