Latest articles
 SOCRadar
CVE-2026-22709: vm2 Sandbox Escape Vulnerability
A recently disclosed critical vulnerability in the vm2 Node.js sandbox library, tracked as CVE-2026-22709, allows attackers to escape the sandbox and execute arbitrary code on the host system when applications…
 SOCRadar
CVE-2026-1470 & CVE-2026-0863: Severe Sandbox Escape Vulnerabilities Expose n8n Instances to RCE
Workflow automation platforms sit at the core of modern operations and handle sensitive data and system access. Recent n8n disclosures show how weak sandboxing can break these trust assumptions. Security…
 SOCRadar
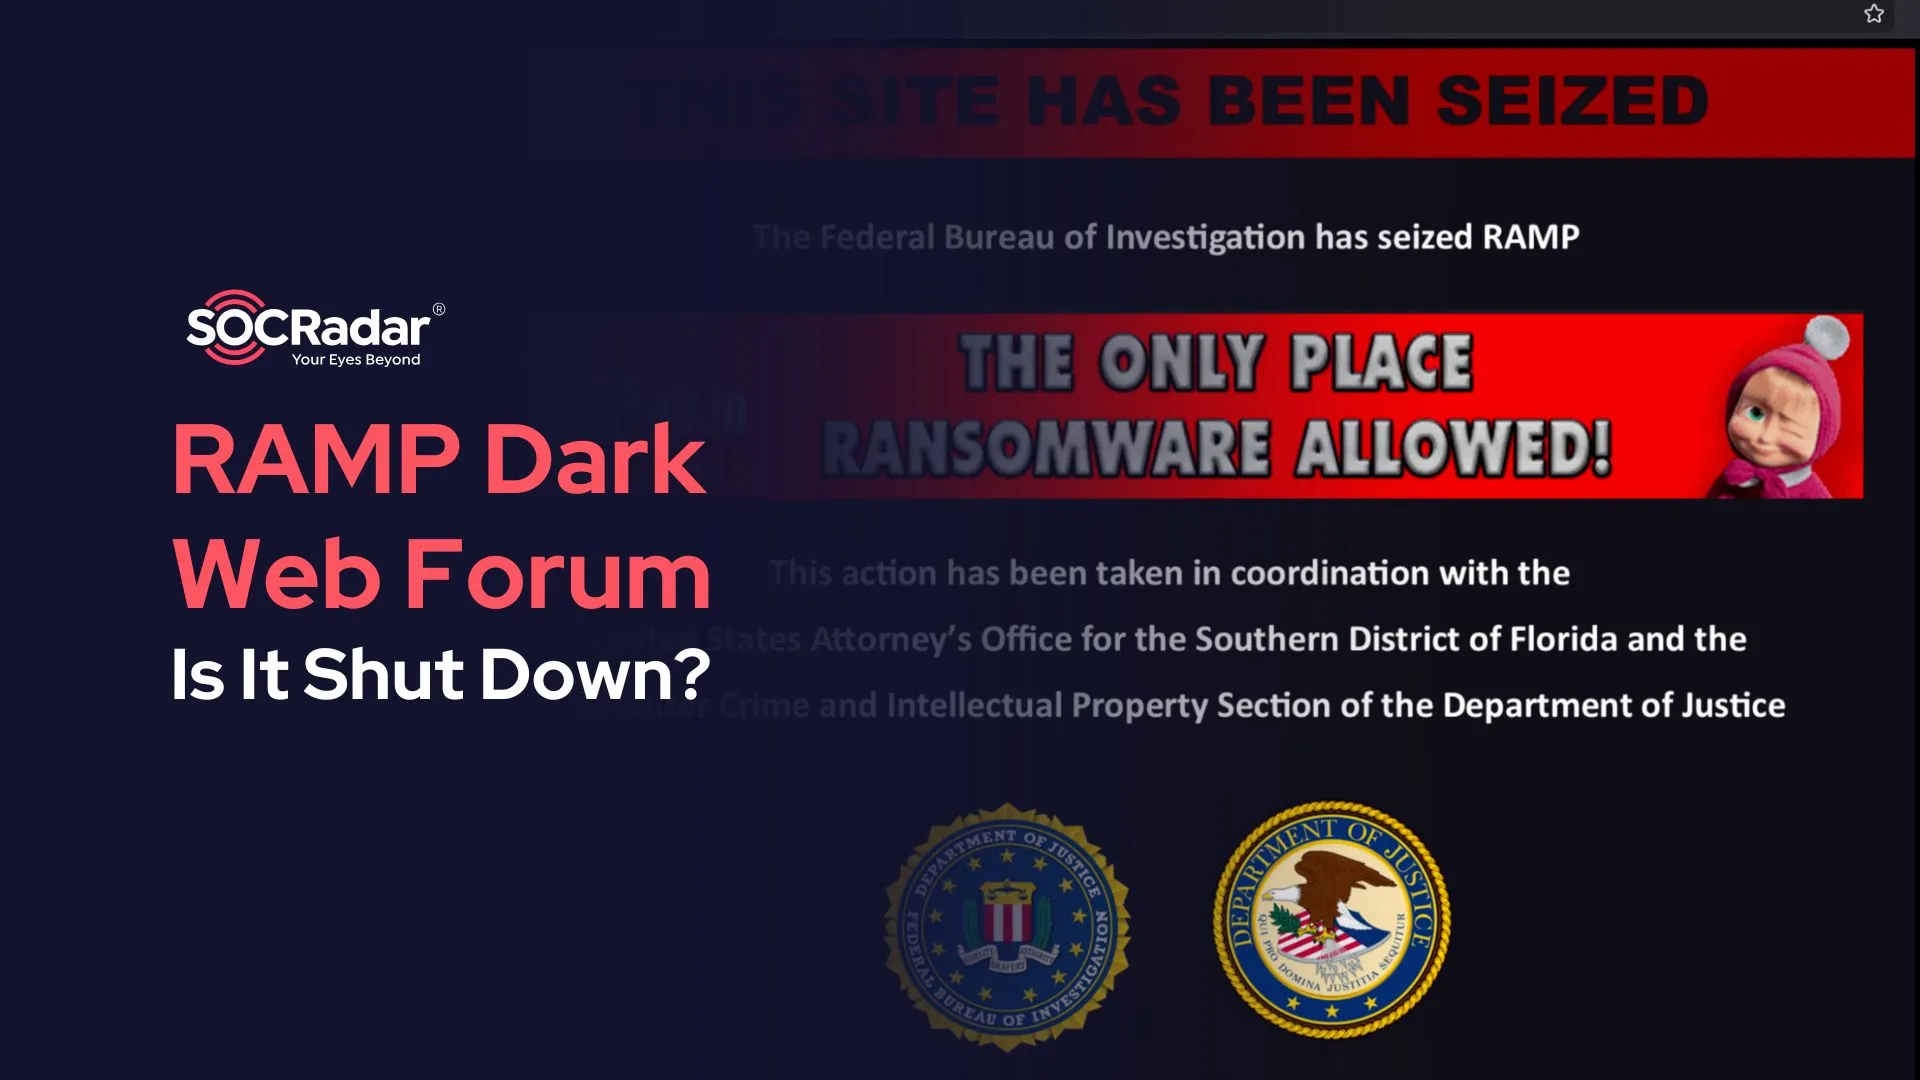
Is the RAMP Dark Web Forum Shut Down?
[Update] February 27, 2026: “RAMP Members Exposed Through Independent OSINT Research” RAMP (Russian Anonymous Marketplace) has been taken offline following a law enforcement seizure. The shutdown was publicly confirmed by…
 SOCRadar
CVE-2026-24858: Patch Released for Fortinet FortiOS SSO Authentication Bypass
A recent authentication bypass vulnerability affecting Fortinet products has drawn significant attention from security teams after confirmation of active exploitation in real-world environments. Tracked as CVE-2026-24858, the issue impacts FortiOS…
 SOCRadar
Stolen Credentials Aren’t the Real Problem – Turn Identity Alerts Into Real Defense
Credentials get reset. Multi-Factor Authentication (MFA) is enabled. The incident ticket is closed. Yet weeks later, the same account is abused again. For many security teams, this pattern is uncomfortably…
 SOCRadar
Top Impersonation Tactics Used in Social Engineering and Phishing
Impersonation attacks succeed by borrowing trust. Attackers pretend to be a familiar brand, a trusted vendor, a help desk agent, or an executive whose request feels urgent and non-negotiable. That…
 SOCRadar
Alleged Axtria & Salesfloor Data Leaks Surface on Dark Web
SOCRadar’s Dark Web Team identified several new underground posts this week, including alleged data leaks involving Axtria and Salesfloor, a claimed user database sale linked to investment platform Republic, and…
 SOCRadar
Czechia Under Coordinated DDoS Assault: Weekly DDoS Threat Intelligence Analysis
Analysis Period: January 19–25, 2026 Between 19 and 25 January 2026, SOCRadar identified an intensive coordinated DDoS campaign conducted by the pro-Russian threat actor NoName057(16) and their DDoSia attack tool.…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action