ZoomInfo Sale, TryCircle, Vicente López, HDB, and X Leaks

Ameer OwdaameerowdaEdit Profile
SOCRadar Dark Web Team identified several underground posts, including an alleged ZoomInfo database sale involving 185 million records, an alleged TryCircle customer data leak, and an alleged Vicente López municipal database exposure. Other posts advertised a previously compromised HDB Financial Services dataset and an unverified X (Twitter) user database leak claim.
Alleged ZoomInfo Database Sale is Detected
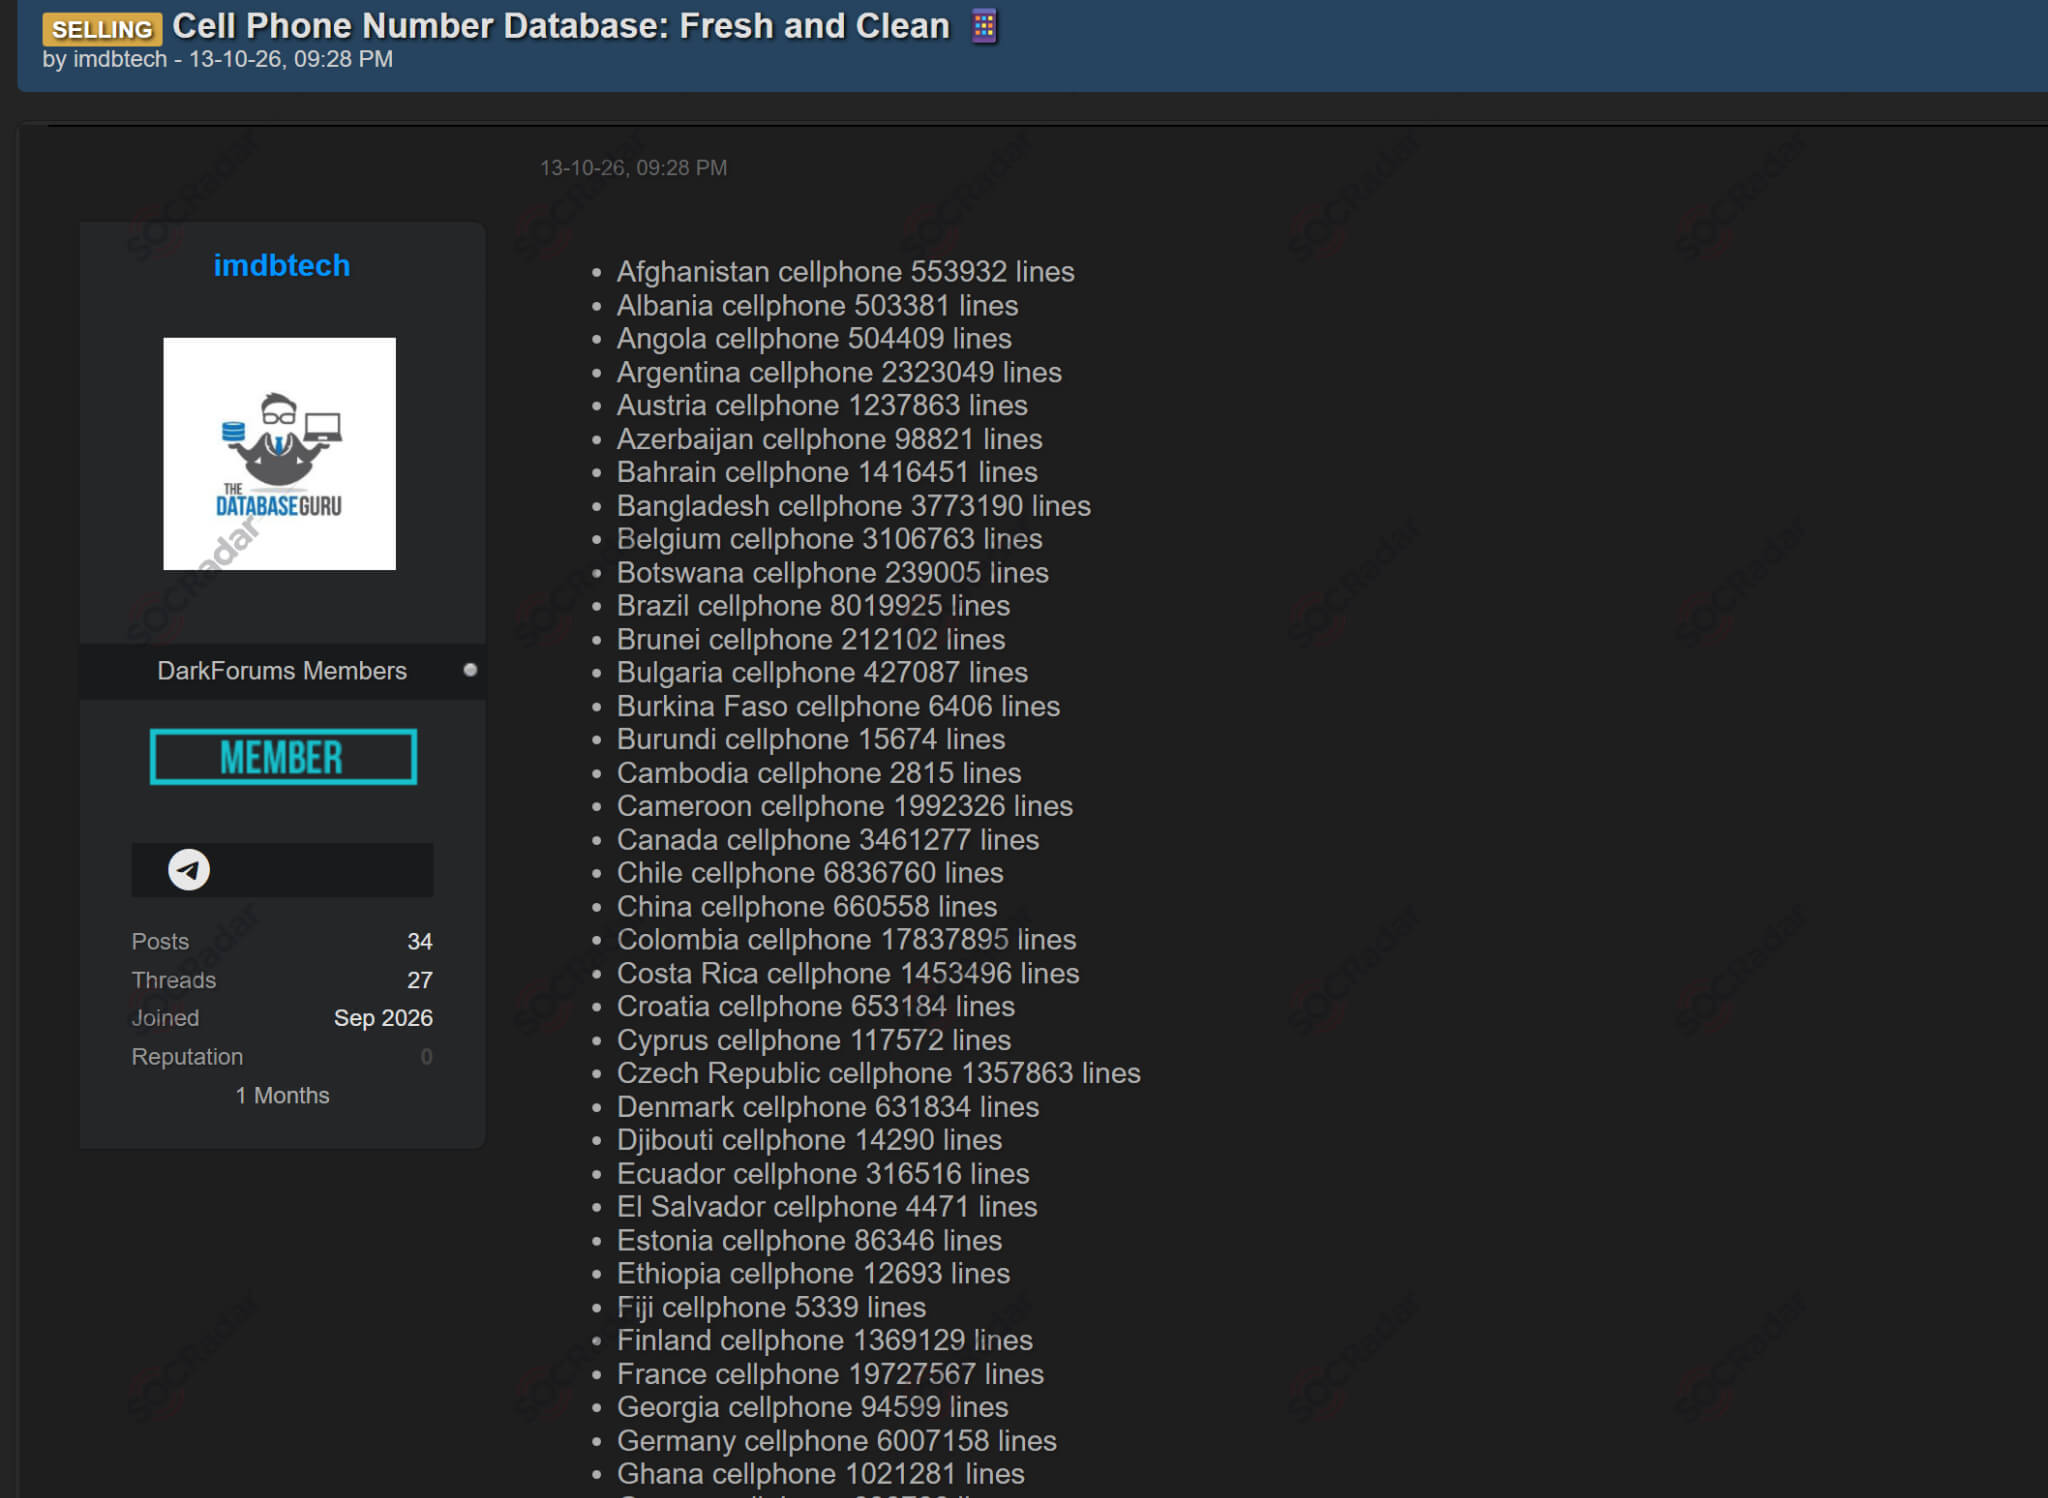
SOCRadar Dark Web Team identified a post on the XSS forum advertising an alleged 185 million-record database associated with ZoomInfo, a business intelligence and contact data platform. The seller claimed to possess an extensive collection of professional contact details and corporate information, providing sample records to support the listing. However, the dataset’s authenticity and whether it originated from scraping or unauthorized access remain unverified.
The advertised data reportedly includes full names, business and personal email addresses, mobile phone numbers, job titles, seniority levels, departments, and LinkedIn profiles, alongside company names, domains, industry classifications, revenue ranges, and employee counts. The sample also contained business email validation fields, suggesting the information may have been collected or processed for lead generation. If authentic, the dataset could facilitate targeted phishing, Business Email Compromise (BEC), and corporate impersonation campaigns.
Alleged TryCircle Customer Database Leak is Detected
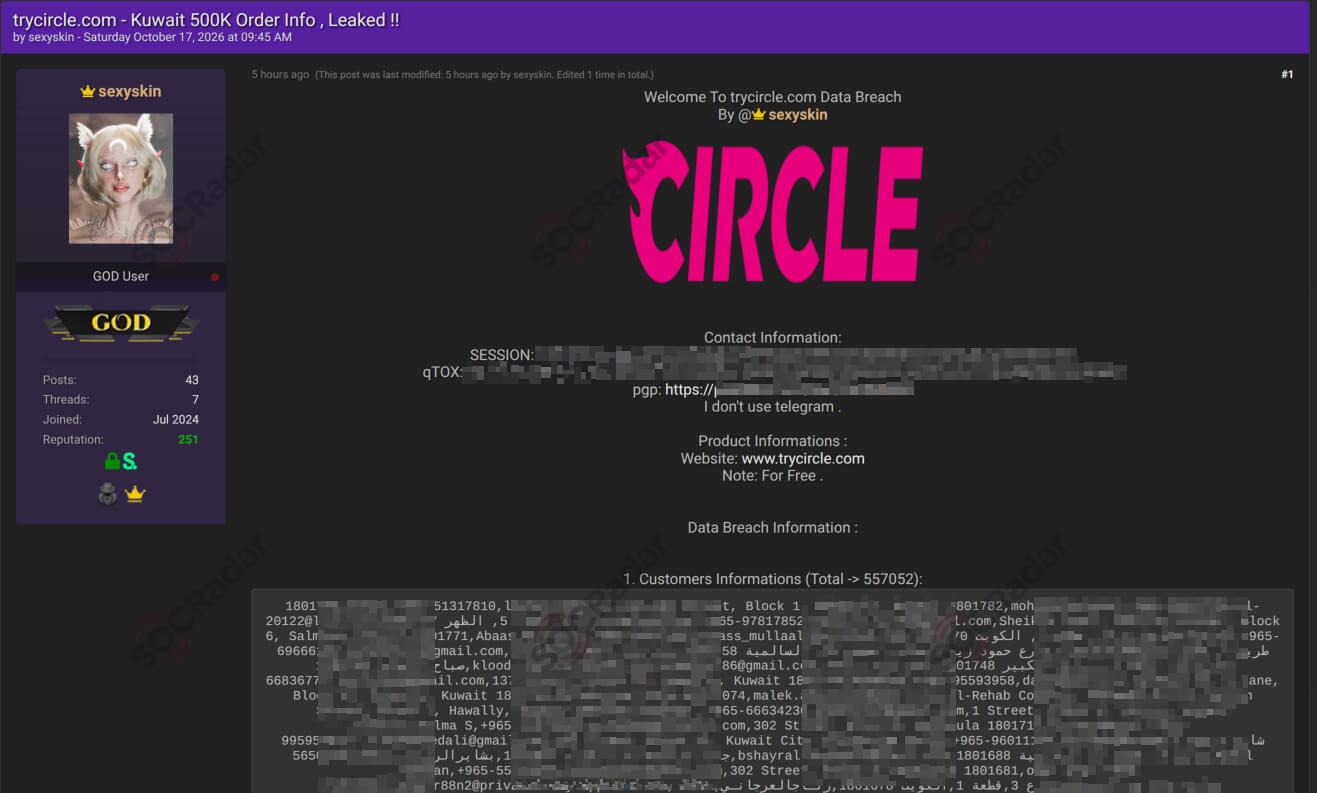
SOCRadar Dark Web Team detected a post claiming a breach of TryCircle, an e-commerce platform operating in Kuwait. The threat actor, identified as sexyskin, claimed to have leaked a database containing 557,052 customer records and made the information available on an underground forum.
The exposed records reportedly include full names, mobile phone numbers, email addresses, and detailed physical delivery addresses. The availability of this information could increase the risk of targeted phishing, smishing, identity fraud, and social engineering against customers in Kuwait. The alleged breach has not been independently confirmed.
Alleged Vicente López Municipal Database Leak is Detected
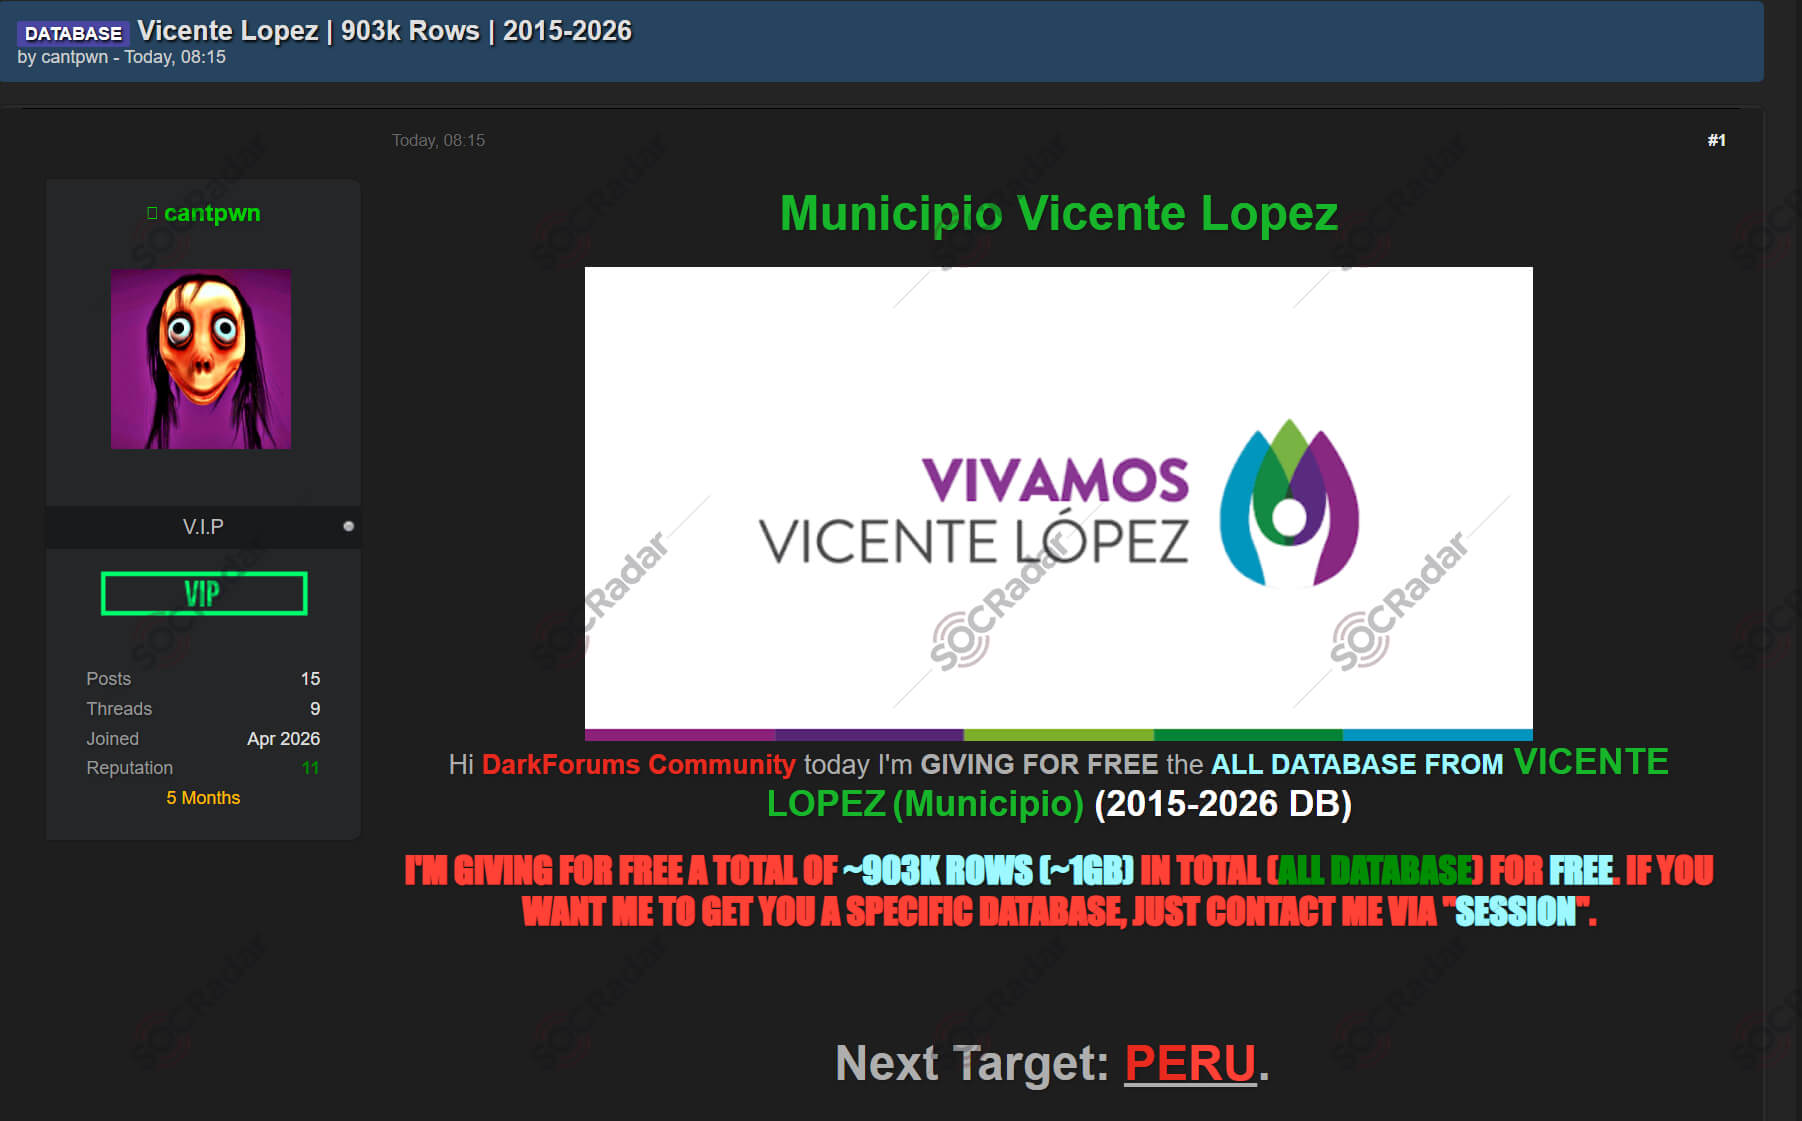
SOCRadar Dark Web Team detected a post claiming to release a database allegedly belonging to Municipalidad de Vicente López, a municipality in Argentina’s Buenos Aires Province. The actor, operating under the alias cantpwn, claimed to have published approximately 903,000 records, covering information collected between 2015 and 2026.
The reportedly exposed dataset, estimated at approximately 1GB, includes names, dates of birth, nationality, marital status, identification numbers, email addresses, phone numbers, and administrative registration details. The actor offered the database for free and indicated that systems in Peru could be targeted next. If genuine, the exposure could facilitate identity theft, fraud, and targeted social engineering against residents.
Alleged HDB Financial Services Data Leak Resurfaces
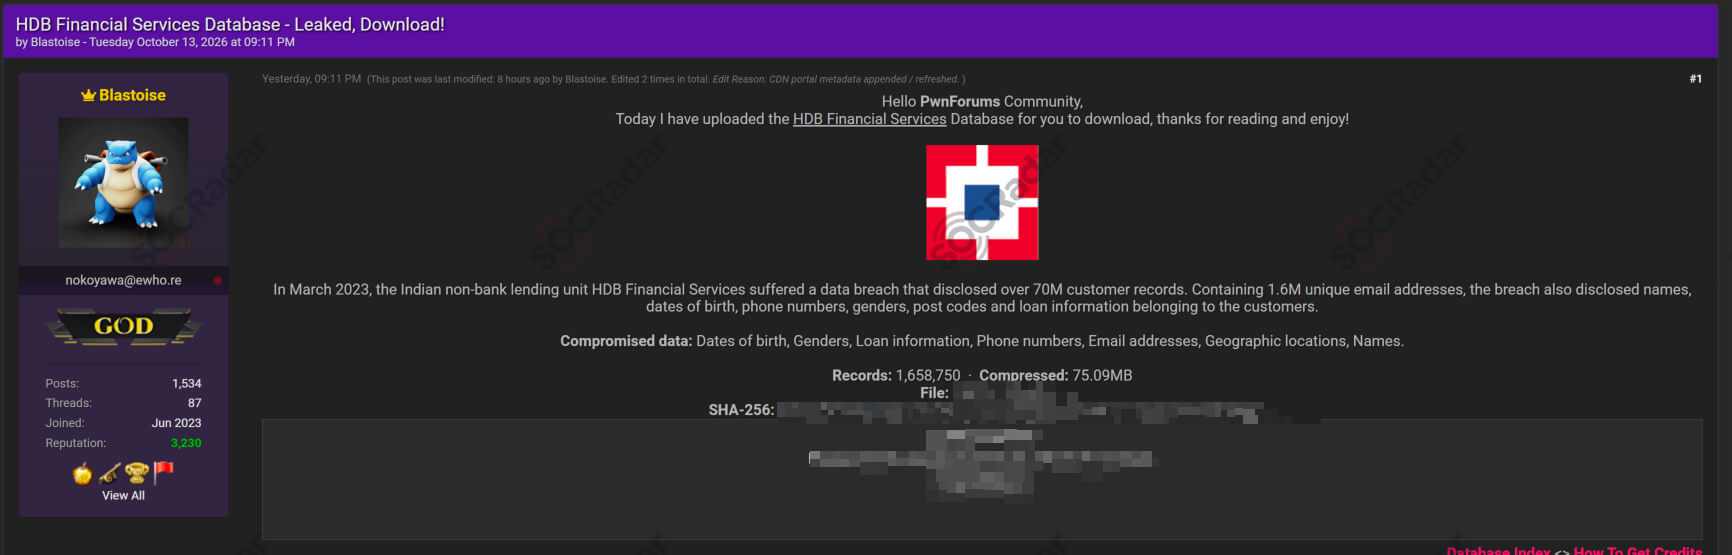
SOCRadar Dark Web Team detected a post distributing customer information allegedly belonging to HDB Financial Services, an Indian non-bank financial institution. The actor, identified as Blastoise, shared an archive containing approximately 1.66 million records, reportedly associated with a breach dating back to March 2023.
The dataset reportedly includes customer names, dates of birth, genders, phone numbers, email addresses, geographic information, and loan-related details. The archive was listed at approximately 75MB compressed, with a SHA-256 hash provided alongside the download. Although the data appears to relate to a historical incident rather than a new compromise, its renewed circulation could support financial fraud, phishing, and identity theft.
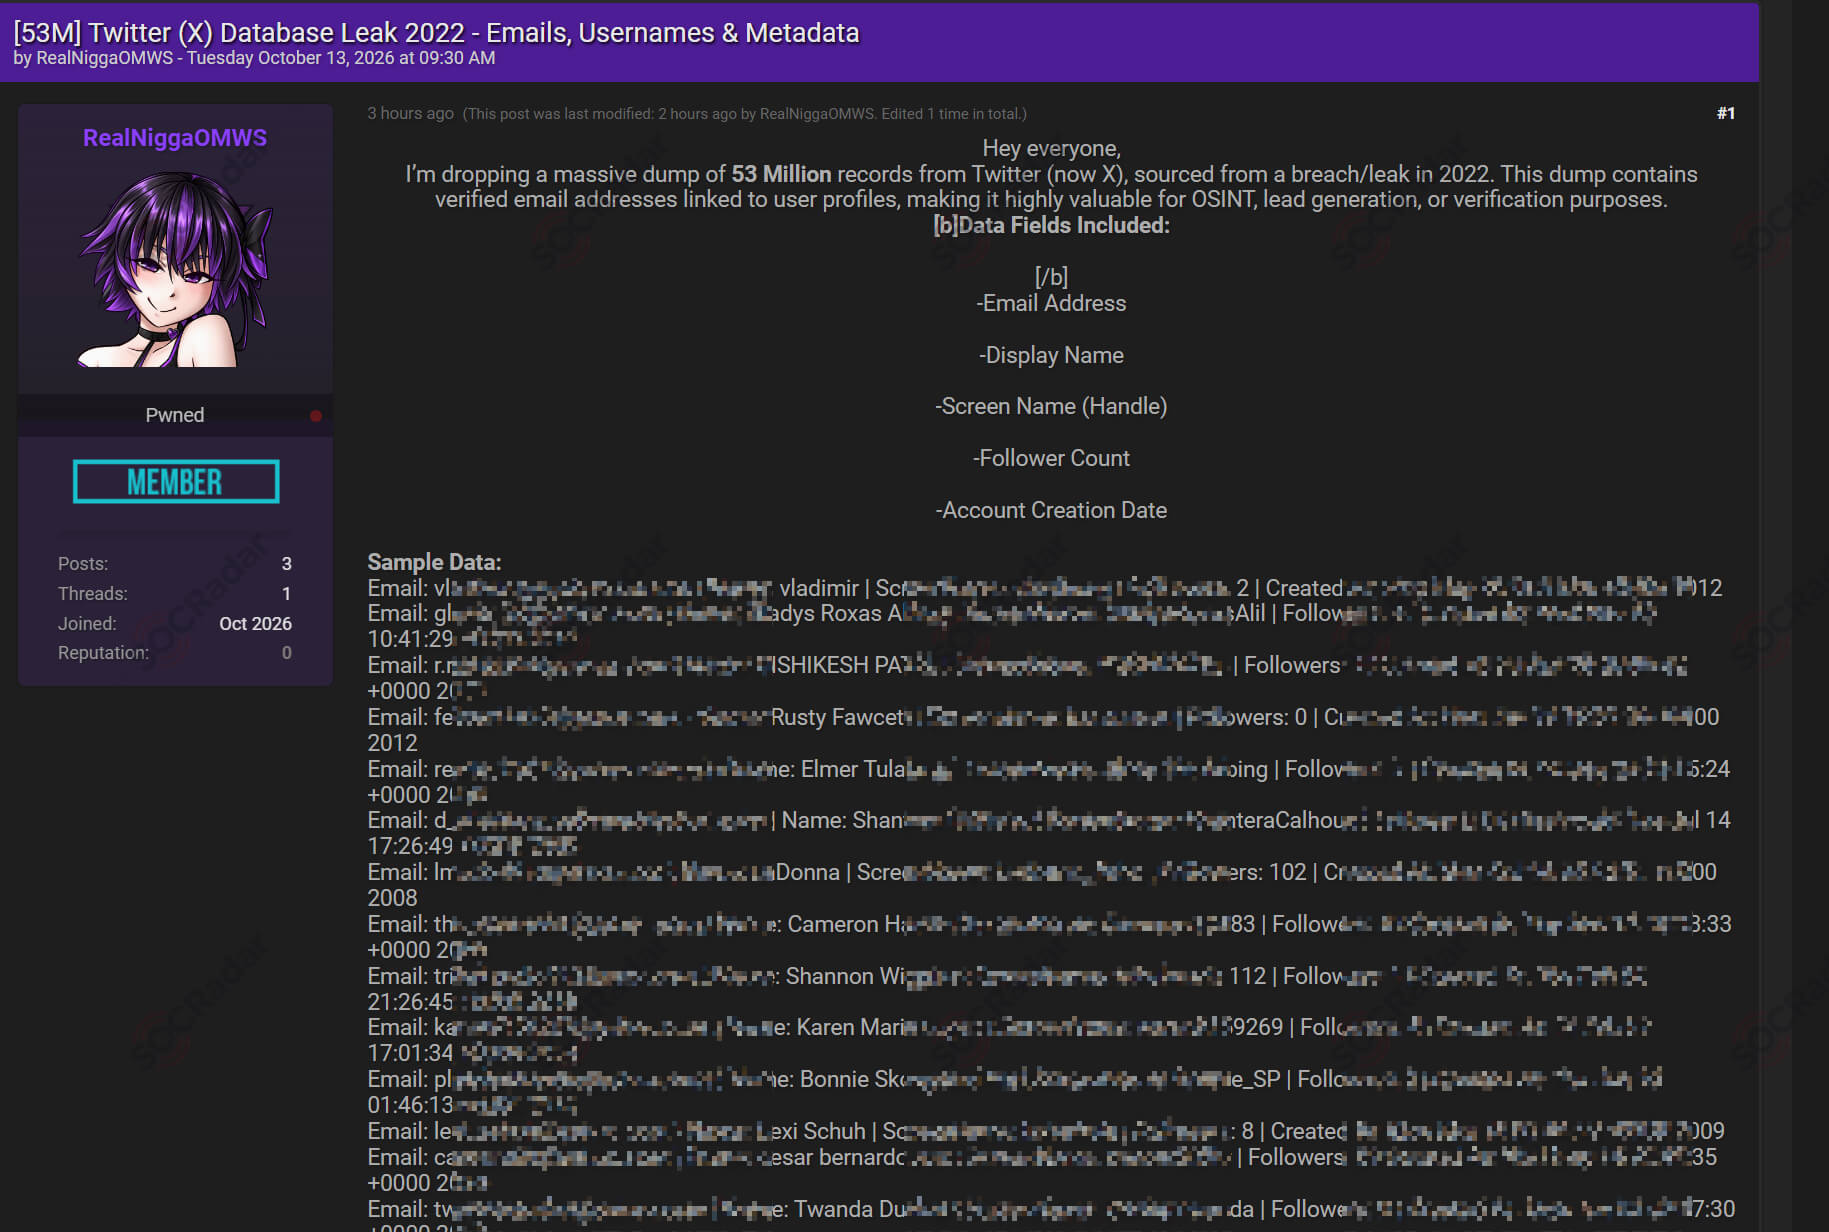
SOCRadar Dark Web Team detected a post advertising an alleged 53 million-record dataset associated with X (formerly Twitter). The seller claimed the information originated from a 2022 leak and included email addresses linked to user profiles, display names, usernames, follower counts, and account creation dates.
A separate underground report described another actor claiming to possess 200 million email and password combinations allegedly associated with X. Unlike the 53 million-record listing, this second claim reportedly provided no sample data for verification. The two claims should be treated as distinct and unverified. If authentic, the exposure could facilitate phishing, user profiling, credential stuffing, and account takeover attempts.
Powered by DarkMirror™
Gaining visibility into deep and dark web threats can be extremely useful from an actionable threat intelligence and digital risk protection perspective. However, monitoring all sources is simply not feasible, which can be time-consuming and challenging. One click-by-mistake can result in malware bot infection. To tackle these challenges, SOCRadar’s DarkMirror™ screen empowers your SOC team to follow up with the latest posts of threat actors and groups filtered by the targeted country or industry.