Latest articles
 SOCRadar
Epstein Files Guide: How to Reliably Search the Epstein Files?
This guide is for informational purposes only. The release of Jeffrey Epstein’s investigative files has been one of the most significant transparency efforts in recent years. However, navigating these millions…
 SOCRadar
CVE-2026-25253: 1-Click RCE in OpenClaw Through Auth Token Exfiltration
CVE-2026-25253 is a critical security vulnerability classified as an Incorrect Resource Transfer Between Spheres (CWE-669) with a high severity score (CVSS 8.8). It affects OpenClaw (formerly known as Clawdbot and…
 SOCRadar
SolarWinds Web Help Desk Update Addresses High-Risk RCE & Auth Bypass Bugs
SolarWinds has released an urgent security update for its Web Help Desk (WHD) platform after disclosing multiple vulnerabilities, several of which carry critical severity ratings. SolarWinds Web Help Desk is…
 SOCRadar
CVE-2026-1281 & CVE-2026-1340: Ivanti EPMM Zero-Day Vulnerabilities Enable Unauthenticated RCE
Ivanti has released emergency security updates after disclosing two critical vulnerabilities (CVE-2026-1281 and CVE-2026-1340) in Ivanti Endpoint Manager Mobile (EPMM) that have been actively exploited as zero-day attacks. Both flaws…
 SOCRadar
CVE-2026-22709: vm2 Sandbox Escape Vulnerability
A recently disclosed critical vulnerability in the vm2 Node.js sandbox library, tracked as CVE-2026-22709, allows attackers to escape the sandbox and execute arbitrary code on the host system when applications…
 SOCRadar
CVE-2026-1470 & CVE-2026-0863: Severe Sandbox Escape Vulnerabilities Expose n8n Instances to RCE
Workflow automation platforms sit at the core of modern operations and handle sensitive data and system access. Recent n8n disclosures show how weak sandboxing can break these trust assumptions. Security…
 SOCRadar
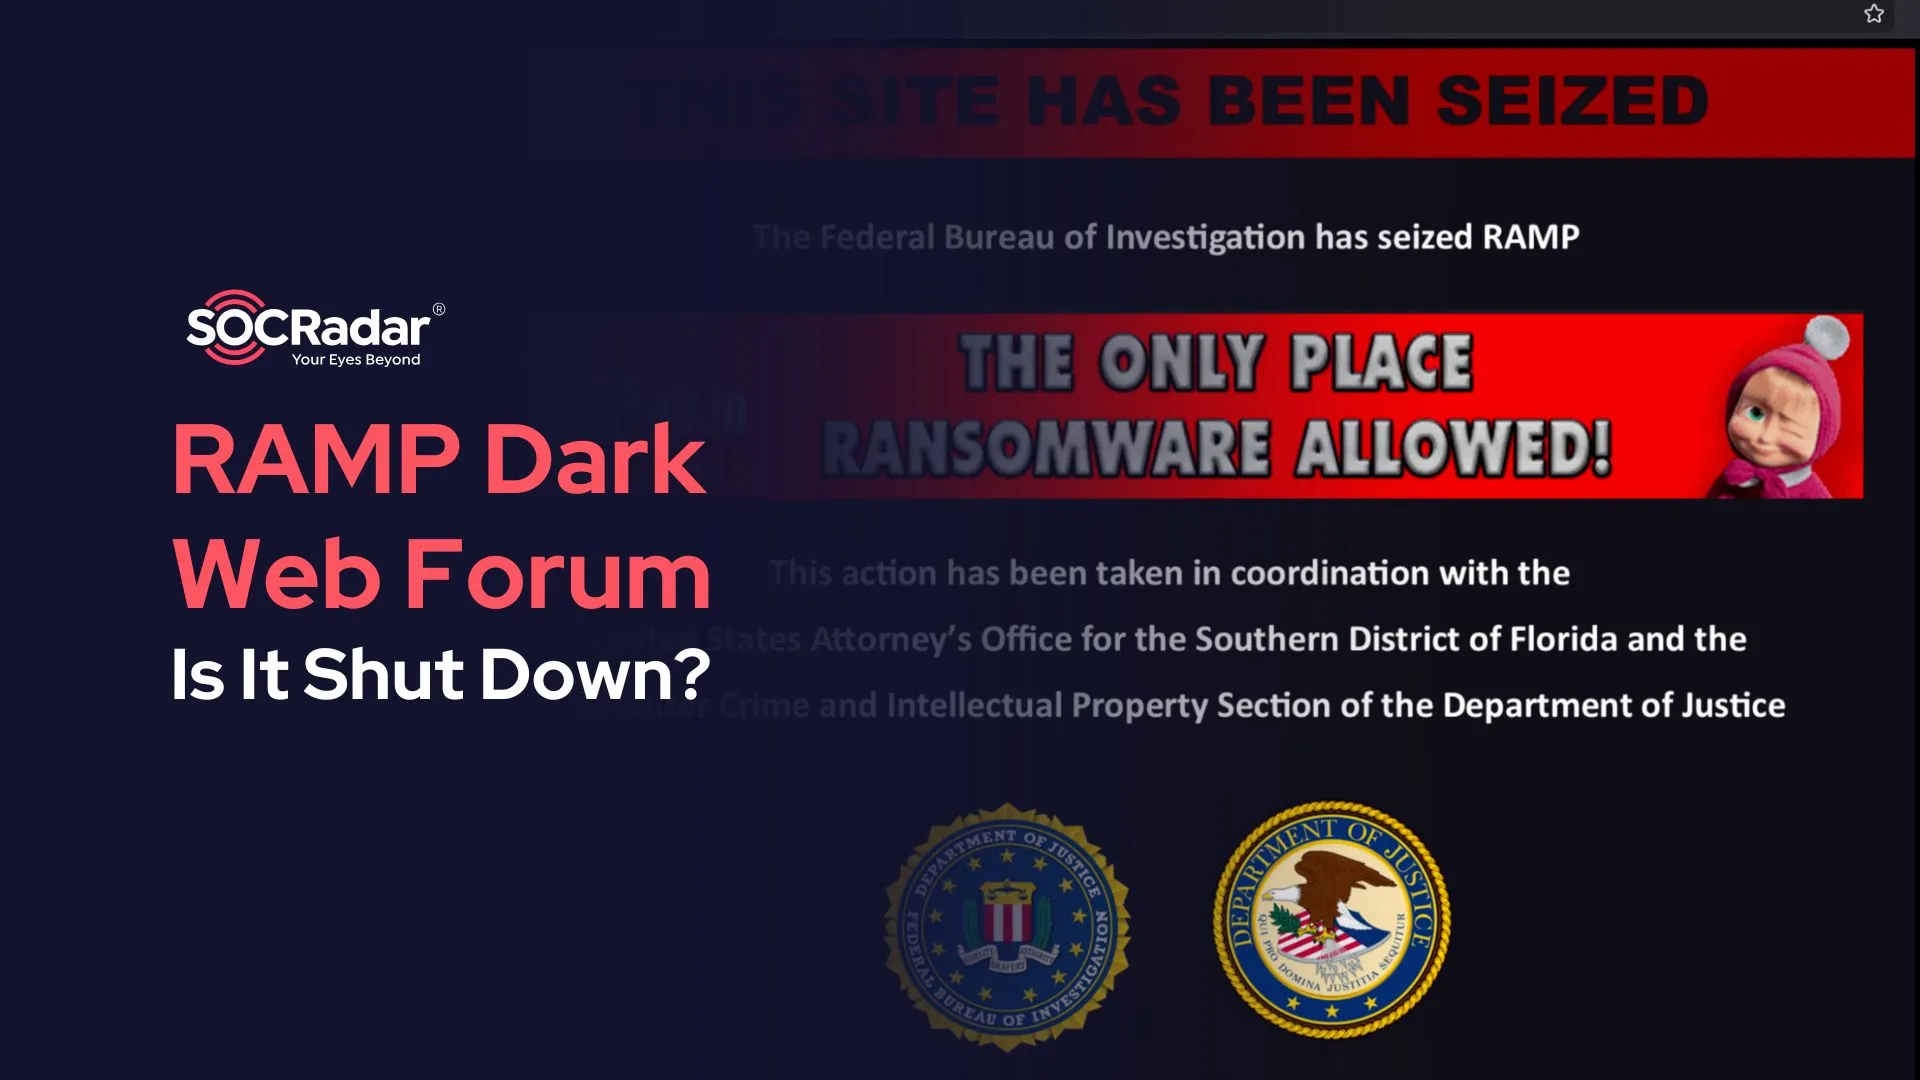
Is the RAMP Dark Web Forum Shut Down?
[Update] February 27, 2026: “RAMP Members Exposed Through Independent OSINT Research” RAMP (Russian Anonymous Marketplace) has been taken offline following a law enforcement seizure. The shutdown was publicly confirmed by…
 SOCRadar
CVE-2026-24858: Patch Released for Fortinet FortiOS SSO Authentication Bypass
A recent authentication bypass vulnerability affecting Fortinet products has drawn significant attention from security teams after confirmation of active exploitation in real-world environments. Tracked as CVE-2026-24858, the issue impacts FortiOS…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action