Latest articles
 SOCRadar
Top 10 Cybercrime Law Enforcement Operations of 2025
This report highlights a set of major law enforcement operations from 2025 that we selected for their substantial CTI value. Like last year’s review of global takedowns and enforcement actions…
 SOCRadar
Weapon Bot Toolkit, MadLicense Exploit Demand, and 413K Credit Cards Observed
SOCRadar’s Dark Web Team identified multiple underground posts this week, including a major auction for global credit card records, a buyer seeking a weaponized PoC for the Windows MadLicense vulnerability…
 SOCRadar
Riyadh Airports Access Claim, Golden Goose Trojan, and NEWSAN Leak Surface Online
SOCRadar’s Dark Web Team identified several notable underground posts this week, including alleged unauthorized access to Riyadh Airports’ operational systems, a new malware loader called the Golden Goose Trojan, and…
 SOCRadar
Dark Web Market: B1ack’s Stash
On the dark web, every new carding market tries to gain instant credibility. Nothing does that faster than free leaked credit cards. B1ack’s Stash entered the deep web carding scene…
 SOCRadar
Inside Morte Loader: How Loader as a Service Builds Modern Botnets
Morte is a Loader as a Service (LaaS) that turns vulnerable SOHO routers, IoT devices and web applications into a flexible botnet platform. It does not focus on one payload…
 SOCRadar
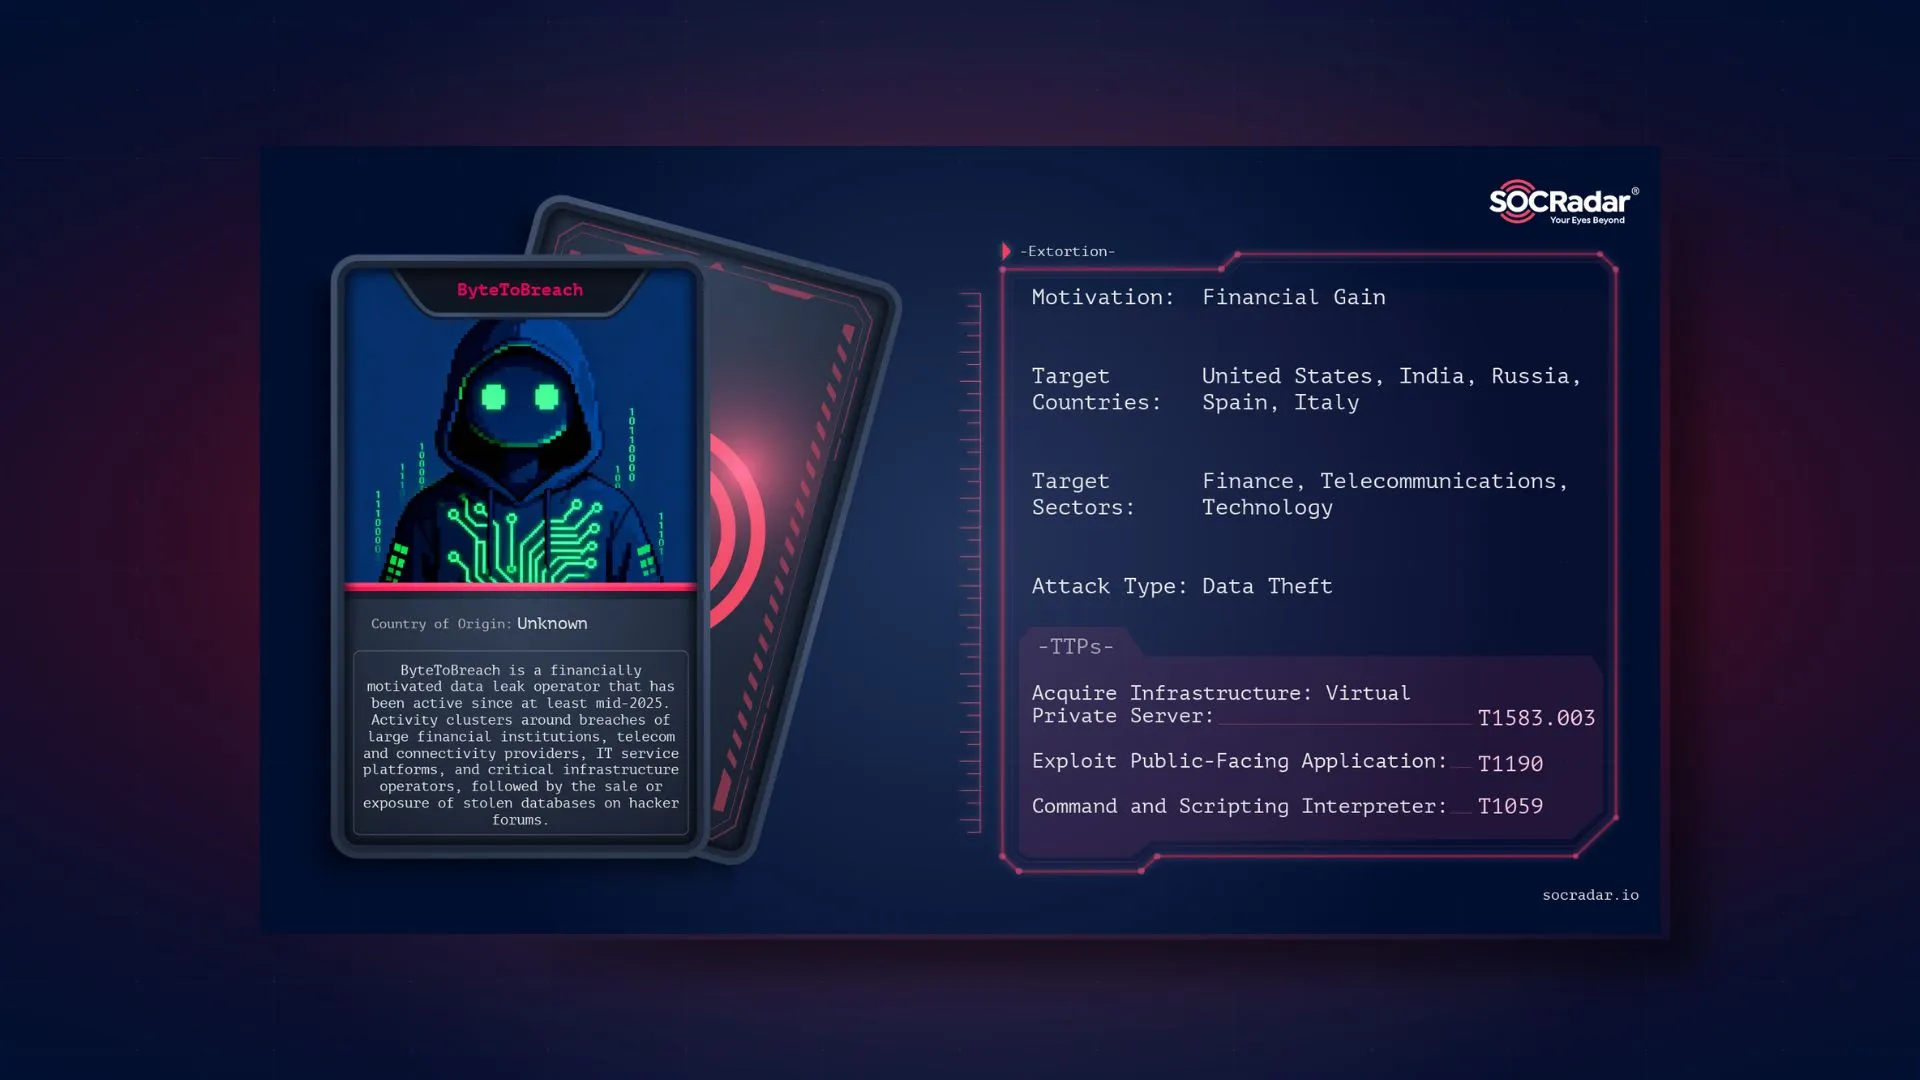
Dark Web Profile: ByteToBreach
By mid-2025, the alias ByteToBreach was already an active seller on a major cybercrime forum, offering access and databases from banks, telecom, airlines, and other large enterprises. On November 14,…
 SOCRadar
Alleged SeAH, Under Armour, SecureTeen, and Cloudeka Data Exposures Detected
SOCRadar’s Dark Web Team identified several high-impact underground posts this week, including alleged leaks involving SeAH Holdings, Under Armour, SecureTeen, and Indonesian cloud provider Cloudeka. Threat actors claimed supply chain…
 SOCRadar
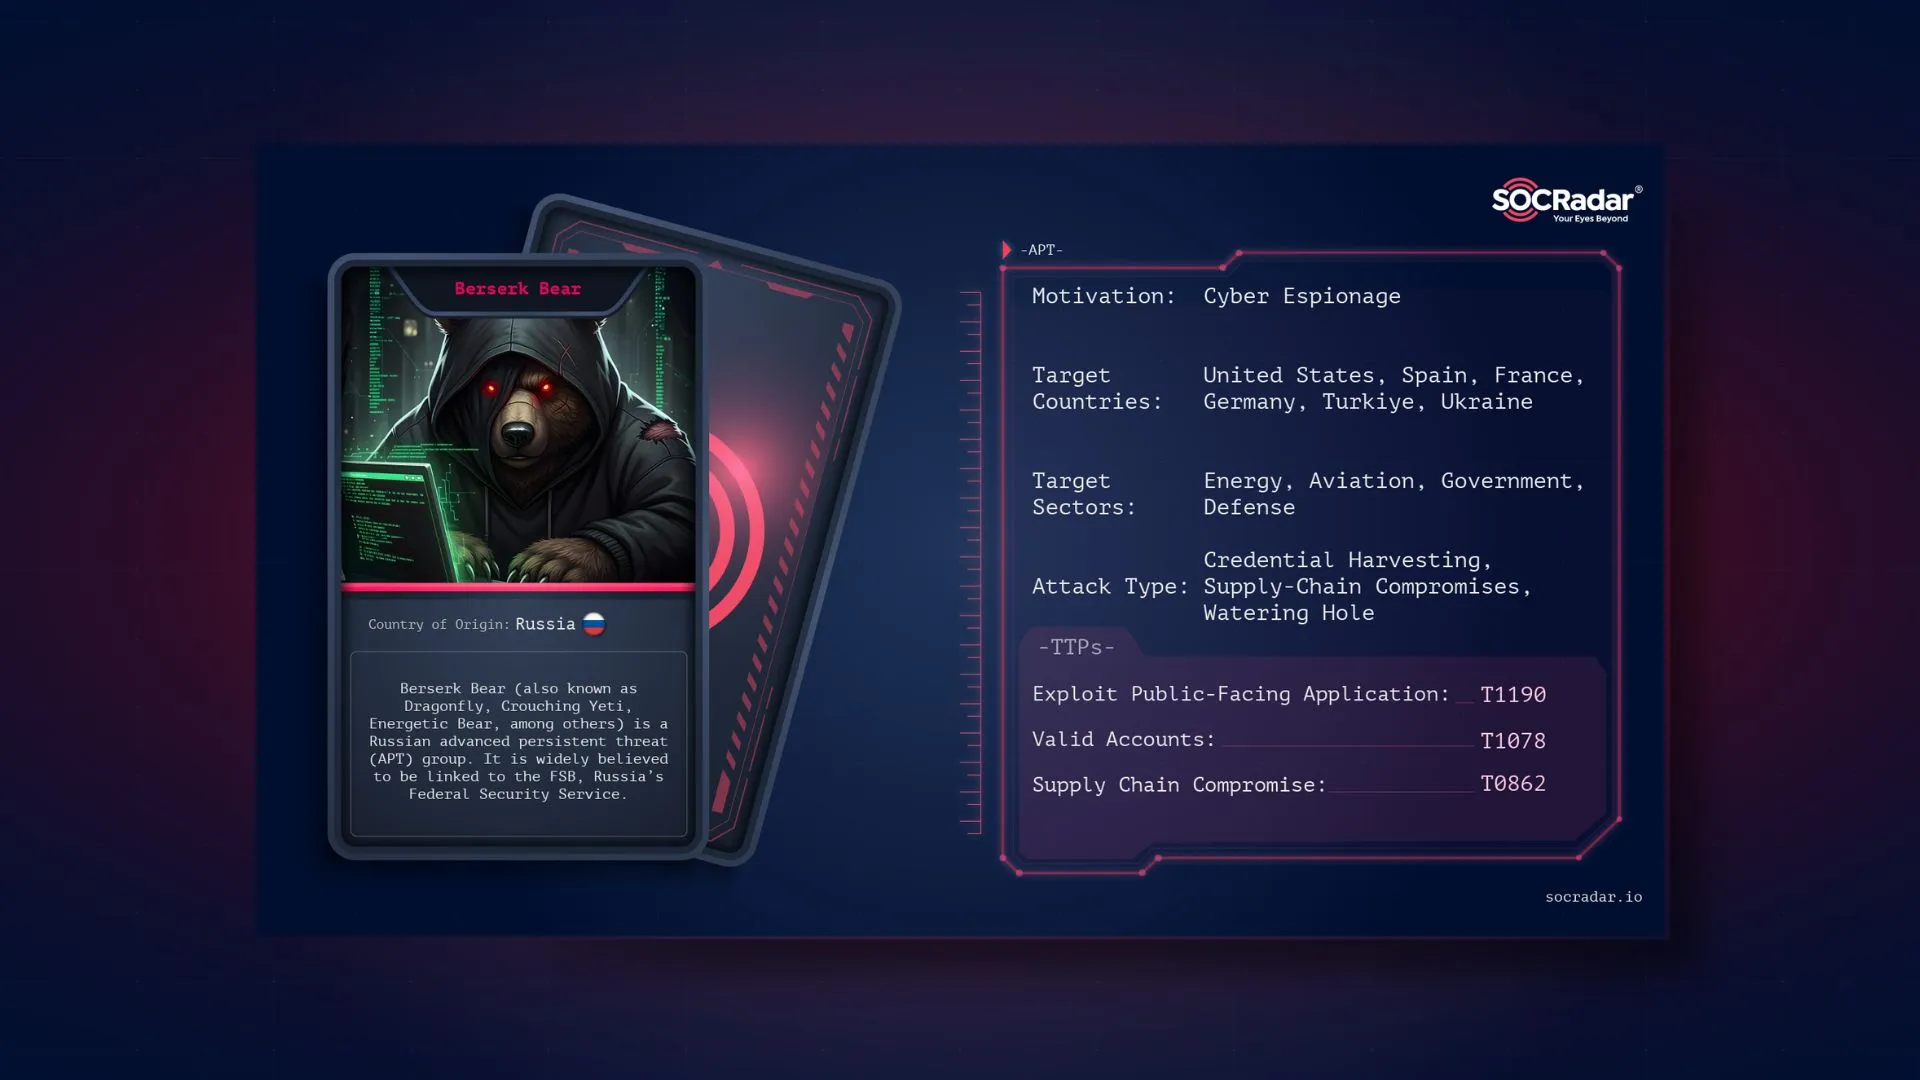
Dark Web Profile: Berserk Bear
Berserk Bear is a Russian state-sponsored cyber espionage group linked to the FSB. They have been active since at least 2010 under many names (Dragonfly, Energetic Bear, Havex, Crouching Yeti,…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action