Latest articles
 SOCRadar
What Are Initial Access Brokers (IABs)?
Cyberattacks rarely begin with encryption or data theft. They often start with a quiet exchange: one threat actor selling unauthorized access to a compromised network. This is the role of…
 SOCRadar
Android Root Exploit, Oracle EBS Flaw, Crypto Logins, and Cisco Access Posted for Sale
SOCRadar’s Dark Web Team has identified several new posts on underground forums offering high-value exploits, access credentials, and corporate network access. The listings include alleged zero-day vulnerabilities targeting Android and…
 SOCRadar
New Alleged Leaks Hit Vodafone Egypt, SAP Israel, OKX, and T-Mobile US
SOCRadar’s Dark Web Team has detected multiple alleged database listings this week involving high-profile companies across telecom, technology, and finance sectors. Threat actors claim to be selling or leaking user…
 SOCRadar
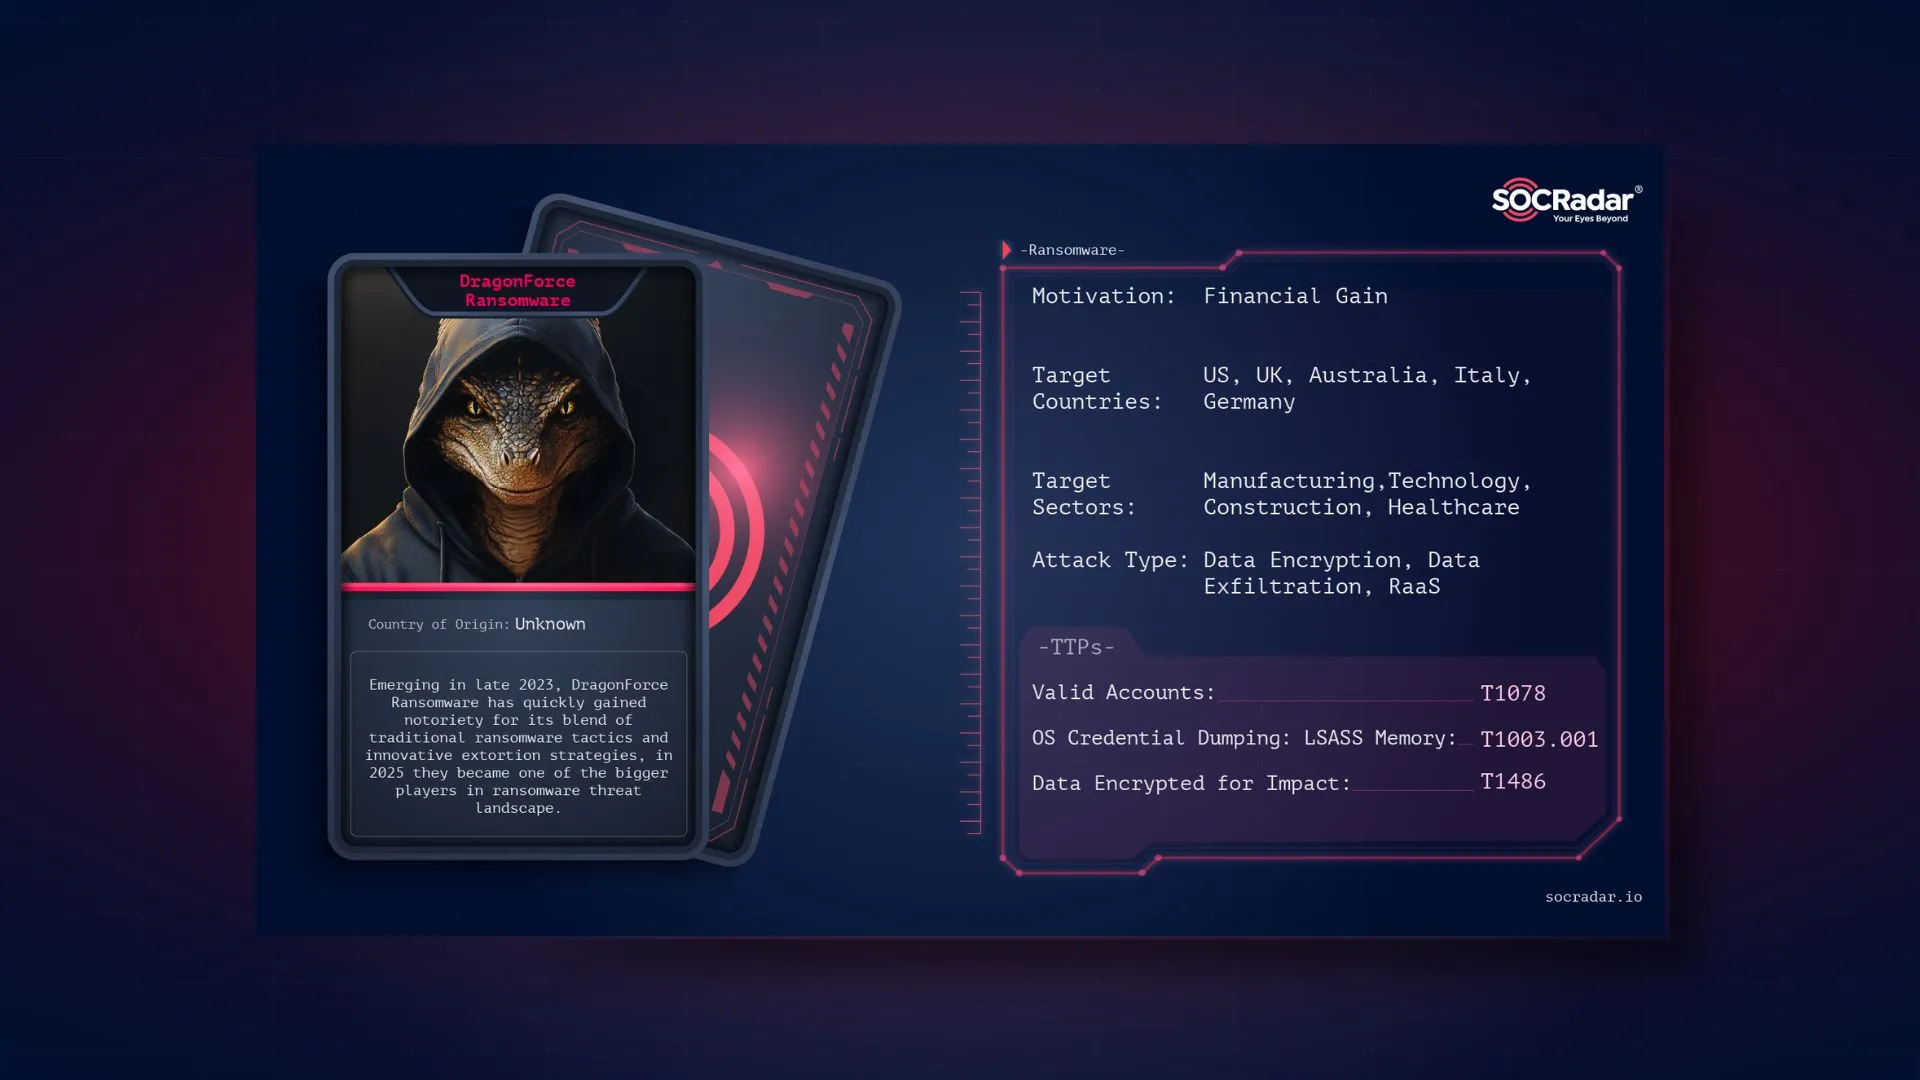
Dark Web Profile: DragonForce Ransomware
June 12, 2025: The blog content has been fully updated. DragonForce Ransomware has emerged as an intriguing adversary. Known for its prominent targets and unusual ways of communication, it has…
 SOCRadar
Fusion Stealer Rises, Android 0-Day for Sale, EDF Leak Exposed
SOCRadar’s Dark Web Team has uncovered a series of concerning cybercriminal offerings this week, ranging from an alleged Android 0-day exploit with global espionage implications to the rental of the…
 SOCRadar
Top Stealer Log Telegram Channels
Telegram has become a widely used tool among cybercriminals involved in the collection and trade of infostealer logs. These logs, obtained by malware designed to steal credentials, cookies, cryptocurrency wallets,…
 SOCRadar
New Alleged Breaches: Bank Banten Customer Data, Deloitte Source Code, and TotalEnergies France
Cybercriminal activity across the Dark Web continues to highlight the vulnerability of organizations and personal data. This week, SOCRadar’s Dark Web Team has tracked multiple high-profile incidents: two separate posts…
 SOCRadar
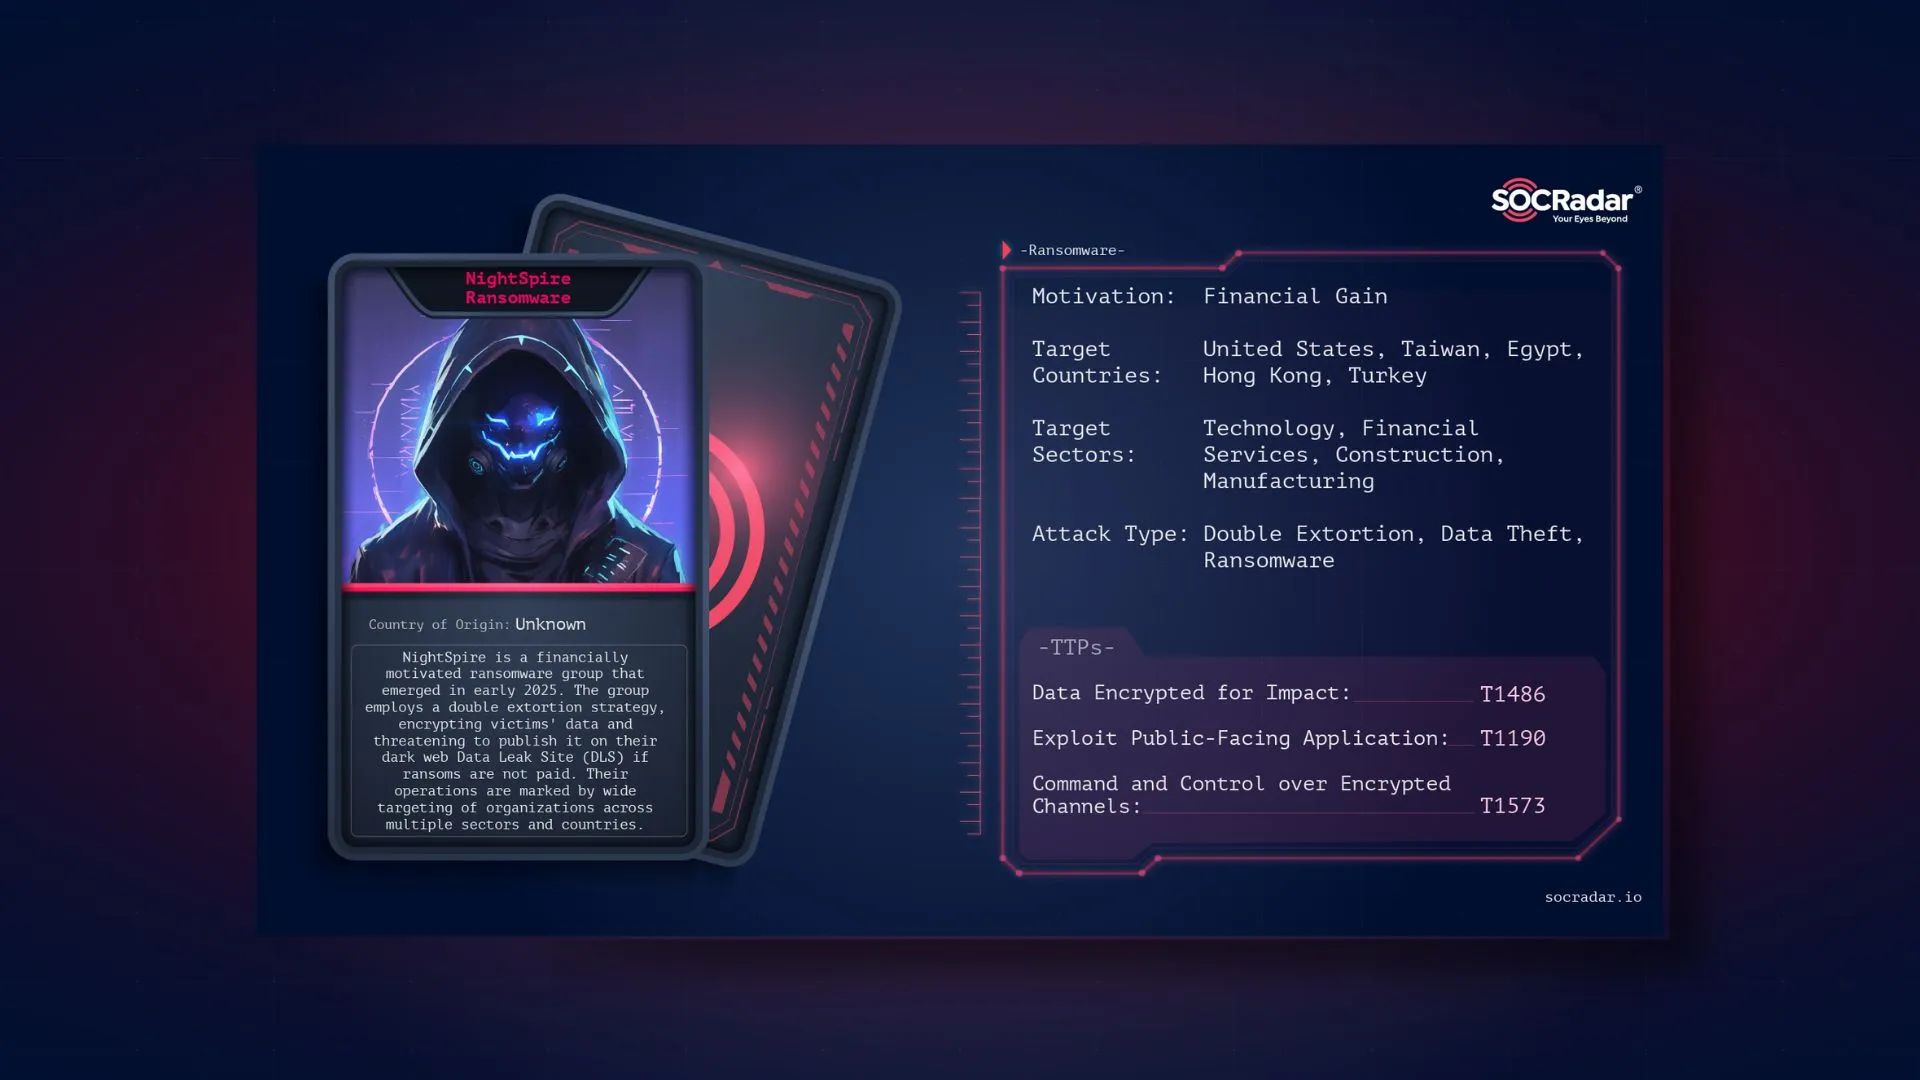
Dark Web Profile: NightSpire Ransomware
NightSpire is a financially motivated ransomware group that emerged in early 2025. The group employs a double extortion strategy, encrypting victims’ data and threatening to publish it on their Dark…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action