Latest articles
 SOCRadar
Top Dark Web Telegram Groups & Channels 2026
Note: This article is intended for cybersecurity awareness and research purposes only. It does not promote or endorse illegal content. The top Dark Web Telegram channels and groups monitored in…
 SOCRadar
Top 10 Dark Web Markets in 2026: List & Threat Analysis
Dark Web marketplaces in 2026 are underground platforms where cybercriminals buy and sell stolen data, credentials, stealer logs, payment card records, malware, fraud services, counterfeit documents, drugs, and access to…
 SOCRadar
Alleged FortiBleed Access Auction, Sens Unique Paris Data Sale, and libsodium DoS Claims
SOCRadar Dark Web Team identified new underground activity involving alleged FortiBleed-related access, an alleged 529,892-record customer database linked to French retailer Sens Unique Paris, and a claimed libsodium and NaCl…
 SOCRadar
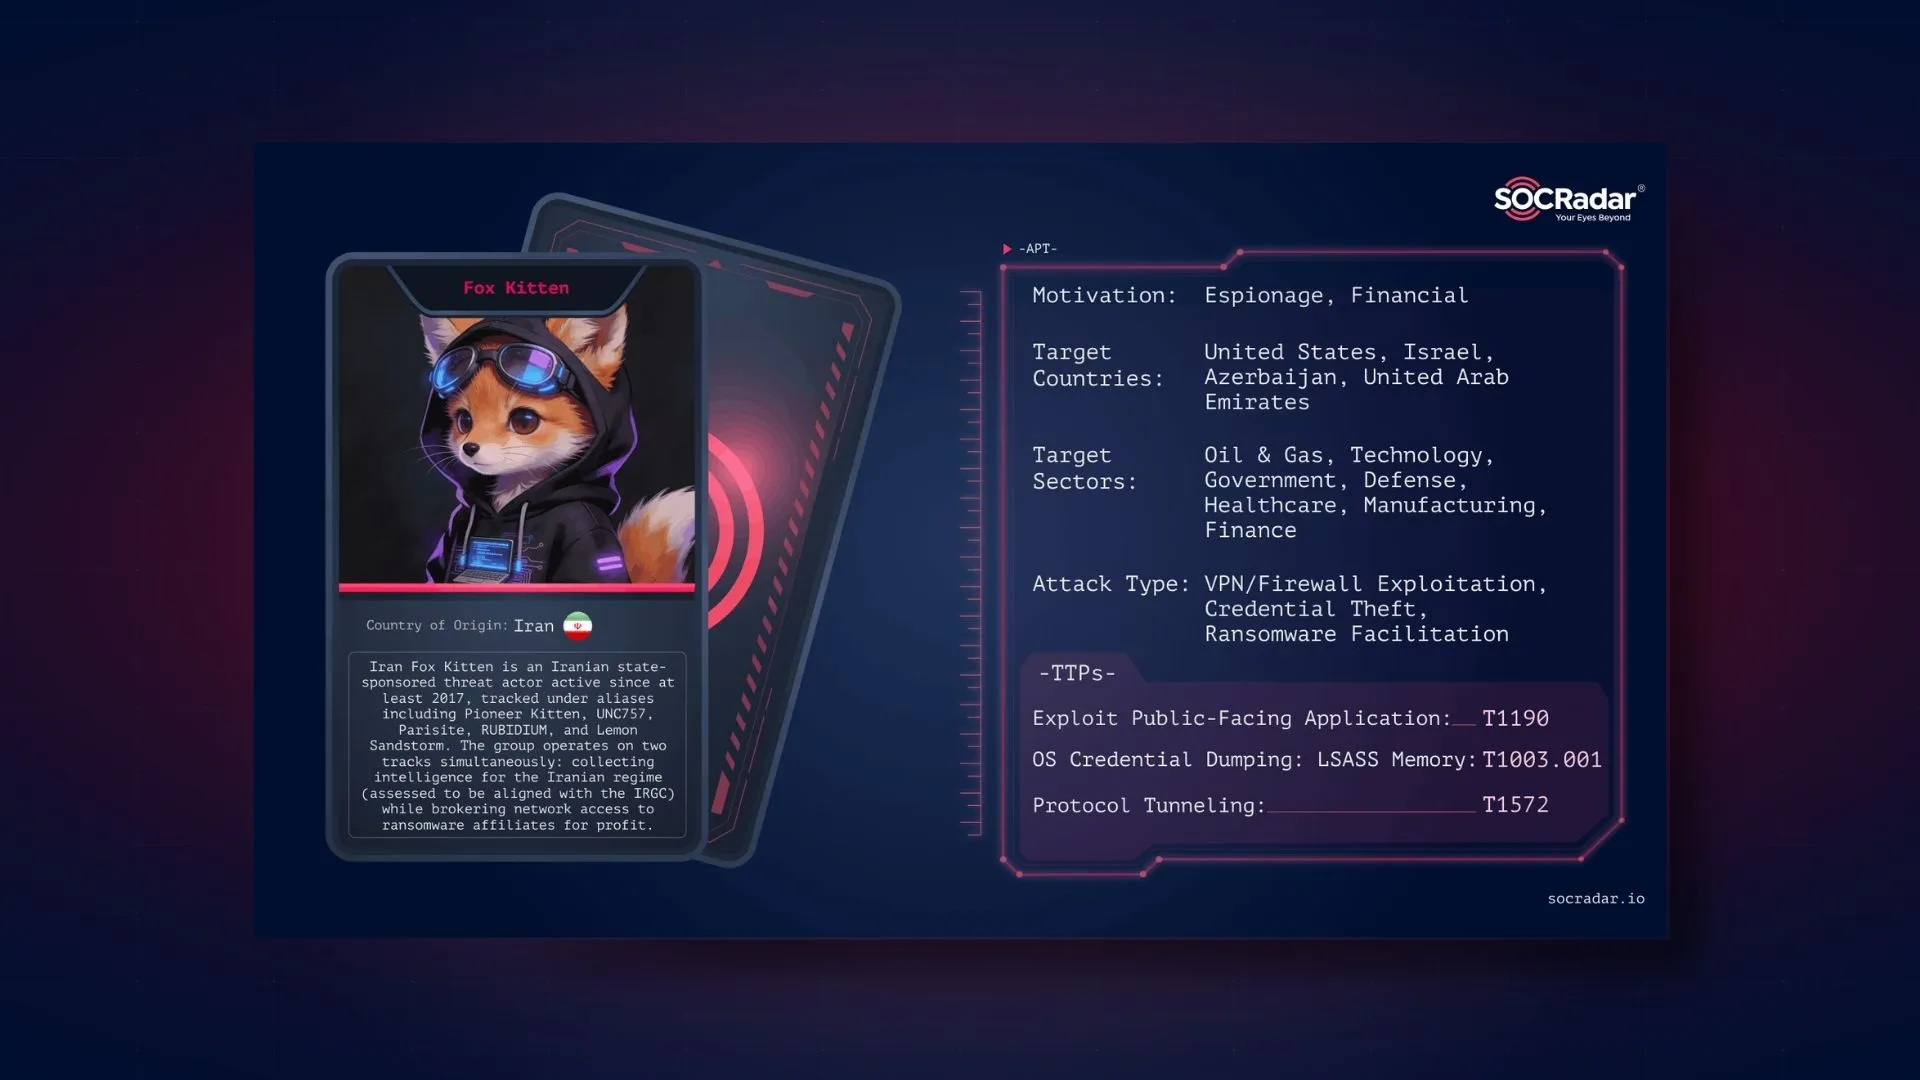
Dark Web Profile: Fox Kitten
Fox Kitten stands out among Iranian Advanced Persistent Threat (APT) groups for operating on two tracks simultaneously: collecting intelligence for the Iranian regime while brokering network access to ransomware affiliates…
 SOCRadar
Iran Hajj Organization Data Claim, Crypto Leads Sale, APT43 Tooling Claim, Sweden User Data, and Chrysler Breach Claim
SOCRadar’s Dark Web Team identified several new underground posts, including an alleged 168 million-record database sale tied to Iran’s Hajj and Pilgrimage Organization and a separate listing offering large volumes…
 SOCRadar
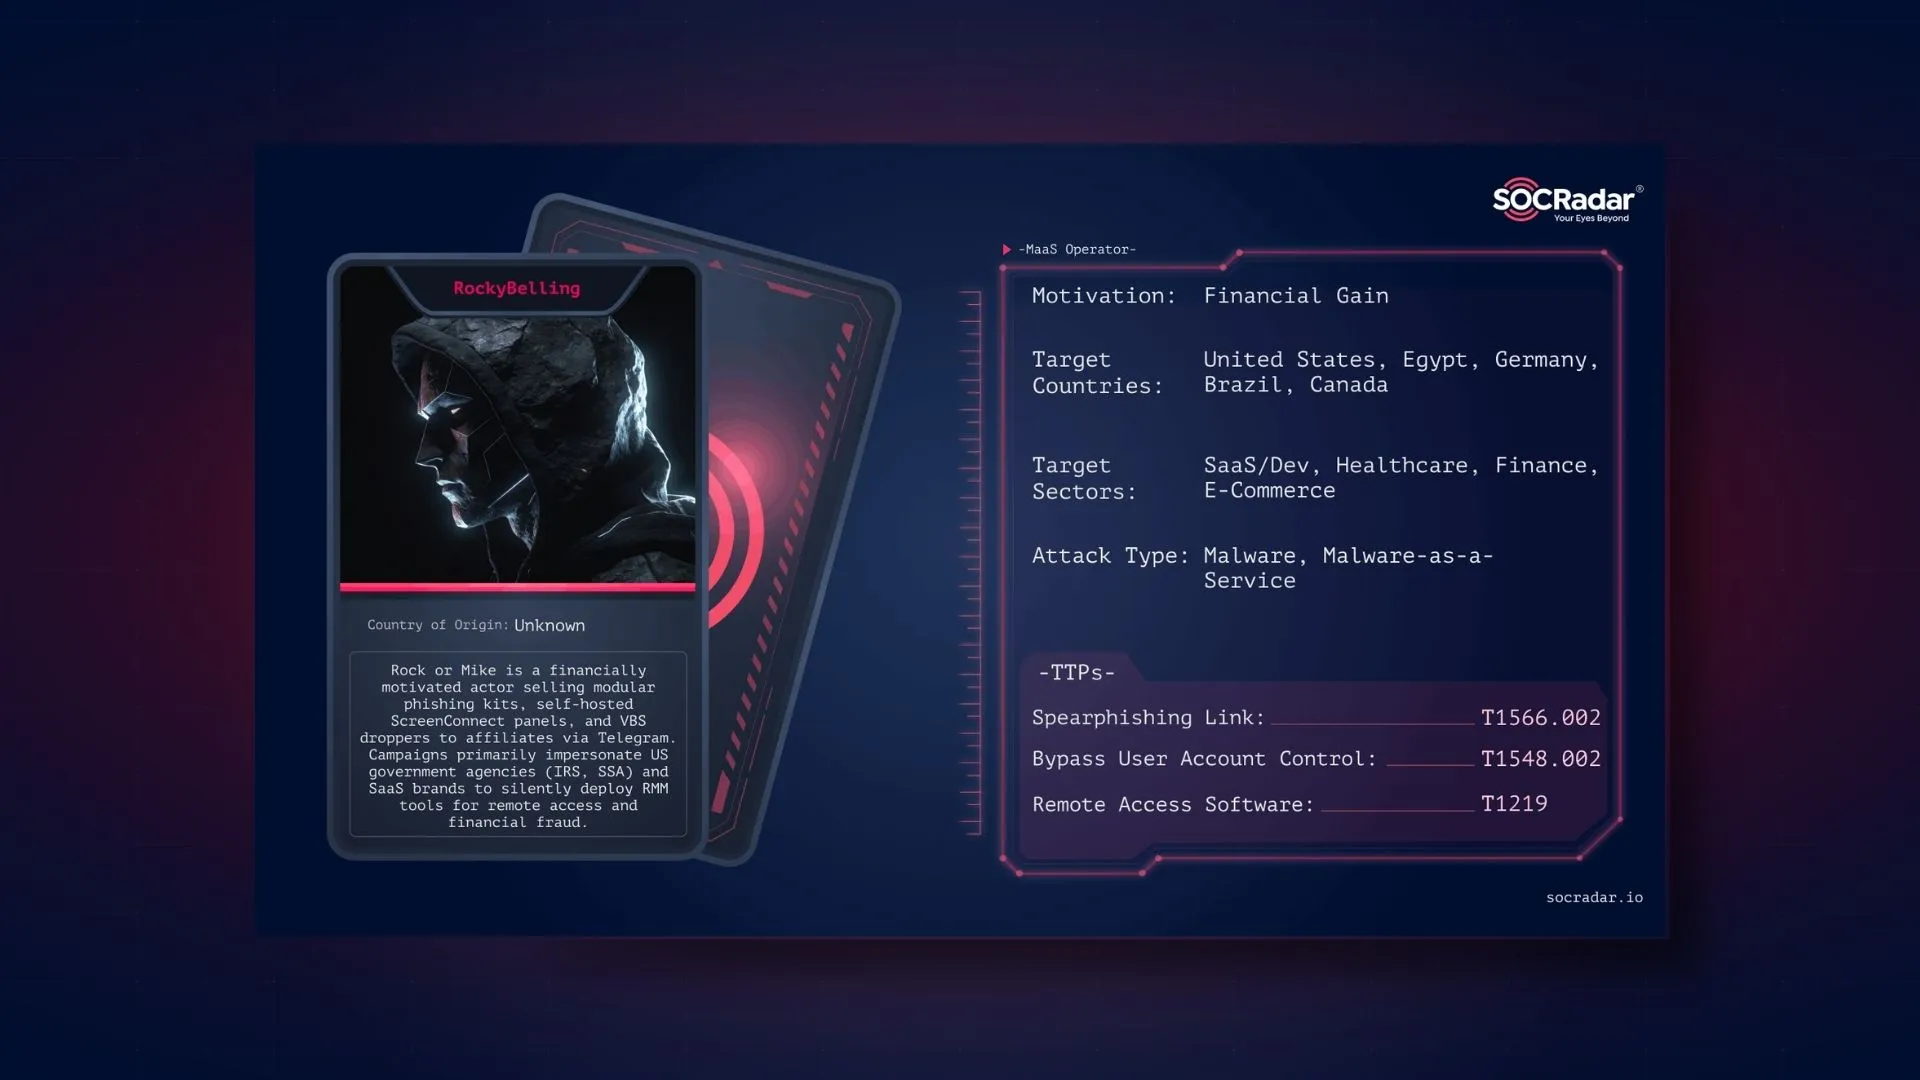
Dark Web Profile: Rock
Most Phishing-as-a-Service operations are run by a faceless brand. Rock is the opposite: a single developer who builds, maintains, and sells an entire phishing and remote access toolkit, then sits…
 SOCRadar
New Data Extortion Group “Pink” Goes Big Game Hunting With Evasive Phishing Kits
Pink Data Extortion Group is emerging as one of the latest examples of how voice phishing and data extortion continue to shape the threat landscape. Instead of relying on noisy…
 SOCRadar
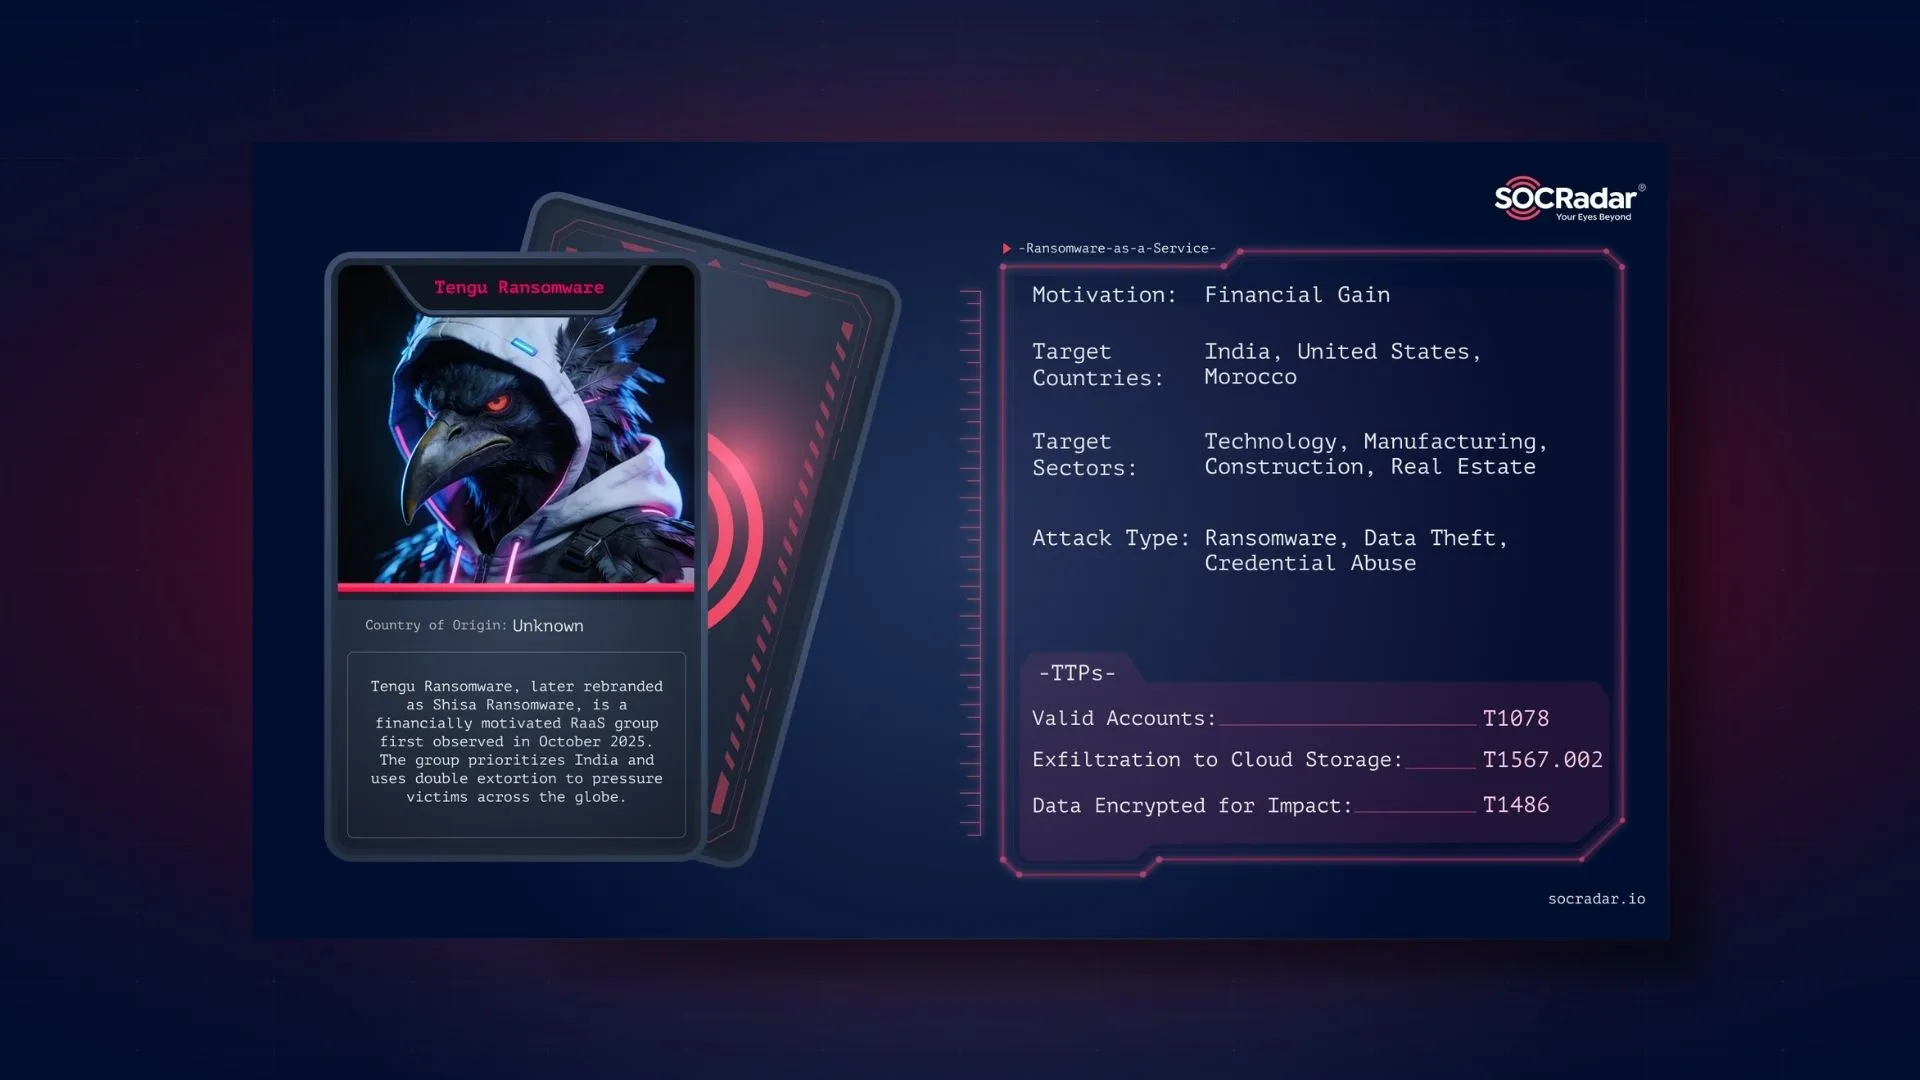
Dark Web Profile: Tengu Ransomware (Shisa)
Despite a measured public persona, Tengu Ransomware operates as a financially motivated, well-organized threat. First observed in late 2025, the group emerged as a Ransomware-as-a-Service (RaaS) operation combining a double-extortion…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action