Latest articles
 SOCRadar
 Unveils ‘Treemium’: Report a Bug, Plant a Future with SOCRadar
We are overjoyed to pull back the curtain on a new initiative from SOCRadar – Treemium! This new initiative, rooted in our commitment to environmental stewardship and robust cybersecurity, is…
 SOCRadar
Microsoft’s August 2023 Patch Tuesday Fixes Six Critical Vulnerabilities and Two Exploited Zero-Days
Microsoft’s August 2023 Patch Tuesday has just arrived. The update addresses a total of 74 vulnerabilities, six of which have critical severity, and two zero-days that are actively exploited. Additionally,…
 SOCRadar
Complex RCE Vulnerability (CVE-2023-39143) in PaperCut Application Servers
PaperCut NG and PaperCut MF are extensively utilized software solutions for print management servers. CVE-2023-39143 refers to path traversal vulnerabilities found in PaperCut NG and PaperCut MF versions released prior…
 SOCRadar
Critical Microsoft Power Platform Vulnerability: Proactive Security Methods to Prevent Exploitation
Microsoft fixed a critical vulnerability in its Power Platform after facing criticism for the delayed response. Tenable reported the vulnerability to Microsoft on March 30, 2023, and an official fix…
 SOCRadar
Threat Actors Employ New Phishing Tactic Using Google AMP
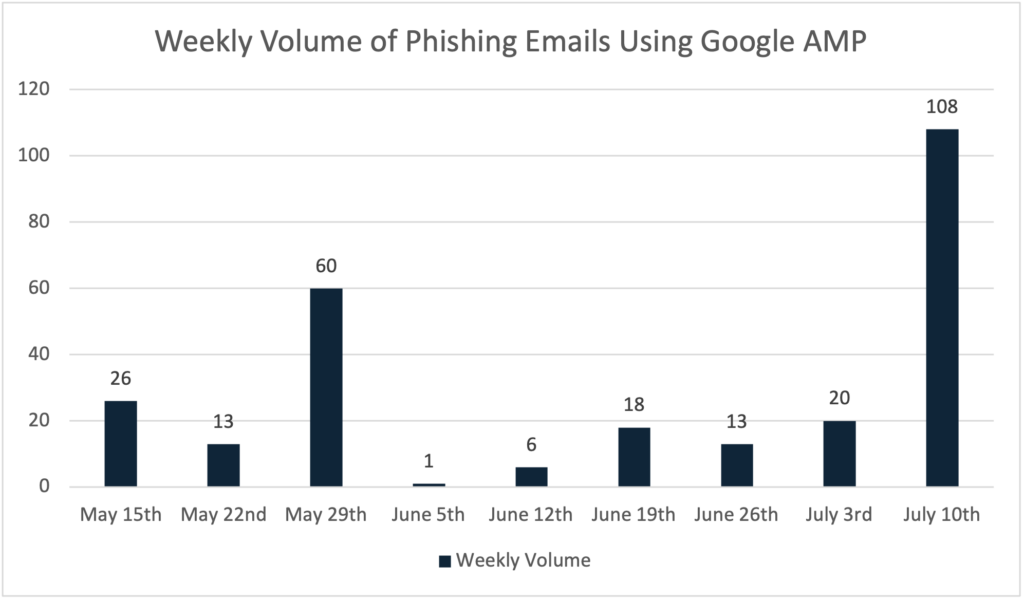
Researchers have uncovered a highly effective phishing tactic, which utilizes Google AMP (Accelerated Mobile Pages). Google AMP is an open-source HTML framework designed to create websites optimized for mobile browsers.…
 SOCRadar
Living Off the Land (LOTL): The Invisible Cyber Threat Lurking in Your System
[Update] January 10, 2024: “Countering Living Off the Land (LOTL) Attack Methods with AI and ML” What is LOTL Attack? Living Off the Land (LOTL), also known as lolbins, is…
Top 10 Ransomware Demands
In cyberspace, few threats rival ransomware attacks’ pervasive and destructive nature. As our interconnected world grows, these digital extortionists demonstrate unparalleled audacity. Their actions span from crippling multinational corporations to…
 SOCRadar
P2Pinfect: A Worm-Like Botnet Malware Targeting Redis Deployments
[Update] June 26, 2024: “P2PInfect Botnet: Recent Developments and Ransomware Deployment” Researchers have identified an unknown group of hackers employing a novel strain of malware named “P2Pinfect” to target publicly-accessible…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action