Latest articles
 SOCRadar
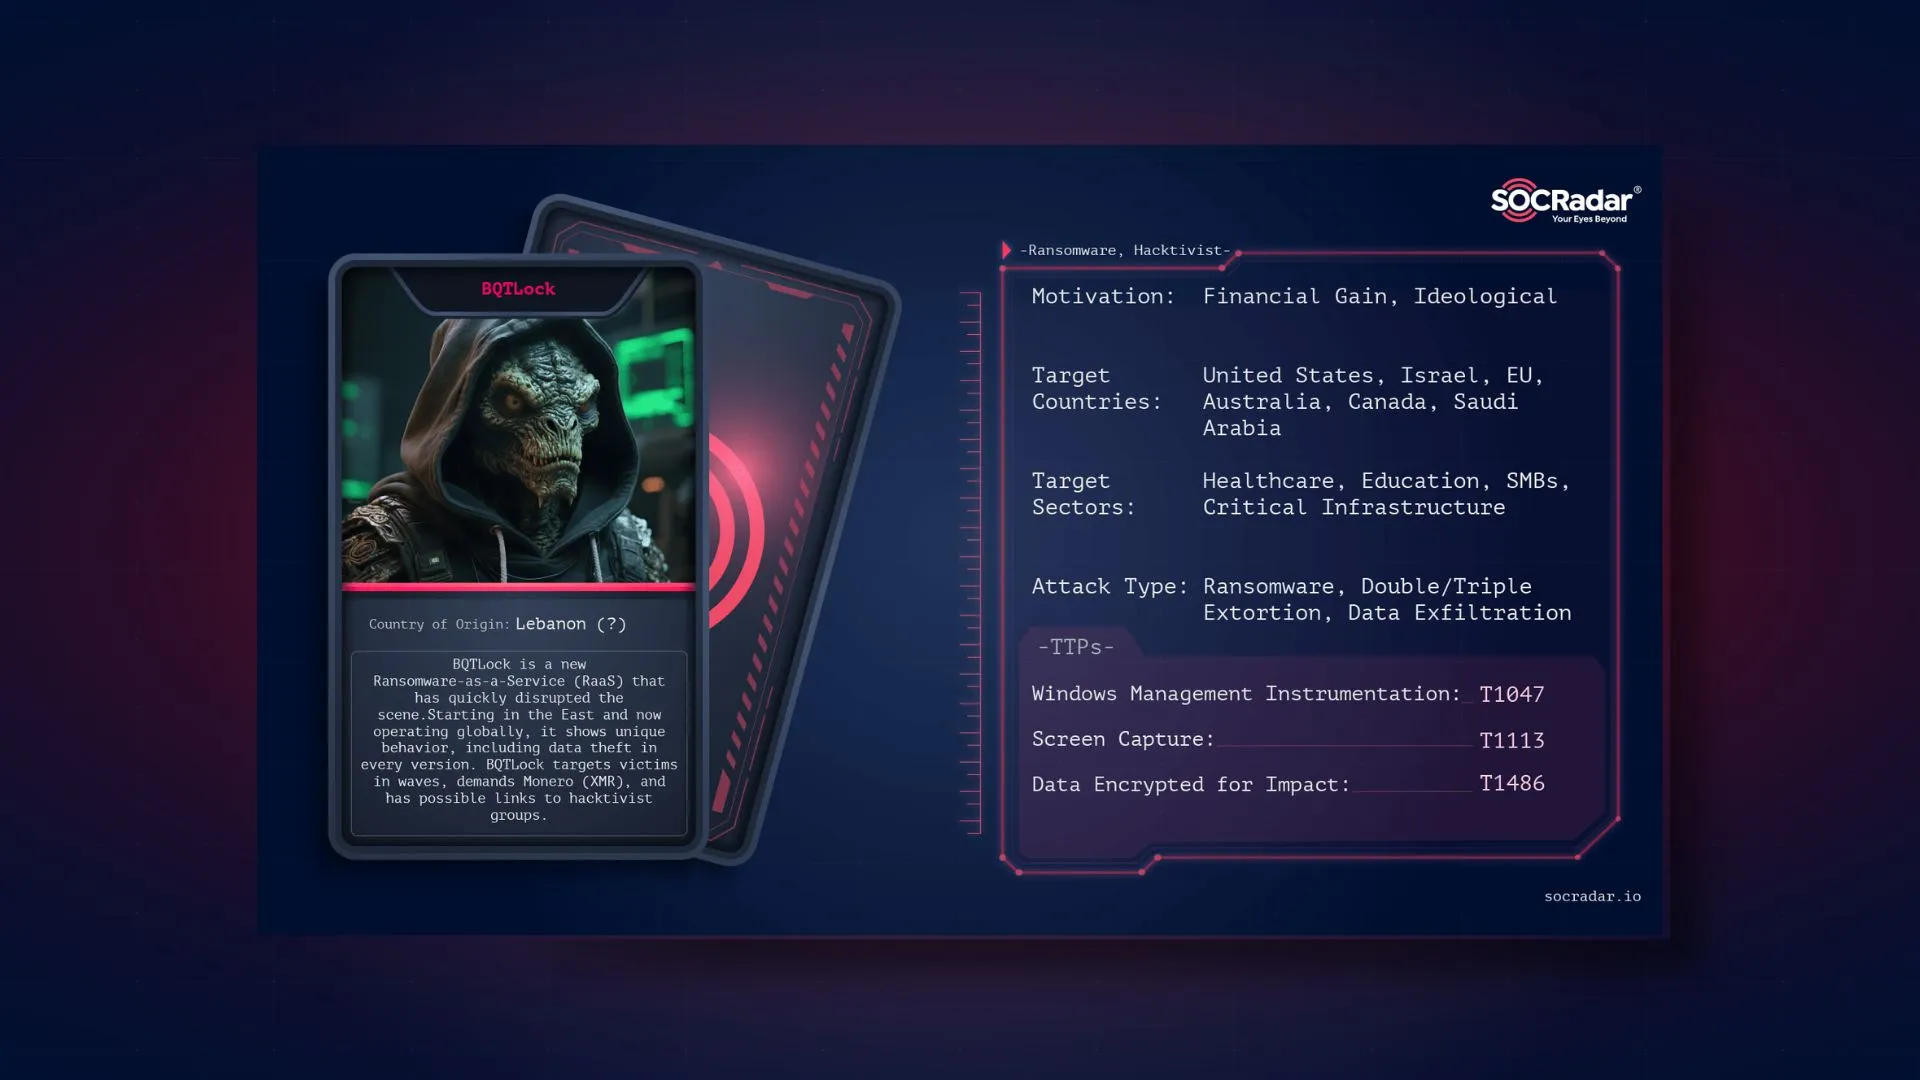
Dark Web Profile: BQTLock Ransomware
BQTLock is a new and advanced Ransomware-as-a-Service (RaaS) that has quickly gained attention for its disruptive operations and unique methods. Emerging from the Middle East and expanding globally, it shows…
 SOCRadar
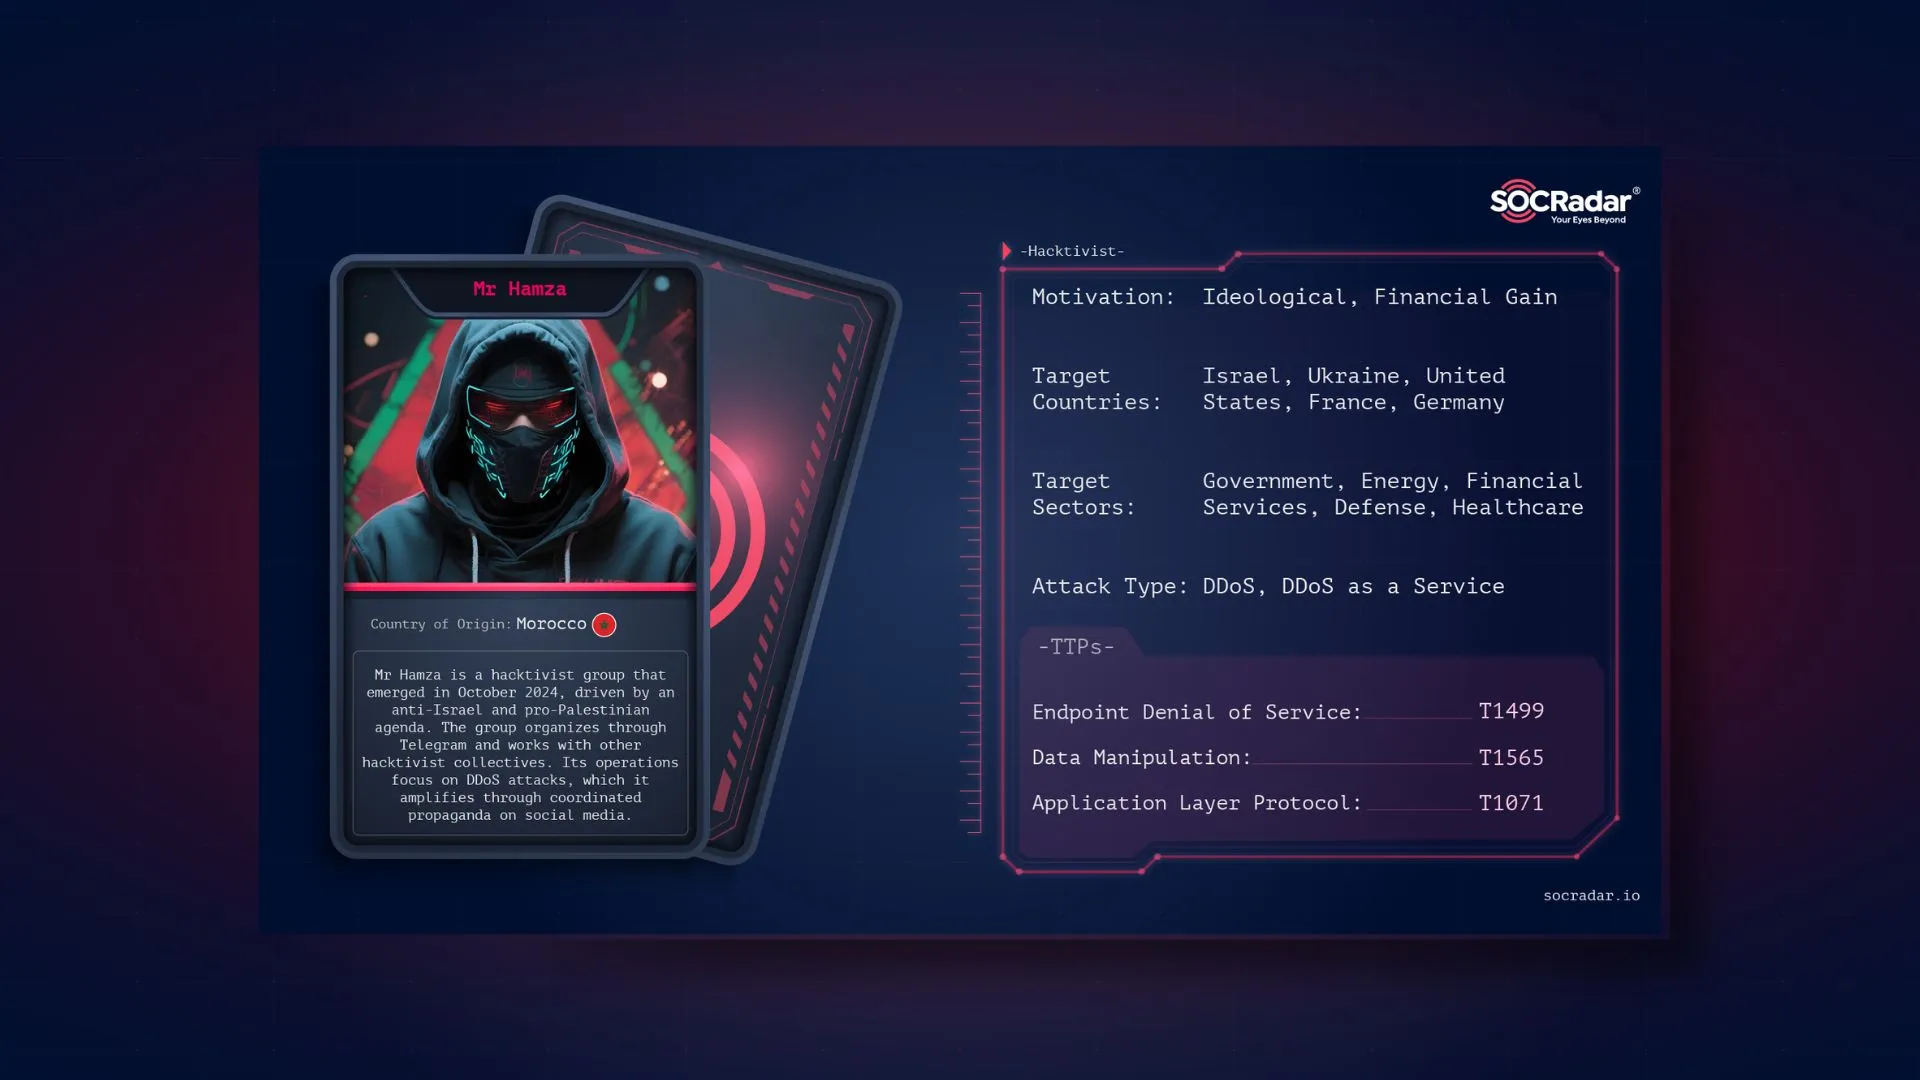
Dark Web Profile: Mr Hamza
Hacktivist groups like Mr Hamza have turned Telegram into a staging ground for cyber campaigns. These channels serve as meeting points where supporters coordinate Distributed Denial of Service (DDoS) attacks,…
 SOCRadar
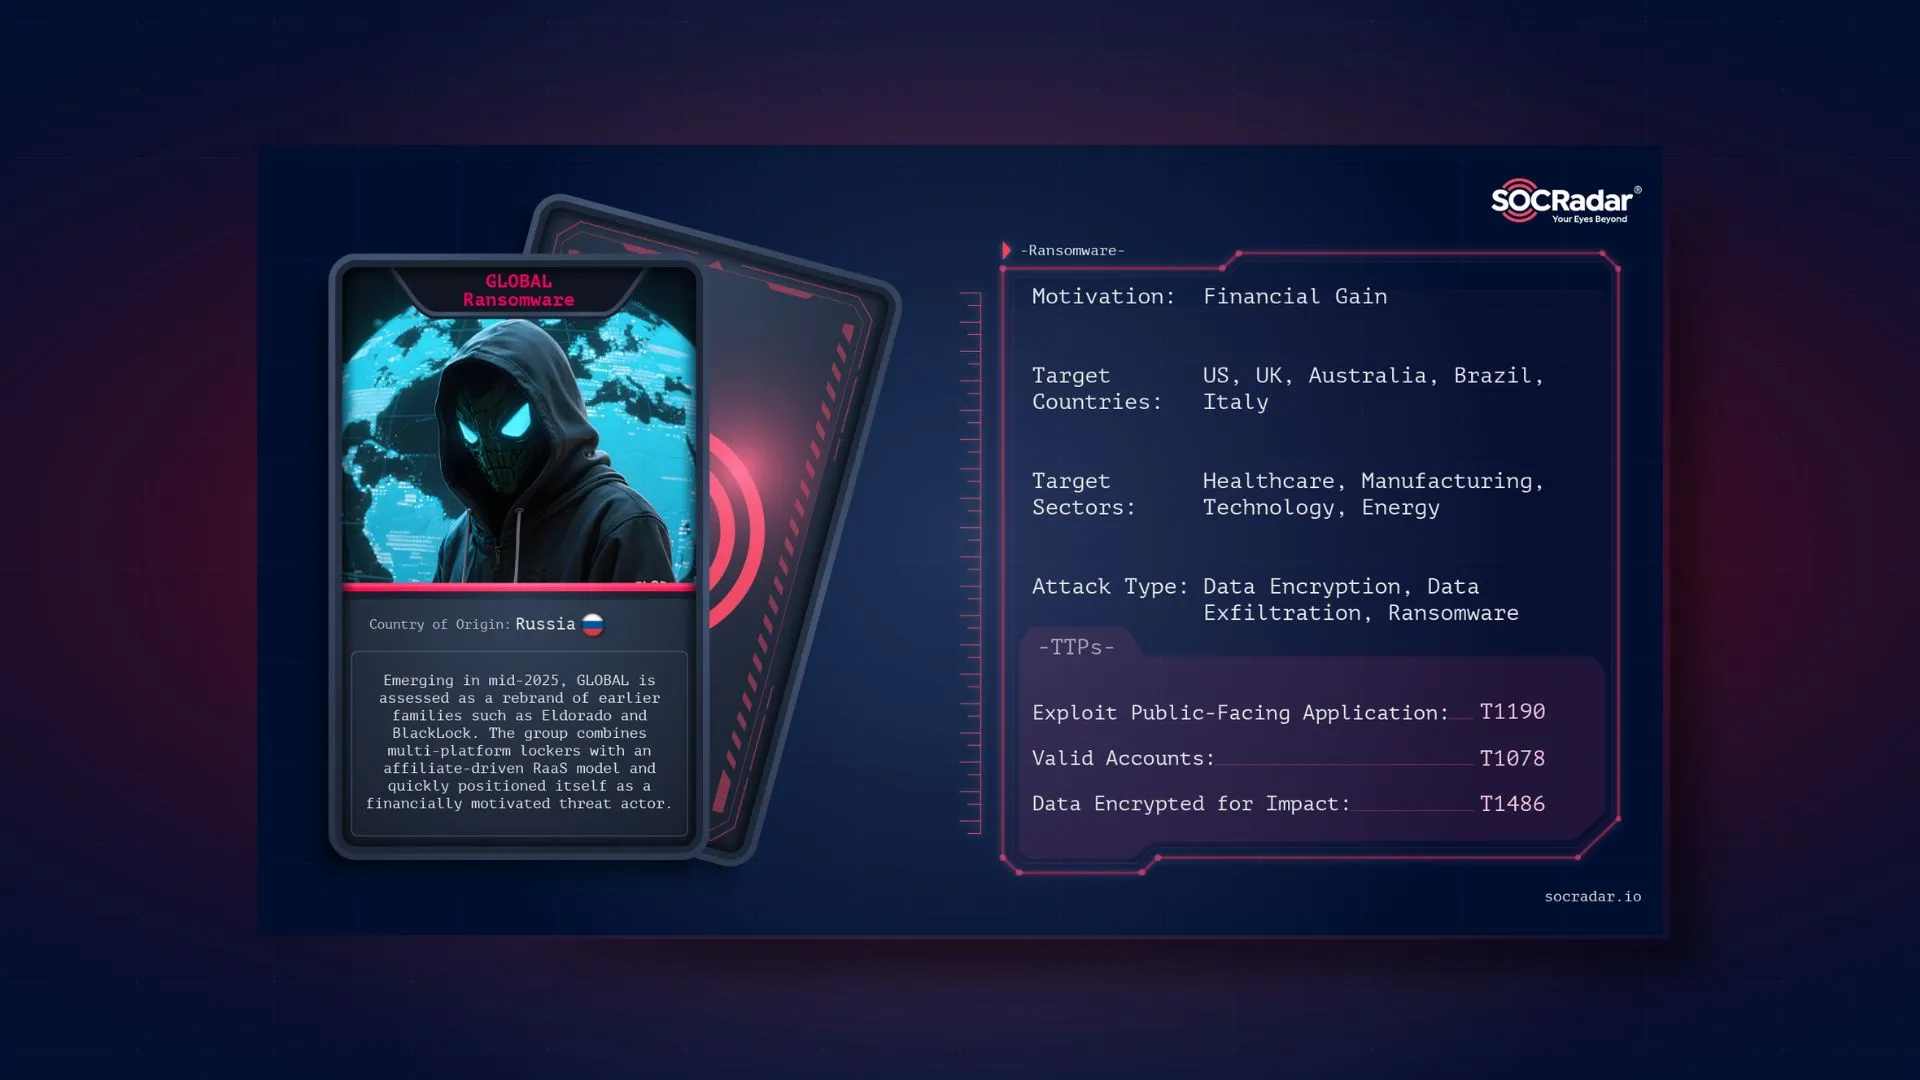
Dark Web Profile: GLOBAL Ransomware
GLOBAL Ransomware, also known as the GLOBAL GROUP, is a newly branded Ransomware-as-a-Service (RaaS) operation that surfaced in mid-2025. Despite being presented as a new player, forensic evidence links GLOBAL…
 SOCRadar
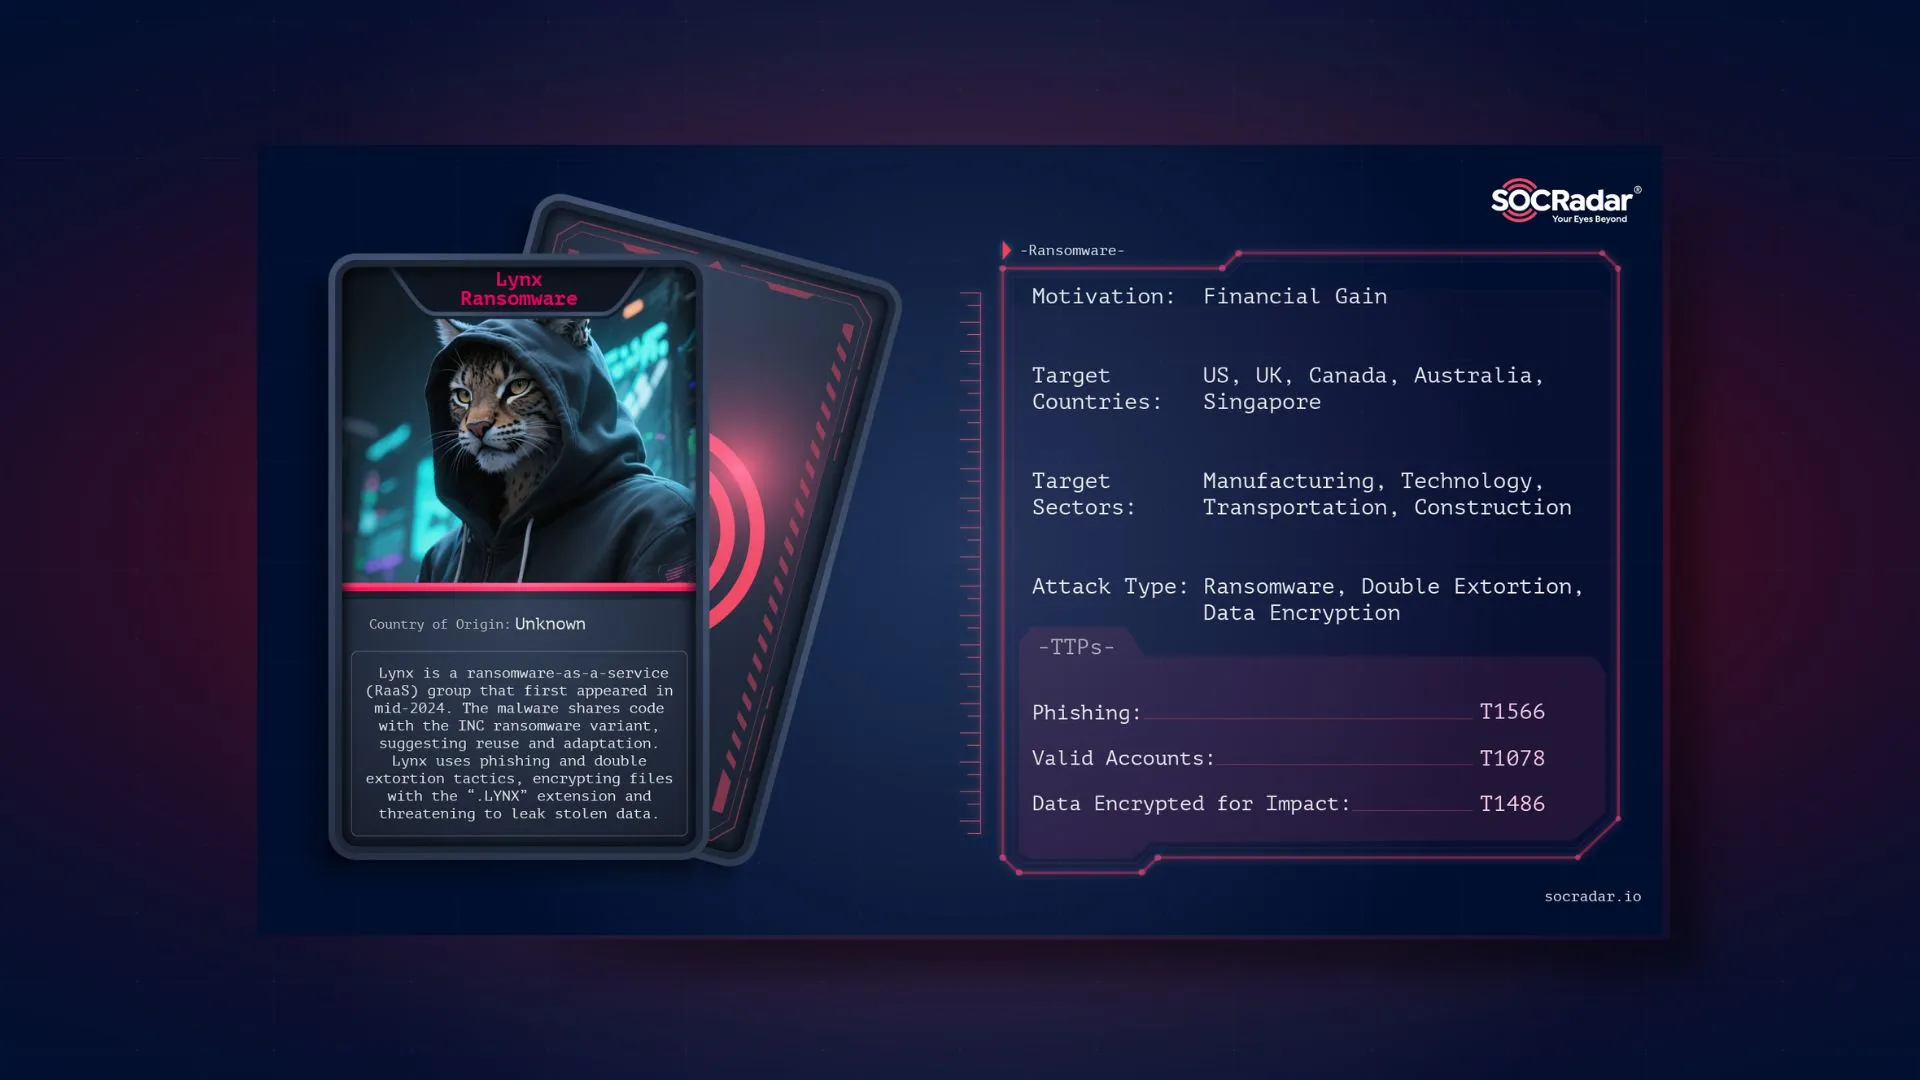
Dark Web Profile: Lynx Ransomware
Lynx is a ransomware group that appeared in mid-2024 and is widely believed to be a rebrand of the INC ransomware operation. The group follows a Ransomware-as-a-Service (RaaS) model, providing…
 SOCRadar
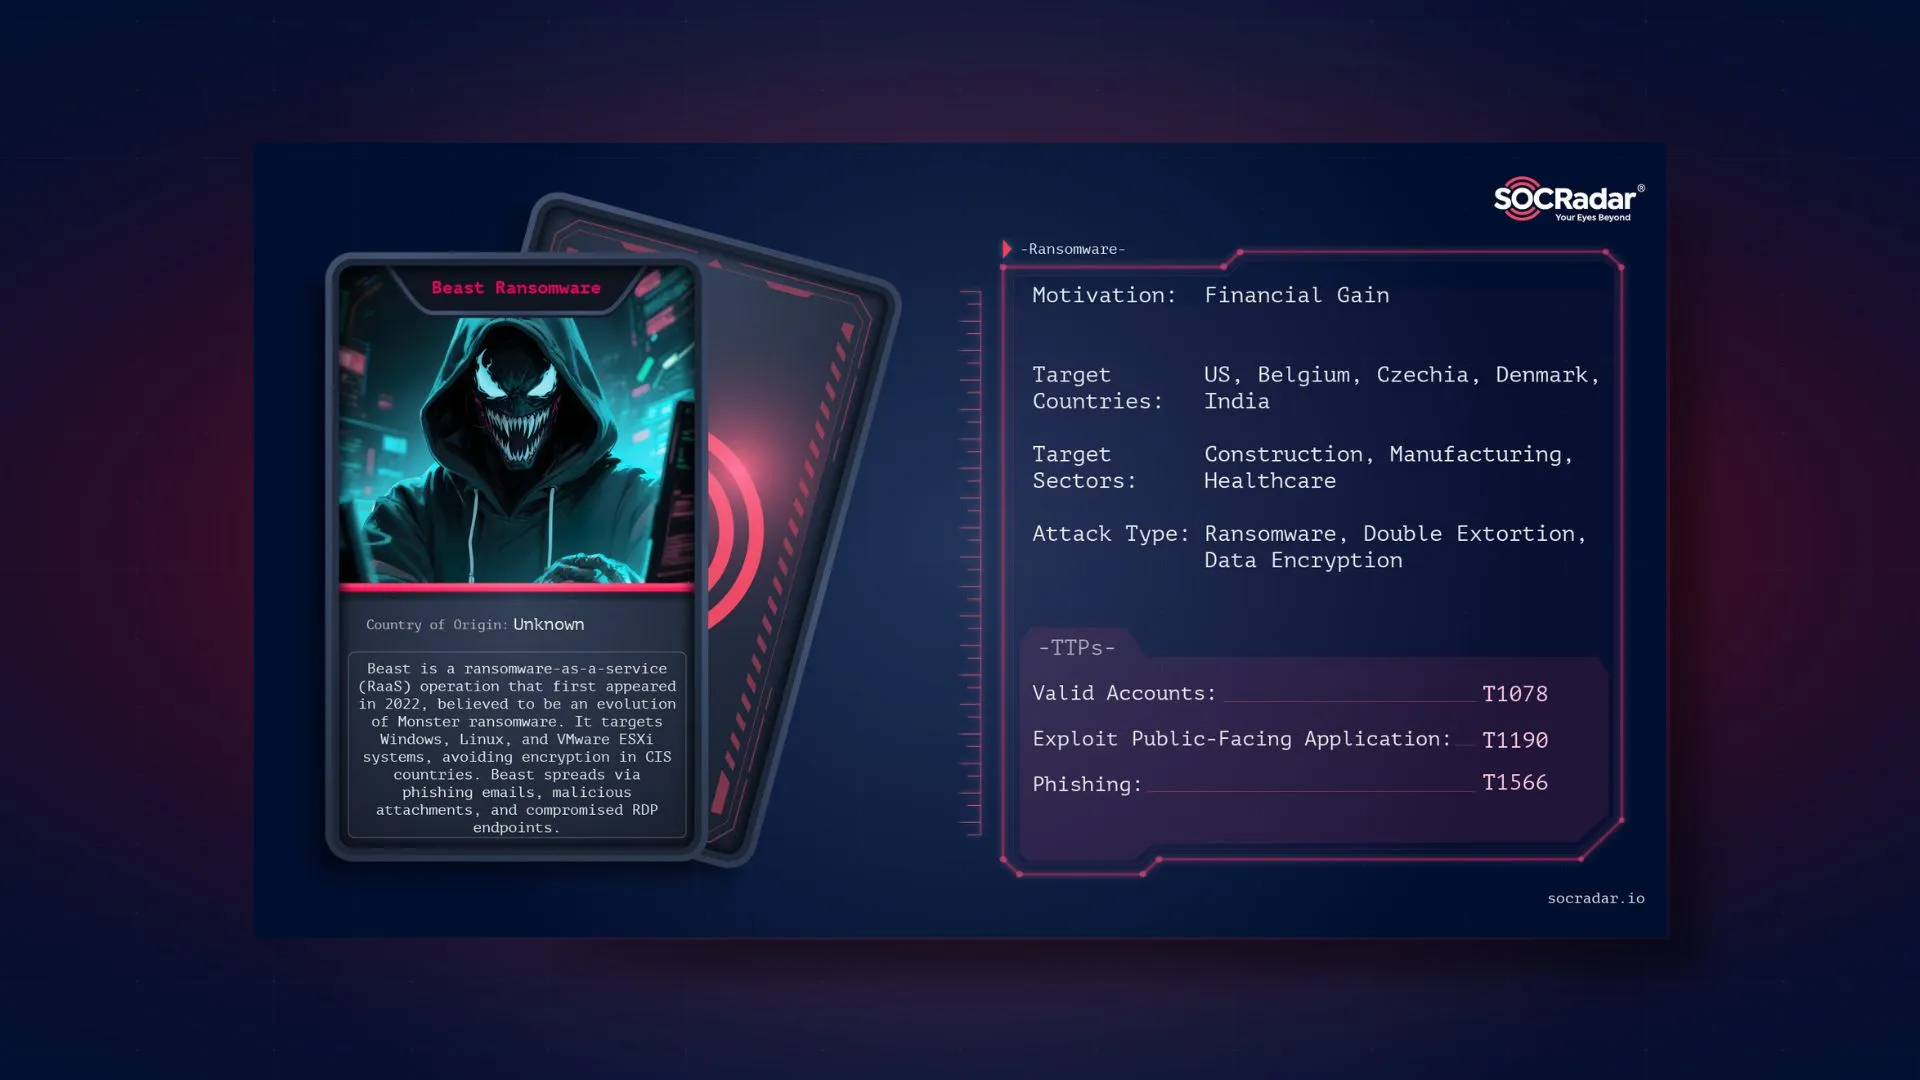
Dark Web Profile: Beast Ransomware
Beast Ransomware is the evolved form of an earlier strain known as Monster, first detected in March 2022 during an investigation by the BlackBerry Incident Response team. Initially developed in…
 SOCRadar
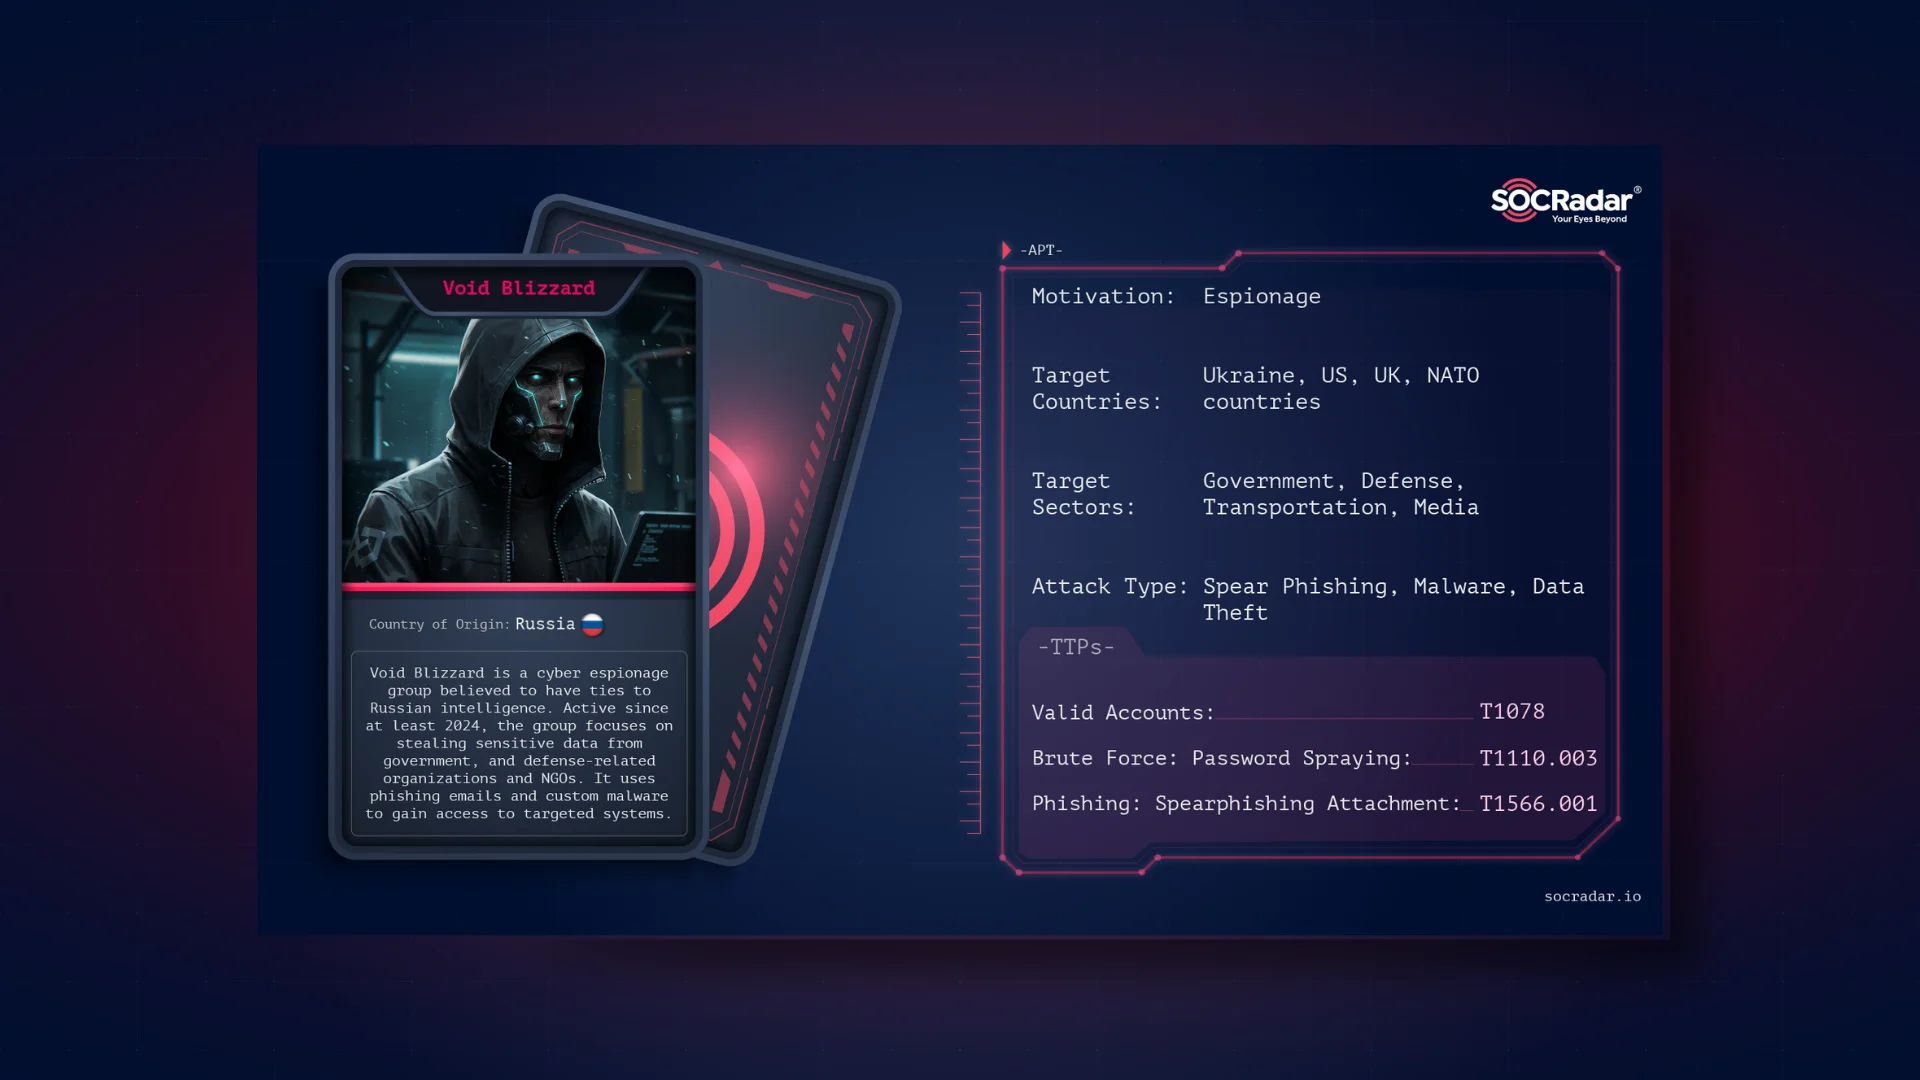
Dark Web Profile: Void Blizzard
Void Blizzard is a newly identified Russian state-sponsored cyber threat group. Also known as Laundry Bear, the group first drew attention after an attack on the Dutch police in September 2024.…
 SOCRadar
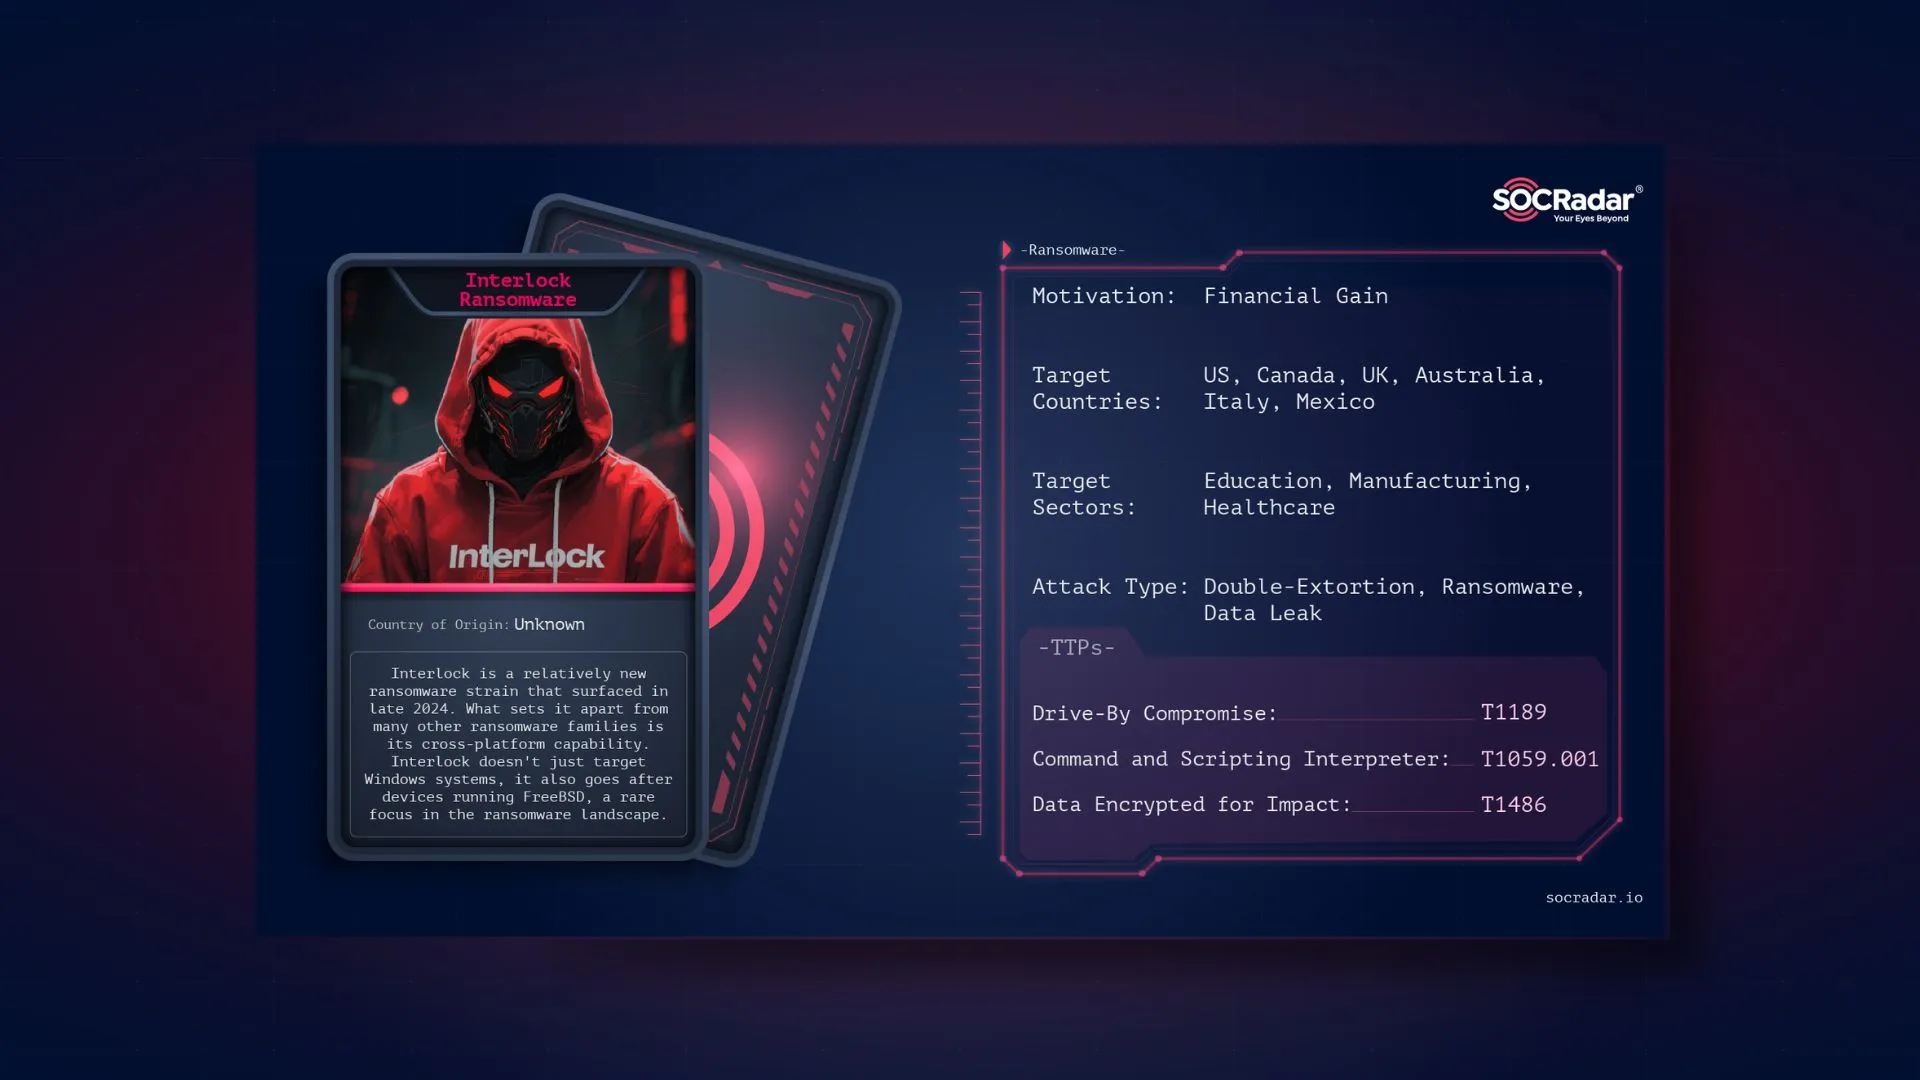
Dark Web Profile: Interlock Ransomware
Interlock is a ransomware group active since late 2024, most recently gaining attention for its use of advanced social engineering tactics. Its latest technique, called ClickFix, tricks users into pasting malicious PowerShell…
 SOCRadar
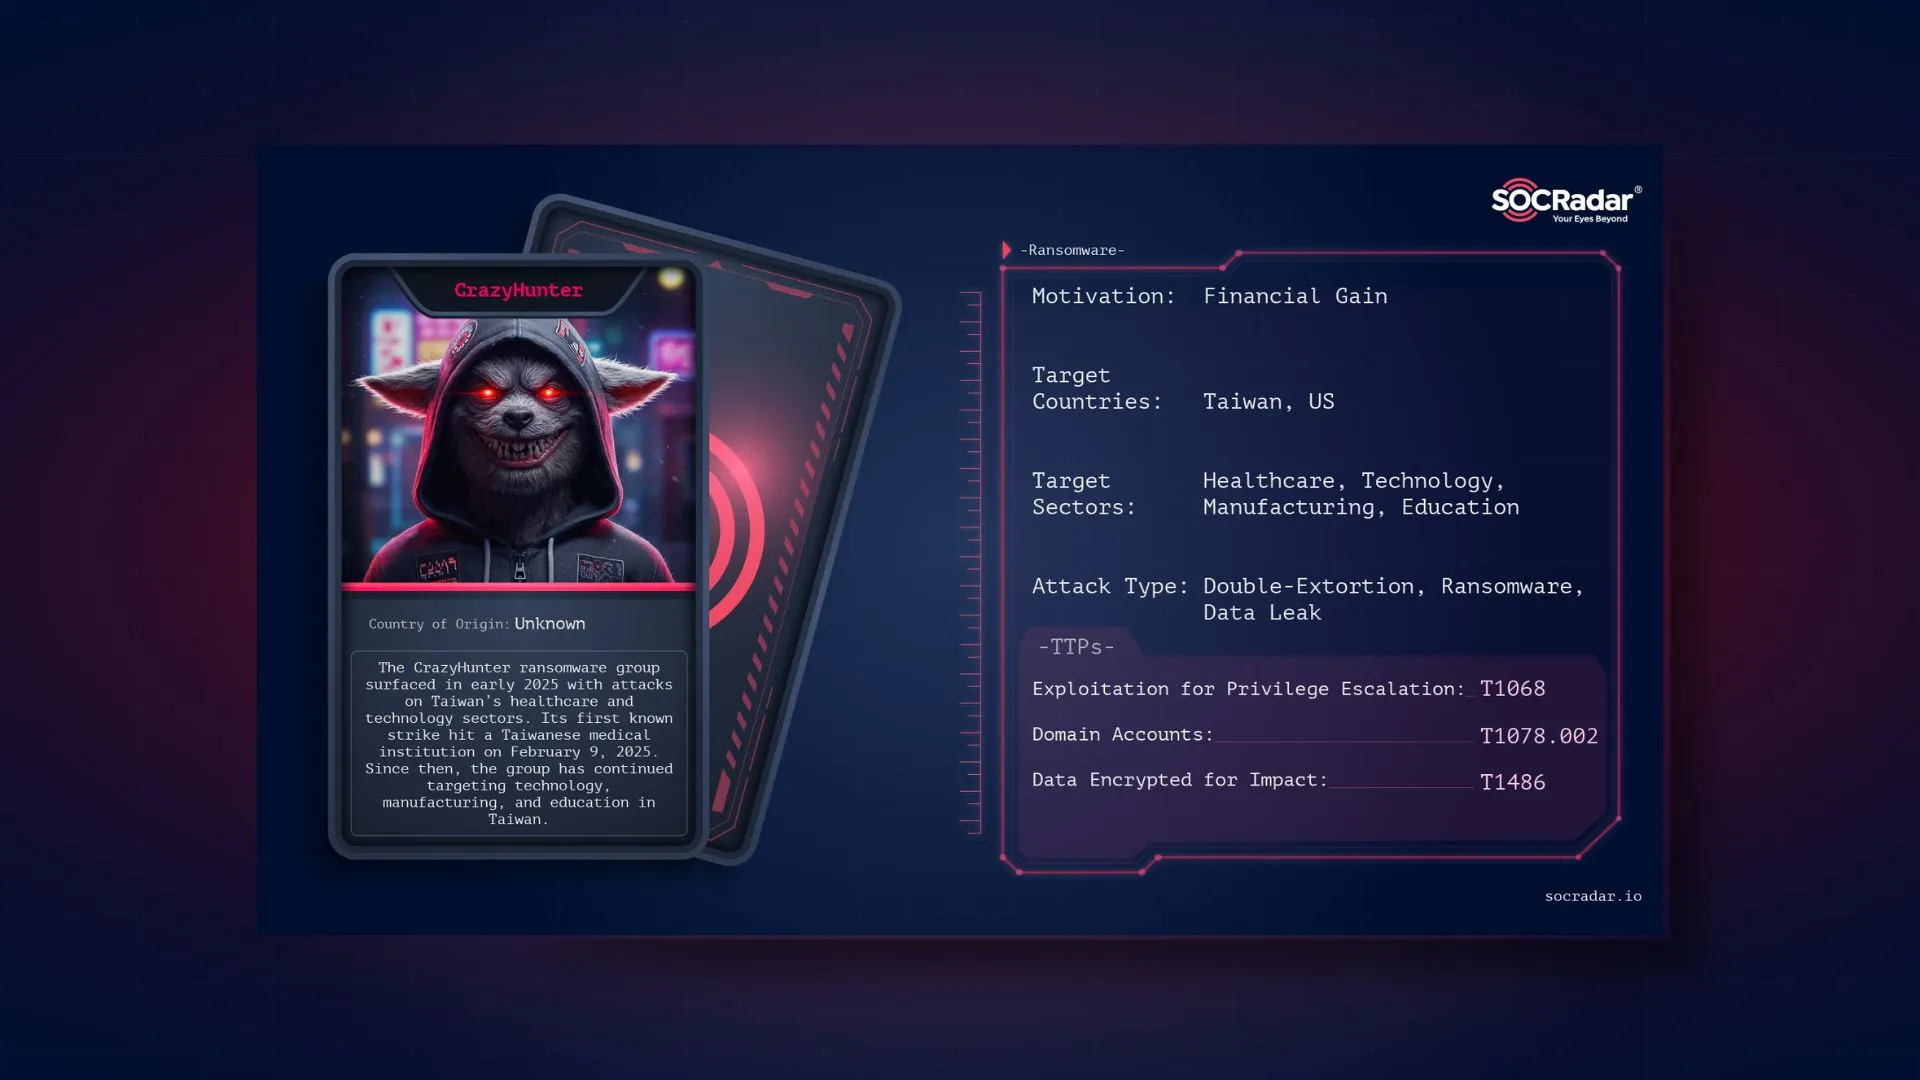
Dark Web Profile: CrazyHunter Ransomware
On February 9, 2025, Taiwan MacKay Memorial Hospital suffered a major ransomware attack. It hit the emergency and outpatient systems at both the Taipei and Tamsui campuses. More than 500…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action