Latest articles
 SOCRadar
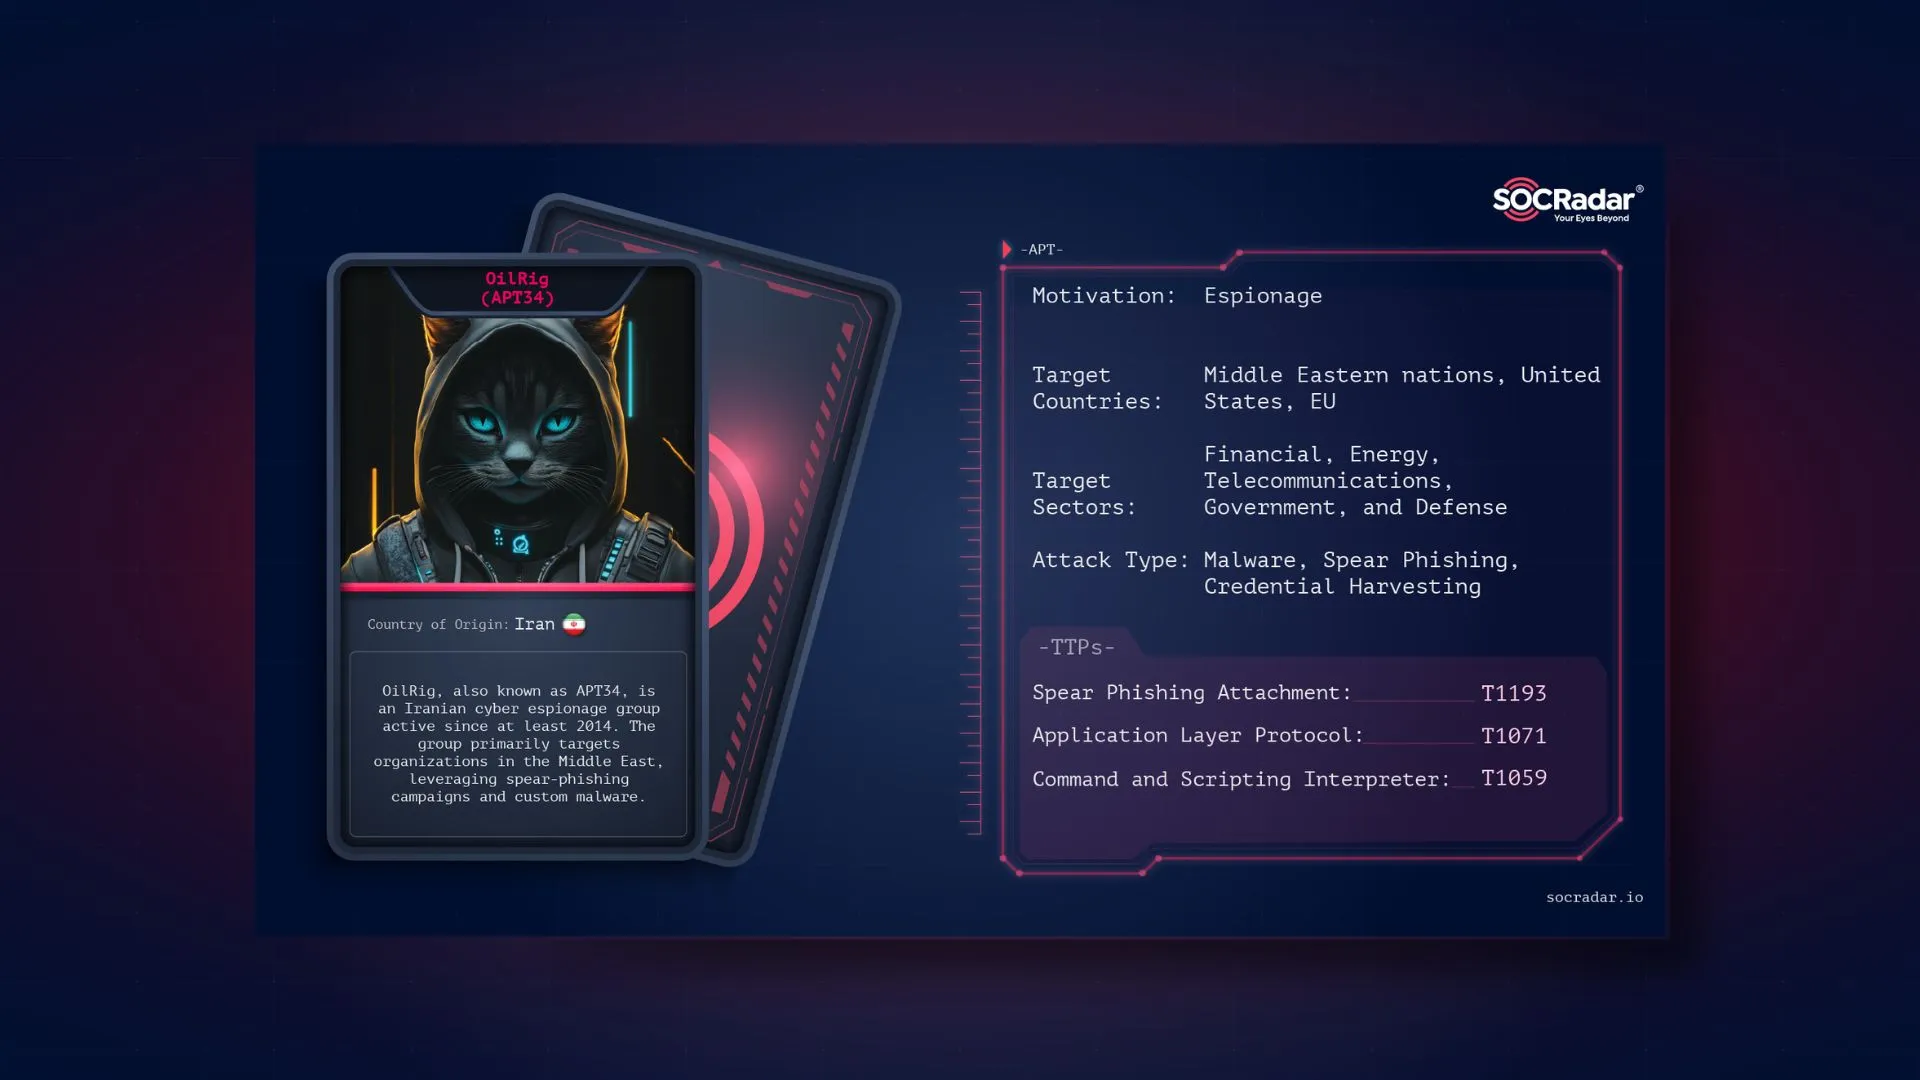
Dark Web Profile: OilRig (APT34)
OilRig, also known as APT34, is a state-sponsored Advanced Persistent Threat (APT) group with strong ties to Iranian intelligence. Known for its sophisticated cyber-espionage campaigns, OilRig primarily targets government, energy,…
 SOCRadar
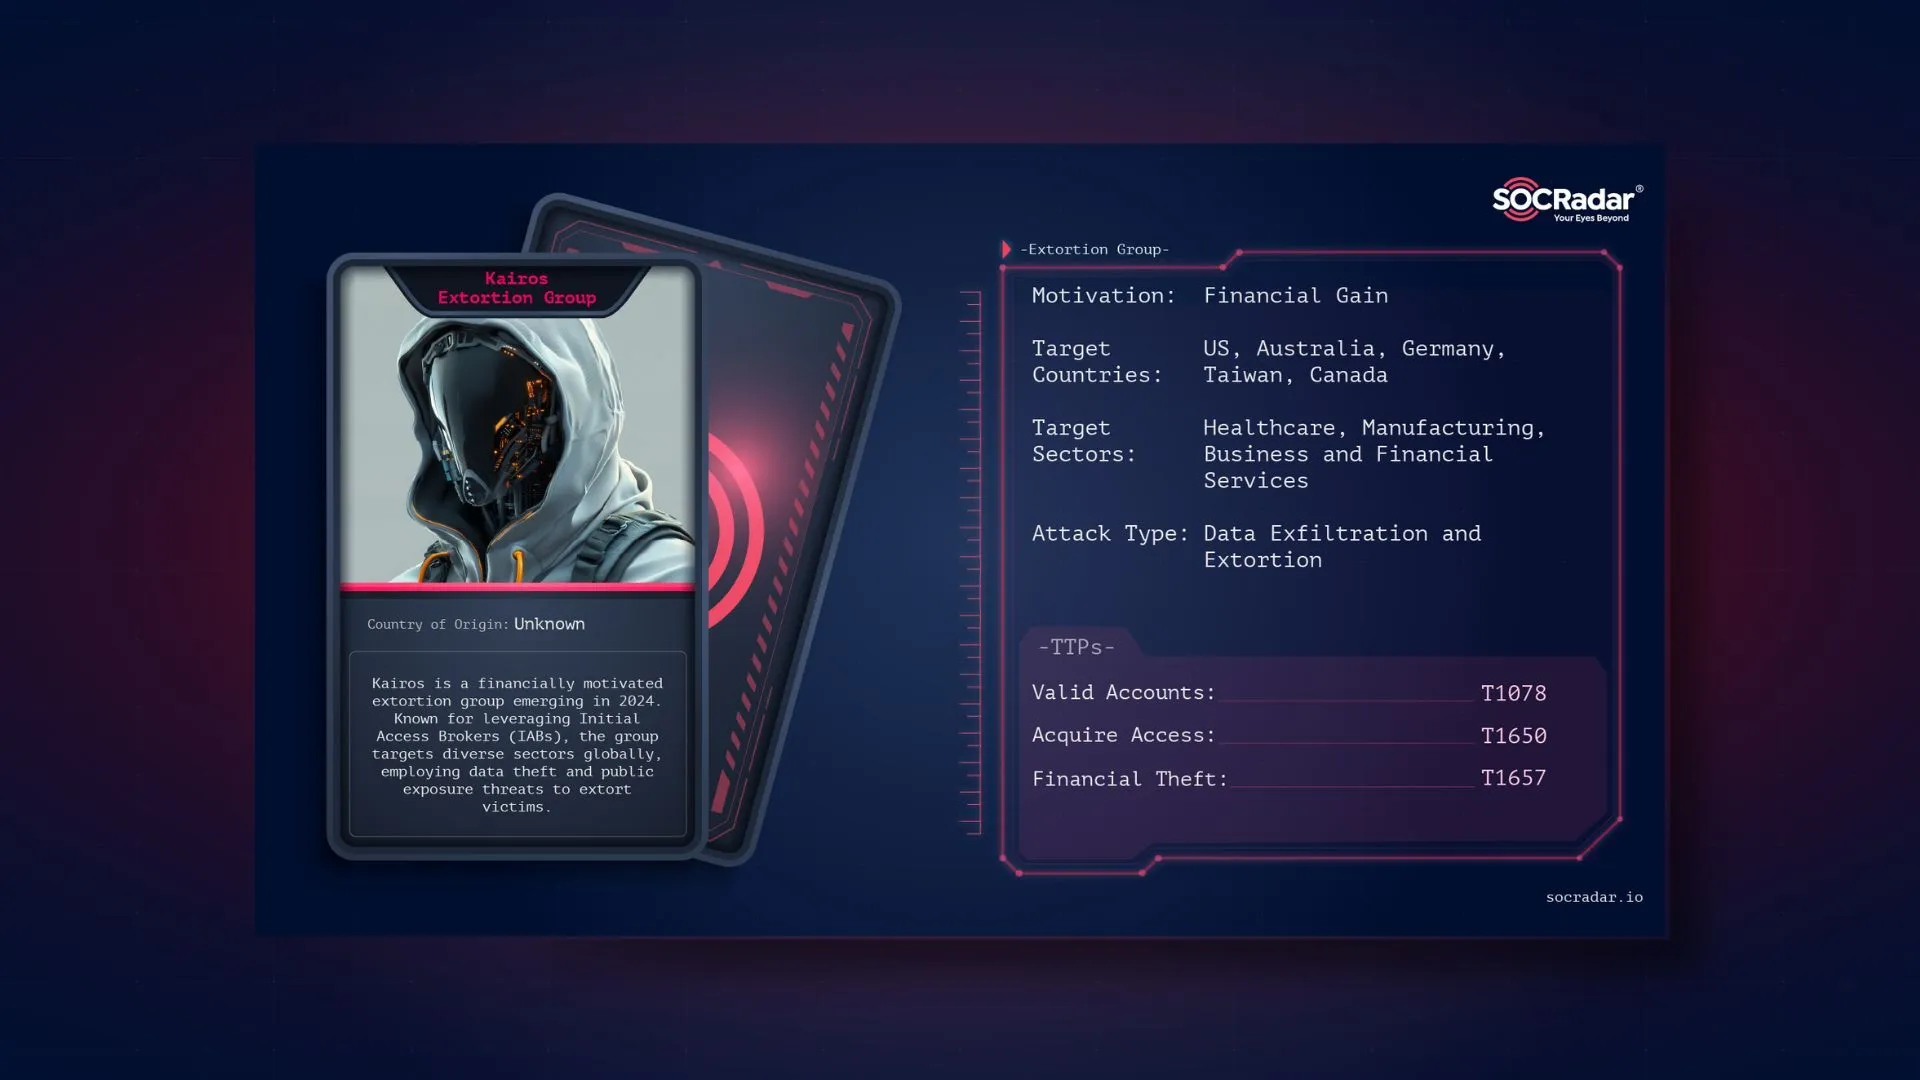
Dark Web Profile: Kairos Extortion Group
Kairos is a low-profile but rising cyber extortion group that has been active since late 2024. Unlike many of its counterparts, Kairos does not rely on ransomware in its attacks…
 SOCRadar
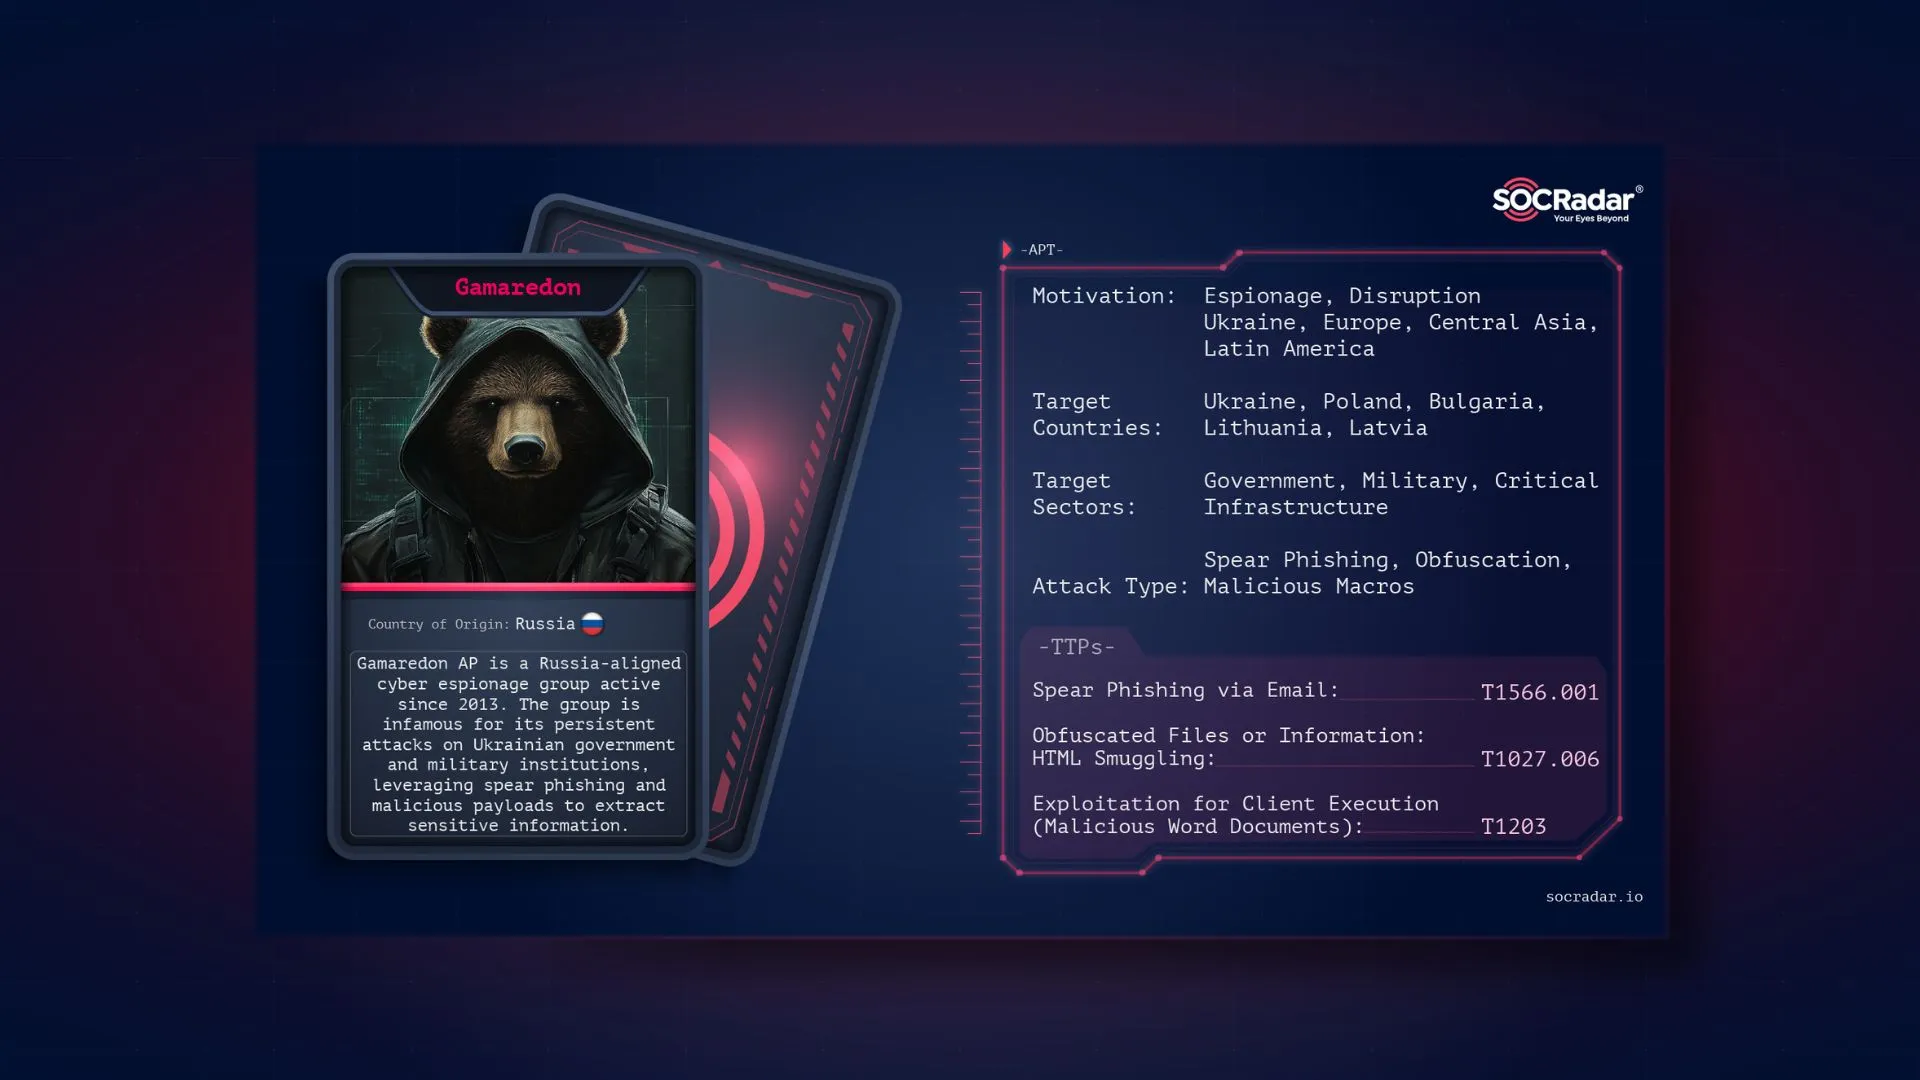
Dark Web Profile: Gamaredon APT
Gamaredon APT is a notorious Russian cyber espionage group active since 2013. Closely linked to Moscow’s Federal Security Service (FSB), it has primarily targeted Ukraine‘s government, military, and critical infrastructure sectors.…
 SOCRadar
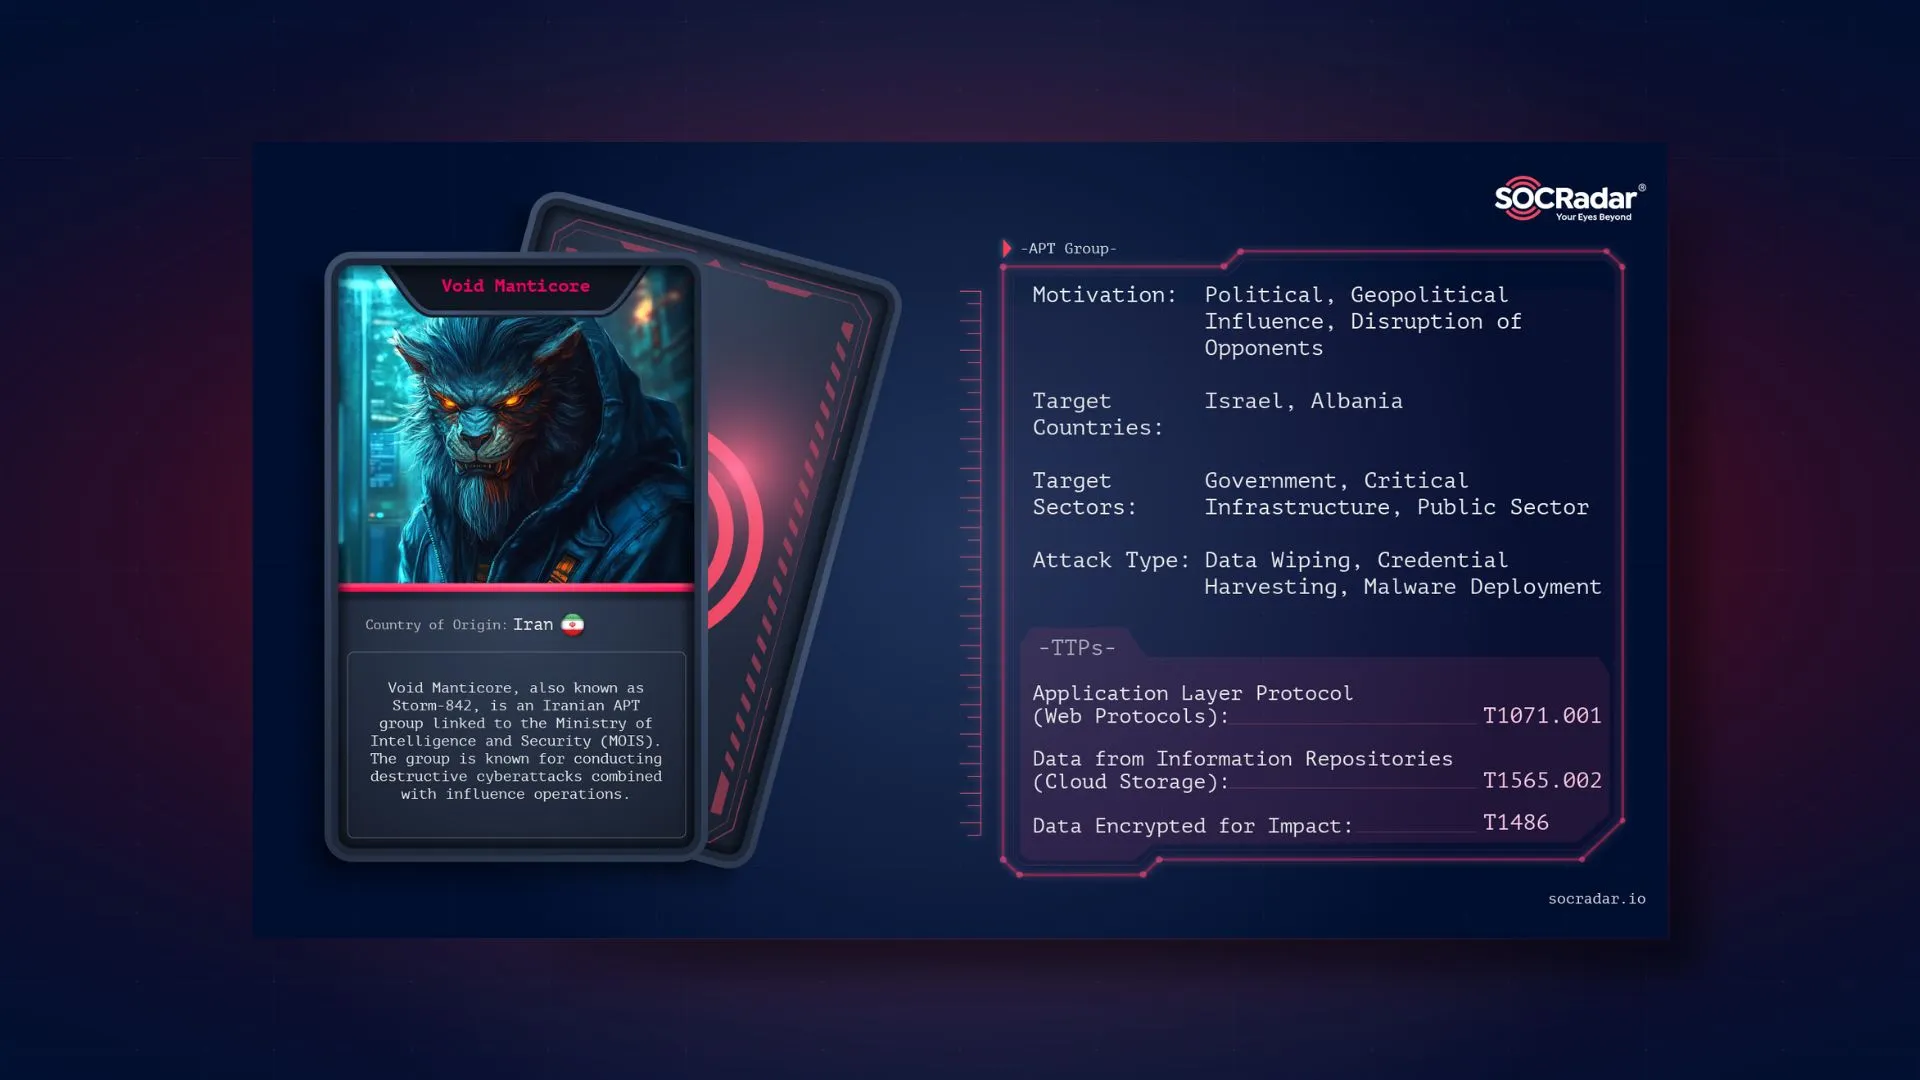
Dark Web Profile: Storm-842 (Void Manticore)
On September 23, 2022, the Federal Bureau of Investigation (FBI) and the Cybersecurity and Infrastructure Security Agency (CISA) released a joint advisory addressing a series of cyberattacks against Albania’s government.…
 SOCRadar
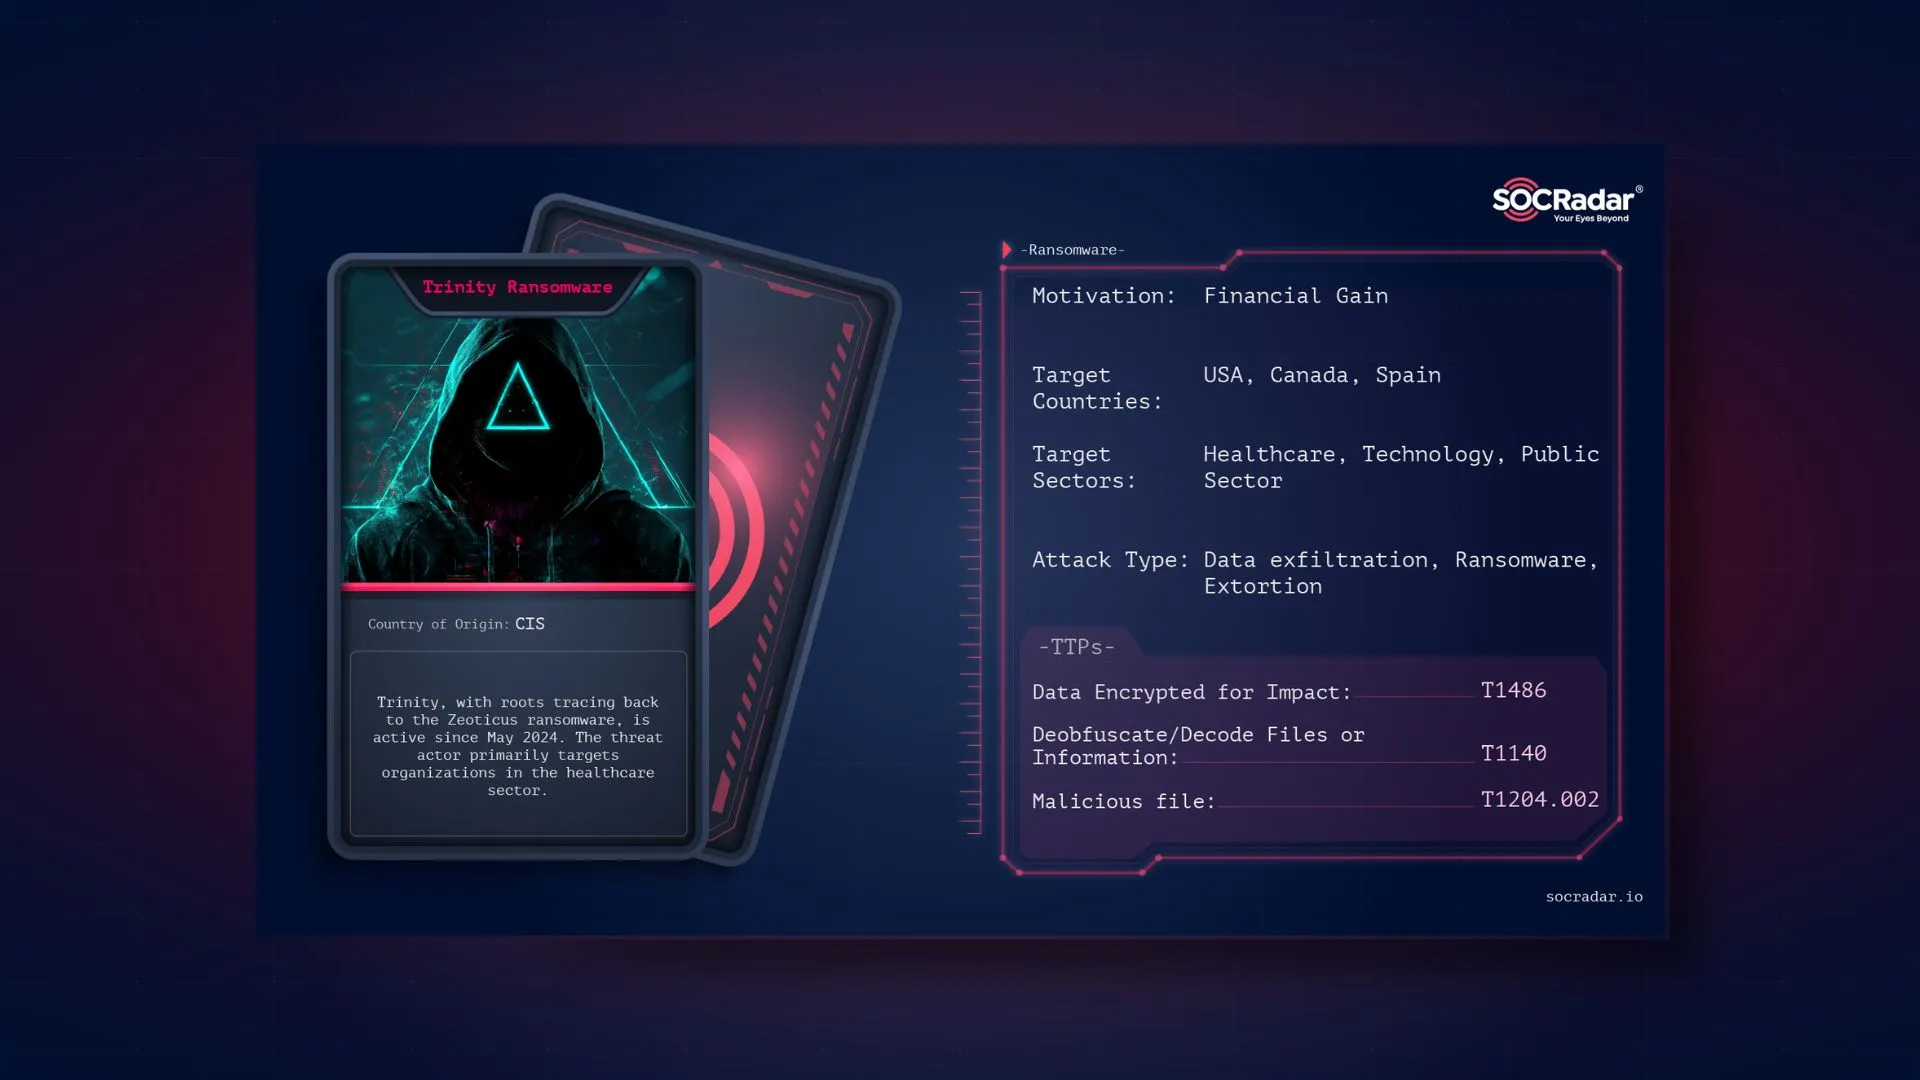
Dark Web Profile: Trinity Ransomware
First discovered in May 2024, the Trinity ransomware has quickly positioned itself as a significant actor in the threat landscape. Leveraging a double extortion tactic, it not only encrypts victims’…
 SOCRadar
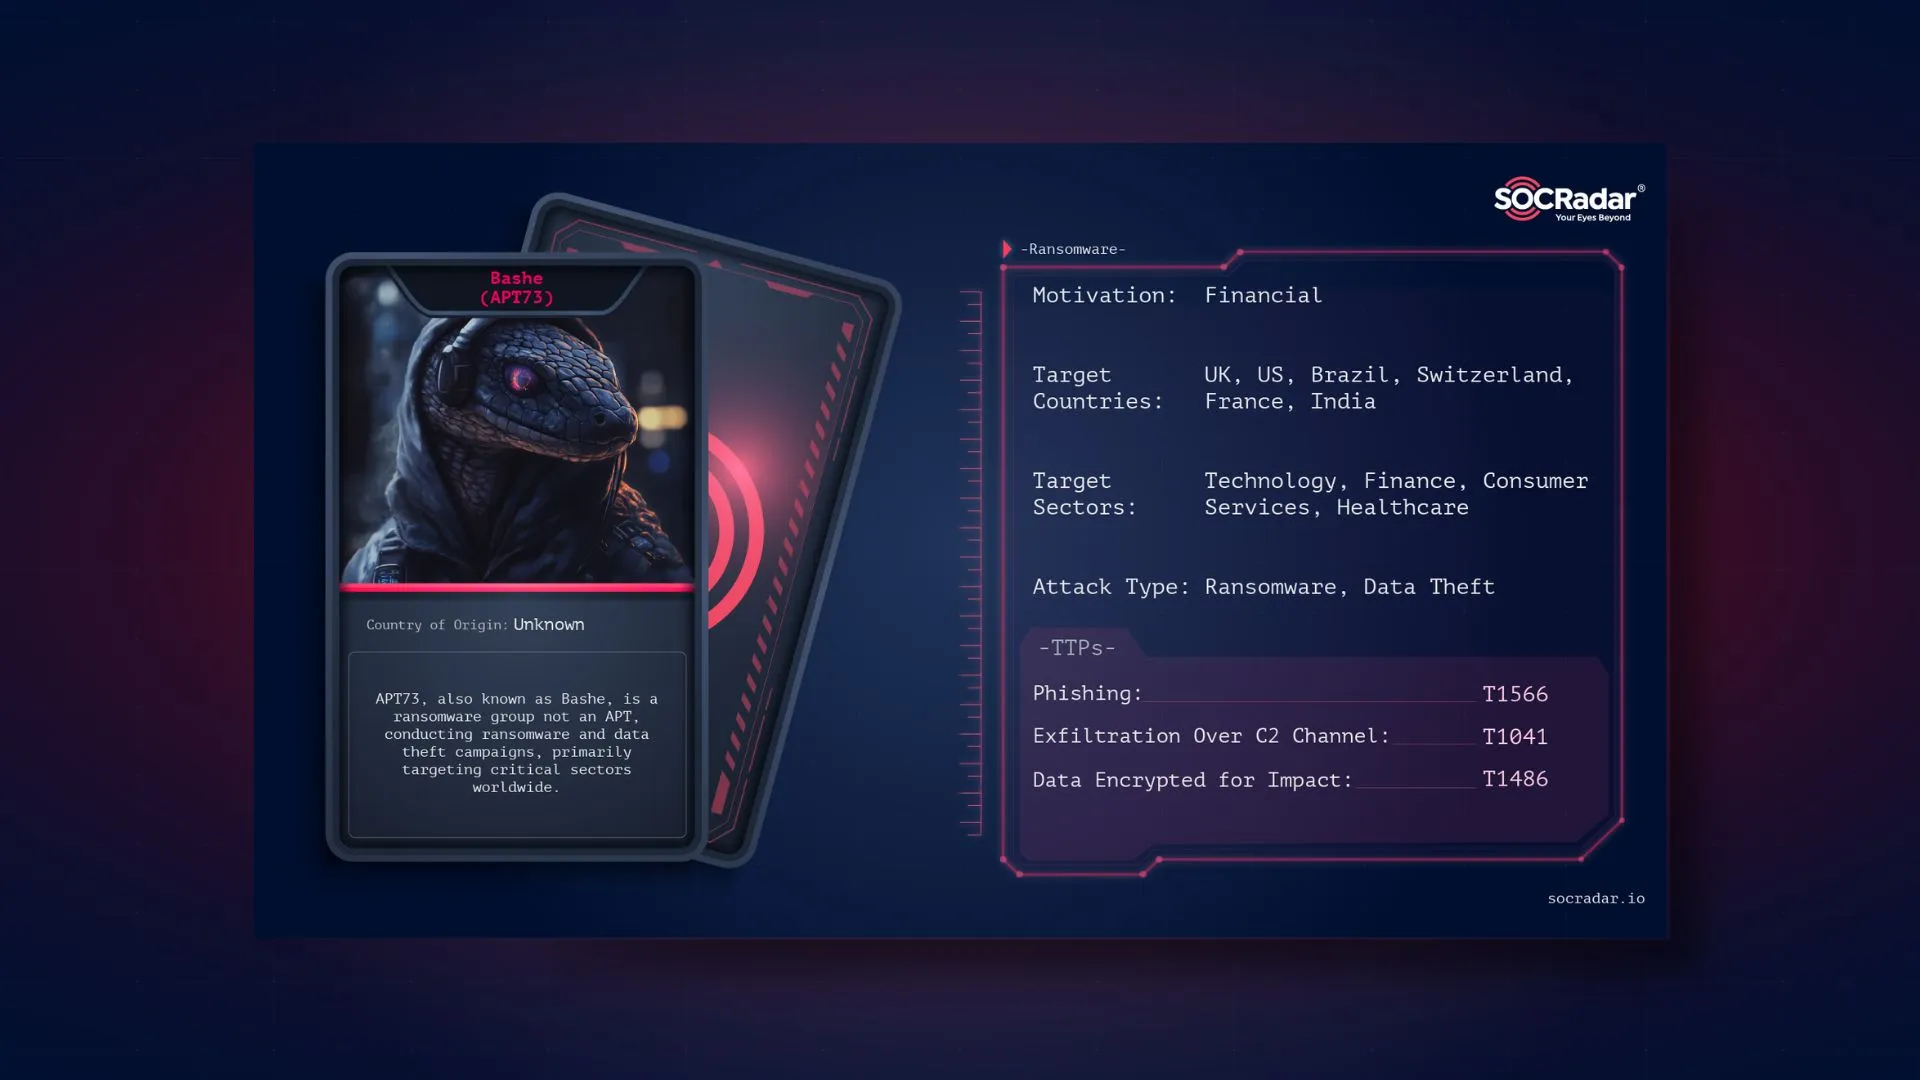
Dark Web Profile: Bashe (APT73)
Bashe, previously known as APT73 or Eraleig, is a ransomware group that emerged in 2024, employing tactics reminiscent of LockBit to target critical industries across developed nations. Operating through a…
 SOCRadar
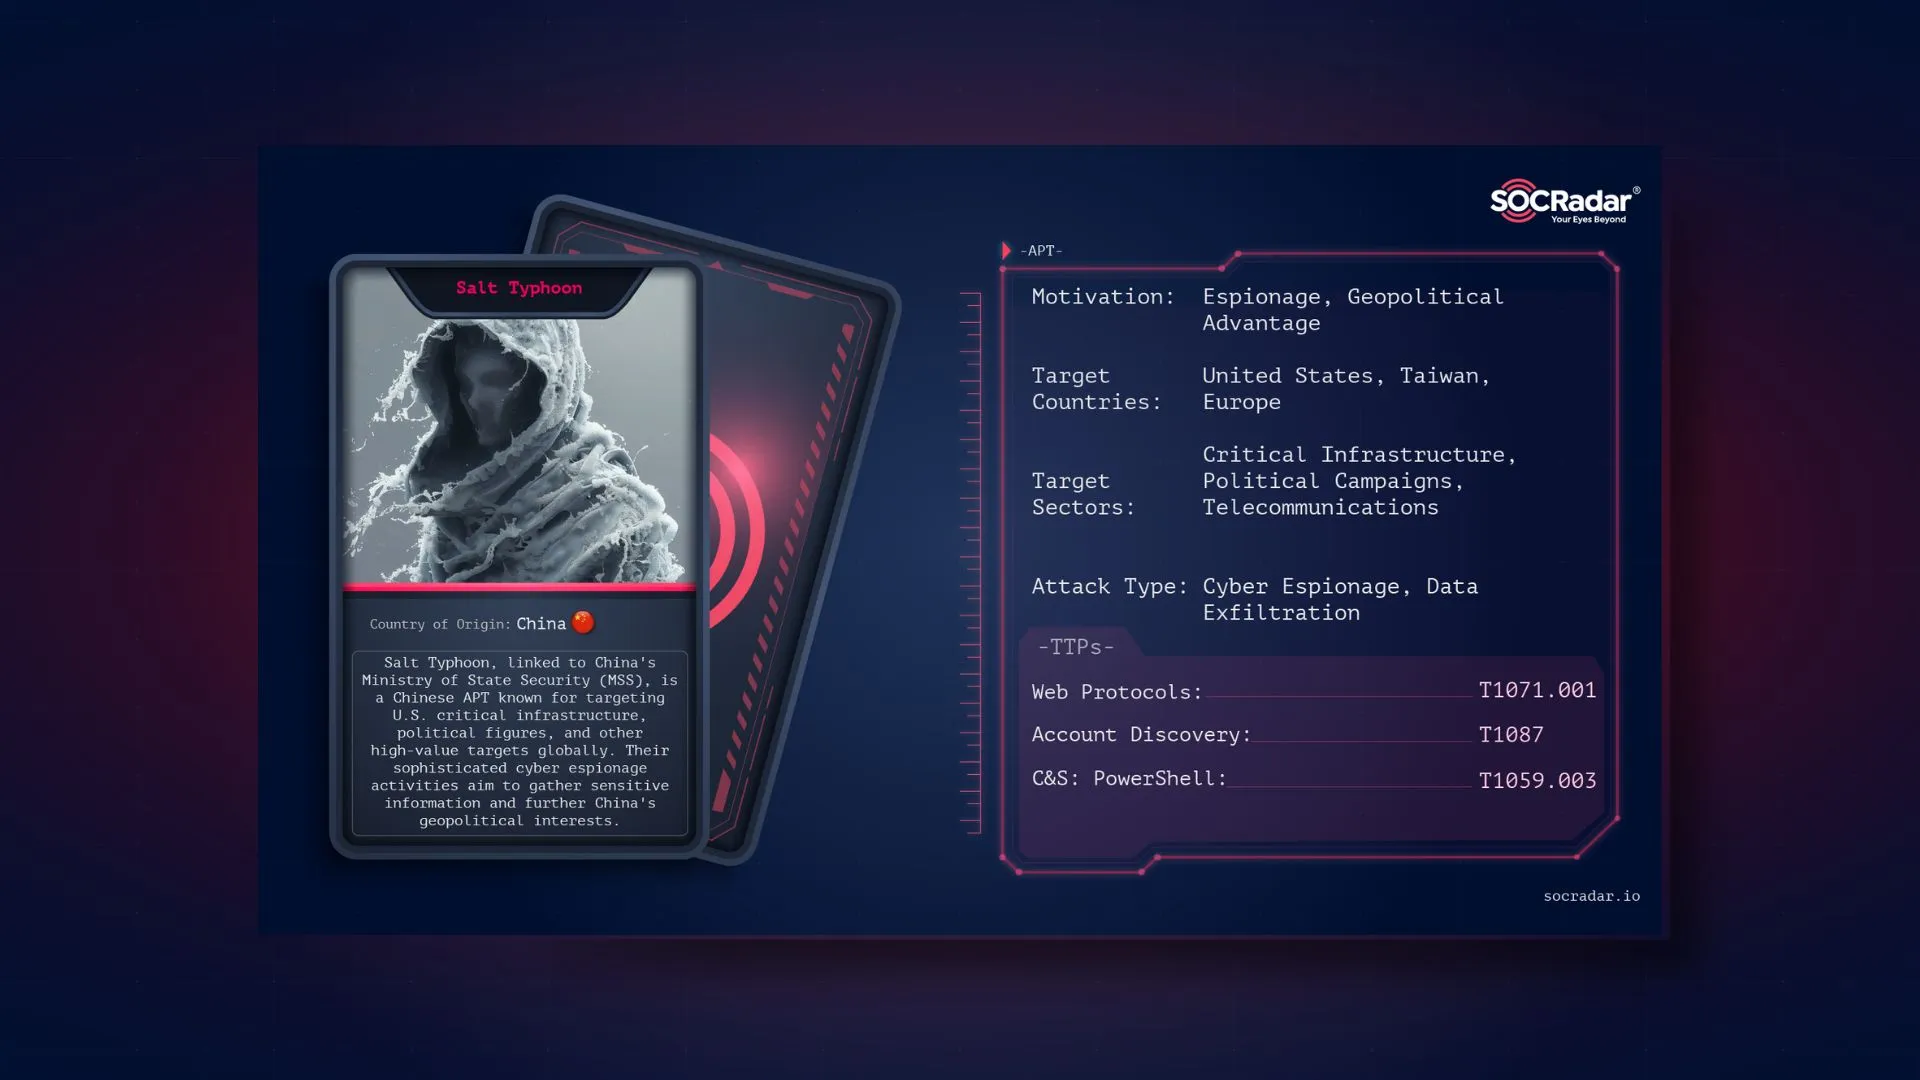
Dark Web Profile: Salt Typhoon
[Update] February 15, 2025: “Salt Typhoon Exploited Cisco Router Flaws and Breached Telecoms” Salt Typhoon, a Chinese state-sponsored Advanced Persistent Threat (APT), has been a formidable force in cyber espionage…
 SOCRadar
Dark Web Profile: Ymir Ransomware
The emergence of Ymir ransomware adds a new layer to the cybersecurity landscape, featuring advanced tactics that challenge traditional security defenses. Originating from stealer malware as its initial access vector,…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action