Finaxis, WoWInstaller, Moodle, MyHairCare & HT Médica Leaks
SOCRadar Dark Web Team identified several underground posts, including an alleged Finaxis.cloud data sale involving 400GB of information, a resurfaced WoWInstaller database containing historical user credentials, and an alleged Argentine Moodle platform data leak. Other posts advertised an alleged MyHairCare Australia customer database and an alleged HT Médica database containing 2.2 million records.
Alleged Finaxis.cloud Data Breach is Advertised
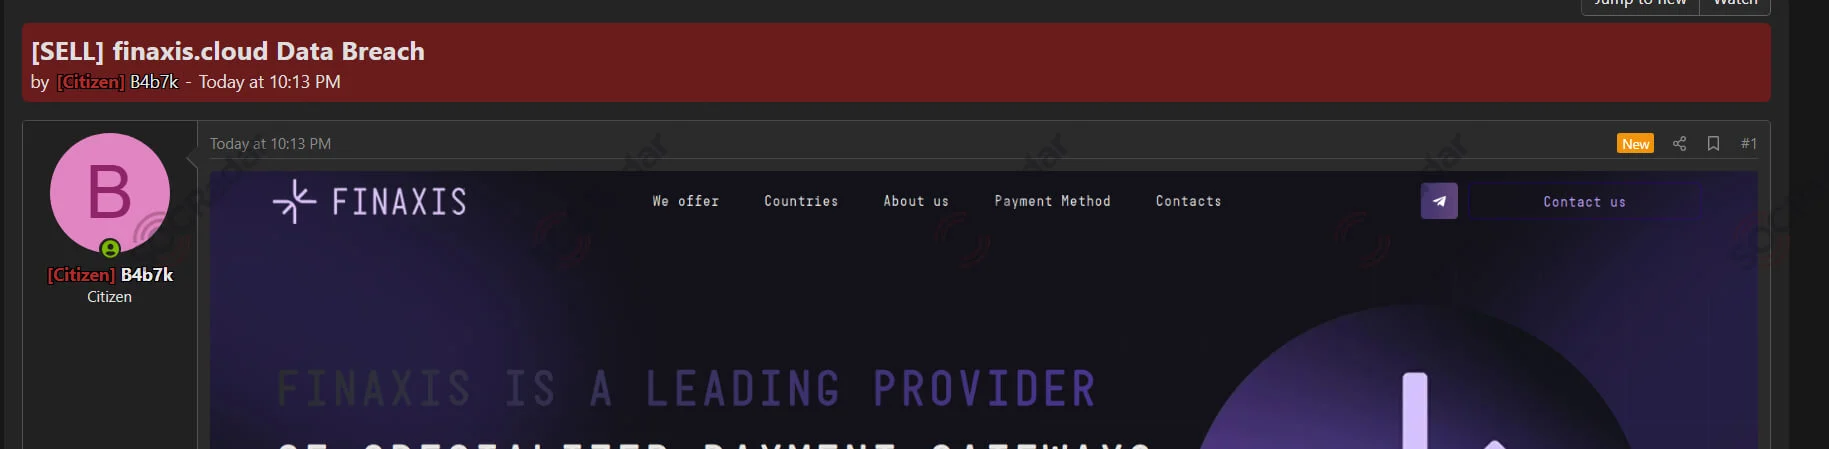
SOCRadar Dark Web Team detected a post advertising an alleged 400GB data breach involving Finaxis.cloud, a payment processing platform serving high-risk industries, including iGaming. The threat actor claimed to have obtained sensitive internal information after the company’s management allegedly refused to meet ransom demands.
The advertised data reportedly includes full source code, merchant and partner lists, P2P agent and trader contact information, financial statements, and banking details. The seller offered individual components for purchase or the complete dataset for $15,000. If authentic, the exposure could facilitate financial fraud, targeted attacks against business partners, and further exploitation of the platform’s infrastructure.
Alleged WoWInstaller Database Leak Resurfaces
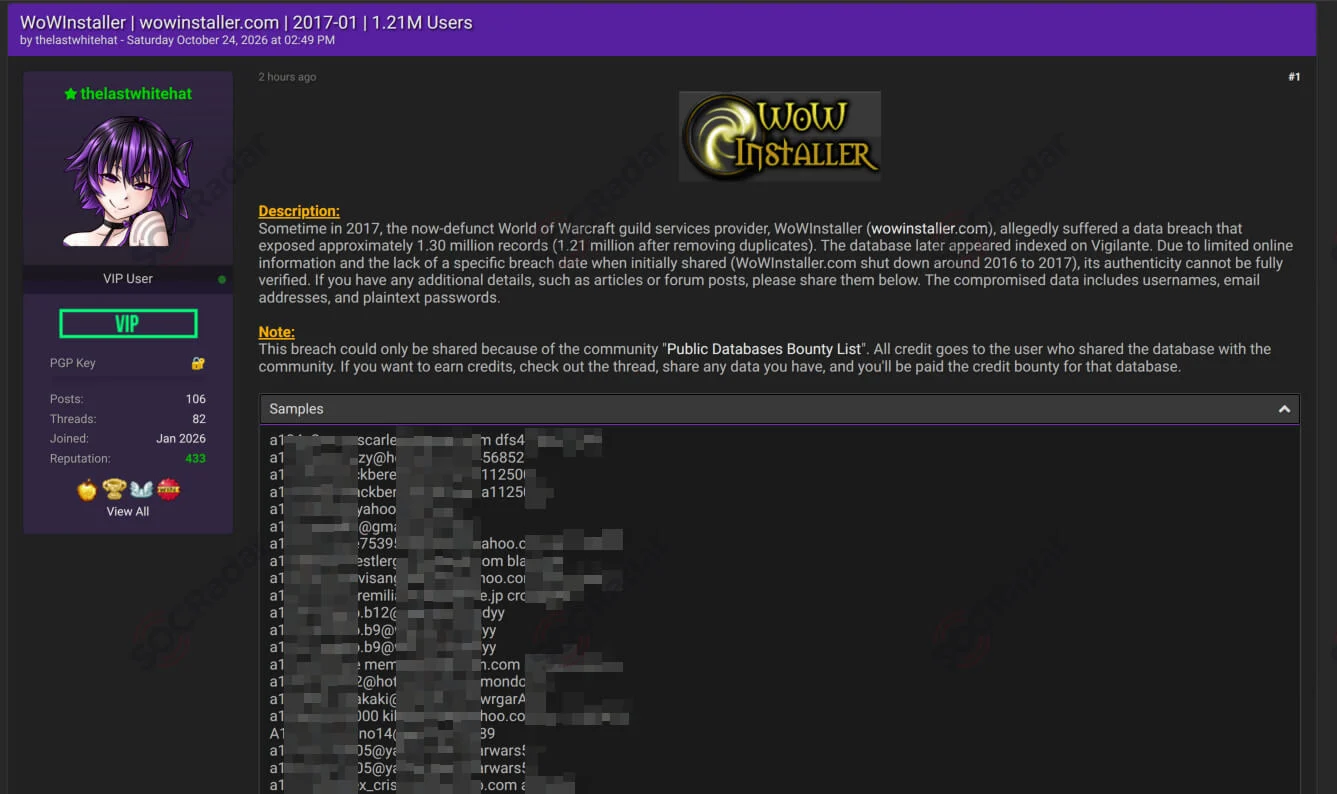
SOCRadar Dark Web Team identified a forum post sharing an alleged historical database belonging to WoWInstaller, a now-defunct World of Warcraft guild services provider. The seller claimed the database originated from a breach dating back to approximately 2017 and contained around 1.21 million records after duplicate entries were removed.
The dataset reportedly includes usernames, email addresses, and plaintext passwords. Although the service is no longer operational, the circulation of historical credentials could expose former users to credential stuffing and account takeover attempts if they reused the same passwords across other services. The authenticity of the database remains unverified.
Alleged Argentine Moodle Data Leak is Detected
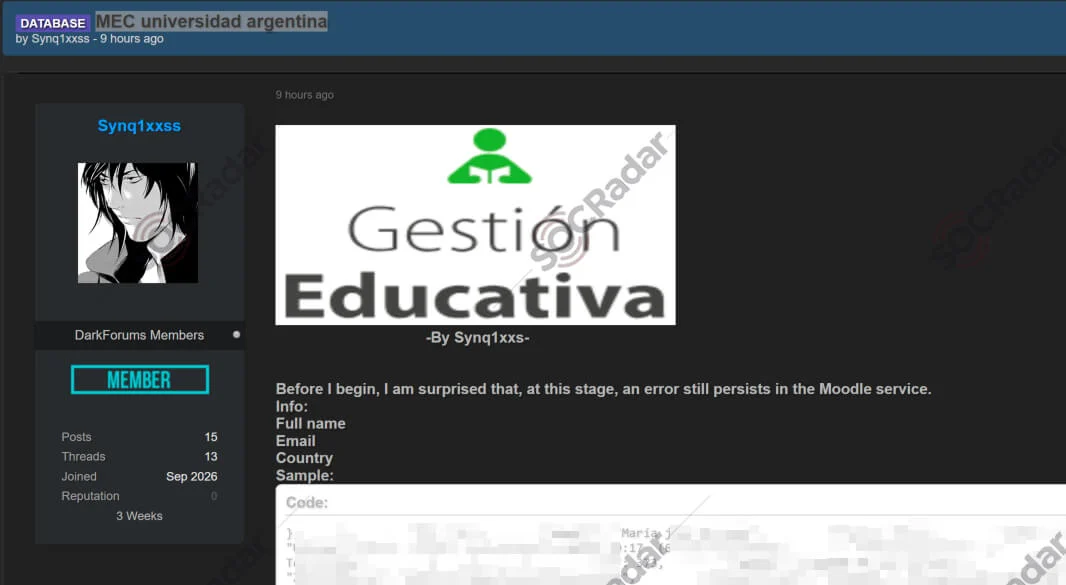
SOCRadar Dark Web Team detected a post claiming to expose user information from an Argentine educational platform using Moodle. The actor, operating under the alias Synq1xxs, shared sample records allegedly associated with an educational management system identified as MEC and claimed that a persistent issue within the Moodle service had enabled the exposure.
The advertised information reportedly includes full names, email addresses, country information, time zone settings, and course enrollment details. Some records allegedly contain recent login activity, suggesting the dataset may include current users. If verified, the exposure could support phishing, impersonation, and social engineering attacks targeting students and educational personnel. The platform’s precise institutional affiliation remains unconfirmed.
Alleged MyHairCare Australia Database Sale is Detected
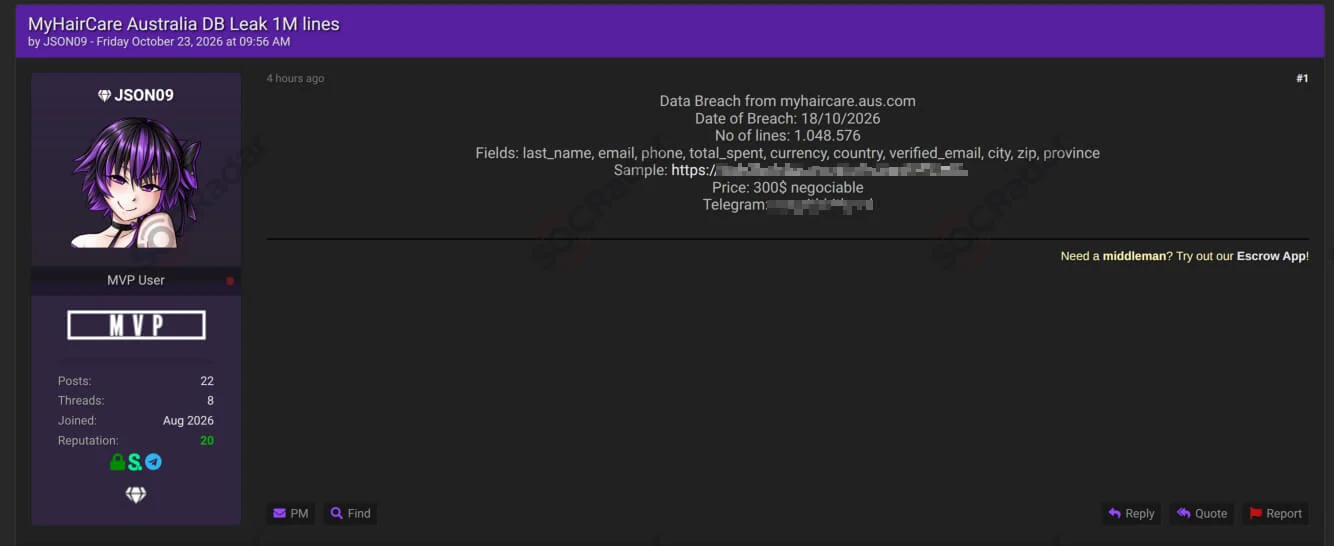
SOCRadar Dark Web Team identified a dark web post advertising an alleged database belonging to MyHairCare Australia, an Australian beauty and haircare retailer. The seller, identified as JSON09, claimed the dataset contained 1,048,576 records obtained during an incident dated October 18, 2026.
The advertised data reportedly includes customer last names, email addresses, phone numbers, total spending amounts, currency information, and geographic details, including cities, postal codes, and provinces. The dataset was offered for $300, with a sample link provided by the seller. If authentic, the information could facilitate targeted phishing, customer impersonation, and fraudulent communications using purchase-related details.
Alleged HT Médica Database Sale is Detected
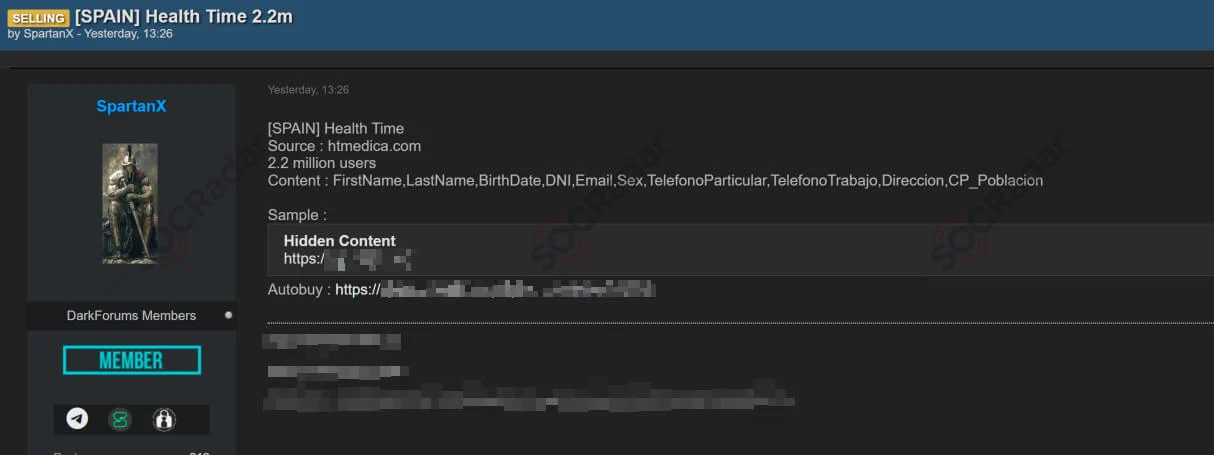
SOCRadar Dark Web Team detected a post advertising an alleged 2.2 million-record database associated with HT Médica, a Spanish healthcare provider specializing in diagnostic imaging. The seller, operating under the alias SpartanX, claimed to possess personal information associated with the organization and provided a sample link to support the listing.
The advertised dataset reportedly contains first and last names, dates of birth, DNI identification numbers, email addresses, gender information, personal and work phone numbers, and physical addresses. If authentic, the exposure could create significant privacy risks and facilitate identity theft, phishing, and targeted fraud against affected individuals. The breach remains unverified, and the listing does not establish that clinical records were compromised.
Powered by DarkMirror™
Gaining visibility into deep and dark web threats can be extremely useful from an actionable threat intelligence and digital risk protection perspective. However, monitoring all sources is simply not feasible, which can be time-consuming and challenging. One click-by-mistake can result in malware bot infection. To tackle these challenges, SOCRadar’s DarkMirror™ screen empowers your SOC team to follow up with the latest posts of threat actors and groups filtered by the targeted country or industry.