




Mar 10, 2026
Sep 11, 2026
8 Mins Read
Table Of Content
Key Takeaways
How Agentic Threat Intelligence Differs from Traditional Approaches
Real-World Use Cases of Agentic Threat Intelligence
What Technologies Are Behind Agentic Threat Intelligence?
What Are Risks and Challenges?
Frequently Asked Questions
The Road Ahead for Agentic AI in Threat Intelligence
Related Articles

SMS Bombing

Threat Actors
Jan 08, 2026

Dark Web Monitoring
Feb 19, 2026

Dark Web
Jan 31, 2026

Ransomware
Jan 31, 2026

What Is Agentic Threat Intelligence (ATI)?
Agentic Threat Intelligence (ATI) is threat intelligence carried out by autonomous AI agents that pursue a goal rather than follow a fixed playbook. An ATI agent decides which sources to query, correlates what it finds, scores the risk, and then recommends or triggers a response, without being walked through each step.
Cyber threats are advancing faster than many traditional defenses can handle. While automation and AI have helped teams scale their security operations, most threat intelligence platforms still rely on fixed rules and static workflows. These approaches often fall short when faced with novel attacks, zero-day exploits, or adaptive threat actors. What is needed is more than speed. It is intelligence that can adapt, reason, and act.
Powered by Agentic AI, ATI systems correlate Indicators of Compromise (IOCs), contextualize threat data, and even recommend or initiate mitigation steps. They monitor, analyze, and adapt to emerging threats as conditions change.
Key Takeaways
- Agentic Threat Intelligence (ATI) is threat intelligence executed by autonomous AI agents that plan their own steps instead of following fixed rules.
- Four traits separate an agent from an automation script: autonomy, memory, goal-directed reasoning, and environmental awareness.
- Traditional CTI is reactive and rule-bound. ATI is adaptive, and it decides which tools to use, what to prioritize, and when to escalate.
- The enabling technologies are large language models, memory and feedback systems, and workflow orchestration.
- Autonomy carries its own risks, so guardrails, audit logs, and explainable decision paths are prerequisites rather than extras.
How Agentic Threat Intelligence Differs from Traditional Approaches
Most traditional threat intelligence platforms are reactive. They rely on static rules, pulling from known feeds and triggering alerts when patterns match. While effective for known threats, these systems struggle to adapt when facing novel attacks, ambiguous indicators, or evolving infrastructure.
Agentic Threat Intelligence (ATI) introduces a new model. One that is built on autonomous agents that do not just process information, but actively interpret, learn, and act.
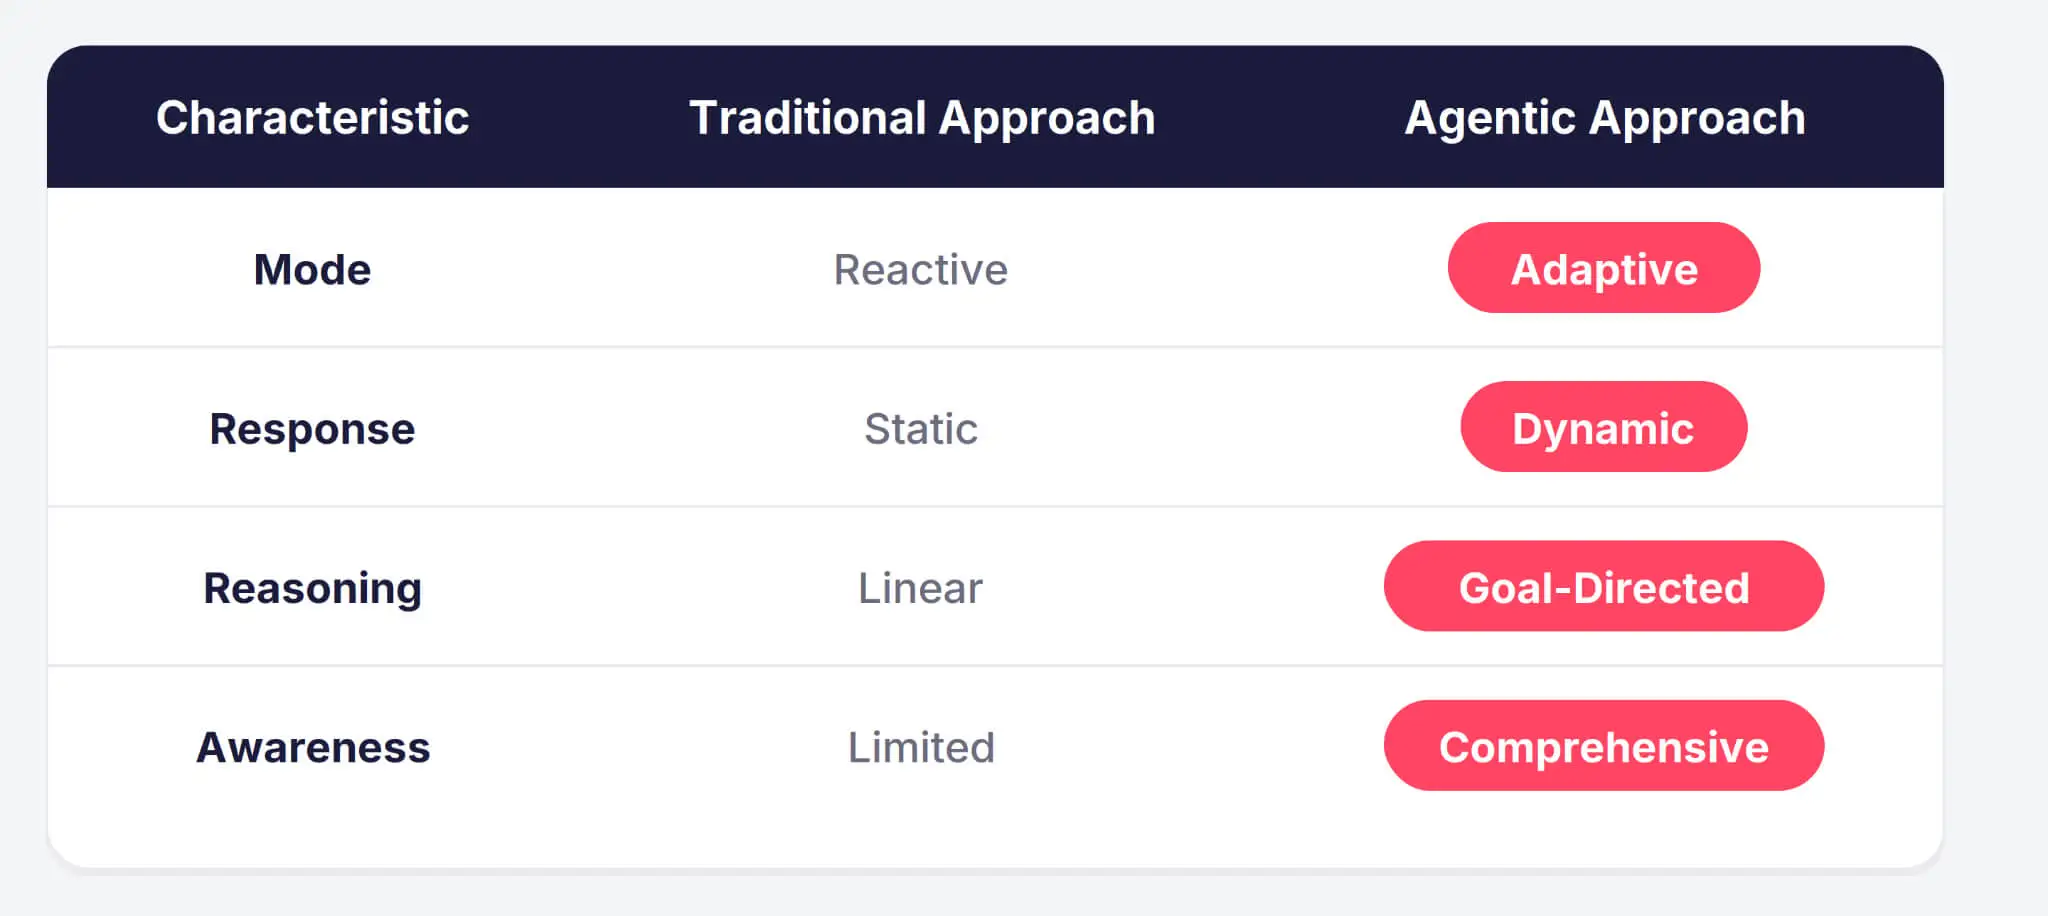
Agentic Threat Intelligence compared with traditional threat intelligence.
Core Capabilities of Agentic Threat Intelligence
- Autonomy: Agents operate independently, responding in real time without waiting for human direction.
- Memory and Learning: They retain context across interactions and refine their behavior over time.
- Goal-Directed Reasoning: ATI agents don’t just react; they pursue specific outcomes – like identifying emerging attacker infrastructure or prioritizing high-risk IOCs.
- Environmental Awareness: Systems adapt based on threat activity, context shifts, and infrastructure changes.
This marks a shift away from rigid automation. Instead of following linear playbooks (e.g., If X, then Y), ATI systems evaluate live conditions and decide what actions to take, as well as which tools to use, what to prioritize, and when to escalate.
For example, rather than just logging a suspicious domain:
- An agent may assess its registration data
- Cross-reference it with recent campaigns
- Score its risk level
- And suggest or trigger containment, without human prompting.
The result? A move from passive data collection to intelligent, adaptive threat interpretation, built to handle what static systems can’t.
Side by side, the two models diverge on four points:
| Characteristic | Traditional Approach | Agentic Approach |
|---|---|---|
| Mode | Reactive | Adaptive |
| Response | Static | Dynamic |
| Reasoning | Linear | Goal-Directed |
| Awareness | Limited | Comprehensive |
SOCRadar has already launched its Agentic Threat Intelligence (ATI), with agents that automate enrichment, correlate infrastructure, triage alerts, and generate ready-to-use reports – helping teams move faster and with better context.
Real-World Use Cases of Agentic Threat Intelligence
Agentic Threat Intelligence goes far beyond traditional CTI by embedding autonomous agents into core workflows. Key functional use cases include:
- Autonomous IOC Investigation & Correlation: ATI agents connect the dots between indicators across multiple sources (like threat intel feeds, malware sandboxes, and DNS logs), assigning confidence scores and reducing alert fatigue.
- End-to-End Threat Enrichment: Instead of relying on manual lookups, agents pull Whois data, passive DNS, threat actor TTPs, and campaign history to automatically create detailed threat profiles.
- Real-Time Alert Triage: False positives are dismissed with reasoning. Real threats are escalated with pre-built investigation packages, reducing analyst workload and response time.
- Proactive Threat Hunting: Agents scan for early signals (such as suspicious domain registrations, credential leaks, or C2 infrastructure changes) before the threat even targets your environment.
Here’s how organizations can put Agentic Threat Intelligence to work:
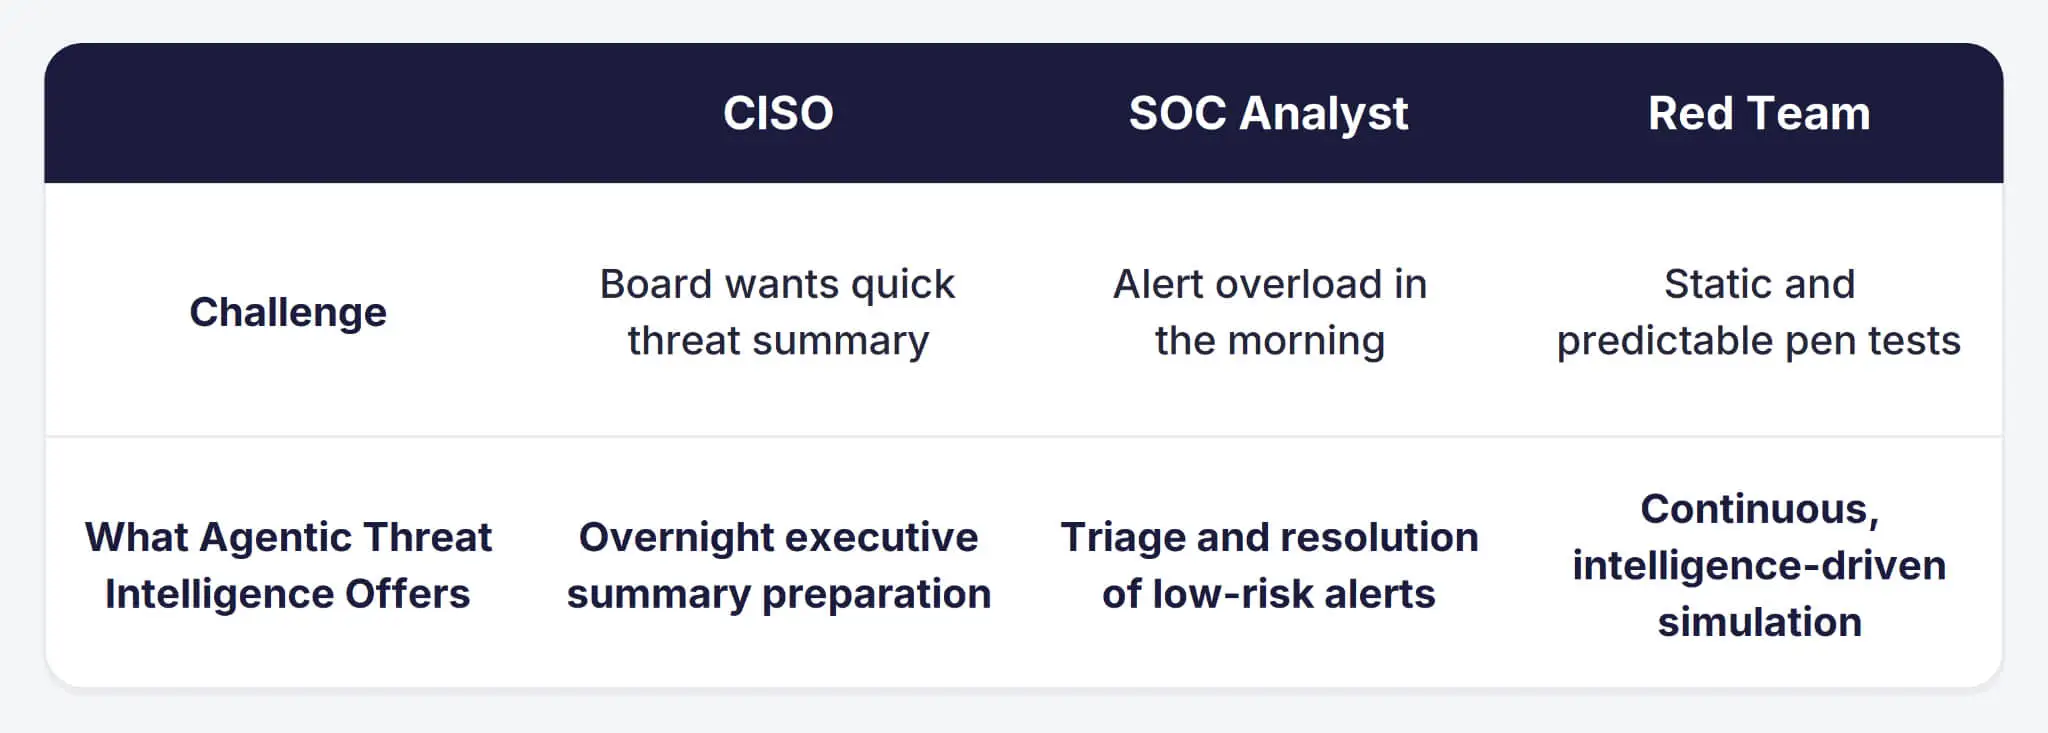
Example use cases of Agentic Threat Intelligence for CISOs, SOC analysts, and red teams.
CISO Perspective: Briefing Executives Without the Fire Drill
The challenge: The board wants a summary of top threats and business risk by 9 AM.
With ATI: Agents work overnight, analyzing sector-specific threats, mapping risk to assets, and preparing an executive summary complete with impact ratings and regulatory context. The CISO walks into the meeting with everything ready.
SOC Analyst Perspective: No More Morning Alert Overload
The challenge: 200+ alerts overnight, most of them noise.
With ATI: Agents triage, investigate, and resolve low-risk alerts before analysts log in. High-priority items arrive already enriched with related indicators, likely attack paths, and recommended actions, cutting hours off the response cycle.
Red Team Perspective: Continuous, Intelligence-Driven Simulation
The challenge: Traditional pen tests are too static and predictable.
With ATI: AI agents simulate evolving attacker behavior using current APT tactics. Simulations adapt to your environment, test defenses in real time, and report gaps dynamically, making red teaming a continuous validation process.
What Technologies Are Behind Agentic Threat Intelligence?
Agentic Threat Intelligence draws on several technologies to function effectively:
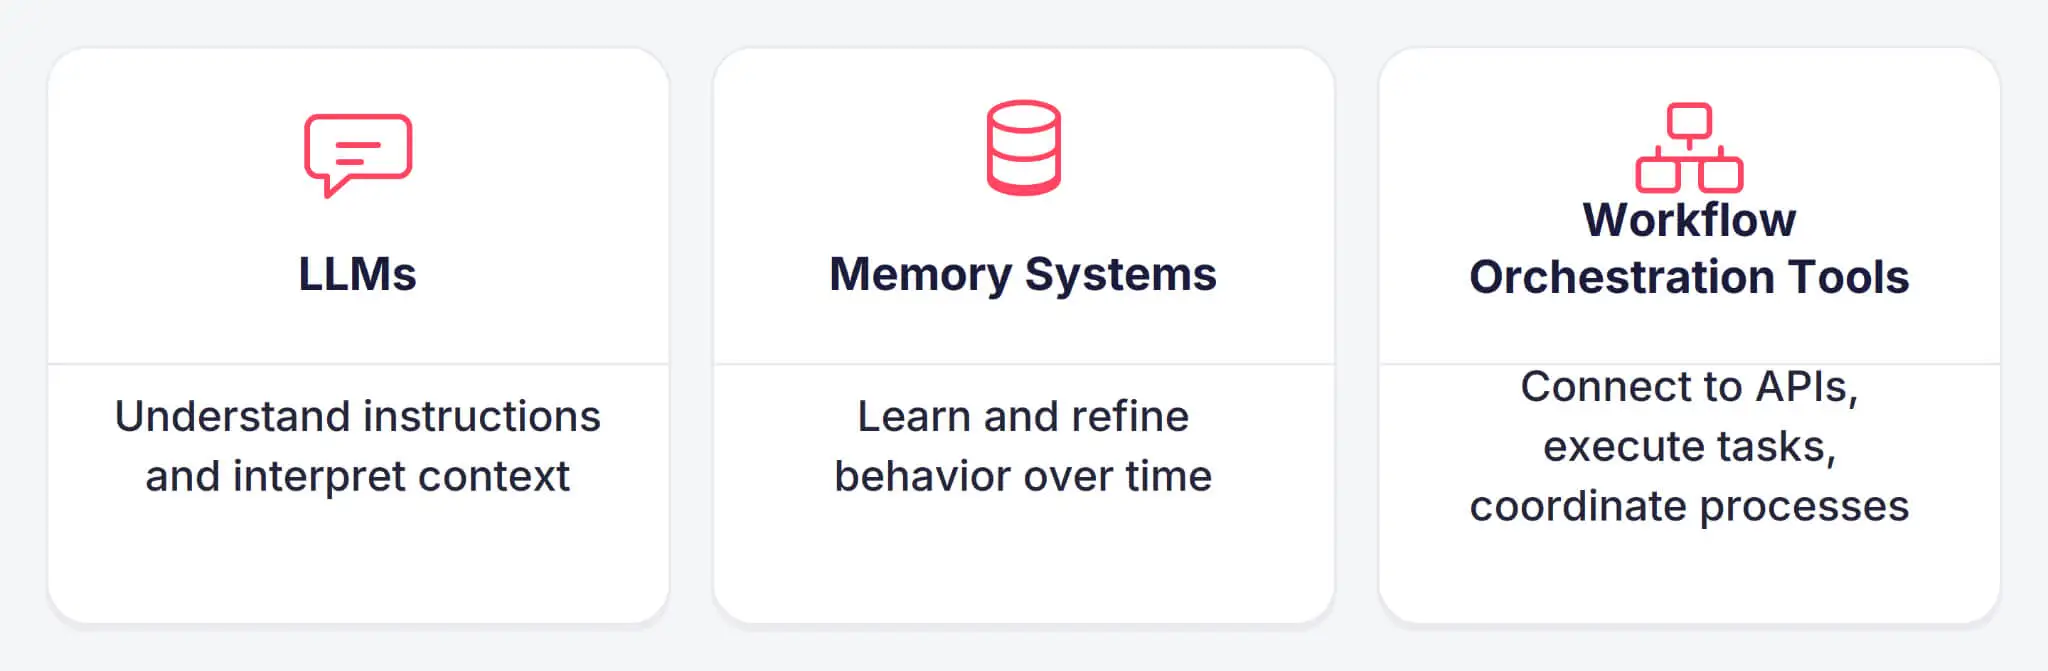
Technologies behind Agentic Threat Intelligence: LLMs, memory systems, and workflow orchestration tools.
- Large Language Models (LLMs) enable agents to understand unstructured input, interpret threat context, and communicate findings clearly. Their natural language understanding powers everything from log parsing to decision justification.
- Memory systems and feedback loops: agents retain context between tasks, remember previous decisions, and refine their actions over time. This ongoing learning allows ATI systems to improve correlation accuracy and avoid repeating irrelevant investigations.
- Workflow orchestration tools: agentic systems connect to external tools (threat intelligence feeds, sandbox environments, SIEMs, and more) through APIs. Orchestration frameworks allow them to combine actions into multi-step workflows without human instruction.
Together, these technologies enable ATI systems to function less like static tools and more like intelligent teammates. Multi-agent frameworks may soon enable fully digital security teams capable of end-to-end incident management.
What Are Risks and Challenges?
While Agentic Threat Intelligence brings speed and autonomy to cybersecurity operations, it also introduces new risks. Especially when these agents begin making independent decisions in high-stakes environments.
- Unpredictable Autonomy: Agentic systems act based on their interpretation of data, which may be incomplete or flawed. Without proper design and constraints, an agent might block legitimate activity, mishandle sensitive data, or escalate minor issues, creating new vulnerabilities rather than solving them.
- Reasoning Errors and Execution Risks: Ambiguous prompts, unexpected inputs, or unfamiliar scenarios can cause agents to behave unpredictably. In security environments, even a single bad decision, like misidentifying a threat or executing the wrong workflow, can have significant operational impact.
- The Need for Guardrails and Oversight: Implementing clear limits on what agents can do is essential. Organizations should monitor agent behavior, include safeguards for high-risk actions, and ensure traceability. Audit logs and explainable decision paths help maintain accountability and support compliance.
Agentic AI must be introduced into your cybersecurity environment with a thoughtful approach. With the right controls in place, it can enhance security operations without sacrificing safety or trust.
Frequently Asked Questions
Q: What is Agentic Threat Intelligence (ATI)?
A: Agentic Threat Intelligence is threat intelligence performed by autonomous AI agents that take a goal, choose their own steps, and act on the result. Rather than matching an indicator against a rule and raising an alert, an ATI agent decides which sources to check, weighs the context it gathers, and either escalates with a prepared case or resolves the item itself.
Q: How is agentic threat intelligence different from traditional threat intelligence?
A: Traditional threat intelligence is reactive and rule-bound: it pulls from known feeds and fires when a pattern matches. Agentic threat intelligence is adaptive. It reasons toward an outcome, retains context between tasks, and adjusts as infrastructure and attacker behavior change.
Q: Is agentic threat intelligence just automation with a new name?
A: No. Automation and SOAR playbooks execute a path someone defined in advance, in the form of if X, then Y. An agent is given the objective instead of the path, and selects the tools and sequence itself. That is why it holds up against inputs nobody wrote a rule for.
Q: What does “agentic” actually mean in a threat intelligence context?
A: It refers to four properties working together: autonomy to act without prompting, memory that persists across tasks, goal-directed reasoning toward a stated outcome, and awareness of a changing environment. Remove any one and you are back to scripted automation.
Q: What are the main risks of agentic threat intelligence?
A: Three stand out. An agent may act on an incomplete reading of the data and block something legitimate. Ambiguous input can produce reasoning errors with real operational cost. And autonomy without traceability makes incidents hard to audit. Guardrails on high-risk actions, audit logs, and explainable decision paths address all three.
The Road Ahead for Agentic AI in Threat Intelligence
As adoption grows, agentic AI is poised to play a central role in next-generation cyber defense.
Security teams are beginning to experiment with modular, task-specific agents designed for use cases like phishing detection, alert triage, and IOC enrichment. Some platforms are exploring flexible frameworks that allow organizations to design and deploy agents tailored to their operational environments.
SOCRadar’s Agentic Threat Intelligence (ATI) takes this approach, using adaptable AI agents across enrichment, correlation, alert triage, and reporting.
Longer term, the goal is to build coordinated systems of agents that work together across the entire threat lifecycle. This concept of multi-agent collaboration promises a distributed and efficient model of threat management, where tasks are divided among agents and resolved in parallel.
In this vision, AI becomes a collaborative partner in the SOC, managing high-volume tasks while human analysts focus on strategy and exceptions.












