



Angi Data Sale, The Tour Guy Breach, Healthcare Leads, KPN Leak, and CafeMom Data Resurface
Oct 12, 2026

Instantly access dark web findings about your organization's assets.
Check if there is anything about you in SOCRadar's ever-expanding breach database.
Track threat actors and groups by country or industry for effective follow-up.
Explore threat actors' tactics, techniques, activities, and detailed profiles targeting your industry or region.
All-in-one next-generation tools for investigating everyday events like phishing, malware, account breach, etc.
Power your search with SOCRadar's IOC Radar.
Check whether your domain or IP appears in the FortiBleed breach dataset.
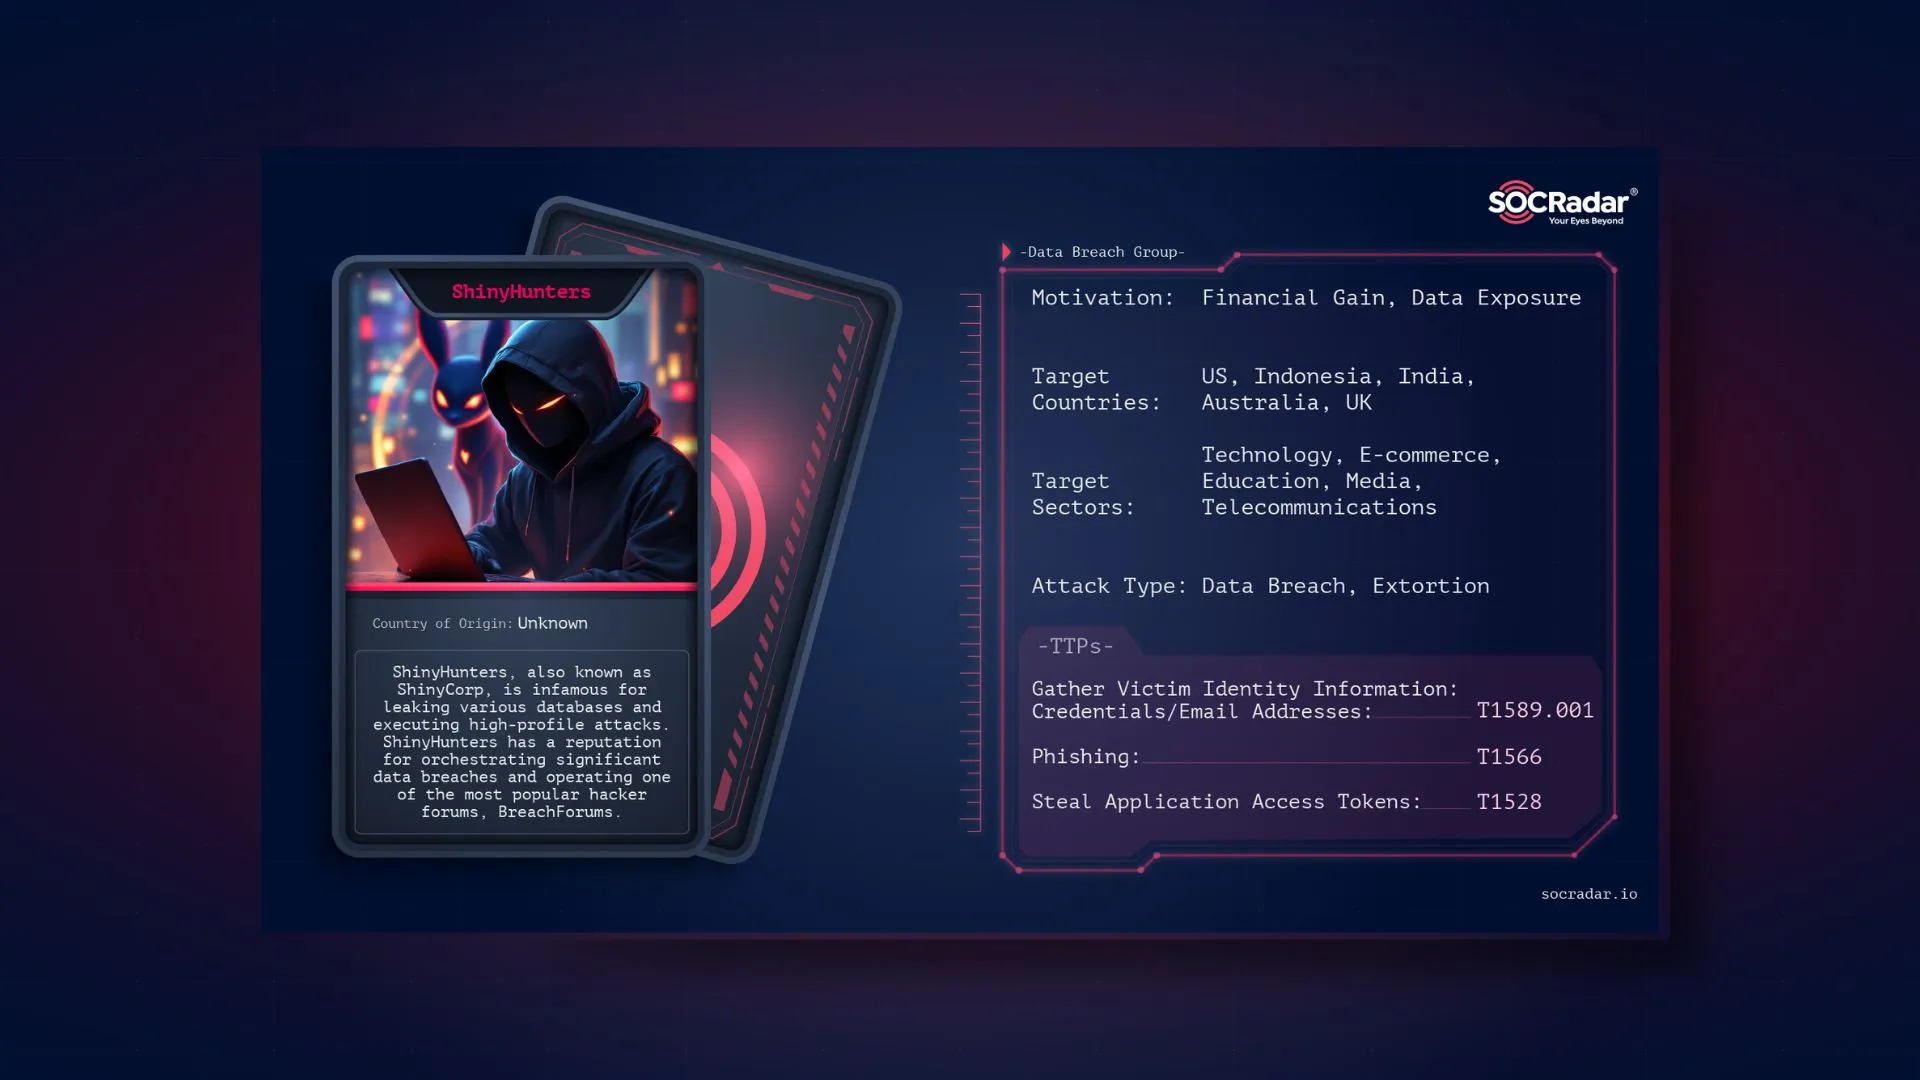
Dark Web Profile: ShinyHunters [Update] July 31, 2025: “ShinyHunters Behind CRM Attacks on Qantas, Adidas, and Others” Within the obscured world of the Deep/Dark Web, where cybercrime flourishes amids...
Binance Stealer Logs, Exodus Botnet, Instagram 0-day Exploit, and Database Sales Explore the most recent dark web threats identified by SOCRadar’s Dark Web Team. From the exposure of Binance user ste...
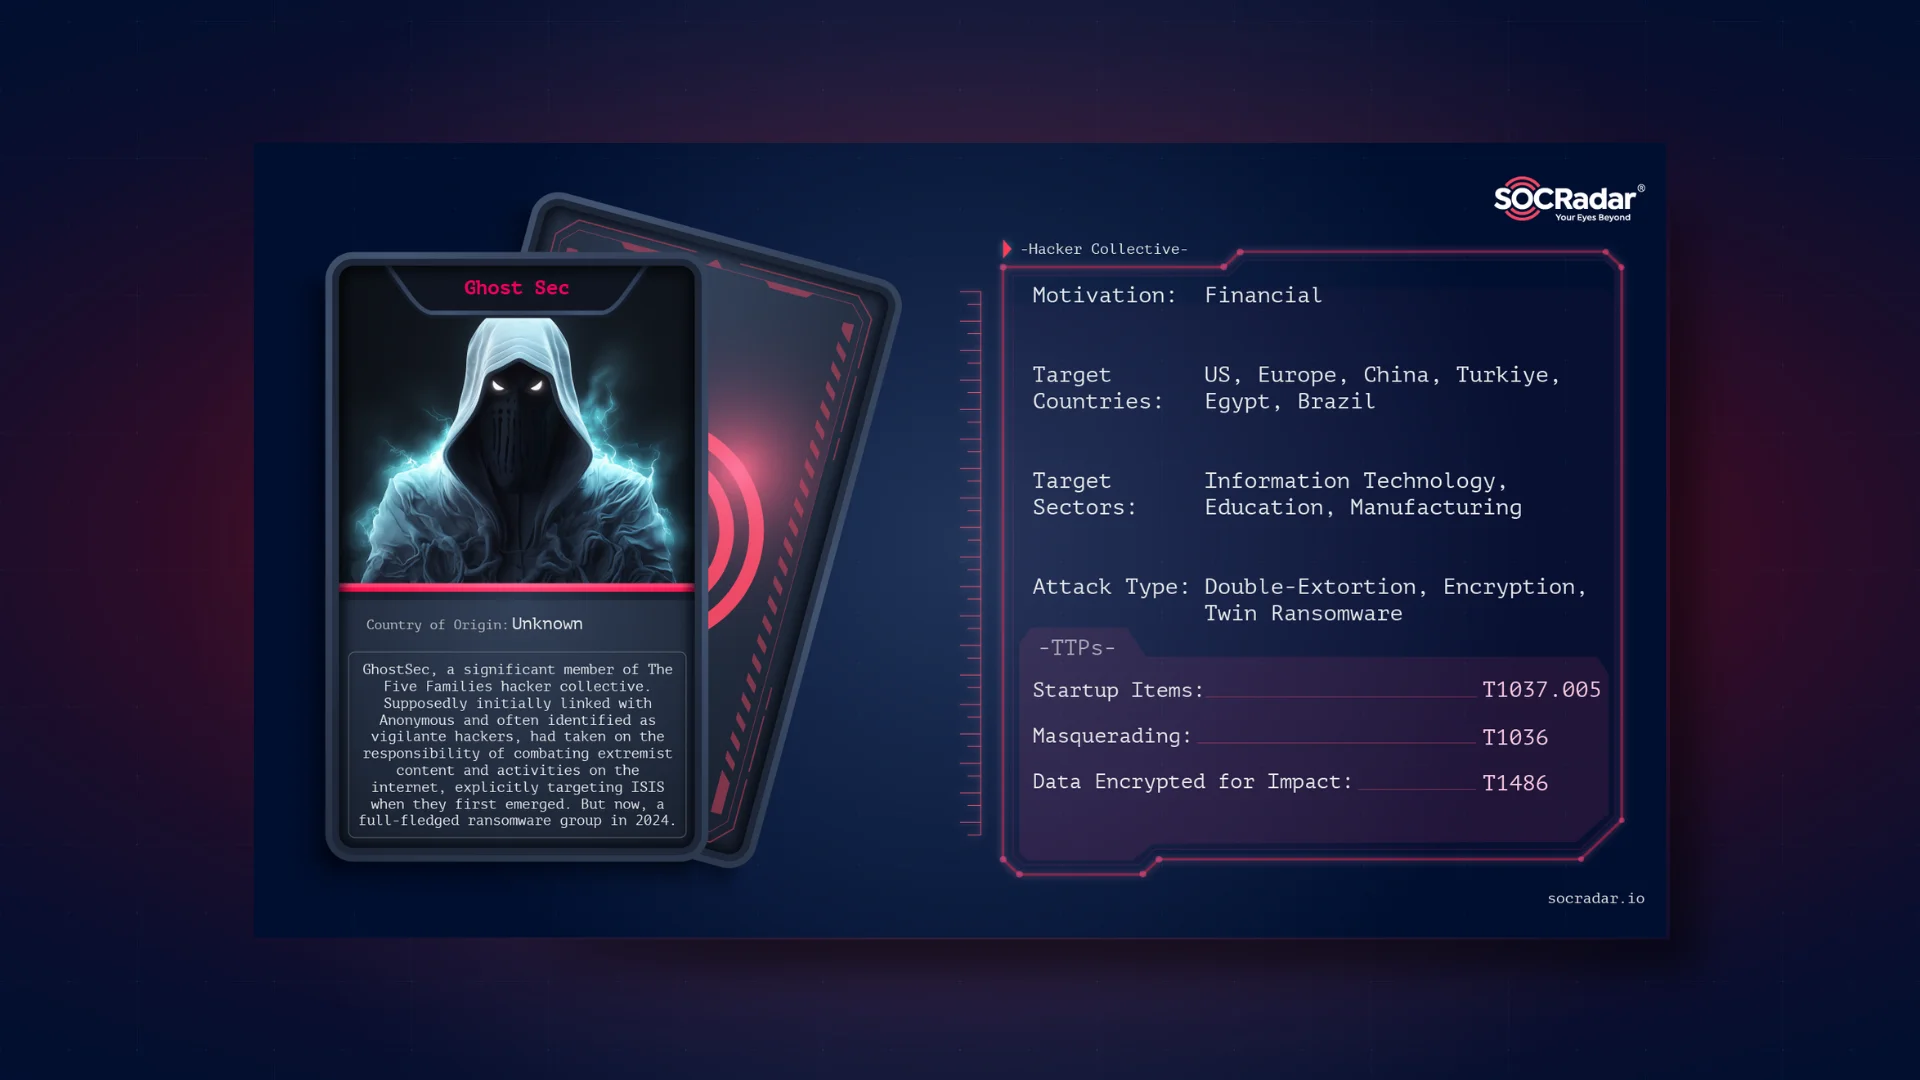
Dark Web Profile: GhostSec [Update] May 16, 2024: “GhostSec Shifts Focus from Cybercrime to Hacktivism” GhostSec, a significant member of The Five Families, has garnered substantial attention with the...
Top 10 Vulnerabilities on the Dark Web in 2023 In the Dark Web, where cybercriminals and hackers converge to trade secrets and illicit goods, vulnerabilities can easily become weapons for many, and th...
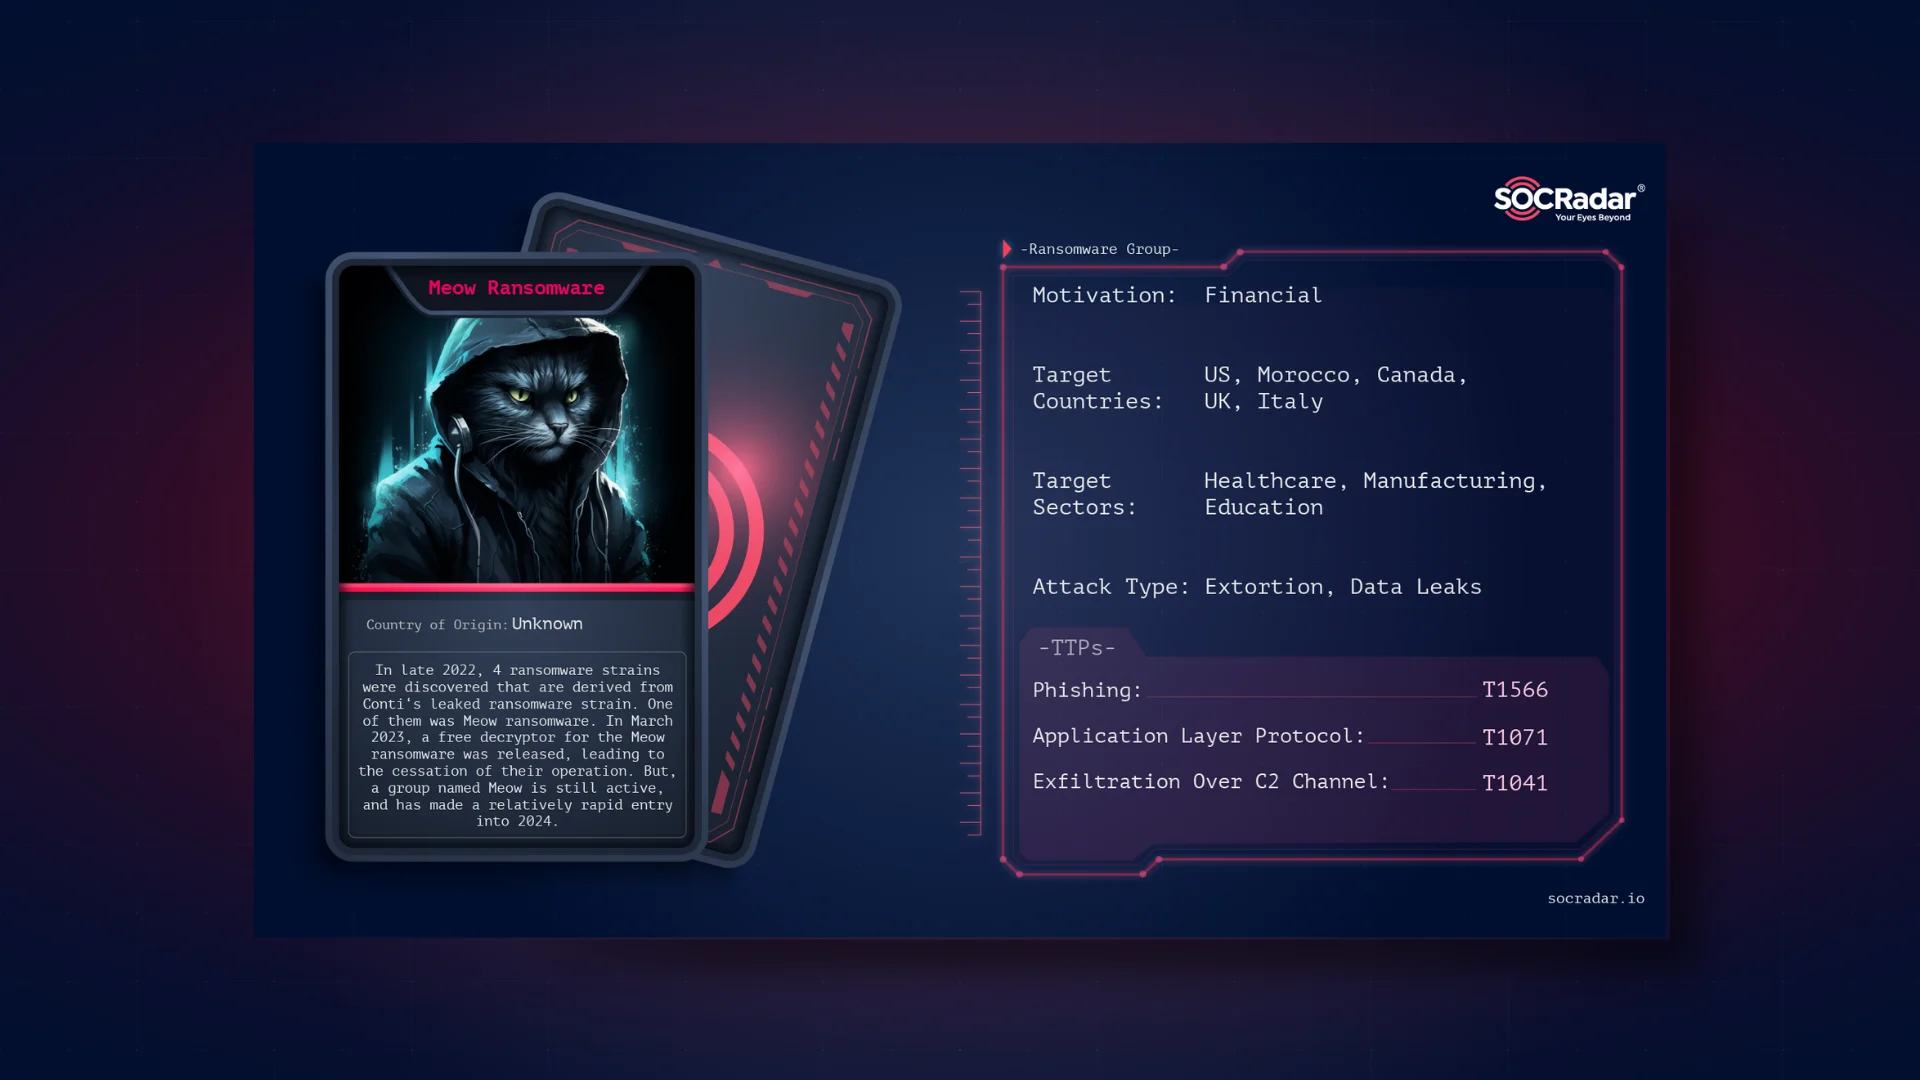
Dark Web Profile: Meow Ransomware In late 2022, 4 ransomware strains were discovered that are derived from Conti‘s leaked ransomware strain. One of them was Meow ransomware. The operation of this cryp...
Acuity Federal Contractor Breach, Okta Customers Leak, DCRat Exploit and Access Sales In the Dark Web, a world of illicit activities and cyber threats, the SOCRadar Dark Web Team has uncovered a serie...
Dark Peep #12: The Ransomware Group That Never Was Welcome to Dark Peep #12, where we dive into the latest cyber escapades reminiscent of tales from the Wild West. This edition is packed with stories ...
Navigating the Shadowy Depths of the Migo Malware Campaign The Migo malware campaign emerged as a formidable adversary, targeting Redis servers with novel system-weakening techniques aimed at cryptoja...
ALPHV’s Roller Coaster, $22 Million Ransom [Update] March 7, 2024: “Money Paid, Data Retained; ALPHV’s Exit Scam” The ransomware attack on Change Healthcare has become one of the most disruptive incid...
0-Day Exploit Sales for Outlook and Jenkins, Insurance and Banking Data Leaks, and More Journey through the sinister realms of cyberspace with SOCRadar’s Dark Web Team. The sale of critical 0-day expl...
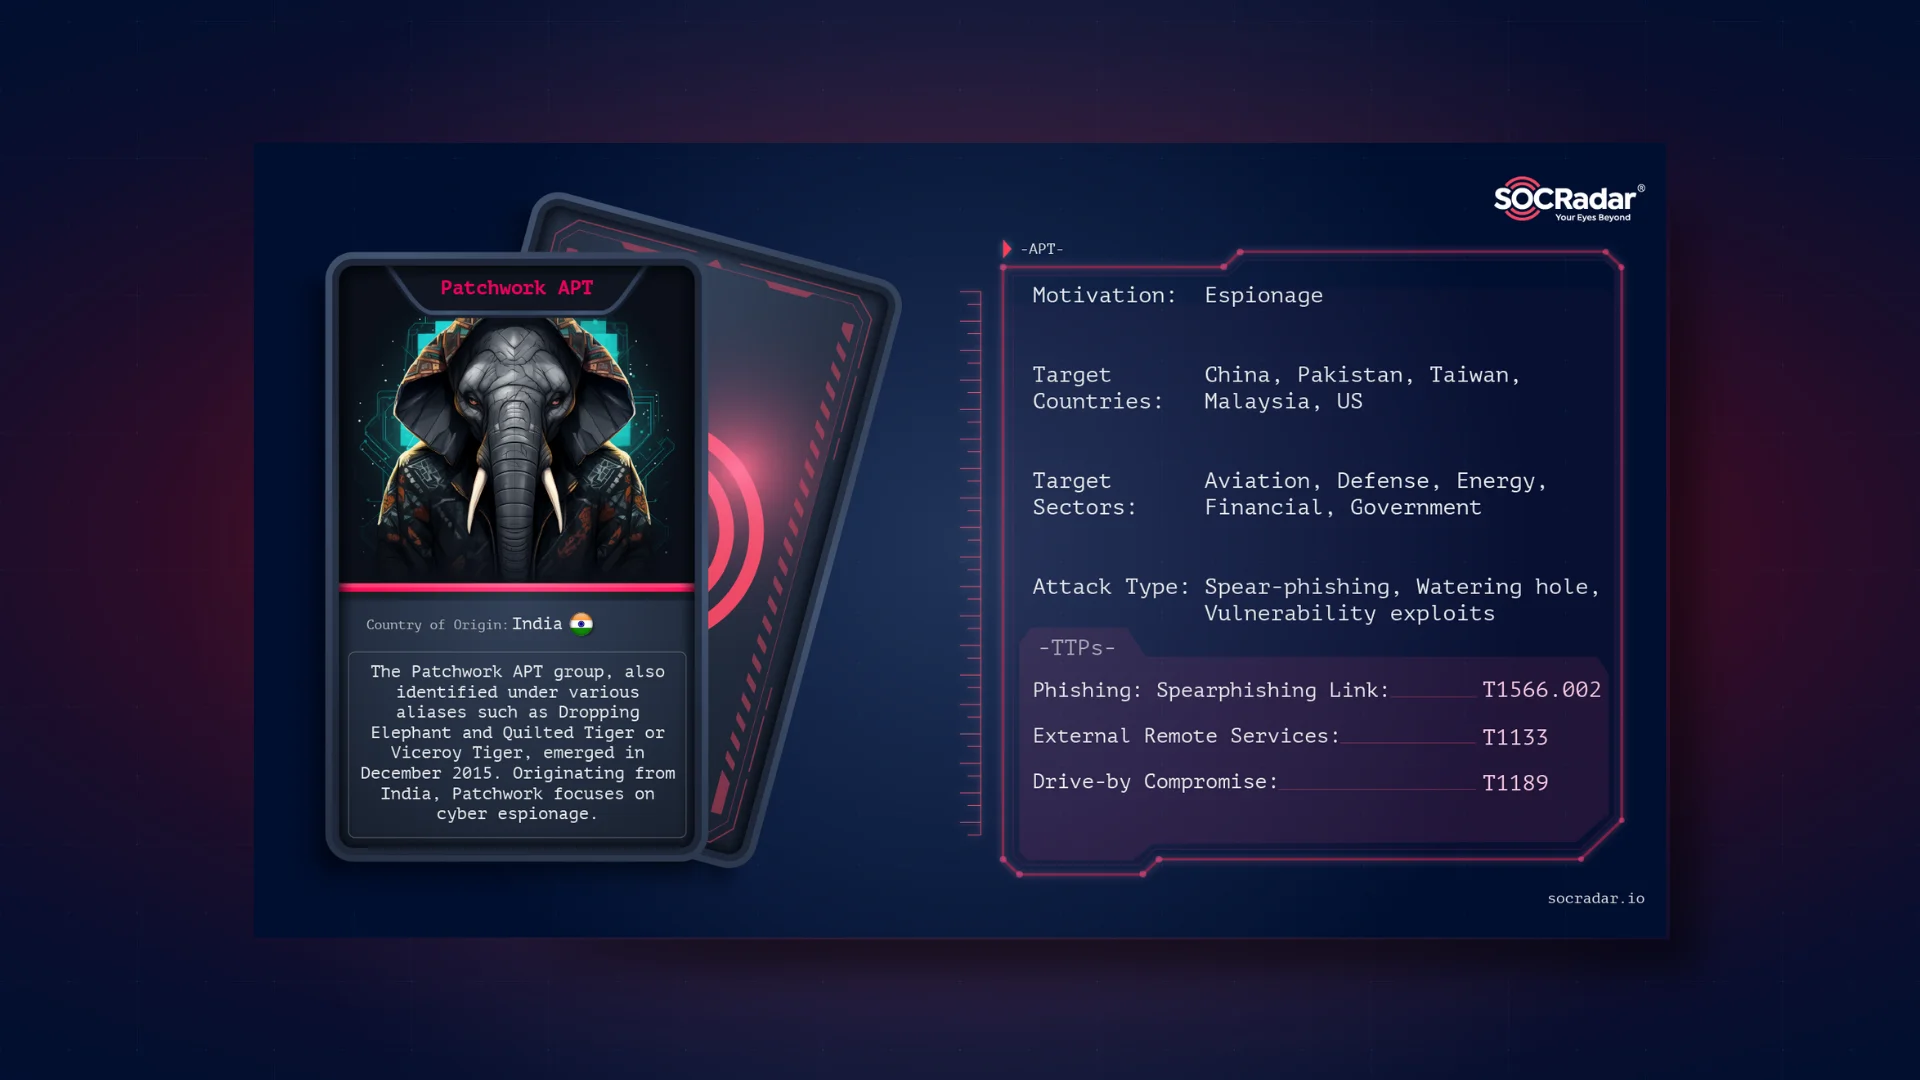
Dark Web Profile: Patchwork APT The Patchwork APT group, identified in December 2015 but probably active since 2009, is a cyber espionage entity suspected to be based in India. It targets a variety of...
LAX and Generali Database Leaks, US Credit Card Sales, Unauthorized Accesses, and Recruitment Posts Discover the latest revelations from the SOCRadar Dark Web Team, exposing a myriad of security breac...
Dark Peep #11: The Final Curtain for LockBit Ransomware (Operation Cronos) Digital Olympians and seekers of cyber lore! “Dark Peep #11” unfurls its scroll to reveal tales of cunning, courage, and chao...
Power of AI: Dark Web Monitoring with ChatGPT The dark web, often shrouded in mystery and intrigue, is a part of the internet that remains hidden from conventional search engines and browsers. It’s a ...
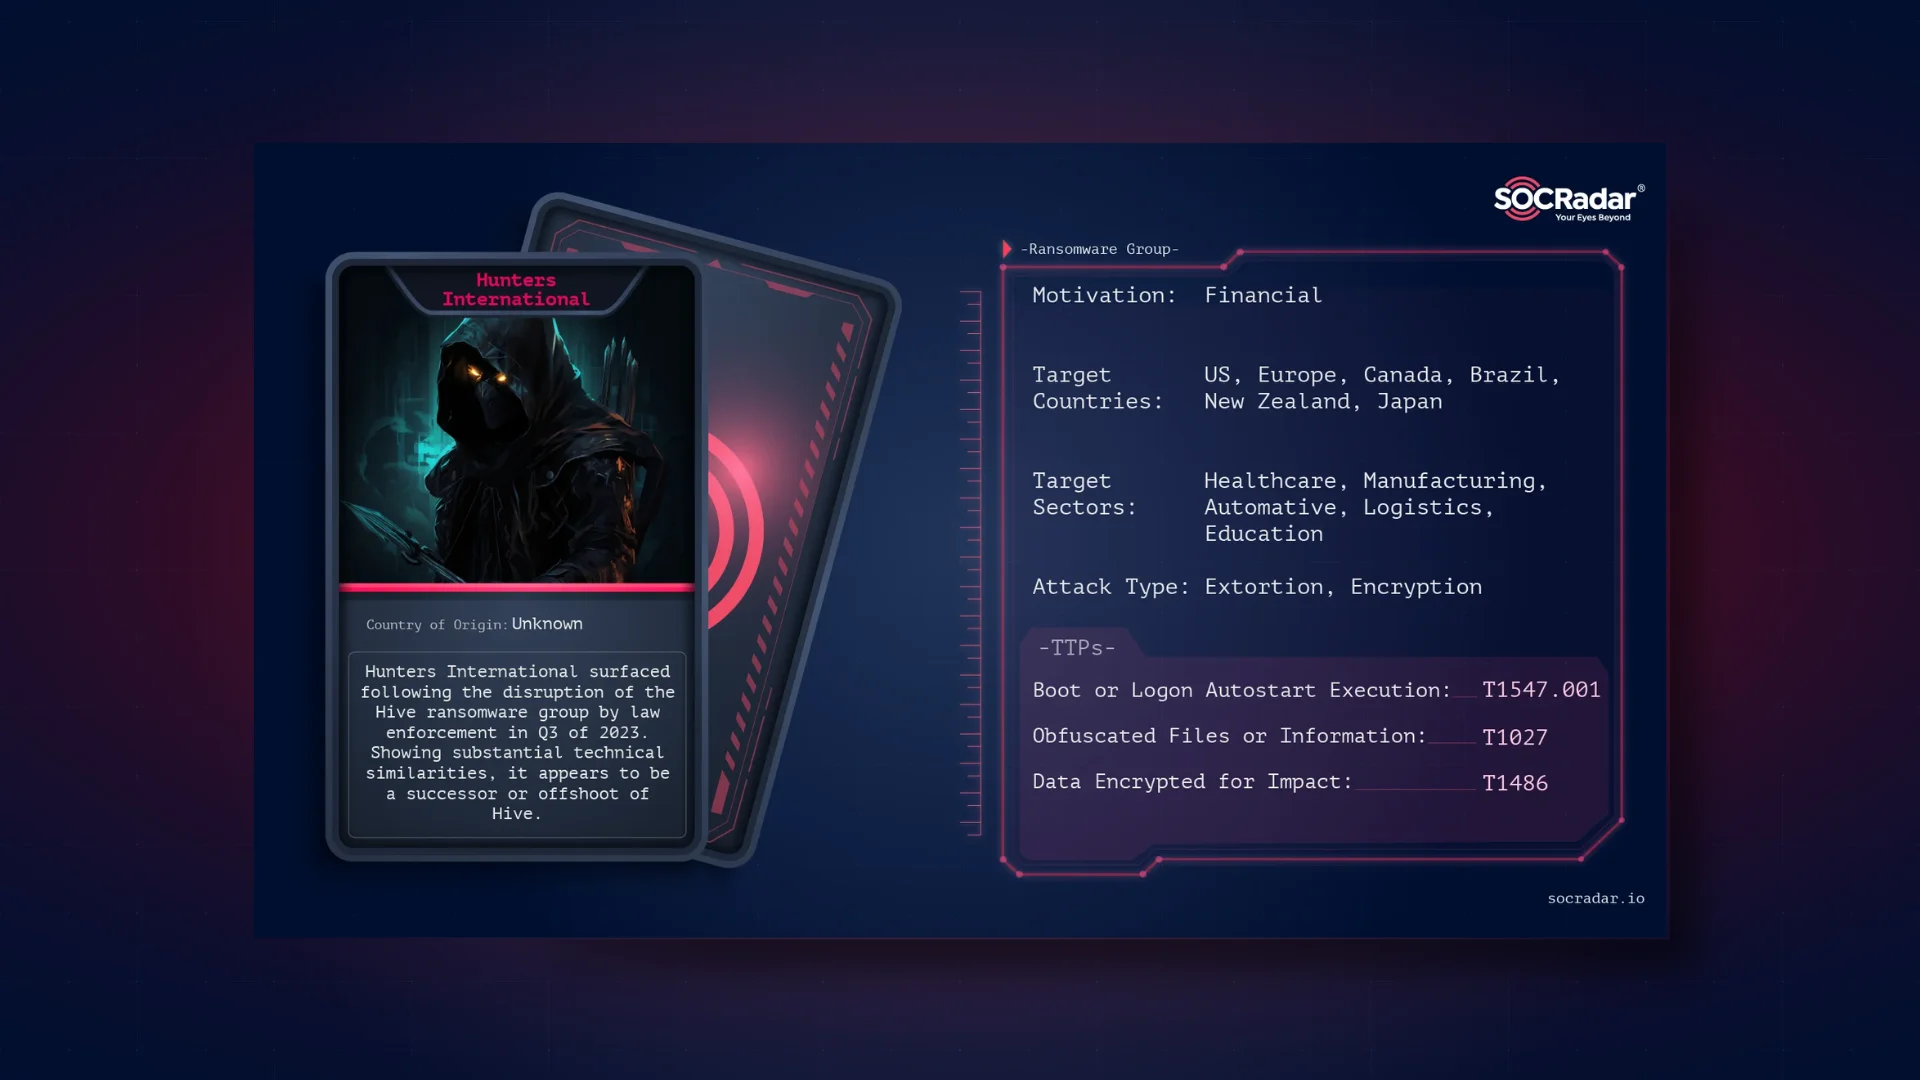
Dark Web Profile: Hunters International [Update] July 22, 2025: “Hunters International Shuts Down, Rebrands as World Leaks” Originating in the latter part of 2023, this Ransomware-as-a-Service (RaaS) ...
International Authorities Strike Blow Against LockBit Ransomware: Operation Cronos [Update] October 1, 2024: “New Arrests and Infrastructure Seizures” [Update] June 6, 2024: “FBI Offers +7,000 LockBit...
Sales of bfBot Stealer & Knight Ransomware Source Code, Dior Vulnerabilities, Passport Leaks, and More The SOCRadar Dark Web Team exposed alarming sales, from ransomware source codes to leaked pas...
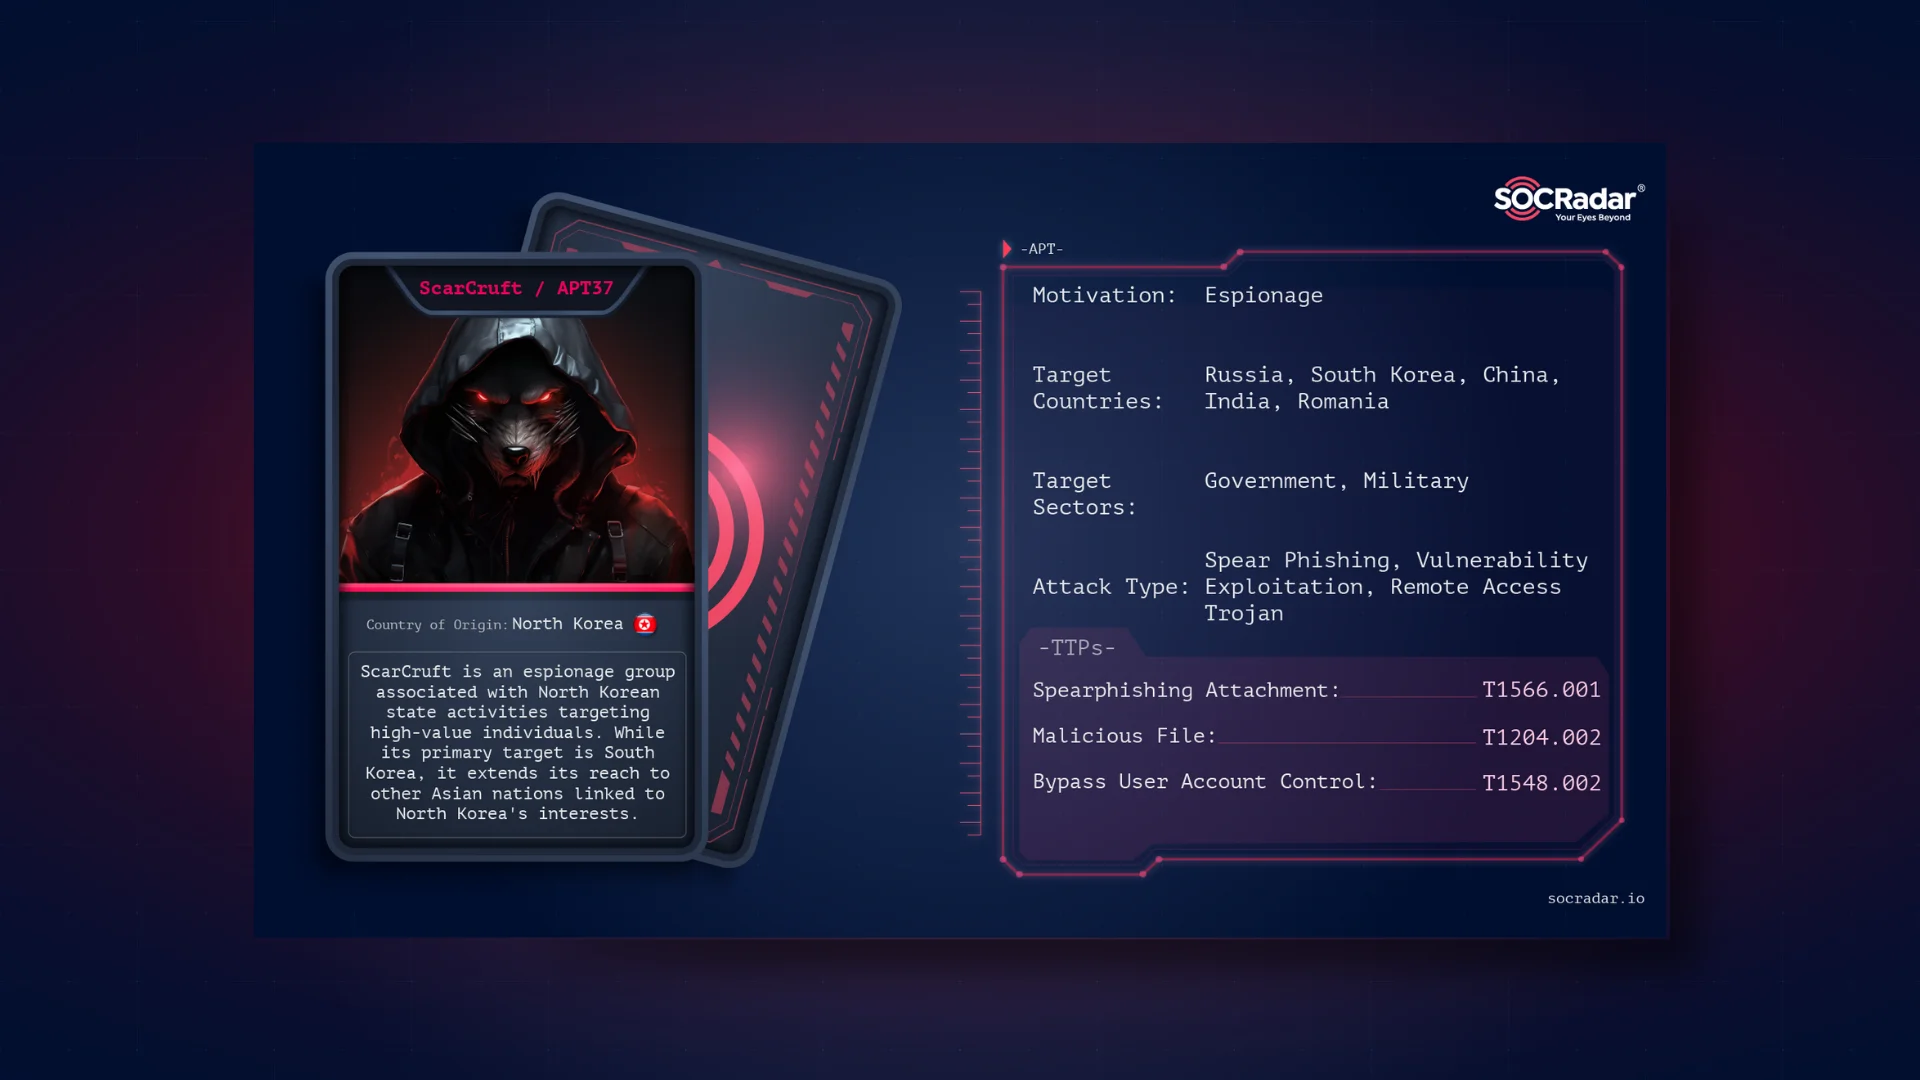
Dark Web Profile: ScarCruft / APT37 [Update] October 17, 2024: “ScarCruft Exploits CVE-2024-38178 to Deploy RokRAT Malware” ScarCruft, also widely known as APT37 or Reaper APT, is an espionage group a...
Pipeline to Peril: Unpacking the ALPHV Attack on Trans-Northern [Update] February 16, 2024: “US State Department’s Reward for Information on ALPHV/BlackCat Ransomware” In the ever-evolving landscape o...
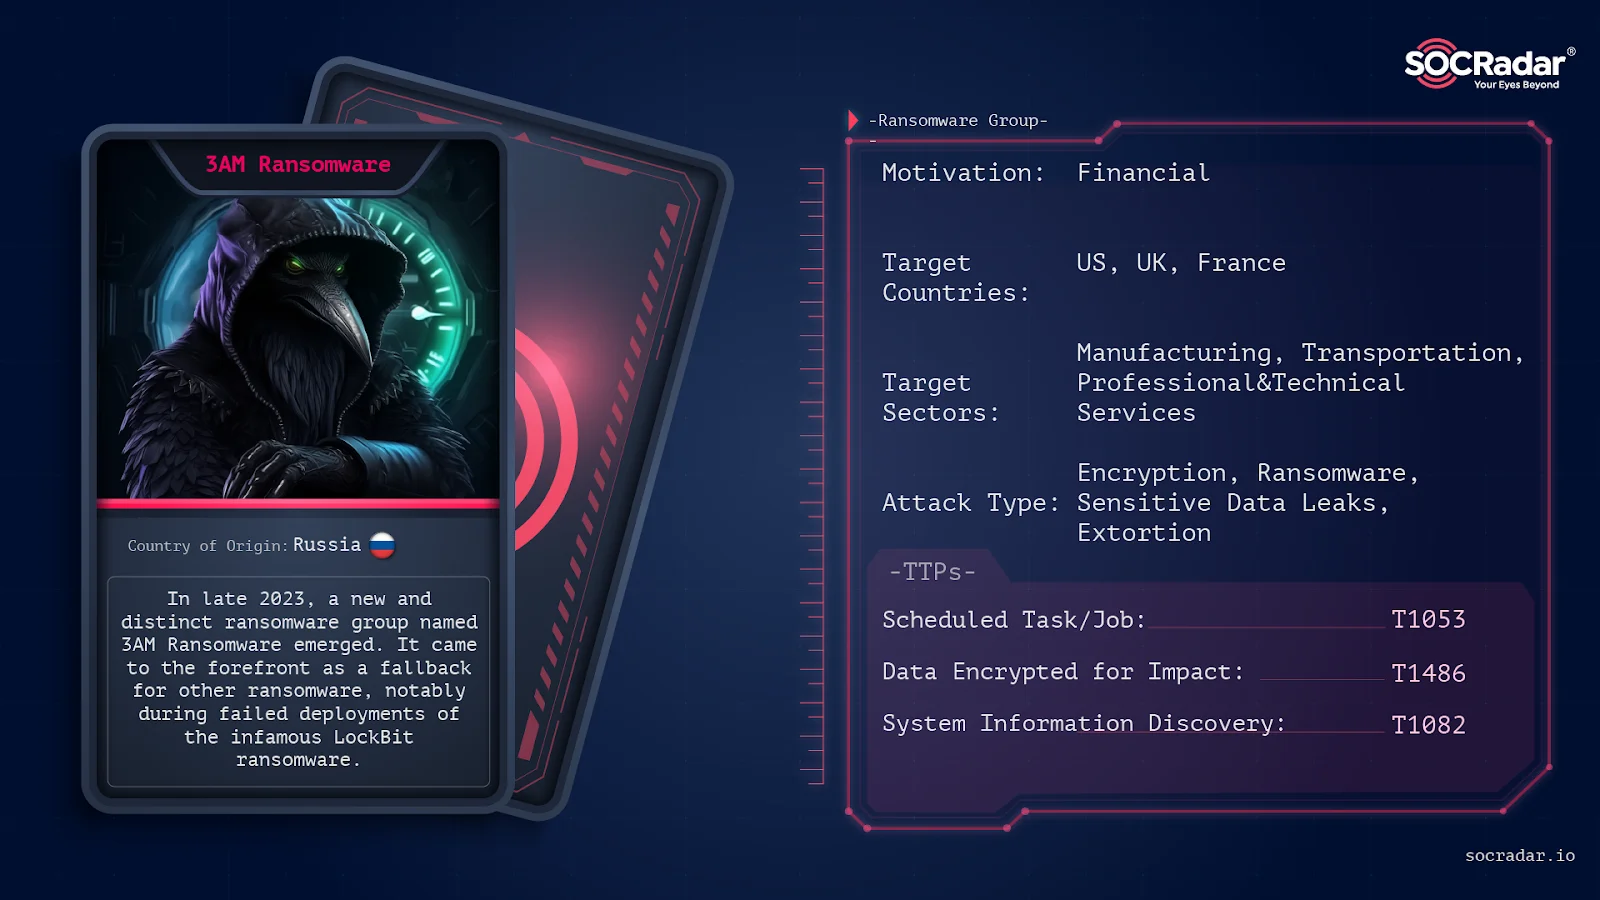
Dark Web Profile: 3AM Ransomware In late 2023, a new and distinct ransomware group named 3AM Ransomware emerged. It came to the forefront as a fallback for other ransomware, notably during failed depl...
PROTECTION OF PERSONAL DATA COOKIE POLICY FOR THE INTERNET SITE
Protecting your personal data is one of the core principles of our organization, SOCRadar, which operates the internet site (www.socradar.com). This Cookie Usage Policy (“Policy”) explains the types of cookies used and the conditions under which they are used to all website visitors and users.
Cookies are small text files stored on your computer or mobile device by the websites you visit.
Cookies are commonly used to provide you with a personalized experience while using a website, enhance the services offered, and improve your overall browsing experience, contributing to ease of use while navigating a website. If you prefer not to use cookies, you can delete or block them through your browser settings. However, please be aware that this may affect your usage of our website. Unless you change your cookie settings in your browser, we will assume that you accept the use of cookies on this site.
1. WHAT KIND OF DATA IS PROCESSED IN COOKIES?
Cookies on websites collect data related to your browsing and usage preferences on the device you use to visit the site, depending on their type. This data includes information about the pages you access, the services and products you explore, your preferred language choice, and other preferences.
2. WHAT ARE COOKIES AND WHAT ARE THEIR PURPOSES?
Cookies are small text files stored on your device or web server by the websites you visit through your browsers. These small text files, containing your preferred language and other settings, help us remember your preferences on your next visit and assist us in making improvements to our services to enhance your experience on the site. This way, you can have a better and more personalized user experience on your next visit.
The main purposes of using cookies on our Internet Site are as follows:
3. TYPES OF COOKIES USED ON OUR INTERNET SITE 3.1. Session Cookies
Session cookies ensure the smooth operation of the internet site during your visit. They are used for purposes such as ensuring the security and continuity of our sites and your visits. Session cookies are temporary cookies and are deleted when you close your browser; they are not permanent.
3.2. Persistent Cookies
These cookies are used to remember your preferences and are stored on your device through browsers. Persistent cookies remain stored on your device even after you close your browser or restart your computer. These cookies are stored in your browser’s subfolders until deleted from your browser’s settings. Some types of persistent cookies can be used to provide personalized recommendations based on your usage purposes.
With persistent cookies, when you revisit our website with the same device, the website checks if a cookie created by our website exists on your device. If so, it is understood that you have visited the site before, and the content to be presented to you is determined accordingly, offering you a better service.
3.3. Mandatory/Technical Cookies
Mandatory cookies are essential for the proper functioning of the visited internet site. The purpose of these cookies is to provide necessary services by ensuring the operation of the site. For example, they allow access to secure sections of the internet site, use of its features, and navigation.
3.4. Analytical Cookies
These cookies gather information about how the website is used, the frequency and number of visits, and show how visitors navigate to the site. The purpose of using these cookies is to improve the operation of the site, increase its performance, and determine general trend directions. They do not contain data that can identify visitors. For example, they show the number of error messages displayed or the most visited pages.
3.5. Functional Cookies
Functional cookies remember the choices made by visitors within the site and recall them during the next visit. The purpose of these cookies is to provide ease of use to visitors. For example, they prevent the need to re-enter the user’s password on each page visited by the site user.
3.6. Targeting/Advertising Cookies
They measure the effectiveness of advertisements shown to visitors and calculate how many times ads are displayed. The purpose of these cookies is to present personalized advertisements to visitors based on their interests.
Similarly, they determine the specific interests of visitors’ navigation and present appropriate content. For example, they prevent the same advertisement from being shown again to the visitor in a short period.
4. HOW TO MANAGE COOKIE PREFERENCES?
To change your preferences regarding the use of cookies, block or delete cookies, you only need to change your browser settings.
Many browsers offer options to accept or reject cookies, only accept certain types of cookies, or receive notifications from the browser when a website requests to store cookies on your device.
Also, it is possible to delete previously saved cookies from your browser.
If you disable or reject cookies, you may need to manually adjust some preferences, and certain features and services on the website may not work properly as we will not be able to recognize and associate with your account. You can change your browser settings by clicking on the relevant link from the table below.
5. EFFECTIVE DATE OF THE INTERNET SITE PRIVACY POLICY
The Internet Site Privacy Policy is dated The effective date of the Policy will be updated if the entire Policy or specific sections are renewed. The Privacy Policy is published on the Organization’s website (www.socradar.com) and made accessible to relevant individuals upon request.
SOCRadar
Address: 651 N Broad St, Suite 205 Middletown, DE 19709 USA
Phone: +1 (571) 249-4598
Email: [email protected]
Website: www.socradar.com


