CVE-2026-102764: BeyondTrust Zero-Day Exploited
BeyondTrust has disclosed CVE-2026-102764, a critical Remote Support vulnerability exploited as a zero-day weeks before customers received a patch.
The attack began on August 29, 2026, when one BeyondTrust-hosted Remote Support instance and one self-hosted appliance were compromised. BeyondTrust detected the hosted incident during proactive hunting on September 28, reproduced the entry vector that day, released patches on October 8, and publicly disclosed the CVE on October 15.
Researchers attribute the activity to ARMORY CASTLE, formerly tracked as UNC5221, a suspected PRC-nexus espionage actor known for targeting edge appliances.
What Is CVE-2026-102764?
CVE-2026-102764 is an improper origin validation vulnerability (CWE-290) in an internal Remote Support messaging component.
According to BeyondTrust, the component did not adequately validate where received messages originated. Under the right conditions, this allows remote attackers to trigger file operations without authentication or user interaction. BeyondTrust rates the flaw Critical with a CVSS v4.0 score of 9.3.
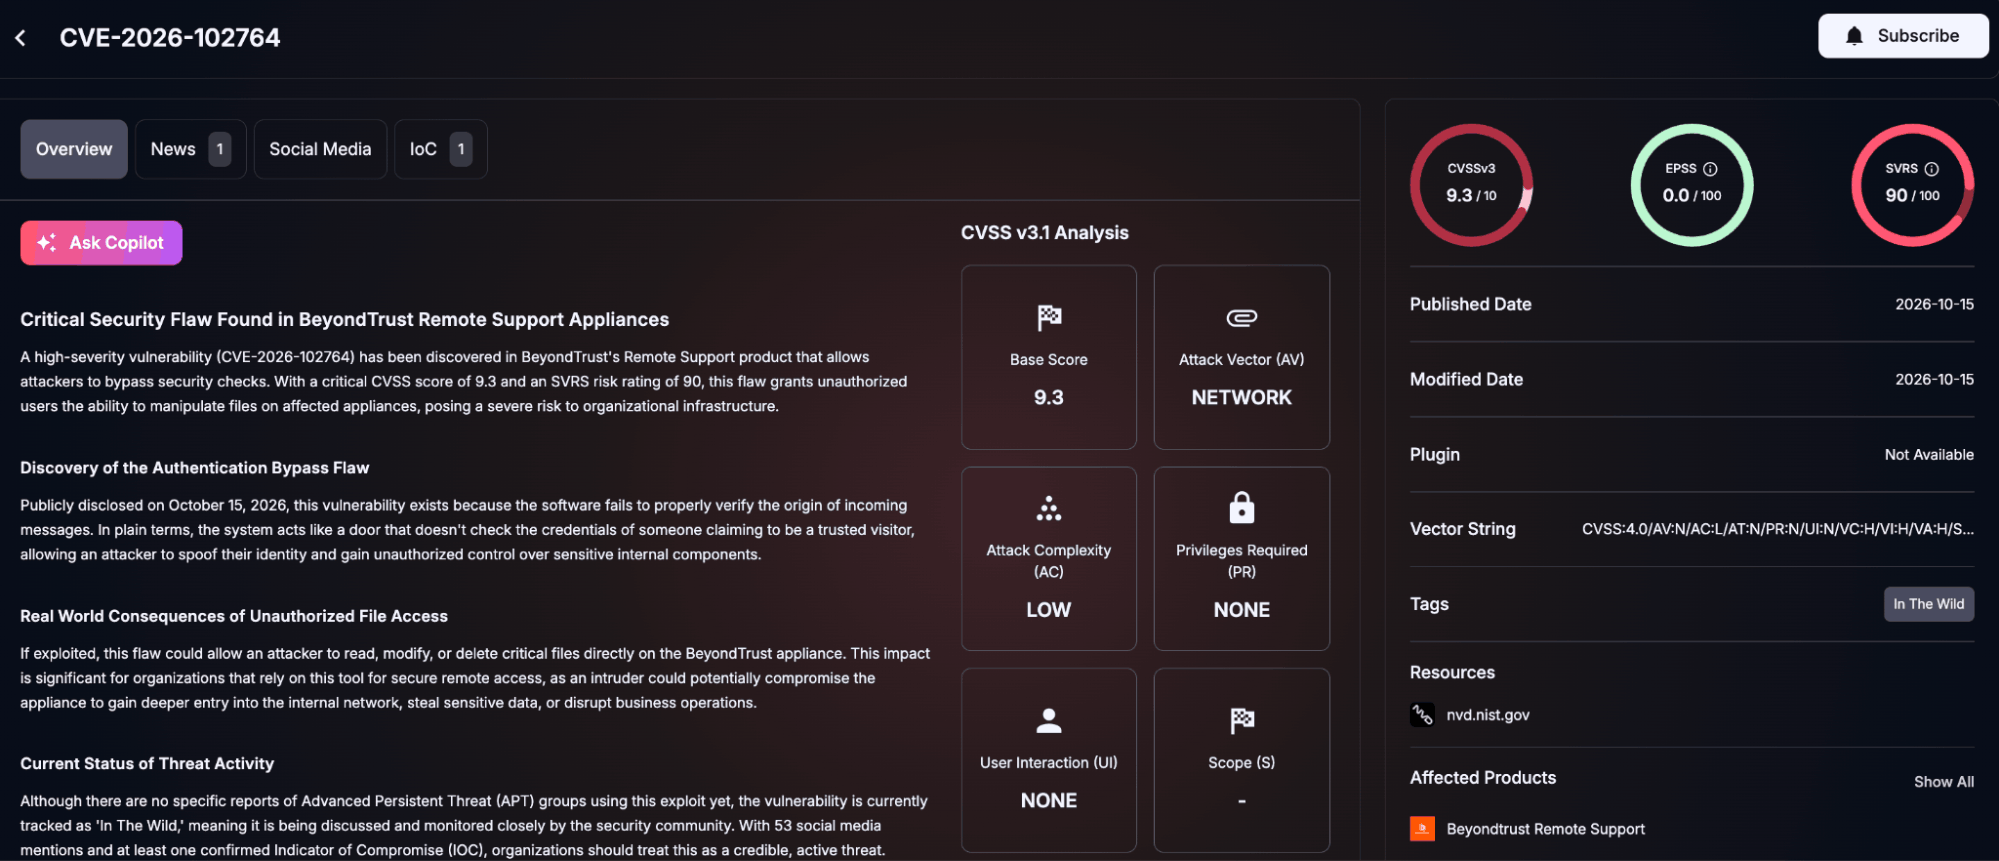
The vulnerability itself provides the file operation capability. Root access is a subsequent exploitation outcome: observed attackers upload a webshell and later elevate privileges to gain full control of the appliance.
Which BeyondTrust Versions Are Affected?
| Product | Status |
| Remote Support 26.2.3 and earlier | Affected |
| Versions 24.3.1–26.2.3 | Apply BT26-05-RS |
| Versions older than 24.3.1 | Upgrade first, then apply patch |
| Remote Support SaaS | Patched by October 9 |
BeyondTrust released the patch on October 8, before coordinated public disclosure on October 15. SaaS instances were automatically remediated, while self-hosted customers must verify that BT26-05-RS was applied through the /appliance interface or automatic updates.
Privileged Remote Access shares affected code, but BeyondTrust says it has not identified an exploitation path for PRA. The company nevertheless released a precautionary patch and recommends that self-hosted PRA customers apply it.
How Did ARMORY CASTLE Exploit BeyondTrust?
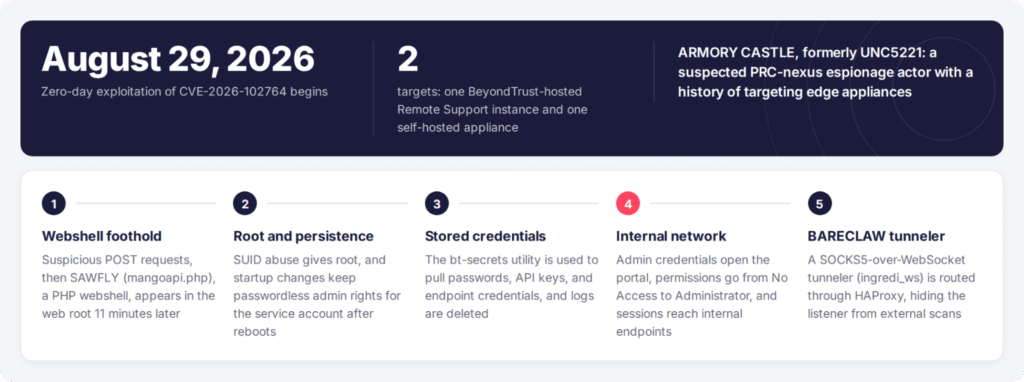
BeyondTrust’s incident advisory says CVE-2026-102764 was exploited as a zero-day on August 29, 2026, against one BeyondTrust-hosted Remote Support instance and one self-hosted appliance. BeyondTrust detected the hosted activity during proactive hunting on September 28, reproduced the entry vector that day, and released the BT26-05 patch on October 8 ahead of coordinated disclosure on October 15.
In their detailed investigation, Google Threat Intelligence Group (GTIG) and Mandiant attributed the zero-day exploitation and subsequent malware deployment to ARMORY CASTLE, formerly tracked as UNC5221. GTIG describes the group as a suspected PRC-nexus espionage actor with a history of targeting edge appliances.
After exploiting CVE-2026-102764, the actor moved through several stages to turn the initial file upload capability into persistent access and internal network reach.
1. Establishing a Webshell Foothold
Following the initial exploit, suspicious POST requests were observed. About 11 minutes later, the appliance recorded creation of SAWFLY (mangoapi.php), a lightweight PHP webshell placed in the web root. ARMORY CASTLE then used SAWFLY as a primary interactive foothold.
2. Escalating to Root and Establishing Persistence
SAWFLY initially ran under an unprivileged service account. The actor abused SUID permissions to obtain root-level execution, then modified startup configuration so the service account retained passwordless administrative privileges after reboots or configuration resets.
3. Targeting Stored Credentials
With root access, ARMORY CASTLE attempted to use BeyondTrust’s native bt-secrets utility to retrieve credentials from the appliance’s secrets store, including passwords, API keys, and endpoint credentials.
The actor also deleted related logs and other appliance records, reinforcing BeyondTrust’s recommendation that defenders preserve telemetry off the appliance rather than relying only on local evidence.
4. Moving Into the Internal Network
The attacker later used compromised administrator credentials to access the Remote Support portal and changed Jump Item and Team permissions from No Access to Administrator.
That access allowed the actor to initiate Remote Support sessions to internal endpoints and use the platform’s built-in file transfer capabilities to obtain sensitive documents useful for internal reconnaissance.
5. Deploying BARECLAW
ARMORY CASTLE also deployed BARECLAW (ingredi_ws), a custom SOCKS5-over-WebSocket tunneler, and modified HAProxy configuration to route a specially configured web path to the locally running tunnel.
This provided another channel through the compromised Remote Support appliance for reaching downstream systems while making the local listener harder to identify through ordinary external scanning.
GTIG warns that ARMORY CASTLE has previously moved from selective zero-day exploitation to broader, opportunistic attacks after vulnerabilities become public. As of the October 15 analysis, however, widespread exploitation of CVE-2026-102764 had not been confirmed.
Track Emerging Zero-Day Threats with SOCRadar
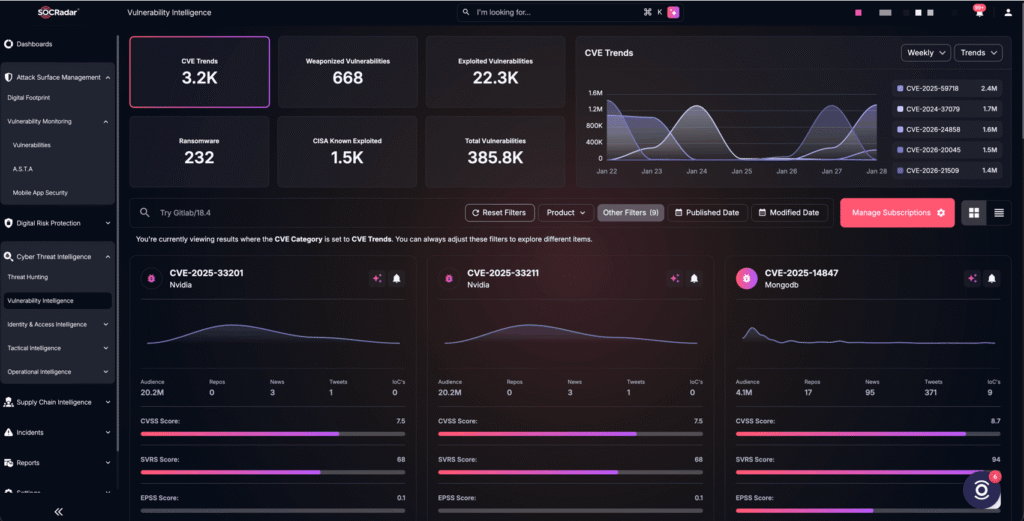
SOCRadar’s Cyber Threat Intelligence module, powering Vulnerability Intelligence, can help teams monitor CVE-2026-102764 for exploitation developments, threat actor activity, indicators, and remediation changes.
Vulnerability Intelligence provides additional technical and risk context, while Attack Surface Management can help identify internet-facing BeyondTrust Remote Support appliances that require immediate patch validation and compromise assessment.
What Should Defenders Do?
Treat any vulnerable Remote Support appliance that was internet-accessible during the exploitation window as potentially compromised until reviewed, rather than assuming that installing the patch resolves prior compromise.
Defenders should:
- Patch immediately: Apply BT26-05-RS. Systems older than 24.3.1 must first move to a supported release.
- Preserve evidence: Snapshot virtual appliances and retain external syslog, WAF, reverse-proxy, firewall, and authentication telemetry before rebuilding.
- Rebuild suspected systems: It is recommended to redeploy confirmed or potentially compromised appliances from a clean, patched image rather than relying on cleanup.
- Rotate credentials after remediation: Include appliance administrators, API secrets, SAML material, vault credentials, integrations, and credentials used during support sessions.
- Reduce exposure: Restrict /login and /appliance administration to trusted networks, limit outbound connectivity, and forward logs off the appliance.
For hunting, prioritize unexpected privileged sessions from residential or VPN networks, unknown PHP files in web directories, web-service accounts spawning shells, user_changed events that elevate Jump Item or Team permissions, unusual WebSocket traffic, HAProxy changes, and unexplained gaps in forwarded logs. BeyondTrust specifically stresses off-appliance logging because the observed actor deleted local evidence.
Indicators of Compromise (IOCs)
Mandiant also published file indicators and YARA rules for SAWFLY and BARECLAW in its technical analysis, which defenders can incorporate into investigations alongside behavioral hunting.
File Indicators
- app_84304470%2Ephp (Staging webshell)
- mangoapi.php (SAWFLY webshell) – SHA-256: dc14e215269a93fdbc4c1a80b984c23faf7af0911c6dbb85309796a6f2ae95fb
- ingredi_ws (BARECLAW tunneler) – SHA-256: 1f19b9a27d79c11bda00a1e8faf74a7fdd683d38ccef1b60df2fd0307e3aa462
YARA Rules
For SAWFLY:
rule G_Hunting_Webshell_SAWFLY_1 {
meta:
author = “Google Threat Intelligence Group”
strings:
$b32 = “ABCDEFGHIJKLMNOPQRSTUVWXYZ234567” ascii wide
$rc4 = “range(0,255)” ascii wide
$pack = “pack(‘H*’,” ascii wide
$eval = “@eval(” ascii wide
$code404 = “http_response_code(404)” ascii wide
condition:
filesize < 20KB and
all of them
}
For BARECLAW:
rule G_Hunting_Backdoor_BARECLAW_1 {
meta:
author = “Google Threat Intelligence Group”
strings:
$s1 = “[%s ws_socks5d] ” ascii wide
$s2 = “–obfs requires –token” ascii wide
$s3 = “mux: %s (frame[%lu]: %s)” ascii wide
$s4 = “cannot create stream pump/writer thread (stream %d)” ascii wide
$s5 = “reject: bad or missing token from %s” ascii wide
$s6 = “listening on %s path=%s (token=%s obfs=%s max_tunnels=%d threads=%d)” ascii wide
$s7 = “–ws-path must start with ‘/’” ascii wide
$b_xorshift = { 48 c1 e0 17 48 31 c1 48 89 f0 48 c1 e8 1a 48 31 f0 48 31 c8 48 c1 e9 11 48 31 c8 }
condition:
uint32(0) == 0x464c457f and (5 of ($s*)) or ($b_xorshift and (3 of ($s*)))
}