Canadian Webmail Access, US Bank Dump, Peru Leak, Spencer’s Breach, and ZoomInfo Sale
SOCRadar Dark Web Team identified several underground posts, including an alleged webmail access sale targeting a Canadian infrastructure company, a claimed US banking database dump involving sensitive credentials, and an alleged Peruvian government registry leak affecting more than 20 million records. Other posts advertised an alleged Spencer’s retail database breach and millions of business contact records reportedly sourced from ZoomInfo.
Alleged Canadian Infrastructure Webmail Access Is Offered for Sale
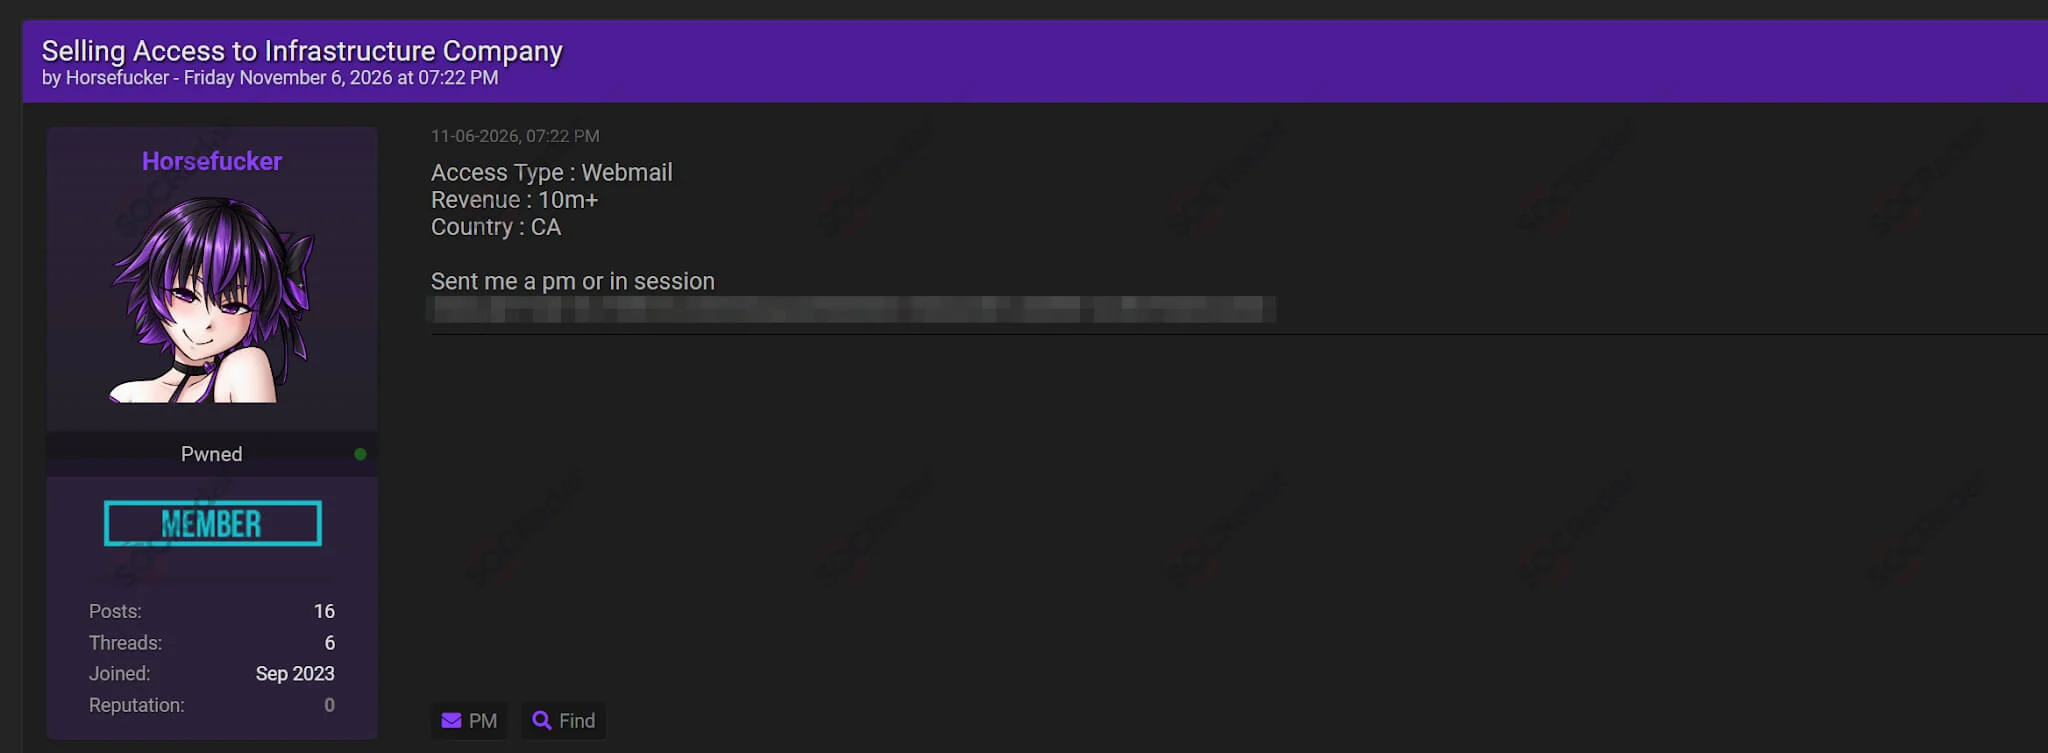
SOCRadar Dark Web Team detected a dark web post advertising alleged webmail access to a Canadian infrastructure company. The threat actor, operating under the alias Horsefucker, claimed that the targeted organization generates more than $10 million in annual revenue.
The listing identified Canada as the target country and webmail as the access type but did not disclose the organization’s name, email domain, or supporting evidence. If legitimate, compromised webmail access could facilitate Business Email Compromise (BEC), credential theft, phishing, and further unauthorized access to corporate systems. The claim remains unverified.
Alleged US Bank Database Dump and Cloud Credentials Are Advertised
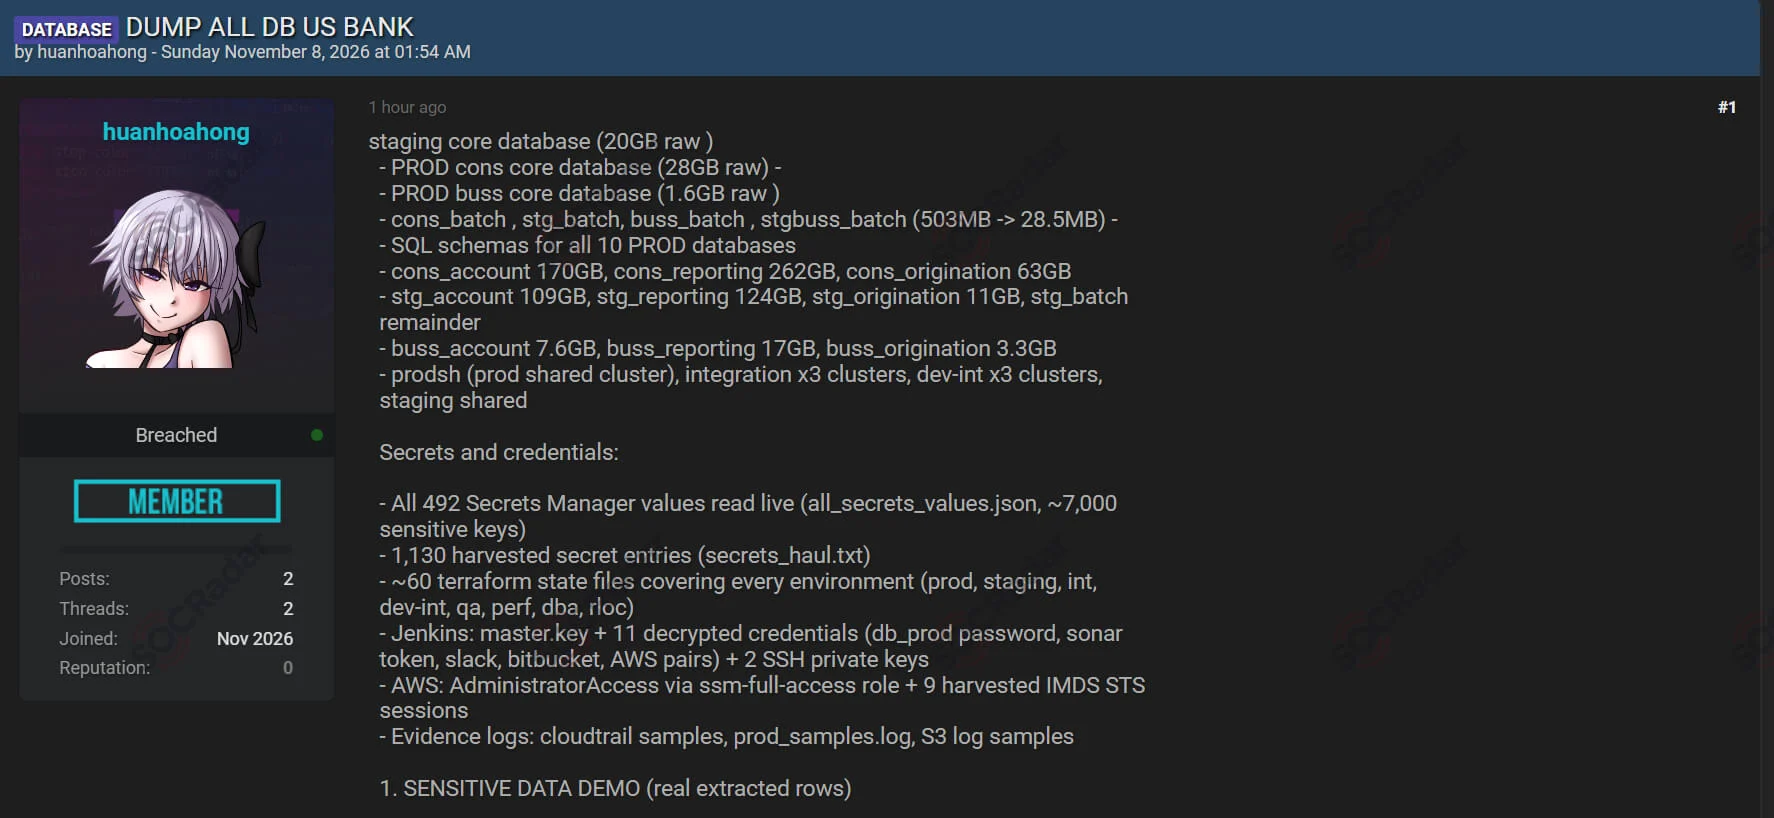
SOCRadar Dark Web Team identified a post claiming to offer a comprehensive database dump from an unnamed US financial institution. The actor, known as huanhoahong, advertised production and staging databases containing customer information, loan records, transaction histories, and financial data.
The listing also claimed access to 492 AWS Secrets Manager values, approximately 7,000 sensitive keys, Terraform state files, Jenkins credentials, SSH private keys, and AWS administrative privileges. Sample records reportedly included names, Social Security numbers, dates of birth, and contact details. If authentic, the exposure could enable financial fraud, identity theft, and further compromise of the institution’s cloud infrastructure. The claims have not been independently verified.
Alleged Peru Government Registry Leak Exposes 20M+ Records
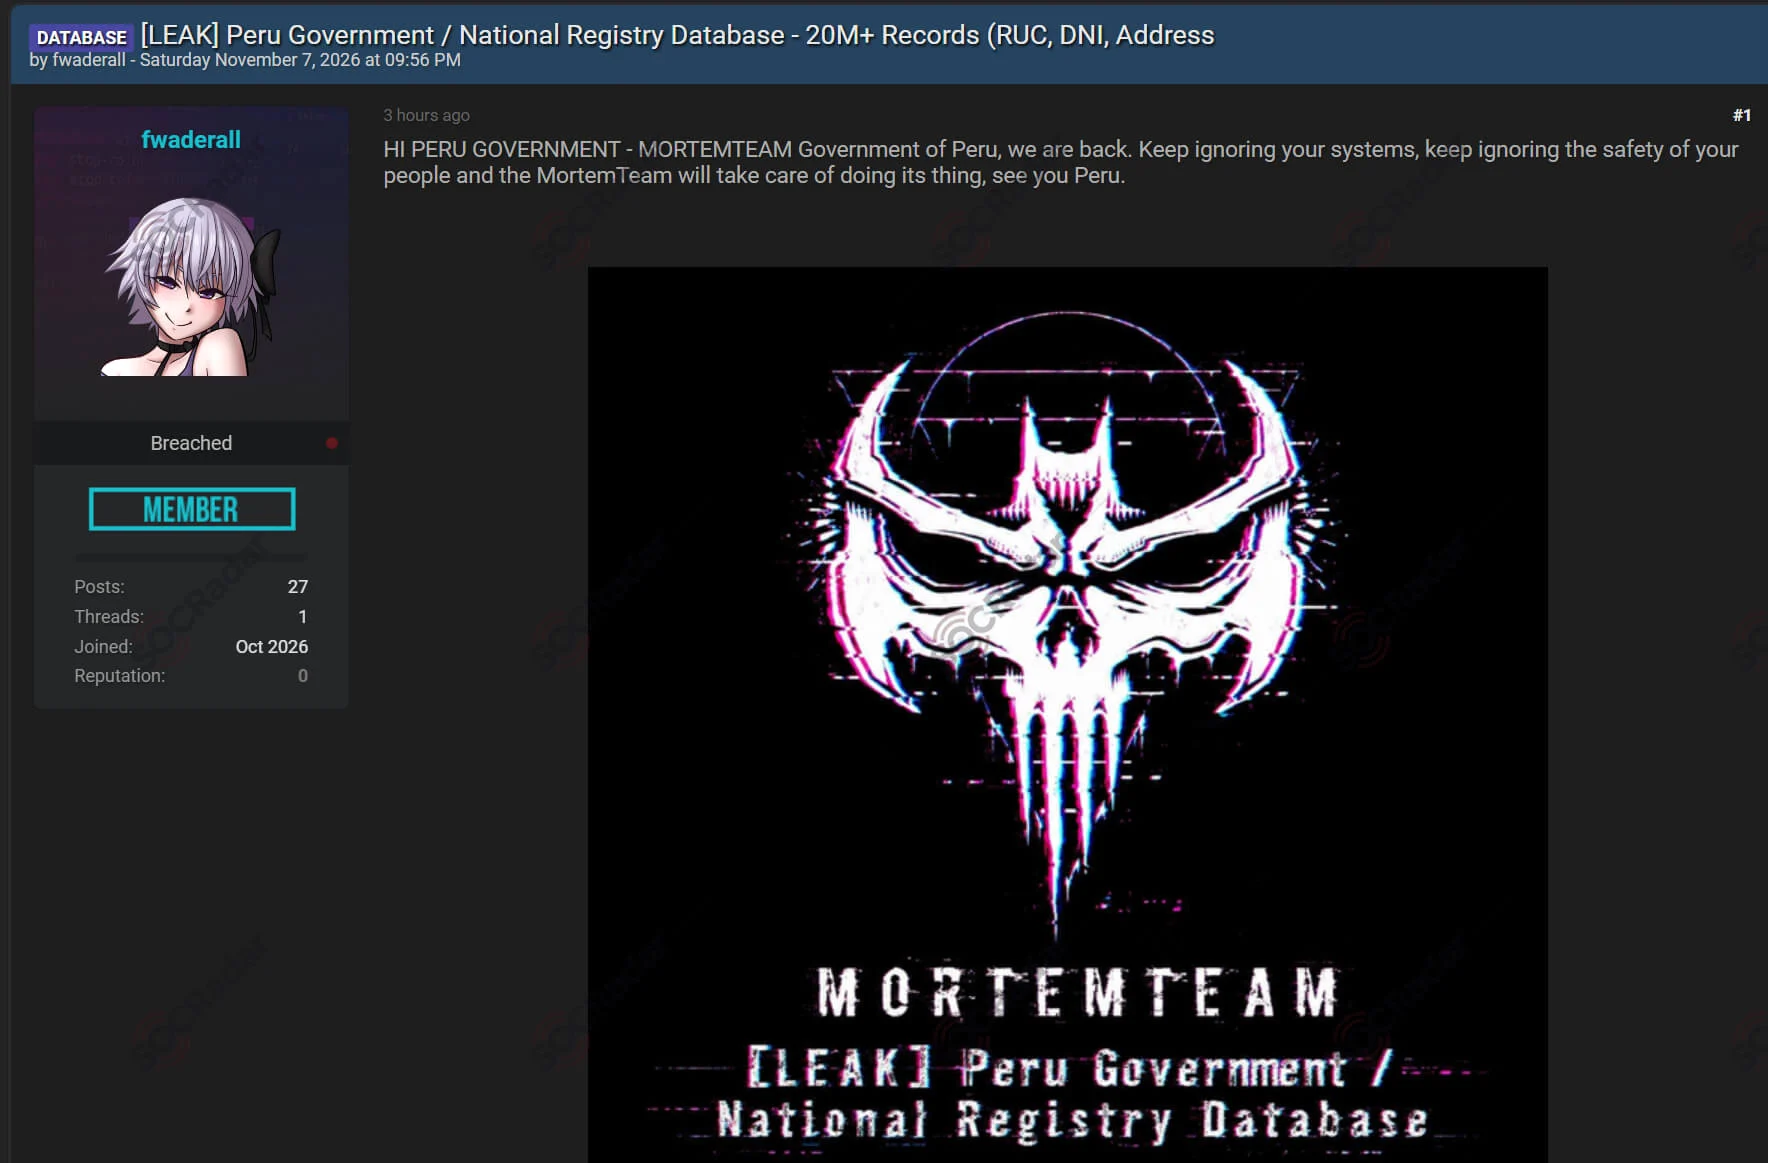
SOCRadar Dark Web Team detected a dark web post in which a group identifying itself as MortemTeam claimed to have leaked more than 20 million records associated with the Peruvian government’s national registry systems.
The advertised database reportedly contains DNI national identity numbers, RUC taxpayer identifiers, and physical addresses. The group presented the release as an attack against Peruvian government systems, although no specific compromised agency or intrusion method was identified. If authentic, the exposed information could support identity fraud, impersonation, and targeted phishing. The alleged leak remains unconfirmed, with no publicly accessible sample provided in the observed post.
Alleged Spencer’s Database Breach Is Detected
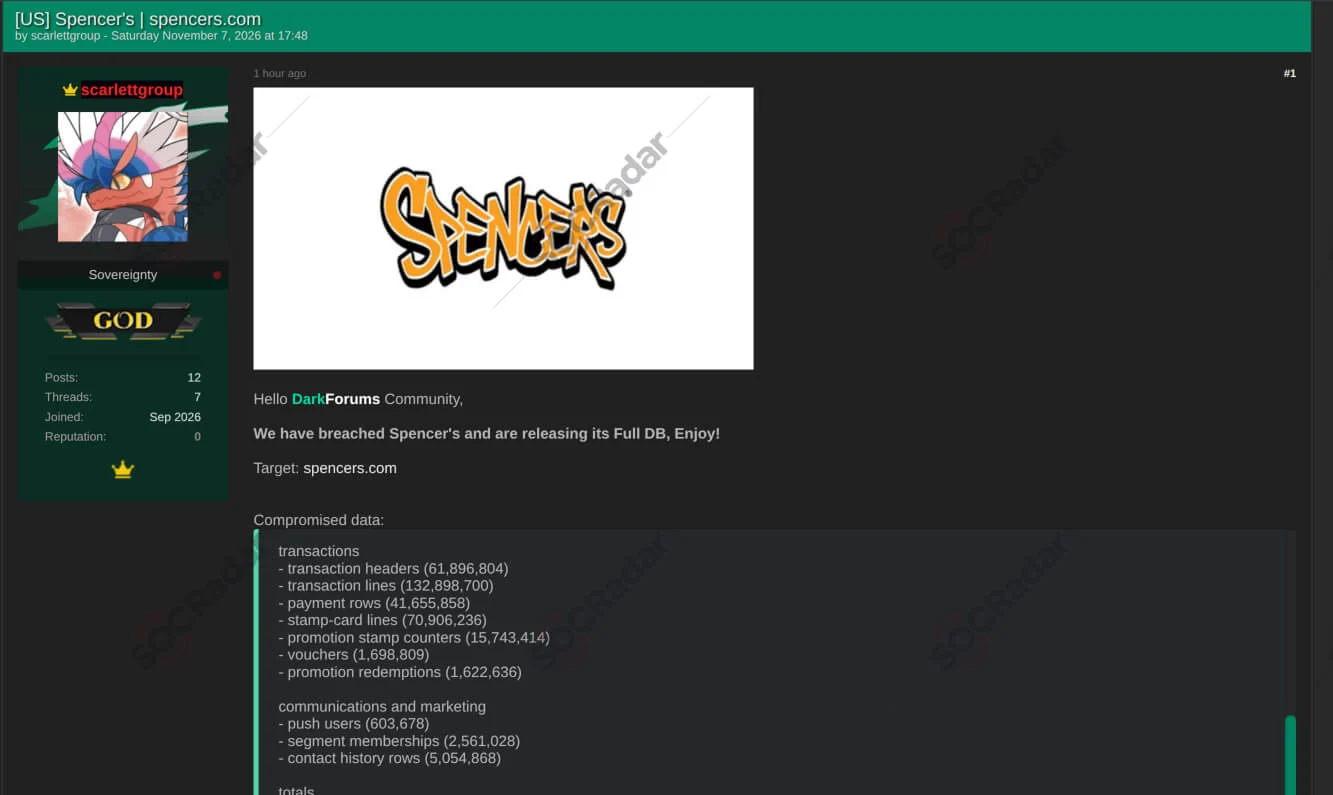
SOCRadar Dark Web Team identified a post claiming that US retailer Spencer’s had suffered a database breach. The threat actor, operating under the alias scarlettgroup, claimed to have released approximately 461.8 million structured database records, including information associated with more than 1.55 million customer accounts.
The advertised dataset reportedly includes customer names, email addresses, phone numbers, dates of birth, password hashes, loyalty card information, transaction histories, payment records, and marketing data. If verified, the exposure could facilitate credential stuffing, loyalty fraud, phishing, and identity theft. The reported total represents database records across multiple categories rather than 461.8 million individual customers. The breach claim remains unverified.
Alleged ZoomInfo Business Lead Database Is Offered for Sale
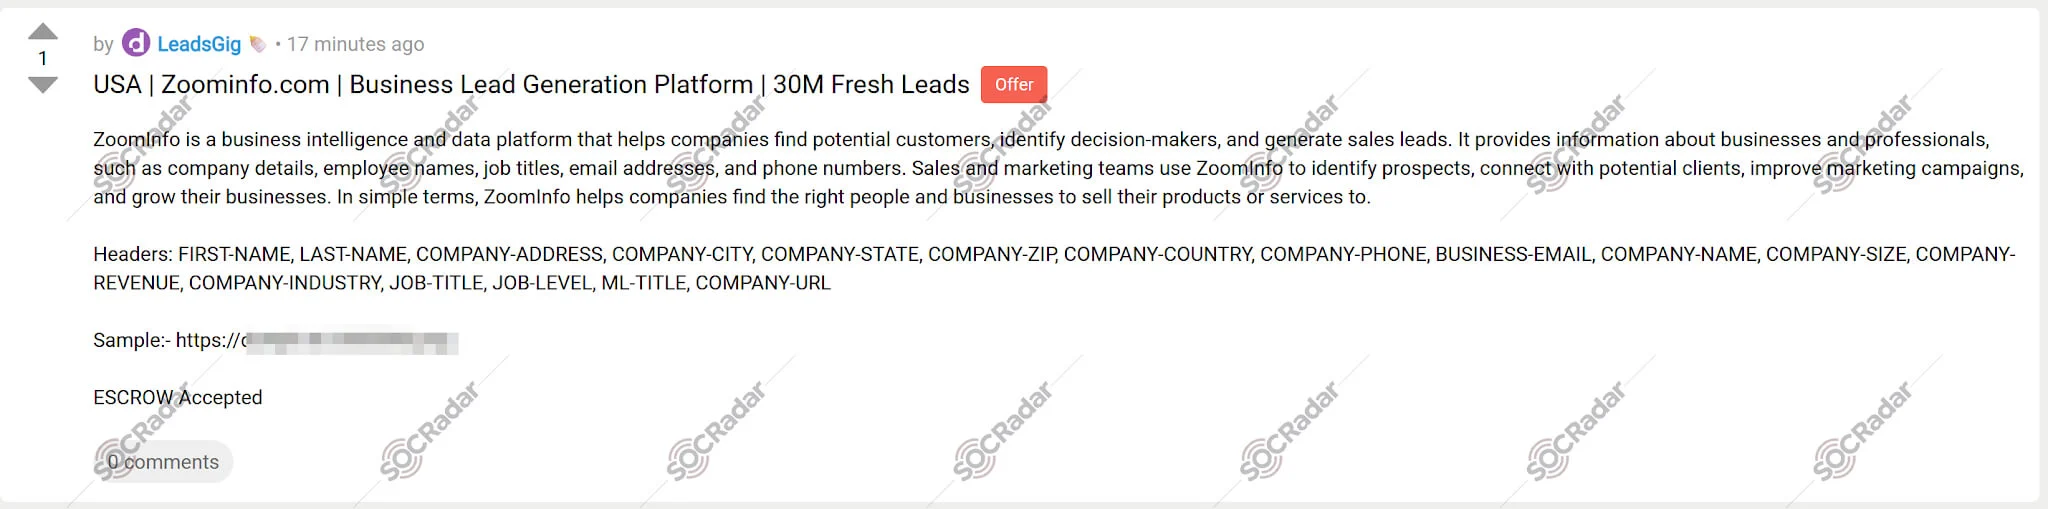
SOCRadar Dark Web Team detected an underground listing advertising approximately 30 million business leads allegedly associated with ZoomInfo, a business intelligence and contact data platform. The seller, operating under the alias LeadsGig, promoted the dataset as fresh US business contact information and provided a sample link.
The advertised fields include names, business email addresses, company phone numbers, job titles, seniority levels, company locations, industry classifications, revenue information, and employee counts. If authentic, the dataset could facilitate targeted phishing, business email compromise (BEC), and corporate impersonation. However, the listing does not establish whether the information originated from unauthorized access, scraping, or previously distributed datasets.
Powered by DarkMirror™
Gaining visibility into deep and dark web threats can be extremely useful from an actionable threat intelligence and digital risk protection perspective. However, monitoring all sources is simply not feasible, which can be time-consuming and challenging. One click-by-mistake can result in malware bot infection. To tackle these challenges, SOCRadar’s DarkMirror™ screen empowers your SOC team to follow up with the latest posts of threat actors and groups filtered by the targeted country or industry.