Latest articles
 SOCRadar
OpenAI Notifies Users of Mixpanel Security Incident
A recent security incident involving Mixpanel, a third-party analytics provider that OpenAI used to track frontend web interactions on its API platform, has raised important questions. On November 26, 2025,…
 SOCRadar
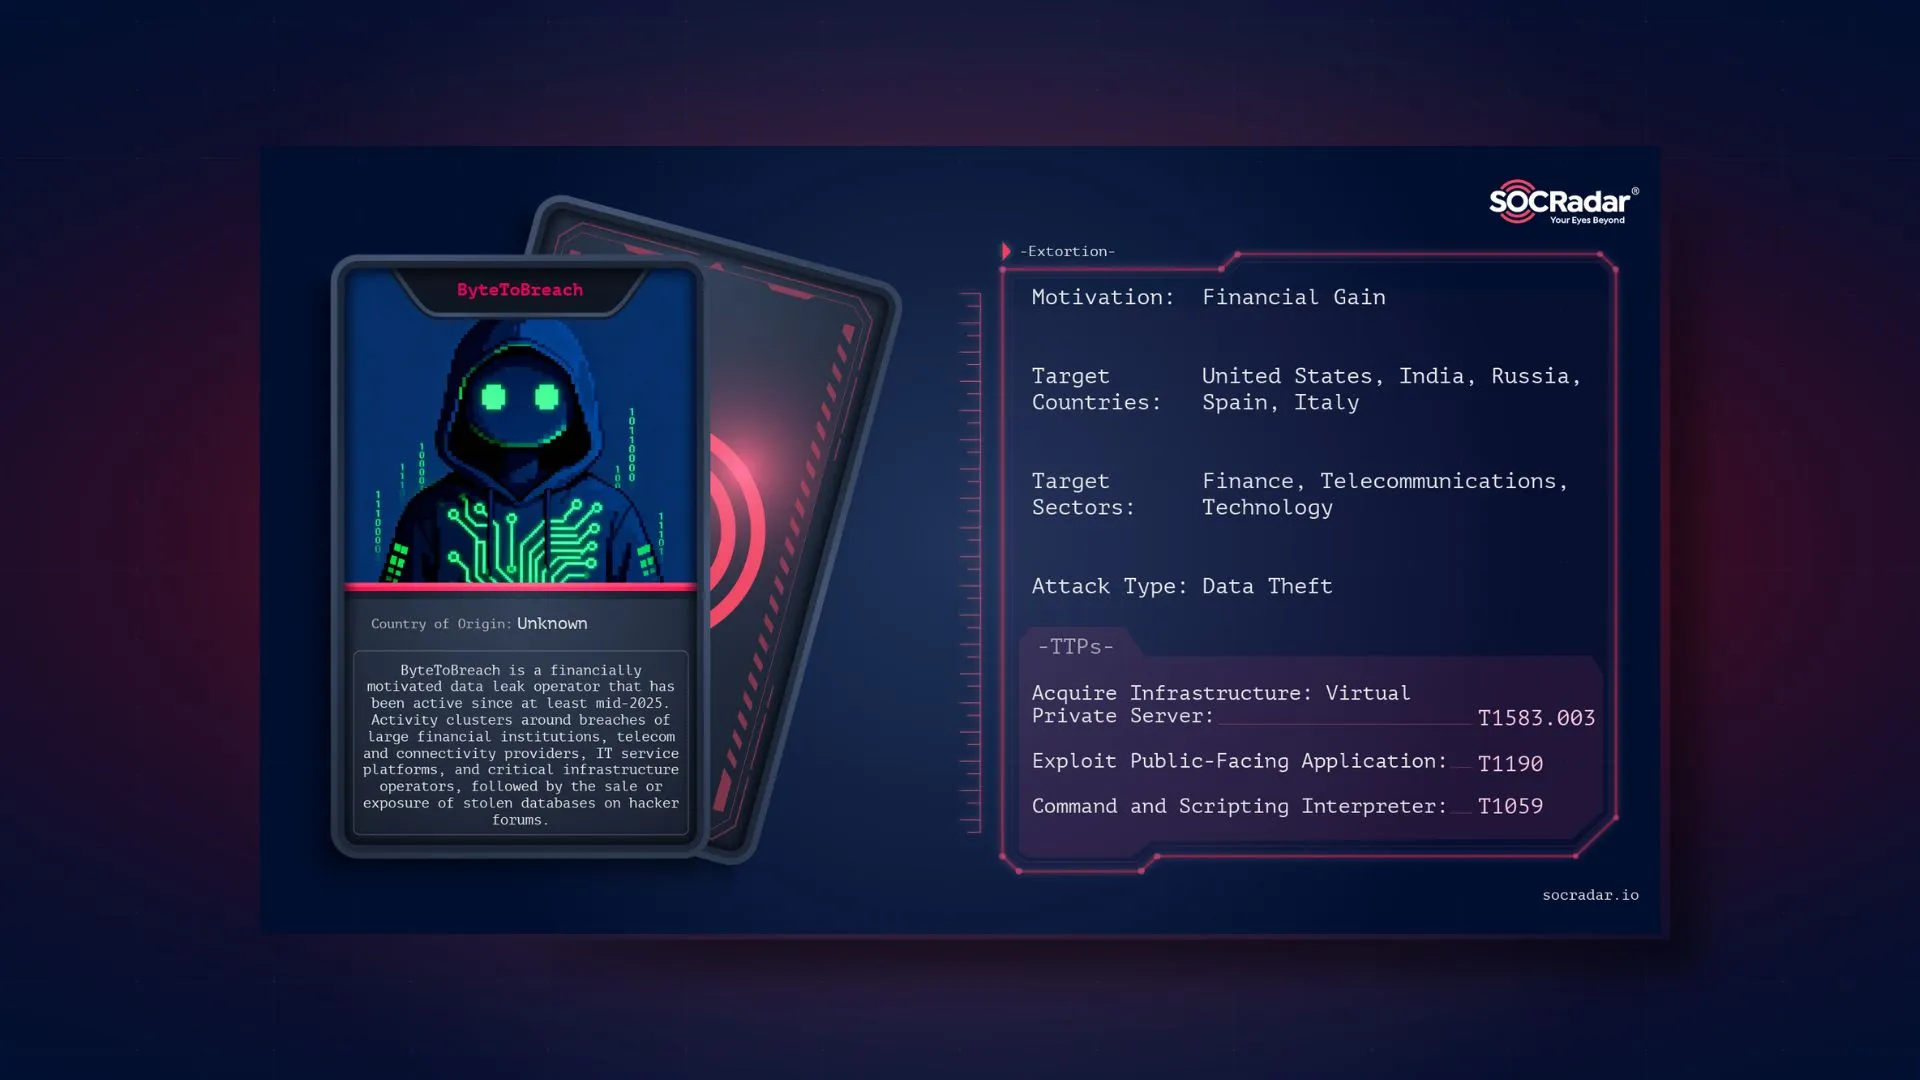
Dark Web Profile: ByteToBreach
By mid-2025, the alias ByteToBreach was already an active seller on a major cybercrime forum, offering access and databases from banks, telecom, airlines, and other large enterprises. On November 14,…
 SOCRadar
Alleged SeAH, Under Armour, SecureTeen, and Cloudeka Data Exposures Detected
SOCRadar’s Dark Web Team identified several high-impact underground posts this week, including alleged leaks involving SeAH Holdings, Under Armour, SecureTeen, and Indonesian cloud provider Cloudeka. Threat actors claimed supply chain…
 SOCRadar
Shai Hulud’s “The Second Coming”: New npm Campaign Hits Zapier, ENS, Postman
Security teams face yet another npm supply chain emergency. A new wave of Shai Hulud: The Second Coming. The worm has trojanized hundreds of packages from major projects like Zapier,…
 SOCRadar
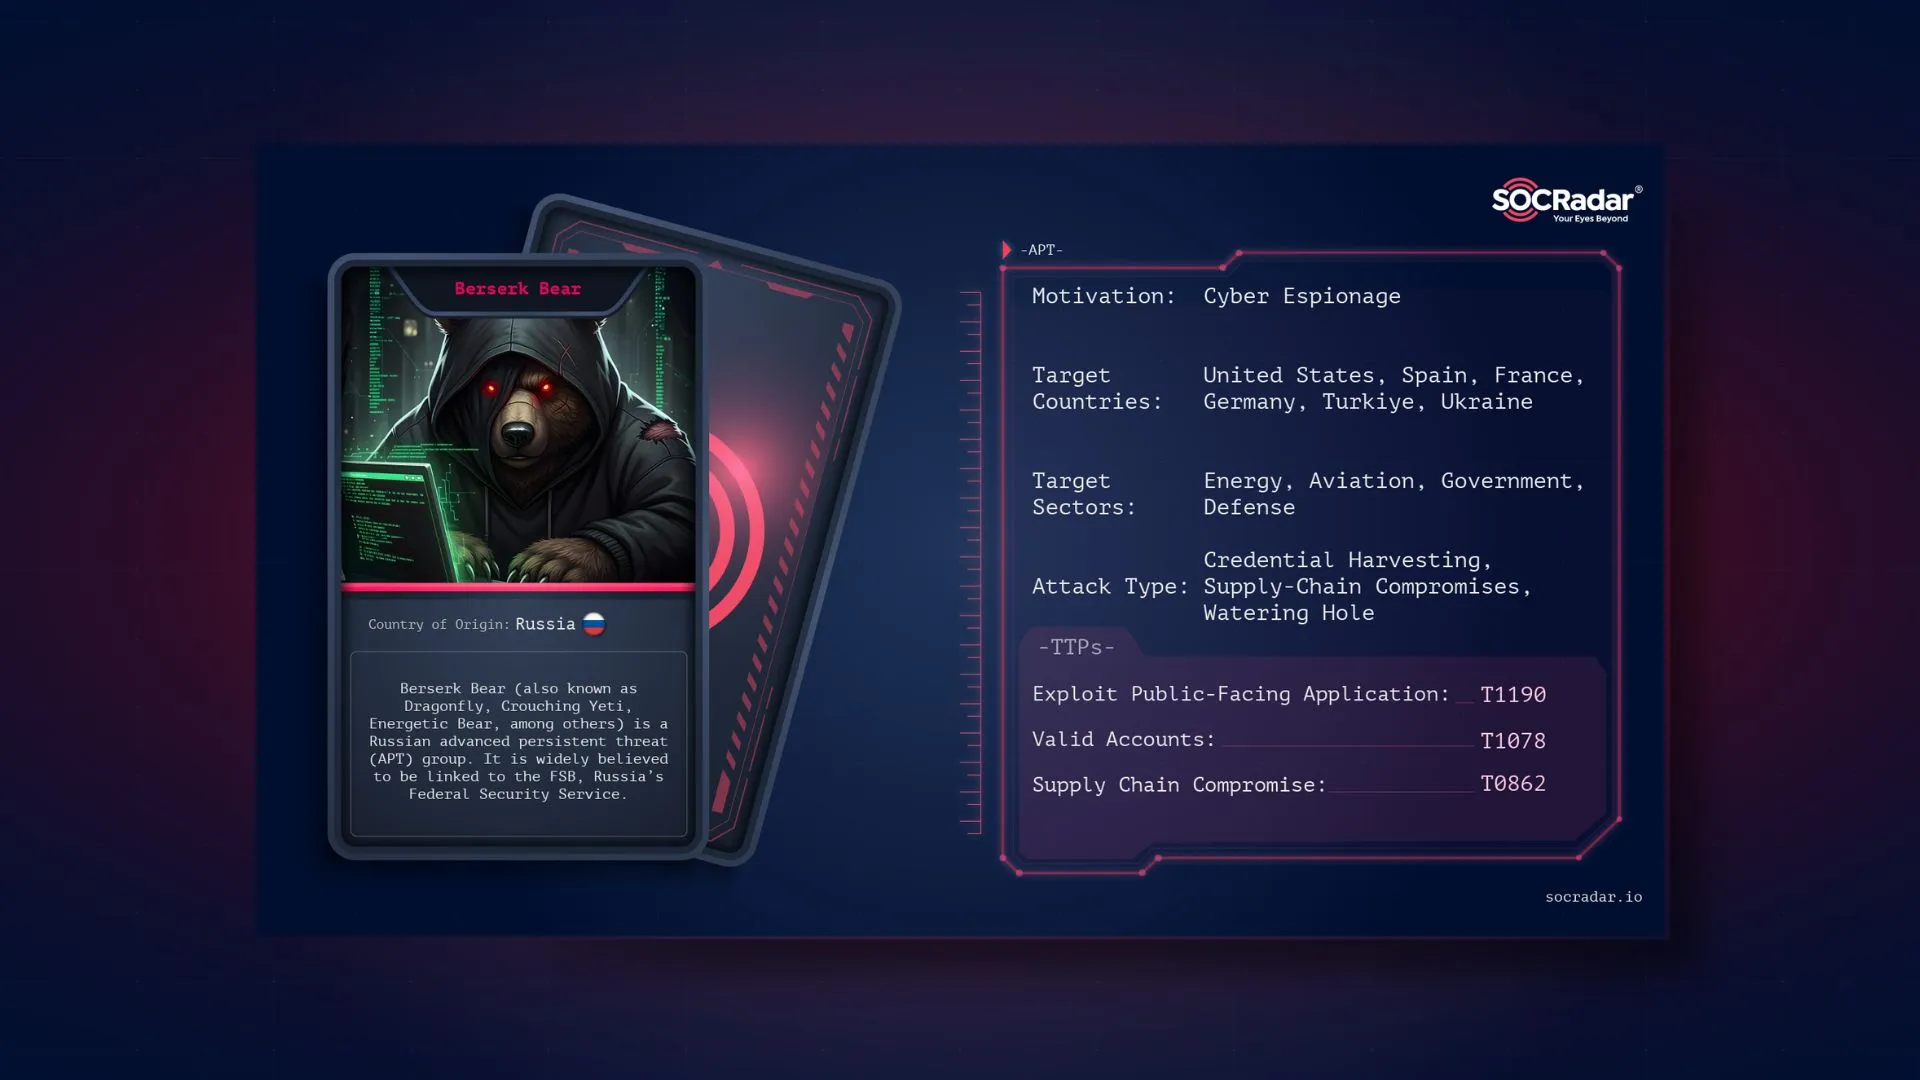
Dark Web Profile: Berserk Bear
Berserk Bear is a Russian state-sponsored cyber espionage group linked to the FSB. They have been active since at least 2010 under many names (Dragonfly, Energetic Bear, Havex, Crouching Yeti,…
 SOCRadar
DDoSia Shifts Its Focus Toward Sweden: Weekly DDoS Threat Intelligence
Analysis Period: November 17 to 23, 2025 NoName057(16), a pro-Russian hacktivist group, conducted coordinated DDoS attacks against multiple NATO and EU countries during the week of November 17-23, 2025. The…
 SOCRadar
CVE-2025-61757: Oracle Identity Manager Auth Bypass Flaw Added to CISA’s KEV
CISA recently added CVE-2025-61757 to its Known Exploited Vulnerabilities (KEV) Catalog after confirming active exploitation. The listing highlights a critical flaw affecting Oracle Identity Manager – part of Oracle Fusion…
 SOCRadar
What You Need To Know About Gainsight Breach
Salesforce warned customers about a new incident involving the Gainsight app after detecting unusual activity in connected environments. Google’s threat team says more than 200 Salesforce instances may be affected.…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action