Latest articles
 SOCRadar
Shai-Hulud Hades PyPI Campaign: 19 Packages Trojanized via Wheel Startup Hooks
A PyPI supply-chain campaign in the Shai-Hulud / Mini Shai-Hulud / Miasma lineage compromised 19 Python packages by shipping trojanized wheel artifacts. Researchers observed 37 malicious wheels that add a…
 SOCRadar
Handala Claims It Disrupted Israeli Radar Systems: Here’s What We Actually Know
On the same day that Iran and Israel traded missile strikes in their most serious exchange since the April ceasefire, an Iranian-linked hacker group called Handala posted a series of…
 SOCRadar
2026 FIFA World Cup Threat Landscape: The Kickoff for Cybercriminals
The fraud and threat ecosystem targeting the 2026 FIFA World Cup is already live, with thousands of phishing domains, active credential theft campaigns, and nation-state actors in position months before…
 SOCRadar
CVE-2026-20230: Cisco Unified CM WebDialer SSRF Can Lead to Root-Level Compromise
[Update] July 3, 2026: Cisco Confirms Active Exploitation of CVE-2026-20230 Cisco has released fixes for CVE-2026-20230, an unauthenticated remote vulnerability affecting Cisco Unified Communications Manager (Unified CM) and Unified CM…
 SOCRadar
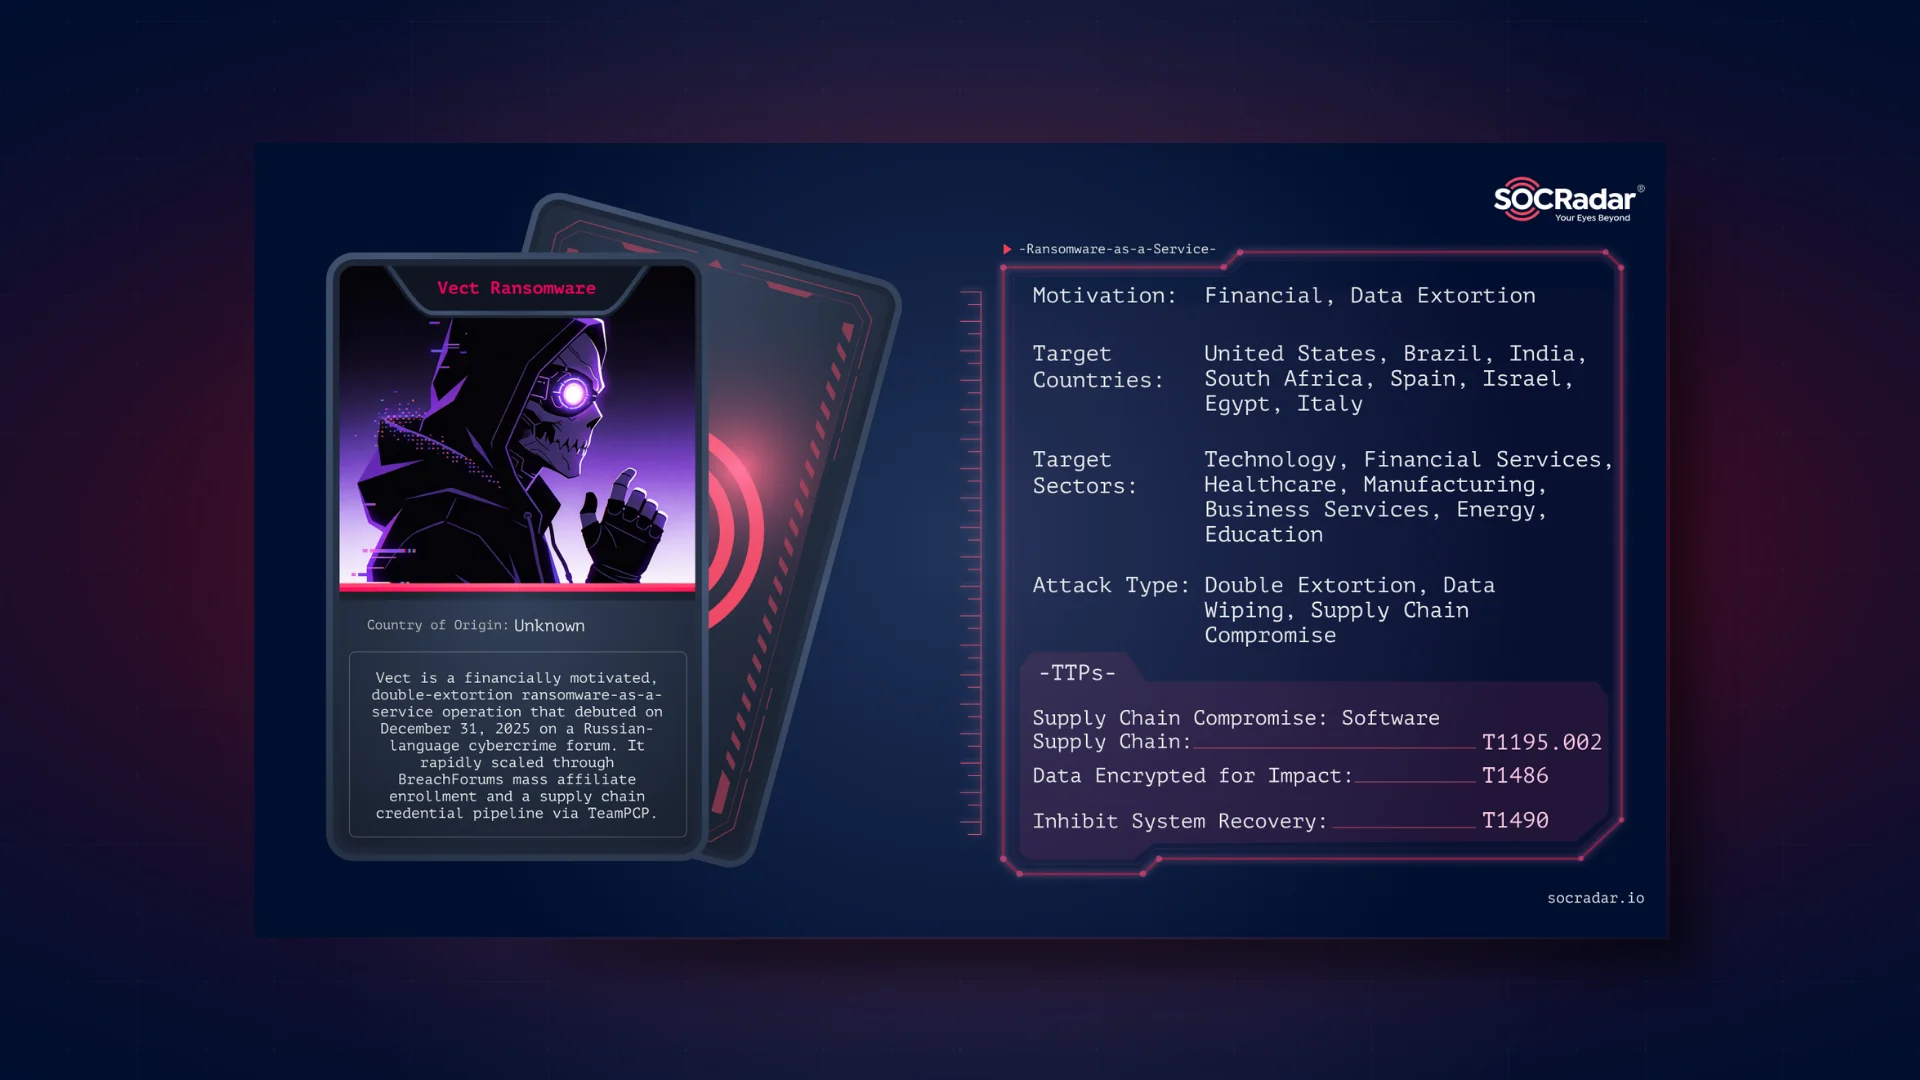
Dark Web Profile: Vect Ransomware
Most new ransomware operations spend their first months in the shadows, courting affiliates one at a time on closed forums. Vect did the opposite. Within four months of its December…
 SOCRadar
HTTP/2 Bomb: How Default Configurations Open a New DoS Vector
A newly disclosed Denial-of-Service (DoS) technique dubbed HTTP/2 Bomb can crash or stall servers that run default HTTP/2 configurations across several widely deployed stacks. The technique chains two behaviors that…
 SOCRadar
CVE-2025-48595: June 2026 Android Security Update Fixes Framework Zero-Day
Google’s June 2026 Android Security Bulletin includes a fix for an Android Framework elevation of privilege zero-day tracked as CVE-2025-48595. Google noted the issue “may be under limited, targeted exploitation,”…
 SOCRadar
Top 10 Cyber Threat Actors Targeting Brazil
Brazil enters the second half of 2026 as Latin America’s undisputed top cybercrime target. With a general election approaching in October 2026 and a booming digital economy built on platforms…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action