Latest articles
 SOCRadar
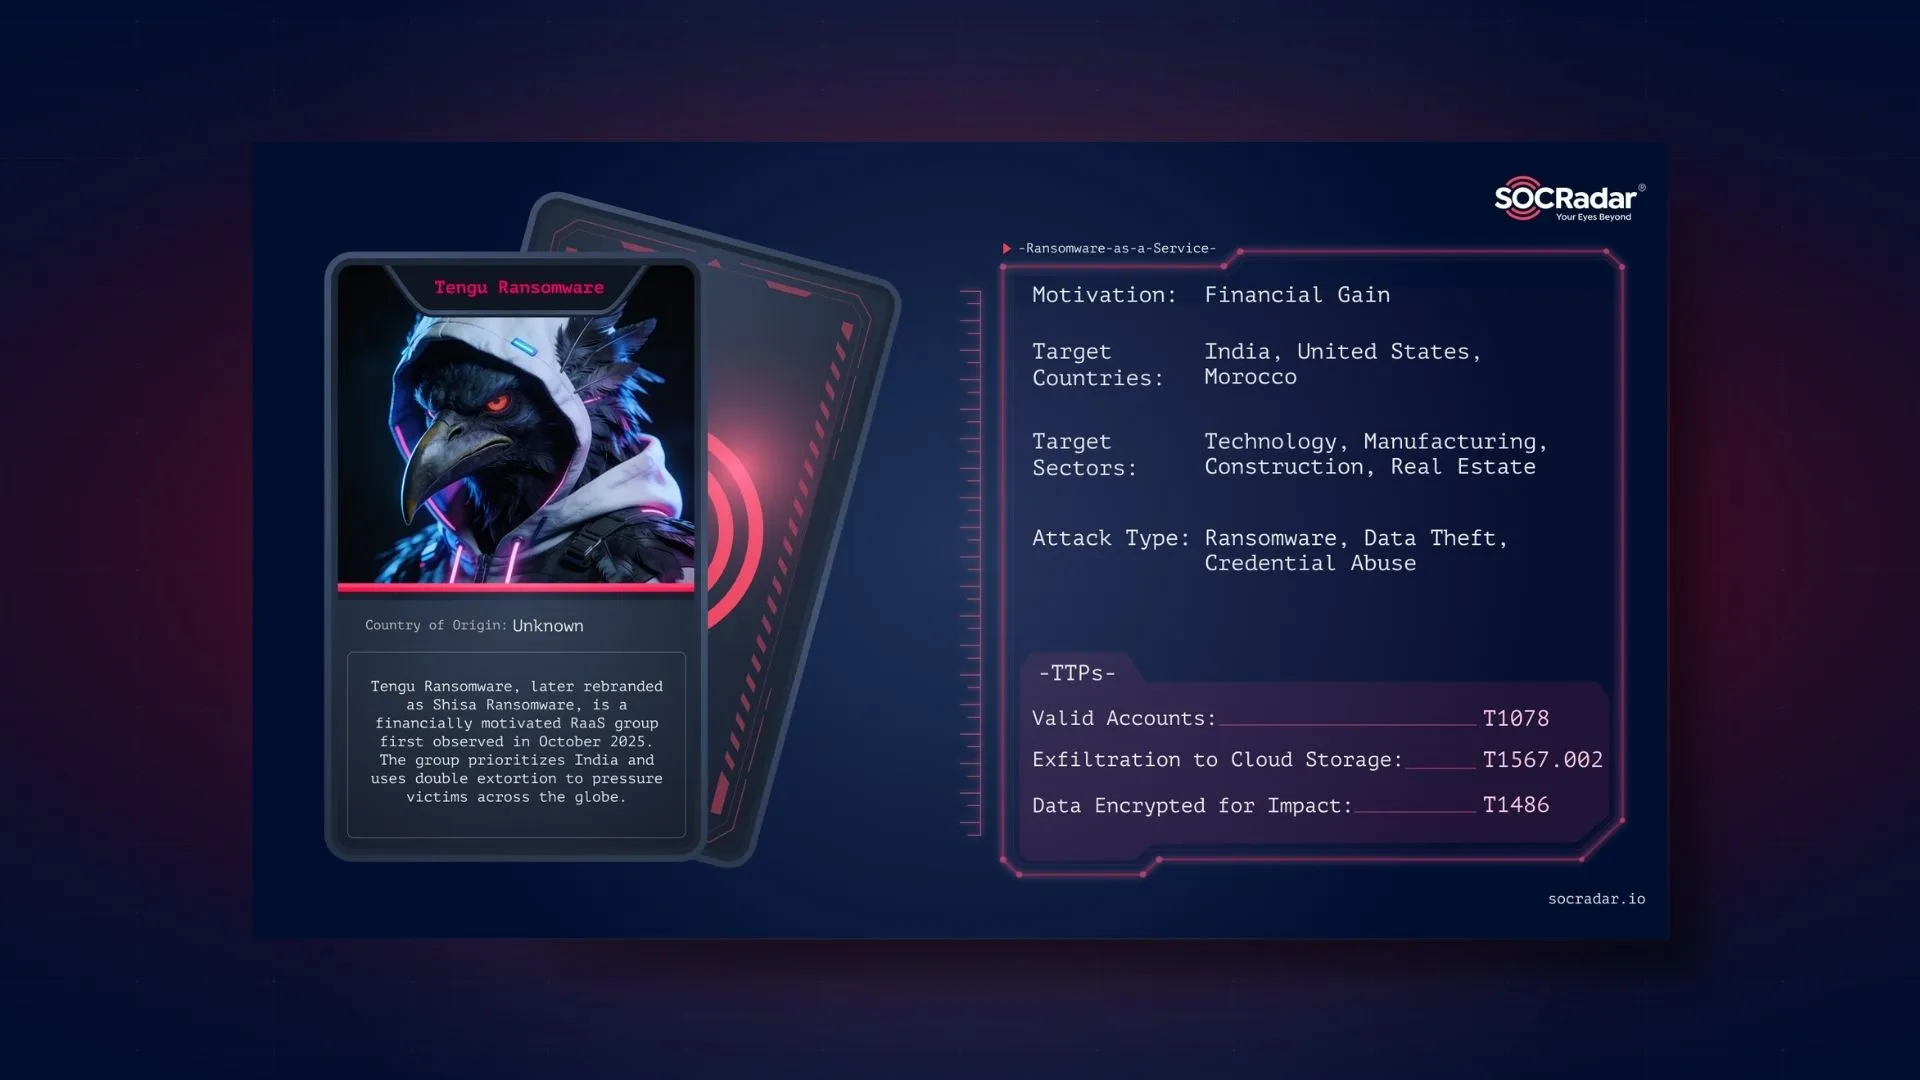
Dark Web Profile: Tengu Ransomware (Shisa)
Despite a measured public persona, Tengu Ransomware operates as a financially motivated, well-organized threat. First observed in late 2025, the group emerged as a Ransomware-as-a-Service (RaaS) operation combining a double-extortion…
 SOCRadar
ServiceNow Breach: Customer Data Exposed Through Unauthenticated API Access
In early June 2026, ServiceNow notified impacted customers about malicious activity involving unauthorized access to customer instance data, now documented under KB3067321. In this blog post, we will outline what…
 SOCRadar
Ivanti Sentry’s CVE-2026-10520 Enables Root RCE
CVE-2026-10520 is a critical OS command injection vulnerability in Ivanti Sentry that can allow a remote, unauthenticated attacker to execute commands as root on vulnerable appliances. The issue is reachable…
 SOCRadar
June 2026 Patch Tuesday: 206 Vulnerabilities, Three Zero-Days Including HTTP/2 Bomb Flaw (CVE-2026-49160)
Microsoft released its June 2026 Patch Tuesday security updates, resolving a total of 206 vulnerabilities across Windows and a wide range of Microsoft products and components. This month’s release includes…
 SOCRadar
SAP Security Patch Day June 2026: Critical CVE-2026-44748 SAML Flaw Could Allow Full Authentication Bypass
On June 9, 2026, SAP released its monthly security updates, which included 15 new Security Notes addressing vulnerabilities across several SAP products. SAP Security Patch Day June 2026 updates cover…
 SOCRadar
What Do You Need to Know About Claude Fable 5?
On June 9, 2026, Anthropic released Claude Fable 5, calling it the most capable model it has ever made available to the general public. For security teams, CISOs, and anyone…
 SOCRadar
CVE-2026-11645: Exploited Chrome V8 Bug Enables In-Browser Code Execution
CVE-2026-11645 is a high-severity Google Chrome zero-day in the V8 JavaScript/WebAssembly engine caused by an out-of-bounds (OOB) read/write condition. Google has confirmed it is aware that an exploit exists in…
 SOCRadar
CISA KEV Highlights LiteLLM RCE (CVE-2026-42271) & Check Point VPN Auth Bypass (CVE-2026-50751)
CISA added two vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog on June 8, 2026: CVE-2026-42271 in BerriAI LiteLLM and CVE-2026-50751 in Check Point Security Gateway. Both issues affect high-value…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action