Latest articles
 SOCRadar
The Quarry: Inside the PhaaS Operation Behind Hundreds of IRS and SSA Phishing Campaigns
What looks like a wave of disconnected phishing incidents – some impersonating the IRS, others mimicking the Social Security Administration or DocuSign – can trace back to a single developer…
 SOCRadar
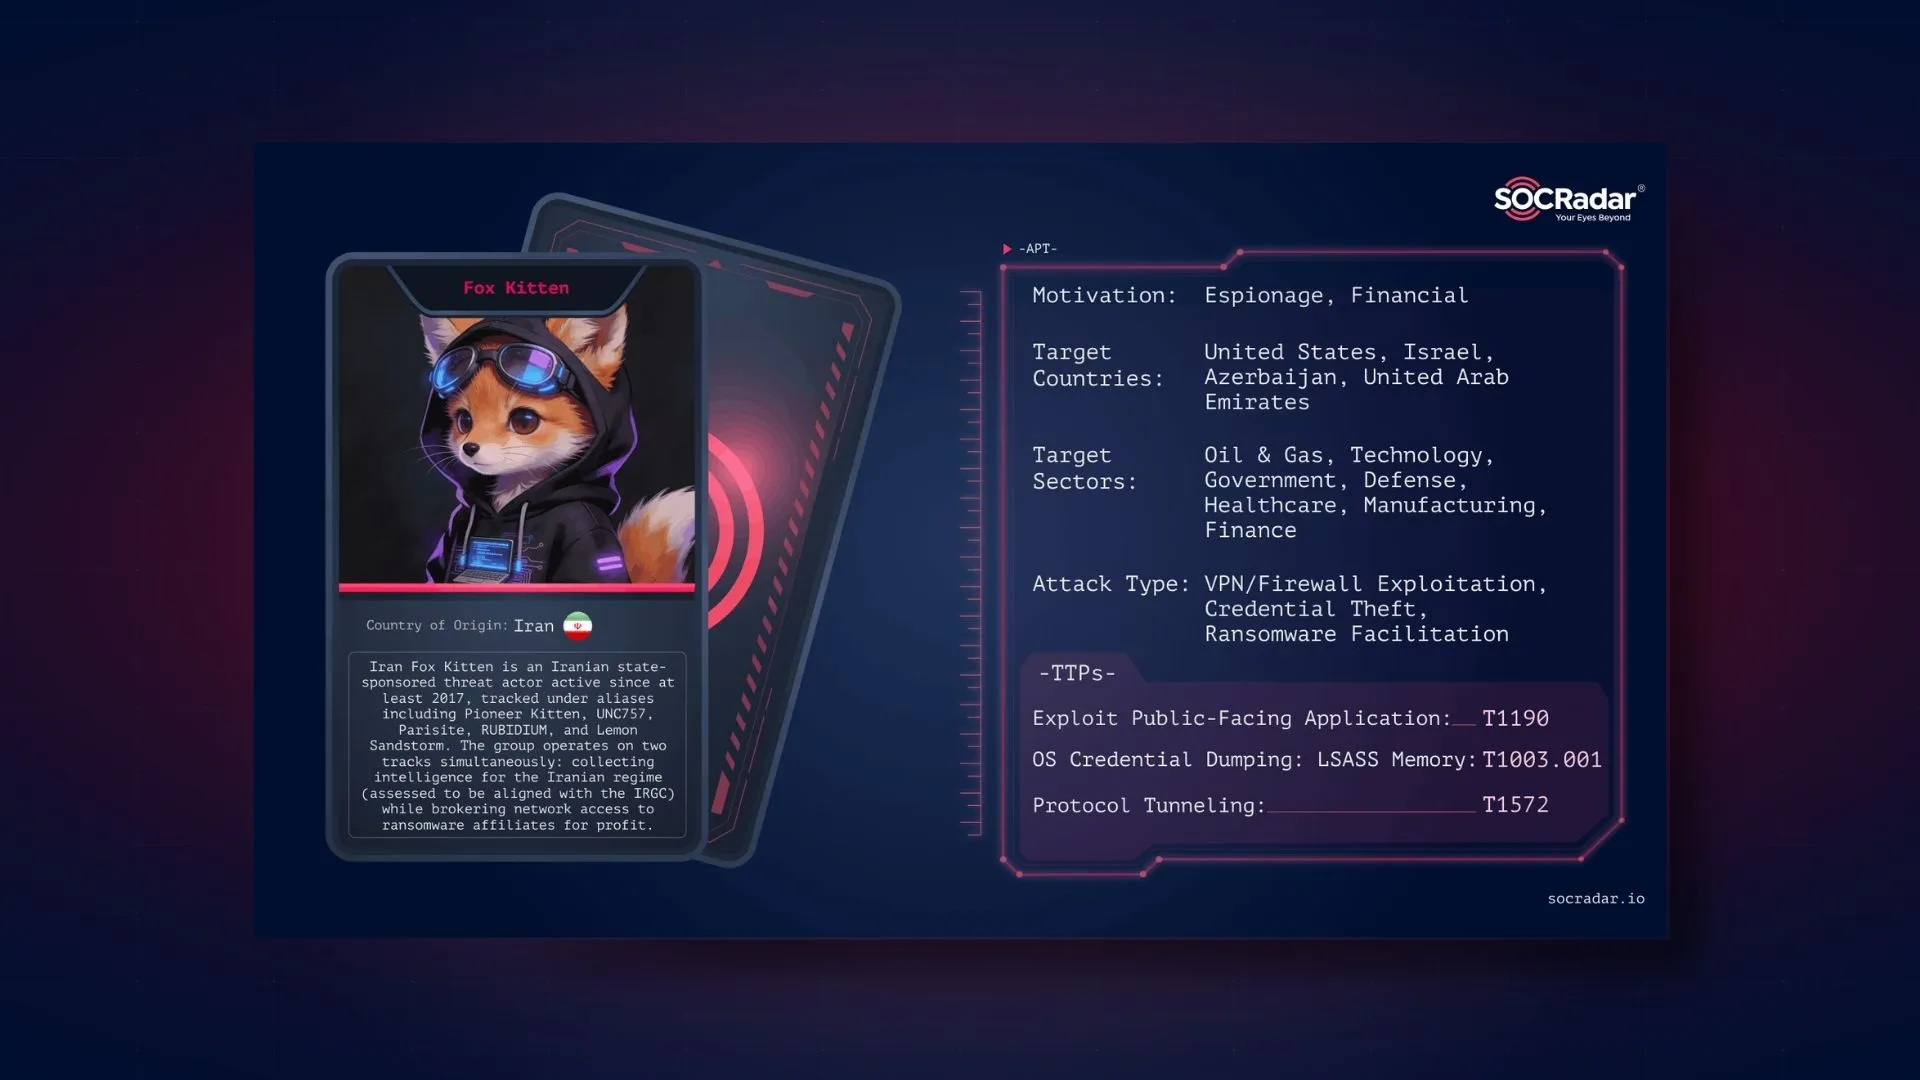
Dark Web Profile: Fox Kitten
Fox Kitten stands out among Iranian Advanced Persistent Threat (APT) groups for operating on two tracks simultaneously: collecting intelligence for the Iranian regime while brokering network access to ransomware affiliates…
 SOCRadar
Iran Hajj Organization Data Claim, Crypto Leads Sale, APT43 Tooling Claim, Sweden User Data, and Chrysler Breach Claim
SOCRadar’s Dark Web Team identified several new underground posts, including an alleged 168 million-record database sale tied to Iran’s Hajj and Pilgrimage Organization and a separate listing offering large volumes…
 SOCRadar
What the EU AI Act Actually Requires for Cybersecurity (And Where Enterprises Are Exposed)
The EU AI Act contains specific cybersecurity requirements. Article 15 names the threats. Article 73 sets reporting deadlines. Article 9 mandates continuous risk management. But most coverage of the Act…
 SOCRadar
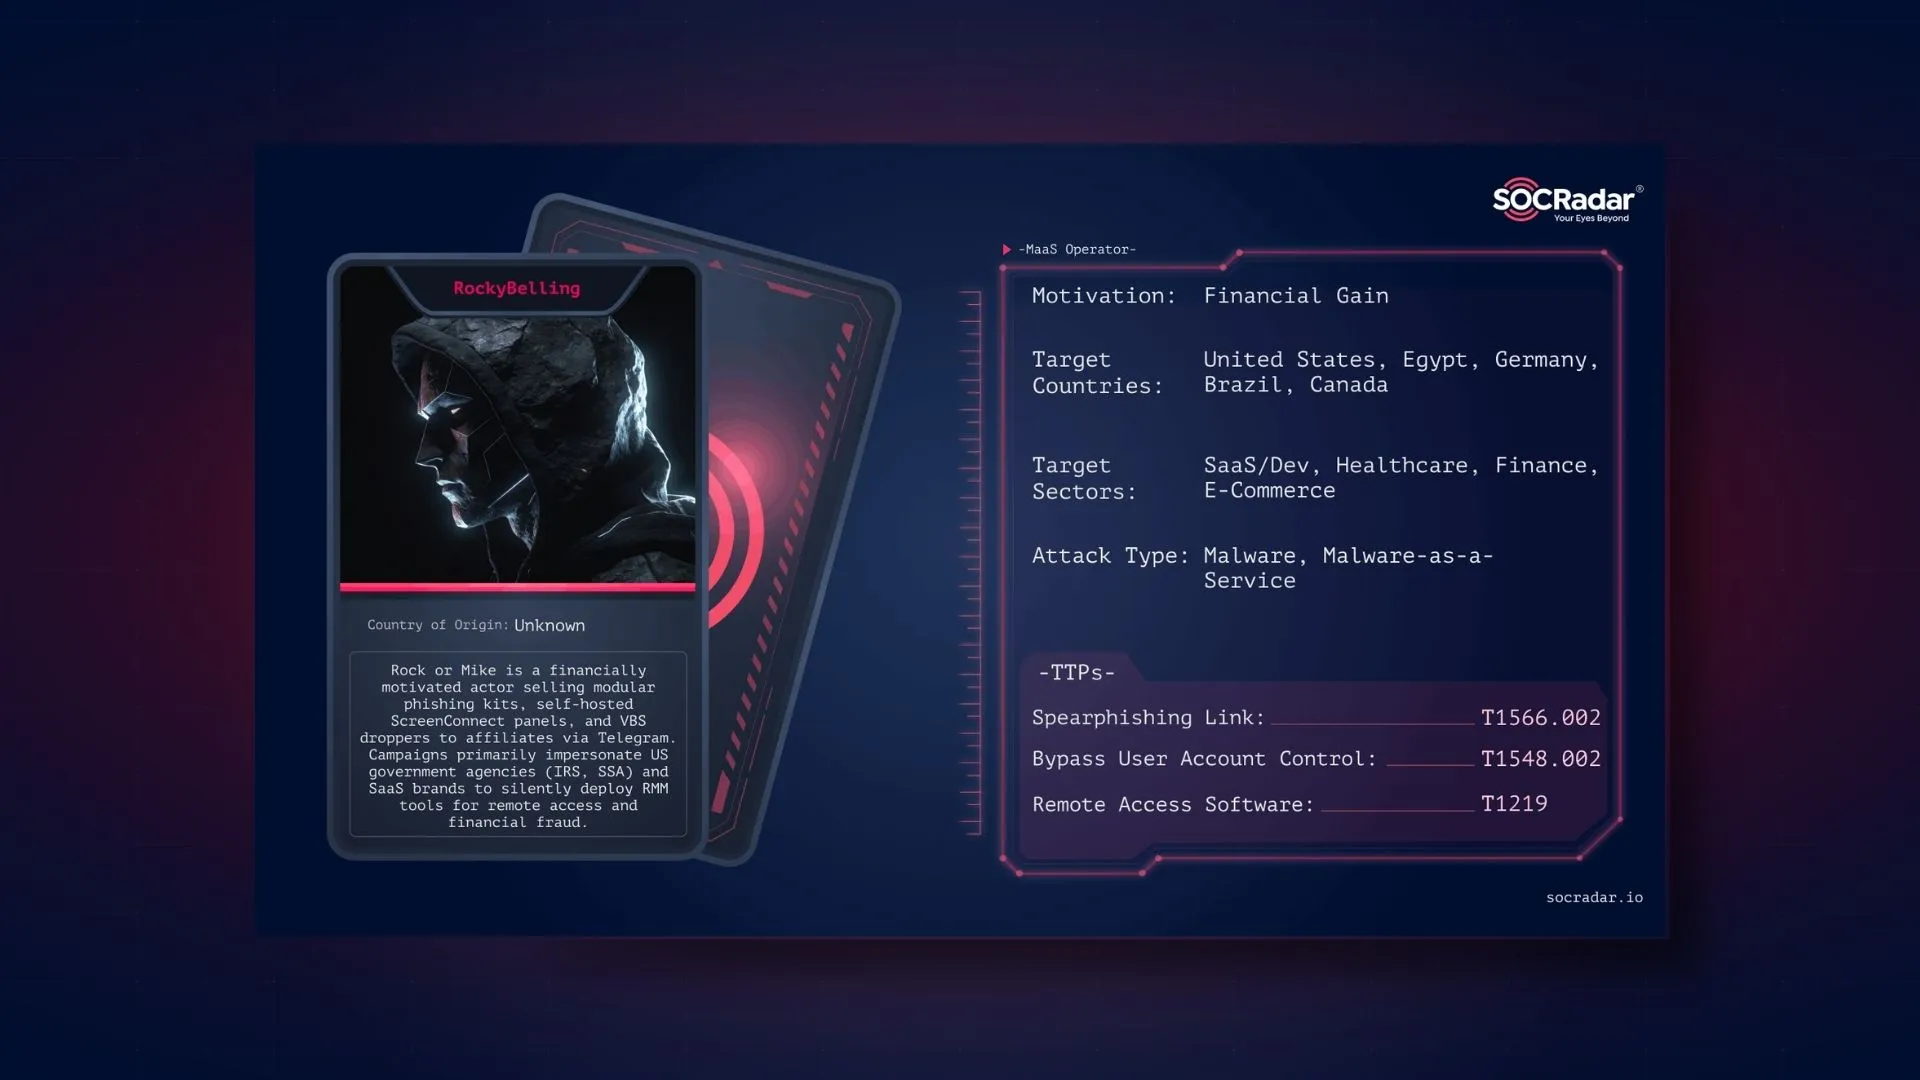
Dark Web Profile: Rock
Most Phishing-as-a-Service operations are run by a faceless brand. Rock is the opposite: a single developer who builds, maintains, and sells an entire phishing and remote access toolkit, then sits…
 SOCRadar
CVE-2026-35273 in Oracle PeopleSoft PeopleTools EMHub Under Active Exploitation
[Update] October 28, 2026: Research Shows CVE-2026-35273 Chains Three PeopleSoft Flaws [Update] September 28, 2026: ShinyHunters Resurges PeopleSoft Exploitation Using WAF Evasion Techniques Oracle has disclosed CVE-2026-35273, a critical Remote…
 SOCRadar
New Data Extortion Group “Pink” Goes Big Game Hunting With Evasive Phishing Kits
Pink Data Extortion Group is emerging as one of the latest examples of how voice phishing and data extortion continue to shape the threat landscape. Instead of relying on noisy…
 SOCRadar
Electronic Warfare, Drones, and Cyber: Inside Modern Hybrid Warfare
Electronic warfare, drone warfare, and cyber operations all depend on the same foundation, the electromagnetic spectrum and the digital networks built on top of it. Anyone who can contest that…
Never miss a critical advisory.
Join 30,000+ security professionals who read SOCRadar research every week.
See SOCRadar in Action